
GoDaddy email scam: how to spot it and what to do
The GoDaddy email scam has emerged as a significant threat, affecting countless people through a sophisticated and widespread deceptive email operation. These fraudulent campaigns use a large-scale distribution strategy, sending thousands of emails to unwitting recipients.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove GoDaddy email scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps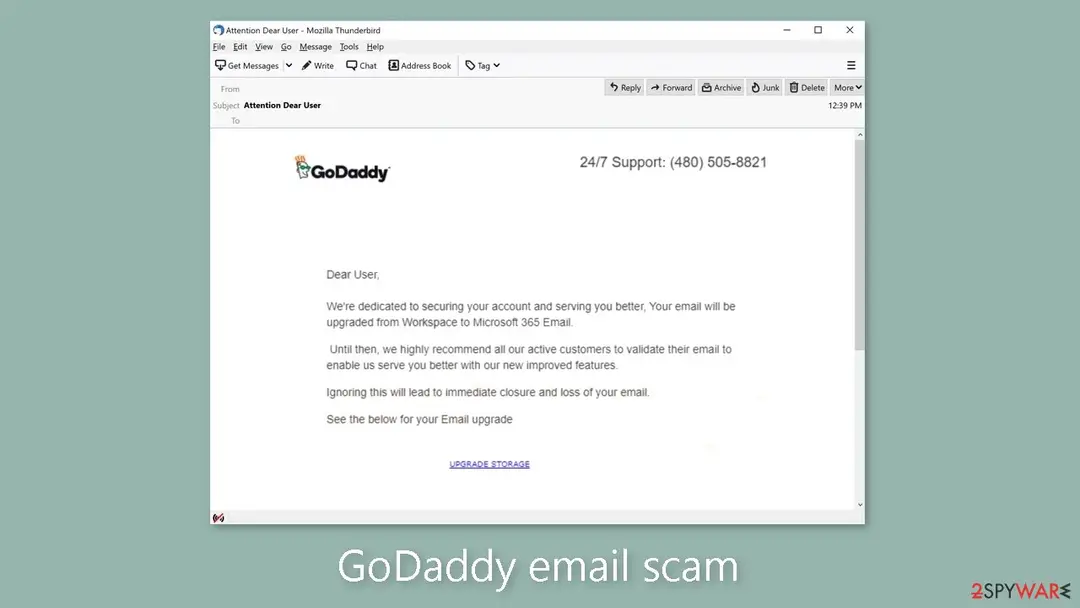
GoDaddy email scam: summary
| Distribution | |
|---|---|
| NAME | GoDaddy email scam |
| TYPE | Phishing, fraud |
| SYMPTOMS | Fraudulent emails falsely assert that recipients are required to validate their email accounts in order to enhance their functionality. |
| DANGERS | Illicit online transactions, modified passwords for online accounts, identity theft, and unauthorized computer access. |
| Name | GoDaddy email scam |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 10 more facts
| Type | Phishing message |
|---|---|
| Symptoms | A phishing e-mail asking you to sign in and a support phone number shown on screen |
| Evidence | 4 write-ups by security sites; no sample analysed yet |
| Arrives as | |
| Pretends to be | Microsoft |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| Phone number | (480) 505-8821 |
| First seen | 8 June 2023 |
| Facts checked | 5 October 2026 |
What the GoDaddy email scam e-mail looks like
Subject: Attention Dear User
GoDaddy
24/7 Support: (480) 505-8821
Dear User,
WE're dedicated to securing your account and serving you better, Your email will be upgraded from Workspace to Microsoft 365 Email.
Until then, we highly recommend all our active customers to validate their email to enable us serve you better with our new improved features.
Ignoring this will lead to immediate closure and loss of your email.
See the below for your Email upgrade
UPGRADE STORAGE
Blake Irving
CEO, GoDaddy
Copyright © 1999-2021 GoDaddy Operating Company, LLC. 14455 N. Hayden Rd, Ste. 219, Scottsdale, AZ 85260, USA. All Rights Reserved.
How to tell the GoDaddy email scam e-mail is fake
- Phone number:
(480) 505-8821
Is GoDaddy email scam dangerous? What the senders want
From our report of Jun 2023 · not reviewed since
GoDaddy email scam tries to redirect users to a phishing site to obtain their login credentials
The GoDaddy email scam has emerged as a significant threat, affecting countless people through a sophisticated and widespread deceptive email operation.
These fraudulent campaigns use a large-scale distribution strategy, sending thousands of emails to unwitting recipients.
From our report of Jun 2023 · not reviewed since
How the GoDaddy email scam works
The emails used in this scam are expertly designed to look like they came from GoDaddy, a reputable internet domain registrar and web hosting company.
These messages falsely inform recipients of an upcoming email account upgrade and deceptively request that they verify their accounts in order to proceed with the alleged enhancement.
It is critical to emphasize that all of the information contained in these deceptive emails is completely false, and they have no affiliation with the genuine GoDaddy, Inc. The subject lines of the fake "GoDaddy" emails frequently include phrases like "Attention Dear User" or similar variations.
They claim that email accounts will be moved from the "Workspace" platform to "Microsoft 365 Email." Recipients are prompted to validate their email accounts in order to initiate this upgrade and gain access to allegedly new and improved features.
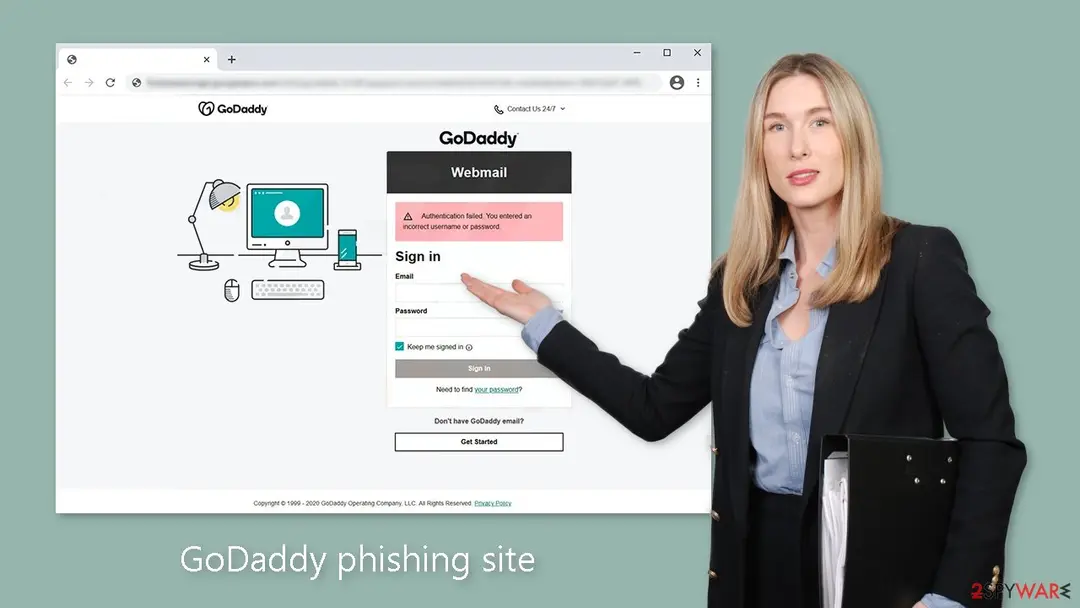
In an attempt to persuade recipients to act quickly, the scam messages threaten account closure or blockage if they do not comply. The emails usually include a call-to-action button, such as "UPGRADE STORAGE," that redirects recipients to a phishing website that has been cleverly disguised as a legitimate sign-in page.
From our report of Jun 2023 · not reviewed since
Shielding against deceptive email scams: tips for users
By adopting the following measures, individuals can bolster their online security and reduce the risk of falling victim to such fraudulent schemes:
- Be skeptical: Develop a healthy skepticism towards unsolicited emails, especially those requesting personal information or urging immediate action. Verify the authenticity of the email by double-checking the sender's email address and looking for any signs of suspicious or unprofessional content.
- Confirm legitimacy: If you receive an email claiming to be from a reputable organization like GoDaddy, independently verify its legitimacy by contacting the company directly through official channels. Do not use the contact details provided in the suspicious email.
- Update compromised credentials: If you have already fallen victim to the GoDaddy email scam or any similar phishing attempt, immediately change the login credentials of potentially compromised accounts. This step ensures that scammers no longer have unauthorized access to your information.
- Seek official support: Reach out to the official support channels of the platforms or services associated with your compromised email account. Report the incident and follow their guidance on securing your account and mitigating any potential risks.
- Recognize phishing red flags: Educate yourself about common characteristics of phishing emails, such as generic greetings, grammatical errors, urgent language, or requests for sensitive information. By spotting these red flags, you can better protect yourself from falling prey to such scams.
- Maintain security software: Install and regularly update reputable antivirus or anti-spyware software on your devices. These tools can help detect and prevent malware infections, including those distributed through email scams.
From our report of Jun 2023 · outdated details corrected in October 2026
Check your system for malware
If you suspect that you opened an infected attachment in an email, you should take action.
Crooks frequently disguise their malicious programs as "useful" tools in order to make them more difficult to detect for the average user. People also frequently fail to delete all related files and entries, which can result in the reinfection of an infection. Because the program could have any name or icon, this step is best performed by anti-malware software.
However, if manual removal is what you prefer, we have instructions for Windows and Mac machines:
To fully remove an unwanted app, you need to access Application Support, LaunchAgents, and LaunchDaemons folders and delete relevant files:
- Enter Control Panel into Windows search box and hit Enter or click on the search result.
- Under Programs, select Uninstall a program.
- From the list, find the entry of the suspicious program.
- Right-click on the application and select Uninstall.
- If User Account Control shows up, click Yes.
- Wait till uninstallation process is complete and click OK.
- Click on Windows Start > Settings > Apps > Apps & features to uninstall programs.
- In Control Panel, select Programs > Uninstall a program.
- Pick the unwanted application by clicking on it once.
- At the top, click Uninstall/Change.
- In the confirmation prompt, pick Yes.
- Click OK once the removal process is finished.
- From the menu bar, select Go > Applications.
- In the Applications folder, look for all related entries.
- Click on the app and drag it to Trash (or right-click and pick Move to Trash)
- Select Go > Go to Folder.
- Enter /Library/Application Support and click Go or press Enter.
- In the Application Support folder, look for any dubious entries and then delete them.
- Now enter /Library/LaunchAgents and /Library/LaunchDaemons folders the same way and terminate all the related .plist files.
From our report of Jun 2023 · not reviewed since
Clear cookies and cache
Performance, stability, and usability issues are significant concerns when it comes to email scams and browser security.
The repercussions of falling victim to email scams can be far-reaching, sometimes leading to malware infections that wreak havoc on your computer. These infections can cause a range of problems, including altering the Windows registry database, damaging crucial bootup and system sections, deleting or corrupting DLL files, and more.
Once malware damages a system file, traditional antivirus software may not be sufficient to repair it. This is where comes into play. It is specifically designed to address the damage caused by malware infections, offering solutions to various issues that can render your computer unusable. From Blue Screen errors and freezes to registry errors and damaged DLLs, it can help restore your system's functionality.
Another common concern is the accumulation of cookies and cache files. These files not only occupy valuable disk space but can also pose security risks, potentially allowing unauthorized access to your personal information. takes browser security seriously by automatically clearing cookies and cache, reducing the risk of data breaches, and enhancing your online privacy.
From our report of Jun 2023 · not reviewed since
Consequences of falling victim to the scam
When unsuspecting individuals fall victim to the GoDaddy email scam, they face a number of potentially serious consequences.
Victims unknowingly give scammers access to their email accounts by entering their login credentials on the phishing website. Because of this unauthorized access, scammers can exploit the hijacked accounts in a variety of harmful ways.
One significant concern stems from the fact that email accounts are frequently linked to multiple platforms and services. Scammers with access to a victim's email account can pose as the legitimate owner and deceive contacts, friends, or followers into providing loans or financial assistance via communication platforms such as emails, social networks, or messaging apps.
Scammers can also use compromised email accounts to distribute malware. They can infect other users' devices and spread malicious software by sharing infectious files or links. Furthermore, financial accounts associated with the compromised email address, such as banking, online money transfer services, digital wallets, or e-commerce platforms, can be used to conduct fraudulent transactions and make unauthorized online purchases.
In conclusion, trusting the deceptive "GoDaddy" scam emails can expose users to serious privacy violations, financial losses, and even identity theft. Individuals must exercise caution and remain vigilant against such scams.
What to do after the GoDaddy email scam e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you typed a password on the page the GoDaddy email scam message opened, assume the sender has it. Go to the real site by typing its address yourself and change the password there, choosing one you have never used.
Change it anywhere else the same password was used, and sign out all other sessions if the service offers it. Any browser on Windows 11 or Windows 10 will do, as long as you do not follow the e-mail's link.
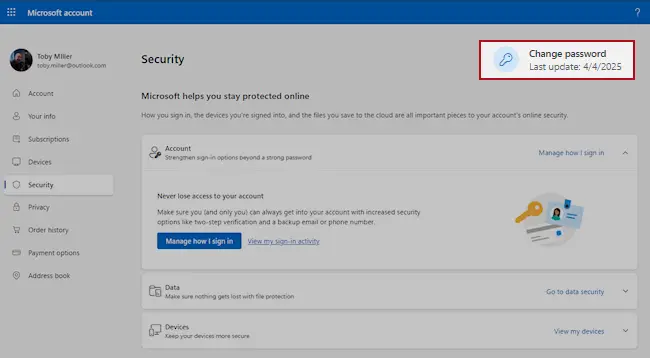
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
With two-step verification on, a stolen password alone no longer opens the account, because a sign-in from a new device also needs a code from your phone.
Switch it on for the e-mail account first, then for banking, shopping and social accounts that use that address.
Check the recovery phone, the recovery e-mail and any forwarding rules while you are in the settings, since attackers change them to come back. The pages are the same on Windows 11 and Windows 10.
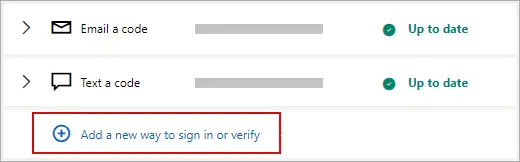
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Do not reply and do not click anything else in the message. In Outlook select the e-mail and choose Report > Report phishing; in Gmail open the three-dot menu next to Reply and pick Report phishing.
That trains the filter for everyone on the service, and the message goes to the junk folder. If the e-mail came to a work address, forward it to your IT team as an attachment first.
The steps are the same in the web mail and the mail apps on Windows 11 and Windows 10.
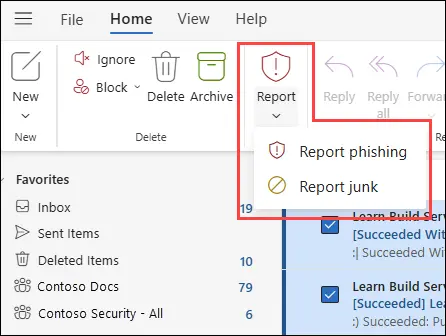
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A fake sign-in page only steals what you type, so most readers can skip this step. If the GoDaddy email scam e-mail made you download or open a file, delete it and scan the PC.
In Windows Security > Virus & threat protection > Scan options, run a Full scan and then Microsoft Defender Antivirus (offline scan) > Scan now. The offline scan restarts Windows 11 or Windows 10 and takes about 15 minutes.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about GoDaddy email scam
I opened the "Attention Dear User" e-mail. Am I hacked?
No. Opening and reading a phishing e-mail does not give anyone access to your account or your PC. Modern mail programs block scripts and remote content by default, so reading the message "Attention Dear User" only showed you text and pictures.
The danger comes from clicking the button and typing your password on the page it opens, or from opening an attached file. If you did neither, report the message as phishing and delete it.
If you clicked but closed the page without typing anything, there is also nothing to fix. If you did type a password, change it from another device and turn on two-step verification.
Can I trust the people at (480) 505-8821?
No. They may sound professional, know your Windows version and show you real system screens, but all of that is part of a sales script. The aim of the people behind (480) 505-8821 is to get remote access to your PC and money from you, sometimes repeatedly through "refund" tricks.
Anything they found was invented or normal, such as warnings in Event Viewer that every Windows PC has. Hang up, do not let them connect and do not pay. If you have already done so, disconnect the PC from the internet and work through the steps for callers in this guide.
I typed my password after "Attention Dear User". What now?
Act within the hour. From another device, open the real site of the account the message "Attention Dear User" imitated and change the password. If the same password is used anywhere else, change it there too.
Sign out of all other sessions, check the recovery e-mail and phone number, and look for mail forwarding rules or filters you did not create. Then turn on two-step verification with an authenticator app or a passkey.
If the fake page also asked for a card number or a bank login, call your bank and ask them to block the card. Finally, report the e-mail so others are warned.
They called me back from (480) 505-8821 offering a refund. Is it real?
No. The refund call is a second scam by the same people. They say they will return your money, ask you to log in to online banking while they are connected, then claim they sent too much and ask you to send the difference back, by transfer or gift cards.
In reality they moved your own money between your accounts or edited the page. Hang up on any call from (480) 505-8821 or anyone who mentions your earlier repair.
If you want a refund, ask your bank or card issuer directly. If they had remote access, remove their tool and change your passwords from another device.
Could GoDaddy email scam be a genuine message?
We checked it, and it is not. Microsoft is only the costume. The message exists to get your password, and real companies handle that inside your account, after you sign in normally, not through links, attachments or phone numbers in a message you did not expect.
Scammers copy logos and footers perfectly, so the design proves nothing. The sender address, the link target and the request are the reliable signs, and all three point to a scam here. Delete it, and if you are worried, check your account directly.
Who answers (480) 505-8821?
Not the company named in the message. (480) 505-8821 leads to a call centre that runs GoDaddy email scam, often far from the country it claims to be in. The agents follow a script: they confirm a charge you never made, then offer a refund that requires remote access to your PC.
Scammers change numbers often and may also spoof caller ID when they call you back. If you want to talk to the real company, find its number on its official site or on your card or statement, never in the message.
Should I scan my PC after GoDaddy email scam?
Yes, it is a quick way to rule out one possible cause. Open Windows Security and run a full scan; it takes about half an hour. If it finds nothing and there are no unknown programs or extensions, the account problem behind an e-mail with the subject "Attention Dear User" most likely started with a leaked or phished password.
If it finds a stealer or trojan, remove it first, then change your passwords from another device, then sign out of all sessions, because stolen cookies keep working until you do.
Why did I receive GoDaddy email scam?
Scam messages go to millions of addresses and numbers collected from data breaches, public websites and simple guessing. Receiving GoDaddy email scam does not mean your PC is infected or that an account of yours was hacked.
If the message includes an old password of yours, it comes from a breach of some website; change that password wherever you still use it. Mark the message as spam or phishing so your provider blocks similar ones. Never reply to ask to be removed from the list: the sender treats a reply as proof that the address works.
Can I trick the scammers or waste their time?
Better not. Replying to GoDaddy email scam confirms that your address or number is live and puts it on lists that sell for more. Scammers who are teased sometimes switch to harassment or try to use any detail you reveal, such as your name, employer or location.
Playing along also risks a slip, like opening a link or a file they send. Report the message, block the sender and delete it. Your report does more damage to the operation than a conversation would.
Will Fortect remove GoDaddy email scam?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For GoDaddy email scam, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia, the free encyclopedia: Phishing (read October 5, 2026)
- Malwarebytes: Malware (read October 5, 2026)
- Nerdwallet: Identity Theft: What It Is, How to Prevent It, Warning Signs and Tips (read October 5, 2026)
- FTC: How to recognize and avoid phishing scams (read October 5, 2026)
- CISA: Recognize and report phishing (read October 5, 2026)