
NTAppHelper on Mac: what it is and how to remove it
NTAppHelper is a LaunchAgent element related to the Tracker Package app installed on your Mac. When this potentially unwanted program (PUP) is on your device, it may change your homepage and new tab address to search. searchtp. com, trackerpackage1tab. com, or another suspicious URL - these are very common symptoms of a browser hijacking, which can occur on Safari, Google Chrome, or another web browser.
Facts checked October 7, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with NTAppHelper.
Do it yourself · free Remove NTAppHelper yourself 7 steps, about 21 minutes, no software needed.
Start the steps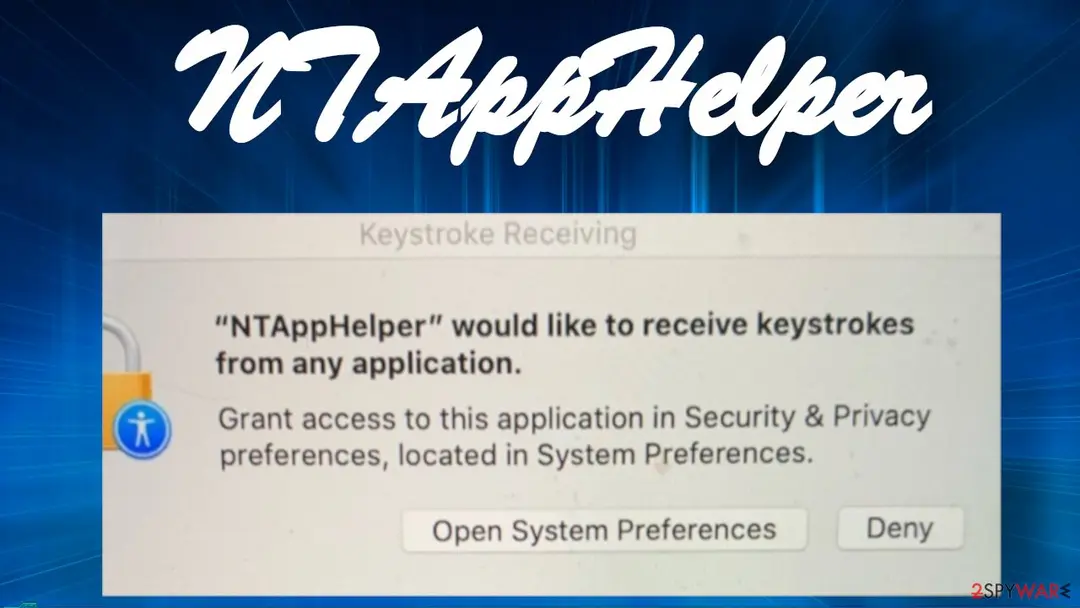
NTAppHelper: summary
| Distribution | Software bundles, deceptive ads |
|---|---|
| Damage | Shady search sites are capable of recording your browsing-related data and inject ads into search results. Keyloggers can lead to financial losses, privacy issues, identity theft |
| name | NTAppHelper |
| Type | PUP, keylogger, Mac virus |
| Associated app | Tracker Package |
| Promoted fake search site | search.searchtp.com (may vary) |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Symptoms | An unknown website opens each time you log in to your Mac, slower device performance, error messages |
|---|---|
| Detection names | No Microsoft detection name is known |
| Name | NTAppHelper |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 22 March 2021 |
| Facts checked | 7 October 2026 |
What NTAppHelper does
From our report of Mar 2021 · not reviewed since
NTAppHelper – a Mac virus with plenty of of malicious features
NTAppHelper is a LaunchAgent element related to the Tracker Package app installed on your Mac.
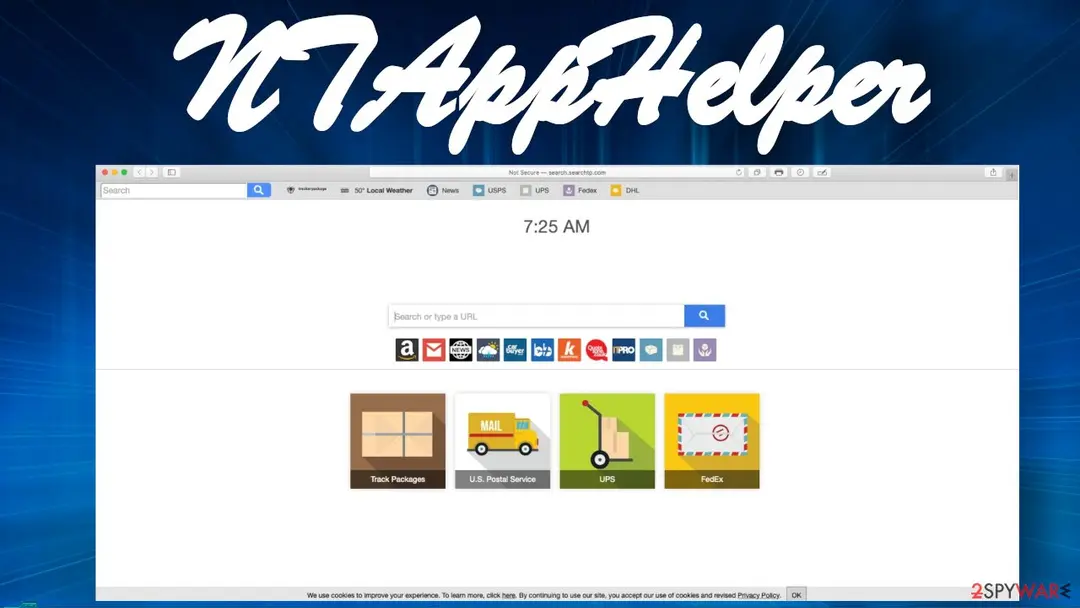
When this potentially unwanted program (PUP) is on your device, it may change your homepage and new tab address to search.searchtp.com, trackerpackage1tab.com, or another suspicious URL - these are very common symptoms of a browser hijacking, which can occur on Safari, Google Chrome, or another web browser.
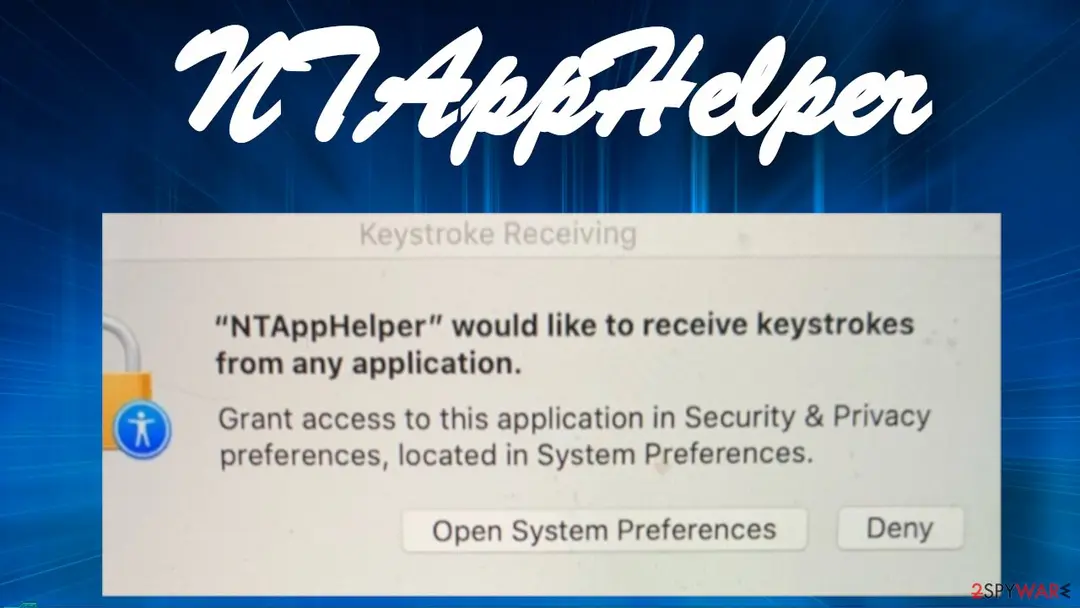
Moreover, users have reported about the NTAppHelper virus asking to grant it access to log keystrokes from any applications. You should never grant such privileges to any app of such type as it could record your private details, banking credentials, passwords, etc., and send this information to unknown parties (potentially, cybercriminals).
Cyber infections that try to steal your info through keystroke recording are called keyloggers and are extremely dangerous. Thus please don't download the Tracker Package virus as it can endanger both you and your device. If you already did, read this article to find out how to get rid of it and restore your system to a pre-contamination phase.
As we've mentioned before, the first thing that stands out when you have Tracker Package virus installed on your Mac is that each time you log in, a page with search.searchtp.com is displayed. It's a fake search site that redirects users to legitimate search engines like Yahoo, Bing, or others.
But by doing so, NTAppHelper can do two things - gather your browsing habits (search inquiries, IP addresses, geolocations, used apps, device/browser info, etc.) and show ads in search results. Advertisers use the collected data to customize ads specifically for you, making them irresistible.
While shown Tracker Package ads can redirect you to websites that you wouldn't normally visit. Usually, the deceptive ads have nothing in common with the sites you will be redirected to. Thus an ad for an amazing deal on a new TV might redirect you to pages with:
But that's just the tip of the iceberg. Users who had NTAppHelper installed on their Macs have reported a message that asked to grant access to receive keystrokes from any applications. The whole prompt read:
Allowing such privileges to NTAppHelper virus might pose a myriad of dangers to you. It could record all your login details for social media platforms, emails, banks, etc. This information could be used to empty your bank accounts or take over any of your accounts online.
Therefore you shouldn't wait for another second before scanning your Mac with dependable anti-malware software if you believe that this app is installed on it. You can remove NTAppHelper by downloading free apps like or and performing a full system scan.
You can also opt for the manual elimination steps we provide below, although keep in mind that it may not be as effective. In some cases, a browser reset can do the trick.
Then, cybersecurity experts from Uirusu.jp highly recommend using one more tool to finish NTAppHelper removal. It's the time-proven system optimizer that has been on the market for ages. This app will completely eliminate any traces of the infection from your Mac.
- gambling,
- malware,
- PUPs,
- porn,
- various scams, etc.
From our report of Mar 2021 · not reviewed since
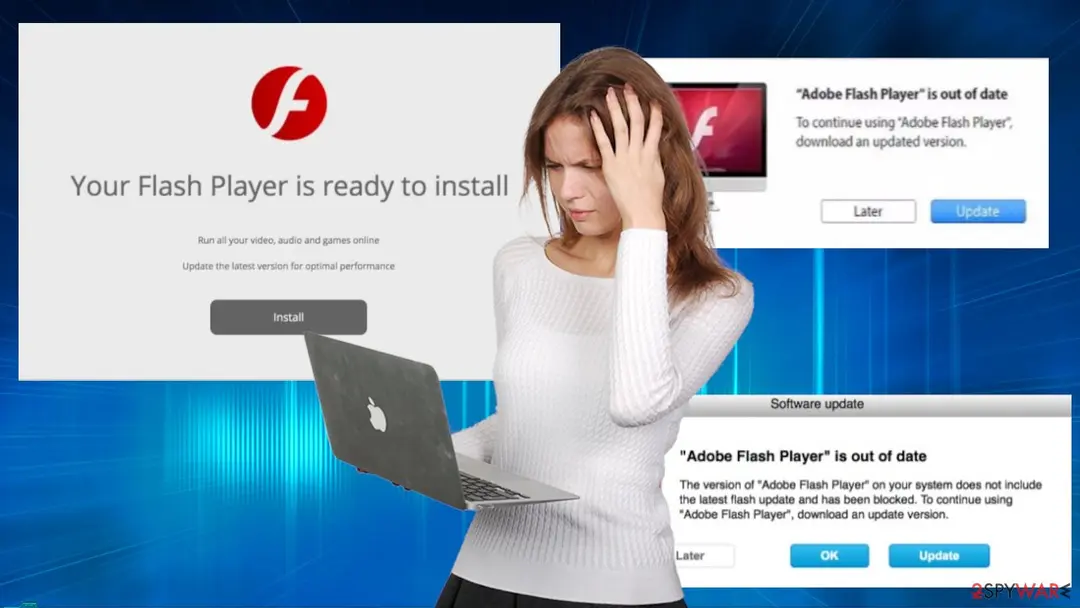
Please don't install Flash Player updates as the service is discontinued
For a long time, Macs were impenetrable, meaning there were very few potentially dangerous apps floating around the web that were targeting these platforms.
But since the brand got more and more popular, cybercriminals saw an opportunity to make some cash off of Apple device users. Although Mac viruses aren't as pervasive as those developed for Windows platforms, they can still pose dangers.
Thus Mac users should be careful while visiting shady websites, where most infections lurk. Our research has determined that a big part of Mac malware is traveling with fake Flash Player updates. Since that software is discontinued, all prompts suggesting that you need to update it are either PUPs or malware. Please don't ever click on any of such deceptive ads.
From our report of Mar 2021 · not reviewed since
More from our earlier report on NTAppHelper
- If you see any symptoms of an infection, scan your Mac with a trustworthy anti-malware tool immediately to remove it
- PUPs and viruses leave a lot of residual files and entries that AV tools can remove.
- Use the time-proven software to resolve any issues concerning your Mac
- Keystroke Receiving "NTAppHelper" would like to receive keystrokes from any applications.
- Grant access to this application in Security & Privacy preferences, located in System Preferences.
How to remove NTAppHelper
How to remove NTAppHelper from a Mac
Start with the passwords and crypto, from another device: a stealer copies them in seconds.
Then clean the Mac, or erase it.
Step 1: Change passwords from another device first
If you pasted a command into Terminal or opened a downloaded file from NTAppHelper, assume the passwords saved in the browsers and in Keychain on this Mac are known to the attacker.
From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and work accounts, and sign out of all other sessions on each one.
Move any cryptocurrency to a new wallet created on a clean device, because a seed phrase that was stored on this Mac is compromised. Do this before cleaning the Mac: cleaning does not undo the theft.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Step 3: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
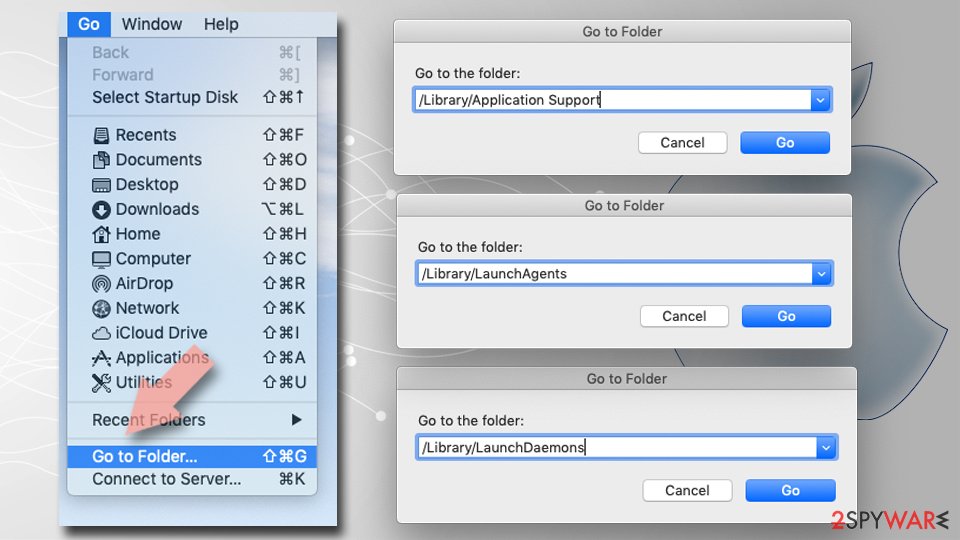
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 4: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from NTAppHelper or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 5: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 6: If it was an infostealer, erase and reinstall macOS
Stealers copy data and often leave persistence you cannot be sure you found.
The only complete fix is to back up your personal files only (documents, photos, not apps or settings), then open System Settings > General > Transfer or Reset > Erase All Content and Settings, or use macOS Recovery to erase the disk and reinstall macOS, as Apple describes in its support articles.
Restore only your files afterwards, and install apps again from their official sources.
Step 7: Report it and watch your accounts
Report the site and the command to the authorities in your country, and tell your bank if any card was saved in a browser or in Keychain.
Over the next weeks watch your e-mail, bank and exchange accounts for sign-ins and transfers you did not make. Keep the notes you made, such as the process names and the file dates, in case a bank or the police ask for them.
Full procedure with screenshots: Report a cyber attack or scam to the authorities
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
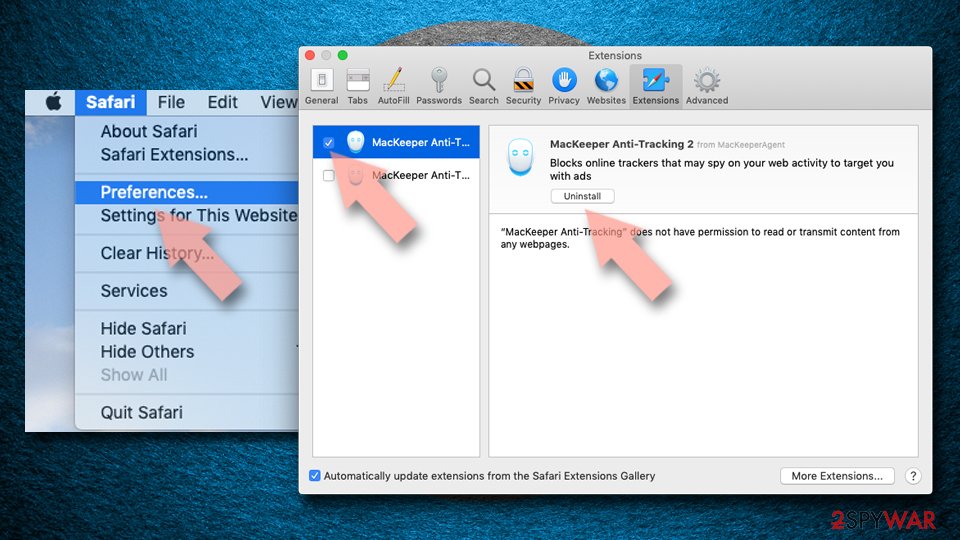
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
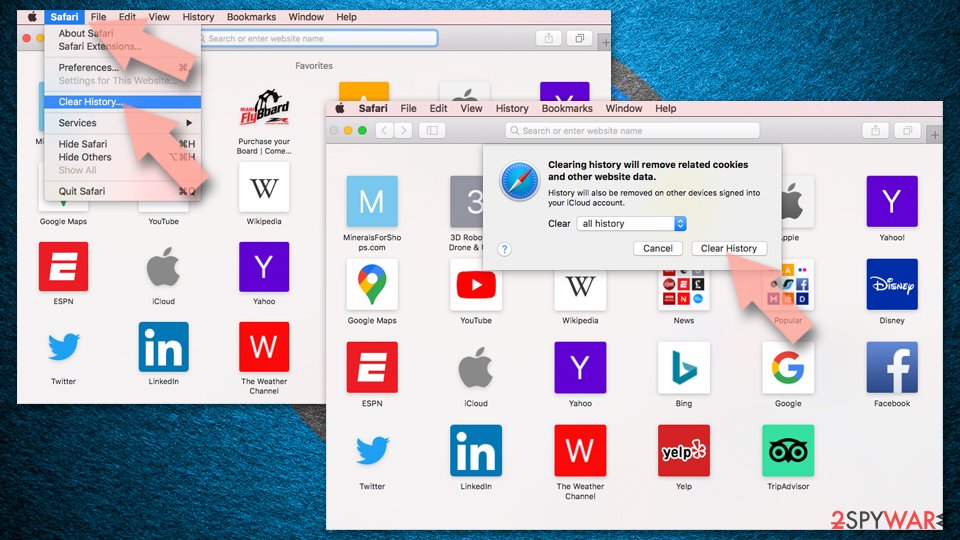
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
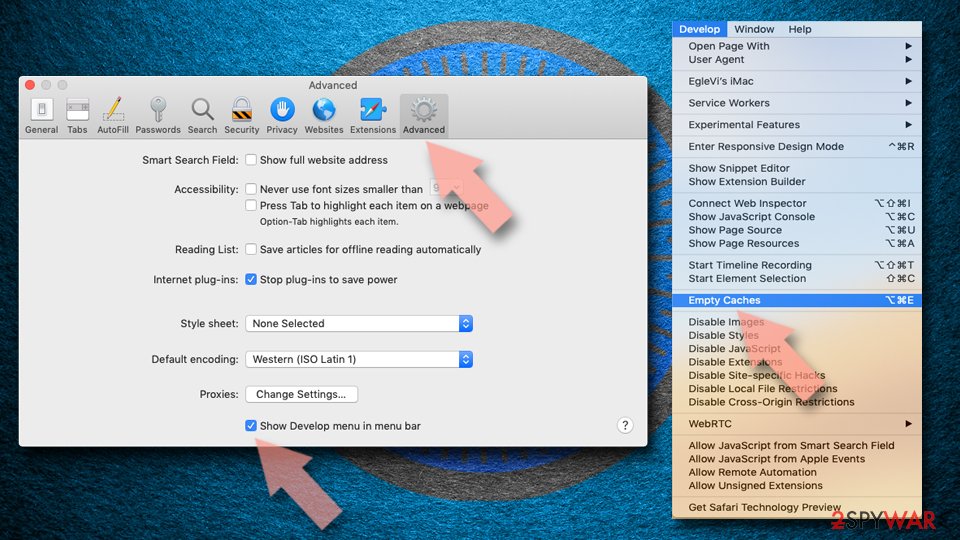
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
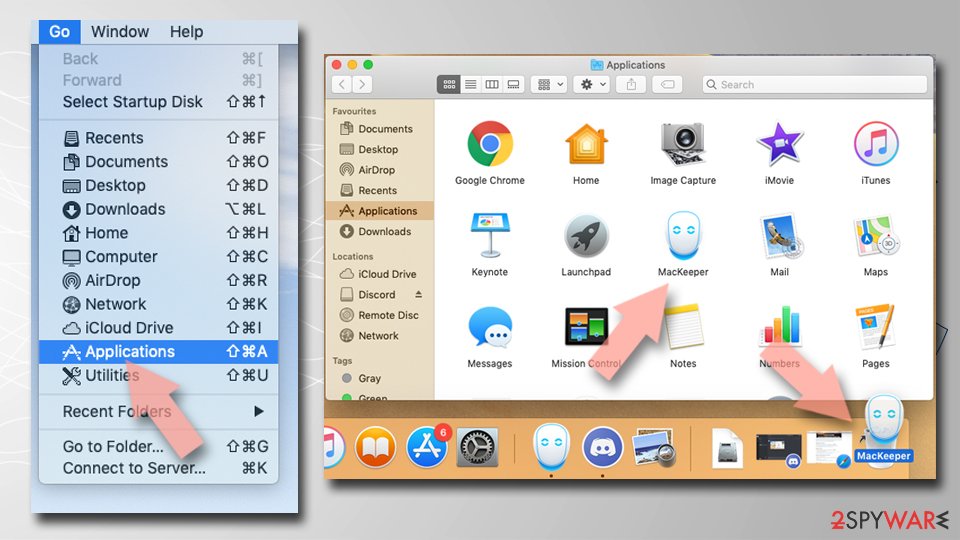
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of Mar 2021 · not reviewed since
Remove NTAppHelper virus by scanning your Mac with a reliable anti-malware tool
NTAppHelper virus is a malicious program with many hazardous functions, with keylogging being one of the harshest ones.
The app responsible for this virus is the Tracker Package, which is falsely advertised as a useful tool that will make package tracking easier.
Trustworthy anti-malware software is a must these days, even for Mac users. A proper security tool will prevent you from visiting dangerous websites, block malware, and will also be needed to remove NTAppHelper. All you have to do is perform a full system scan and let the AV tool do the rest.
To finish NTAppHelper removal, you must clear the web browser which settings were changed by the unwanted apps.
Questions about NTAppHelper
Is NTAppHelper a virus?
Most programs that appear the way NTAppHelper did are not viruses in the strict sense. They are potentially unwanted programs:
- real software that arrives bundled with other downloads and then shows offers
- changes browser settings
- starts with Windows
Some are harmless, some are annoying and a few carry adware. What makes it worth removing is that you did not choose it.
Uninstall it from Installed apps and check the startup list and the browsers for anything added the same day. If it refuses to uninstall or returns after a restart, treat it as more serious and run a Microsoft Defender offline scan.
NTAppHelper came back after I uninstalled it. Why?
Something else is reinstalling it. Common causes are a second program from the same publisher, a scheduled task that downloads it again, or a browser extension that keeps prompting for it. Sort Installed apps by install date and uninstall each entry from the same day that you did not choose.
Then open Task Scheduler and look in the Task Scheduler Library for tasks with updater-style names that you do not recognise. Check Startup apps in Task Manager too. If NTAppHelper still returns, start Windows in Safe Mode, uninstall it there and run a Microsoft Defender offline scan, which looks for loaders that ordinary scans can miss.
I have two-step verification. Am I protected?
Partly. Two-step verification stops an attacker who has only your password. But stealers also take session cookies, which represent a login that already passed the second step.
With a cookie, an attacker can open the account until the session expires or you sign out of all devices. So, after an infection, end all sessions as well as changing passwords.
Passkeys and hardware security keys resist phishing better, but a stolen session still needs to be ended. Review trusted devices and remove any you do not recognise.
Why is there no analysis of NTAppHelper?
Because nobody has shared a sample yet. Reports start with what victims see, here NTAppHelper in the list of installed apps; analysis follows only when the file that caused it reaches researchers.
Many stealers also delete themselves after sending the data, which leaves little to analyse on the PC. This guide therefore sticks to what is safe for every case:
- secure the accounts
- clean the PC
- remove the likely source
If you find the file you ran before this started, do not open it again; keep it for a scan.
Do I need to reinstall Windows to get rid of NTAppHelper?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see NTAppHelper in the list of installed apps again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Can I get back what NTAppHelper took?
Accounts, usually yes; money, sometimes. Most services restore an account through their recovery process if you act quickly and still control the e-mail address. Card payments can often be disputed with the bank.
Crypto sent after NTAppHelper in the list of installed apps is much harder, because transactions cannot be reversed; report it to the exchange the funds went to and to the police, with the wallet addresses and times. Do not answer offers from "recovery services" that contact you; they are a common second scam aimed at people who just lost funds.
Can I change my passwords on the infected PC?
Not while the spyware may still be running. A keylogger or stealer would capture the new passwords too. Use a phone or another computer that was never infected, or wait until the Microsoft Defender offline scan on this PC comes back clean.
Start with your main e-mail account, because it can reset every other password, then banking and payment accounts. When you return to this PC, sign in to the browser again only after the scans are clean and you have ended old sessions.
Nothing has happened yet. Do I still need to change passwords?
Yes. Stolen logs are often sorted and sold before anyone uses them, so the quiet period can last weeks.
The criminals look for the most valuable accounts first, usually crypto, banking and e-mail, and may only reach yours later. Changing passwords and ending sessions now makes the copy worthless whenever it is used.
It takes an evening. Start with e-mail, then money, then everything else saved in the browser, and turn on two-step verification as you go. Watch for login alerts over the following months.
How can I tell if a keylogger is installed?
There are rarely visible signs. Check Installed apps and Startup apps for names you do not know, look in Task Manager's Details tab for processes with no description or publisher, and run a full and offline scan.
On a shared or work PC, also ask whether monitoring software was installed by IT or a family member. If you suspect a keylogger, use another device for logins until the PC is checked. Hardware keyloggers, small plugs between a desktop keyboard and the PC, also exist.
Will Fortect remove NTAppHelper?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For NTAppHelper, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- Wikipedia: Potentially unwanted program (read October 7, 2026)
- Cso: What is a keylogger? How attackers can monitor everything you type (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)