
Nedbank Data Breach: 2026 Update, Scams and 0860 775 775
- Nedbank data breach in 2026: the short answer
- Timeline: from the contractor leak to 2025 scam warnings
- What changed since 2020
- Scams that reuse leaked Nedbank data
- Steps to protect your Nedbank account
- What is still unknown
- Our original 2020 report
- Software vulnerability at Computer Facilities is to blame
- In the wake of a data breach, Nedbank asks customers to be vigilant
- Related guides on 2-Spyware
Nedbank data breach in 2026: the short answer
The Nedbank data breach is an old incident, but its data still matters. In February 2020 Nedbank disclosed that its marketing contractor Computer Facilities (Pty) Ltd had a security issue that exposed data of about 1.7 million past and current clients, 1.1 million of them active.[6] Names, ID numbers, phone numbers and addresses were in the subset at risk.[1]
We found no later Nedbank statement that changes this picture as of 2026. What changed is the scam side. Nedbank now keeps a page of current scams and a 24/7 fraud line, and in 2025 it warned about fraudsters who pose as its own fraud department.[7][8] Leaked ID and phone data makes such calls more convincing.
| Question | Answer |
|---|---|
| Where the leak happened | Computer Facilities (Pty) Ltd, a contractor for SMS and email marketing[6] |
| When it was disclosed | February 2020[6] |
| Clients affected | About 1.7 million, of which 1.1 million active[6] |
| Data at risk | Names, ID numbers, phone numbers, physical and email addresses[1] |
| Accounts or passwords | Not affected, according to Nedbank[1] |
| Fraud line today | 0800 110 929, available 24/7[8] |
Timeline: from the contractor leak to 2025 scam warnings
| Date | Event |
|---|---|
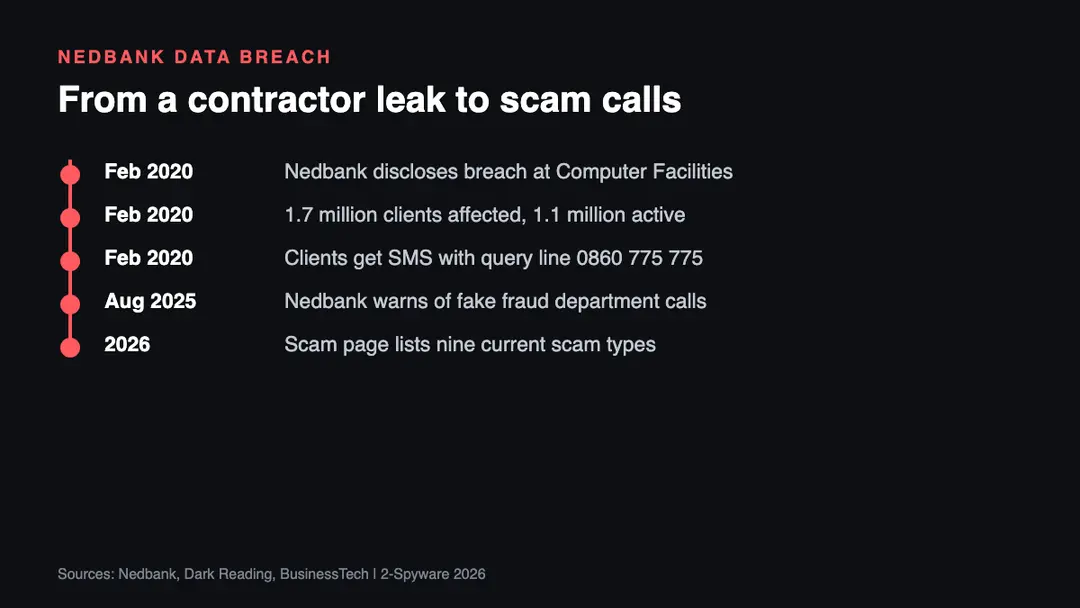
| February 2020 | Nedbank discloses a data security issue at Computer Facilities (Pty) Ltd[6] |
| February 2020 | Contractor systems are taken off the internet and Nedbank client data is destroyed[6] |
| February 2020 | Affected clients receive an SMS listing 0860 775 775 and DataProtection@Nedbank.co.za[3] |
| August 29, 2025 | BusinessTech reports a Nedbank warning about fraudsters posing as its fraud department[7] |
| 2026 | Nedbank's scam page lists client coaching, selfie, SIM swap and other scams[8] |
What changed since 2020
The breach itself is closed as far as public records show. Nedbank said it destroyed the client data held by the contractor and that the contractor took its systems off the internet.[6] We found no report of a second leak at Computer Facilities and no later court case about it. We also found no public fine linked to this incident.
The threat moved to the phone. In August 2025 Nedbank warned that criminals call clients while claiming to be from its fraud department. They say there is a suspicious debit order, and some register their numbers as "Nedbank Investigations" to look real.[7] They then ask clients to change Nedbank ID details, accept an Approve-it message or share an OTP.[7]
The bank's scam page now lists nine scam types, from SIM swap to parcel and SARS scams, and gives the fraud line 0800 110 929.[8] The 2020 query number 0860 775 775 was set up for breach questions. We could not confirm whether it still handles them in 2026, so use the numbers on Nedbank's website.
Scams that reuse leaked Nedbank data
Our analysis: leaked names, ID numbers and phone numbers do not open a bank account on their own, but they make a scam call sound believable. These are the patterns to watch for.
- Fake fraud department calls. A caller knows your name and ID number and says a large debit order is pending. Nedbank says its staff never ask you to change your login details.[7]
- Smishing. SMS messages with a link to a fake Nedbank sign-in page. Nedbank lists phishing and smishing among current scams.[8]
- SIM swap. Criminals move your number to a new SIM to catch OTPs. Nedbank lists SIM swap scams on its page.[8]
- Fake app downloads. A caller asks you to install an Android app that gives remote control. Nedbank warns about app download scams on Android.[8]
- Account number testing. Small test payments or fake verification requests that check whether an account is live. Treat any unexpected request to confirm account numbers as suspicious.
Steps to protect your Nedbank account
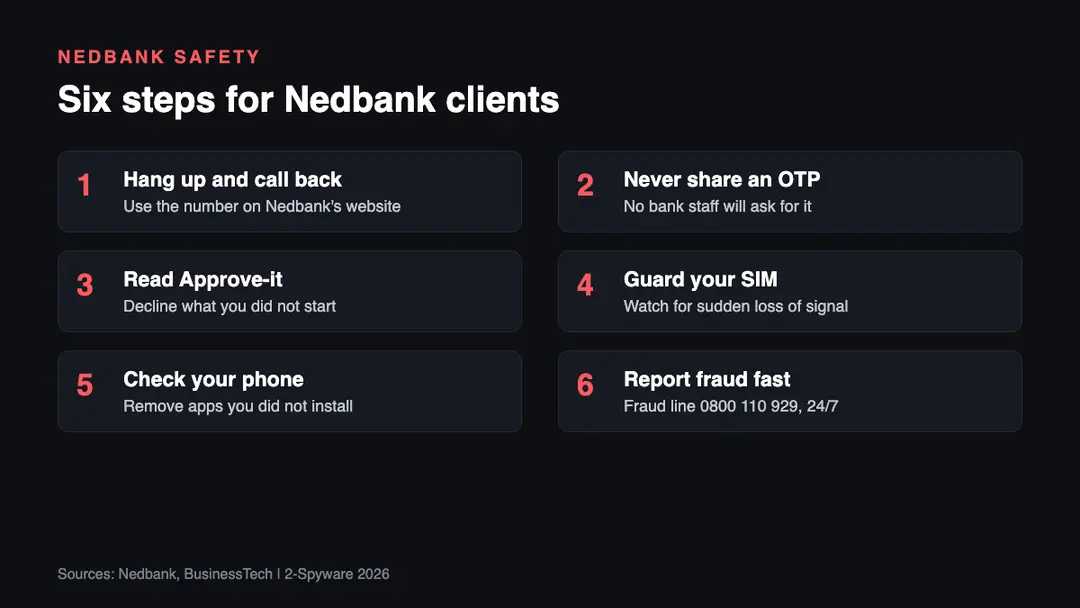
1. Hang up and call back. If someone calls as Nedbank, end the call and dial the number from Nedbank's website yourself. Caller ID can be faked, which is why banks warn against trusting it.[7]
2. Never share an OTP. Nedbank says you should never share a one-time PIN, and its staff would never ask you to change your Nedbank ID details.[7]
3. Read every Approve-it message. Check the amount and the action before you accept. Decline anything you did not start yourself.[7]
4. Guard your SIM. If your phone suddenly loses signal for no reason, call your network and the bank. SIM swap is on Nedbank's list of current scams.[8]
5. Check your phone. Remove apps you did not install on purpose, mainly remote access tools. Scan the device with a trusted security app. You can also check whether your email appeared in a leak with our leak check.
6. Report fraud fast. Call Nedbank's fraud line on 0800 110 929, which the bank says is available 24/7.[8] Forward fake messages and report phishing pages, as our guide on reporting phishing explains.
What is still unknown
- How the attackers got into Computer Facilities. We found no published forensic report.
- Whether the leaked 2020 data was later sold or published. We found no public record of it.
- Whether the 0860 775 775 breach query line still works as of 2026.
Our original 2020 report
The text below is our report as first published in 2020. We keep it unchanged for the record; the sections above bring it up to date.
Nedbank, one of the largest financial institutions in South Africa, has announced a data breach on Thursday.[1] In the publicly published warning to the customers, the bank informed that its third-party service provider Computer Facilities (Pty) Ltd disclosed personal data of 1.7 million customers due to security issues on its system.
The marketing company Computer Facilities was used by Nedbank for promotional campaigns as well as SMS and email-based communications with clients. Because the third-party did not have any connections to systems employed at Nedbank, no sensitive information, such as login credentials or pins/passwords, were compromised.
Nedbank warns users that the following data might have been compromised by unknown attackers:
A subset of the potentially compromised data at Computer Facilities included personal information (names, ID numbers, telephone numbers, physical and/or email addresses) of some Nedbank clients.
No Nedbank systems or client bank accounts have been compromised in any manner whatsoever or are at risk as a result of this data issue at Computer Facilities (Pty) Ltd.
Nedbank Group is one of the biggest insurance, asset management, and wealth management financial institution which also runs its services in six other countries, including Lesotho, Malawi, Mozambique, Namibia, Swaziland, and Zimbabwe.[2]
Software vulnerability at Computer Facilities is to blame
Nedbank said that the data breach was discovered during a routine audit at Computer Facilities, which is a part of a continuous monitoring program. During a checkup, it was found that the service provider did not maintain the security of its systems correctly, as it was impacted by a vulnerability.
Computer Facilities was holding names, ID numbers, phone numbers, home addresses, and emails of 1.7 million bank's customers, 1.1 million of which were still active. Computer Facilities did not have access to Nedbank's systems, which prevented sensitive data leak.
As soon as the security hole was spotted by Nedbank representatives at Computer Facilities, all the information related to its customers was immediately contained and destroyed, as well as. As additional security and precautionary measure, all the machines were also disconnected from the internet "until further notice." Nedbank also instructed the third-party service provider to inform its clients about the data breach.
Besides containing customer information, the bank also began working with relevant law enforcement agencies, as Nedbank Group Chief Information Officer Fred Swanepoel explains:
Our team of IT specialists and external cyber security experts have been working continuously with them since we became aware of this matter. Clients' bank accounts have not been compromised in any manner whatsoever and clients have not suffered any financial loss. Nedbank remains vigilant in its efforts to contain cyber-crime
In the wake of a data breach, Nedbank asks customers to be vigilant
Upon discovery, Nedbank immediately started informing the impacted clients about the breach and sent out the following SMS:[3]
Dear Client, we regret that some of your personal information (name, ID, contacts) was potentially compromised at the premises of a third-party service provider we used for communications. We assure you your accounts & money are safe. Our systems, your passwords and pins were not affected in any way. Don't share passwords and pins. No action required from your, remain vigilant. Queries: 0860 775 775, DataProtection@Nedbank.co.za
According to Nedbank, it shares some non-sensitive but personal information with third-parties in order to provide adequate services to clients. However, the company is also responsible for the data that it shares, and, in case of any leaks like this one, they are obliged to act immediately. Currently, Netbank's IT specialists and third-party forensic experts are employed to investigate the incident, as it is yet unknown how precisely the attackers managed to breach Computer Facilities' servers via the vulnerability.
Luckily, this ordeal is nowhere near as bad as Capital One bank's breach,[4], but users should be aware that they might be targeted by scammers.[5] Nedbank also warns that customers might also receive a call from fraudsters that would pretend to be bank representatives, so it is extremely important to be vigilant and not provide any additional information via unsolicited calls or emails.
Related guides on 2-Spyware
Frequently asked questions
What was the Nedbank data breach?
It was a 2020 leak at Computer Facilities (Pty) Ltd, a marketing contractor that sent SMS and email messages for Nedbank. Data of about 1.7 million past and current clients was exposed, of which 1.1 million were active customers.{6} Names, ID numbers, phone numbers and addresses were in the subset at risk. Nedbank said its own systems and accounts were not affected.{1}
What is 0860 775 775?
It is the query number Nedbank listed in its 2020 breach SMS to affected clients, together with the address DataProtection@Nedbank.co.za.{3} The number appears in our original report below. To report fraud today, Nedbank's own scam page lists a separate fraud line, 0800 110 929, available 24/7.{8} Always dial numbers you find on the official site yourself.
Was my Nedbank account hacked in the breach?
No, according to the bank. Nedbank said no Nedbank systems or client bank accounts were compromised and that passwords and PINs were not affected.{1} The leaked data was contact and ID information. That kind of data is useful to scammers who call or text you while pretending to be the bank, so the risk is fraud through contact, not a direct account break-in.
What are the latest Nedbank scams?
Nedbank's scam page lists client coaching, selfie, Android app download, phishing and smishing, SARS, parcel, vishing, loan and SIM swap scams.{8} In August 2025 the bank also warned that fraudsters pose as its fraud department, sometimes with numbers saved as "Nedbank Investigations", and ask clients to change their Nedbank ID details or share an OTP.{7}
Why does my Nedbank credit card keep getting hacked?
Repeated card fraud usually means the card details or your login are still known to criminals, often through phishing, a fake call or a compromised device. Ask Nedbank to replace the card, check your phone for unknown apps, and never approve an Approve-it message or share an OTP you did not start yourself.{7}{8}
Does Nedbank ever ask for my password or OTP?
No. Nedbank says its staff would never ask you to change your Nedbank ID username and password, and that you should never share an OTP.{7} If a caller asks about a transaction, the bank advises you to answer only whether it is yours or not and to share nothing secret.
Log in to comment
No comments yet. Be the first.