
555.in.th redirect ads: what it is and how to remove it
555.in.th virus is a browser hijacker which started spreading around in 2014. Unfortunately, but it is still active and there is no chance it will stop hijacking computers in the nearest future.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Not sure what sends your browser to 555.in? An automatic scan looks at the usual sources for you.
Do it yourself · free Remove 555.in.th redirect ads yourself 3 steps, about 9 minutes, no software needed.
Start the steps
555.in.th redirect ads: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | 555.in.th redirect |
| Type | Ad redirect domain |
| Symptoms | Redirects to an unknown domain |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Evidence | One write-up by a security site; details still limited |
|---|---|
| Domains | 555.in |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 22 July 2016 |
| Facts checked | 6 October 2026 |
Is 555.in.th redirect ads dangerous?
From our report of Jul 2016 · not reviewed since
Why do I see 555.in.th on my browser?
555.in.th virus is a browser hijacker which started spreading around in 2014.
Unfortunately, but it is still active and there is no chance it will stop hijacking computers in the nearest future. If this potentially unwanted program has already showed up on Google Chrome, Mozilla Firefox, Safari or another web browser, you should stop using it because it mostly displays fake search results.
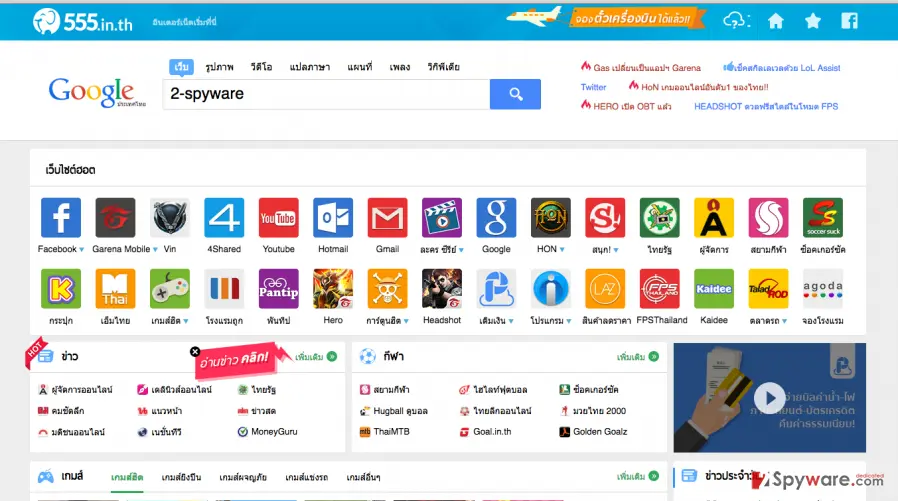
At first sight it may seem that it is very helpful and easy to use because it contains many links to popular websites that are divided into certain categories. It also displays temperature of the weather and allows to access Facebook, Instagram and Twitter with one click.
Unfortunately, you should keep in mind that such questionable search engines may display search results that are fill with third party links. At this point, you should realize that you may be redirected to a malicious websites which is filled with questionable and suspicious programs. To protect yourself from all possible infections, you should remove 555.in.th from your computer.
Redirects to hxxp://www.555.in.th/?tn=999_003 and similar URLs may start interrupting you out of nowhere because this hijacker spreads with the help of bundling. To prevent its infiltration, you must double-check every freeware before downloading it to your computer.
By saying that, we have in mind reading the Privacy Policy, End User's License Agreement and similar information provided to the user. Also, you should opt for Custom or Advanced installation option to get an ability to follow the installation process of the freeware and prevent optional downloads that are hidden in it.
Otherwise, you may let 555.in.th or any other browser hijacker start causing redirects to sponsored websites and similar activities. If you have already let this PUP attach your browsers, you should take care of its removal. For that you can rely on a guide that is given below or use .
From our report of Jul 2016 · not reviewed since
How can this virus hijack my browsers?
This doubtful website may start appearing on your browser (IE, Mozilla Firefox, Google Chrome) every time you start your browsing on the Internet.
If that happens, it means that your internet browsers have already been hijacked by 555.in.th virus. In order to find the source of this infiltration, you should check your recently installed programs. We say so because this dubious application usually travels around bundled with all kinds of freeware.
This distribution technique has been working without a trouble because many internet users fail to check if the programs that they are installing on their computers have hidden attachments or not. It is not a secret that most of the free software is filled with questionable attachments, such as plug-ins, add-ons, extensions and so on.
Check your browser and PC
- Address:
555.in
How to remove 555.in.th redirect ads
How to stop the 555.in.th redirect redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Step 1: Check the browser's extensions
Redirects to
555.inon sites that normally behave mean something in the browser is sending you there. In Chrome openchrome://extensions, in Edge edge://extensions, in Firefox the menu > Extensions and themes.Remove every extension you do not remember adding, especially new tab, search, coupon, PDF or video downloader add-ons. The extension pages look the same on Windows 11 and Windows 10.
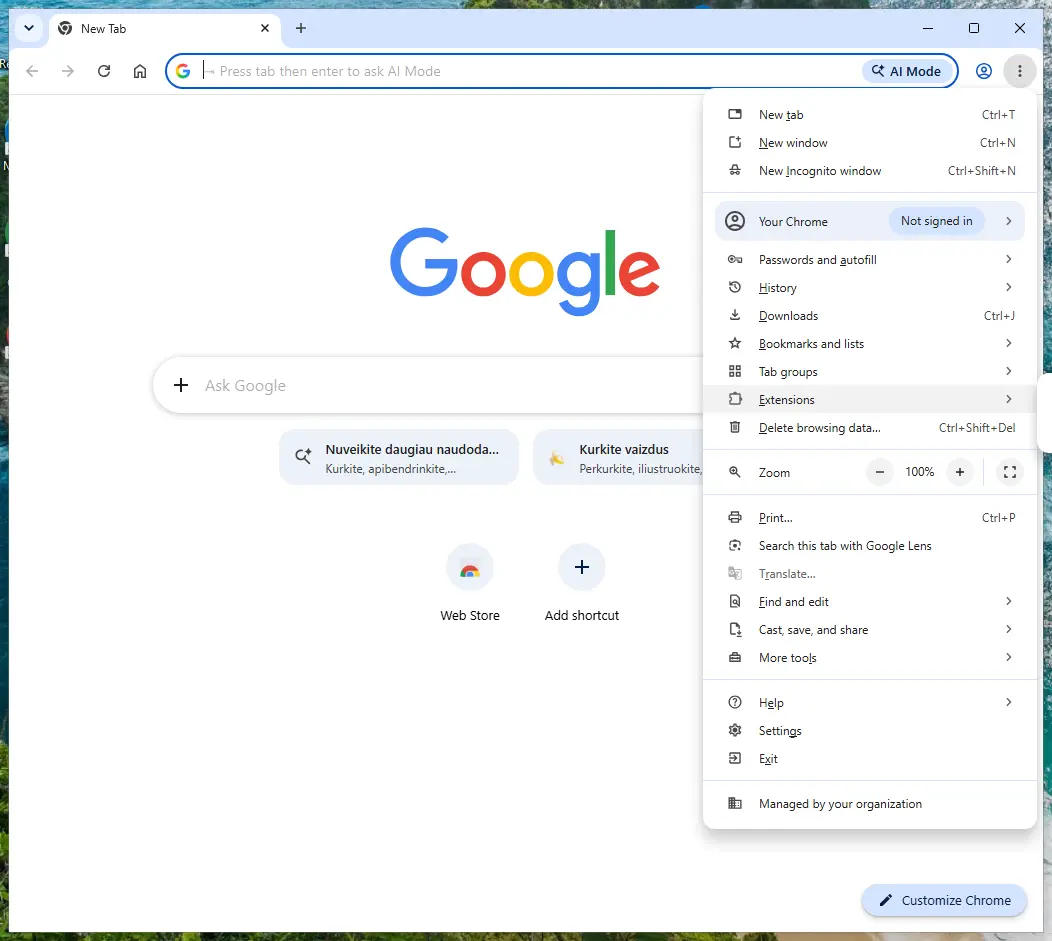
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Reset the browser if the redirects continue
If
555.instill opens after the extensions are gone, put the browser's settings back to their defaults. In Chrome open Settings > Reset settings > Restore settings to their original defaults; in Edge Settings > Reset settings; in Firefox Help > More troubleshooting information > Refresh Firefox.Tip: Bookmarks and saved passwords stay, while site permissions, the start page and the search engine are reset.
Redirects that survive a reset in every browser point to a program installed in Windows 11 or Windows 10, so uninstall anything you do not recognise in Settings > Apps > Installed apps.
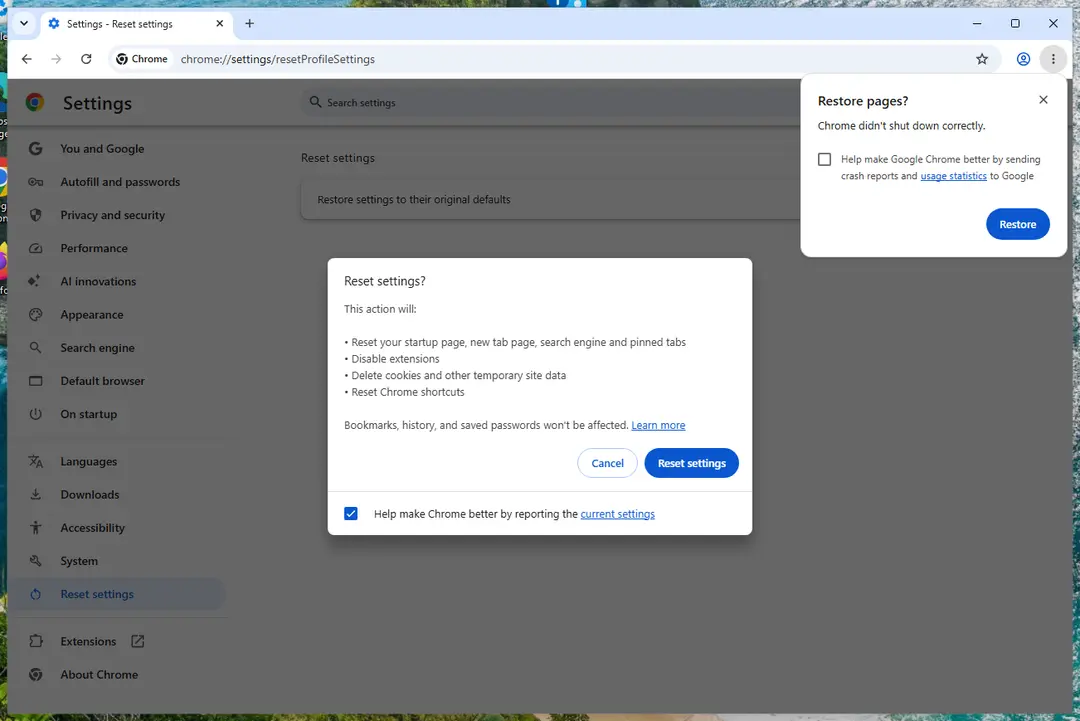
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Scan the PC if you downloaded anything from the ads
If you only saw the notifications and clicked nothing, you can stop before this step. If a notification led you to download or run something, delete that file, then scan Windows.
In Windows Security > Virus & threat protection > Scan options, run a Full scan, then choose Microsoft Defender Antivirus (offline scan) and Scan now. The offline scan restarts the PC and takes about 15 minutes on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
When trying to complete 555.in.th removal on your computer and forget about this browser hijacker, you must get rid of each of its components. In this case, check your Task Manager for these entries: 555.in.th, startgo123.com, worldsearchpro.com, searchnow360.com, etc.
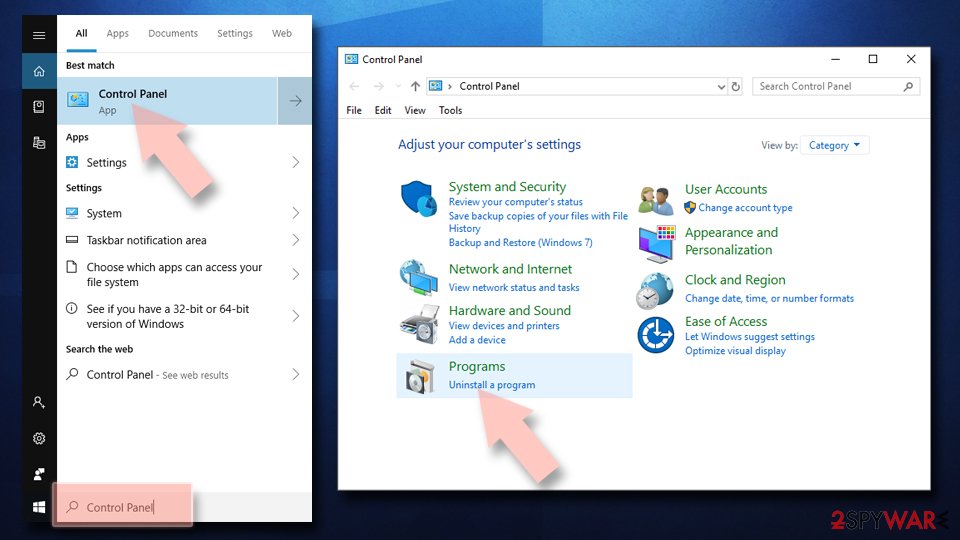
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
Uninstall from Windows 7/XP:
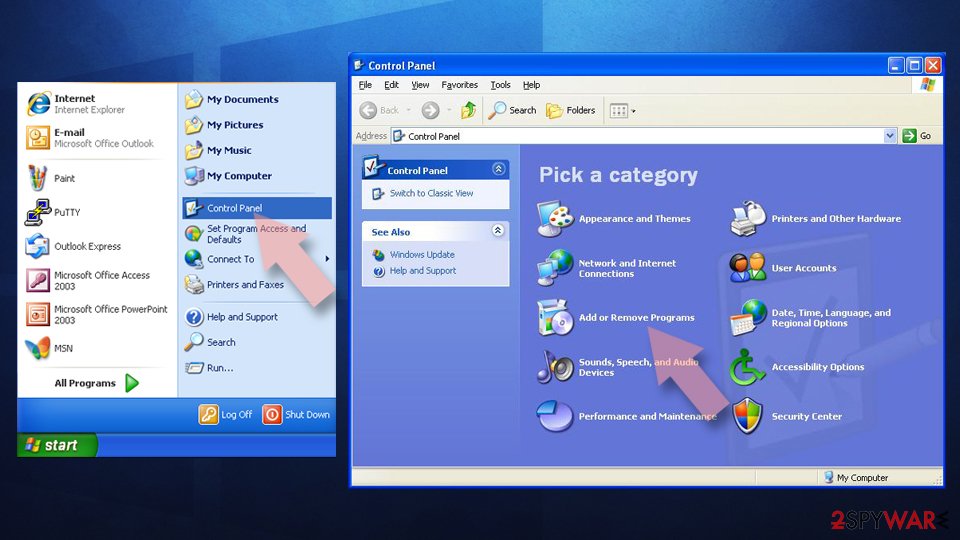
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
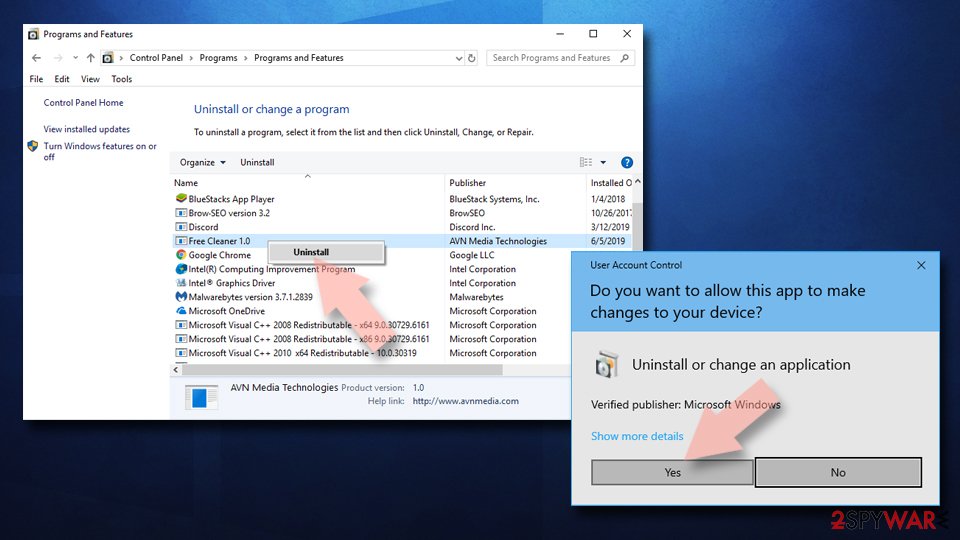
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
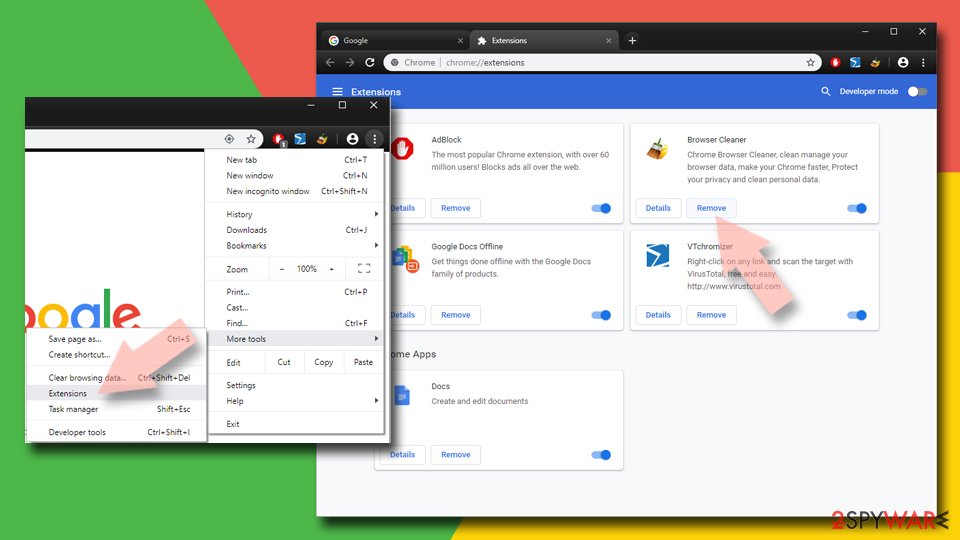
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
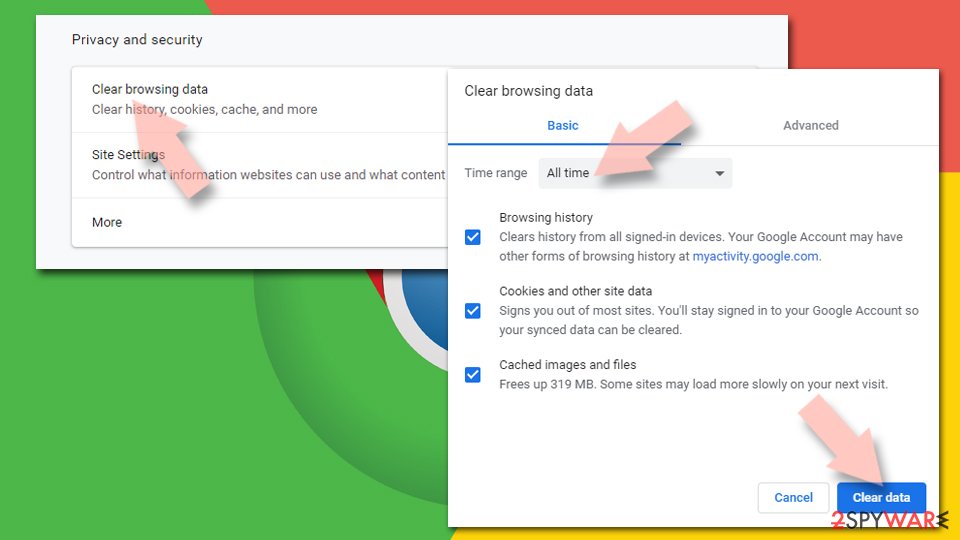
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
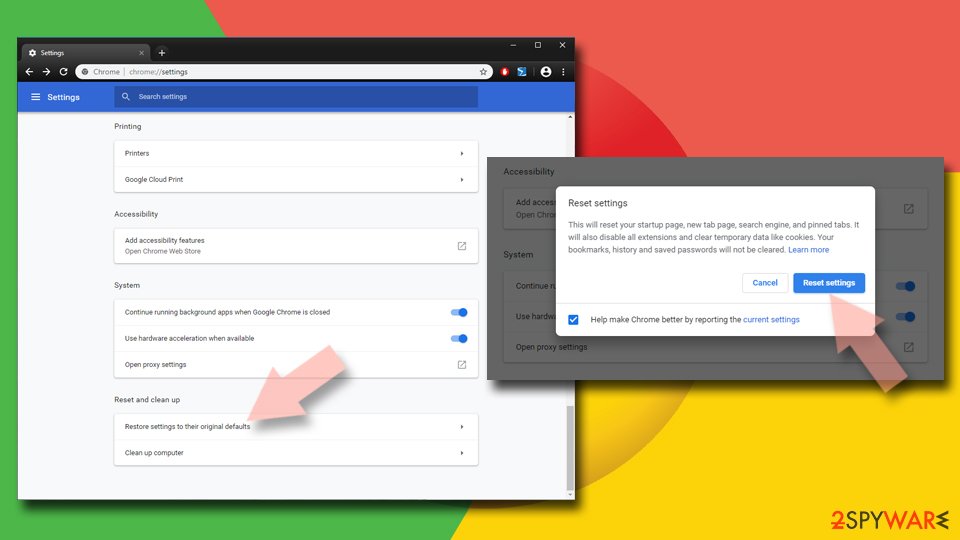
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Mozilla Firefox (FF)
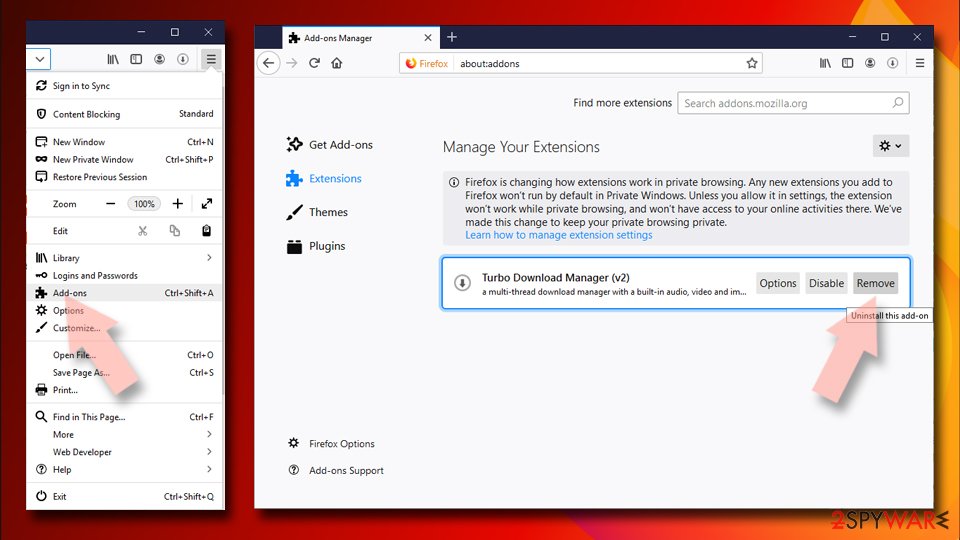
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
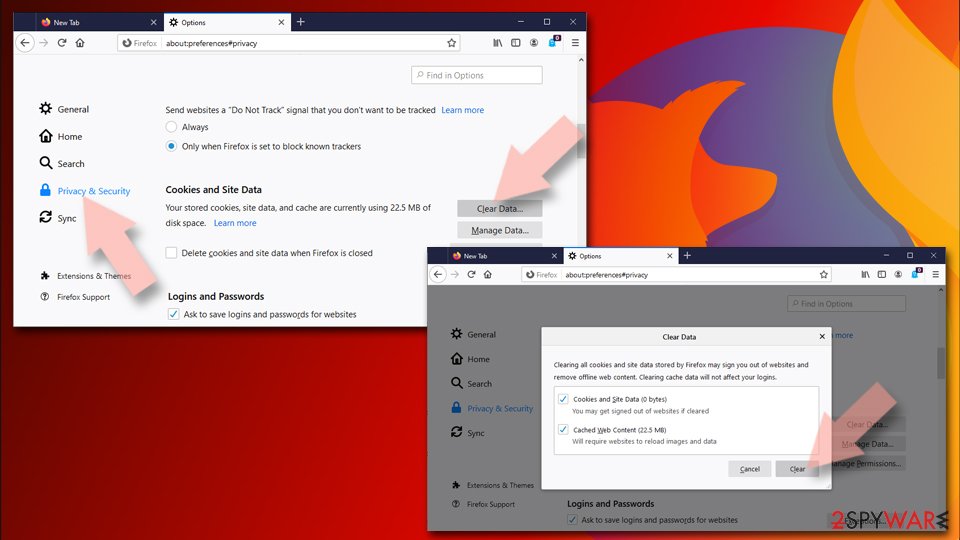
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
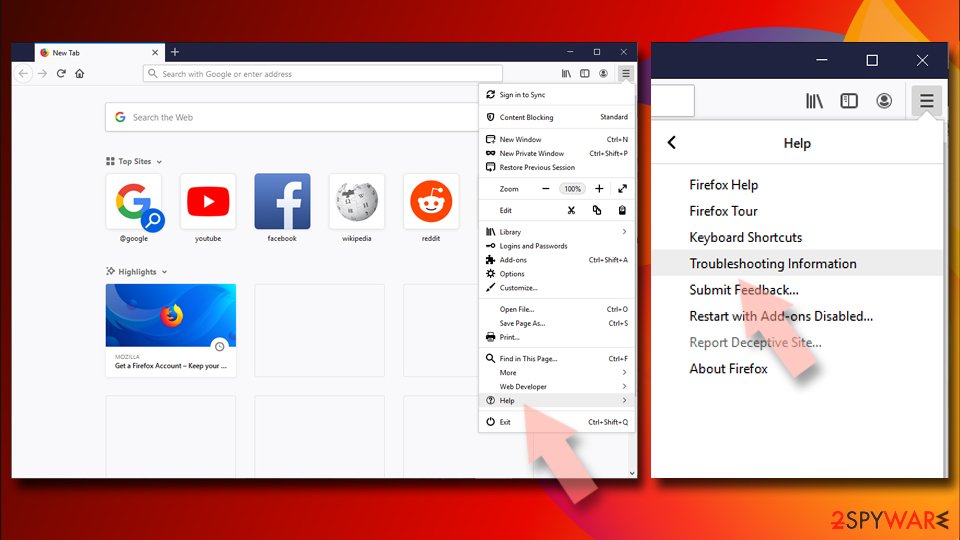
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
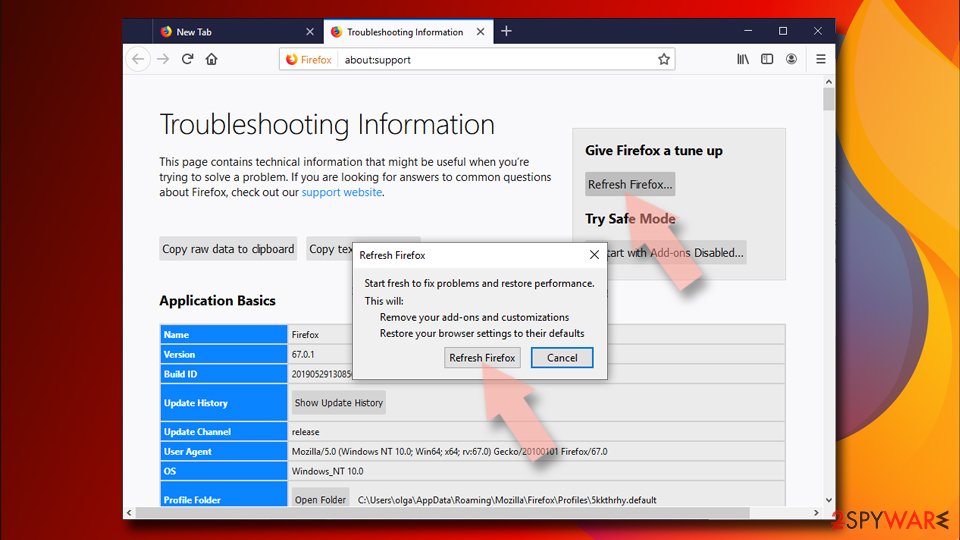
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
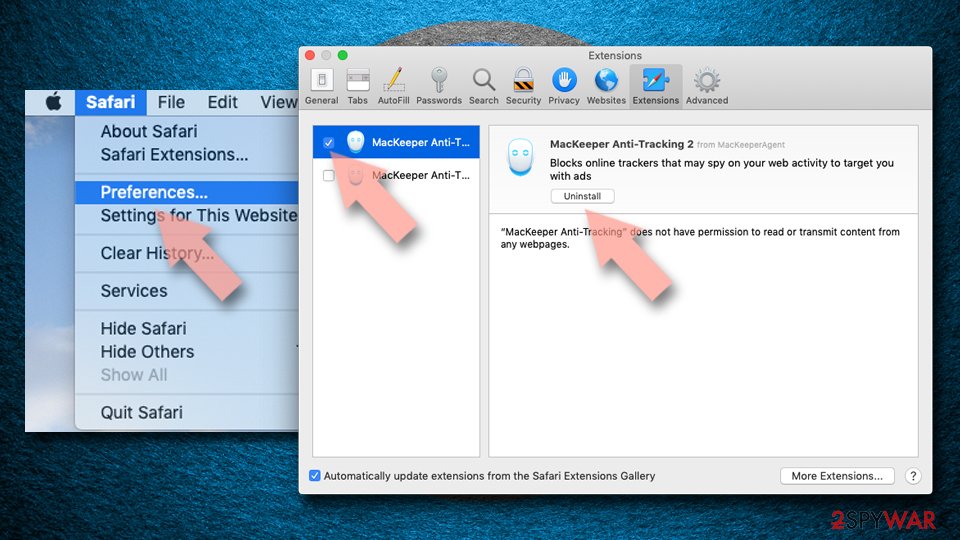
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
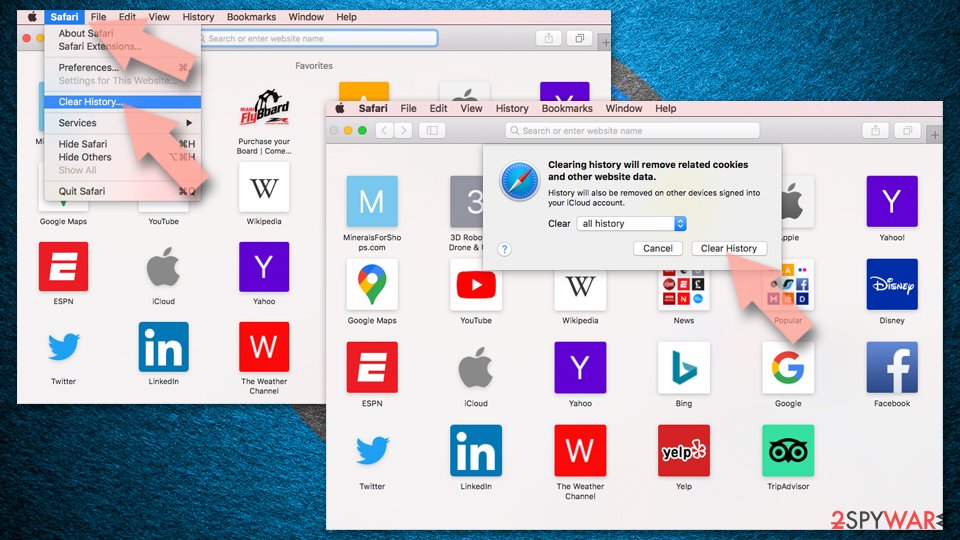
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
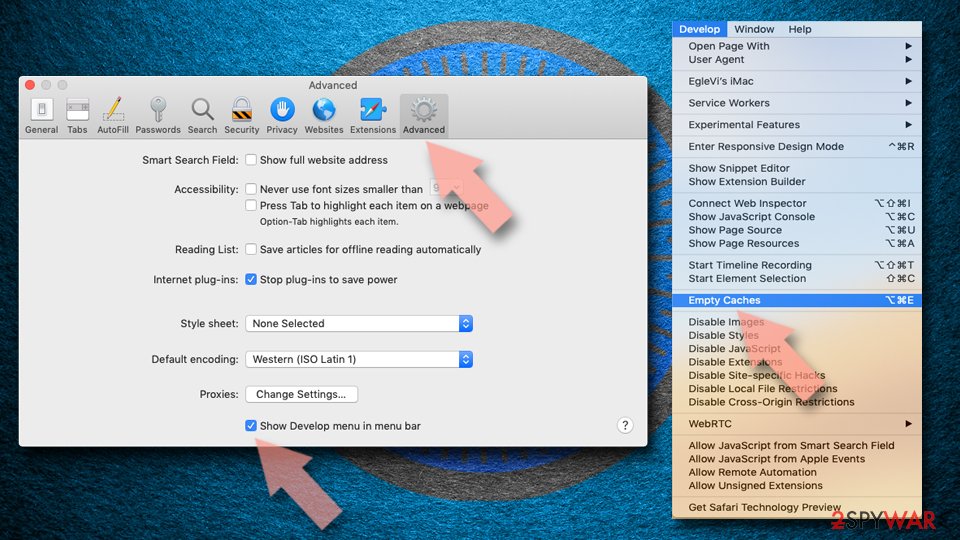
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
You should uninstall every component of 555.in.th virus if you want to prevent its reappearance on your computer in the future. We recommend eliminating these and similar entries: 555.in.th, startgo123.com, worldsearchpro.com, searchnow360.com, etc.
Remove the unwanted application:
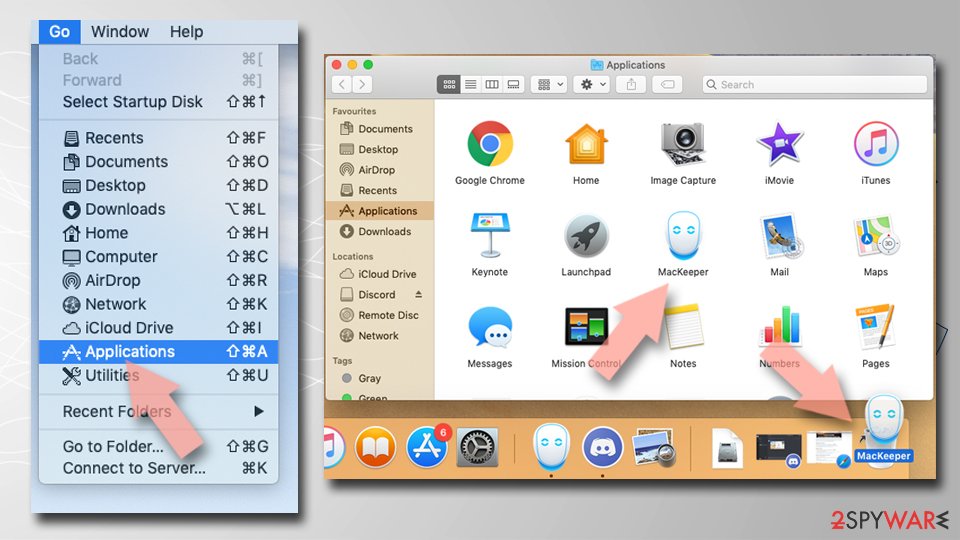
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
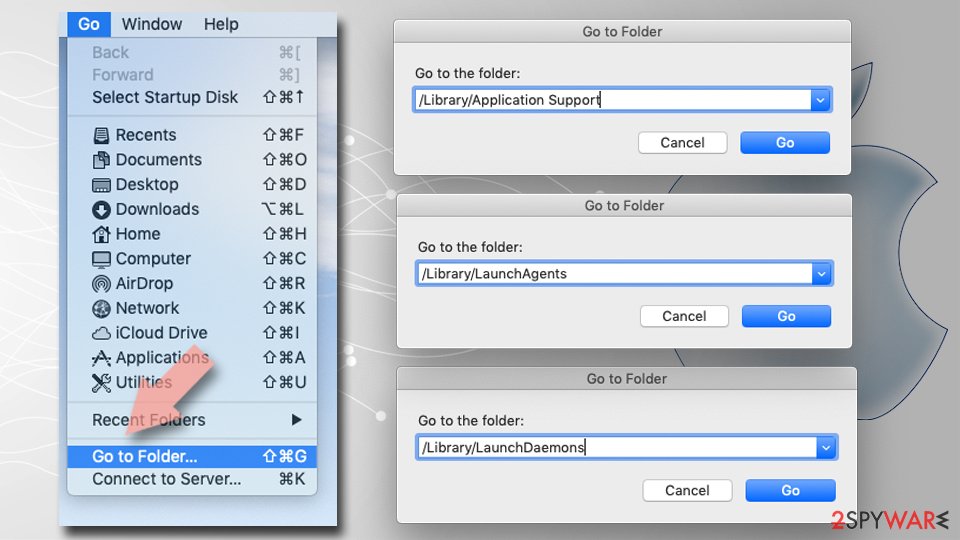
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
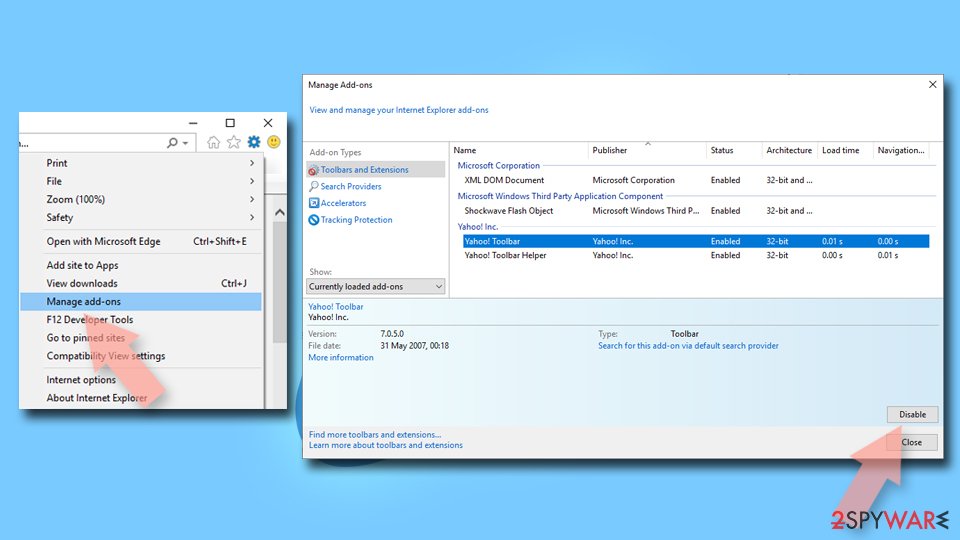
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
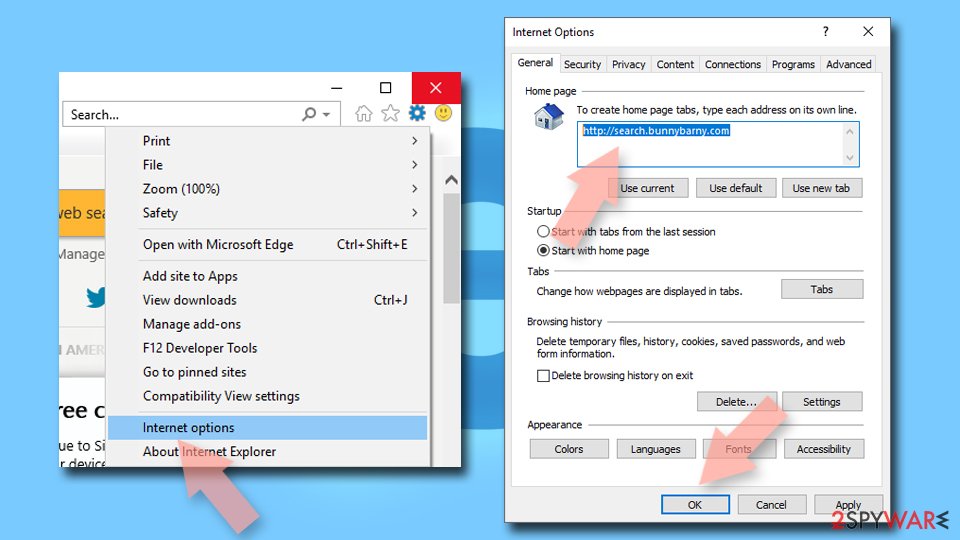
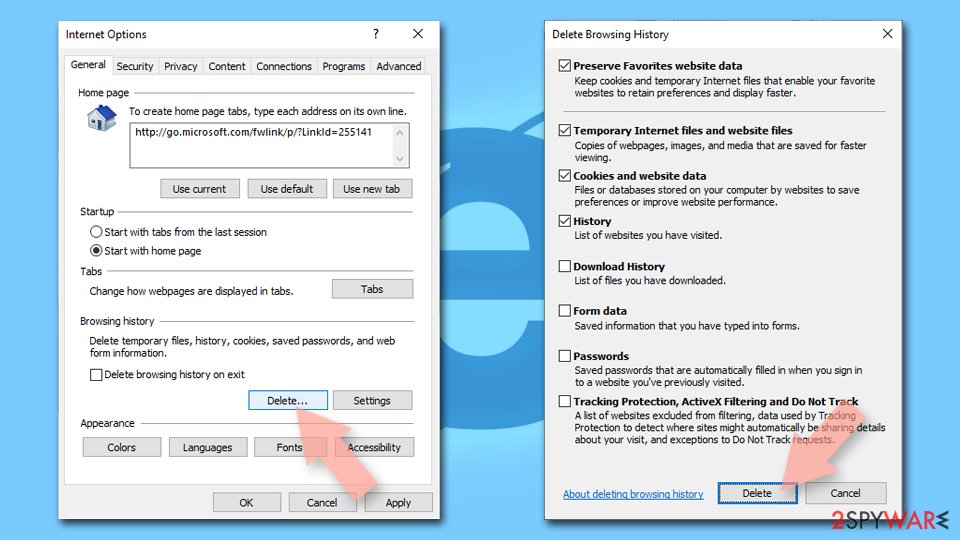
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
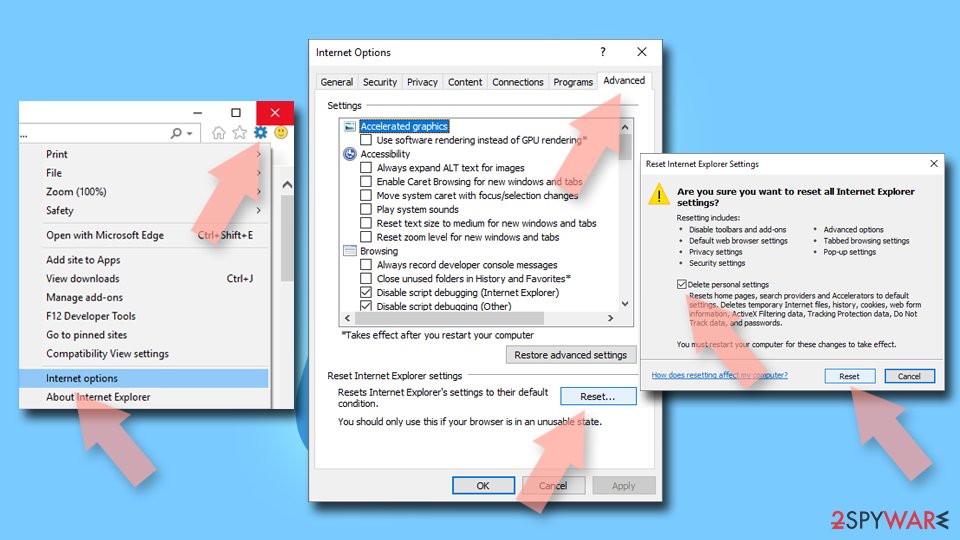
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
From our report of Jul 2016 · not reviewed since
How to remove 555.in.th virus from my computer?
Otherwise, you may be tricked by its sponsored links, pop-up ads and similar content which belongs to third parties and seeks to trick users into visiting sponsored websites.
To stay safe, you should be very careful with free software which is offered on the Internet. However, if you have already been tricked into downloading 555.in.th to your PC system, follow these instructions and remove the browser hijacker from your system:
Questions about 555.in.th redirect ads
How do I stop 555.in from opening?
Find and remove whatever opens it. Start with the browser's extensions page and remove anything you do not remember adding. Next, open the notification settings and take away permission from sites you do not recognise.
Then check Settings > Apps > Installed apps for programs added around the day the redirects began, and uninstall those. Restart the browser and test a few links after each step.
If 555.in still appears, reset the browser, which restores the default search engine, start page and permissions without deleting bookmarks or saved passwords. Redirects that survive a reset in every browser point to a program in Windows, and a full scan is the next step.
Did 555.in install a virus on my PC?
Very unlikely, unless you downloaded and opened something from the pages it led to. Redirect domains such as 555.in sell your visit to advertisers; they do not need to install anything to make money.
What can be installed is the thing that causes the redirects in the first place, such as an extension or an ad-supported program that came with free software. That is why the checks in this guide look at extensions, notification permissions and Installed apps.
A full scan with Microsoft Defender afterwards gives you a clear answer about the rest of the PC. If the scan is clean and the redirects stop after removing the cause, you are done.
Why does 555.in.th redirect show me ads?
Because that is its whole purpose. 555.in.th redirect is an ad redirect domain, and its operators are paid for every ad it displays and every click it gets. In this case the ads take the form of redirects through ad pages.
They are chosen by ad networks that accept almost any advertiser, which is why so many look like warnings or prizes. The ads are not a sign that your PC is broken or infected with something worse; they are a sign that something on it, or in the browser, has permission to advertise. Removing that permission or program stops them.
Is 555.in safe to visit?
No. The site 555.in exists to push visitors towards ads, and the pages it leads to include fake virus warnings, fake updates, prize scams and notification prompts. Visiting it once does not infect an up-to-date PC, but anything you click or download there is a gamble.
Do not enter personal details, do not allow notifications and do not call phone numbers it shows. If it opens by itself, close the tab and check the browser's extensions and notification permissions. Blocking the single domain helps little, because the operators register new names regularly.
Do I have to clean every browser?
Yes, if you use more than one. We saw 555.in.th redirect in Chrome, Edge and Firefox, and each browser keeps its own extensions, notification permissions and settings. Chrome and Edge share the same extension format, so one installer can add the same adware to both, while Firefox has its own add-ons.
Check every browser on the PC, including ones you rarely open. If you sync a browser with an account, clean it while signed in, so that the removal reaches your other computers rather than the adware returning from them.
How do I know the ads come from 555.in.th redirect?
Look for redirects to 555.in. That is the trace 555.in.th redirect leaves, and it shows up as redirects through ad pages. Ads that appear on every site, including ones that never carried ads before, point to something on your PC or in the browser rather than to the sites themselves.
A quick test is a private window, where extensions are off by default: if the ads disappear there, an extension is responsible. If they appear even with the browser closed, the source is a notification permission or a program in Windows.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
Why didn't my antivirus catch 555.in.th redirect?
Many security products do not block adware or notification sites by default, because users often agreed to them, even through a misleading prompt. Notification spam installs nothing at all, so there is no file to detect.
In Windows 11 you can make Microsoft Defender block potentially unwanted apps: open Windows Security > App & browser control > Reputation-based protection settings and turn on Potentially unwanted app blocking. If notifications caused the pop-ups, no scanner will report them; the fix is in the browser's site settings.
Will Fortect remove 555.in.th redirect?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For 555.in.th redirect, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)