
Puabundler:win32/msetup: what it is and how to remove it
Puabundler:win32/msetup is a potentially unwanted program that installs bundled with other software. The 2023 guide noted this threat causes browser hijacking and system damage through bundled distribution methods.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether ReimageRepair.exe is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove Puabundler:win32/msetup yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Puabundler:win32/msetup: summary
| Distribution | Torrent websites, bundled software |
|---|---|
| NAME | Puabundler:win32/msetup |
| TYPE | Potentially unwanted program |
| SYMPTOMS | This infection may be able to install other threats, cause pop-up spam, browser setting changes, or performance issues |
| DANGERS | Other malware and PUP installations, system damage |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Damage | Not recorded in the old report |
|---|---|
| Name | Puabundler:win32/msetup |
| Type | Loader |
| Symptoms | An unknown process in Task Manager |
| Evidence | 4 write-ups by security sites; details still limited |
| File names | ReimageRepair.exe |
| First seen | 3 January 2023 |
| Facts checked | 5 October 2026 |
What Puabundler:win32/msetup does on an infected PC
From our report of Jan 2023 · not reviewed since
Potential threats
One of the main potential threats of Puabundler:win32/msetup is that it may be able to install other types of malware on your computer.
Malware is a general term for any software that is designed to perform malicious actions on your computer, such as stealing sensitive information or damaging your system.
Puabundler:win32/msetup may also act as a potentially unwanted program (PUP) on your computer. PUPs are programs that are not necessarily malicious but may perform unwanted or unnecessary actions, such as displaying advertisements or altering your browser settings. PUPs may also be difficult to remove and can cause a range of symptoms, including:
While the exact capabilities of Puabundler:win32/msetup are unknown, it is possible that this virus may be able to cause these and other problems on your computer. If you think your computer may be infected with Puabundler:win32/msetup, it is important to take steps to remove it as soon as possible. This will help to prevent any potential damage to your system and ensure that your computer is secure.
- Constant pop-ups and redirects
- Changes to your browser settings or homepage
- Unwanted toolbars or extensions added to your browser
- Slow performance or system crashes
- Difficulty accessing certain websites
From our report of Jan 2023 · not reviewed since
More from our earlier report on Puabundler:win32/msetup
- Use trusted anti-malware tools to eliminate viruses
What Puabundler:win32/msetup can steal or download
From our report of Jan 2023 · not reviewed since
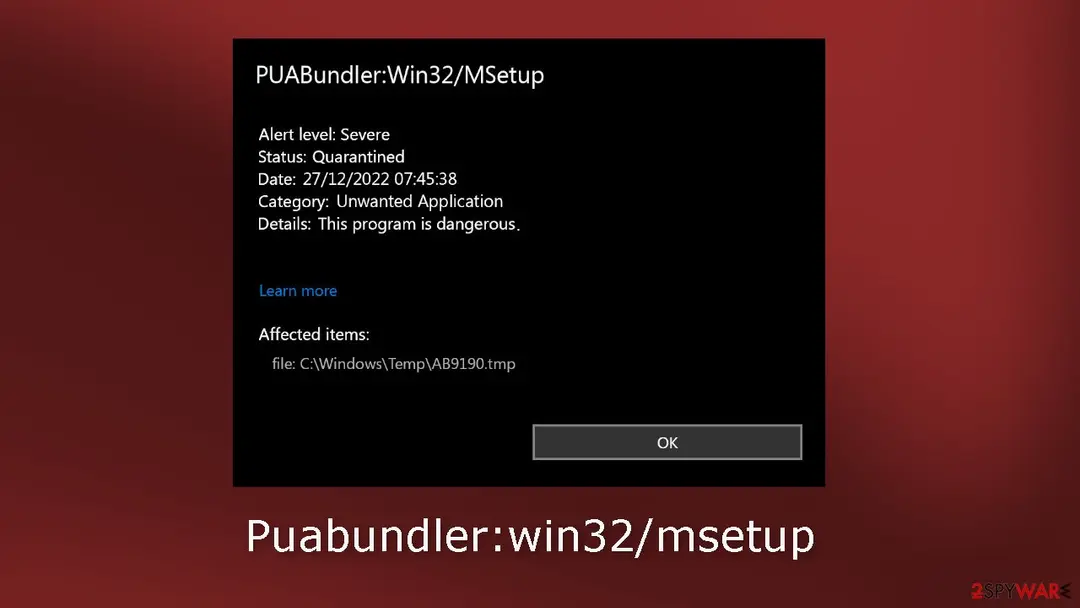
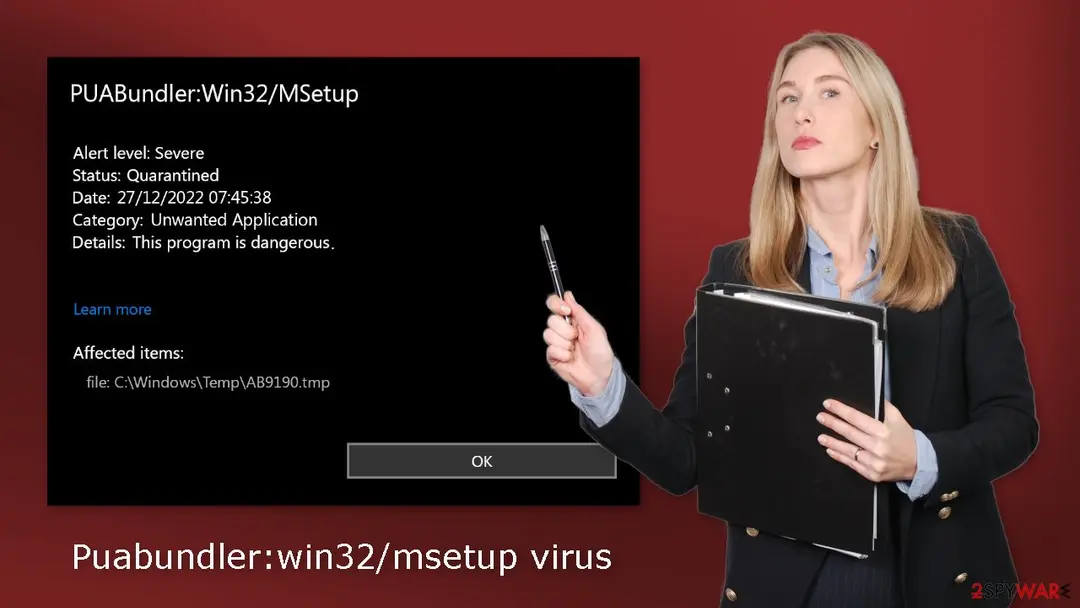
Puabundler:win32/msetup is a typical detection name for an unwanted program in Windows.
This is a potentially malicious virus that may cause a range of problems. Such viruses are often downloaded from software or media piracy websites and may be bundled with other software, which means they could be installed on your computer without your knowledge or consent. If you want to know more about this threat and learn how to remove it, please continue reading this article.
How Puabundler:win32/msetup got on your PC
From our report of Jan 2023 · not reviewed since
Puabundler:win32/msetup is most likely distributed through software or media piracy websites, where users may download illegal copies of software or media.
It may also be bundled with legitimate software and could be installed along with it. This means that you could accidentally download and install the virus while trying to download something else.
To stay safe online and avoid accidentally downloading Puabundler:win32/msetup or other types of malware, there are a few steps you can take:
- Only download software from reputable websites. Avoid downloading software from unfamiliar or untrustworthy websites, as this is a common way that malware is distributed.
- Be cautious when installing software. Always pay attention to the installation process and watch for any additional offers or prompts to install other software. If you are not sure whether a program is safe to install, you can do some research online or ask a trusted source for advice.
- Keep your computer and software up to date. Make sure you have the latest updates and patches for your operating system and any installed programs. This can help to protect your computer from vulnerabilities that could be exploited by malware.
- Use antivirus software. Antivirus software can help to protect your computer from malware and other threats. Make sure you have a reputable antivirus program installed and keep it up to date.
How to check the PC for Puabundler:win32/msetup
- File:
ReimageRepair.exe
How to remove Puabundler:win32/msetup
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where ReimageRepair.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
ReimageRepair.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like Puabundler:win32/msetup add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Puabundler:win32/msetup, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Puabundler:win32/msetup that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Puabundler:win32/msetup can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
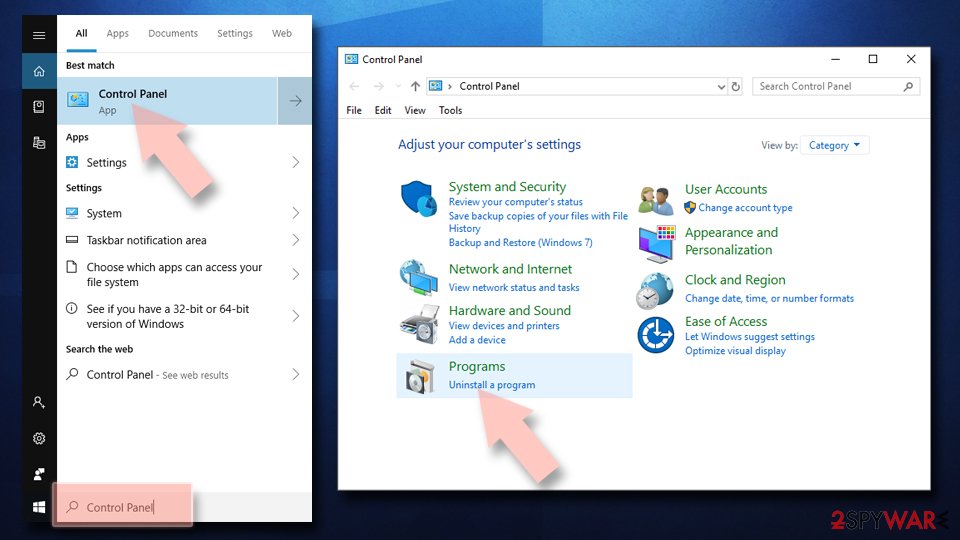
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
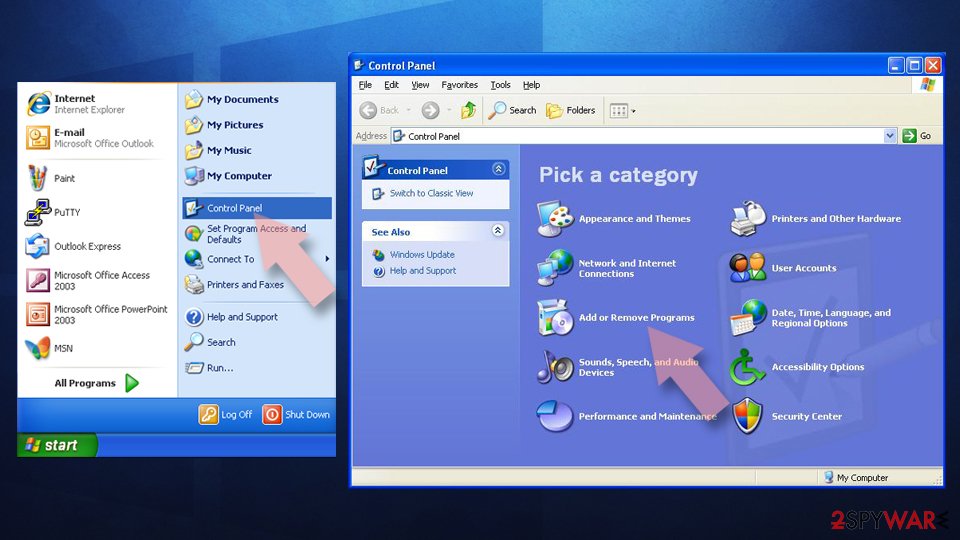
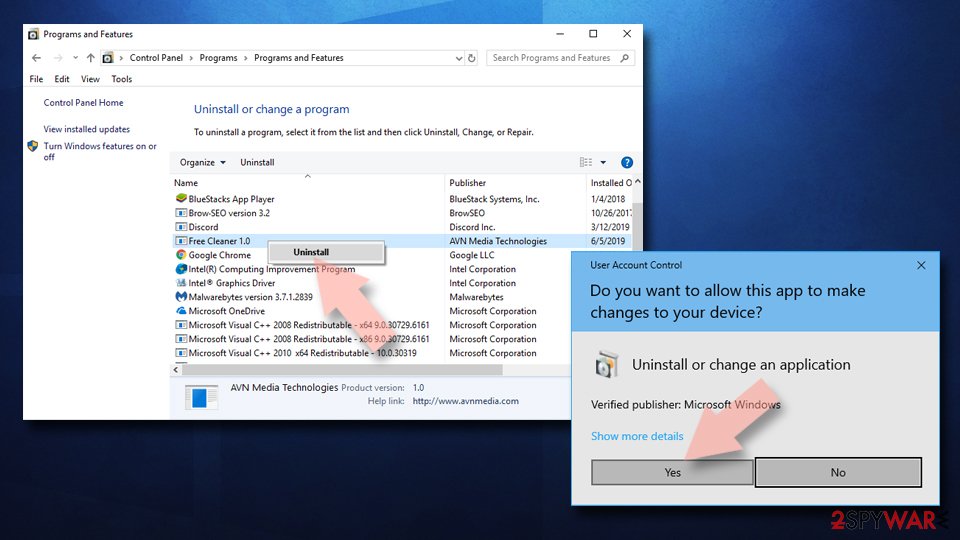
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
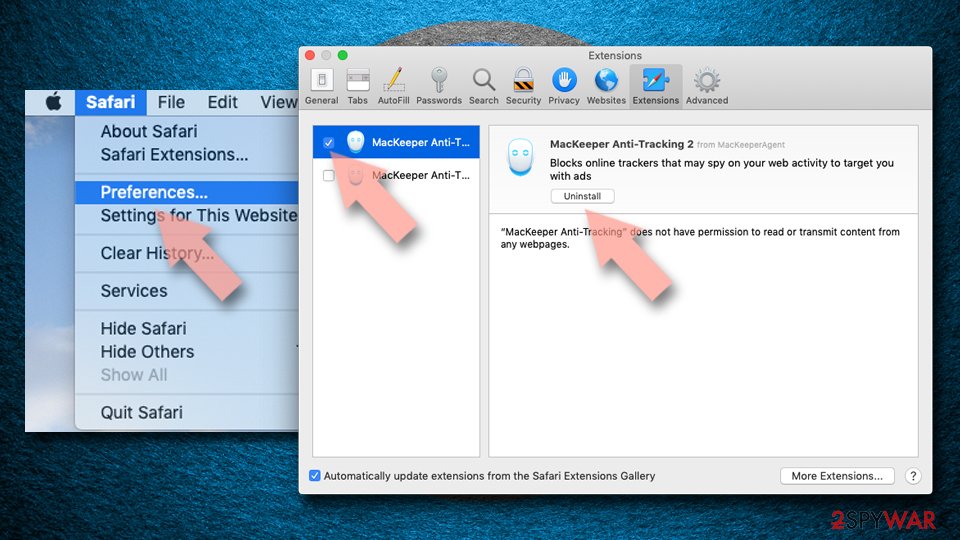
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
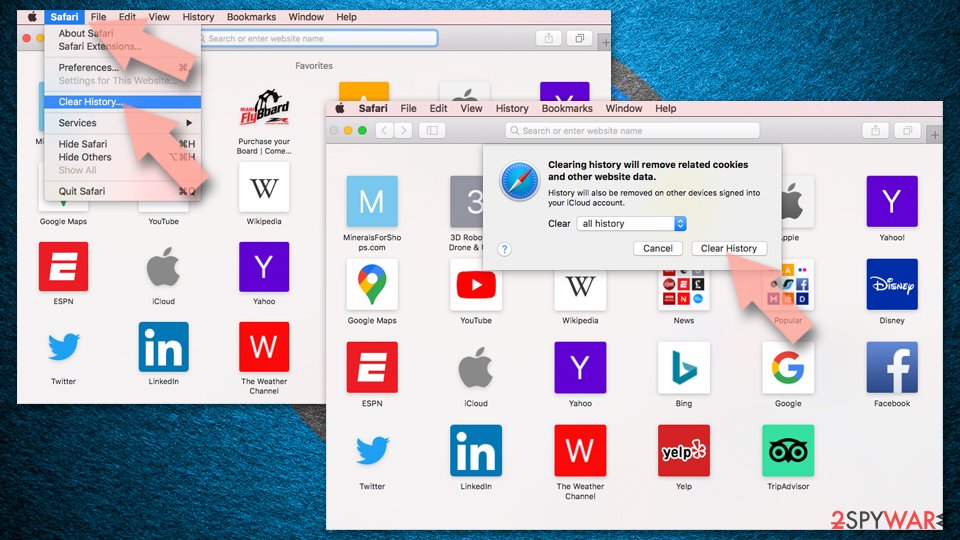
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
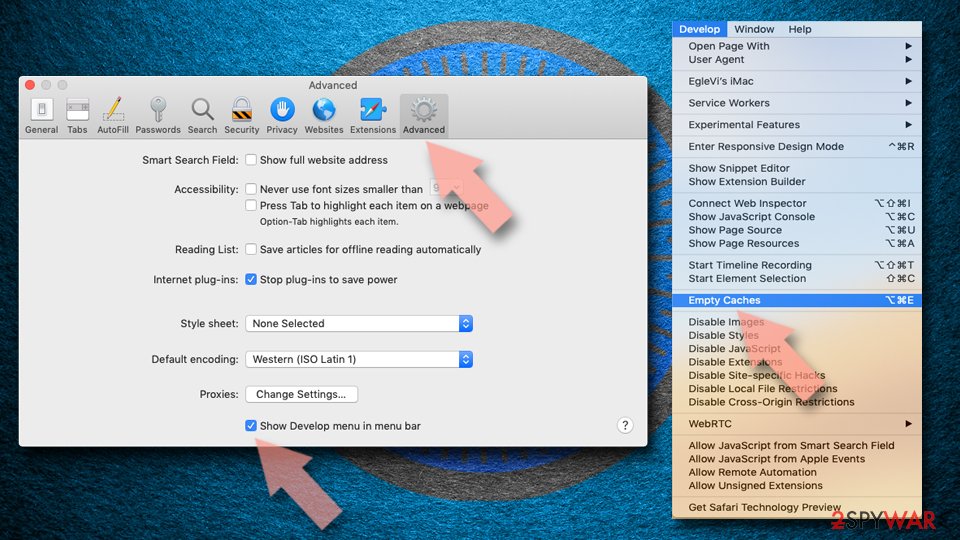
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
From our report of Jan 2023 · outdated details corrected in October 2026
Get rid of security threats with anti-malware tools
Once malware or PUPs enter the system, there is no better way to remove it than good quality, automized professional security tools.
However, the malicious program may block such tools, so you need to perform additional steps. It becomes difficult to remove serious threats like this over time as their damage increases.
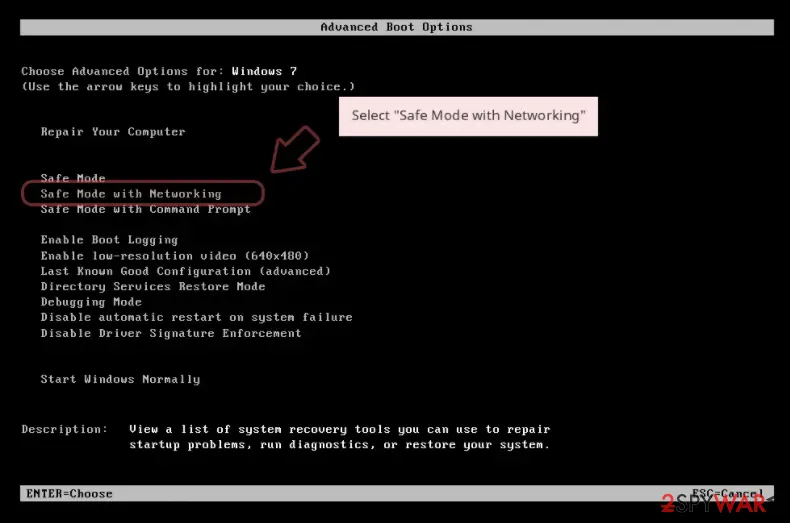
You need to enter Safe Mode with Networking if malware is blocking it. From there, you will be able to perform a scan with anti-malware tools with no problems. If you are not sure how to do that, follow the guide below:
Windows 7 and earlier versions (Vista, XP)
Windows 10 / Windows 11 and later
Once you reach Safe Mode, launch or , and perform a full system scan to eradicate malware and all its malicious components. Puabundler:win32/msetup may cause serious damage if you leave it on the system. This is why we do not suggest you try to remove the threat manually, as the process is very complicated and not suitable for people with minimal IT skills.
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
- Right-click on Start button and select Settings.
- On the left side of the window, pick Recovery.
- Click Restart now.
- Select Troubleshoot.
- Go to Advanced options.
- Select Startup Settings.
- Click Restart.
- Press 5 or click 5) Enable Safe Mode with Networking.
From our report of Jan 2023 · not reviewed since
Fix system damage
We highly recommend using a one-of-a-kind, patented technology of repair.
Not only can it fix virus damage after the infection, but it is also capable of removing malware that has already broken into the system thanks to several engines used by the program. Besides, the application is also capable of fixing various Windows-related issues that are not caused by malware infections, for example, Blue Screen errors, freezes, registry errors, damaged DLLs, etc.
By employing , you would not have to worry about future computer issues, as most of them could be fixed quickly by performing a full system scan at any time. Most importantly, you could avoid the tedious process of Windows reinstallation in case things go very wrong due to one reason or another.
- Download the application by clicking on the link above.
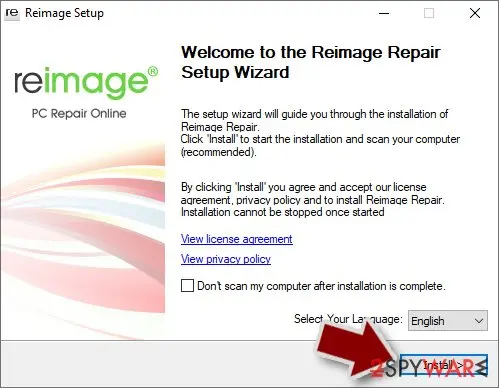
- Click on the ReimageRepair.exe.
- If User Account Control (UAC) shows up, select Yes.
- Press Install and wait till the program finishes the installation process.
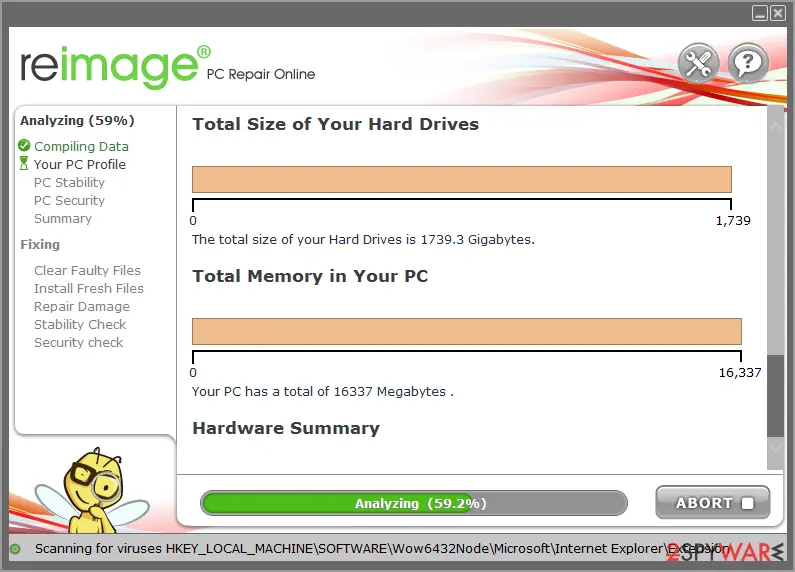
- The analysis of your machine will begin immediately.
- Once complete, check the results - they will be listed in the Summary.
- You can now click on each of the issues and fix them manually.
From our report of Jan 2023 · not reviewed since
Unwanted browser behavior, ads, and pop-ups
If you experience unwanted browser behavior, such as constant pop-ups and redirects, changes to your browser settings or homepage, or unwanted toolbars or extensions, it is possible that Puabundler:win32/msetup is at fault. To address these issues, there are a few steps you can take:
By taking these steps, you may be able to address unwanted browser behavior and remove any malware that may be causing the issue. It is also a good idea to practice safe browsing habits and avoid downloading software or media from piracy websites, as this is a common way that malware is distributed. By following these precautions, you can help to protect your computer from malware and other threats.
You can also find instructions on how to fix these various issues below this article.
- Remove unwanted programs and extensions. Check your list of installed programs and extensions and uninstall anything that you do not recognize or that you no longer want.
- Reset your browser settings. If your browser settings have been changed without your consent, you can try resetting them to their default settings. This may help to remove unwanted toolbars and extensions and restore your previous settings.
- Block pop-ups in your browser. Most modern browsers have a built-in option to block pop-ups. You can enable this feature to help prevent unwanted pop-ups and redirects.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called ReimageRepair.exe in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about Puabundler:win32/msetup
What is Puabundler:win32/msetup?
It is a potentially unwanted program detection name indicating malicious bundled software on your Windows computer. This virus may install other threats, cause pop-up spam, browser setting changes, or performance issues.
It is typically downloaded from software or media piracy websites and bundled with other software, meaning it could be installed without your knowledge or consent. The detection suggests your system contains unwanted programs disguised within legitimate-looking software packages. While the exact capabilities vary, it can cause system damage and enable installation of additional malware.
How does Puabundler:win32/msetup get installed?
It is most commonly distributed through pirated software and media websites where users download illegal copies. It may also bundle with legitimate software and install along with your intended download.
When you use a Quick or Default installation method, additional components hide in the installer. Users accidentally download and install the virus while trying to get something else entirely.
Third-party software sites serve as perfect distribution grounds for adware and PUPs. Installers routinely include additional apps within them, with distributors actively hiding promotional offers in standalone packages. Most users skip through installation steps without noticing the additional offerings.
What damage can Puabundler:win32/msetup cause?
It may install other types of malware onto your computer, potentially causing severe damage. The threat can modify browser settings, install unwanted toolbars or extensions, trigger slow performance or system crashes. Infected systems may experience changes to homepage, search engine settings, and new tab pages.
It typically functions as a potentially unwanted program rather than traditional malware, but can open doors to more serious infections. Performance degradation becomes noticeable through increased resource consumption. Additionally, damage to system files and registry corruption may require professional repair after removal.
Should I be worried about other malware if I have this?
Yes. Puabundler:win32/msetup often acts as a gateway for additional malicious software installation. The presence of this bundled threat indicates your system security was already compromised enough to allow infiltration.
Additional malware may have been installed alongside or after this threat. Perform comprehensive scans with multiple security tools to detect all components. Do not assume a single threat removal solves all problems.
More sophisticated threats may hide in your system after this obvious detection. Use full system scans in Safe Mode to catch hidden infections that normal scans might miss.
How do I remove Puabundler:win32/msetup?
Enter Safe Mode with Networking and launch antivirus software to perform full system scans. Use Windows Defender or alternative security tools to systematically remove all detected components.
Do not attempt manual removal as the process is complicated and unsuitable for users with minimal IT skills. After security software removes the threat, check your installed programs list and uninstall anything suspicious.
Remove unwanted browser extensions and reset browser settings to defaults. Clear your browser cache and temporary files. After removal, use system repair tools to fix any virus damage, registry errors, damaged DLLs, or Windows-related issues caused by the infection.
Why can't I remove it with standard uninstall?
The threat creates multiple system-level components that simple uninstall methods cannot reach. Malware often modifies system services, startup programs, and registry entries to ensure persistence. Standard uninstall tools cannot access or modify these deep system changes.
The program intentionally embeds itself to avoid removal through normal channels. This is why security software is necessary—it has access to system-level locations and can forcefully remove all components, including those hidden in Windows services or startup folders. Manual removal risks damaging vital system files and causing system instability.
Should I try Safe Mode removal?
Yes. Rebooting into Safe Mode with Networking is essential for complete removal. Malware and system utilities run at reduced capacity in Safe Mode, preventing them from defending themselves against removal tools.
Press F8 during boot to access Advanced Boot Options and select Safe Mode with Networking. Once in Safe Mode, launch your antivirus software and perform complete system scans.
Safe Mode allows security software to remove files and services that would otherwise be protected by running processes. This approach has higher success rates for persistent threats that resist removal in normal Windows mode.
How can I prevent Puabundler:win32/msetup?
Only download software from reputable websites and avoid unfamiliar or untrustworthy sources where malware is common. Be cautious during software installation—watch for additional offers or prompts to install other software.
Always select Advanced/Custom installation options instead of Recommended/Quick modes. Research software before installation to verify safety. Keep your computer and all installed software updated with latest patches.
Install and maintain reputable antivirus software that provides real-time protection. Be skeptical of offers bundled with downloads and actively deselect them. If unsure whether software is safe, research it online or consult trusted sources before proceeding with installation.
Will Fortect remove Puabundler:win32/msetup?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Puabundler:win32/msetup, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Zdnet: Google: Unwanted bundled software is way more aggressive than malware (read October 5, 2026)
- Howtogeek: PUPs Explained: What is a "Potentially Unwanted Program"? (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)