
Rigj virus: what it is and how to remove it
Rigj virus is not a program developed by trusted people. Criminals made the threat to extort money from people with all the claims about file recovery possibilities.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Before you restore backups, a full scan can confirm the program that added .rigj is gone.
Do it yourself · free Remove Rigj virus yourself 6 steps, about 18 minutes, no software needed.
Start the steps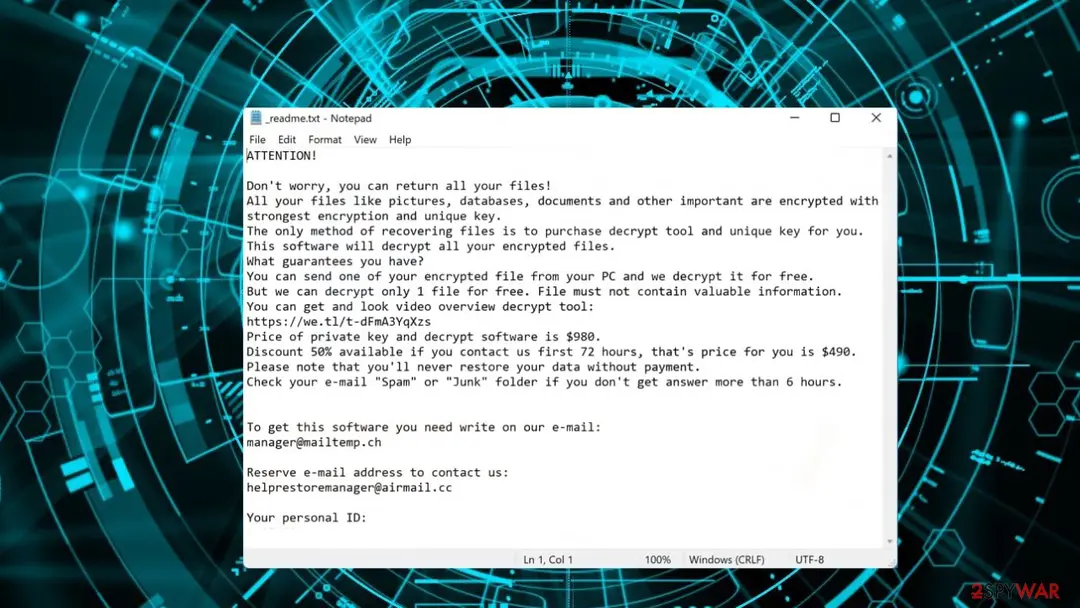
Rigj virus: summary
| Distribution | Files with malicious code can get attached to emails or distributed via cracked and pirated software, games |
|---|---|
| Name | Rigj virus |
| Type | Ransomware, file-locker |
| Family | Djvu/STOP ransomware |
| Contact emails | manager@mailtemp.ch, helprestoremanager@airmail.cc |
| Ransom note | _readme.txt |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 13 more facts
| Ransom amount | $980 and the discount on the first 72 hours for $490 |
|---|---|
| Possible recovery options | Media files can get restored, in some cases with the proper tool. Otherwise is not the decryptable versions. Additional helpful tips are listed below |
| Detection names | No Microsoft detection name is known |
| Encrypted file extension | .rigj |
| Decryptor | No free decryptor is known for this variant; check No More Ransom (nomoreransom.org) for updates |
| Damage | Not recorded in the old report |
| Symptoms | Files renamed with a new extension and a ransom note left in folders |
| Evidence | 4 write-ups by security sites; no sample analysed yet |
| Encrypted files | .rigj |
| Attacker contacts | manager@mailtemp.ch |
| Free decryptor | No free decryptor is known (checked 6 October 2026) |
| First seen | 26 November 2021 |
| Facts checked | 6 October 2026 |
- File extension:
.rigj - Note file:
_readme.txt - Contact:
manager@mailtemp.ch
From our report of Nov 2021 · not reviewed since
More from our earlier report on Rigj virus
- Treat the system properly with an anti-malware tool, so the malware is terminated fully
- The system data gets affected and even damaged, so repair tools like can help with virus damage and leftovers
The Rigj virus ransom note
ATTENTION!
Don't worry, you can return all your files!
All your files like pictures, databases, documents and other important are encrypted with strongest encryption and unique key.
The only method of recovering files is to purchase decrypt tool and unique key for you.
This software will decrypt all your encrypted files.
What guarantees you have?
You can send one of your encrypted file from your PC and we decrypt it for free.
But we can decrypt only 1 file for free. File must not contain valuable information.
You can get and look video overview decrypt tool:
hxxps://we.tl/t-Tjb0YqckGX
Price of private key and decrypt software is $980.
Discount 50% available if you contact us first 72 hours, that's price for you is $490.
Please note that you'll never restore your data without payment.
Check your e-mail "Spam" or "Junk" folder if you don't get answer more than 6 hours.
To get this software you need write on our e-mail:
manager@mailtemp.ch
Reserve e-mail address to contact us:
helprestoremanager@airmail.cc
Your personal ID:
How to remove Rigj virus
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Rigj virus and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so Rigj virus cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.rigjand the instructions are in_readme.txt. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for Rigj virus, no free decryptor is known (checked 6 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing Rigj virus does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
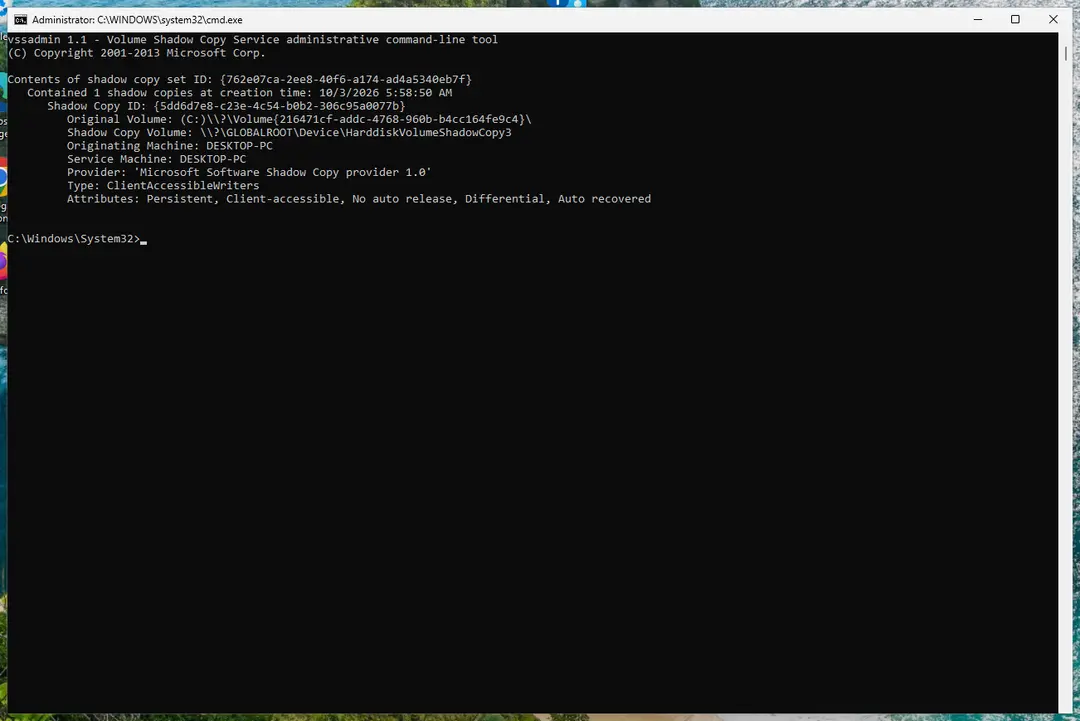
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that Rigj virus deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Restore Windows "hosts" file to its original state
Some ransomware might modify Windows hosts file in order to prevent users from accessing certain websites online. For example, Djvu ransomware variants add dozens of entries containing URLs of security-related websites, such as 2-spyware.com. Each of the entries means that users will not be able to access the listed web addresses and will receive an error instead.
Here's an example of "hosts" file entries that were injected by ransomware:
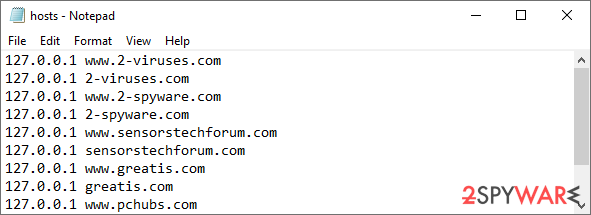
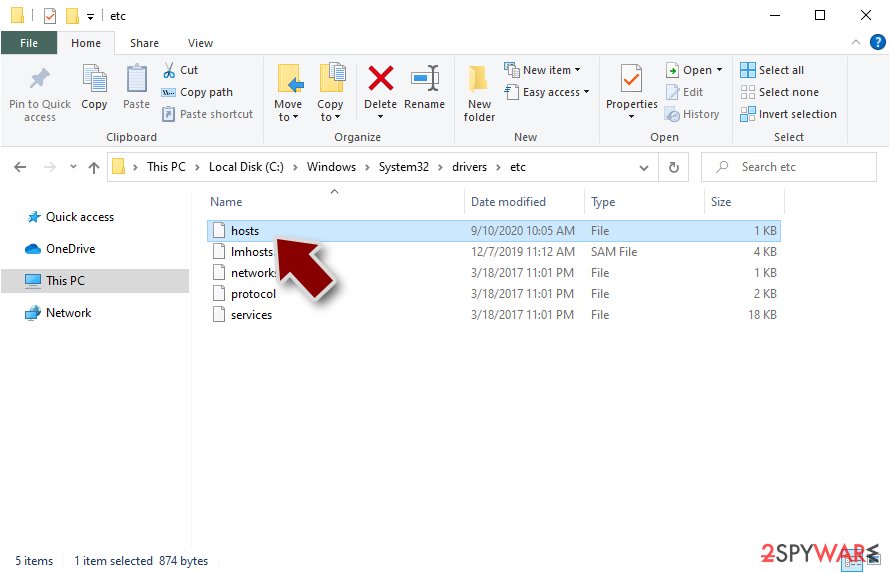
In order to restore your ability to access all websites without restrictions, you should either delete the file (Windows will automatically recreate it) or remove all the malware-created entries. If you have never touched the "hosts" file before, you should simply delete it by marking it and pressing Shift + Del on your keyboard. For that, navigate to the following location:
C:\\Windows\\System32\\drivers\\etc\\
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
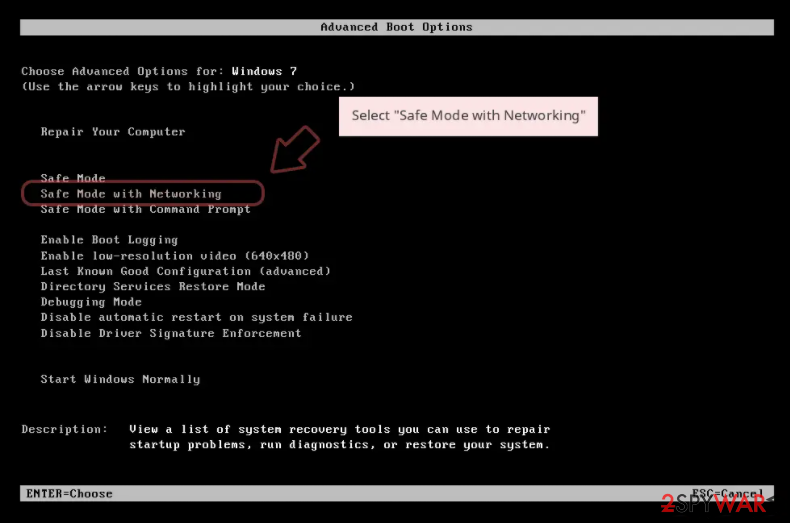
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
- Right-click on Start button and select Settings.
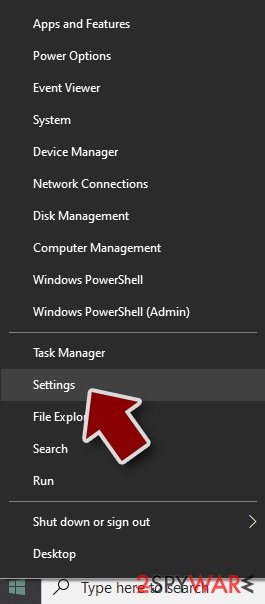
- Scroll down to pick Update & Security.
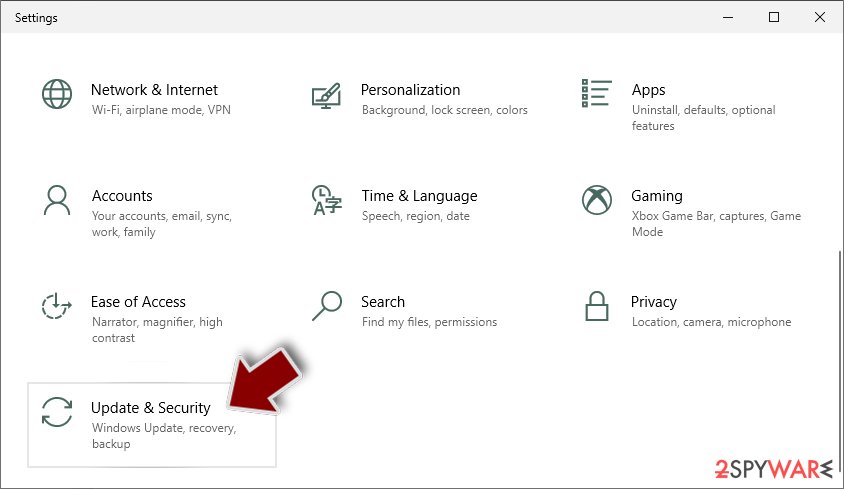
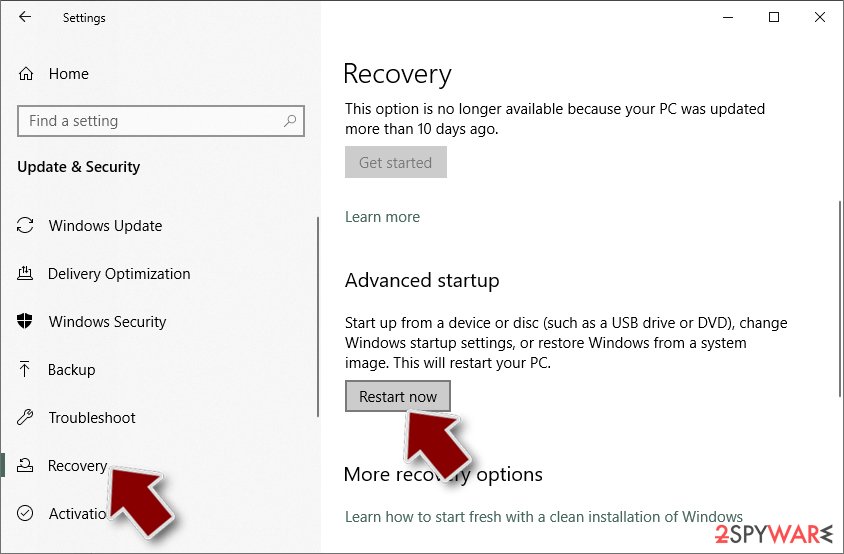
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
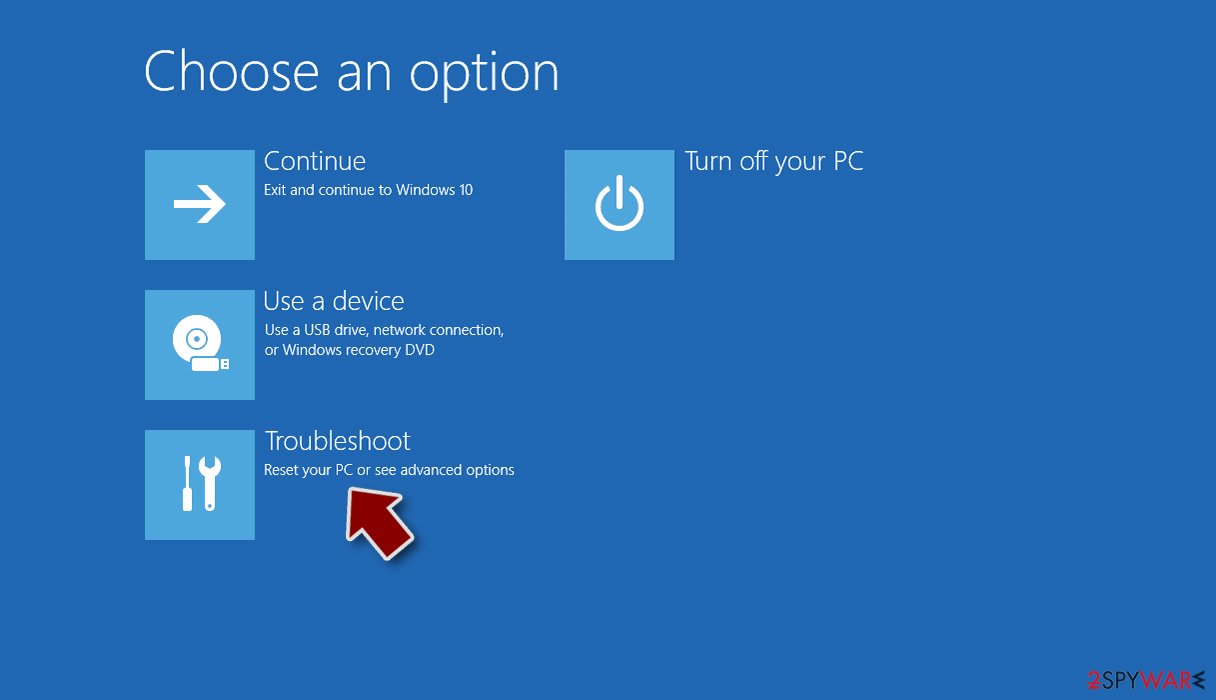
- Select Troubleshoot.
- Go to Advanced options.
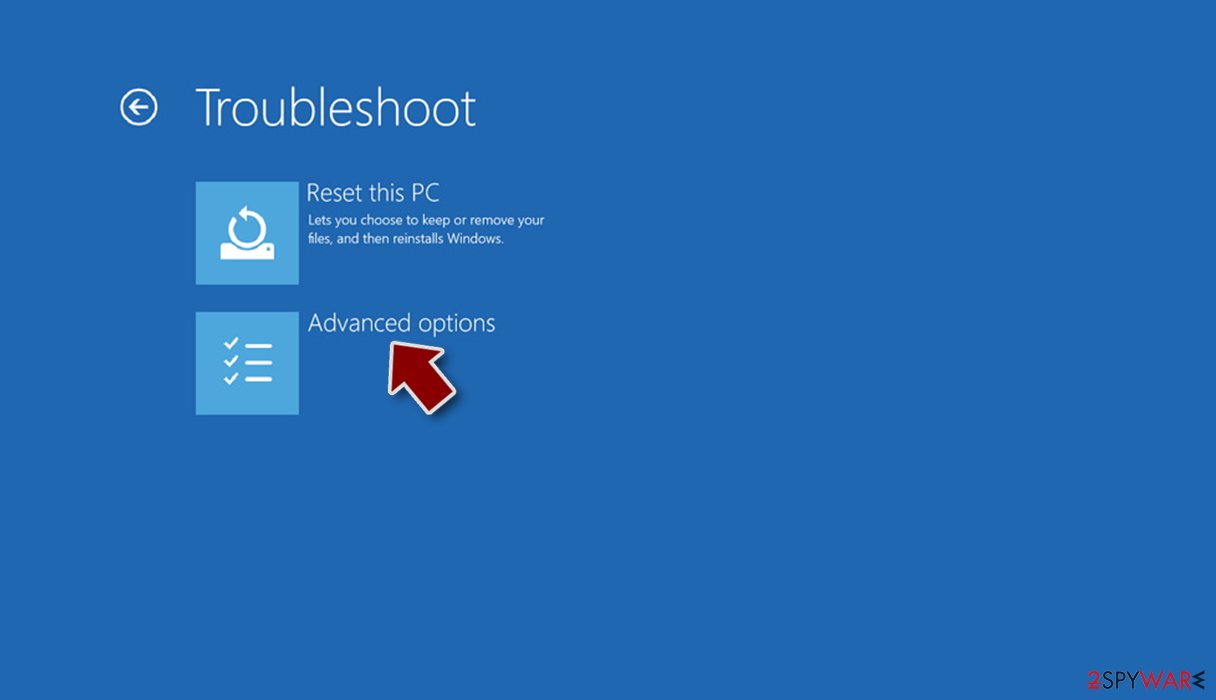
- Select Startup Settings.
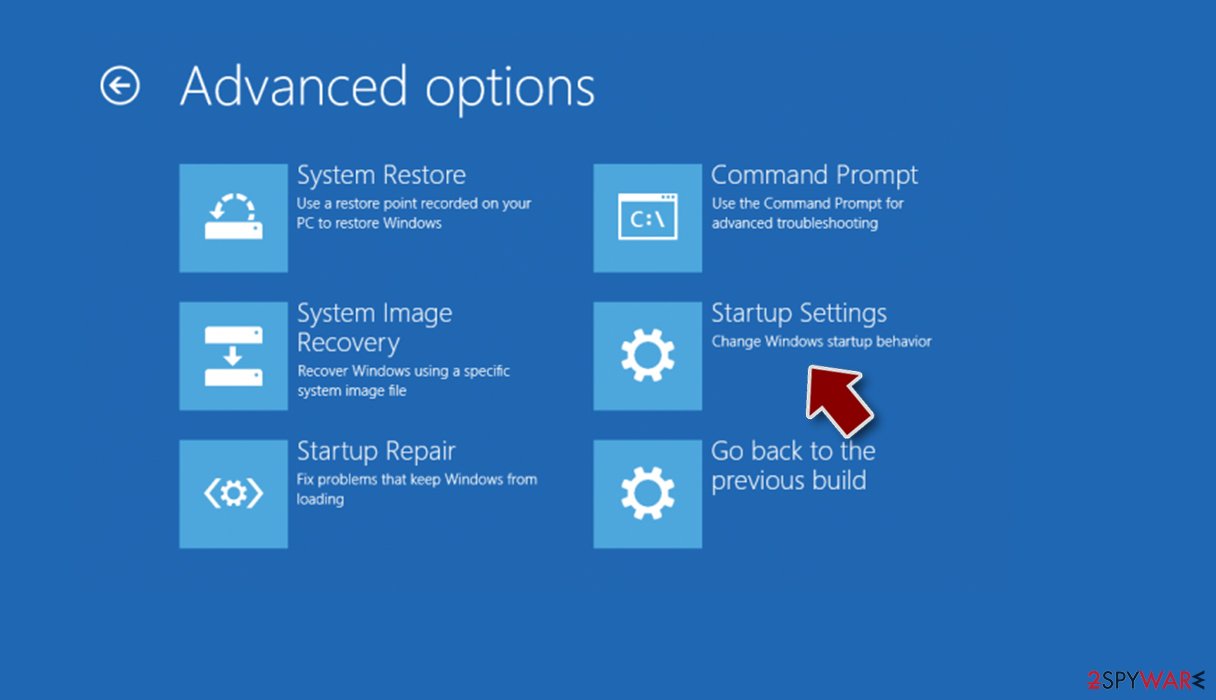
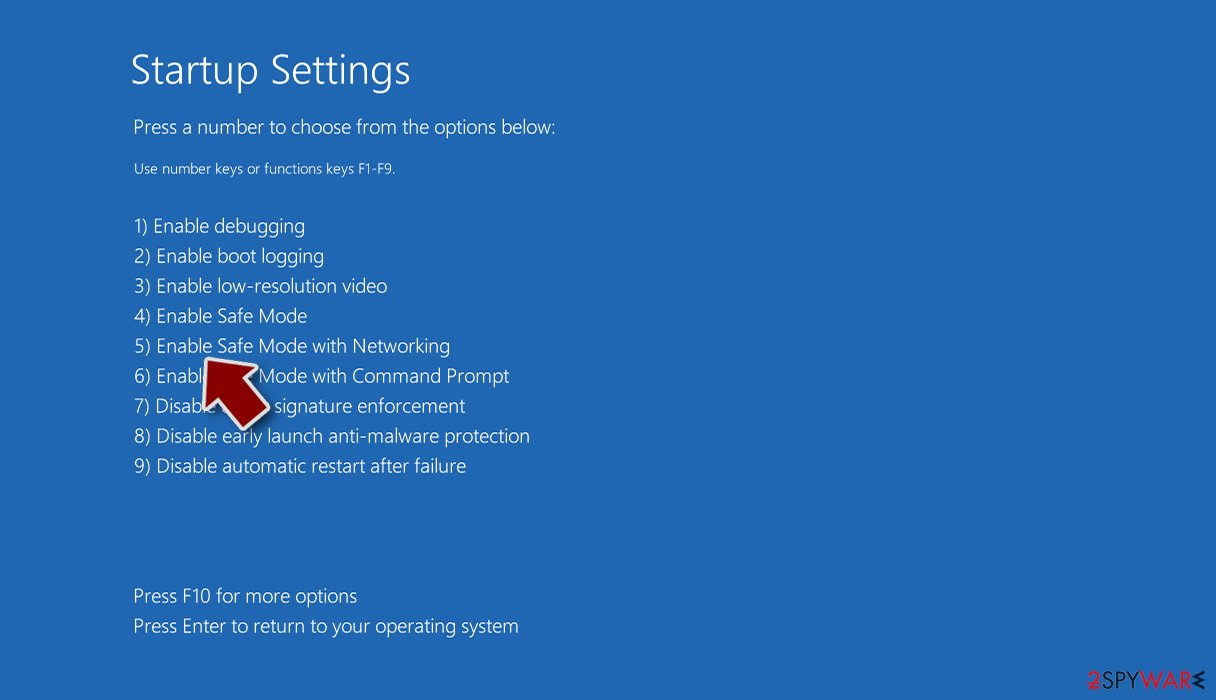
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
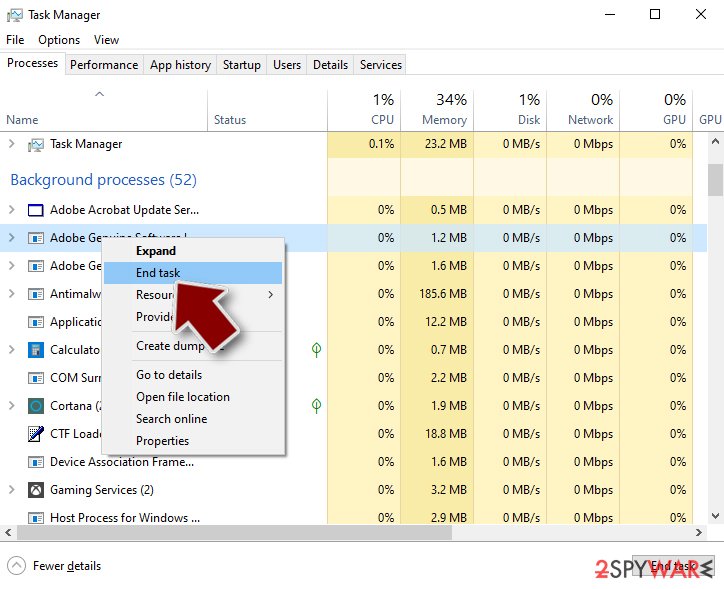
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
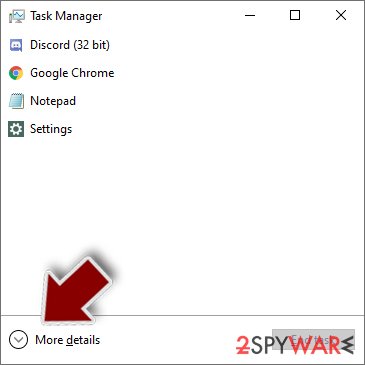
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
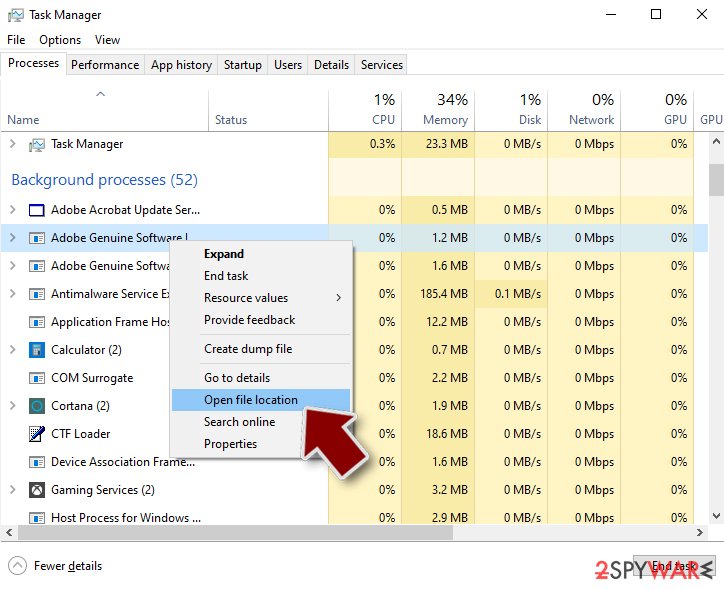
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
Step 3. Check program Startup
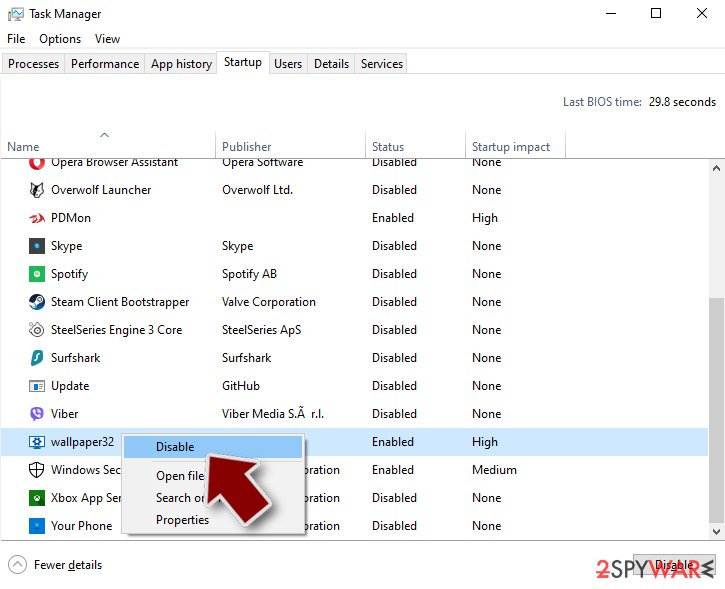
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
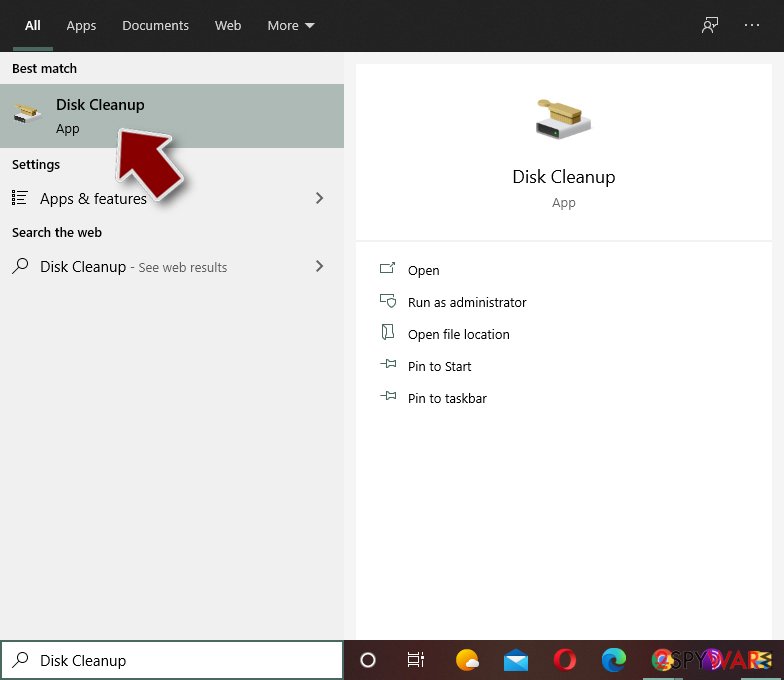
- Type in Disk Cleanup in Windows search and press Enter.
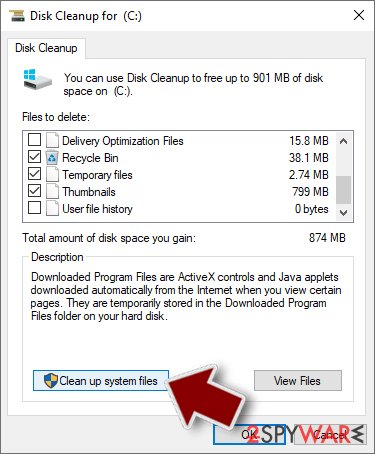
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Restore files using data recovery software
Since many users do not prepare proper data backups prior to being attacked by ransomware, they might often lose access to their files permanently. Paying criminals is also very risky, as they might not fulfill the promises and never send back the required decryption tool.
While this might sound terrible, not all is lost - data recovery software might be able to help you in some situations (it highly depends on the encryption algorithm used, whether ransomware managed to complete the programmed tasks, etc.). Since there are thousands of different ransomware strains, it is immediately impossible to tell whether third-party software will work for you.
Therefore, we suggest trying regardless of which ransomware attacked your computer. Before you begin, several pointers are important while dealing with this situation:
- Since the encrypted data on your computer might permanently be damaged by security or data recovery software, you should first make backups of it - use a USB flash drive or another storage.
- Only attempt to recover your files using this method after you perform a scan with anti-malware software.
Install data recovery software
- Download .
- Double-click the installer to launch it.

- Follow on-screen instructions to install the software.
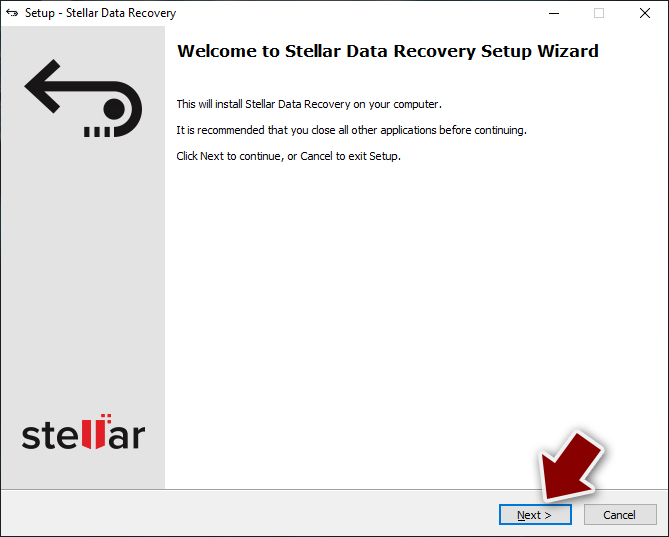
- As soon as you press Finish, you can use the app.
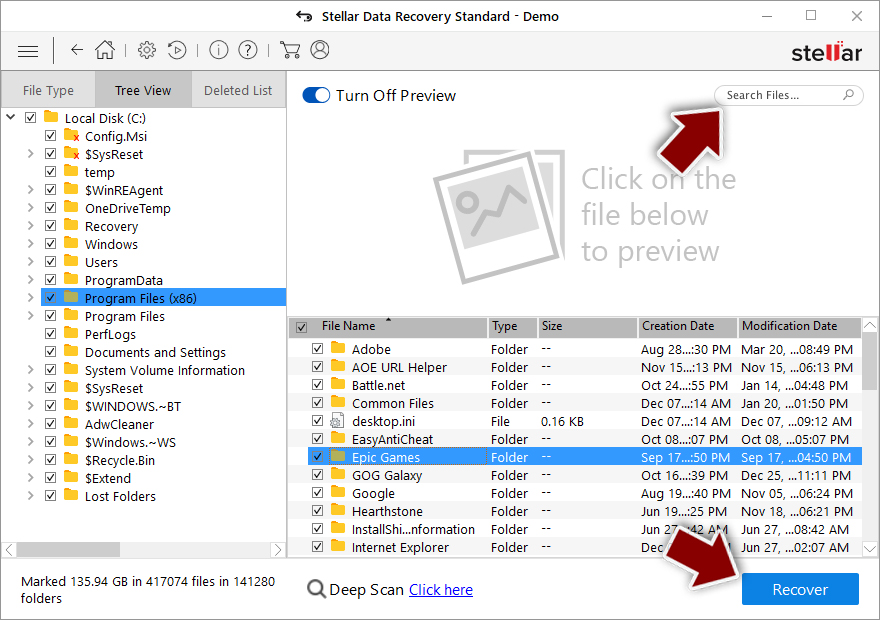
- Select Everything or pick individual folders where you want the files to be recovered from.
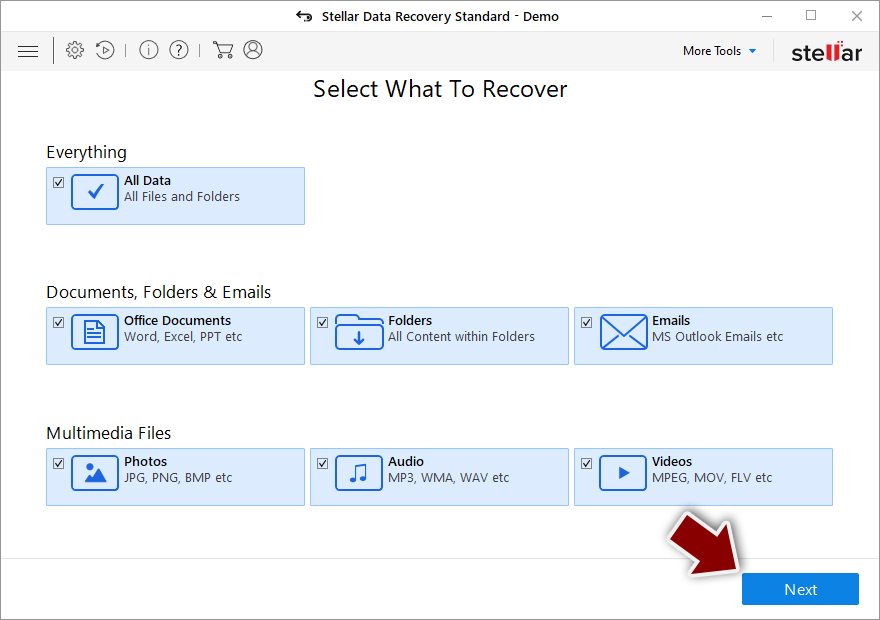
- Press Next.
- At the bottom, enable Deep scan and pick which Disks you want to be scanned.
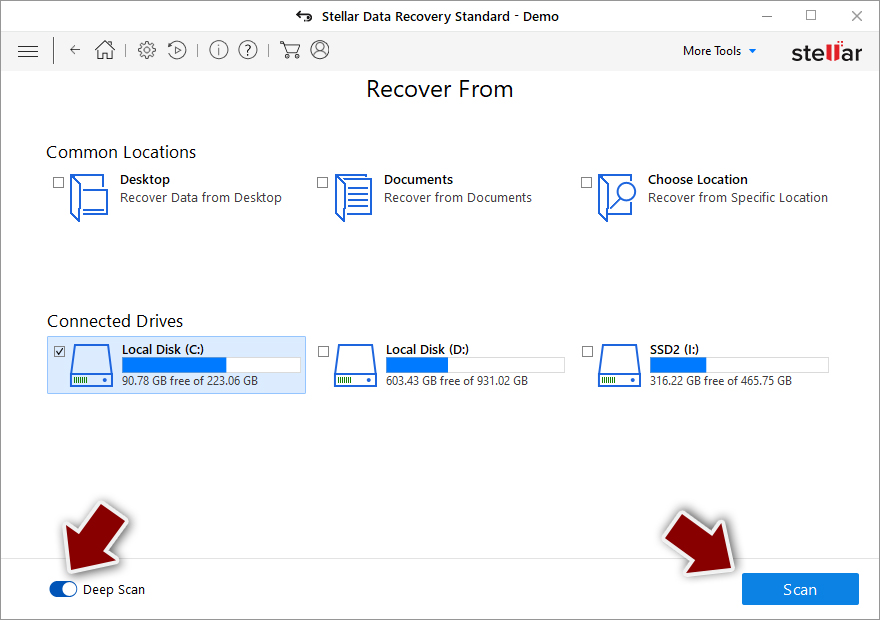
- Press Scan and wait till it is complete.
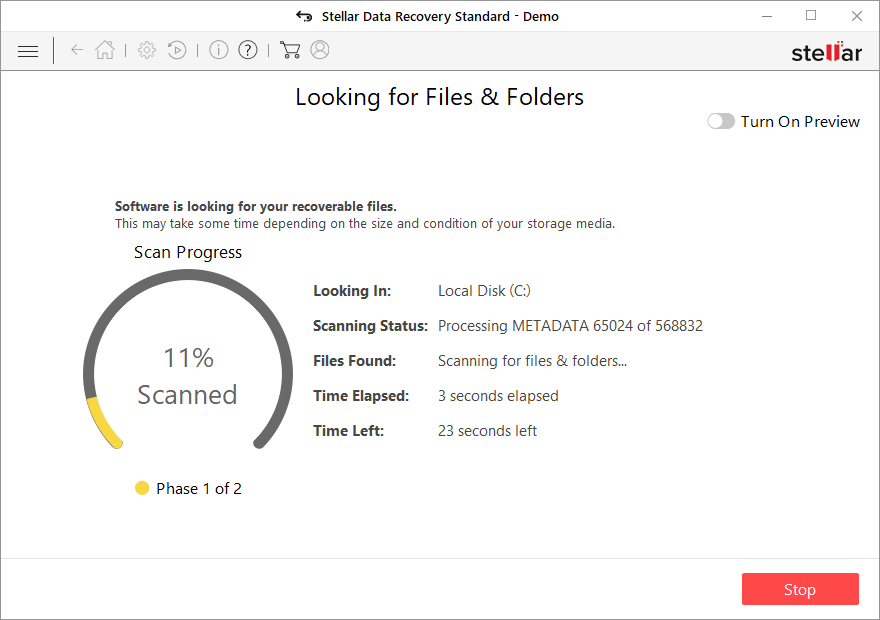
- You can now pick which folders/files to recover - don't forget you also have the option to search by the file name!
- Press Recover to retrieve your files.
Create data backups to avoid file loss in the future
Report the incident to your local authorities
Ransomware is a lucrative, highly illegal business, and authorities are actively targeting ransomware operators. The level of investigation and follow-up depends on the country, the scale of the incident, and whether the attack is linked to known ransomware groups. To increase the likelihood of identifying the culprits, the agencies need information. In many cases, reports are used primarily for intelligence gathering, trend analysis, and victim support rather than immediate identification of attackers.
Therefore, by reporting the crime, you could help stop the cybercriminal activities and catch the threat actors. Reporting does not guarantee investigation or recovery of data, but it contributes to broader efforts to track ransomware campaigns. Make sure you include all the possible details, including how did you notice the attack, when it happened, etc. Relevant details may also include affected systems, ransom demands, cryptocurrency wallet addresses, and any communication with the attackers. Additionally, providing documents such as ransom notes, encrypted files, or malware executables would be beneficial.
Law enforcement agencies typically deal with online fraud and cybercrime, although it depends on where you live. Here is the list of local authority groups that handle incidents like ransomware attacks, sorted by country:
- USA - Internet Crime Complaint Center IC3
- United Kingdom - ActionFraud
- Canada - Canadian Anti-Fraud Centre
- Australia - ScamWatch
- New Zealand - ConsumerProtection
- Germany - Polizei
- France - Ministère de l'Intérieur
If your country is not listed above, you should contact the local police department or communications center.
Isolate the infected computer
Some ransomware strains aim to infect not only one computer but hijack the entire network. As soon as one of the machines is infected, malware can spread via the network and encrypt files everywhere else, including Network Attached Storage (NAS) devices. NAS devices are commonly compromised via reused administrator credentials and remote access services, and attackers may also delete existing snapshots. If your computer is connected to a network, it is important to isolate it to prevent re-infection after ransomware removal is complete.
In modern environments, ransomware often spreads using stolen credentials, remote management tools, VPN connections, and cloud synchronization services, not only through shared network drives.
The easiest way to disconnect a PC from everything is simply to plug out the ethernet cable. This does not disconnect wireless networks, VPN connections, or cloud services, which must also be disabled separately. However, in the corporate environment, this might be extremely difficult to do (also would take a long time). In many organizations, devices are centrally managed, and network isolation is typically performed by IT or security teams using endpoint security or device management tools. The method below will disconnect from all the networks, including local and the internet, isolating each of the machines involved.
On modern Windows systems, network connections can also be disabled through the Settings app or automatically isolated using endpoint detection and response (EDR) tools.
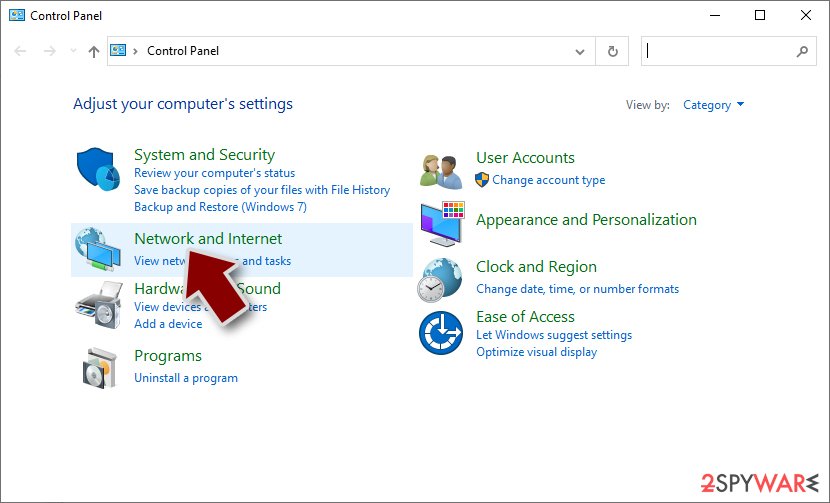
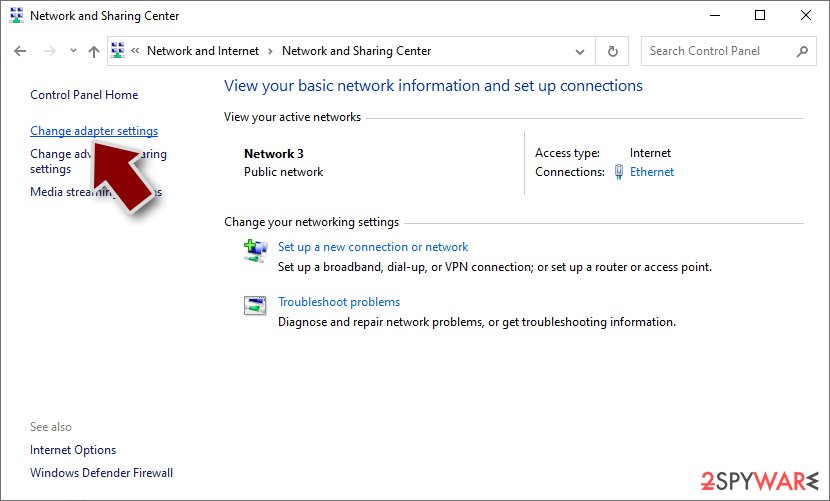
- Type in Control Panel in Windows search and press Enter
- Go to Network and Internet
- Click Network and Sharing Center
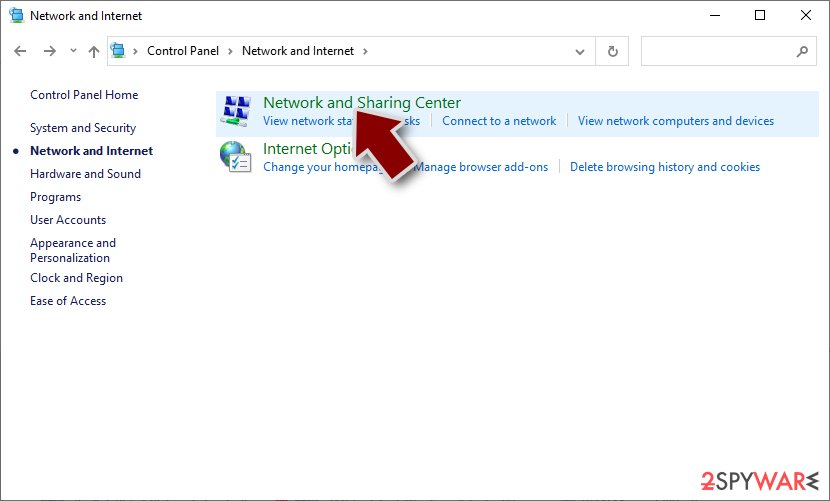
- On the left, pick Change adapter settings
- Right-click on your connection (for example, Ethernet), and select Disable
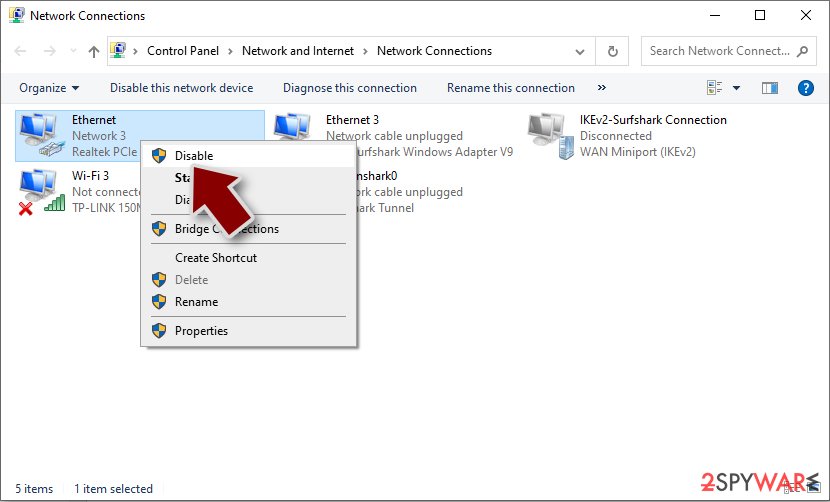
- Confirm with Yes.
If you are using some type of cloud storage you are connected to, you should disconnect from it immediately. It is also advisable to disconnect all the external devices, such as USB flash sticks, external HDDs, etc. Once the malware elimination process is finished, you can connect your computers to the network and internet, as explained above, but by pressing Enable instead. Before reconnecting, credentials should be reset, persistence mechanisms checked, and backups verified to ensure reinfection does not occur.
From our report of Nov 2021 · not reviewed since
Rigj ransomware is a virus that asks almost $1000 by claiming that decryption is possible after the payment
Rigj virus is not a program developed by trusted people.
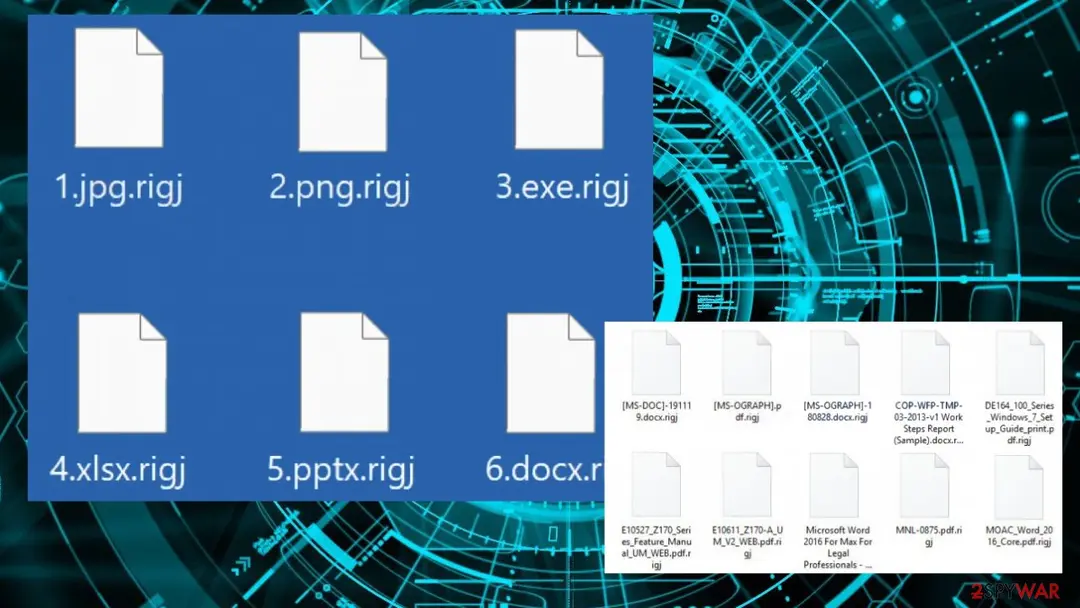
Criminals made the threat to extort money from people with all the claims about file recovery possibilities. The ransomware is a file-locker that is using an encryption algorithm which allows the original code of the file to get changed. Once that is done, you see the appendix .rigj added to files.
When the _readme.txt file is delivered to your screen and placed in other folders, it is safe to say that this Rigj files virus has already caused havoc across the system. It runs in various parts system-wide, and settings get altered. This infection will affect preferences like security options or functions that control users' access, so many helpful features get disabled.
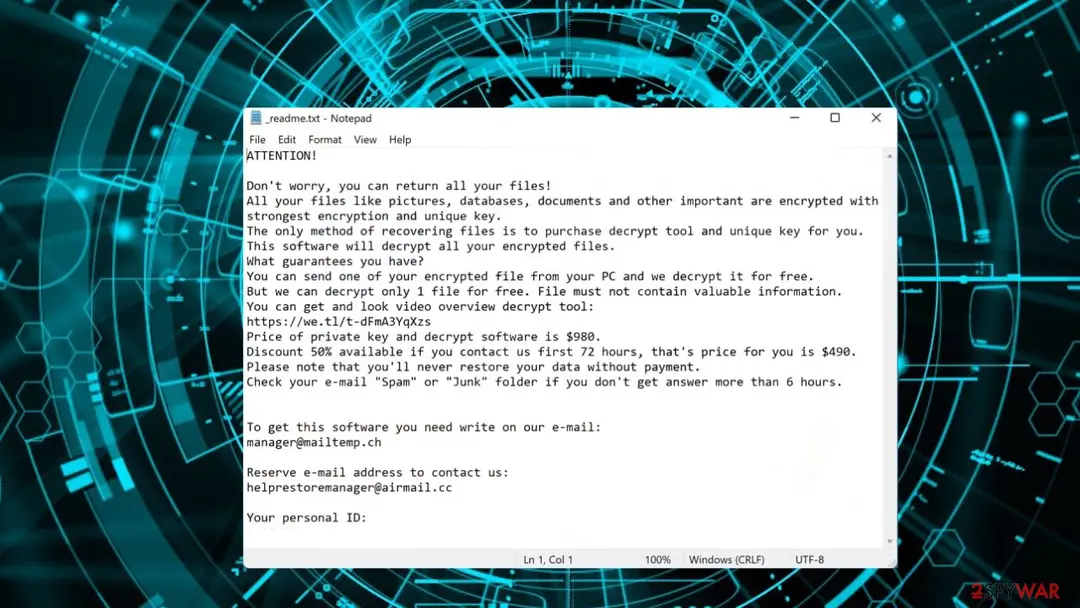
The ransom note lists the possible options and contact information. The victim gets the encouragement to contact the people behind this malware via email manager@mailtemp.ch, helprestoremanager@airmail.cc. The amount of the ransom starts with $490 because this is the way criminals try to create trust. It doubles after 72 hours, but it is not recommended to even consider contacting Rigj ransomware creators.
The ransom note:
This infection changes files and can make them unreadable unless decryption is possible or the ransom is paid. Once you start communicating with people behind a virus, threat actors might send malicious links instead of their promised app for unlocking your encrypted data.
Rigj is one of the most recent ransomware from the Djvu virus family variants to hit the headlines. This threat encrypts files and appends the filename with a unique extension. This function is not the only issue with the file-locking virus because it is persistent and damaging. More than people think of, so remove the threat as soon as those files get locked, as researchers recommend.
The Rigj virus is used to create havoc on the machine, so users are eager to pay when criminals claim about the issues with their computer and data. Encryption algorithms allow hackers to change the original coding of documents, images, video, audio. Unreadable files are not recoverable with proper tools. But still can be replaced by the file copies from backups.
The threat mainly is distributed via spam email via file attachments. Once someone has been tricked into opening these malicious attachments, it leads them into becoming a ransomware victim. Threat actors demand payment in Bitcoin, so the payment is not easily traced, but the promise of decryptor is false. Remove the threat instead of contacting criminals.
From our report of Nov 2021 · not reviewed since
Elimination is key and should be taken care of first
Rigj ransomware is a dangerous threat that can affect your system and control various processes.
This type of malware aims to get money from victims, so there are no reasons to trust the people behind this virus since they only care about the cash. Sometimes even after transferring payment for decryption, tool delivery does not happen anymore, which means those infected may never see their precious information again.
The ransomware is a kind of threat that encrypts your files and then forces you to pay. The Rigj file virus first infects computers through emails containing attachments with malicious scripts attached. However, some users may have been tricked into downloading executables via HTTP downloads embedded directly within web pages where they appear innocent enough.
Those can be fake ads placed alongside content that would lead unsuspecting visitors straight down an infected page without realizing what had happened until it was too late. Avoid these issues by keeping the tool like on the machine.
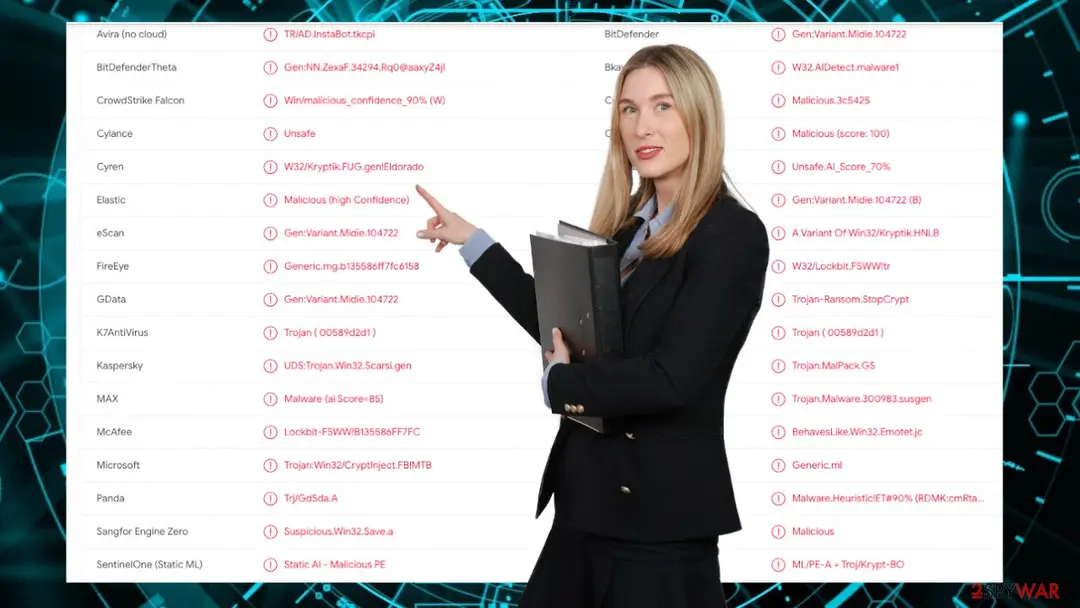
It not only can help with security but also removes the infection that is already on the PC. As well as , such tools scan the machine and clear any malicious pieces. Then you can worry about your data.
From our report of Nov 2021 · not reviewed since
Try the decryption option for the versions with offline ID
If your computer got infected with one of the Djvu variants, you should try using Emsisoft decryptor for Djvu/STOP.
It is important to mention that this tool will not work for everyone - it only works if data was locked with an offline ID due to malware failing to communicate with its remote servers.
Even if your case meets this condition, somebody from the victims has to pay criminals, retrieve an offline key, and then share it with security researchers at Emsisoft. As a result, you might not be able to restore the encrypted files immediately.
Thus, if the decryptor says your data was locked with an offline ID but cannot be recovered currently, you should try later. You also need to upload a set of files - one encrypted and a healthy one to the company's servers before you proceed.
From here, there are three available outcomes:
- After pressing Download button, a small pop-up at the bottom, titled decrypt_STOPDjvu.exe should show up - click it.
- If User Account Control (UAC) message shows up, press Yes.
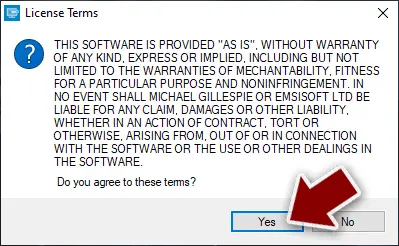
- Agree to License Terms by pressing Yes.
- After Disclaimer shows up, press OK.
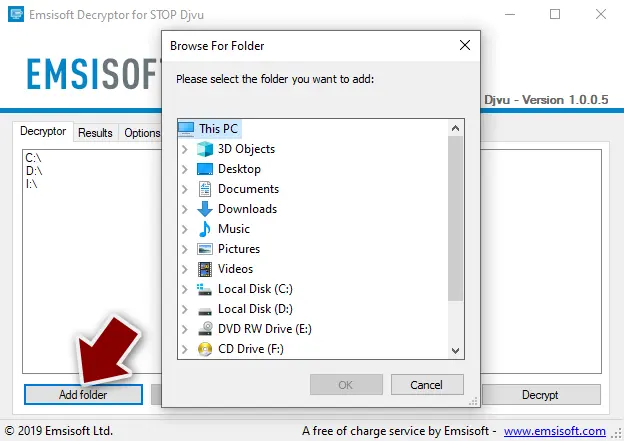
- The tool should automatically populate the affected folders, although you can also do it by pressing Add folder at the bottom.
- Press Decrypt.
- "Decrypted!" will be shown under files that were decrypted successfully - they are now usable again.
- "Error: Unable to decrypt file with ID:" means that the keys for this version of the virus have not yet been retrieved, so you should try later.
- "This ID appears to be an online ID, decryption is impossible" - you are unable to decrypt files with this tool.
From our report of Nov 2021 · not reviewed since
Recover after the infection
One of the easiest ways to get a computer infected with malware is by downloading files and programs from an unknown source.
This could be as simple as opening up an email attachment or clicking on a link in spam messages which will take you somewhere dangerous. The malware drop is also possible when the random pirating package installs lead people into installing infections onto their systems without knowing about them beforehand.
Rigj ransomware is related to criminals and can be spread around with data-stealing purposes and more in-depth plans. Always examine every website before entering personal information like credit card numbers. Encryption is not the only process that these threats can cause. There are many more issues related to cryptovirus infiltrations.
Once a computer is infected with malware, its system is changed to operate differently. For example, an infection can alter the Windows registry database, damage vital bootup, and other sections, delete or corrupt DLL files, etc. Once a system file is damaged by malware, antivirus software cannot do anything about it, leaving it just the way it is.
Consequently, users might experience performance, stability, and usability issues, to the point where a full Windows reinstallation is required.
Therefore, we highly recommend using a one-of-a-kind, patented technology of repair. Not only can it fix virus damage after the infection, but it is also capable of removing malware that has already broken into the system thanks to several engines used by the program.
Besides, the application is also capable of fixing various Windows-related issues that are not caused by malware infections, for example, Blue Screen errors, freezes, registry errors, damaged DLLs, etc.
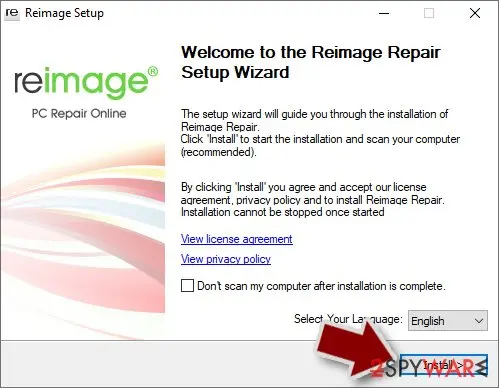
- Download the application by clicking on the link above
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
From our report of Nov 2021 · not reviewed since
How to avoid the virus infection
Do not trust any pop-ups or suspicious alerts.
If something seems off, it is best practice not to click on whatever appears on your screen because clicking can install a program that could allow hackers into your system and cause irreversible damage. Using P2P can give you severe malware, including the Rigj ransomware.
To avoid this problem, it is recommended to install only authorized official sources for software and avoid free downloads from third-party sites that offer little security against viruses or other malicious programs like keyloggers.
Also, pay attention to details. There have been cases when this fake update was displayed as an official-looking message from the Windows system to mask the encryption process and keep users' attention from the slowness of the machine.
Make sure to keep the security apps like , , and run them every time the system shows any suspicious activity, so you can clear infections, stop malware from running. Remember that removing the threat is not the same as decrypting files, so move to file repair only when the threat is eliminated.
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Make the next attack harmless
Rigj virus could only hurt the files that had no second copy, and the signs (files that end in .rigj and no longer open) showed exactly which ones those were.
The 3-2-1 rule fixes that:
- three copies
- two media
- one disconnected
A practical version for a home PC: OneDrive or another cloud backup with version history, plus an external disk that you plug in once a week for File History and then unplug. Test a restore now and then by opening a few files from the backup on another device.
Details, schedules and what not to back up are in our 3-2-1 backup guide for Windows.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Rigj virus
How do I open .rigj files?
You cannot open them by renaming or by choosing another program. The .rigj ending shows that Rigj virus encrypted the content, and only the matching key can reverse it. Renaming a file back to .docx or .jpg changes nothing except the icon, and it can confuse a future decryptor, so leave the names as they are.
To get the content back, use a backup, an unencrypted copy elsewhere, or a decryptor listed on No More Ransom if one exists for Rigj virus. Store the encrypted files on an external disk until then.
Did Rigj virus steal my files or passwords?
We do not know yet. Nothing published so far shows data theft by Rigj virus, but the only confirmed sign is files that end in .rigj and no longer open, which says nothing about what happened before. Many current ransomware attacks copy files or run a password stealer first, so it is wise to act as if they did.
From a clean device, change the passwords that were saved in the browsers on this PC, starting with e-mail and banking, sign out of all sessions and turn on two-step verification. Watch bank statements and account activity for the next few weeks.
Is there a free Rigj virus decryptor?
We last checked on 6 October 2026, and for Rigj virus no free decryptor is known. We check No More Ransom, which collects free tools from police and security companies, and the decryptor pages of the major antivirus vendors. A working decryptor exists only when the encryption has a flaw or the keys were leaked or seized.
Ignore sites and videos that offer a "Rigj virus decryptor" for download or for a fee: these are usually scams or malware. Real decryptors are free and come from known security companies or law enforcement. Keep the encrypted files in case a tool appears later.
Should I pay the ransom?
We advise against it, and so do the FBI, Europol and national cyber agencies. Payment does not guarantee a working tool: some attackers never reply, some tools damage files, and some variants have no decryptor at all. Paying also funds further attacks and can make you a target again.
Before considering payment, try every recovery option in this guide and report the attack. Companies must involve their legal adviser and insurer, because payments to sanctioned groups can be illegal. If files are truly irreplaceable, store the encrypted copies and wait; decryptors sometimes appear later.
Can a data-recovery company decrypt my files for a fee?
Only if a decryptor already exists or the company pays the attackers for you. Some "ransomware recovery" services advertise that they can decrypt families with no known flaw; in practice they negotiate with the attackers and add their own fee. Others use the same free tools listed on No More Ransom.
Before you hire anyone, ask in writing how they will recover the files, whether they will contact the attackers and what happens if they fail. A legitimate service answers clearly. If a free decryptor exists for your family, you can run it yourself.
How did Rigj virus get on my computer?
The way Rigj virus spreads has not been documented yet, so look at your own recent activity. On home PCs, ransomware most often comes with cracked programs, game cheats, key generators and fake updates, or with an e-mail attachment that was opened. On business networks, attackers usually log in through Remote Desktop with a stolen or guessed password.
Think back to what was downloaded or installed in the days before files that end in .rigj and no longer open, and check the Downloads folder and Installed apps sorted by date. Keep anything suspicious for your report, but do not run it again.
Is Rigj virus the same as other ransomware with a similar name?
Not necessarily. Ransomware names come from the file extension, the note or a word in the code, so unrelated families often end up with similar names, and one family can appear under several names. The difference matters: a decryptor or advice for one family does not fit another and can damage files.
Compare the ending added to your files and the exact name of the note with the summary table at the top of this guide, then upload the note and one encrypted file to ID Ransomware from a clean device. If the result names another family, follow the guide for that family instead.
Can I just remove .rigj from the file names?
You can try it on a copy, but for real ransomware it will not help. The .rigj extension is only a label; the file content has been scrambled with a key the attackers hold.
If a renamed copy opens normally, the malware only renamed files, which happens with some fake ransomware, and you can rename the rest back. If it does not open, leave the files as they are. Renaming encrypted files can confuse a decryptor later, so always work on copies.
Can I delete _readme.txt?
Yes, the note itself is harmless text and deleting it does not affect your files. Keep at least one copy first, outside the infected PC. _readme.txt contains your personal ID and the attackers' contact details, which identification services use to tell which family encrypted your files, and which a decryptor may need later.
Police reports also ask for it. Once you have saved a copy, you can remove the notes from every folder after the ransomware program has been removed and your files are restored or backed up.
Will Fortect remove Rigj virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Rigj virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Encryption (read October 6, 2026)
- Dieviren: Dieviren (read October 6, 2026)
- CSOonline: Ransomware explained: How it works and how to remove it (read October 6, 2026)
- CISA: StopRansomware (read October 6, 2026)
- No More Ransom (read October 6, 2026)