
URL:Phishing: what the Avast and AVG alert means and what to do
URL:Phishing is the name Avast and AVG show when they stop a connection to a web address they judge to be a fake page; it is a verdict on the address, not a program on your PC. Find out whether the page, Avast or your PC is the problem before you remove anything.
Facts checked October 13, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove URL:Phishing yourself 4 steps, about 12 minutes, no software needed.
Start the steps
URL:Phishing: summary
| Type | An Avast or AVG block on a web address, not a program; the address can be a fake page, a hacked page or a clean one flagged by mistake |
|---|---|
| Risk | Medium until you know what the address is; high if it came from a message you did not expect and you entered details |
| Symptoms | A window saying Threat secured and the name URL:Phishing, and a page that will not load; nothing else in most of the cases we read |
| How to get rid of it | Find out whose problem it is; clean up the PC (browser reset, uninstall, full and offline scans) only if the cause is on it; site owners report a false positive to Avast |
| Our check (6 October 2026) | No PC test and no site to test; we read four forum cases, one Avast employee reply and two guides |
| First seen | Our guide of 8 October 2020; the name is older and we found no first-seen date |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Shown by | Avast and AVG, which share a detection engine according to unflagdomain |
|---|---|
| Not to be confused with | URL:Mal and HTML:Script-inf, other Avast names for malware links and injected scripts |
| Name | URL:Phishing |
| Evidence | 0 write-ups by security sites; details still limited |
| Arrives as | |
| Pretends to be | A well-known company |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against four public Avast and AVG forum cases (2022 to 2026), an Avast employee's reply of June 2026, one third-party guide for site owners and the Chrome, Firefox, Apple, Microsoft and FTC pages. We ran no PC test, and the removal steps were not tried on a live infection.
What URL:Phishing is, and what it is not
URL:Phishing is the name Avast and AVG give to a web address they judge to be a fake page, and the "Threat secured" window is the product telling you it stopped the connection. It is a verdict about a page, not a program on your PC and not a virus.
- 1
What the window says
In our 2020 pictures both products show the same text: "We've safely aborted connection on" and the address, "because it was infected with URL:Phishing", with a green check mark and a "Threat secured" heading. The product ended the connection before the page loaded, so nothing from that page ran on your PC at that moment.
- 2
What the name means
A third-party guide for site owners, unflagdomain, describes URL:Phishing as an Avast threat name for a page judged to imitate another site, next to URL:Mal (a URL linked to malware) and URL:Blacklist (a reputation-only listing). Avast does not explain its names on a page we could read, so treat that as one outside source, not as Avast's definition.
- 3
Who shows it
Avast and AVG, which are both Gen Digital products. The same source says they share one detection engine, so a verdict cleared at Avast clears at AVG too. That is the reason the old guide found the same warning on both.
- 4
Where the decision is made
The verdict belongs to the address, and Avast keeps it in its own database. Resetting your browser or scanning your PC does not edit that database, which matters for the next chapters: you can fix a cause on your PC, but you cannot clear a wrong verdict from your side.
- Shown by
- Avast and AVG (Web Shield / web protection), with the text "We've safely aborted connection"
- What it labels
- A web address, not a file and not a process in Task Manager
- Is it a virus?
- No. It is a block on a page. The page may be a real phishing page, a hacked page or a harmless one flagged by mistake
- Platform
- Windows and Mac where Avast or AVG runs; the old guide gave steps for both
- Not the same as
- URL:Mal (malware link) and HTML:Script-inf (page with an injected script), which are other Avast names
So the first job is not removal. It is to find out whose problem it is: the site's, Avast's, or your PC's. The chapters below separate the three.
What does URL mean in the name URL:Phishing?
URL stands for Uniform Resource Locator, which is the web address you type or click, such as the text that begins with https:// in your browser's address bar.
It tells the browser which server to contact and which page or file to ask for. In the alert, the word URL says that the thing judged is an address.
In the name URL:Phishing, the part before the colon is the kind of object Avast or AVG checked, and the part after it is the verdict. So URL:Phishing means that Avast judged a web address to lead to a fake page that tries to collect logins or card details. It does not name a program installed on your PC.
This is why the alert can appear even though no file was found on your computer. The security program compared the address with its lists and rules and stopped the connection before the page loaded. Whether the verdict is right is a separate question, and the sections above show how to check the address and what to do in each case.
How to tell the URL:Phishing message is fake
How unwanted programs and fake links reach a PC
This is the part of the old guide that still holds. It explains why alerts can come with adware, and why they can come from one careless click.
- 1
Software bundling
A free program ships with extra programs the installer asks about in small print. The old guide said this is the usual route for unwanted programs and that developers use it on purpose because it helps them spread.
- 2
Email attachments and links
A message about an order, a payment or an account problem with a link or file. A link in such a message is the classic way to reach a fake page, and it is the case where the URL:Phishing block does its job.
- 3
Fake ads that redirect
An ad or a pop-up that sends you on to an unsafe page. The old guide said this is where the detection gets triggered even if you avoid insecure sites.
- 4
Unofficial download pages
The old guide warned that pages with questionable material can offer adware, trojans, worms or ransomware, and that you can lose files, sign-in details and money. Use the maker's own site or the Microsoft Store instead.
- 5
Custom install
If you must use an unofficial source, choose Advanced or Custom in the installer and untick every extra program. That is the only screen that lists them.
Check the address before you decide anything
Write down exactly what the window says before you click: the product, the address and the name. Then find out how you got to that address.
- 1
Copy the alert
Take a photo of the window. Note the product (Avast or AVG), the full address and, if the window shows one, the alert or detection ID. The 2026 case quotes one in the form of an ID followed by a date and time.
- 2
Ask how you got there
A link from a message you did not expect, an ad or a pop-up is a different case from an address you typed or a bookmark you use for years. Do not open the link again to look.
- 3
Ask someone who does not use Avast or AVG
Open the address on a phone or PC with a different security product, or ask the site's owner. The old guide's advice was to double-check with another engine. We agree, with one change: a clean result there does not clear the address.
- 4
Do not run two security products at once
The old guide said running a few at the same time can cause compatibility problems and more false alarms. Open Settings > Apps > Installed apps and look for a second product with live protection. Disable one fully before you test with the other.
- 5
Look the address up in a reputation checker
Sites like VirusTotal show what many scanners say about an address. A few detections from little-known vendors usually mean a false alarm; many names from well-known vendors do not.
- 6
Update the virus database
Open the product, find the update option and update. Avast's reply in June 2026 asked for exactly this once a wrong detection was removed, so an old database can keep an old verdict.
Keep unwanted programs and fake links away
The old guide's advice, with current details.
Do
- Keep one security product with live protection switched on. Microsoft Defender is built into Windows 11 and 10.
- Keep the browser, Windows and the security product up to date; the old guide said databases must be updated often so false alarms do not pile up.
- Download programs from their makers' sites or the Microsoft Store, and use Advanced or Custom install to untick extras.
- Treat email, message and ad links as unknown until you know who sent them; go to the site by typing its name yourself.
- Turn on multi-factor sign-in, and keep a backup of your documents on a disk you unplug, so a bad infection costs you a reinstall and not your files.
Don't
- Do not turn off Web Shield or add an exception to open a blocked address.
- Do not run two security products with live protection at once.
- Do not call a number or install a tool because a pop-up told you to.
- Do not trust a page because its address looks like the real one; the block exists because fake pages look real.
Is URL:Phishing dangerous? What the senders want
What we checked on 6 October 2026, and what we could not
There is no site of ours to test, because URL:Phishing is a label and any address can carry it. We read four public cases from Avast and AVG forums (2022 to 2026), one vendor reply, and two guides, and we ran nothing on a PC.
Our reading of the sources, 6 October 2026
- The block is a real product messageThe pictures from our 2020 report and the 2022 to 2026 forum posts all show Avast or AVG blocking an address with the name URL:Phishing.
- Wrong verdicts happenIn June 2026 an Avast employee wrote that the reported domain was checked and the detection was removed, and that the page was now marked clean. A site owner had found the trigger and fixed it a week earlier.
- Clearing takes timeThe same reply says the change can take up to an hour, and to update the Avast virus database afterwards. In a 2023 AVG thread a report filed through the form had no answer for days.
- What the page really wasIn the cases we read, the site owners say their pages are clean and name outside scanners (VirusTotal, Sucuri, URLVoid) that agree. We have no way to confirm that for any of them.
- Your own blocked addressNot tested. We do not know which address you were blocked on, so we cannot say whether it is a false alarm.
- A quiet result on another scannerDoes not clear an address. Phishing pages are often live for hours and then gone, or show different content to different visitors, so one clean check proves little.
Treat the address as unconfirmed until you know what it is Most of the cases we read look like wrong verdicts on sites that owners can vouch for, but we cannot show that for yours. Do not open the page by turning protection off. Look at who sent you there first. Nothing was tested on a PC, and one clean scan never clears an address.
Whose problem is it: the site's, Avast's or your PC's?
The old guide blamed adware on your computer. That is one cause, and the forum cases show at least two more. The table shows how to tell them apart in a few minutes.
| What you see | Most likely | What to do |
|---|---|---|
| One address is blocked, and it works on your phone without Avast or AVG | A verdict on that site: wrong, or right because the page was hacked or is fake | Do not open it. If it is a site you trust, tell its owner or use the report form |
| Many different, unrelated sites are blocked, or the alert appears when you open an ordinary site | Something on your PC is sending you to other pages or changing the page you load | Go to the plan: browser reset, installed apps, full scan |
| The alert appears right after you clicked a link in an email, an ad or a message | A real phishing link, caught in time | Close the tab, do not retry, report the message. See the chapter on what to do if you opened it |
| The same site is blocked for several people who use Avast or AVG, and fine for others | A verdict in the Avast database | Only the site owner can get it re-checked, through Avast's form |
| Pop-ups, new tabs or a changed search page appear along with the alerts | Adware or an unwanted browser extension | Plan, browser steps |
A case from 2022 shows why: a government webmail host was blocked for Avast and AVG users while the rest of the owner's hosts were fine and other scanners found nothing. The block followed the address, not the PCs. Another reader in the same thread said every address they tried gave the alert, which points to a problem on the PC or in the product instead. One thread cannot tell you which is yours.
How people met it, from 2020 to 2026
Our guide dates from 8 October 2020. The pictures below are from it, and the later entries are public forum posts.
8 October 2020
Our first guide
We described a false warning that stops a page from loading in Avast and AVG and advised a browser reset and a second scan. The picture shows the two windows side by side.
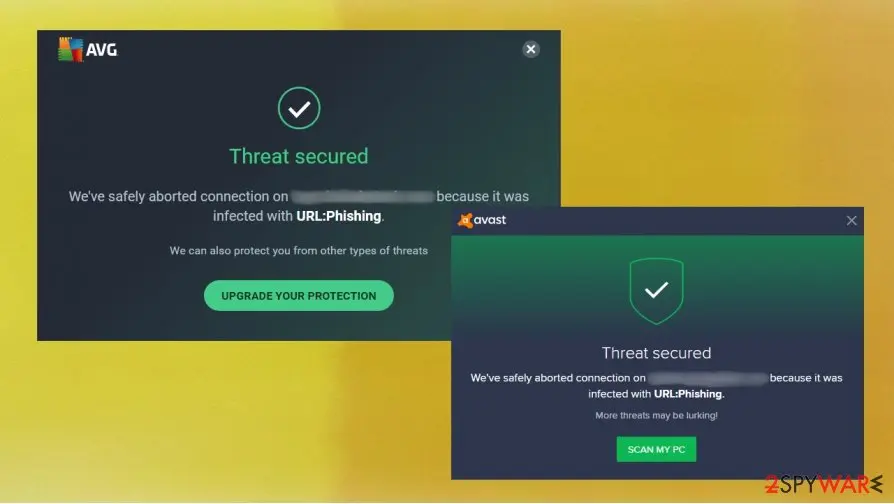
From our 2020 guide: the AVG window (large, with an Upgrade your protection button) and the Avast window (smaller, with a Scan my PC button). The address is blurred in the original. Not a screenshot we took. 2020
The same alert in the cover pictures
Our other 2020 pictures repeat the two windows. The cover picture adds the heading URL:Phishing and a stock photo of a person holding their head; it is an illustration. The third picture adds a red warning triangle, which neither product shows in the window.
Our 2020 illustration: the Avast and AVG windows again, with a red warning triangle that is not part of either product. Not a screenshot we took. November 2022
A webmail host blocked for Avast and AVG users
An administrator of a government webmail host wrote on the Avast forum that users of the two products were getting URL:Phishing, that his tests were clean, and that only Avast and AVG blocked that host. Forum volunteers told him only the Avast team can unblock it. In the same thread another owner said the alert appeared for every address they tried and that a report through the form had no answer yet.
July 2023
A shop app blocked on AVG
The developer of an app that ran on Shopify for years wrote on the AVG forum that its domain was flagged URL:Phishing and that shops could not show the app to customers who used the product. An AVG community agent pointed to the false positive form twice; the developer replied that the form had been sent and had had no answer.
June 2026
A login page cleared by an Avast employee
An owner wrote that Avast Web Guard had blocked a member login page for over a week, that forms had gone unanswered, and that his developer had found and removed the page element that triggered the verdict. After an Avast employee was asked, the reply (29 June) said the detection was removed, that it can take up to one hour, and to update the virus database if the block persists.
What it can cost you, and what it cannot
The old guide listed malware, identity theft and stolen money as the main dangers. Those belong to a real phishing page or to an infected PC, not to the label. The levels below say which cause carries which risk.
- High
A real phishing page
If you were sent to a fake sign-in or payment page and the block failed or you pressed on, your password or card number may be in someone else's hands. This is the case the product exists for.
- High
An infected or adware-ridden PC
Programs that redirect your browser can send you to fake pages again and again. The alerts are then a symptom, and the programs need removing.
- Medium
Turning protection off to get in
Following a forum tip to disable Web Shield or add an exception for the address removes the very check that stopped the page. Do it only for an address you have confirmed with its owner.
- Medium
Being cut off from a site you rely on
Owners in the cases lost customers and member access while a wrong verdict stood. For a reader the cost is a blocked bank, shop or work site.
- Low
The alert alone
In the pictures the product stopped the connection first. A single block, on its own, did not run anything on the PC.
What you may notice
The old guide said you may see fake messages, redirects and pop-up ads, and that Task Manager can show processes. Only the first sign is certain.
| Sign | What it tells you |
|---|---|
| A window saying Threat secured and URL:Phishing | The block itself. It names the address, so write it down before closing |
| A page that will not load, with a warning page from Avast or AVG instead | The product ended the connection. The page itself did not run |
| The alert on many unrelated sites | A sign to check the PC: browser extensions, installed apps, a changed start page |
| Pop-ups, new tabs or a changed search page next to the alerts | Adware. See the plan |
| Unknown names in Task Manager | A weak sign. Windows runs many background processes; check a name before you act, and do not link it to this alert on its own |
| Nothing else | The most common case in the posts we read. It does not prove a clean PC, and it does not prove an infection |
If you clicked the link or replied
The block normally stops the page. If you got past it or entered details somewhere else, treat it as a real phishing case.
- 1
Change the password from another device
Email first, then banking, then every account that used the same password. Turn on multi-factor sign-in; the FTC says it makes it harder for scammers to log in even if they have your password.
- 2
If you gave card or bank details
Call the bank on the number printed on your card and ask about the card. The FTC points US readers to IdentityTheft.gov for the steps that match the information lost.
- 3
If a link or attachment may have installed something
The FTC says to update the security software, run a scan and remove what it finds. Then follow the clean-up chapter above.
- 4
Report the message
The FTC lists forwarding phishing email to the Anti-Phishing Working Group and reporting at ReportFraud.ftc.gov. For text messages, forward to 7726.
What to do after the URL:Phishing e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you entered a password after clicking the link in the URL:Phishing message, treat that account as known to the sender.
Open the provider's real site by typing its address yourself, not through any link in the e-mail, and change the password there. Choose a new one you have never used before, and change it on every other account that shared the old one.
Then use the option to sign out of all other sessions or devices, if the provider has one. This works the same in any browser on Windows 11 and Windows 10.
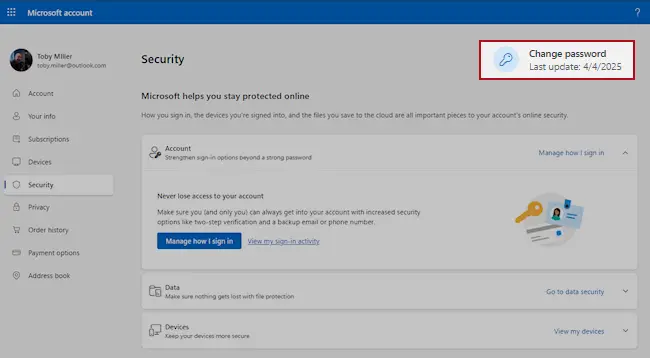
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
Two-step verification asks for a code from your phone or an authenticator app whenever someone signs in from a new device. A stolen password alone is then not enough to open the mailbox.
Turn it on in the security settings of the e-mail account first, then for the bank, shop and social accounts that send their reset links to that address.
While you are there, check the recovery e-mail and phone number and the forwarding rules, which attackers sometimes change to keep access. The settings pages look the same on Windows 11 and Windows 10.
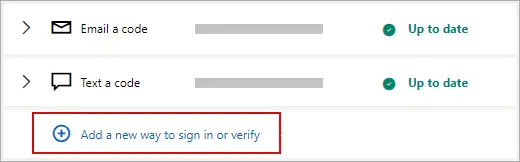
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Report the message instead of only deleting it. In Outlook choose Report > Report phishing, in Gmail the three-dot menu > Report phishing; the provider then blocks the same message for other people.
Do not reply and do not click anything else in it. On a work account, forward it to your IT team as an attachment first. Web mail and the mail apps on Windows 11 and Windows 10 offer the same options.
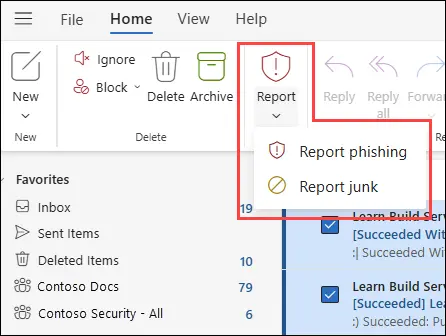
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A page that only asked for a password installs nothing, so most readers can skip this step.
If the URL:Phishing e-mail or the page it opened made you download or open a file, delete it and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
If the cause is on your PC: clean up in Windows 11 and Windows 10
The old guide said to reset the browser and then scan with an anti-malware program. Both steps are sound for adware on your PC, but neither removes a wrong verdict, so do them only when the table above points to your PC. We did not run these steps against a live infection; they follow Chrome, Firefox and Microsoft pages.
- 1
Close the page and stop opening it
Do not turn off protection or add an exception for the blocked address. Close the tab.
- 2
Uninstall programs you did not choose
Open Settings > Apps > Installed apps, sort by Installed on, and uninstall anything that appeared on the day the alerts began and that you do not recognise.
- 3
Reset the browser
Chrome: More > Settings > Reset settings > Restore settings to their original defaults > Reset settings. Google says your bookmarks and passwords are not deleted, and that extensions, cookies, the default search engine and the home page change to defaults.
- 4
Refresh Firefox
Open the menu, choose Help, then More troubleshooting information and click Refresh Firefox. Mozilla says it keeps bookmarks, history, passwords and cookies and removes extensions, themes, website permissions and search engines you added. It also leaves an Old Firefox Data folder on the desktop, which holds private data and should be deleted when you no longer need it.
- 5
Edge and Safari
Edge has a similar reset in its settings, and Safari has per-site settings for pop-ups and notifications under Safari > Settings > Websites, which Apple documents. We did not check Edge's menu names or Safari's extension list on a current version, so follow Microsoft's and Apple's own pages for those two.
- 6
Run a full scan
Open Windows Security > Virus & threat protection > Scan options, choose Full scan and Scan now. The old guide advised a second, different product for a second opinion. Run one product at a time.
- 7
Run Microsoft Defender Offline
In the same Scan options page choose Microsoft Defender Offline scan and Scan now. Microsoft says the PC restarts and the scan runs from a trusted environment outside the normal Windows kernel.
- 8
Check the result
Open Protection history in Windows Security and read what was found before you delete or restore anything.
Do not install a cleaner because a pop-up tells you to. The old guide ended with a recommendation of one powerful anti-malware program. The program should be one you chose yourself from its maker's site, and its alerts about your PC are not an answer to a verdict on an address.
If the site is yours, or you think the verdict is wrong
Only Avast can change the verdict. What you can do is fix a real cause and ask for a re-check.
- 1
Fix the cause first
If the site is yours, look for injected scripts, redirects and forms that look like another brand's. In the June 2026 case the owner found the one page element that triggered the verdict and removed it.
- 2
Report it to Avast
unflagdomain says to use Avast's Submit a website or a file for review page, choose False positive, set the type to URL, and give your email, the exact blocked address, the detection name and the alert ID. A form for AVG also exists at avg.com. unflagdomain says one accepted report clears both products.
- 3
Be specific
Say what the site is, what you removed and when, or that the page has not changed. No attachments, no threats, one report.
- 4
Wait, then update
Avast states no turnaround on that page. In the cases we read, forms stayed unanswered for days, and a request through the community forum produced an answer within four days (25 to 29 June 2026). After a detection is removed, the product can take up to an hour and needs an updated database.
- 5
Reader, not owner
If the site is not yours, tell its owner and keep protection on. The report form needs details only the owner can give.
Questions about URL:Phishing
What does URL:Phishing mean?
URL:Phishing is a threat name Avast and AVG show when they block a web address they judge to be a fake page. The window says the connection was safely aborted because the address was infected with URL:Phishing. It describes the address, not a file on your PC.
One outside guide, unflagdomain, says it marks a page judged to imitate another site; Avast gave no definition on a page we could read. The block can be right, because the page is fake or hacked, or wrong, because the page is clean and the verdict is mistaken.
Is URL:Phishing a virus?
No, it is not a virus. It is a block on a web address, and it is not a program that runs on your computer. The old name "URL:Phishing virus" is misleading because the product stopped the connection before the page loaded, so nothing from it ran at that moment.
What you still need to decide is whether the address was a real phishing page, a clean page flagged by mistake, or a page you were sent to by something on your PC. Our guide separates the three causes, and each has a different fix.
Is the URL:Phishing warning a false positive?
It can be, and the forum cases show that. In June 2026 an Avast employee removed the detection from a login page that the owner said was clean, and told him it could take up to an hour.
In 2022 and 2023 other owners reported the same on Avast and AVG. But a real fake page triggers the same wording. Ask how you reached the address.
If it came from an email, an ad or a pop-up, treat the block as correct and leave the page alone. A clean result from another scanner does not clear it.
How do I remove URL:Phishing from my computer?
Nothing called URL:Phishing sits on your computer, so there is nothing to uninstall for the label itself. If many unrelated sites trigger it, or pop-ups and new tabs come with it, something on your PC may be redirecting you.
Then uninstall programs you did not choose, reset the browser, and run a Full scan and a Microsoft Defender Offline scan from Windows Security. Chrome's reset keeps bookmarks and passwords and clears extensions and the home page. If one address is blocked and others are fine, the fix is a report from the site owner, not a clean-up.
Why does Avast block a website that I know is safe?
Avast keeps a verdict for each address and may keep it after a site is cleaned. unflagdomain lists causes such as a past hack recorded by the crawler, a reputation listing inherited from a shared host, a login or payment form that reads as deceptive to an automated check, and a third-party script on the page.
In June 2026 an owner removed the element he thought caused it and the page stayed blocked until Avast removed the detection. Only the site's owner can ask for a re-check, through Avast's false positive form.
How do I report a URL:Phishing false positive?
Use Avast's Submit a website or a file for review page, choose False positive, set the type to URL, and fill in your email, the exact blocked address, the detection name and the alert ID if the window showed one. Describe in two or three sentences what the site is and what you changed.
AVG has its own form, and unflagdomain says one accepted report clears both products. Avast states no turnaround; in the cases we read, answers took days. After the detection is removed, update the virus database and wait up to an hour.
Does resetting my browser get rid of the URL:Phishing alert?
It removes the alert only when the cause is something in your browser. The old guide told readers to reset the browser as the main step. A reset in Chrome returns the search engine, home page, extensions, cookies and site settings to defaults, and keeps bookmarks and passwords.
Firefox's Refresh keeps bookmarks, history, passwords and cookies and removes extensions and permissions. A reset does not change Avast's verdict on an address, so if only one site is blocked and others load fine, expect the alert to return until the verdict is changed.
Can I turn off Avast or AVG to open the blocked page?
You can, but you should not, unless you have confirmed the page with its owner by another route. The product stopped the connection because the address was on its list, and switching off Web Shield removes that protection for every page, not only the one you want.
If you must reach a site that you know is safe, open it on another device without Avast or AVG, or ask the owner to file the report. Do not add the whole domain to the exceptions list; if you add anything, add the one address and only after confirming it.
What should I do if I typed my password on a page that Avast later flagged?
Change that password from another device straight away, then change every other account that used it, starting with your email. Turn on multi-factor sign-in. If you entered card or bank details, call your bank on the number printed on the card.
If you clicked a link or opened an attachment, the FTC says to update your security software, run a scan and remove what it finds. Report the message: the FTC lists reportphishing@apwg.org for emails, 7726 for text messages and ReportFraud.ftc.gov.
Will Fortect remove URL:Phishing?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For URL:Phishing, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Avast Community: Avast blocking our login page as URL:Phishing, we fixed the issue but it's still blocked (25 to 29 June 2026) (read October 6, 2026)
- Avast Community: False Positive URL:Phishing (November 2022) (read October 6, 2026)
- AVG Community: False Positive URL:Phishing (July 2023) (read October 6, 2026)
- unflagdomain: Avast Flagged My Website: How to Report a False Positive (updated 24 September 2026) (read October 6, 2026)
- Google Chrome Help: Reset Chrome settings to default (no longer online) (read October 6, 2026)
- Firefox Help: Refresh Firefox - reset add-ons and settings (read October 6, 2026)
- Apple Support: Change Websites settings in Safari on Mac (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline scan in Windows (read October 6, 2026)
- FTC: How To Recognize and Avoid Phishing Scams (read October 6, 2026)