
X.bidswitch.net ads: what it is and how to remove it
X.bidswitch.net is a malvertising ad network that delivers redirects, pop-ups, and malicious advertisements to users' browsers. Discovered in 2020, this domain distributes malware through fake updates and auto-downloads of infected software.
Facts checked October 8, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If redirects to x.bidswitch.net keep coming back, a free scan can check extensions, programs and browser settings in one pass.
Do it yourself · free Remove X.bidswitch.net ads yourself 3 steps, about 9 minutes, no software needed.
Start the steps
X.bidswitch.net ads: summary
| Distribution | Various websites, deceptive ads, fake updates, drive-by downloads[3] |
|---|---|
| Name | X.bidswitch.net |
| Type | Redirect virus, adware |
| IP address | 35.211.114.141 |
| Symptoms | The website is blocked several times by security software; suspicious redirects and ads showing up during web browsing sessions |
| Dangers | Redirects to malicious websites can result malware infections or disclosure of personal information, monetary losses, installation of other potentially unwanted programs/malware |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| Domains | x.bidswitch.net |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 6 October 2020 |
| Facts checked | 5 October 2026 |
X.bidswitch.net in 2026: what we found
We opened x.bidswitch.net in a clean desktop Chrome browser on 4 October 2026 and clicked nothing. This is one visit from one location: ad pages often behave differently on a second visit, in another country, on a phone or after a click, and many hide from automated browsers, so a quiet result is not proof that the page is clean.
x.bidswitch.net · desktop Chrome · 4 October 2026
- Notification requestNone on this one visit.
- Pop-ups and new tabsNone on this one visit.
- Where it ledIt stayed on
x.bidswitch.net. - Ad networksNone found in the page.
Quiet on one visit The page made no request and sent us nowhere on this visit. That does not clear it: adware often shows nothing at first and sits quietly for a long time. What it showed you earlier may still be in your browser, so check the permissions below.
IPONWEB and BidSwitch: who runs the network behind x.bidswitch.net
IPONWEB is the advertising technology company that built and runs BidSwitch, a media trading marketplace for online ads.
In its filing of December 9, 2021, Criteo describes IPONWEB as a market-leading AdTech company with more than 20 years of work on technology for the open ad ecosystem. BidSwitch connects about 130 buyers of ad space with close to 150 sellers.
Criteo, a French advertising company, announced on December 9, 2021 that it had entered exclusive negotiations to buy IPONWEB for 380 million US dollars. The price was 305 million in cash and 75 million in Criteo shares. Criteo expected the deal to close in the first quarter of 2022, subject to regulatory approvals. So when you search for IPONWEB BidSwitch today, you meet the same exchange under the Criteo group.
What this means for you: BidSwitch is a real business that passes ad requests between companies, and x.bidswitch.net is one of its addresses, by our reading of the name. The address itself is not a virus. The problem our guide describes is the ads that travel through such exchanges: some of them redirect you, open pop-ups or push fake updates.
How to check yourself: if x.bidswitch.net shows up in your browser history, a blocker log or a security alert, look at the page you were on at that moment. A redirect from a trusted site usually comes from one bad ad. Repeated redirects on many sites, or new tabs that open by themselves, point to adware or a browser extension on your own computer.
Is X.bidswitch.net ads dangerous?
X.bidswitch.net: what changed since our report
October 2020
Our first report
We described X.bidswitch.net on 6 October 2020.
October 2026
Our new check
We opened the address again in a clean browser; the results are above.
From our report of Oct 2026 · not reviewed since
X.bidswitch.net - a redirect virus that could lead to malicious downloads
X.bidswitch.net is a domain that is associated with a variety of dubious activities on users' web browsers and computers.
The URL has been found on a list of ad campaigns that focus on malvertising - users can be exposed to pop-ups, in-text links, auto-play, JavaScript, and other types of malicious ads during their web browsing sessions. In some cases, users might encounter automatic downloads that would install a fake version of CCleaner.
While the so-called X.bidswitch.net virus is usually related to ads and redirects that might be encountered on numerous sites, it might also indicate that some malicious files or programs could have infiltrated the computer. Users reported that the anti-virus repeatedly attempts to block website's (x.bidswitch.net/sync, particularly) access to the PC.
Ad networks are very common and used by millions of websites every day - it allows the content developers to monetize on the displayed ads. While most people prefer not to see ads, they serve great benefit, as it permits creating websites and programs free of charge.
Unfortunately, not all advertisers are fair, and there are plenty of rogue ones. The shady ad networks undertake malvertising (which stands for "malicious advertising") - it uses ads to deliver malware to users' devices. X.bidswitch.net is related to this malicious business model.
However, it is also important to note that website authors who might expose visitors to X.bidswitch.net redirects are not necessarily guilty of the behavior. In some cases, the ad networks can be deceptive and disguise malicious activities in order to inject malicious ads into various sites.
When it comes to the user perspective, however, they can be exposed to very harmful content online due to malvertising. In case the web browser or other software is not fully updated, malicious JavaScript can exploit the vulnerabilities and inject malware as soon as the user lands on a particular site. It is also important to note that such redirects can also be caused by an adware.
Thus, to remove X.bidswitch.net behavior, you should first check your system for potentially unwanted programs that could have downloaded without the intention of doing so. You can follow the instructions we provide below - check for suspicious extensions and programs that might be hiding on your system.
The easiest way to do that is by scanning the computer with , , or another reputable security software. If you want to repair system damage sustained during a malware attack, use .
If you did not find anything suspicious on your computer after several scans, you should take precautionary measures to avoid X.bidswitch.net ads and redirects. Employ a powerful, updated security app, patch your operating system and all the software installed on it, and avoid visiting high-risk sites.
From our report of Oct 2026 · not reviewed since
Clicking ads might lead to malware installation on your computer
As previously noted, ad networks are complex and intricate ecosystems that are often exploited by cybercriminals.
As a result, even the most reputable websites might start displaying ads that are not secure. These ads can execute malicious code on users' computers as soon as they click on suchlike ads. Unfortunately, when a legitimate website gets hijacked by malvertising, there is little that users can do to protect themselves if no precautionary measures are undertaken.
As a general rule, you should support sites that are trustworthy. The occasions when malicious actors manage to infiltrate legitimate ad networks are relatively rare on reputable sites, although it does not mean that it can not happen.
Thus, you should employ an ad-blocking browser extension if you want to repel the attacks during your web browsing sessions. Ad-blocks can not stop all ads, so Google ads will be served on some websites regardless.
Without a doubt, you should not be clicking on random links on suspicious websites. For example, torrent and similar sites that distribute pirated programs and cracks are often boobytrapped with malicious ads - just one click can result in malware infiltration.
From our report of Oct 2026 · not reviewed since
More from our earlier report on X.bidswitch.net
- Ad-blocking extensions can also prevent the execution of malicious ads on the web browser
- Malware or adware infections can diminish the performance of your computer or cause serious stability issues.
Check your browser and PC
- Address:
x.bidswitch.net
How to remove X.bidswitch.net ads
How to stop the X.bidswitch.net redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Step 1: Check the browser's extensions
A browser that keeps landing on
x.bidswitch.netby itself usually has an add-on doing it. Open the extension list (chrome://extensions, edge://extensions, or Extensions and themes in the Firefox menu) and remove anything you do not remember installing.Coupon, PDF, new tab, search and video downloader add-ons are the usual suspects. Do this in every browser on the Windows 11 or Windows 10 PC.
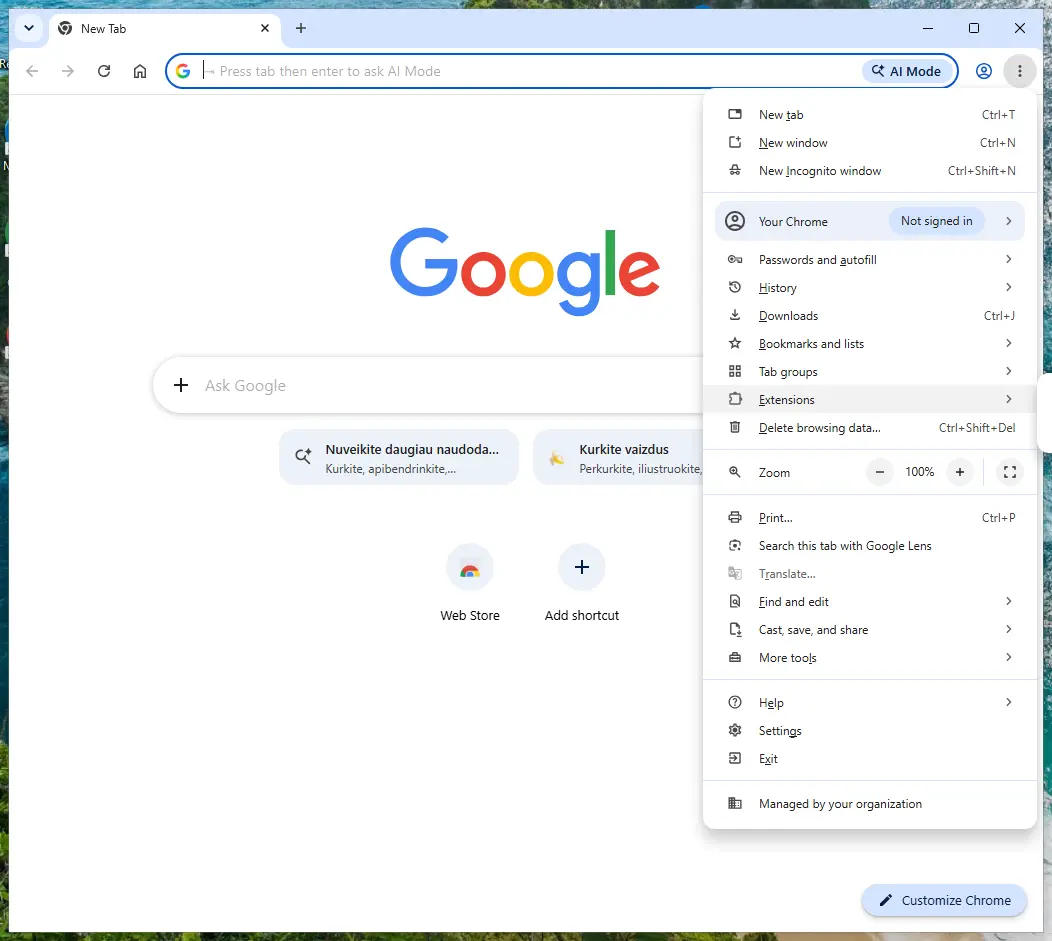
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Reset the browser if the redirects continue
When
x.bidswitch.netkeeps opening after the extensions are cleaned, reset the browser to its defaults. Chrome: Settings > Reset settings > Restore settings to their original defaults; Edge: Settings > Reset settings; Firefox: Help > More troubleshooting information > Refresh Firefox.A reset keeps bookmarks and saved passwords but clears site permissions, the start page and the search engine.
If every browser still redirects afterwards, the cause is a program in Windows 11 or Windows 10: check Settings > Apps > Installed apps for anything you did not install.
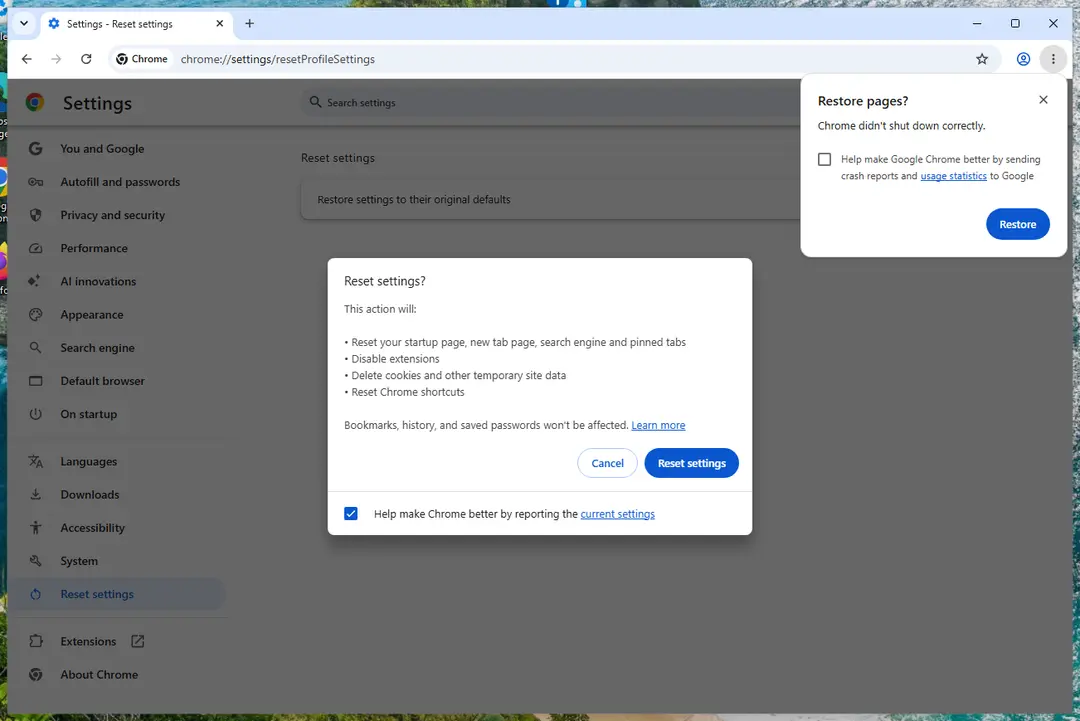
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Scan the PC if you downloaded anything from the ads
Most people who only saw the notifications can skip this step. If a notification or the page it opened made you download or run a file, delete the file and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
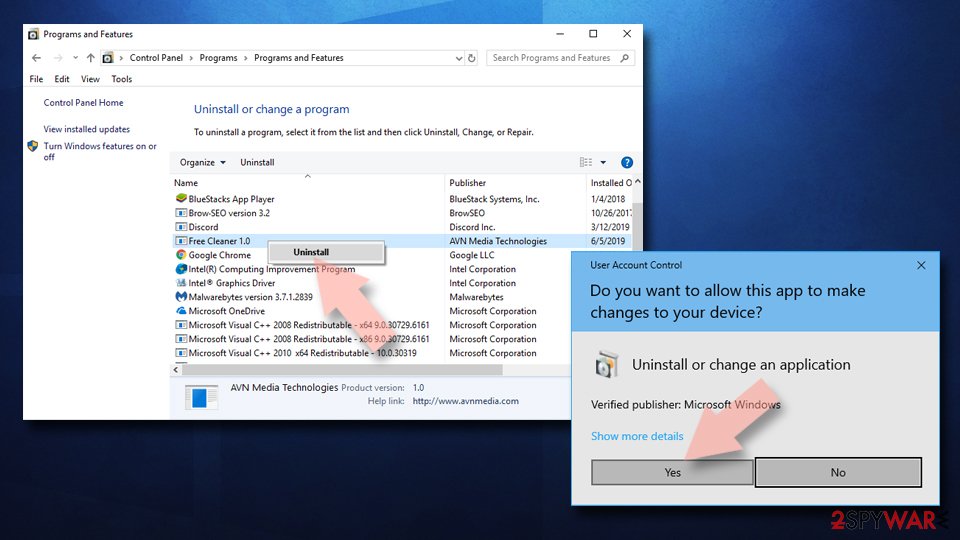
To uninstall potentially unwanted programs from Windows systems, follow these steps:
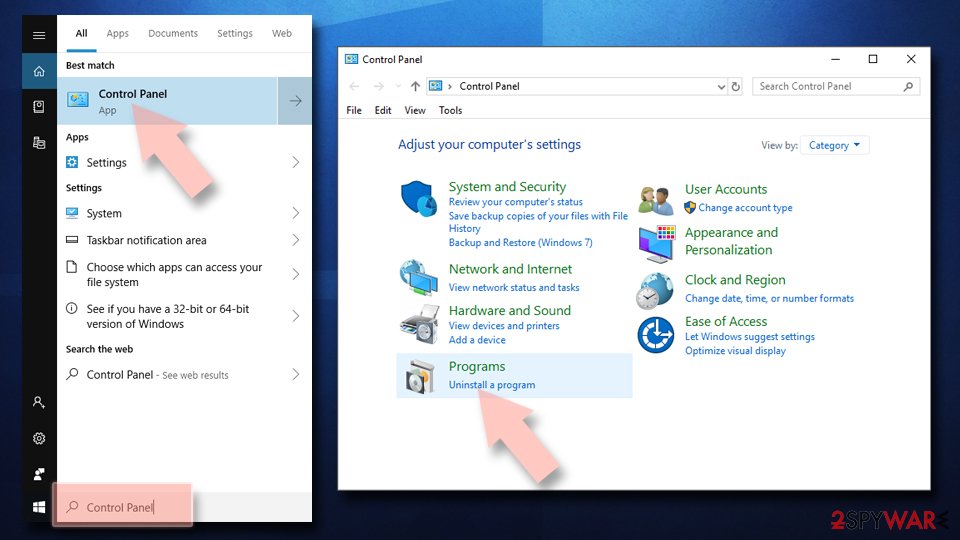
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
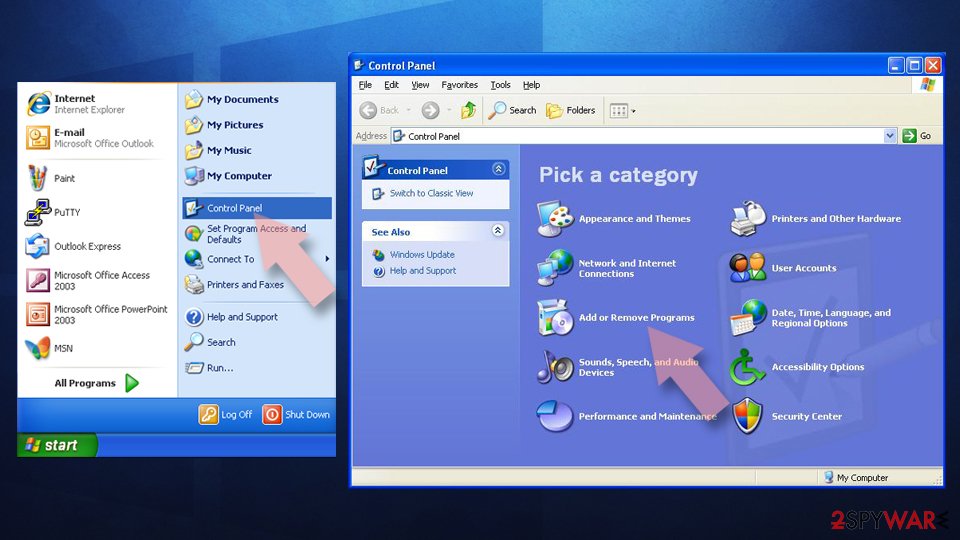
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Check Google Chrome for suspicious extensions or reset the browser to eliminate all the suspicious components:
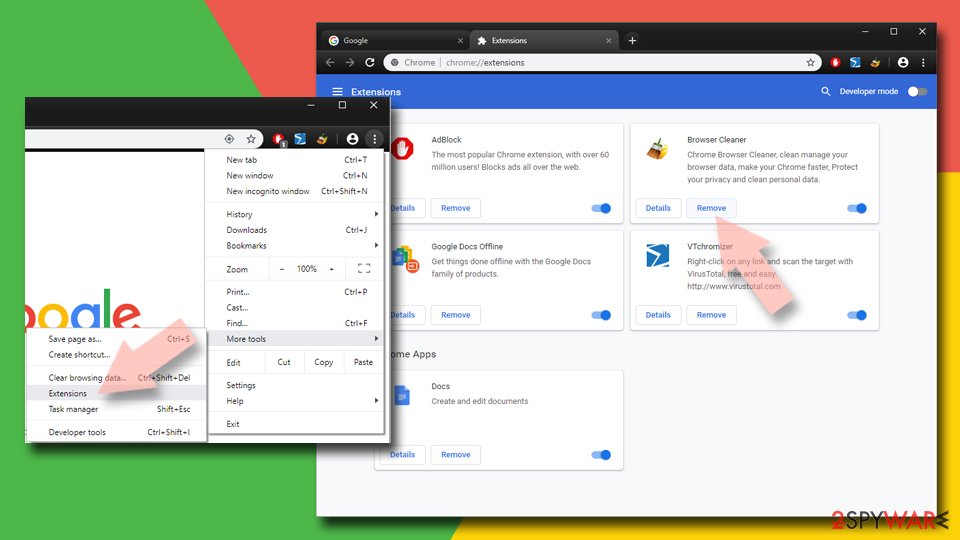
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
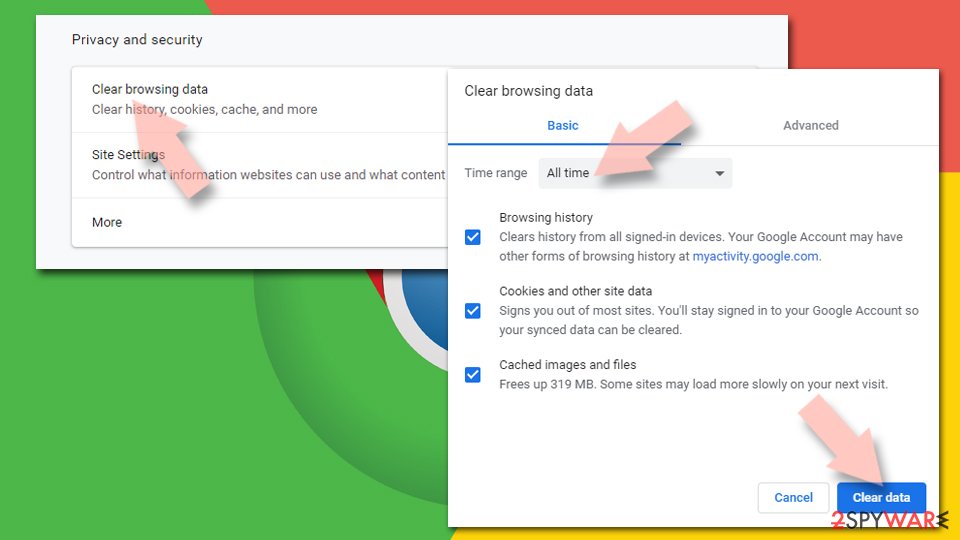
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
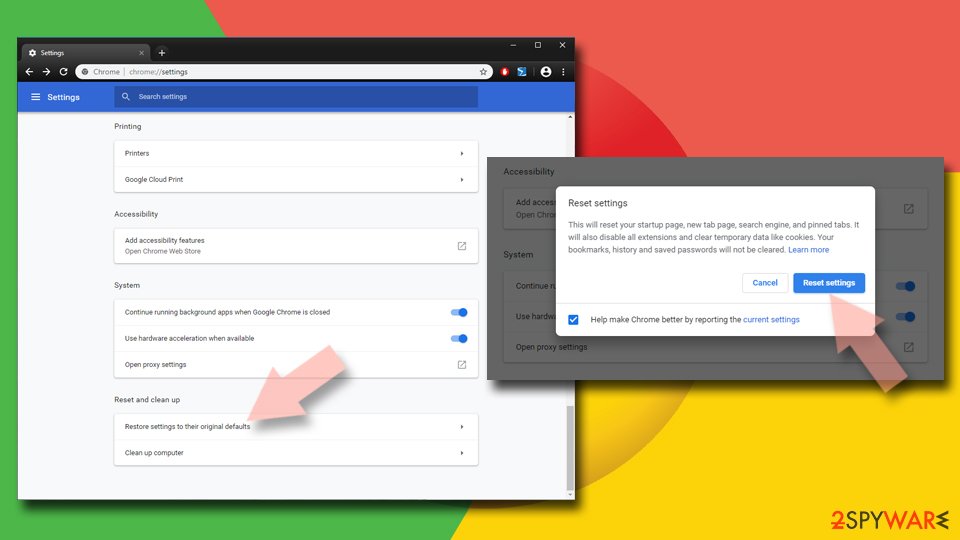
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
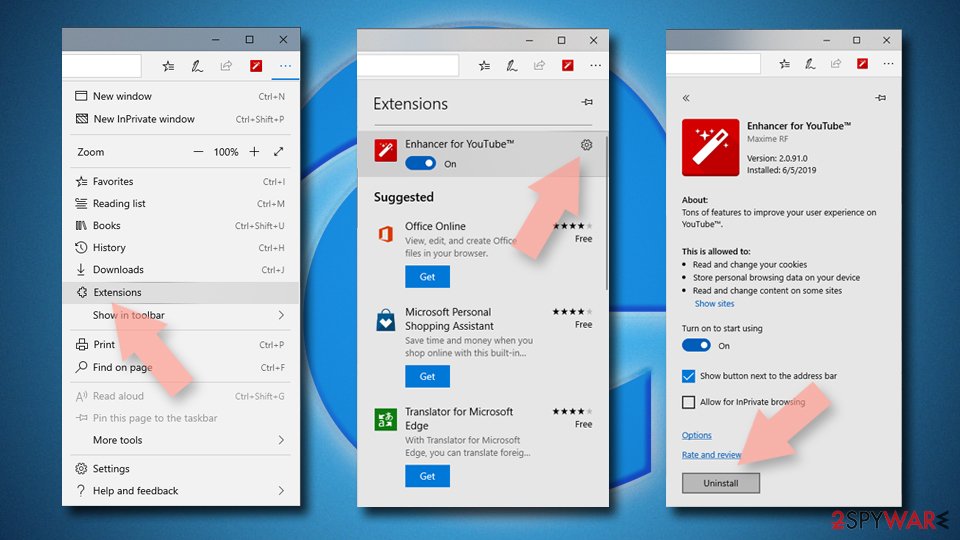
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
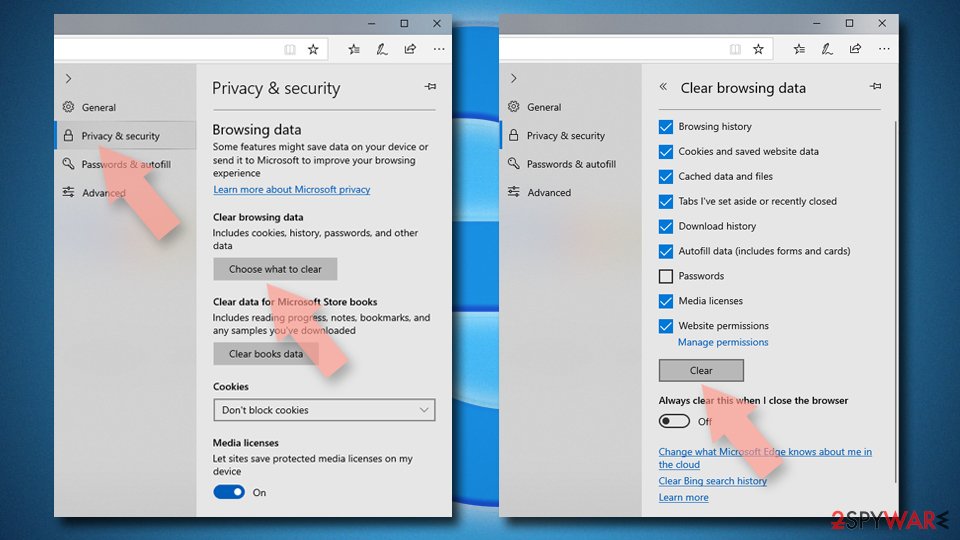
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
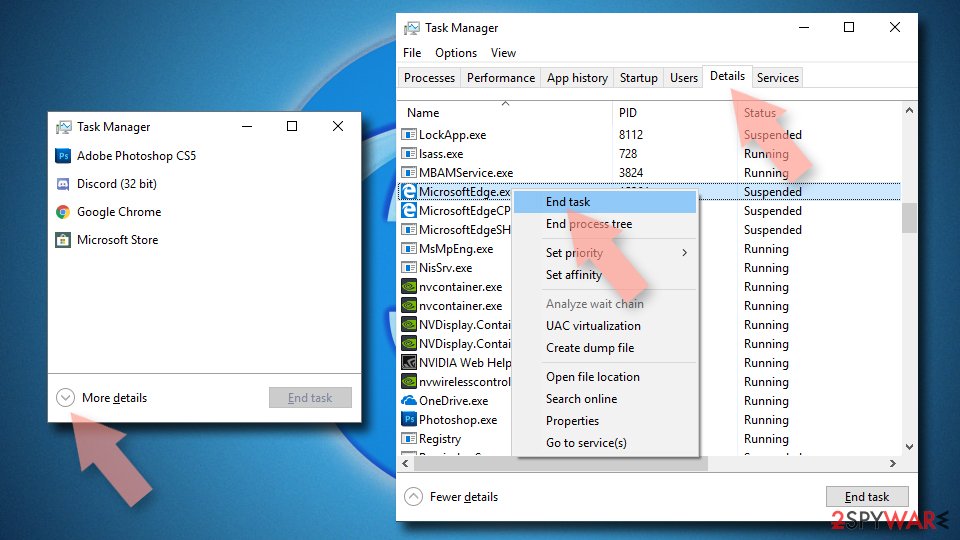
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
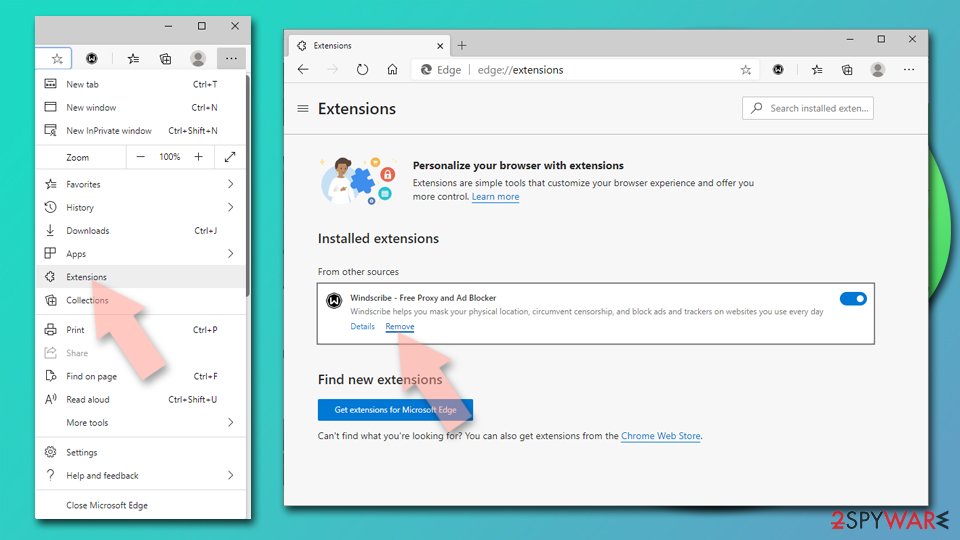
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
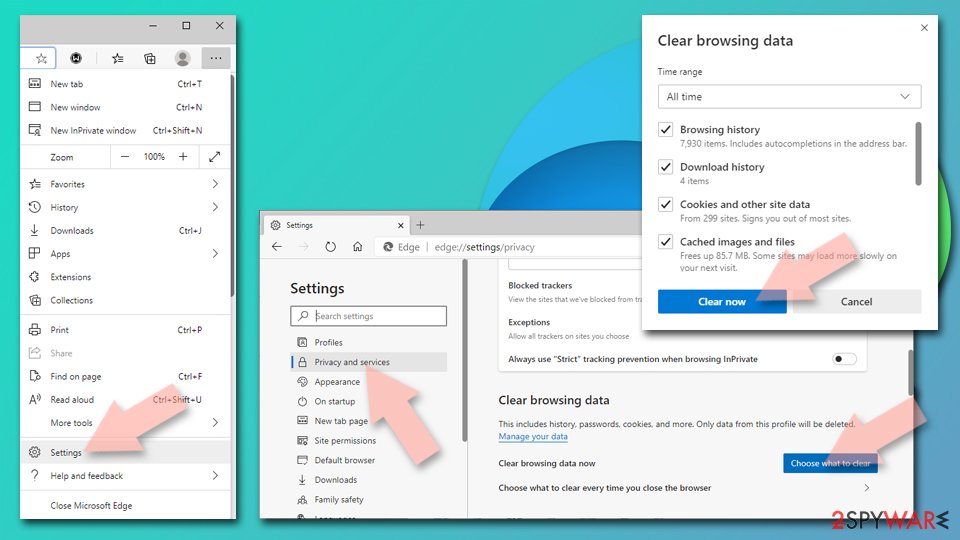
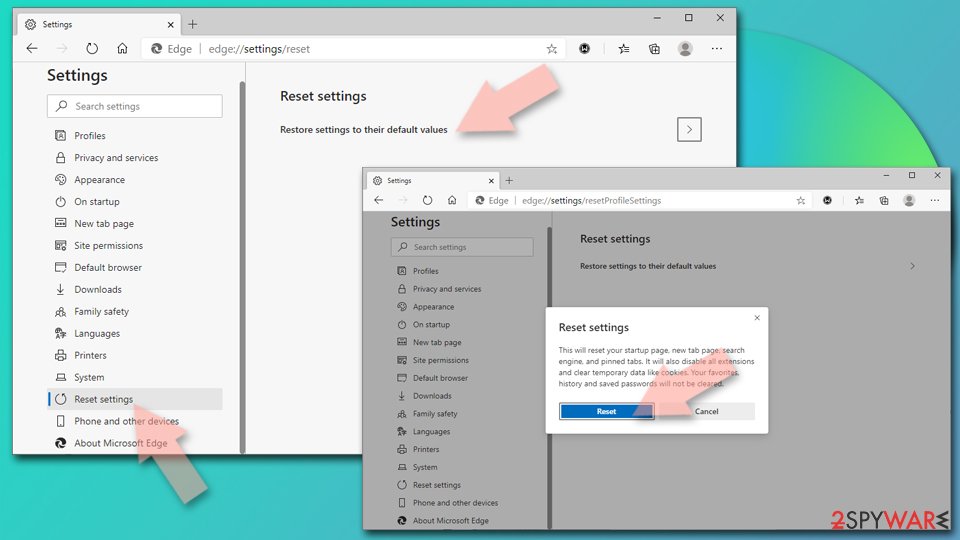
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
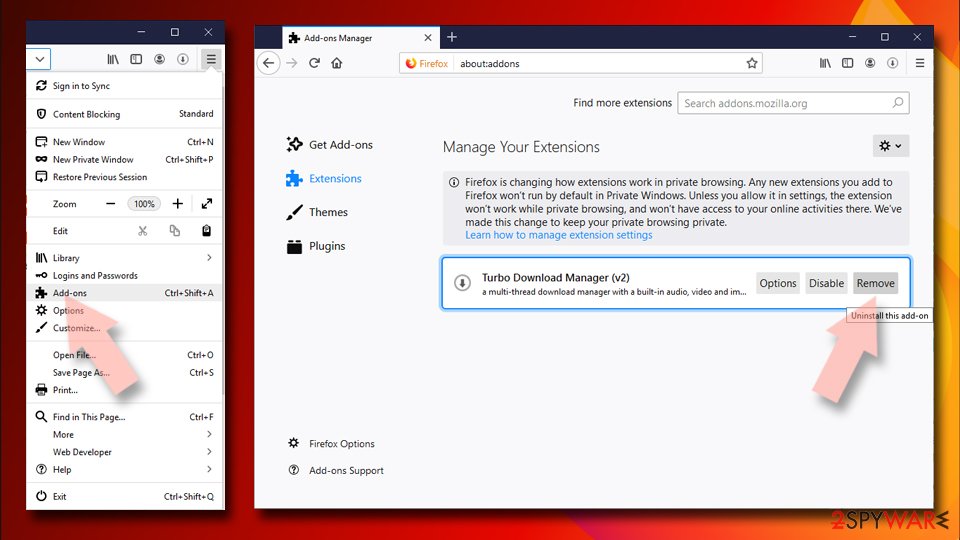
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
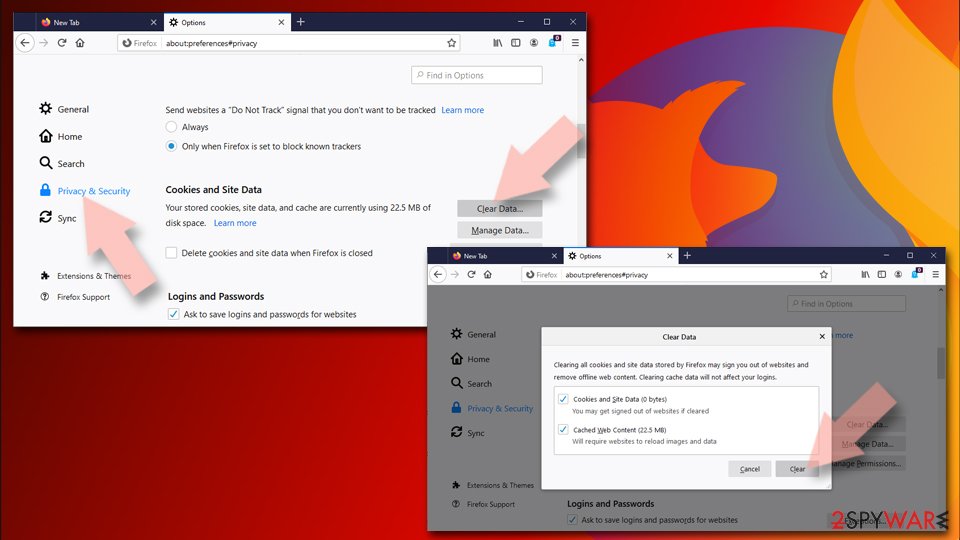
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
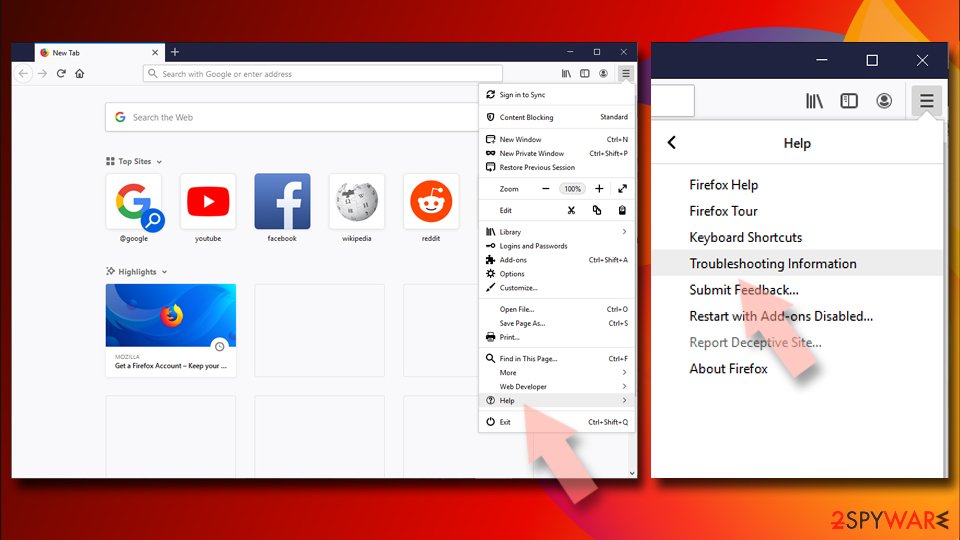
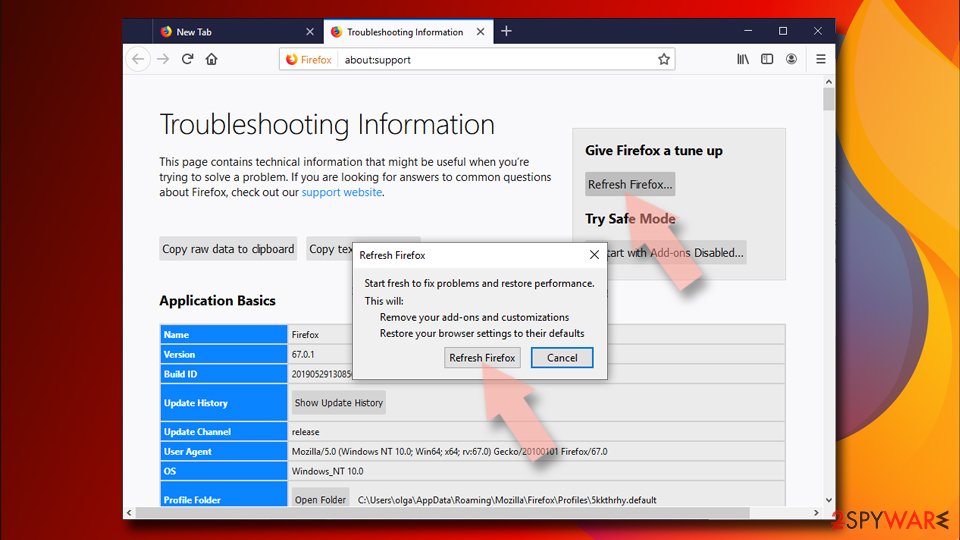
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
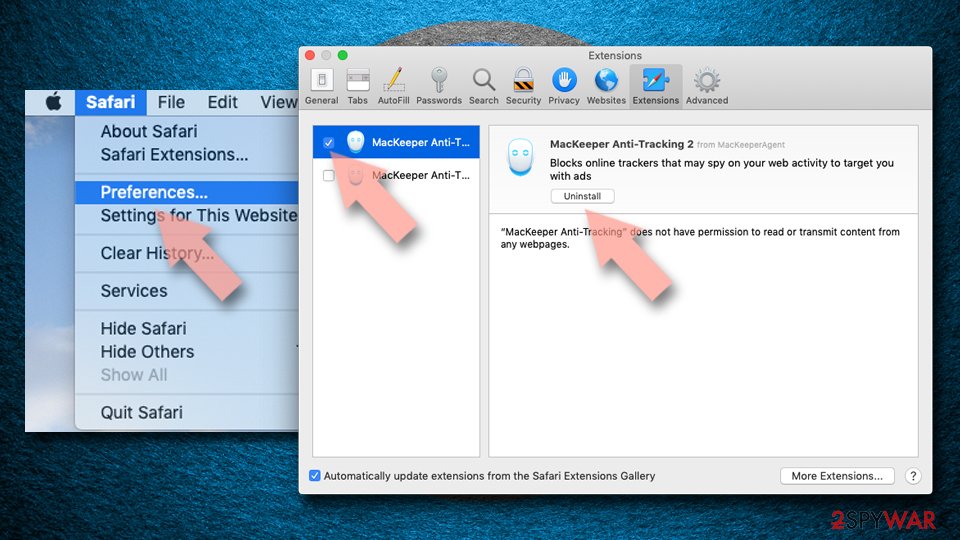
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
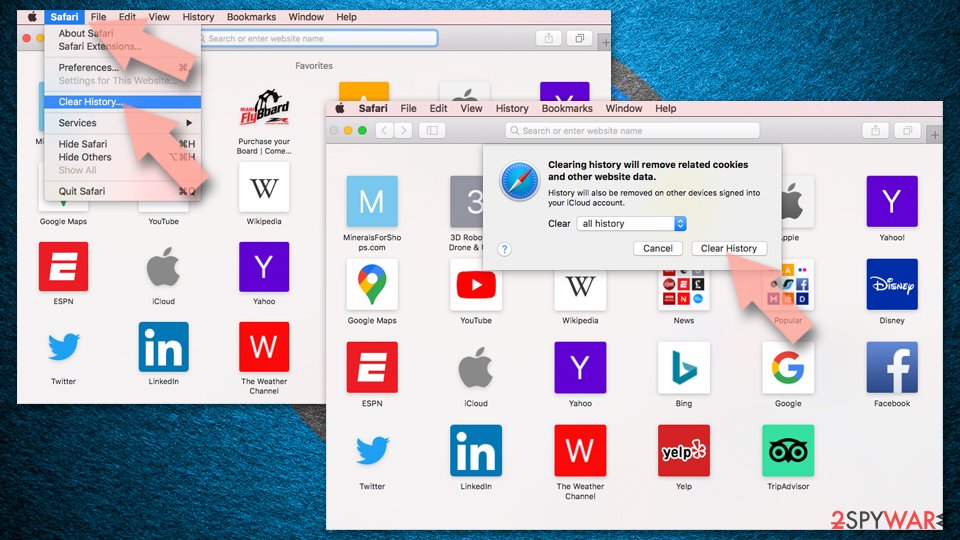
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
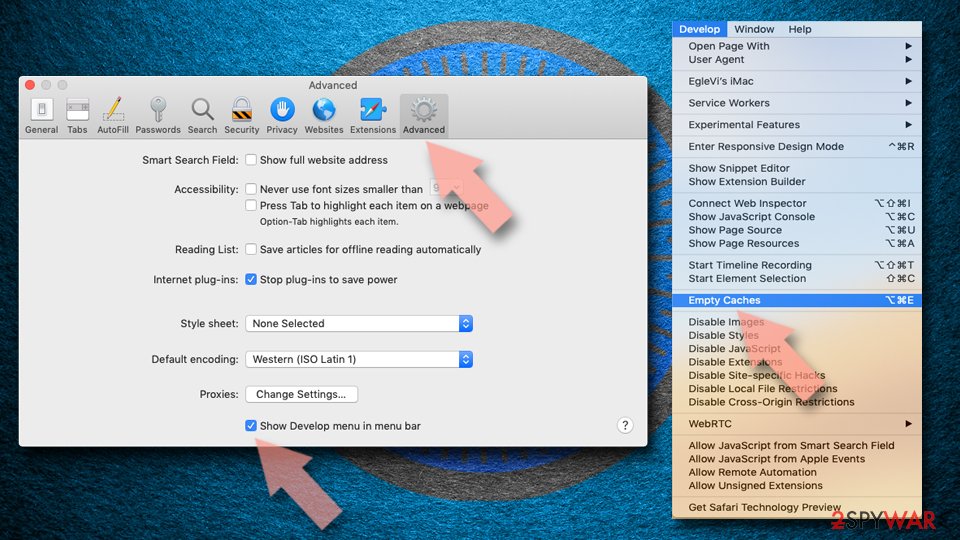
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Remove the unwanted application:
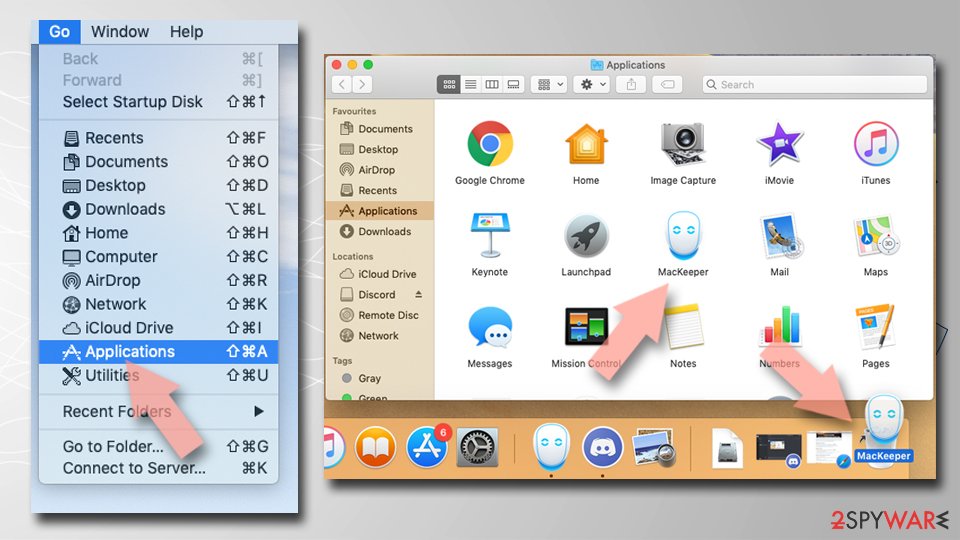
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
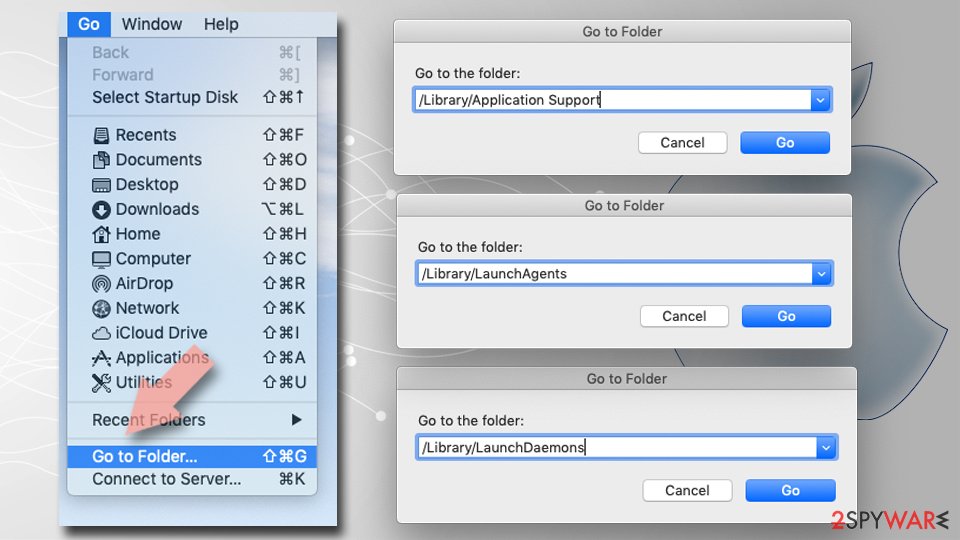
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
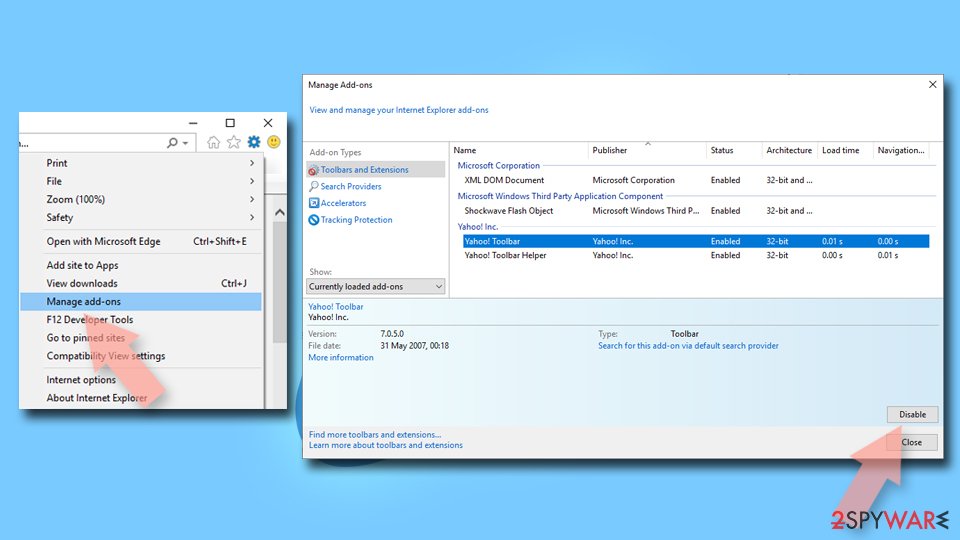
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
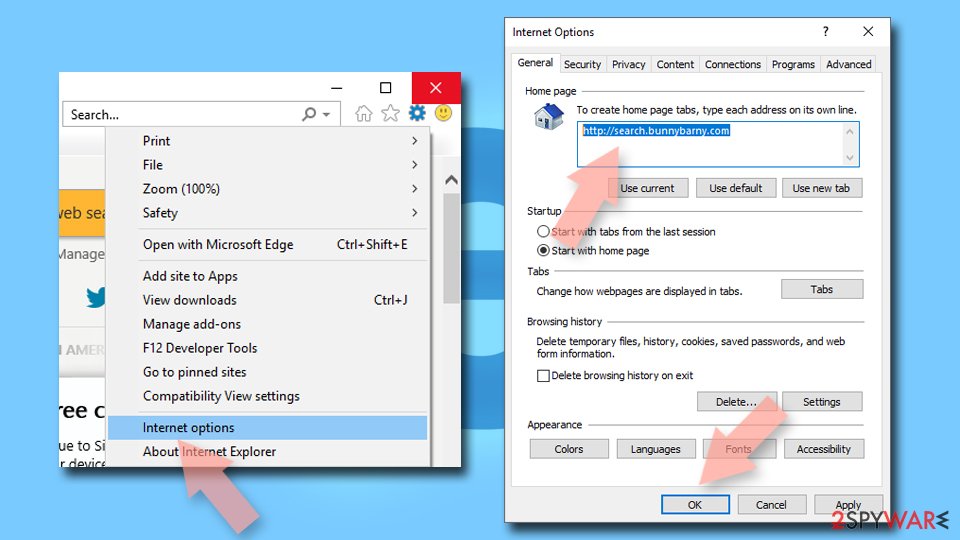
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
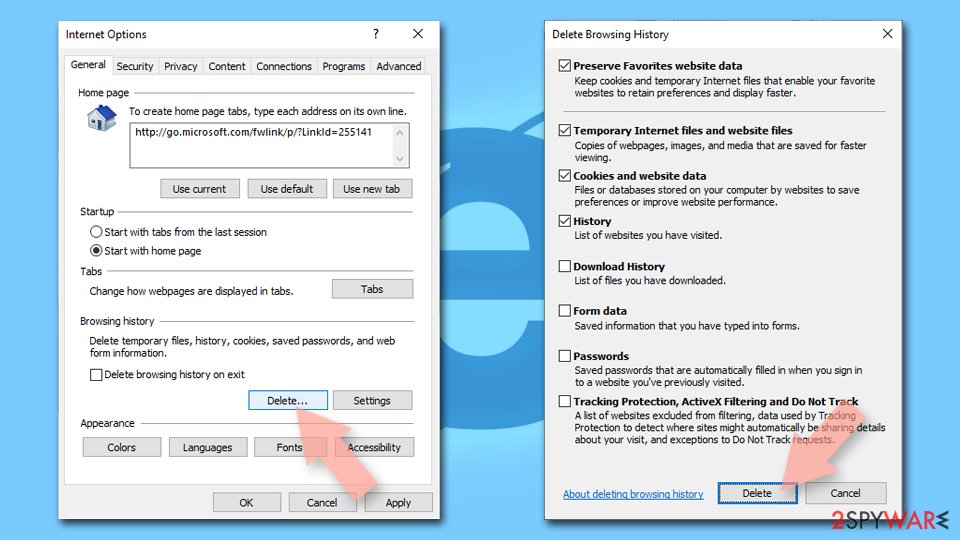
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
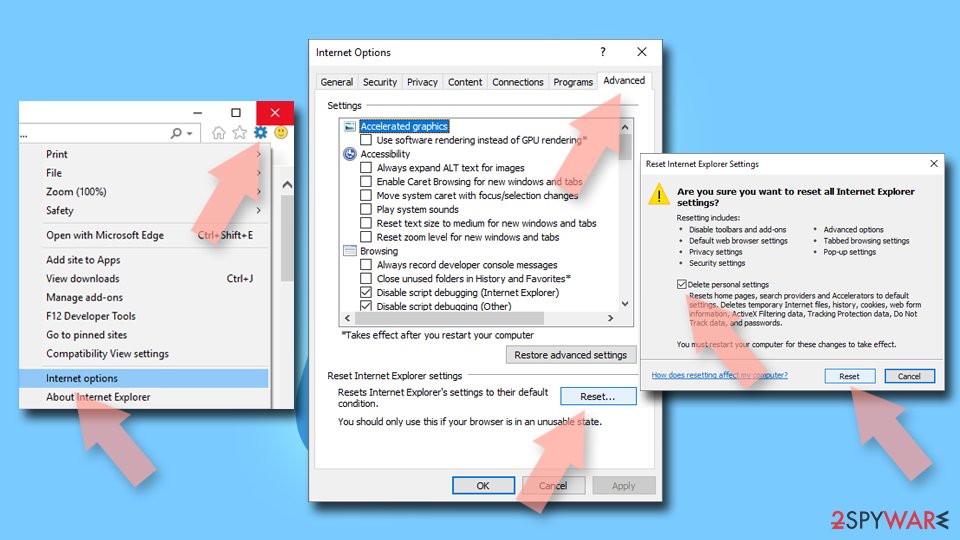
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
From our report of Oct 2026 · not reviewed since
X.bidswitch.net removal guide
There are several different scenarios in which you could encounter the X.bidswitch.net virus.
For example, if your web browser is vulnerable (unpatched), and you get redirected to a malicious site, it could infect your machine with malware automatically. As stated above, these redirects can also be caused by adware that was secretly installed on your PC with another application. Additionally, you can remove X.bidswitch.net redirects with powerful anti-malware, such as .
Nonetheless, it is important to understand that the threat is not adware but rather a domain used in a malware-delivery scheme. Therefore, X.bidswitch.net removal from Google Chrome, Safari, Mozilla Firefox, or another web browser can be performed with a powerful ad-blocker.
Questions about X.bidswitch.net ads
What is x.bidswitch.net?
X.bidswitch.net is a domain associated with malvertising (malicious advertising) campaigns. The 2020 guide identified it on lists of ad campaigns focused on malvertising. It is not malware itself but a malicious ad delivery network.
Websites and ad networks use x.bidswitch.net to display intrusive advertisements. Users see pop-ups, in-text links, auto-play videos, JavaScript ads, and other intrusive content. Anti-virus software frequently blocks access because of malicious activities.
The domain operated a sync endpoint (x.bidswitch.net/sync) that security software specifically targeted. Users may encounter x.bidswitch.net through redirects from compromised websites or ad networks.
The 2020 guide noted that not all websites deliberately expose users to this network; some ad networks deceptively inject malicious ads. X.bidswitch.net functions as a distribution point for malicious ads rather than a single malware program.
Is x.bidswitch.net dangerous?
Yes, x.bidswitch.net presents real security risks to your computer and personal information. The 2020 guide classified it as dangerous due to malvertising and malware distribution. Ads through x.bidswitch.net can exploit browser vulnerabilities to install malware without clicking.
Users reported anti-virus repeatedly blocking access due to attempted fake software downloads, particularly fake CCleaner versions. Clicking ads may result in malware infection, phishing, or unwanted program installation.
Redirects from x.bidswitch.net lead to websites hosting malicious content. Personal information can be exposed through JavaScript ads. The cumulative risk from repeated exposure increases infection probability.
Your machine can be partially compromised without noticeable symptoms. This domain continues serving malicious ads, posing ongoing danger. Vulnerability exposure increases daily as you browse sites served by these ad networks.
How did x.bidswitch.net get redirecting on my browser?
The redirects are caused by adware or PUP already installed on your computer. The 2020 guide noted this runs invisibly, injecting malicious ads into websites you visit.
Adware gets installed through freeware bundling, deceptive advertising, or compromised websites. Users who select Quick installation unknowingly install hidden adware. Deceptive websites trick you into installing ad-serving software.
High-risk websites commonly host malicious redirects. Drive-by downloads exploit browser vulnerabilities to install adware without consent. Browser extensions may deliver ads and redirects.
Some ad networks deceptively inject x.bidswitch.net ads themselves. Not all websites deliberately expose users. Removing underlying adware stops redirects.
Simply closing pop-ups is temporary; adware remains and shows more ads. Until you remove the PUP, x.bidswitch.net redirects continue. Antimalware scanning is necessary for complete removal.
What types of ads does x.bidswitch.net serve?
X.bidswitch.net serves various intrusive advertising types. The 2020 guide noted pop-up ads appearing suddenly over content, blocking your view.
In-text ads appear as highlighted words linking to advertisements. Auto-play videos start without permission, consuming bandwidth. JavaScript ads execute code in browsers, exploiting vulnerabilities.
Banners appear at top, bottom, or sides. These ads promote suspicious products or malicious websites. Some use shocking images designed to trigger clicks.
Malvertising ads contain malicious code exploiting browser vulnerabilities. Users report multiple ad types simultaneously overwhelming legitimate content.
Ad volume increases over time as malware installs additional components. Some ads redirect to other malicious networks. Fake CCleaner downloads appear as update notifications.
Clicking any ad risks infection or phishing. The persistent ad volume degrades browsing experience significantly. Ad-blocking extensions can prevent some ads from displaying.
Can clicking ads from x.bidswitch.net give me malware?
Yes, clicking ads from x.bidswitch.net creates significant malware infection risk. The 2020 guide warned that even simple ads can lead to malware installation.
Some ads execute malicious code without requiring clicks. Unpatched browser vulnerabilities allow silent malware installation through drive-by downloads. Malvertising exploits security holes in browsers and plugins.
Clicking serves double purpose: generating revenue and delivering malware. Downloaded files from ads may be trojans or fake software. Fake update notifications (fake CCleaner) are common infection vectors.
Clicking ads on legitimate websites can redirect to malware sites. The guide emphasized that professional websites don't control which ads appear; criminals compromise ad networks.
Your computer becomes infected within seconds of clicking malicious ads. Even redirects without clicking can install malware through JavaScript exploits. Avoid clicking any ads from x.bidswitch.net entirely.
How do I block x.bidswitch.net redirects and ads?
Blocking x.bidswitch.net requires removing underlying adware and preventing domain access. Install ad-blocking browser extensions designed to block malicious ads and redirects. These block known domains like x.bidswitch.net.
Configure browser security to block pop-ups and JavaScript from suspicious sources. Add x.bidswitch.net to browser's blocked site list. The 2020 guide noted anti-virus software can block access.
However, ad-blockers cannot block all ads. Most importantly, remove underlying adware causing redirects using anti-malware scans. Ad-blockers only prevent display, not adware removal.
Update your browser and plugins to patch vulnerabilities. Without removing the root cause, new redirects continue. Hosts file modifications can also block access.
Clear browser cache and cookies after removing adware. Monitor your browser for remaining redirects indicating incomplete removal. Consider multiple security tools for thorough protection against this and similar threats.
How do I remove x.bidswitch.net from my computer?
Removal requires eliminating underlying adware causing redirects, not just blocking the domain. Download anti-malware software on a separate computer if severely infected. The 2020 guide recommended full system scans to detect all malware.
Transfer the tool to a USB drive and scan your computer. The scanner identifies adware, PUPs, and files injecting x.bidswitch.net redirects. Remove all detected threats and restart.
After removal, configure browser settings to remove suspicious extensions and toolbars. Clear browser cache, cookies, and history. Reset browser to default settings if needed.
Check installed programs and uninstall suspicious applications. Scan again confirming complete removal. Install anti-malware software running continuously.
If redirects continue, the underlying adware remains. Multiple scans or professional help may be needed. Keeping software updated prevents future compromise.
Does x.bidswitch.net mean my computer is seriously infected?
X.bidswitch.net redirects indicate adware or PUP presence but not necessarily severe infections like ransomware. The domain is an ad network, not sophisticated malware.
However, adware causes compromised security needing cleaning. The 2020 guide warned that adware often bundles with other threats you may not notice.
Continuous exposure to malicious ads increases infection risk through drive-by exploits. Malvertising exploits browser vulnerabilities installing trojans or ransomware. Your computer faces phishing and identity theft risks from data-tracking components.
While x.bidswitch.net alone is not catastrophic, your system needs immediate cleaning. Professional antivirus scanning should detect hidden threats beyond visible adware. Multiple antivirus tools may catch different infections.
Regular system maintenance prevents future compromise. Keeping operating system and software updated significantly reduces risk. Your data may still be at risk from concurrent infections.
Will Fortect remove X.bidswitch.net?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For X.bidswitch.net, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Imperva: Malvertising (read October 5, 2026)
- AnyRun: sync (read October 5, 2026)
- Wikipedia: Drive-by download (read October 5, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Criteo: Criteo to acquire IPONWEB (SEC filing, Exhibit 99.1) (read October 8, 2026)