
Phoenix Browser Updater: what it is and how to remove it
Phoenix Browser Updater is an unwanted program that pretends to update your browser, shows ads and redirects you, and is linked to the webalta.ru hijacker family. End it in Task Manager, uninstall it from Windows, check the browser shortcuts, and clean each browser.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Not sure what sends your browser to webalta.ru? An automatic scan looks at the usual sources for you.
Do it yourself · free Remove Phoenix Browser Updater yourself 1 step, about 5 minutes, no software needed.
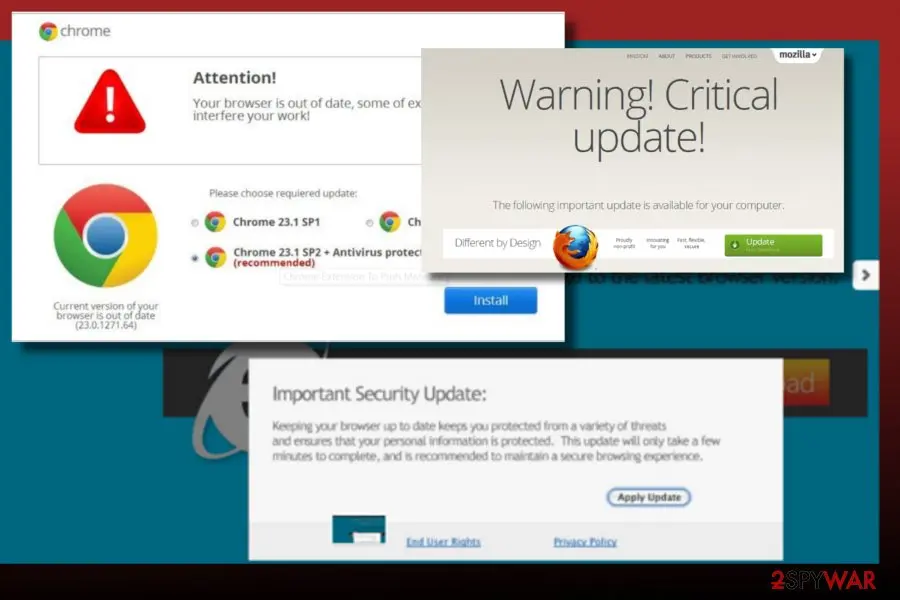
Phoenix Browser Updater: summary
| Type | Adware and browser hijacker, a potentially unwanted program that shows fake update messages and redirects; not ransomware and not a file destroyer |
|---|---|
| Risk | Medium: fake update boxes can lead to more unwanted software and the program sees the pages you open; no file damage reported |
| Symptoms | Pop-ups and banners, fake browser-update boxes, redirects to webalta.ru or other unknown domains, a start page that returns, PhoenixBrowserUpdater.exe running at start-up |
| How to get rid of it | End the process and uninstall it from Installed apps, delete its folder in AppData\Local, clear start.webalta.ru from the browser shortcut Target, run Microsoft Defender full and offline scans, clean each browser, change passwords |
| Our check (6 October 2026) | Not tested: no sample, and webalta.ru answered a plain request with a bot check (HTTP 403); older reports and our 2021 pictures read. A quiet result clears nothing |
| First seen | The file name appears in the EnigmaSoft list dated 31 December 2016; our guide of 7 July 2021 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 10 more facts
| Detection | Microsoft: no name known for Phoenix Browser Updater itself; the related family is BrowserModifier:Win32/Webalta. EnigmaSoft's SpyHunter reports 467 detections of the file |
|---|---|
| File | C:\Users\<username>\AppData\Local\Phoenix Browser Updater\Phoenix Browser Updater.exe, 764,024 bytes (EnigmaSoft list) |
| Linked domain | webalta.ru, registered 28 August 2024 in the .ru registry; Microsoft's Webalta entry dates from 2012 |
| Damage | Ads, fake update boxes and redirects, and a program that sees the pages you open; no file encryption or deletion reported |
| Distribution | Bundled with free software and download clients; fake update pop-ups (our 2021 guide, PCrisk) |
| Evidence | Our 2021 guide and pictures, the EnigmaSoft file list, Microsoft's Webalta entry, PCrisk and the .ru registry |
| Name | Phoenix Browser Updater |
| Domains | webalta.ru |
| Domain registered | 28 August 2024 |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Microsoft's Webalta entry, PCrisk, the EnigmaSoft file list, the .ru registry record and Microsoft and browser help pages. We had no sample and could not read webalta.ru past a bot check, so the behaviour and clean-up steps come from the reports and from our 2021 guide.
What Phoenix Browser Updater is, and what it is not
Phoenix Browser Updater is an unwanted program that presents itself as a browser updater. Our 2021 guide describes a browser extension plus a file called PhoenixBrowserUpdater.exe, and ties both to the Russian site webalta.ru. It is adware and a browser hijacker, not a real update tool from Google, Mozilla or Microsoft, and it is not the Phoenix ransomware.
- 1
A program arrives with something free
Our 2021 guide says it comes as an optional component of free software, installed when the reader accepts the Quick or Recommended option. PCrisk describes the same route for webalta.ru: redirects after free software installed through a download client.
- 2
It claims to keep the browser up to date
The 2021 guide says it tells readers that a browser update is waiting and offers the download, and that its maker sometimes calls it a "shopping assistant" or a tool that improves browser performance. The two pictures of that guide show the kind of fake update box it is known for.
- 3
The browser starts to misbehave
The guide lists pop-ups, banners, links and full-page ads, and redirects to suspicious domains in Chrome, Firefox, Internet Explorer and Edge. PCrisk adds a detail for webalta.ru: it writes start.webalta.ru into the Target field of the browser shortcut, so the start page returns after you change it.
- Kind of program
- Adware and browser hijacker, a potentially unwanted program; not a virus that encrypts or deletes files
- Where our 2021 guide put it
- An extension, and PhoenixBrowserUpdater.exe added to Windows start-up, with its folder in
%LOCALAPPDATA%\Phoenix Browser Updater - The file name in a vendor's list
- "Phoenix Browser Updater.exe" with spaces, in
C:\Users\<username>\AppData\Local\Phoenix Browser Updater\, 764,024 bytes (EnigmaSoft file list, updated 24 October 2025) - Linked domain
- webalta.ru, named in our 2021 guide and in the EnigmaSoft list, which files this exe under Webalta.ru
- Not to be confused with
- Phoenix ransomware (a file encryptor), the Webalta toolbar of 2012 and 2017 (a different file set), or a real browser update
Is Phoenix Browser Updater dangerous?
What we checked on 6 October 2026
We could not test the program itself: we have no copy of it, and no site of its own is named by any source. The one domain the sources tie to it, webalta.ru, answered our plain request with a bot check, so we saw nothing of what it shows today.
Phoenix Browser Updater and webalta.ru · reports, registry, Microsoft entry · 6 October 2026
- Our site testNot run in a browser. A plain request to http://webalta.ru on 6 October 2026 got a redirect to https://webalta.ru/ and then a Cloudflare page titled "Just a moment..." with HTTP status 403. We did not pass that check, so we saw no notification request, pop-up, redirect or ad network from the site on this one visit.
- The programNot seen by us in 2026. The extension, the exe, its folder and the ads come from our 2021 guide and from the EnigmaSoft file list; we ran no sample.
- The domainThe Russian registry (TCI) lists webalta.ru as registered on 28 August 2024 and paid until 28 August 2027. Microsoft's entry about Webalta dates from January 2012, so the name was in use years before this registration. We cannot say whether the present owner is the old one.
- MicrosoftMicrosoft Defender Antivirus has an entry named BrowserModifier:Win32/Webalta (published 22 January 2012, updated 15 September 2017). It describes a different file set, webaltaservice.exe. We know of no Microsoft detection name for Phoenix Browser Updater itself, and we scanned no sample.
- What a quiet result meansNothing. Adware can stay silent by country, device, referrer, a delay or a second visit, and a bot check hides the page from tools like ours. A scan that finds nothing does not clear a PC that shows the symptoms below.
Not cleared One request, no page content seen. We do not say the site is harmless or that it does anything today; the evidence is the older reports. Check your own PC with the steps below.
What the reports and our 2021 guide showed, and what has changed
22 January 2012
Microsoft publishes its Webalta entry
BrowserModifier:Win32/Webalta redirects the browser to webalta.ru, can fetch updates from update.webalta.ru, runs as a Windows service from
%USERPROFILE%\Application Data\Webaltaservice\webaltaservice.exe, and sends process information to stats.webalta.ru. This is the older family our 2021 guide links the updater to.31 December 2016
The earliest dated trace of the file name that we found
The EnigmaSoft list has a record for "Phoenix Browser Updater.exe", 764,024 bytes, last updated on that date, with one detection. Its newer record of 24 October 2025 has the same size and 467 detections reported by SpyHunter, which is the vendor's own tool, so treat the count as that tool's number.
7 July 2021
Our guide is published
We described an extension and an exe that push fake update messages and redirects, and said the page was aimed at Russian-speaking readers. The second picture of that guide shows a Russian-language news page behind the fake prompts.
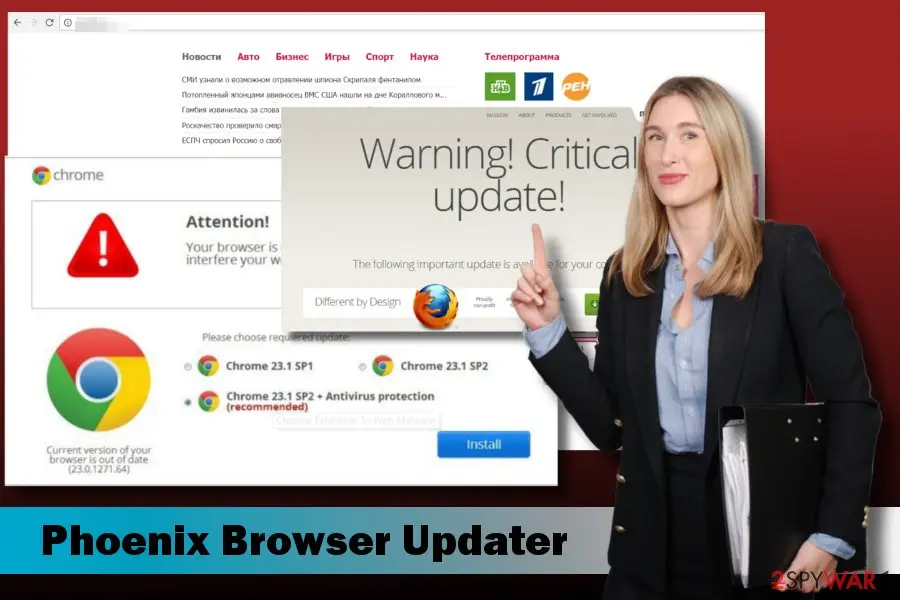
The second picture of our 2021 guide: a browser window with a blurred address and a Russian-language news page (headings Novosti, Avto, Biznes, Igry, Sport, Nauka), in front of the same fake update boxes, with the title "Phoenix Browser Updater". The woman is stock art. We do not know which site the blurred address belongs to, so the picture proves the style of the prompts, not a place. 18 January 2022
PCrisk updates its Webalta guide
It says redirects to webalta.ru follow free software installed through download clients, that Internet Explorer, Chrome and Firefox are affected, and that start.webalta.ru is written into browser shortcut targets.
24 October 2025
EnigmaSoft refreshes the file record
The vendor's list still names Phoenix Browser Updater.exe under Webalta.ru. This is the latest dated report of the file we found.
6 October 2026
We re-check the facts
No sample and no readable site to test. This page keeps what our guide reported, corrects what the sources do not support, and replaces the old Windows 7 and Internet Explorer steps with Windows 11 and 10.
Names that look alike, and what each one is
The name invites mix-ups. Our 2021 guide stated that this program has nothing to do with Phoenix ransomware; the table says which names belong to what, and which we could not tie to this program.
| Name | What it is | Tied to this program? |
|---|---|---|
| Phoenix Browser Updater | The unwanted updater described on this page | Yes: this is it |
| Webalta.ru, start.webalta.ru | A start page and search site that browser hijackers send people to | Yes: named in our 2021 guide and in the EnigmaSoft list, which files this exe under Webalta.ru |
| BrowserModifier:Win32/Webalta | Microsoft's name for a browser modifier that redirects to webalta.ru | Same domain, different file (webaltaservice.exe); no source says the two are the same program |
| Phoenix ransomware | A file-encrypting family | No: our 2021 guide said the updater cannot encrypt your files |
| TheWorld Browser, Chromium Updater, PMB Updater | Programs our 2021 guide listed as other unwanted installs | Reported by our 2021 guide only; we found no second source |
| Stellar Phoenix | Our 2021 guide listed it with the unwanted programs | We could not support this: no source we read links it to this program, so do not remove it on this page's word |
How it gets onto a PC
The sources agree on one route: free software whose installer carries an extra. Our 2021 guide adds a second: a malicious site visit or a pop-up ad you click.
| Route | What you would see | How to check |
|---|---|---|
| Free software with a bundled extra (our 2021 guide, PCrisk) | A setup with a Quick or Recommended option that clicks through everything; the extra is listed only under Custom or Advanced | Settings > Apps > Installed apps, sort by install date: look for an entry from the day you installed the free program |
| A download client (PCrisk) | A small downloader from a free-software site, which offers promoted programs in its own steps | Your Downloads folder, and the programs installed that day |
| A pop-up or fake update box (our 2021 guide) | A box that says the browser is out of date and offers an Install or Update button, like the pictures on this page | Close the tab; update the browser only from its own menu: About Google Chrome, About Mozilla Firefox, About Microsoft Edge |
Do
- Choose Custom or Advanced in every setup, so the whole package is unpacked and each extra can be unticked, as our 2021 guide advised.
- After installing something free, open Installed apps and look for an entry you did not choose, and scan the PC.
Don't
- Assume a PC outside Russia is safe: our 2021 guide says the pages look aimed at Russian-speaking readers, but a program that spreads by bundling can be installed in any country.
The risks, from most to least serious
This is a hijacker and ad program, not a ransomware or a trojan that destroys files. The risk is a program that changes the pages you open and leads you to fake updates, and that can open the door to more unwanted software.
- High
Fake update boxes that install more
Our 2021 guide warned that it can lead to pages full of malware, rogue software or services, and that it may reduce the PC's resistance to malware. The pictures on this page show the bait: a box that claims the browser is out of date. Updating a browser through a link in a web page is how real harm starts, so use only the browser's own About page.
- Medium
Pages and searches seen by a program you did not choose
A program that rewrites your start page and shortcuts can see which sites you open. Our 2021 guide quotes BedyNet.ru that it may leak search data; we could not read that source, and for the older Webalta family Microsoft states process information was sent to stats.webalta.ru. If you used banking or email while it was installed, change those passwords from a clean device and turn on two-factor sign-in, as the FTC advises after malware.
- Medium
A program that starts with Windows
Our 2021 guide says it adds an exe to start-up and runs several processes. That is a cost in time and memory on every start until it is removed.
- Low
Loss of files
No source says Phoenix Browser Updater encrypts or deletes files. Do not pay anyone who writes that your files are locked: that would be a different, real ransomware.
Check your browser and PC
Traces of Phoenix Browser Updater you can check
- Address:
webalta.ru
Files, folders and settings to look for
Check these places on your own PC. They come from our 2021 guide, the EnigmaSoft list, Microsoft's Webalta entry and PCrisk; a name in one list does not prove that the file on your PC is bad, so compare the folder and the date with when your problem began.
| Where | What to look for | Source |
|---|---|---|
%LOCALAPPDATA%\Phoenix Browser Updater | The folder of the program. Paste the path into the File Explorer address bar. The EnigmaSoft list gives the file as Phoenix Browser Updater.exe inside it, 764,024 bytes | Our 2021 guide; EnigmaSoft |
| Task Manager > Processes and Startup apps | An entry named Phoenix Browser Updater, or PhoenixBrowserUpdater.exe as our 2021 guide wrote it, and several processes at once | Our 2021 guide |
| Settings > Apps > Installed apps | Phoenix Browser Updater, a "Webalta Toolbar" entry, or anything installed on the day the browser started to misbehave | Our 2021 guide; PCrisk |
| Browser shortcut > Properties > Target | Text such as start.webalta.ru after chrome.exe, firefox.exe or iexplore.exe | PCrisk |
| Browser extension lists | An extension offering browser updates or a "shopping assistant" | Our 2021 guide |
%APPDATA%\WebaltaService and the service WebaltaService | webaltaservice.exe and webaltaservice.cfg, a Windows service started at each boot. Microsoft wrote Application Data; on Windows 10 and 11 that folder is AppData\Roaming | Microsoft, for the older Webalta family |
Do
- Compare the file's size and folder with the table, and right-click the exe > Properties > Digital Signatures to see whether it is signed and by whom; we have no source that says who signs it.
- Write down what you find before you delete it, in case you ask for help.
Don't
- Edit the Windows registry by hand on a guess: no source we read gives a verified list of keys for Phoenix Browser Updater, so we name none.
- Trust a name alone: a file called like a real updater can be real software. Check the folder first.
What it changes: reported and confirmed
Our 2021 guide listed browser malfunctions in general terms. The table says which change is reported, by whom, and that we have re-tested none of them.
| Reported change | How it shows | Status in 2026 |
|---|---|---|
| Pop-ups, banners, links and full-page ads | Ads on pages that normally have none, and boxes about fake apps and updates | Reported in our 2021 guide; not re-tested |
| Redirects to suspicious domains | The browser opens webalta.ru or another unknown address by itself | Reported in our 2021 guide; webalta.ru redirects are described by PCrisk and Microsoft |
| Start page back after you change it | start.webalta.ru is written into the browser shortcut Target | Reported by PCrisk for webalta.ru; not confirmed for this program |
| A file added to Windows start-up | Phoenix Browser Updater starts with Windows and shows several processes in Task Manager | Reported in our 2021 guide; the EnigmaSoft file path is in the user profile, not in Windows |
| More unwanted installs | Other programs appear that you did not choose | Reported in our 2021 guide; the names it gave are not confirmed by a second source |
| Data sent out | Search data and similar details leave the PC | Our 2021 guide quoted BedyNet.ru on cookies; we could not confirm it. Microsoft says the older Webalta service sent process information to stats.webalta.ru |
| File encryption | Your files locked, a ransom note | No: our 2021 guide said it cannot encrypt files |
How to remove Phoenix Browser Updater
How to stop the Phoenix Browser Updater redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Which browser shows the ads?
Check the browser shortcut
Right-click the Chrome shortcut on the desktop, taskbar and Start menu > Properties, and look at Target. Remove anything after the closing quote of
chrome.exe, such asstart.webalta.ru. PCrisk describes this change for webalta.ru.Remove extensions you do not recognise
Paste
chrome://extensionsinto the address bar and click Remove on anything you did not install yourself. The redirects come from a program in Windows, but it may have added an extension as well; remove any that offers browser updates or shopping help.Full procedure with screenshots: Remove a browser extension
Clear the site data
Press Ctrl + Shift + Delete, choose All time, tick Cookies and other site data and Cached images and files, and click Delete data.
Reset Chrome
Open More > Settings > Reset settings > Restore settings to their original defaults and confirm with Reset settings. This resets the search engine, start page, new tab page and pinned tabs, and turns off extensions and clears cookies; bookmarks and saved passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Check the browser shortcut
Right-click the Edge shortcut on the desktop, taskbar and Start menu > Properties, and look at Target. Remove anything after the closing quote of
msedge.exe, such asstart.webalta.ru. PCrisk describes this change for webalta.ru.Remove extensions you do not recognise
Paste
edge://extensionsinto the address bar and click Remove under anything you did not install yourself.Full procedure with screenshots: Remove a browser extension
Clear the site data
Open Settings > Privacy, search, and services > Delete browsing data > Choose what to clear, set All time, tick Cookies and other site data and Cached images and files, and click Clear now.
Reset Edge
Open Settings > Reset settings > Restore settings to their default values and confirm with Reset. Extensions are turned off and the start page goes back to default; favourites, history and saved passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Check the browser shortcut
Right-click the Firefox shortcut on the desktop, taskbar and Start menu > Properties, and look at Target. Remove anything after the closing quote of
firefox.exe, such asstart.webalta.ru. PCrisk describes this change for webalta.ru.Remove add-ons you do not recognise
Paste
about:addonsinto the address bar, open Extensions, and choose Remove from the three-dot menu of anything you did not install yourself.Full procedure with screenshots: Remove a browser extension
Clear cookies and site data
Open Settings > Privacy & Security > Cookies and Site Data > Clear Data, tick both boxes and click Clear.
Refresh Firefox
Open the menu > Help > More troubleshooting information and click Refresh Firefox. Add-ons and custom settings are removed and the home page goes back to default; bookmarks, history and passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Remove extensions you do not recognise
In Safari > Settings > Extensions, select anything you did not install yourself and click Uninstall. No source we read ties Ads by TS to Safari; this is a precaution for a Mac.
Clear the site data
In Safari > Settings > Privacy > Manage Website Data, remove the data of the site, or use History > Clear History > all history.
Check the Mac for apps you did not install
In Finder, choose Go > Applications, look for entries you did not install, and drag them to the Bin. In System Settings > General > Login Items & Extensions, remove unknown items. The Malwarebytes helper judged the Mac copy in the 2018 topic to be a different infection, so look for programs by their own names, not for Ads by TS.
Then, whichever browser you use
Step 1: Scan the PC if you downloaded anything from the ads
Most people who only saw the notifications can skip this step. If a notification or the page it opened made you download or run a file, delete the file and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
After removal: keep the ads from coming back
Remove the program, the start-up entry and the shortcut change
Our 2021 guide said you can remove it by hand: end the process, delete its files in AppData, and reset the browsers. The steps below are that route, updated for Windows 11 and 10 and the current browsers, and the browser tabs above hold the per-browser detail.
- 1
Find the program
Open Settings > Apps > Installed apps in Windows 11 (Apps & features in Windows 10) and sort by install date. Look for Phoenix Browser Updater, a Webalta Toolbar entry, and anything installed on the day the problem began (Uninstall a program or app in Windows On uGetFix).
- 2
End the process
Press Ctrl + Shift + Esc, find Phoenix Browser Updater (or PhoenixBrowserUpdater.exe) under Processes and Details, right-click it and choose End task. Under Startup apps set it to Disabled.
- 3
Uninstall it
Select the entry in Installed apps, open the three-dot menu and choose Uninstall; accept User Account Control if it asks. Restart the PC afterwards.
- 4
Delete what is left in AppData
Paste
%LOCALAPPDATA%into the File Explorer address bar, look for a folder named Phoenix Browser Updater and delete it if the uninstaller left it. If you see a folder called WebaltaService under%APPDATA%, it belongs to the older Webalta family; open Services (services.msc) and check whether a service called WebaltaService exists before you delete anything. - 5
Fix the browser shortcuts
Right-click each browser shortcut (desktop, taskbar, Start) > Properties and look at Target. Remove anything after the closing quote of
chrome.exe,msedge.exeorfirefox.exe, such asstart.webalta.ru, then click OK. PCrisk describes this change for webalta.ru; we have not seen it on a PC with Phoenix Browser Updater. - 6
Scan, then scan offline
Run a Microsoft Defender Full scan, then Microsoft Defender Offline scan (Windows Security > Virus & threat protection > Scan options), which runs outside the normal Windows kernel. Microsoft's entry for the Webalta family is BrowserModifier:Win32/Webalta; we know of no detection name for Phoenix Browser Updater.
- 7
Clean every browser
Open the extension list of each browser and profile, remove anything that offers updates or shopping help, clear site data, and set your own start page and search engine. If the redirects stay, reset the browser; the tabs above give the exact steps.
- 8
Change what it may have seen
If you signed in to banking, email or shopping while the program was installed, change those passwords from a clean device and turn on two-factor sign-in.
Do
- Ask for human help if the redirects return after a reset: keep the names of the folders and processes you found.
- Update a browser only from its own About page.
Don't
- Click Install or Update on a box that appears inside a web page, like the ones in the pictures above.
- Pay for a cleaner because a pop-up told you the PC is infected: the pop-up is a sales message, not a scan.
How to keep it from happening again
Do
- Choose Custom or Advanced every time you install software: it unpacks the bundle and lets you untick the extras, as our 2021 guide advised.
- Read each screen of a setup; if one adds a toolbar, extension or "updater", cancel.
- After installing something, scan the PC with Microsoft Defender in case an extra slipped in.
- Download programs only from the developer's site or the official store.
- Keep Windows and your browsers updated from their own menus.
- Check Installed apps now and then for anything you did not install.
- Keep a current backup of your files (File History or OneDrive), so an infection does not cost you your documents.
- On public networks a VPN hides your IP address from the sites you visit; it does not block ads or remove a program.
Don't
- Click through a setup with Next: the bundle rides on the Quick option.
- Install anything from a pop-up that says your browser, Flash or Java is out of date.
- Trust a scan that finds nothing as proof the redirects are gone, when the symptoms remain.
Questions about Phoenix Browser Updater
What is Phoenix Browser Updater?
Phoenix Browser Updater is an unwanted program that pretends to update your browser. Our 2021 guide described a browser extension and a file called PhoenixBrowserUpdater.exe that starts with Windows, shows ads, and redirects the browser to suspicious domains. It claims to warn you about pending browser updates, and its maker sometimes calls it a shopping assistant.
The EnigmaSoft file list keeps the file, with spaces in its name, under Webalta.ru, a site that browser hijackers send people to. It is adware, a potentially unwanted program, not a real update tool from Google, Mozilla or Microsoft.
Is Phoenix Browser Updater a virus?
Phoenix Browser Updater is not a virus in the sense of a file destroyer, but it is unwanted software you should remove. Our 2021 guide called it adware and a potentially unwanted program that causes redirects and pop-ups with messages about fake apps and updates.
The risk is the program that changes your browser and the fake update boxes it shows, which can lead to more unwanted installs. We found no report that it encrypts or deletes files. The EnigmaSoft list groups its file as a malware file with 467 detections reported by its own SpyHunter tool, so a security vendor flags it.
Is Phoenix Browser Updater the same as Phoenix ransomware?
No. Phoenix Browser Updater and Phoenix ransomware share a word and nothing else. Our 2021 guide said the updater cannot encrypt personal files or make other system changes directly, though it can expose you to dangerous domains and rogue software.
Ransomware locks files and asks for money; the updater shows ads, fake updates and redirects. If your files are locked and a note asks for payment, you have a different problem and should not pay or follow this page. If you only see redirects and update boxes, the steps on this page apply.
What is the link between Phoenix Browser Updater and webalta.ru?
Our 2021 guide said experts related the updater to Webalta.ru, and the EnigmaSoft file list files Phoenix Browser Updater.exe under Webalta.ru. Webalta is an old browser hijacker family:
- Microsoft's entry
- published in 2012
- says it redirects the browser to webalta.ru and runs a service called webaltaservice.exe
- PCrisk says it writes start.webalta.ru into browser shortcuts
The current registration of webalta.ru dates from 28 August 2024, so we cannot say the present owner is the old one. We did not see the site's content on 6 October 2026.
Why does my browser say it needs an update?
A box inside a web page that says your browser is out of date and offers an Install or Update button is bait, not a message from your browser.
Our 2021 guide's pictures show examples, with a Chrome box listing versions and a Mozilla box titled Warning! Critical update!. A real browser updates itself or through its About page:
- About Google Chrome
- About Mozilla Firefox
- About Microsoft Edge
Close the tab, do not click the button, and check Installed apps for a program you did not choose, because a program like this one can bring the boxes with it.
How do I remove Phoenix Browser Updater?
Remove the program first and clean the browsers second. Open Task Manager and end Phoenix Browser Updater, then open Settings > Apps > Installed apps in Windows 11 (Apps & features in Windows 10) and uninstall it.
Delete the folder %LOCALAPPDATA%\Phoenix Browser Updater if it is left, remove start.webalta.ru from the Target of your browser shortcuts, and run a Microsoft Defender full scan and the offline scan. Then remove unknown extensions in each browser, clear site data and reset the browser if the redirects stay, and change the passwords you used while it was installed.
Why do the redirects come back after I clean the browser?
Redirects return when the program that causes them is still in Windows. Our 2021 guide says it puts a file in start-up and keeps several processes running, so the browser reset alone only clears the symptom. PCrisk adds that start.webalta.ru can sit in the browser shortcut Target, which a browser reset does not touch.
Check Installed apps, Task Manager's Startup apps, and the Target field of every browser shortcut, including the taskbar one, then scan with Microsoft Defender and its offline scan. If it still returns, keep the folder names you found and ask for help.
Can Phoenix Browser Updater steal my passwords?
We have no report that Phoenix Browser Updater steals passwords. Our 2021 guide quoted BedyNet.ru that the program may carry cookies that leak search data and other non-personal details to third parties, and we could not read that source.
For the older Webalta family Microsoft states that it sent process information to stats.webalta.ru. A program that redirects your browser can see the pages you open, so if you used banking or email while it was installed, change those passwords from a clean device and turn on two-factor sign-in.
Is Phoenix Browser Updater only a Windows problem?
The sources describe Windows. Our 2021 guide placed an exe in Windows start-up, and the EnigmaSoft path is a folder in a Windows user profile, so the program itself is Windows software. Our 2021 guide's Mac and Safari steps are kept on this page as a precaution, because no source we read ties the program to a Mac.
A fake update box can still appear on a Mac or an iPhone as a web page; closing the tab and not clicking Update is enough, and nothing is installed by looking at it.
Will Fortect remove Phoenix Browser Updater?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Phoenix Browser Updater, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Microsoft Security Intelligence: BrowserModifier:Win32/Webalta (read October 6, 2026)
- PCrisk: Webalta.ru Virus (updated 18 January 2022) (read October 6, 2026)
- EnigmaSoft: Webalta.ru Files (Phoenix Browser Updater.exe records) (read October 6, 2026)
- TCI (.ru registry): WHOIS record for webalta.ru (read October 6, 2026)
- How-To Geek: PUPs Explained: What is a "Potentially Unwanted Program"? (read October 6, 2026)
- FTC: Malware: How to protect against, detect, and remove it (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline scan in Windows (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)
- Microsoft Support: Uninstall or remove apps and programs in Windows (read October 6, 2026)
- Google Chrome Help: Reset Chrome settings to default (no longer online) (read October 6, 2026)
- Mozilla Support: Disable or remove Add-ons (read October 6, 2026)
- Apple Support: Delete or uninstall apps on Mac (read October 6, 2026)