
Buran ransomware: what it is and how to remove it
Buran ransomware is the version of a cryptovirus that now is marketed as a RaaS. Usually, such ransomware-as-a-service threat operators (GandCrab, REvil, Sodinokibi) take 30 or 40 percent from those ransom payments based on the affiliate marketing scheme, but the VegaLocker virus developers give a discount taking only 25% from the threat distributors using their ransom-demanding creation.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like Buran usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove Buran ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Buran ransomware: summary
| Distribution | Email spam and malicious script injected document attachments are commonly used by ransomware developers, but this threat is known to mainly rely on Rig Exploit Kit as a vector for distribution. Many attacks also got successful due to the exploit of a common CVE-2018-8174 vulnerability |
|---|---|
| Damage | The new versions called Buran 2 can delete shadow volume copies, backup catalog, system state backups, and repeats those processes to ensure the file deletion. Additional changes and these facts make the file recovery even more difficult |
| Name | Buran |
| Malware type | Ransomware |
| Versions | Buran and Buran 2 that is in use currently |
| Extension | The file marker is formed with victim's unique ID and is placed one every file after encryption made them useless |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 12 more facts
| Family | VegaLocker ransomware |
|---|---|
| Ransom note | !!! YOUR FILES ARE ENCRYPTED !!!.TXT; the text is quoted in full below |
| Contact emails | recovery_server@protonmail.com and recovery1server@cock.li, polssh1@protonmail.com, polssh@protonmail.com, sanio.marino@aol.com |
| Detection names | No Microsoft detection name is known |
| Encrypted file extension | Not recorded in our earlier report |
| Decryptor | No free decryptor is known for this variant; check No More Ransom (nomoreransom.org) for updates |
| Type | File-encrypting ransomware |
| Symptoms | An unknown program in Installed apps and a ransom note left in folders |
| Evidence | 8 write-ups by security sites; no sample analysed yet |
| Free decryptor | No free decryptor is known (checked 7 October 2026) |
| First seen | 12 November 2019 |
| Facts checked | 7 October 2026 |
- Note file:
!!! YOUR FILES ARE ENCRYPTED !!!.TXT
From our report of Nov 2019 · not reviewed since
More from our earlier report on Buran
- Use anti-malware tools to remove Buran ransomware and make sure to fix virus damage, corrupted files using as it can run a scan on your Windows machine
- Buran is a stable offline cryptoclocker, with flexible functionality and support 24/7.
- Functional: Reliable cryptographic algorithm using global and session keys + random file keys; Scan all local drives and all available network paths; High speed: a separate stream works for each disk and network path; Skipping Windows system directories and browser directories; Decryptor generation based on an encrypted file; Correct work on all OSs from Windows XP, Server 2003 to the latest; The locker has no dependencies, does not use third-party libraries, only mathematics and vinapi; The completion of some processes to free open files (optional, negotiated); The ability to encrypt files without changing extensions (optional); Removing recovery points + cleaning logs on a dedicated server (optional); Standard options: tapping, startup, self-deletion (optional); Installed protection against launch in the CIS segment.
- Conditions: They are negotiated individually for each advert depending on volumes and material.
How Buran ransomware behaves
From our report of Nov 2019 · not reviewed since
Buran cryptovirus is the ransomware-as-a-service developed by threat actors who offer discounts for criminal customers online
Buran ransomware is the version of a cryptovirus that now is marketed as a RaaS.
Usually, such ransomware-as-a-service threat operators (GandCrab, REvil, Sodinokibi) take 30 or 40 percent from those ransom payments based on the affiliate marketing scheme, but the VegaLocker virus developers give a discount taking only 25% from the threat distributors using their ransom-demanding creation.
In advertisements, this ransomware is described as a stable strain of malware that uses offline crypto locker functionality and offers global session keys, 24/7 support. The month of October 2019 was the big month for the threat because many reports came out, some samples got analyzed and revealed that the Rig Exploit kit is now used as a primary entry vector.
Unfortunately, this virus is evolving and has at least Buran and Buran 2 versions. Researchers cannot offer any decryption tool for the victims because the behavior indicates the continuity and possible improvements like new branding efforts in the future.
A file-encrypting malware form that appends an extension of numerous random letters and numbers can also encrypt data without marking them or changing the extension. Buran virus is capable of removing recovery points, clearing logs, and deleting backups.
The first report about the threat reported that the added appendix looks like a GUID (Globally Unique Identifier), and is added to each encrypted document. Moreover, most of the files are marked with an identifier "BURAN" which signifies the dangerous infection.
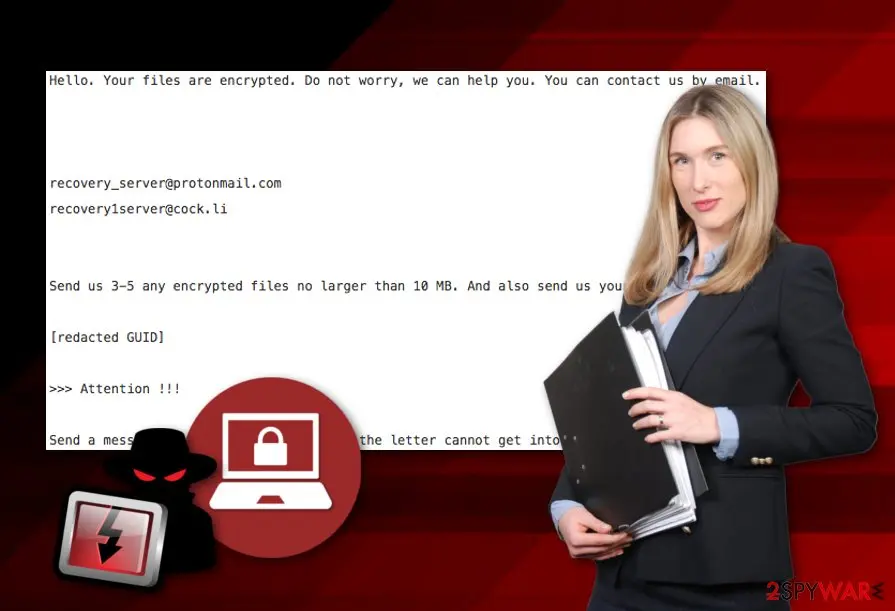
After the data is blocked, a ransom message named !!! YOUR FILES ARE ENCRYPTED !!!.TXT is loaded onto the desktop in order to inform the victims about what just had happened. The criminals urge contact via recovery_server@protonmail.com and recovery1server@cock.li email addresses that can also differ from version to version since this is a product used by many different criminals.
In order to discuss all conditions about data restoring, the crooks demand users send their ID's to both emails and also provide them with an offer of free decryption of from three to five data files that take up no more space than 10 MB.
Buran ransomware is a dangerous threat that no one wants to see on their machines. However, if the cyber threat has already occupied your system, you should be prepared for all possible consequences. Note that, the criminals are capable of modifying various registries entries and tasks by activating remote commands.
This might also allow Buran ransomware to inject other malware straight into the system and cause severe damage to it. If a Trojan horse ends up on your computer, you might find the entire system struggling to carry out even simple actions and launch programs. Moreover, trojans can relate to personal data and identity theft.
If you decide to contact the crooks, they will supposedly offer you a decryption tool for a particular price in order to bring back files that have been locked by Buran ransomware. Such people usually urge for Bitcoin or another type of cryptocurrency which allows the process to remain safe and untrackable by others.
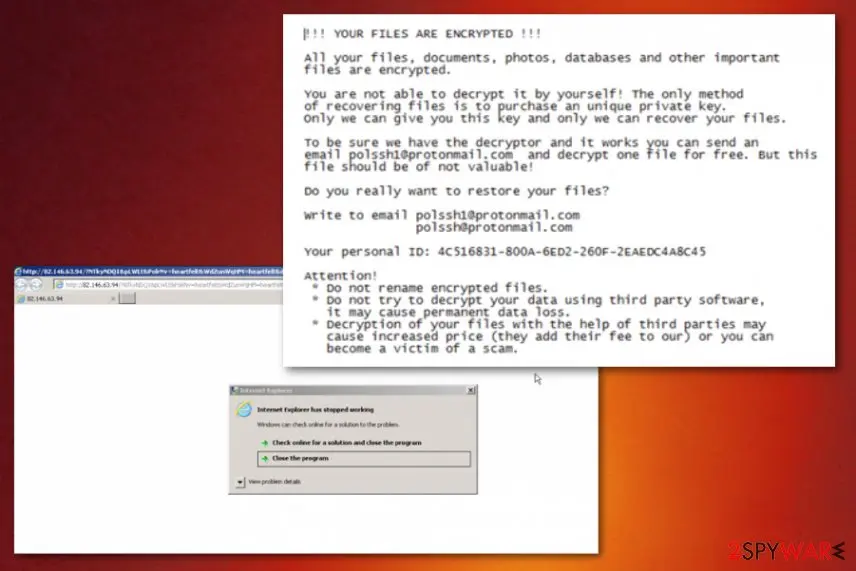
Buran ransomware message placed in text file reads the following:
You risk losing money are being left by nothing. A program like might scan the entire system for potentially damaged or corrupted files and other hazardous content. This will allow you to remove Buran ransomware virus damage entirely.
Note that it is very important to clean locations such as the Windows Task Manager and Registry as the malicious payload needs to be removed, or you will not be able to recover encrypted files. Doing that manually can lead to more serious issues with your device.
From our report of Nov 2019 · not reviewed since
VegaLocker ransomware version Buran 2 advertised as a RaaS
In October 2019 ransomware campaigns got discovered that financially motivated threat actors delivered ransomware to organizations in Germany and other countries.
These high volume attacks targeted companies via employees in the organization and relying on typical demanding messages attempt to make money from them. Improved and crafted malware designed to suit a wide range of environments and infection vectors, so the target was not a specific network.
It is believed that Buran ransomware tends to focus on victims in certain regions, hence the certain language in ransom messages and recent campaigns affecting German companies.
Since it was discovered as a version of VegaLocker, Buran was noticed being sold on various Russian hacker underground forums. Using the affiliated scheme and offering criminals the discount for 25 instead of common 30 or 40 percent cut out of the ransom payments.
Buran creators focus on creating relationships with criminals and negotiate business schemes. The following message was discovered in Russian underground forums:
The message created to promote Buran as a threat compatible with many versions of Windows OS and working for targets from various countries. However, former Soviet Republicks like Armenia, Belarus, Moldova, Russia, Ukraine, and other countries cannot get infected by the Buran 2 ransomware.
This is because of an additional location checking module, which ensures that data encryption in certain countries is not launched. Many facts about the threat remain the same as those characteristics reported back in May, so ransom note will be written to disk with the name "!!! YOUR FILES ARE ENCRYPTED !!!" and each file gets renamed with the new extensions with random values and victims' ID as an appendix.
As experts report, the Buran virus represents the evolution of the ransomware and the primary VegaLocker ransomware had a history of infections targeting companies. Developers are clearly working behind it and developing new features as branding tactics, so profits can generate from malicious actions. Interm of development, new versions with different features got discovered only months apart, so there is an expectation for more variants from these authors.
From our report of Nov 2019 · not reviewed since
Rig Exploit kit and system vulnerabilities used to spread malware
Recent investigations on newer samples revealed that this ransomware was delivered through the Rig Exploit Kit that is popular among other ransomware developers.
This exploit kit also uses Microsoft Internet Explorer VBScript engine, arbitrary code execution vulnerability CVE-2018-8174, to exploit the client-side and deliver malware on the system directly.
According to cybersecurity researchers from LosVirus.es website, spam messages alongside pirated software packages are more often used for carrying a malicious payload. Ransomware-related infections are often spread via email spam and infiltrate users' computers by using stealth techniques. Usually, crooks pretend to be from reputable organizations and urge people to open the attached file for further important information regarding the received email letter.
We urge all users to be very careful while sorting out their email messages. If some letters have fallen straight to the spam section, better get rid of them without even opening as no reliable companies will waste your time by contacting like you in these types of ways.
Furthermore, DO NOT open any attached files without scanning them with antimalware if you are not sure that they are safe to download.
Staying cautious on the Internet sphere and avoiding possible risks of malware infection is very important. The more serious you are with your online and computer safety, the better your chances will be for having a clean, optimized, and undamaged computer system.
If you want to ensure that reputable protection does not fail you at any time of the day, you should get a strong and reliable antimalware program for this.
The Buran ransomware note
!!! YOUR FILES ARE ENCRYPTED !!!
All your files, documents, photos, databases and other important
files are encrypted.
You are not able to decrypt it by yourself! The only method
of recovering files is to purchase an unique private key.
Only we can give you this key and only we can recover your files.
To be sure we have the decryptor and it works you can send an
email polssh1@protonmail.com and decrypt one file for free. But this
file should be of not valuable!
Do you really want to restore your files?
Write to email polssh1@protonmail.com, polssh@protonmail.com
Attention!
* Do not rename encrypted files.
* Do not try to decrypt your data using third party software,
it may cause permanent data loss.
* Decryption of your files with the help of third parties may
cause increased price (they add their fee to our) or you can
become a victim of a scam.
How to remove Buran ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Buran and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so Buran cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
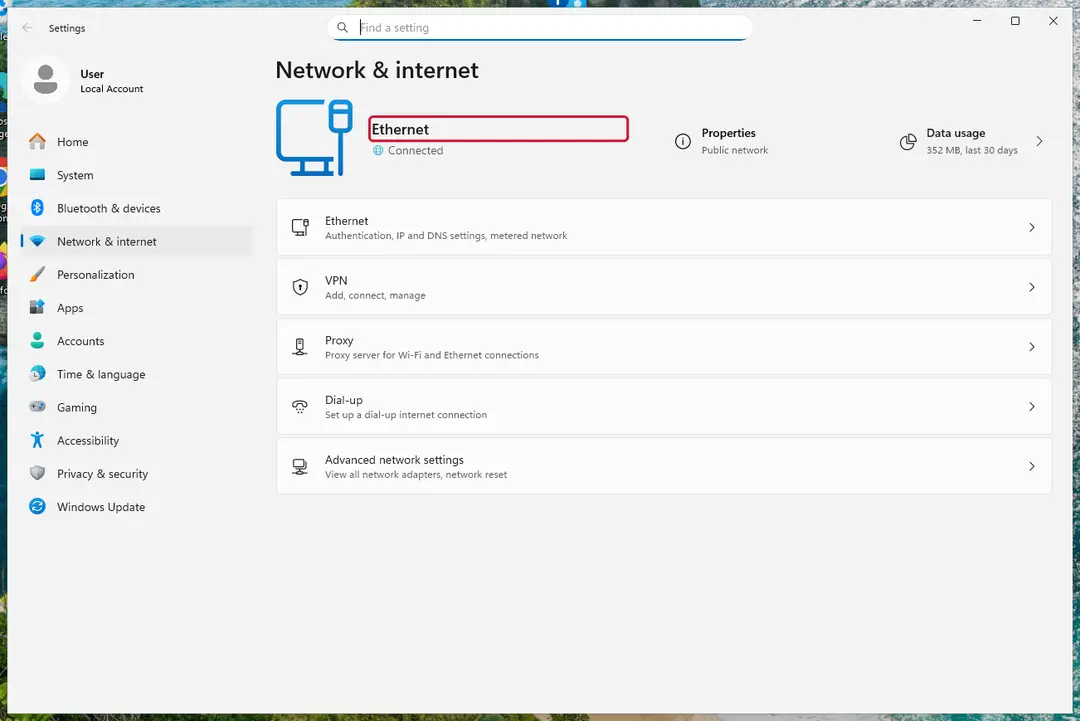
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and identify the family
The name of the family decides whether a free decryptor can help. Copy the ransom note and two small encrypted files to a USB stick, and check them on another device with ID Ransomware or Crypto Sheriff.
Note the extension added to the files, the contact address and the victim ID shown in the note. Keep the originals on the Windows 11 or Windows 10 PC untouched.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for Buran, no free decryptor is known (checked 7 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing Buran does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
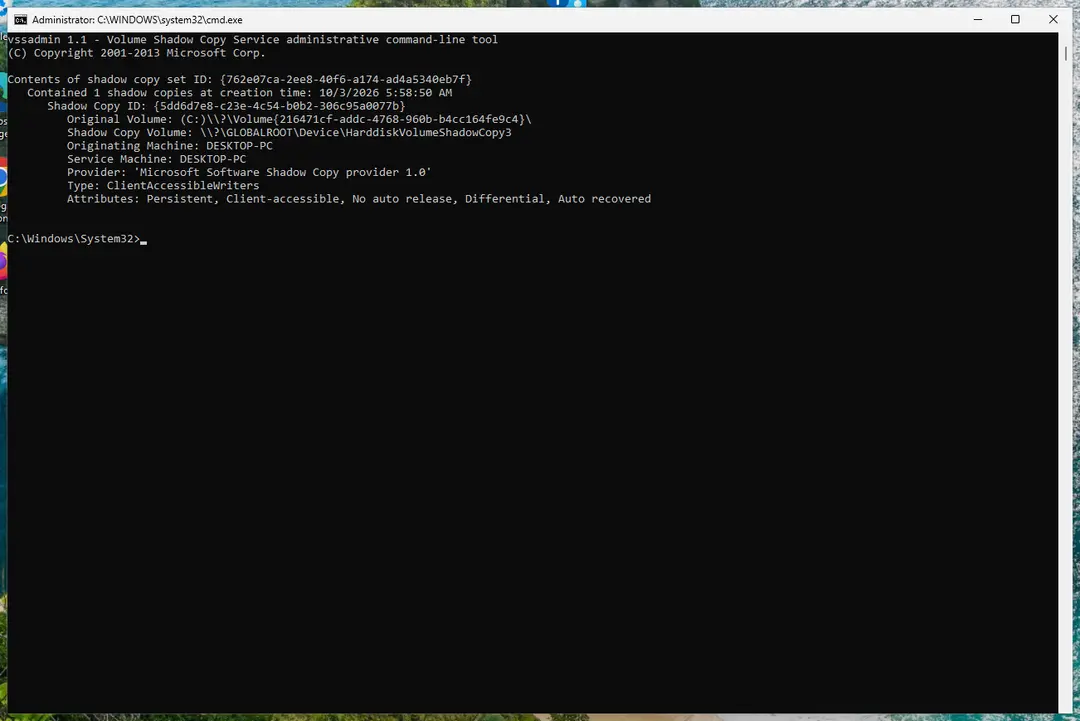
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that Buran deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
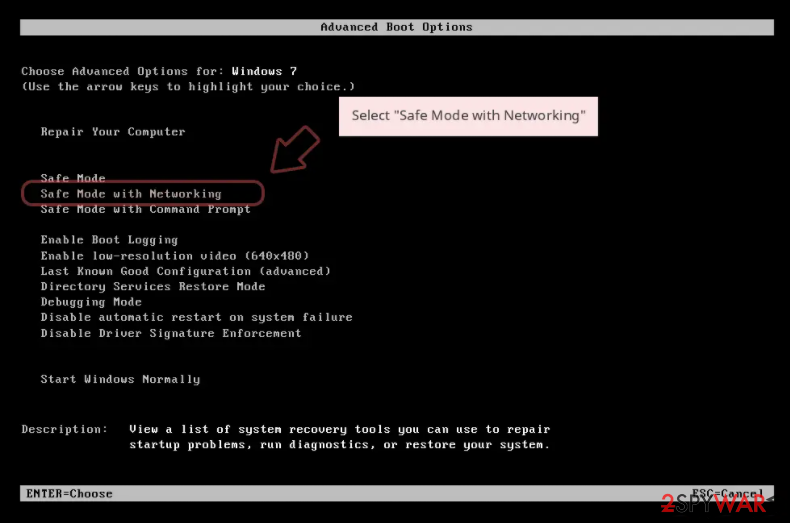
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
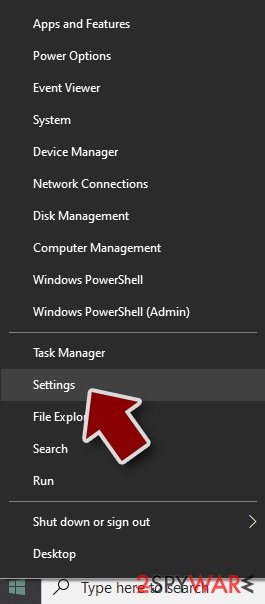
- Right-click on Start button and select Settings.
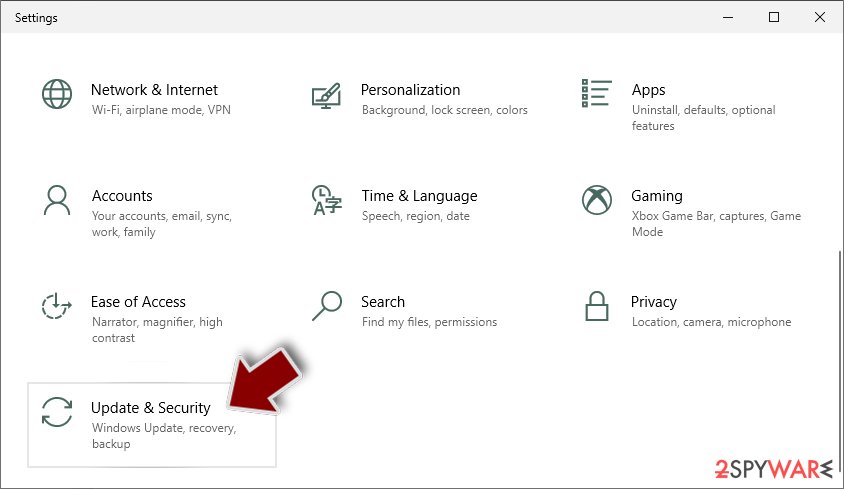
- Scroll down to pick Update & Security.
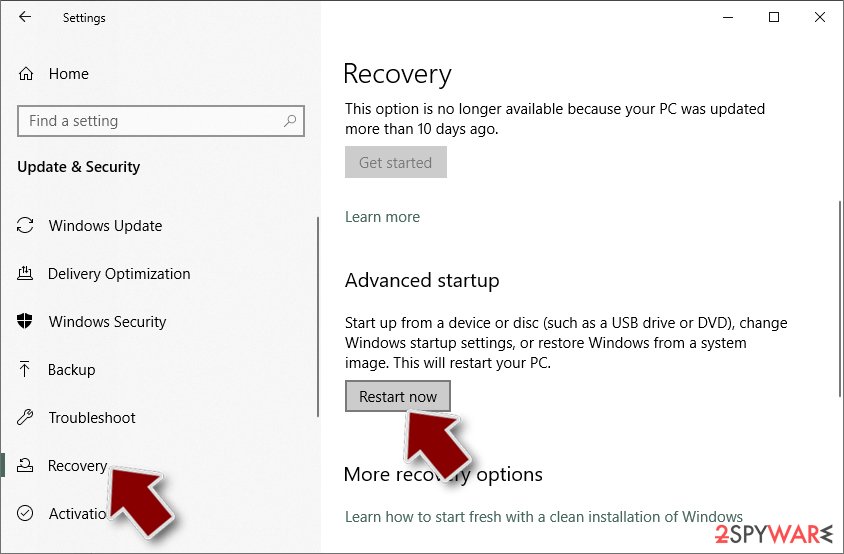
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
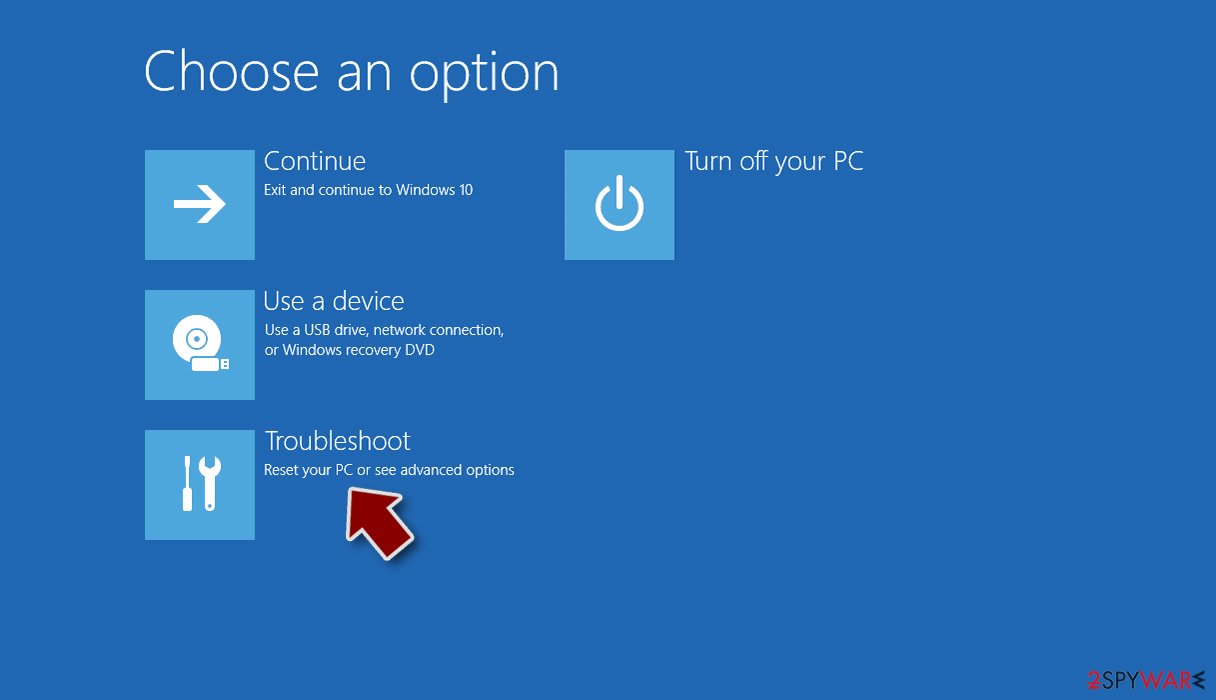
- Select Troubleshoot.
- Go to Advanced options.
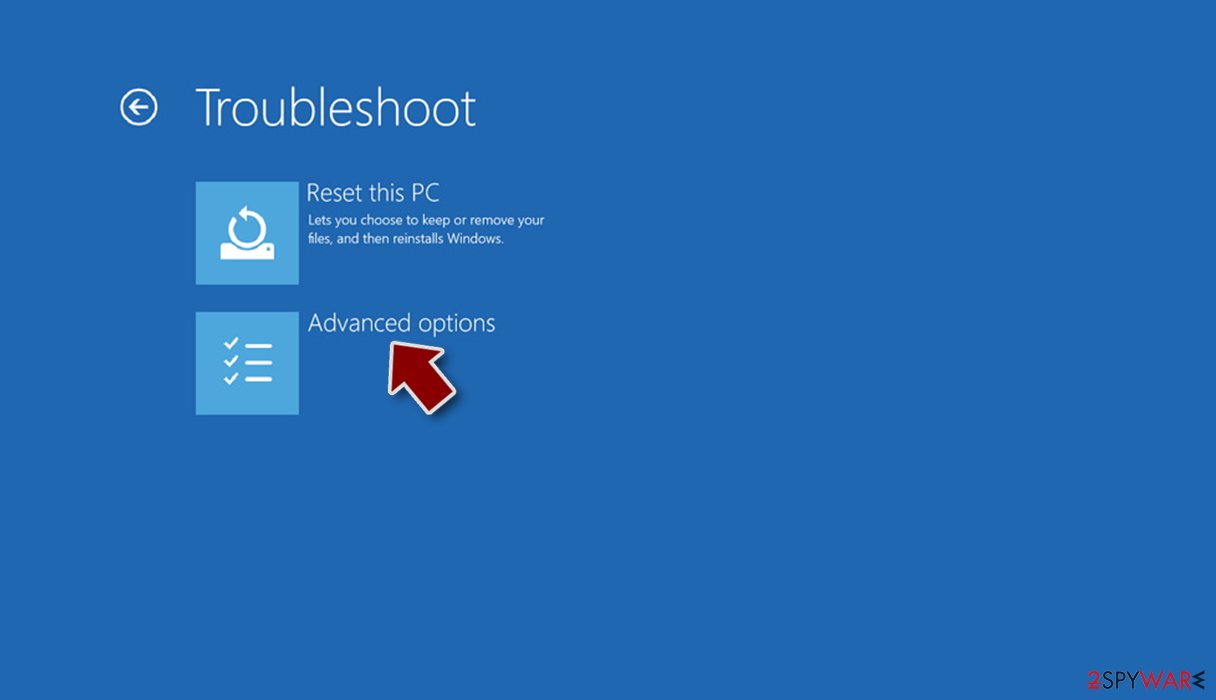
- Select Startup Settings.
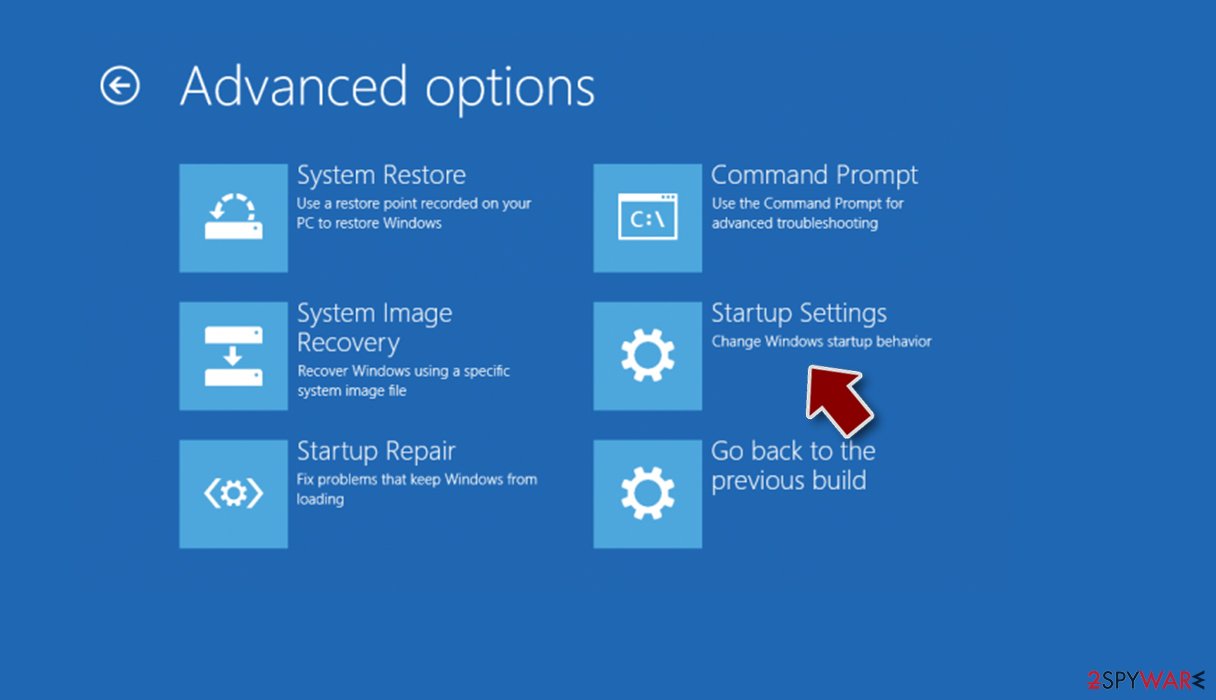
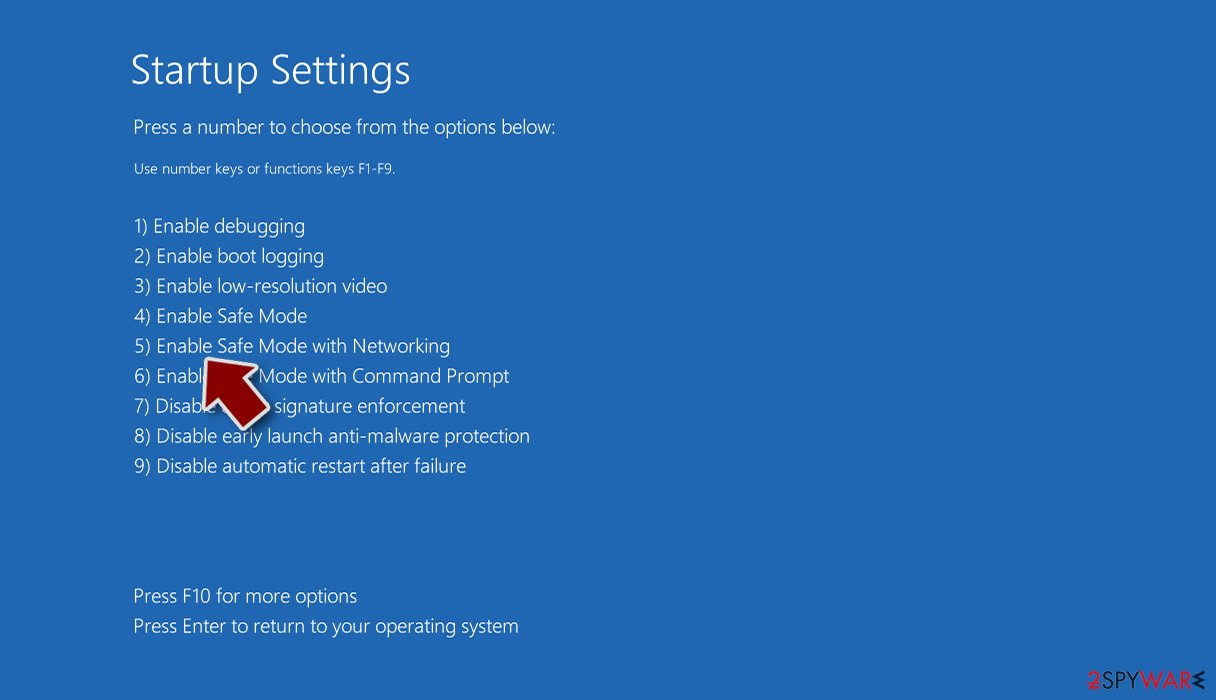
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
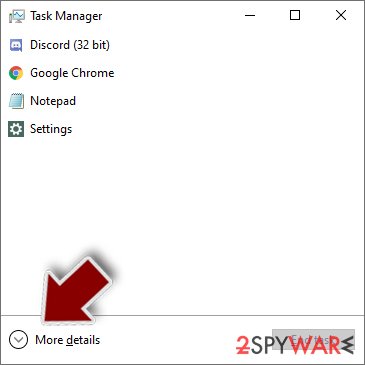
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
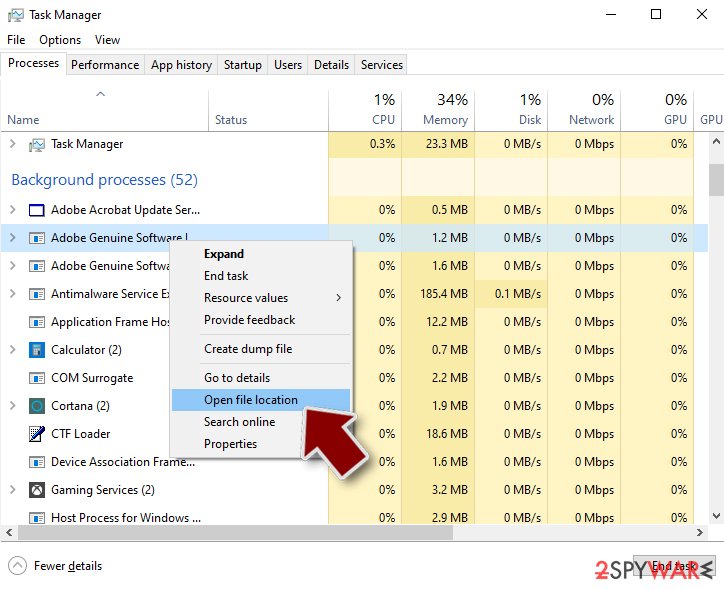
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
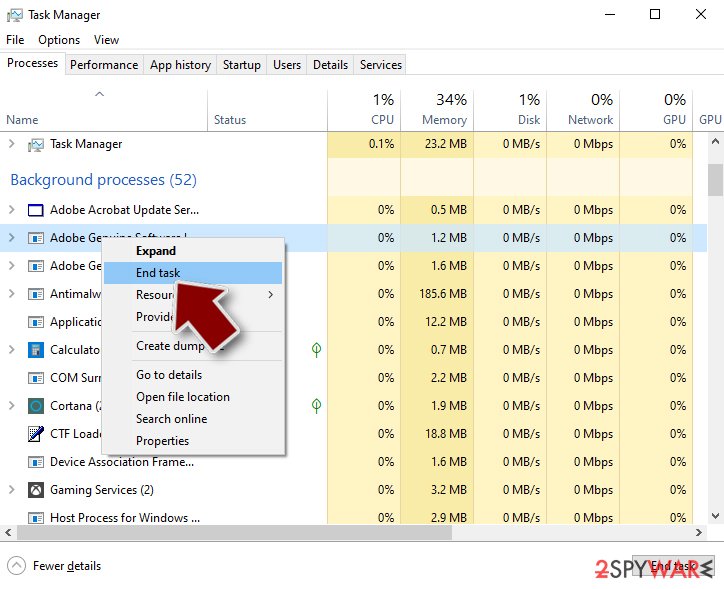
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
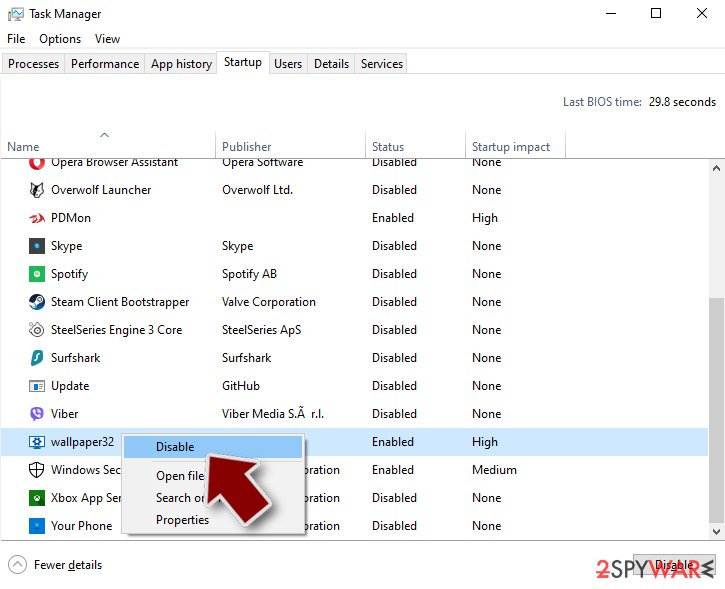
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
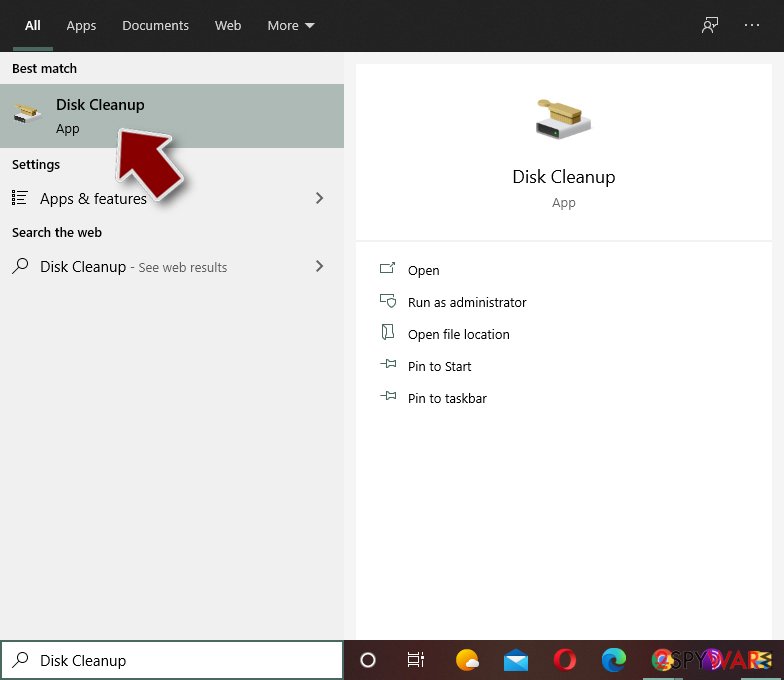
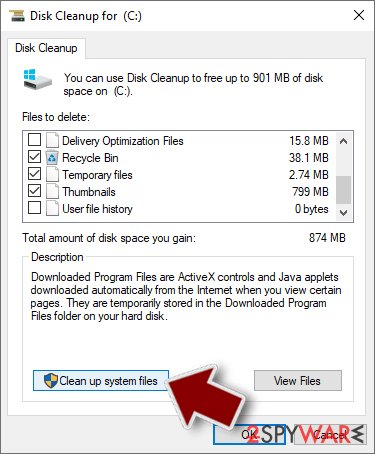
- Type in Disk Cleanup in Windows search and press Enter.
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Nov 2019 · not reviewed since
Automatical removal guidelines for Buran ransomware virus
First, we want to warn you that you should no try removing Buran ransomware virus on your own.
By completing manual actions, you might bring more harm to your computer system, which can, later on, relate in severe machine and software damage. What you have do is reboot the PC with Safe Mode or System Restore to disable ongoing malicious activities.
However, you need to check the entire system for malicious executables and other content before getting rid of the cyber threat. You can complete such a goal with tools such as , , or since these applications may indicate damaged data and fix the issue.
After you remove Buran ransomware, you can start thinking about file recovery. We have provided you with some techniques that are informatively described at the bottom of this article. Just note that the ransomware elimination comes first before data recovery as if the malicious payload is still active, files will be encrypted again.
[GI=method-1]Activate the Safe Mode with Networking function on your Windows computer.
[GI=method-2]Use the System Restore feature to stop Buran ransomware. If you do not know how to activate this function, take a look at these instructing steps:
If Buran ransomware has done some cruel work on your files and you are wondering how to return them back without paying the criminals, we suggest trying this software.
Windows Previous Versions feature is suitable for data restoring:
Restoring encrypted files is a difficult process. However, you might still have a chance of returning some of your documents to their previous states. Continue with this method if you have enabled System Restore in the past:
Shadow Explorer might allow you to return some files back:
If the ransomware virus did not eliminate Shadow Volume Copies of your encrypted data, you should give this method a try, and you might recover some of your locked documents/files.
Sadly, no official Buran ransomware decryptor has been released yet. Cybersecurity experts are currently working on its development.
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Make the next attack harmless
Buran could only hurt the files that had no second copy, and the signs (buran in the list of installed apps) showed exactly which ones those were.
The 3-2-1 rule fixes that:
- three copies
- two media
- one disconnected
A practical version for a home PC: OneDrive or another cloud backup with version history, plus an external disk that you plug in once a week for File History and then unplug. Test a restore now and then by opening a few files from the backup on another device.
Details, schedules and what not to back up are in our 3-2-1 backup guide for Windows.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
Questions about Buran ransomware
Should I pay the ransom in !!! YOUR FILES ARE ENCRYPTED !!!.TXT?
Not before you have tried everything else. Identify the family from !!! YOUR FILES ARE ENCRYPTED !!!.TXT and one encrypted file, check No More Ransom for a free decryptor, and look for clean copies in OneDrive, backups and Previous Versions.
Paying funds further attacks, may be illegal if the group is sanctioned, and is no promise of a working key: many victims get partial or broken decryption. If you consider paying for business-critical data, involve the police and a professional incident responder first, and never pay through intermediaries who promise their own decryption.
Is there a free Buran decryptor?
We last checked on 7 October 2026, and for Buran no free decryptor is known. We check No More Ransom, which collects free tools from police and security companies, and the decryptor pages of the major antivirus vendors. A working decryptor exists only when the encryption has a flaw or the keys were leaked or seized.
Ignore sites and videos that offer a "Buran decryptor" for download or for a fee: these are usually scams or malware. Real decryptors are free and come from known security companies or law enforcement. Keep the encrypted files in case a tool appears later.
Are ransomware recovery services legitimate?
Some are, but read the offer carefully. Genuine data-recovery firms recover deleted originals from disks or rebuild damaged files, and they say so. Others promise to "decrypt any ransomware" for a fixed price, which is impossible without the key; they quietly pay the attackers and keep a margin, sometimes without telling the victim.
Be especially careful with services that contact you after you post about the attack online. Ask for references, a written method and a no-result-no-fee clause, and check the free tools on No More Ransom first.
How did Buran get on my computer?
The way Buran spreads has not been documented yet, so look at your own recent activity. On home PCs, ransomware most often comes with cracked programs, game cheats, key generators and fake updates, or with an e-mail attachment that was opened. On business networks, attackers usually log in through Remote Desktop with a stolen or guessed password.
Think back to what was downloaded or installed in the days before buran in the list of installed apps, and check the Downloads folder and Installed apps sorted by date. Keep anything suspicious for your report, but do not run it again.
Did Buran steal my files or passwords?
We do not know yet. Nothing published so far shows data theft by Buran, but the only confirmed sign is buran in the list of installed apps, which says nothing about what happened before. Many current ransomware attacks copy files or run a password stealer first, so it is wise to act as if they did.
From a clean device, change the passwords that were saved in the browsers on this PC, starting with e-mail and banking, sign out of all sessions and turn on two-step verification. Watch bank statements and account activity for the next few weeks.
Is Buran the same as other ransomware with a similar name?
Not necessarily. Ransomware names come from the file extension, the note or a word in the code, so unrelated families often end up with similar names, and one family can appear under several names. The difference matters: a decryptor or advice for one family does not fit another and can damage files.
Compare the ending added to your files and the exact name of the note with the summary table at the top of this guide, then upload the note and one encrypted file to ID Ransomware from a clean device. If the result names another family, follow the guide for that family instead.
Can I delete !!! YOUR FILES ARE ENCRYPTED !!!.TXT?
Yes, the note itself is harmless text and deleting it does not affect your files. Keep at least one copy first, outside the infected PC. !!! YOUR FILES ARE ENCRYPTED !!!.TXT contains your personal ID and the attackers' contact details, which identification services use to tell which family encrypted your files, and which a decryptor may need later.
Police reports also ask for it. Once you have saved a copy, you can remove the notes from every folder after the ransomware program has been removed and your files are restored or backed up.
How do I open my .docx, .jpg and other files locked by Buran?
You cannot open locked files normally while they stay encrypted, and renaming them will not help. Our earlier report did not record the extension that Buran adds, so check one locked file name and the ransom note for it.
No free decryptor is known for this variant; check No More Ransom (nomoreransom.org) for updates. Do not rename the files, change the extension or edit them, because that can make recovery harder. Copy the locked files to an external drive before you clean the system, so a decryptor released later still has them.
Will Fortect remove Buran?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Buran, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Search Security: GUID (global unique identifier) (read October 7, 2026)
- Pastebin: !!! YOUR FILES ARE ENCRYPTED !!!.TXT (read October 7, 2026)
- Malwarebytes: Trojan (read October 7, 2026)
- Losvirus: Losvirus (read October 7, 2026)
- CISA: StopRansomware (read October 7, 2026)