
IE redirect virus: what it is and how to remove it
IE redirect virus is an annoying browser hijacker that might change your browser's homepage to a suspicious search page without your knowledge. There is also a big chance that you will spot such changes with your default search engine which will supposedly start providing misleading search results.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
A scan of the PC is a quick way to confirm that nothing installed is behind the search.conduit.com redirects.
Do it yourself · free Remove IE redirect virus yourself 3 steps, about 9 minutes, no software needed.
Start the steps
IE redirect virus: summary
| Name | IE redirect virus |
|---|---|
| Type | Potentially unwanted program |
| Main activities | Hijacking the browser's search engine, providing false search results, pushing advertising content, redirecting to developer-sponsored pages |
| Similar applications | Chrome redirect virus, Firefox redirect virus |
| Possible danger | Redirects can take you to malware-based networks |
| Distribution ways | Bundled freeware/shareware, third-party websites (e.g. adult-themed sources) |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 10 more facts
| Remove the threat | Removing the PUP can be easy if you use a tool such as an anti-malware application |
|---|---|
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Symptoms | Redirects to an unknown domain |
| Evidence | 8 write-ups by security sites; details still limited |
| Domains | search.conduit.com |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 13 July 2021 |
| Facts checked | 6 October 2026 |
Is IE redirect virus dangerous?
From our report of Jul 2021 · not reviewed since
Internet Explorer redirect virus is a PUP that forces you to visit suspicious websites
IE redirect virus is an annoying browser hijacker that might change your browser's homepage to a suspicious search page without your knowledge.
There is also a big chance that you will spot such changes with your default search engine which will supposedly start providing misleading search results.
Cybersecurity experts recommend removing this annoying computer infection which is also recognized as the Internet Explorer virus. Usually, the program that starts controlling the browser silently tracks the user's activity and uses collected data to display irritating ads as pop-ups or search results.
Normally, programs that belong to the browser hijacker category are rarely considered dangerous because they are not capable of stealing data or putting infected computer users at risk of financial loss or identity theft. Nonetheless, the Internet Explorer virus can easily initiate various changes on your Internet Explorer browser and add related toolbars, browser add-ons, and extensions .
A hijacked Internet Explorer redirects the user to websites that often look unfamiliar or even suspicious. If the browser gets affected by a browser-hijacking application, the browser will continue launching a particular site (or sites) on a daily basis.
In fact, it is very likely that a hijacked web browser might start redirecting to one of the following pages known to be suspicious (clicking on them will take you to their comprehensive descriptions):
In fact, if your IE browser gets infected by the Internet Explorer virus, it is likely that other browsers may suffer the same consequences too. Microsoft's new and improved equivalent of the Internet Explorer - the Microsoft Edge browser is especially vulnerable to this infection.
So, when the virus alters the default search engine and the start page on your IE browser, your Microsoft Edge will probably undergo the same changes, too.
Beware that such ads can inform you about missing updates and similar things.
You should never trust such warning messages because, in reality, they might seek to infect PC users with other viruses. This way you might end up with a dangerous Trojan or ransomware infection on your machine and face severe damage, the redirect virus removal is the first step you should take to avoid getting infected even further.
Similar to Chrome redirect virus and Firefox redirect virus, the main way how you can get infected with IE redirect malware is based on infected downloads. You simply need to open an infected email attachment, download an illegal program or visit a hacked site and you will be infected by this parasite.
If you have already noticed a different search engine and a new homepage on your Internet Explorer, there is a huge possibility that an IE redirect virus hijack has occurred on your computer. In this case, you should never ignore annoying redirects when using Internet Explorer because you may be tricked into visiting unsafe websites .
On most occasions, this virus interrupts people when they are surfing the web and redirects them to unknown sites that are less popular and need to increase their visitors' number or page rank. However, some experts claim that the Internet Explorer virus may also be used to promote other, more serious viruses and allow their infiltration into the system.
As you can see, you should never ignore questionable redirects because it means that your PC is infected. In order to remove IE redirect virus, you should try running a full system scan with or . Additionally, you will find some manual helping lines at the end of this article that will show you how to clean your web browser from suspicious content.
- Search.Conduit.com;
- WWW-searching.com;
- Default-search.net;
- V9.com;
- WebsSearches.com;
- Trovi.
From our report of Jul 2021 · not reviewed since
Frequently asked questions about IE virus
Question.
I am dealing with a virus on Internet Explorer 11. Every time I open my browser, Trovi.com pops up. I have never set this page as my default start page or something. How can I remove this annoying Trovi virus that causes IE redirects repeatedly?
Answer. Dear visitor, it is clear that your browser is affected by a redirect virus. The cause of the Internet Explorer 11 virus is obviously the Trovi virus, which could have sneaked into your computer alongside other programs you recently installed.
To remove the virus causing IE redirects, uninstall every suspicious program and delete every shady browser extension not only from IE but from the rest of web browsers as well. It is highly advisable to check browser shortcuts as well (see a tutorial provided below).
Question. I am having problems with my browser. Internet Explorer now redirects me to search.conduit.com without my request to do so. How can I solve the Internet Explorer home page redirect problem?
I tried to change my home page settings but no results. The suspicious domain keeps appearing in my browser over and over again.
Answer: Dear visitor, your computer is compromised by the Conduit Search virus, a widely known browser hijacker that causes Internet Explorer redirects and also targets other web browsers such as Chrome or Firefox.
To uninstall it from the system, you must find files related to Conduit and root them out from the computer system. The quickest way to do it is to use an automatic spyware removal tool such as .
From our report of Jul 2021 · not reviewed since
More from our earlier report on IE redirect virus
- You should also take care of the pieces that get altered with
How IE redirect virus got into your browser
From our report of Jul 2021 · not reviewed since
According to Novirus.uk researchers, browser-hijacking programs and other potentially suspicious content have their own ways of entering the targeted machine/device.
The most popular are software bundles as browser hijackers are often inserted into packages of programs as additional components.
Additionally, potentially unwanted programs can be found in other sources such as peer-to-peer networks, online-gaming websites, movie-watching pages, and adult-themed networks. The best ways to avoid the secret installation of browser hijackers are:
- Using the Custom mode for performing downloads and managing all incoming objects. Be aware of all Quick or Recommended modes as these often let suspicious content into the system.
- Keeping a distance from secondary sources while browsing throughout the Web. Avoid all content that looks questionable to you (e.g. links, ads).
- Installing reputable computer protection. Search for an advanced anti-malware tool that includes as many security features as possible for your own and machine's safety purposes.
Check your browser and PC
- Address:
search.conduit.com
How to remove IE redirect virus
How to stop the IE redirect virus redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Step 1: Check the browser's extensions
Redirects to
search.conduit.comon sites that normally behave mean something in the browser is sending you there. In Chrome openchrome://extensions, in Edge edge://extensions, in Firefox the menu > Extensions and themes.Remove every extension you do not remember adding, especially new tab, search, coupon, PDF or video downloader add-ons. The extension pages look the same on Windows 11 and Windows 10.
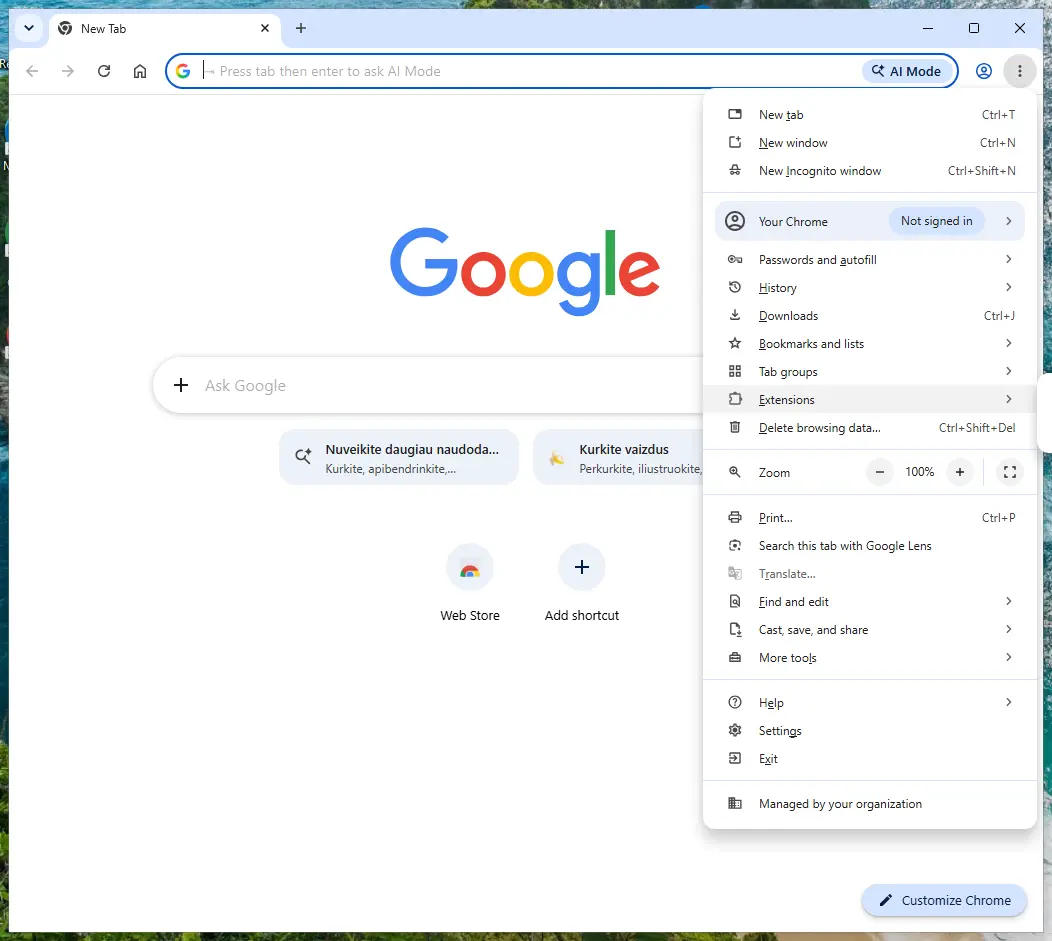
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Reset the browser if the redirects continue
If
search.conduit.comstill opens after the extensions are gone, put the browser's settings back to their defaults. In Chrome open Settings > Reset settings > Restore settings to their original defaults; in Edge Settings > Reset settings; in Firefox Help > More troubleshooting information > Refresh Firefox.Tip: Bookmarks and saved passwords stay, while site permissions, the start page and the search engine are reset.
Redirects that survive a reset in every browser point to a program installed in Windows 11 or Windows 10, so uninstall anything you do not recognise in Settings > Apps > Installed apps.
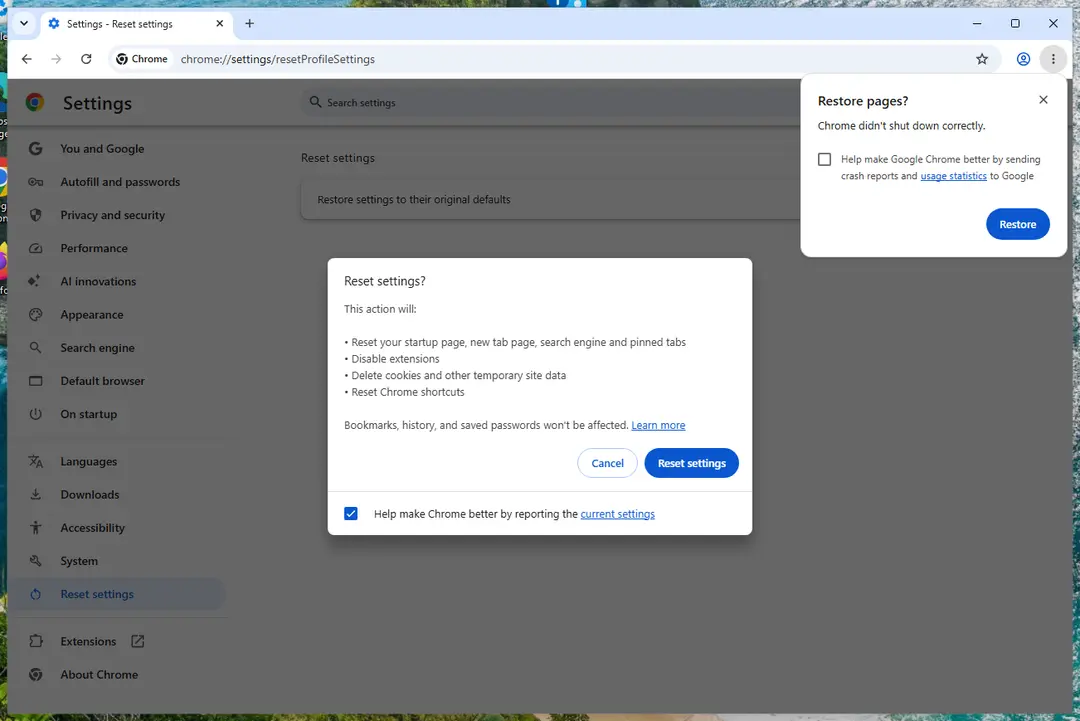
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Scan the PC if you downloaded anything from the ads
If you only saw the notifications and clicked nothing, you can stop before this step. If a notification led you to download or run something, delete that file, then scan Windows.
In Windows Security > Virus & threat protection > Scan options, run a Full scan, then choose Microsoft Defender Antivirus (offline scan) and Scan now. The offline scan restarts the PC and takes about 15 minutes on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
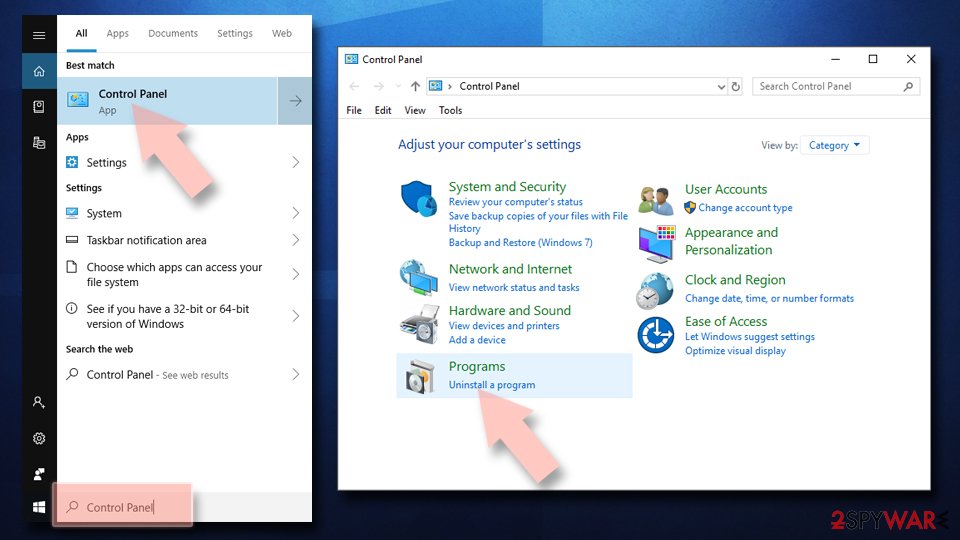
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
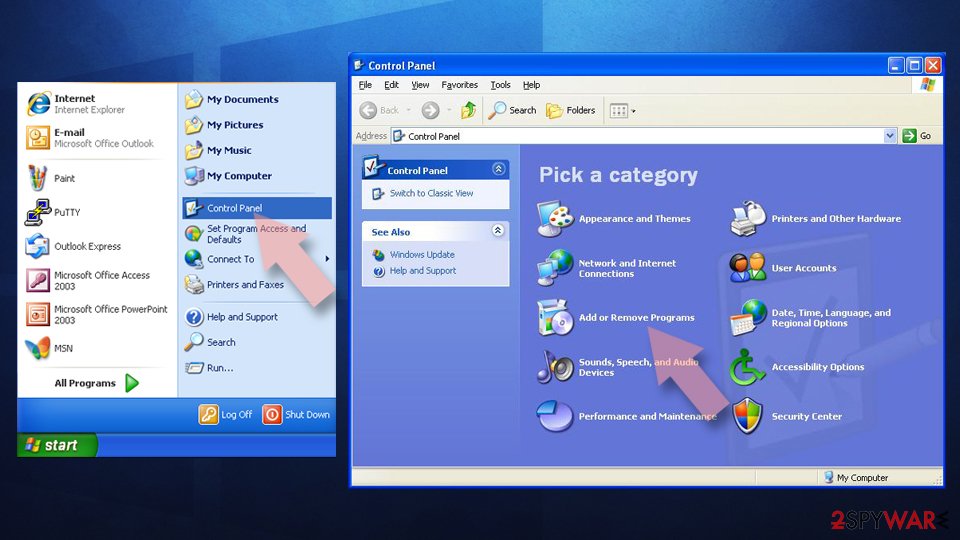
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
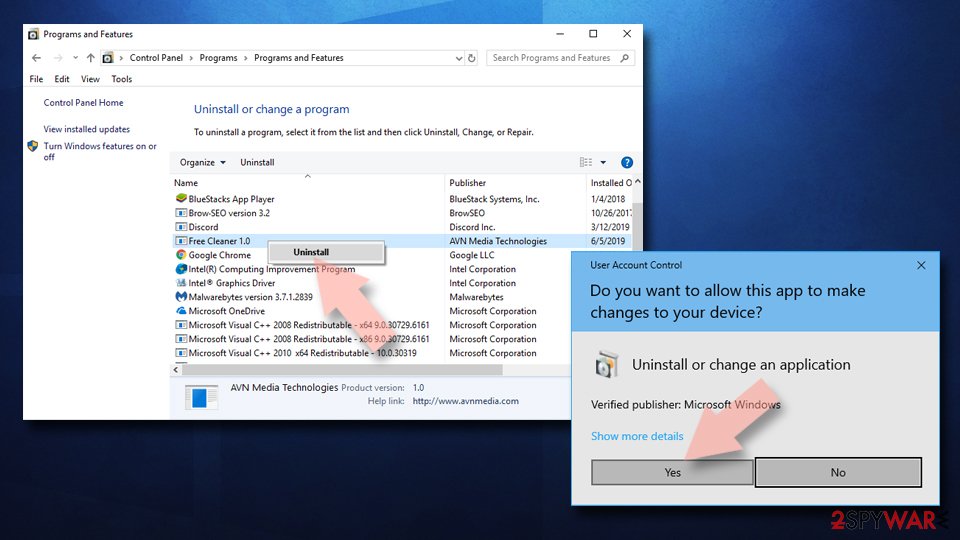
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
Remove dangerous extensions:
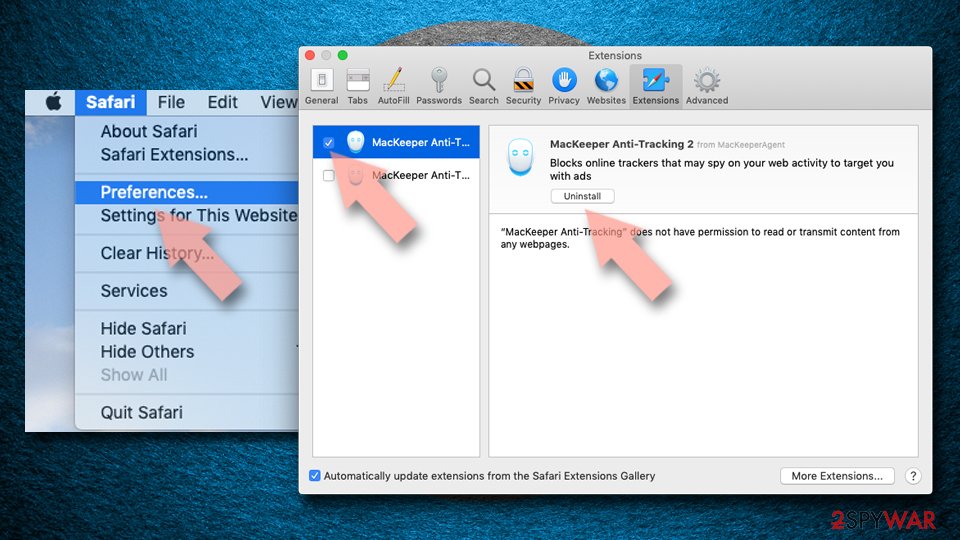
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
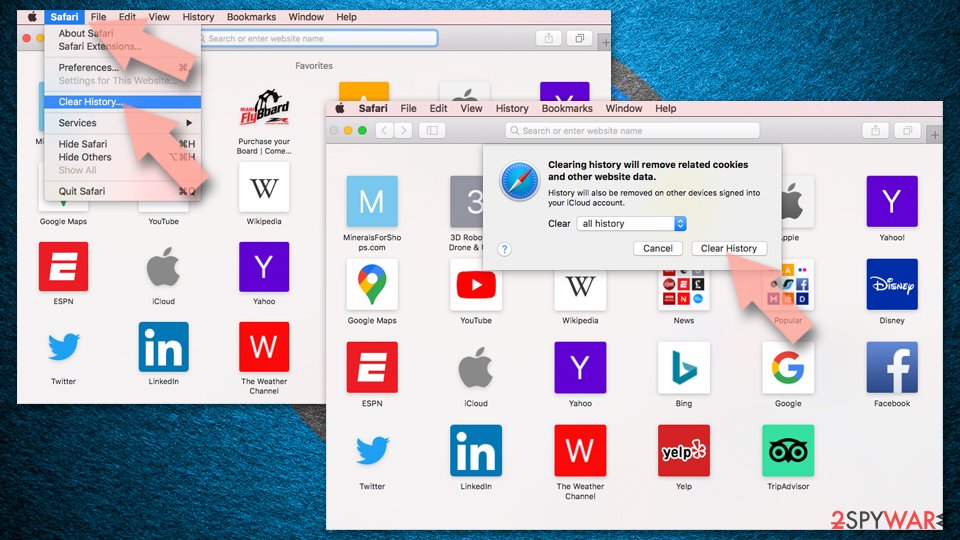
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
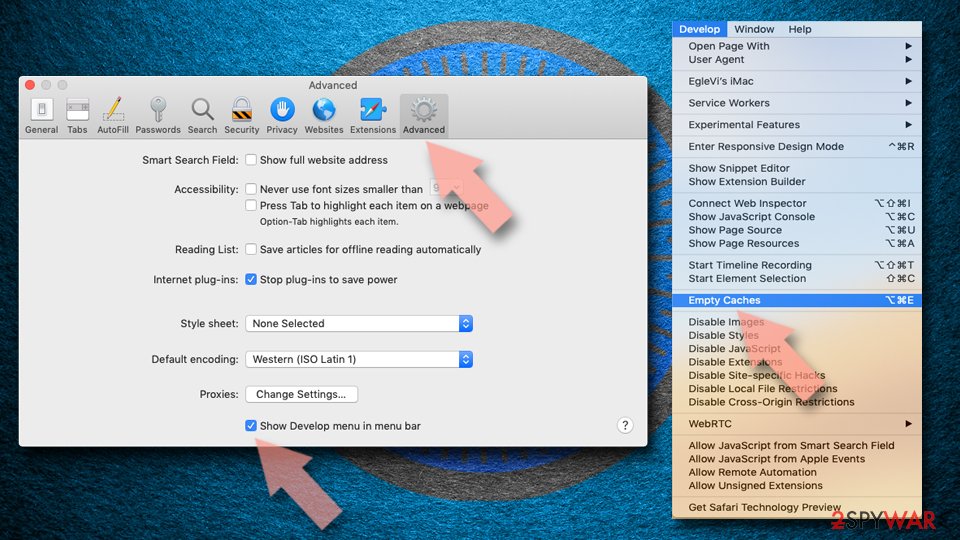
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Remove the unwanted application:
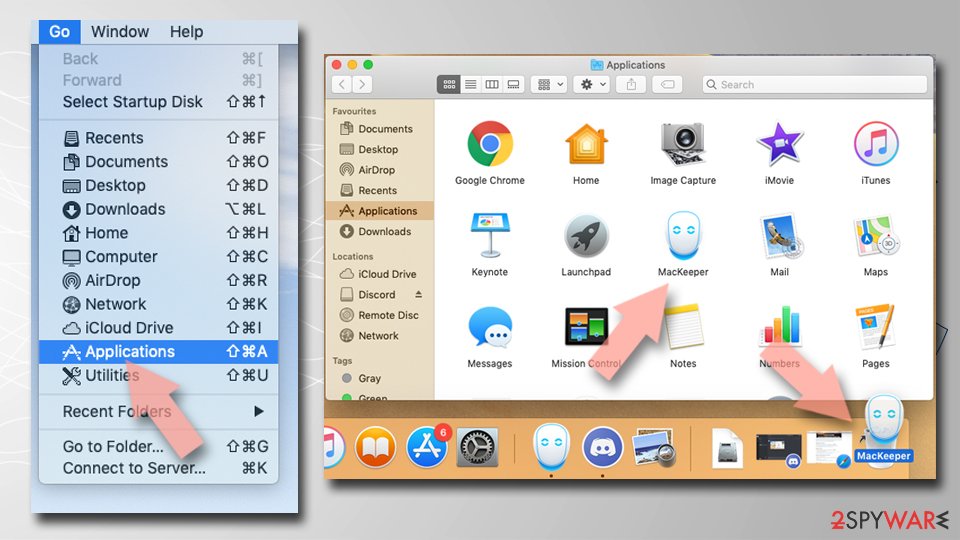
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
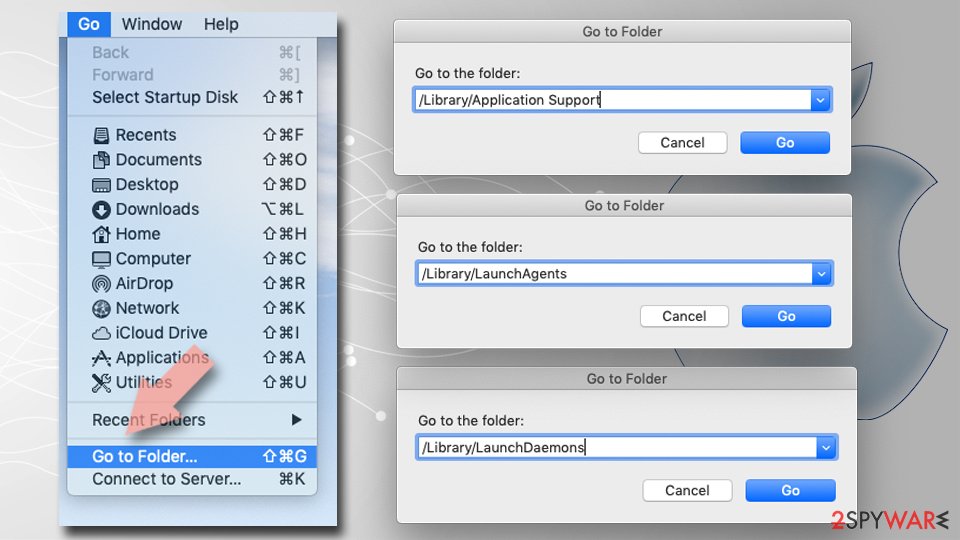
- Finally, empty the Trash to permanently remove the leftovers.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of Jul 2021 · not reviewed since
A guide to IE Redirect virus elimination
In order to remove the redirect virus fully, you should run a full system scan to find the potentially unwanted program that is related to it.
This could be done with the help of legitimate anti-spyware or with the help of the manual removal steps indicated below the article. The choice depends on you but automatical elimination requires less effort and can be done more effectively.
However, when using the manual IE redirect virus removal method, you should know exactly what are you looking for. In this particular case, it's quite difficult, since the virus is good at obfuscating its components and can easily hide in places you'd never expect it to.
Furthermore, the Interner Explorer virus will be eliminated much faster and easier by using reputable anti-malware tools than it can be done by using your own effort. Besides, people who lack experience in dealing with various cyber threats will also find the automatic removal method very helpful and comfortable to carry out.
Questions about IE redirect virus
search.conduit.com opens when I click links. What causes it?
When every click leads to search.conduit.com first, an extension or a script on the page is rewriting the links. If it happens only on one site, that site uses aggressive ads; close it and use another source. If it happens everywhere, open the browser in a private window, where extensions are normally off, and try again.
No redirect in the private window means one of your extensions is responsible: remove the ones you do not know. A redirect in the private window too means the cause is outside the extensions, such as a notification permission, a changed search setting or a program installed on the PC. The removal steps in this guide cover each of those.
Should I worry about redirects to search.conduit.com?
Worry less about search.conduit.com itself and more about what keeps sending you there. A single redirect from a free streaming or download site is normal and harmless once the tab is closed.
Repeated redirects on sites that used to work fine mean something in the browser or in Windows changed, often an extension or program installed alongside other software. It may also collect the pages you visit. Remove the cause with the steps in this guide, and do not act on anything the redirected pages ask:
- no Allow clicks
- no downloads
- no calls
If you already did one of those, the matching section of this guide explains what to do next.
Why does IE redirect virus show me ads?
Because that is its whole purpose. IE redirect virus is an ad redirect domain, and its operators are paid for every ad it displays and every click it gets. In this case the ads take the form of redirects through ad pages.
They are chosen by ad networks that accept almost any advertiser, which is why so many look like warnings or prizes. The ads are not a sign that your PC is broken or infected with something worse; they are a sign that something on it, or in the browser, has permission to advertise. Removing that permission or program stops them.
Is search.conduit.com safe to visit?
No. The site search.conduit.com exists to push visitors towards ads, and the pages it leads to include fake virus warnings, fake updates, prize scams and notification prompts. Visiting it once does not infect an up-to-date PC, but anything you click or download there is a gamble.
Do not enter personal details, do not allow notifications and do not call phone numbers it shows. If it opens by itself, close the tab and check the browser's extensions and notification permissions. Blocking the single domain helps little, because the operators register new names regularly.
Do I have to clean every browser?
Yes, if you use more than one. We saw IE redirect virus in Chrome, Edge and Firefox, and each browser keeps its own extensions, notification permissions and settings. Chrome and Edge share the same extension format, so one installer can add the same adware to both, while Firefox has its own add-ons.
Check every browser on the PC, including ones you rarely open. If you sync a browser with an account, clean it while signed in, so that the removal reaches your other computers rather than the adware returning from them.
How do I know the ads come from IE redirect virus?
Look for redirects to search.conduit.com. That is the trace IE redirect virus leaves, and it shows up as redirects through ad pages. Ads that appear on every site, including ones that never carried ads before, point to something on your PC or in the browser rather than to the sites themselves.
A quick test is a private window, where extensions are off by default: if the ads disappear there, an extension is responsible. If they appear even with the browser closed, the source is a notification permission or a program in Windows.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
Can adware slow down my PC?
Yes. Adware runs in the background, loads ad scripts, opens extra tabs and contacts its servers, all of which use processor time, memory and bandwidth. Ad-heavy extensions also slow down every page, because they inspect and change it before you see it.
The effect is strongest on older PCs and when several adware programs arrived together. After removal, restart the PC and check Task Manager for anything still using a lot of resources that you do not recognise. Speed usually returns to normal once the ads stop.
Will Fortect remove IE redirect virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For IE redirect virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Avast antivirus blog: What is a browser hijacker (read October 6, 2026)
- Microsoft: Microsoft Edge. The faster, safer browser designed for Windows (read October 6, 2026)
- Computer World: What's a Peer-to-Peer (P2P) Network? (read October 6, 2026)
- Search Security: Antimalware (anti-malware) (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)