
Win64:malware-gen: what it is and how to remove it
Win64:malware-gen is a heuristic detection for 64-bit trojans on Windows systems. False positives are common, so verification is important before removal.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If Win64:malware-gen keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove Win64:malware-gen yourself 5 steps, about 15 minutes, no software needed.
Start the steps
Win64:malware-gen: summary
| Damage | In most cases, the infection can lead to financial losses, infiltration of other malware, data loss, sensitive data disclosure and even identity theft |
|---|---|
| Name | Win64:malware-gen |
| Type | Trojan, false-positive |
| Infiltration | Trojans can be spread in many different ways, including spam emails, pirated software installers, software cracks/keygens/loaders downloaded from torrent sites, malicious links, fake updates, etc. |
| Capabilities | Trojans can perform a variety of malicious tasks on the infected machines, including sending spam, stealing sensitive information, taking screenshots, injecting other malware, and much more |
| Similar heuristics | Win32:Malware-gen, Trojan.genericKDZ, Other:Malware-gen [Trj], IDP.Generic, Trojan.Win32.Generic, etc. |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Symptoms | An unknown program in Installed apps |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 26 June 2020 |
| Facts checked | 5 October 2026 |
What Win64:malware-gen does on an infected PC
From our report of Jun 2020 · not reviewed since
Win64:malware-gen - heuristic detection of some antivirus providers that is used to describe a Trojan
Win64:malware-gen is a detection name for a type of malware known as a Trojan.
Trojans are among one of the most prevalent and versatile threats around, as their nature and working mechanisms can deffer vastly, although all of them have one thing in common; users get infected with a Trojan when they open a malicious file, believing that it is actually legitimate, e.g., a software crack or a spam email attachment.
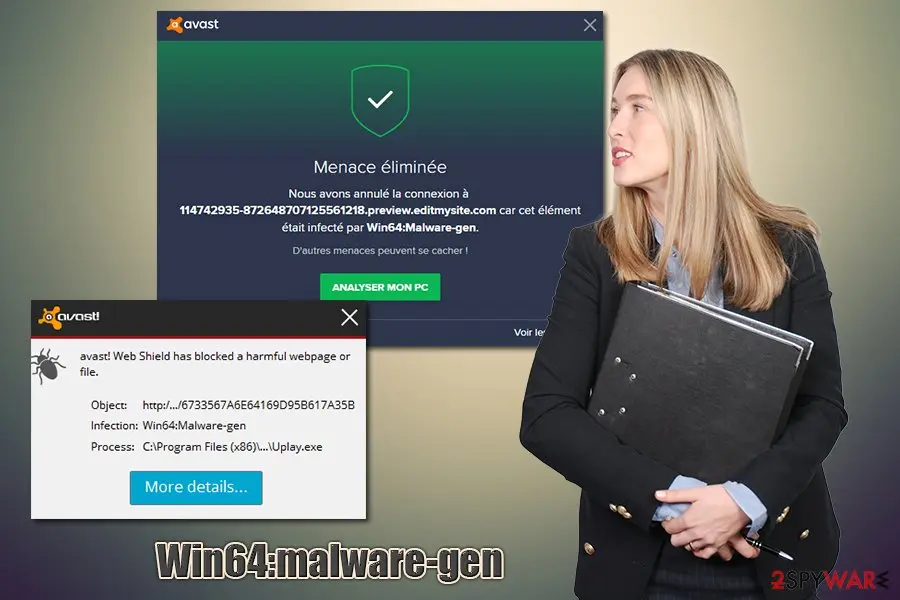
While most of such threats are quickly eliminated by the anti-malware, there are several issues with heuristic-based detection. For example, many users complained that legitimate files are being tagged as malicious or that the detection reoccurs on a regular basis. These inconsistencies are common when it comes to generic malware analysis as Win64:malware-gen, and each of the cases which provides some types of difficulties should be investigated carefully.
Anti-virus software uses several methods to detect malicious software on your computer, including signature-based, machine learning, sandboxing, application whitelisting, heuristics, etc. Win64:malware-gen belongs to the latter category. This method looks at software behavior rather than checking signatures within the database, which ensures higher detection rates and stopping of the newest malware samples.
However, due to the principle of its operation, Win64:malware-gen detection also falls victim to a relatively high rate of false-positives. This means that legitimate files can get flagged as malicious as soon as it introduced to the system or after an update to security software or the detected app is applied.
In such a case, it is worth making an exclusion within the security application and updating it, which would remove Win64:malware-gen from the list of malicious files.
If you have doubts about a particular file that you believe to be legitimate, you should either contact the developer of software, as well as the anti-virus and clear things out about it.
Additionally, you could also perform a scan with alternative anti-malware software to check whether Win64:malware-gen Trojan detection is correct. Finally, you can also use free analysis tools like Virus Total - simply upload a file and check its detection rate.
Win64:malware-gen removal should be performed as soon as possible if the detection is not a false-positive. Trojans are particularly dangerous, as they can be equipped with an array of different functions. There are thousands of new malware samples released each day, so heuristics are one of the best ways to determine malware of such type.
In case no anti-malware software is installed on the targeted system Win64:malware-gen can cause significant damage to it, as well as the end-user. Here's what Trojans are capable of:
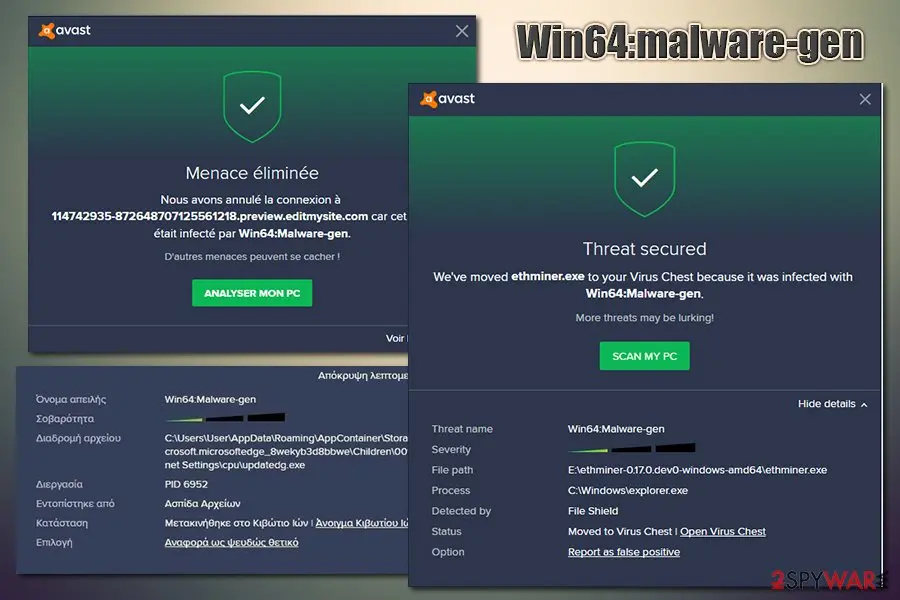
Repeated detection might also occur when an anti-malware app is incapable of eliminating all the malicious files, when particular background connections are established, or when the Win64:malware-gen virus attempts to destroy the security app's functionality. In such a case, you should access Safe Mode with Networking and perform a full system scan from there.
Additionally, since Trojans are considered to be serious types of infection, you should also take care of fixing your operating system post-infection - you can use automatic tools like for the purpose. Additionally, since Win64:malware-gen is a Trojan, it could have stolen your personal information, so we advise you to monitor your online banking and change passwords for all your accounts.
- Install other malware;
- Give cybercriminals a remote access via the compromised PC;
- Use the infected computer as a spam tool;
- Take screenshots;
- Steal sensitive information such as logins, banking details, Social Security Numbers, etc.;
- Deliver intrusive advertisements;
- Include the host into a botnet, etc.
From our report of Jun 2020 · not reviewed since
More from our earlier report on Win64:malware-gen
- In most cases, users encounter Win64:malware-gen pop-up via their security tools, most commonly, various Avast products.
- Win32:Malware-gen, Trojan.genericKDZ, Other:Malware-gen , IDP.Generic, Trojan.Win32.Generic, etc.
- Reset all the installed web browsers, change passwords, monitor your online banking and fix Windows issues with tools like
How to remove Win64:malware-gen
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Win64:malware-gen or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever Win64:malware-gen installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Jun 2020 · not reviewed since
Prevent Trojan infections by following these tips
As mentioned above, Trojans are very flexible and can perform a variety of different actions, based on what the attackers program it to do.
The ramifications of a malware infection can be significant, as personal information theft can destroy credit scores, result in monetary losses, and result in identity theft/fraud. Therefore, it is extremely important to protect your computer from such infections, and there are several methods that would help you with that.
Of course, no methods can provide 100% security, as any machine can be breached if enough effort is put into it. However, the more security measures are applied, the less likely it is to happen. Thus, follow these useful tips provided by security experts from dieviren.de:
- Employ powerful security software that uses various analysis methods;
- Patch your computer with the latest security updates (as well as the installed software);
- Do not download software cracks or pirated applications;
- Never allow spam email attachments to run macro function;
- Upload unknown files to free sandbox analysis services like Virus Total;
- Enable Firewall and ad-block;
- Use strong passwords for all your accounts;
- Disable Remote Desktop connection as soon as you don't need it and never use a default port for it.
From our report of Jun 2020 · not reviewed since
Remove Win64:malware-gen if it is not a false-positive
As previously mentioned, there are several scenarios where you can encounter the Win64:malware-gen virus alert.
In most cases, you should not think about it is much, as your security software should get rid of it automatically. However, difficulties arise when a legitimate file is flagged as malicious, and you should investigate further. If you are not sure whether the file is connected to malware, you should first make sure that your anti-malware is up to date.
If that does not help, you should scan the device, an alternative security tool, or upload it to virustotal.com. In case it is flagged by many other AVs, you should not hesitate to remove Win64:malware-gen as soon as possible.
If, for some reason, you are unable to perform Win64:malware-gen removal smoothly, you can access Safe Mode with Networking, as we explain below.
[GI=method-1]If Win64:malware-gen is giving you troubles when trying to eliminate it, perform a full scan with anti-malware software in Safe Mode with Networking:
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed win64:malware-gen in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
Questions about Win64:malware-gen
What is Win64:malware-gen?
Win64:malware-gen is a heuristic detection name used by antivirus providers like Avast to identify trojans on 64-bit Windows systems. Trojans are among the most prevalent and versatile threats, and their working mechanisms vary vastly. However, all trojans share a common trait:
- users become infected when they open a malicious file believing it is legitimate
- such as a software crack
- spam email attachment
Most users encounter Win64:malware-gen through security tool notifications, commonly from Avast products. The heuristic detection method analyzes behavior rather than matching signatures, leading to inconsistencies and false positives.
Can Win64:malware-gen be a false positive?
Yes. Heuristic-based detection frequently generates false positives where legitimate files are tagged as malicious. Many users have reported that legitimate files are incorrectly flagged or that detections reoccur regularly after removal.
These inconsistencies are common with generic malware analysis. Each case providing difficulties should be investigated carefully before action. If only Avast flags the file while other antivirus engines ignore it, a false positive is likely.
Legitimate files can get flagged as soon as they are introduced to the system or after a security software update.
How can I verify if the detection is accurate?
Upload the flagged file to VirusTotal to see how multiple security engines classify it. If many antivirus vendors flag it as malicious, the detection is more credible. If only one or two vendors detect it, especially if others ignore it, the likelihood of a false positive is higher.
Alternatively, contact the software developer to clarify whether the file belongs to their product and whether detection is expected. You could also scan with different anti-malware software to get a second opinion on whether the file is genuinely malicious.
How do trojans infect systems?
Trojans spread through many channels including spam emails, pirated software installers, software cracks and keygens downloaded from torrent sites, malicious links, and fake updates.
Trojans perform various malicious tasks on infected machines including sending spam, stealing sensitive information, taking screenshots, injecting other malware, and facilitating remote access. Users often unknowingly assist the infection by opening attachments or executing downloaded files thinking they are legitimate.
What damage can Win64:malware-gen cause?
Infection can lead to significant financial losses, infiltration of other malware, complete data loss, sensitive data disclosure, and identity theft. The trojan might use your infected computer as a spam tool, include your host into a botnet, or steal passwords and banking details.
Repeated detections may indicate the anti-malware is struggling to eliminate all malicious files or that the trojan keeps attempting to restore itself. In such cases, accessing Safe Mode with Networking and running a full system scan is necessary.
What should I do if this is a false positive?
If you determine the detection is a false positive on a trusted file, add the file to your antivirus exclusion list. Open your security software settings, find the exclusion or whitelist section, and add the file path.
Update the antivirus so it no longer flags this file. If the flagged file is part of software you use regularly and trust, this approach preserves functionality while preventing repeated alerts. However, only exclude files you are confident are legitimate.
How do I remove a genuine Win64:malware-gen trojan?
Perform a full system scan with updated anti-malware software, preferably in Safe Mode with Networking to prevent the trojan from interfering. If Win64:malware-gen is giving troubles during elimination, Safe Mode ensures the infection cannot block removal processes.
Do not attempt manual removal, as trojans hide components throughout the system. After removal, change passwords for all important accounts and monitor online banking for fraudulent activity. Use system recovery tools to repair any damage the trojan may have caused.
How can I prevent trojan infections?
Employ powerful security software using various analysis methods and keep it updated. Patch your computer with latest security updates and keep installed software current.
Do not download software cracks or pirated applications. Never allow spam email attachments to run macro functions. Upload unknown files to free sandbox analysis services like VirusTotal before executing them.
Use strong passwords for all accounts. Disable Remote Desktop connection when not needed and never use default ports for it. These measures significantly reduce trojan infection risk.
Will Fortect remove Win64:malware-gen?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Win64:malware-gen, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Avast: Avast keeps catching Virus : Win64:Malware-gen (read October 5, 2026)
- AV-Comparatives: Spotlight on security: The problem with false alarms (read October 5, 2026)
- Dieviren: Dieviren (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)