
Trojan.Win32.Generic: what it is and how to remove it
Trojan.Win32.Generic is a heuristic detection by multiple antivirus programs that may refer to any unknown trojan or malware infection exhibiting suspicious behavior. This generic alert sometimes represents false positives but should always be investigated when detected.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If Trojan.Win32.Generic keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove Trojan.Win32.Generic yourself 5 steps, about 15 minutes, no software needed.
Start the steps
Trojan.Win32.Generic: summary
| Distribution | The Trojan.Win32.Generic related virus can be distributed via pirated software, malicious websites, freeware additions, software cracks, spam email attachments, and other methods exploited by cybercriminals |
|---|---|
| Name | Trojan.Win32.Generic |
| Also known | HEUR.Trojan.Win32.Generic Generic.dx!vpv Trojan.Generic.5408453 Agent2.CBME TROJ_GEN.R42C3AR Trojan.BHO!IK Mal/BHO-AY HackTool:win32/autoKMS Win32/suptab!blnk, etc. |
| Classification | Generic AV detection, possibly Trojan or other malware infection |
| Symptoms | Trojan.Win32.Generic alert, if it denotes a malware infection, can be accompanied by high CPU usage, Windows freezes, prolonged bootup time, web browser's corruption, error messages, and regular AV popups warning about suspicious activities on the system |
| Danger level | High. Suchlike generic AV detections are usually triggered by Trojans[2] or Spyware, meaning that the system may be infected with a malicious virus that may try to steal your credentials, personally identifiable information or lock/leak data stored on the hard disk |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Type | Loader |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 7 October 2020 |
| Facts checked | 5 October 2026 |
What Trojan.Win32.Generic does on an infected PC
From our report of Oct 2020 · not reviewed since
Trojan.Win32.Generic - a generic AV alert flagging an unknown software caught due to malicious activities
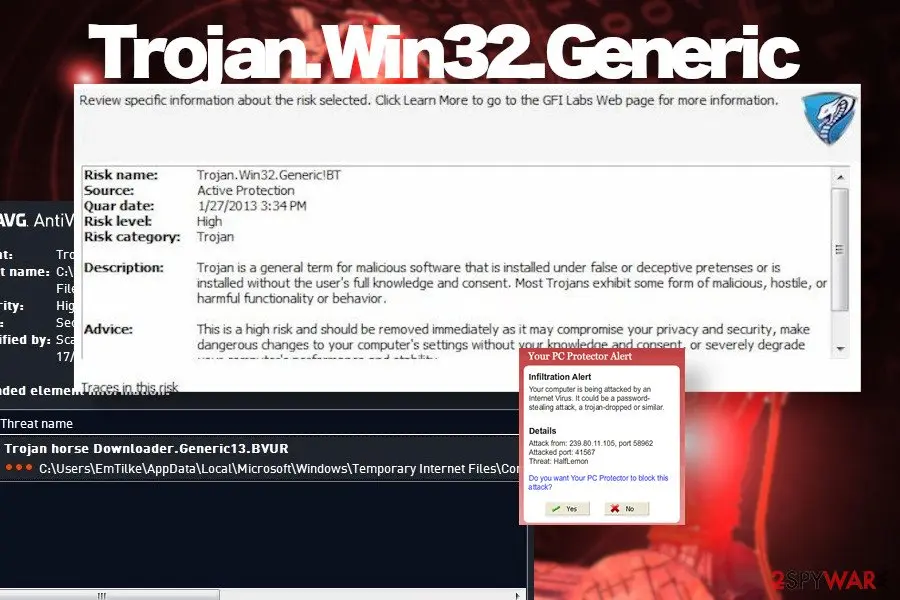
Trojan.Win32.Generic is a heuristic detection by multiple antivirus programs, which may refer to a Trojan or another previously unknown virus infection.
Multiple cybersecurity websites associate this detection with a Trojan, though, in fact, it can be related to any other malware type, including ransomware, spyware, keylogger, adware, and etc. In most of the cases, this alert may be accompanied by long system boot time, high CPU usage, and software freezes.
This applies if Trojan.Win32.Generic determines respectability towards a particular system's threat. Nevertheless, in some of the cases, this detection may be false-positive or a false alarm indicating a non-existent threat.
Also known as HEUR.Trojan.Win32.Generic, the Trojan.Win32.Generic virus may indicate a newly released virus that exhibits never-seen-before activities that an AV engine recognizes as malicious. However, it may also denote a variant of a virus that is already spreading in the wild. This particular detection can be possibly related to Zeus and Andromeda Trojans.
There are many ways of Trojan.Win32.Generic malware infiltrating the system. Typically, PC owners are tricked into downloading malicious entries on email messages, which often look harmless and reliable. In addition, the Trojan may be injected using the drive-by-download method, when a Trojan-carrying program automatically gets downloaded onto the system without user's granted permission for the download.
Apart from the mentioned methods, malware can be installed along with pirated software, game cracks or fake updates. In these cases, the user is more or less aware of the risks that he or she takes relying on illegal/compromised software.
The criminals behind the Trojan.Win32.Generic virus may try to initiate a multitude of malicious activities, such as:
As pointed out by dieviren.de cybersecurity team, Trojan.Win32.Generic virus detection by any reputable anti-virus program may be triggered by a newly released ransomware variant of such infamous families as Djvu, STOP, CryptoMix, Dharma, and many others. Therefore, the emergence of regular popups by your AV engine that flag a malicious activity by Trojan Win32 Generic should be treated seriously.
To prevent data encryption, loss of important documents, financial information, the system's crash, and similar activities, an immediate Trojan.Win32.Generic removal is required. Even though the antivirus engine is powerful enough to detect and quarantine the malicious entry, it may not be able to finish up the removal process.
That's because the antivirus database may not contain the signature of the detected infection. In this case, you may need to install the latest AV definition updates.
Moreover, security software may fail to remove Trojan.Win32.Generic virus because its scanner is terminated once launched. to bypass the block, try to restart the system into Safe Mode.
If, however, the system does not exhibit abnormal behavior, but the AV that you are currently using keeps reporting Trojan.Win32.Generic malware, try an alternative anti-virus engine and compare their findings. Since such heuristic detections can sometimes be false-positive, you may be looking for a non-existent virus.
- diminish the system's protection to open a backdoor for other cyber infections;
- connect to remote servers and download malware without user's awareness;
- initiate tracking activities with an intention to collect confidential information, including credit card details, passwords, login data, etc.
- compromise web browser's settings in a way to trigger redirects to phishing websites;
- generate aggressive pop-ups, hyperlinks, banners, and another context that may expose a potential victim to dangerous viruses or offensive material;
From our report of Oct 2020 · not reviewed since
More from our earlier report on Trojan.Win32.Generic
- Trojan.Win32.Generic removal is possible with a professional AV tool only.
- This detection signals a malicious infection, which may root into Windows registries and hack the core system's files.
- Nevertheless, the AV program may only be able to quarantine the infection, but the removal may require launching updates of databases and modules
- The repair of any damage caused to the inner Windows system files and registries will not be obtained by Trojan.Win32.Generic removal.
- A powerful recovery tool, such as is required
How Trojan.Win32.Generic got on your PC
From our report of Oct 2020 · not reviewed since
Although there are more techniques for virus/malware distribution, the most common places where people get tricked into installing malicious pieces of malware are infected websites, pirated software or freeware download websites, and leaked email accounts.
Despite the fact that potential victims are not aware of a possible virus attack, the installation of Trojan, spyware or other malware is seldom possible with the user's intervention. In most of the cases, people are redirected to phishing websites or websites with hacked URLs after clicking on a questionable popup, hyperlink or visiting adult content websites intentionally.
The same applies to the software that carries malware. Apart from some exclusions, legitimate software distributed on official websites or other reliable sources is checked and signed as safe to download. However, if the user relies on freeware download websites that are publicly described as a source for malware, as well as searches shady forums for cracks and keygens, the user takes the responsibility for a possible virus infection.
The best piece of advice is to raise consciousness about dangers online. Do not rely on freeware just because they are offered for free. Keep in mind that these sites get monetized in other ways, for example, receive commissions for distributing malware.
However, the biggest malware download source remains malicious spam emails. Criminals take advantage of botnets to send thousands of infected emails to leaked email addresses. Typically, these emails are poorly written, contain many mistakes and are received from suspicious senders. Therefore, email filters typically send such emails to a spam folder by default.
However, there are many "successful" spam campaigns that mimic well-known organizations like Red Cross or FedEx. Such messages may contain reliable information, well-developed style, convincing details, trustful sender, and so on. It's advisable to double-check the sender or set the AV engine to scan the attachment of the email to make sure that it's not infected. Otherwise, it's best to delete such a message from the inbox.
How to remove Trojan.Win32.Generic
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Trojan.Win32.Generic or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever Trojan.Win32.Generic installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
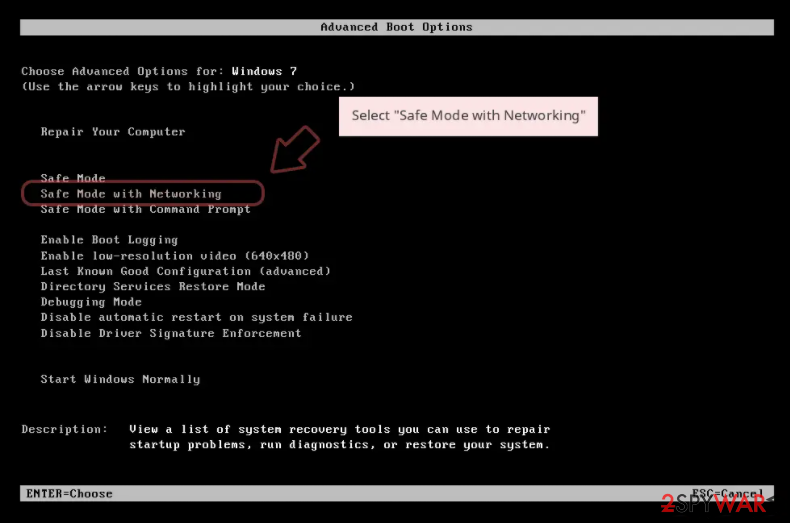
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
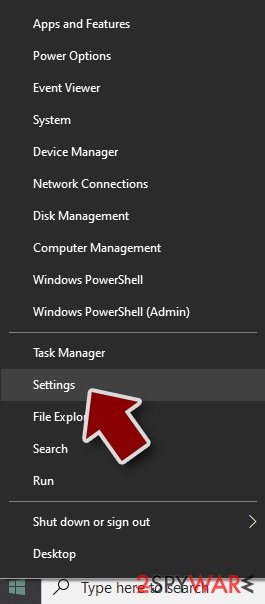
- Right-click on Start button and select Settings.
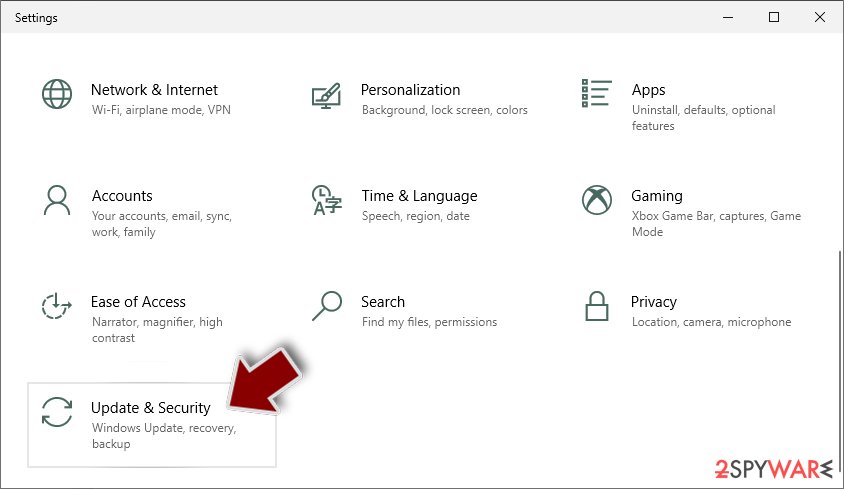
- Scroll down to pick Update & Security.
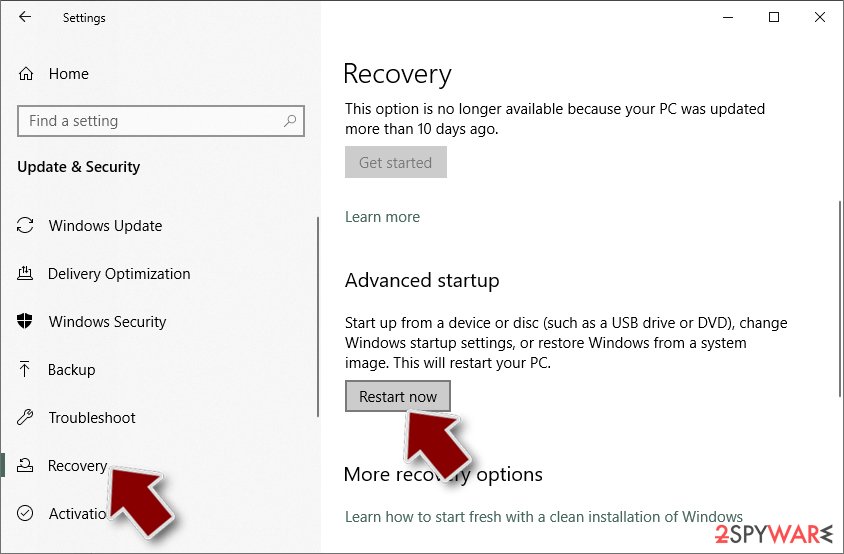
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
- Select Troubleshoot.
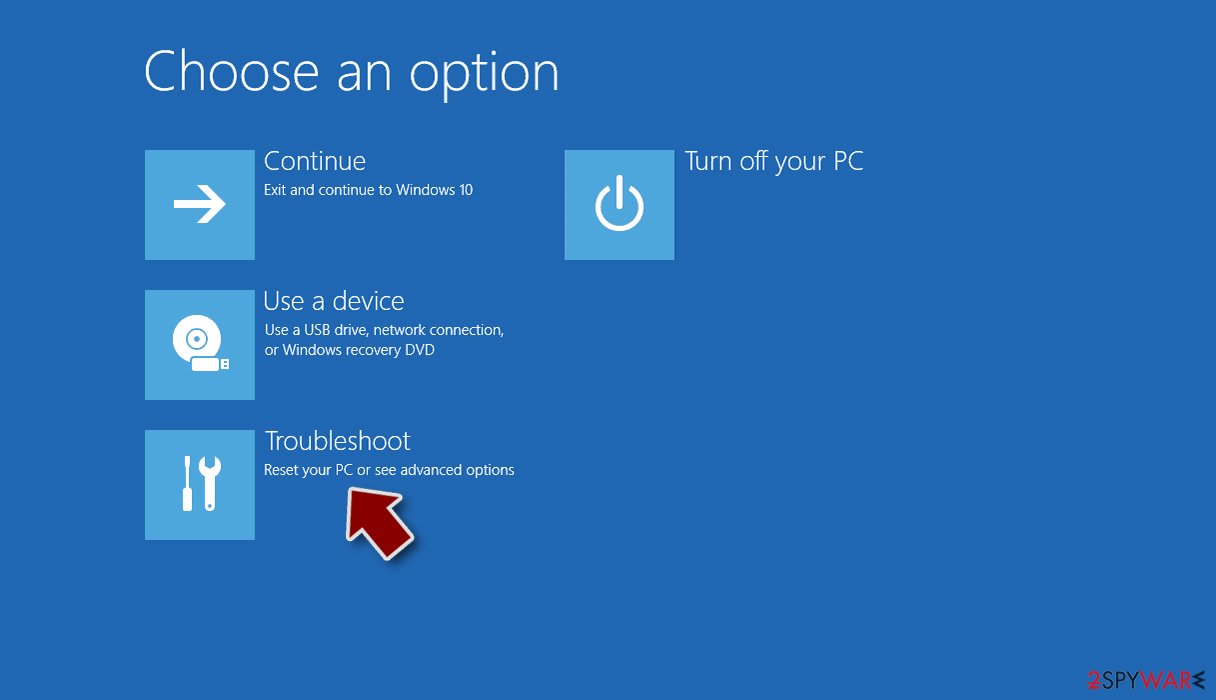
- Go to Advanced options.
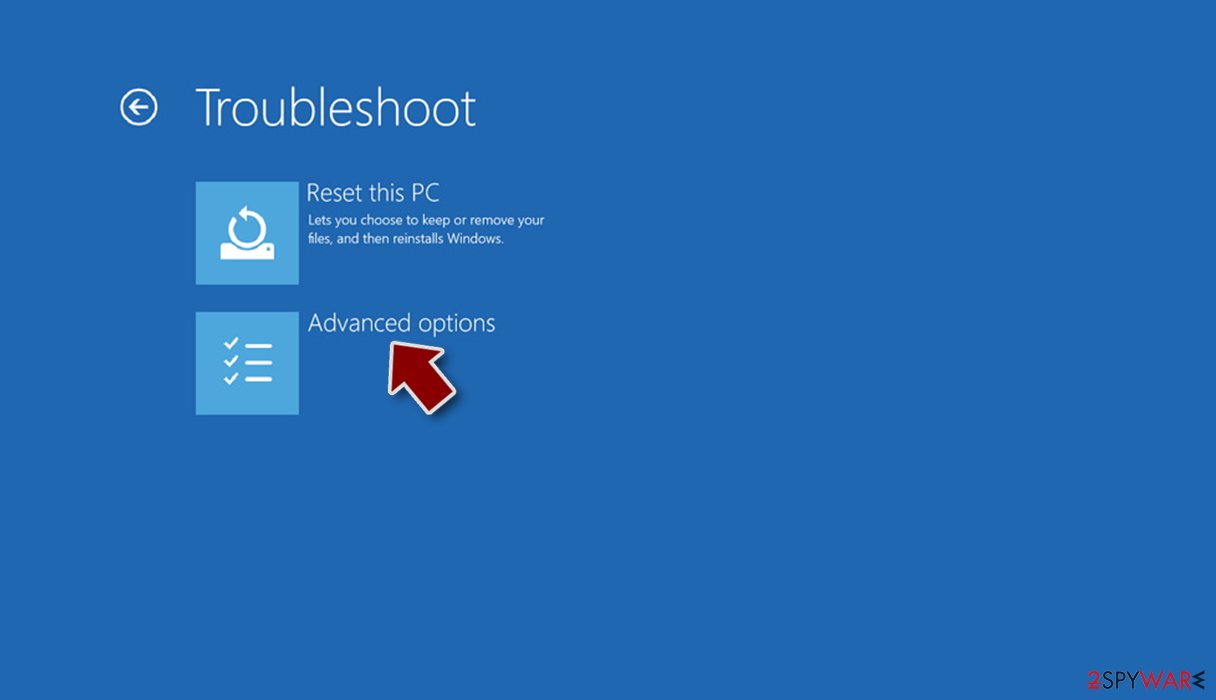
- Select Startup Settings.
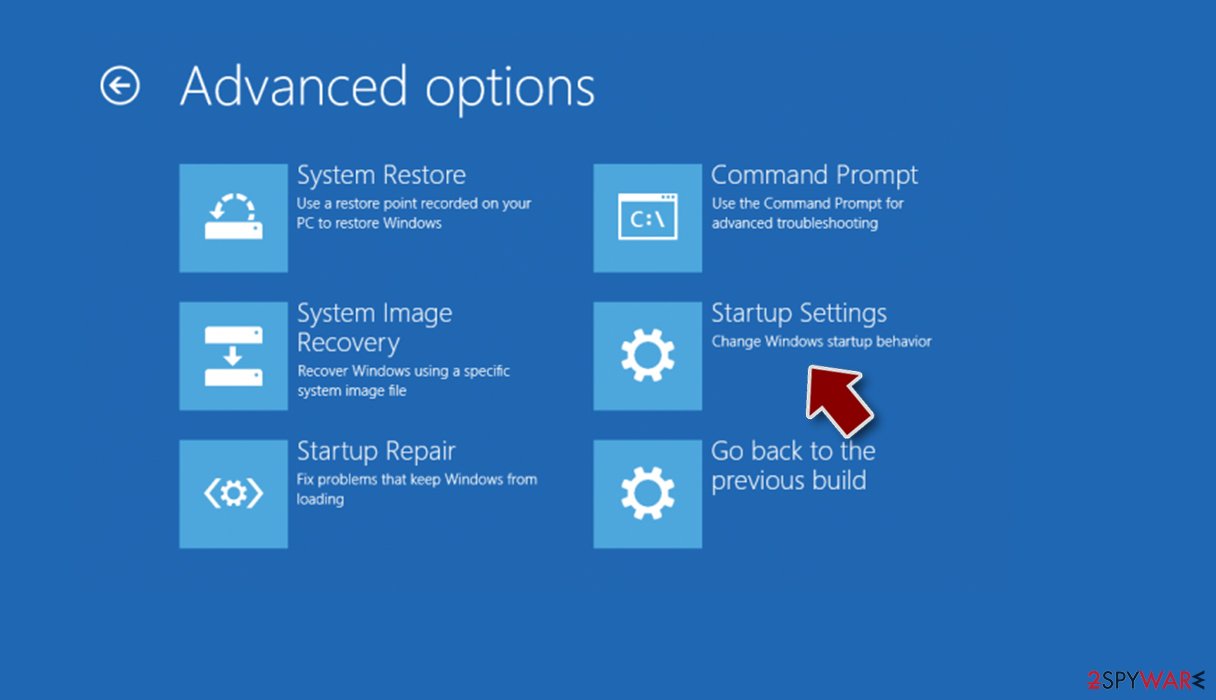
- Press Restart.
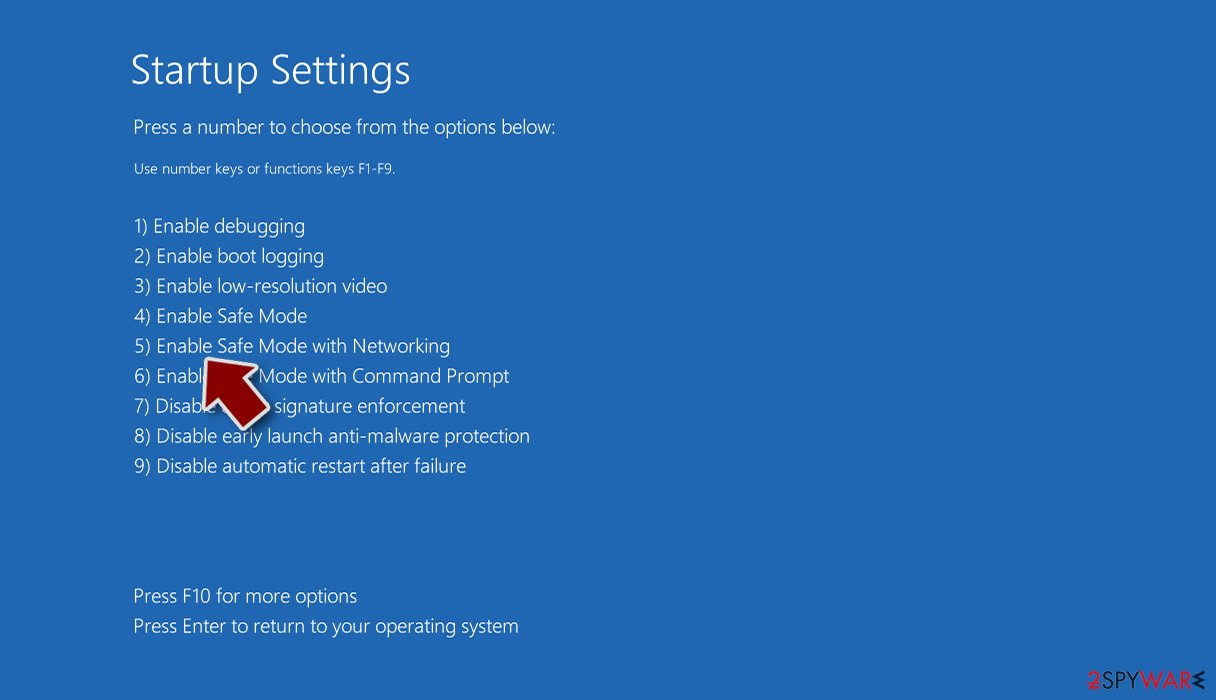
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
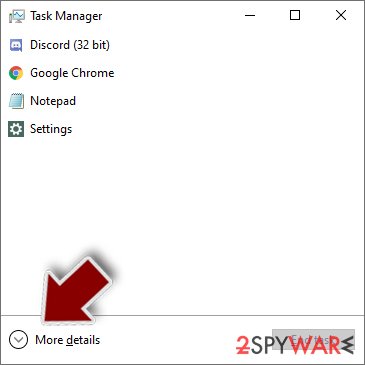
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
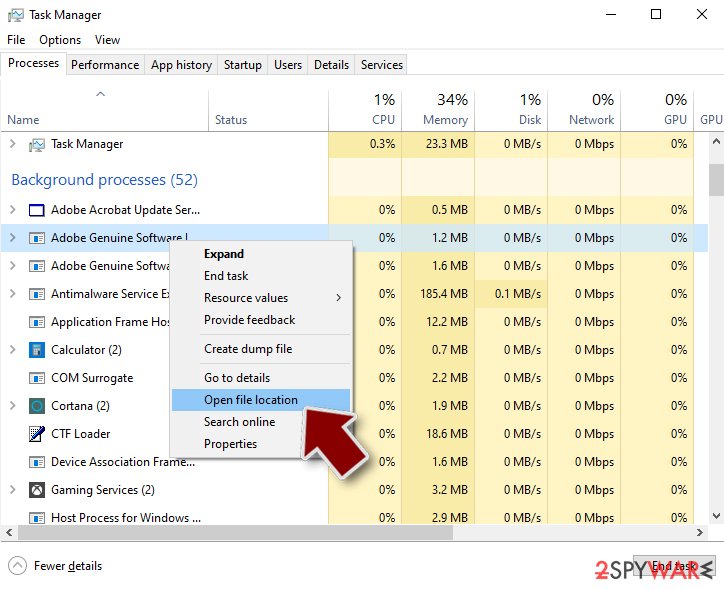
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
- Go back to the process, right-click and pick End Task.
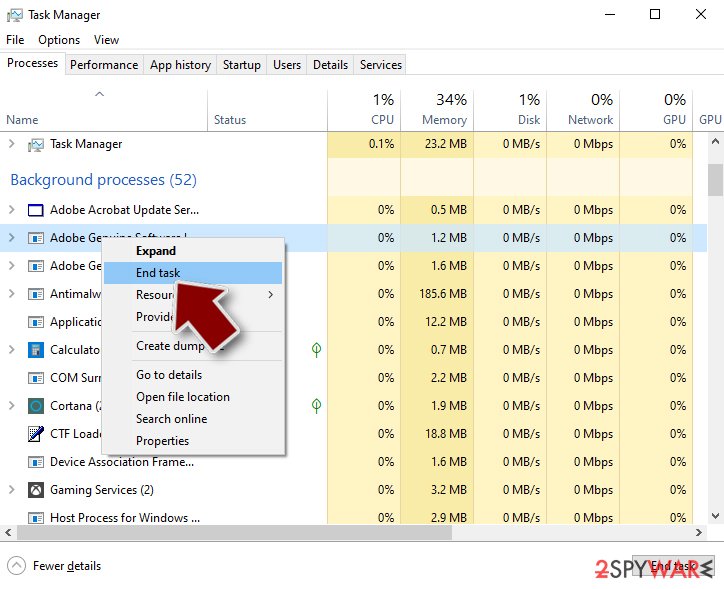
- Delete the contents of the malicious folder.
Step 3. Check program Startup
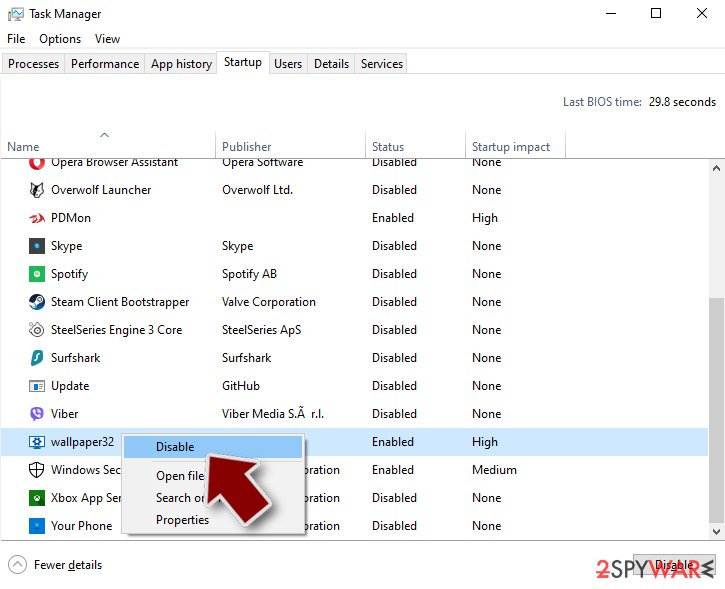
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
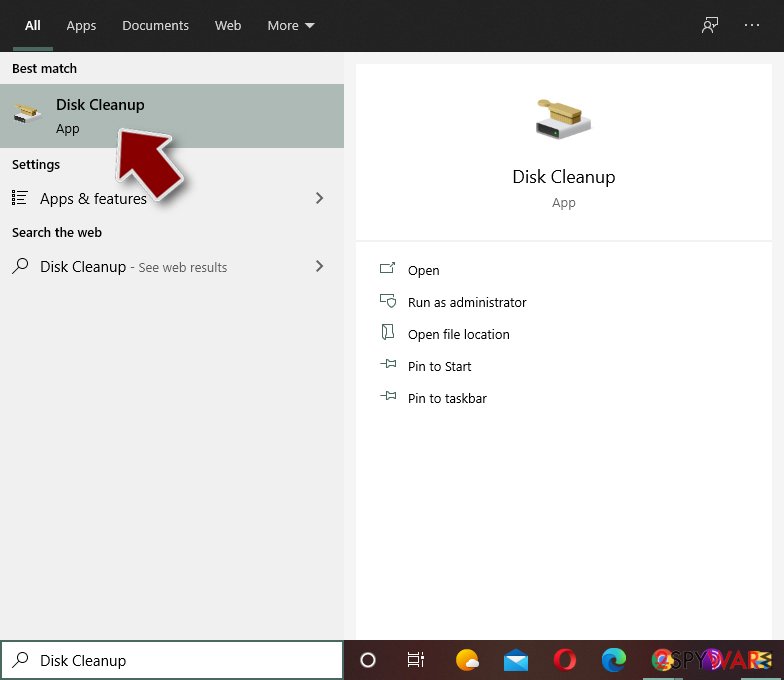
- Type in Disk Cleanup in Windows search and press Enter.
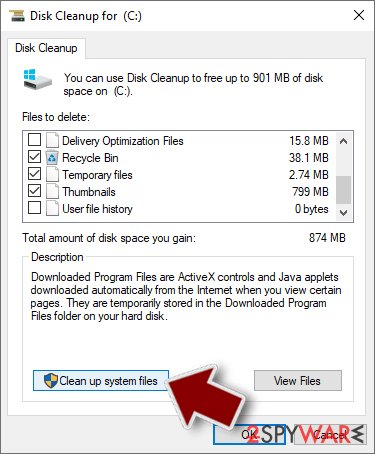
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Oct 2020 · not reviewed since
Eliminate Trojan.Win32.Generic virus from the system immediately to prevent possible damage
Having Trojan.Win32.Generic malware on the system poses a high risk of cyber attacks.
Criminals may be using this infection for the distribution of ransomware, spyware, keyloggers and similar viruses that may cause money loss or identity theft.
Even though the machine that is said to encounter this generic infection is not exhibiting suspicious activities and does not seem to be infected, beware that Trojans and likewise malware are exceptionally persistent. Malicious files may be dispersed in various system areas and block AV engines to remain unnoticed.
To ensure successful Trojan.Win32.Generic removal, go to the Safe Mode with Networking, a thorough guide on how to do that is given down below, and try to download the latest virus definition updates for the security software that you are using. After that, while still in Safe Mode, run a deep system scan.
The mentioned programs are capable of detecting malware and eliminated all related malicious entries. In addition to elimination of the malware, you should also take care of the system's stability, which may be breached. can help in fixing corrupted registry entries, deleting duplicates, and eliminated other side effects caused by virus infection.
[GI=method-1]Since your anti-virus may be blocked malicious processes, boot the system into Safe Mode to remove Trojan.Win32.Generic once and for all
[GI=method-2]Elimination of viruses can be initiated with the help of the Windows Previous Version feature. To enable it, please follow this guide
After removal: passwords, accounts and prevention
Your passwords after Trojan.Win32.Generic
Removing Trojan.Win32.Generic does not undo what it may already have sent out while the PC showed trojan.Win32.Generic in the list of installed apps.
Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Trojan.Win32.Generic
What is Trojan.Win32.Generic?
Trojan.Win32.Generic is a heuristic detection by multiple antivirus programs that may refer to a trojan or any previously unknown virus infection.
Because cybersecurity websites associate this detection with trojans, it typically represents malicious software, though it can relate to other malware types like ransomware, spyware, keyloggers, and adware. The generic nature of the detection means your antivirus cannot identify the specific threat—only that something exhibits malicious characteristics.
In most cases, this alert accompanies long system boot times, high CPU usage, and software freezes when the detection indicates a genuine threat. However, this detection is also known to produce false alarms where legitimate files are incorrectly flagged as malicious.
Is Trojan.Win32.Generic always a real threat?
No, Trojan.Win32.Generic sometimes appears as a false-positive indicating a non-existent threat. Although most detections are genuine, security tools can flag newly released viruses that exhibit never-seen-before activities that an antivirus engine recognizes as malicious but hasn't confirmed as threats. The detection can also denote a new variant of a virus already spreading in the wild.
In some cases, the detection is related to known trojans like Zeus or Andromeda, indicating genuine infections requiring removal. However, you should verify whether the detection is real before taking action. Scanning the flagged file with multiple security tools helps determine genuineness—if most tools flag it, it's malicious; if only one flags it, it's likely a false-positive.
What are alternative detection names for this threat?
Trojan.Win32.Generic appears under various alternative detection names from different security vendors, including HEUR.Trojan.Win32.Generic, Generic.dx!vpv, Trojan.Generic.5408453, Agent2.CBME, TROJ_GEN.R42C3AR, Trojan.BHO!IK, Mal/BHO-AY, HackTool:win32/autoKMS, and Win32/suptab!blnk. Different antivirus companies use their own naming conventions for generic detections, so the same file might generate different detection names from different security tools.
This variation in naming is why it's essential to use multiple security tools for verification—you need to determine if different scanners agree on the threat's presence. If your primary antivirus flags something under one name while other tools clear it completely, the detection is likely a false-positive.
What symptoms indicate Trojan.Win32.Generic infection?
Genuine Trojan.Win32.Generic infections can produce multiple symptoms indicating malware presence. High CPU usage even when not running demanding applications suggests resource-abusing malware. Windows freezes and prolonged bootup times indicate system corruption or background malicious processes.
Web browser corruption, including unexpected crashes or error messages, suggests browser hijacking trojans. Regular antivirus pop-ups warning about suspicious activities confirm security software detecting ongoing malicious behavior. However, not all genuine infections produce obvious symptoms—many trojans operate completely silently in the background.
The malware might be stealing information, opening backdoors for remote access, or deploying additional malware without causing noticeable performance issues. This is why regular security scans are essential—they catch silent threats before they cause detectable problems.
How does Trojan.Win32.Generic get on my computer?
Trojan.Win32.Generic infections arrive through multiple distribution methods. The most common vectors are pirated software, with users downloading malicious installers for cracked games or software. Malicious websites containing exploit kits automatically download trojans when you visit.
Freeware additions bundled with legitimate software often contain hidden malware. Software cracks and keygens from suspicious sources are notoriously malicious. Spam email attachments disguised as documents frequently distribute trojans.
Each method depends on tricking users or exploiting security vulnerabilities. Users are often more aware of the risks with pirated software but underestimate dangers from legitimate-looking email attachments or websites they visit through normal browsing.
Can Trojan.Win32.Generic lead to ransomware?
Yes, antivirus engines frequently detect ransomware variants under the Trojan.Win32.Generic name, particularly new strains from infamous families like Djvu, STOP, CryptoMix, and Dharma. When your antivirus reports this generic trojan detection, there's significant risk that ransomware could be present on your system.
Regular pop-ups from your antivirus engine flagging Trojan.Win32.Generic should be treated seriously because it may indicate an emerging ransomware variant your security software recognizes as malicious but hasn't specifically identified.
To prevent data encryption and file loss, immediate removal is essential. The longer you delay addressing this detection, the greater the risk that ransomware activates and locks your files with encryption demands.
Why can't my antivirus fully remove it?
Even powerful antivirus engines sometimes struggle to completely finish removal of Trojan.Win32.Generic virus. The antivirus database might not contain the complete signature of the detected infection, preventing full removal. Your security software may succeed in quarantining the malware but fail to eliminate all related files and registry modifications.
The antivirus database requires latest definition updates, and scanning with outdated definitions might miss components. Additionally, malicious processes might terminate the antivirus scanner itself, preventing the removal process from completing.
In such cases, restart your system into Safe Mode where the malware cannot interfere with removal processes. Download latest antivirus definition updates before scanning. Try alternative security tools if your primary antivirus cannot complete removal—different products may have better detection signatures.
How do I completely remove Trojan.Win32.Generic?
Complete removal requires rebooting your system into Safe Mode with Networking to limit malware's ability to protect itself. In Safe Mode, run your antivirus software with the latest virus definitions installed. Perform a comprehensive full system scan to detect all malware components.
If your current antivirus cannot remove the threat, install alternative antivirus software and run scans from it—different security tools have different detection signatures. After removal, repair system damage using recovery tools that fix corrupted registry entries and restore system stability.
Your system may experience performance issues until these repairs complete. Perform repeat scans to verify all malicious components are eliminated. Never remove files you're unsure about without first verifying they're genuinely malicious using multiple security tools.
Will Fortect remove Trojan.Win32.Generic?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Trojan.Win32.Generic, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Kaspersky: What is Heuristic Analysis? (read October 5, 2026)
- Panda Security: Trojan (read October 5, 2026)
- Dieviren: SICHERHEIT- UND SPYWARE-NEUIGKEITEN (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)