
Other:Malware-gen [Trj]: what it is and how to remove it
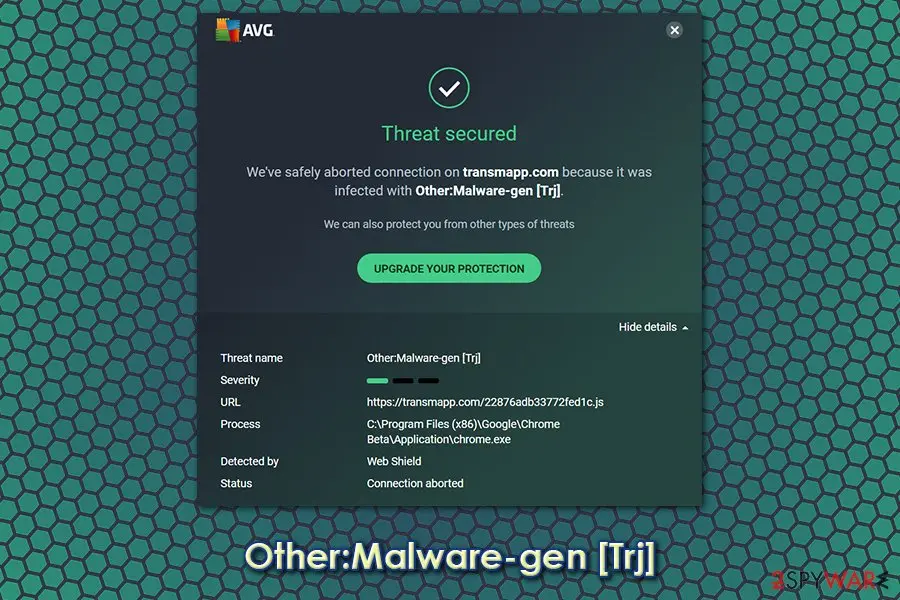
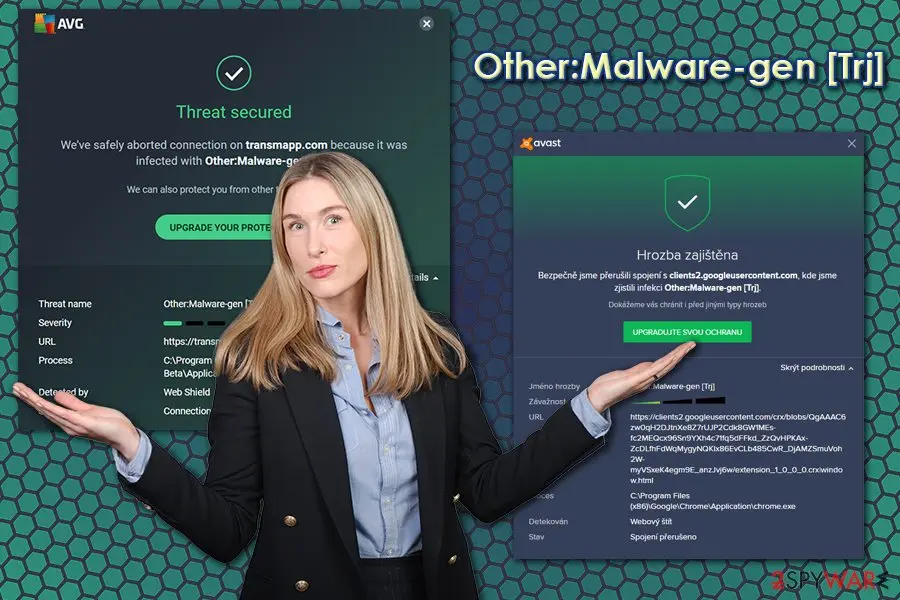
Other:Malware-gen is a heuristic detection name used by Avast and AVG for unidentified malicious activity on websites or in browsers. It may indicate true malware or a false-positive from corrupted security software.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan can look at Chrome.exe and the other programs installed around the same time.
Do it yourself · free Remove Other:Malware-gen [Trj] yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Other:Malware-gen [Trj]: summary
| Name | Other:Malware-gen [Trj] |
|---|---|
| Type | Malware (could be a false-positive) |
| Related | Win32:Malware-gen, Hacktool:win32/keygen, Win32:Dropper-gen |
| Infiltration | The detection might pop-up at any time and might stem from malicious browser extensions, installed apps, or various components stored within the browser. PUPs are malware that can be installed in various different ways, including software bundles, spam emails, exploits, fake updates, etc. |
| Symptoms | In the case of a Trojan infection, users are highly unlikely to experience visible infection symptoms, although it is possible to observe suspicious processes running in the background, as well as computer errors or crashes. However, in most cases, users only experience Other:Malware-gen [Trj] pop-ups regularly |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Distribution | Not recorded in the old report |
|---|---|
| Damage | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| File names | Chrome.exe |
| First seen | 29 May 2020 |
| Facts checked | 5 October 2026 |
What Other:Malware-gen [Trj] does on an infected PC
What readers reported about Other:Malware-gen [Trj]
removing system progessive protection. I attempted to remove the spyware with instructions online. When I run software for removal nothing happens. System just sits idle. Is there any other way to remove this?
How to get rid of incredibar?. I ve got a problem, everytime i start firefox it redirects me to other search engine 'MyStart' by IncrediBar. mystart.incredibar.com I'm trying to fing the answers in google, on incredibar virus removal, but it seems there is no information.. how do I get rid of it?
From the comments under our earlier guide; names and contact details removed.
From our report of May 2020 · not reviewed since
Other:Malware-gen - a heuristic detection name for malware that can be encountered on various websites
Other:Malware-gen is a computer infection that defines a particular type of computer applications or malicious online connections that can occur via Google Chrome or another web browser.
Users started to complain that the pop-up shows up as soon as they try to access relatively harmless websites, or even with every browser launch.
While Other:Malware-gen might also be a false-positive (in most cases, it occurs due to corrupted AV program files or outdated database), it is important to investigate each case carefully, as it might indicate malware. Nevertheless, it is possible to double-check it by scanning the device with a different security tool and then adding the particular website to exclusion if it is a false positive.
Users can only see the Other:Malware-gen detection if they have particular security applications installed on their devices. In most cases, the source for the detection seems to be Chrome.exe, although the websites that are detected as malicious can vary.
Users claimed that Other:Malware-gen pop-ups constantly return, even after the security software detects and seemingly sends the detected items to the quarantine. However, once the quarantine is checked, no files are shown inside. Nevertheless, users are soon reminded about the same issue, and they do not know how to remove Other:Malware-gen once and for all.
In case Other:Malware-gen is not a false-positive, it can be a result of real Trojan infection. These types of malicious applications are usually disguised as something legitimate, such as email attachment from a seemingly reliable source, or a useful application that was placed on a third-party website.
In some cases, users can encounter Trojans when they download software cracks or keygens - these are particularly dangerous as there is no way for a regular user to check whether such tools would actually result in malware infection.
Trojans such as Other Malware Gen Trj can be set to perform a variety of different tasks on the infected machine. Typically, the infection routine starts and completes very quickly, all while the Windows changes are applied in the background without users' noticing.
Depending on malware's features, Trojans can usually perform the following tasks on the infected machines:
As evident, Other:Malware-gen infection can cause serious financial losses, compromise privacy, and result in personal data loss. Therefore, it is vital to ensure that Trojans do not gain access to your system.
Since the detection of this kind can mean many things, there are also many ways to perform Other:Malware-gen removal. First of all, it is important to make sure as your security software is running on the latest version, as new definitions and updates ensure that false-positives are eliminated and do not bug users.
If the Other:Malware-gen virus detection is still present, we highly advise performing a full system scan with another security software, such as or . This second check will help to confirm or deny malware prescience on the system.
In case nothing is found, it is highly likely to be a false-positive, although we do recommend contacting the AV maker if some doubts remain. Finally, if your computer was indeed infected, eliminate malware and then fix the damage that was done to system files with .
In some cases, there might be some files that are hidden within Google's servers. In such a case, it is recommended to reset sync of the account. For more instructions, please check the bottom section of the article.
- Establish background connections to remote Command & Control servers controlled by hackers;
- Steal financial information, browser cookies, crypto-wallet data, etc.;
- Take screenshots and use video camera remotely;
- Proliferate other malware, such as ransomware, behind users' backs;
- Gain elevated privileges within the system, which allows the attackers to move laterally within the network if such exists;
- Send spam and connect the affected machine to a botnet, etc.
From our report of May 2020 · not reviewed since
More from our earlier report on Other:Malware-gen [Trj]
- The name is typically used by Avast or AVG security software and is typically connected to various browser-related components that might have been dropped by malicious scripts on various sites.
- There are several methods to eliminate the detection pop-ups.
- Scan your machine with another anti-malware software and then add an exclusion if it is a false-positive.
- Otherwise, reset Chrome Sync or the web browser itself
- If you machine was infected with malware, repair the damage done to it with tools like
- Avast and AVG did state that several domains where whitelisted after users reported that it was a false-positive.
How to check the PC for Other:Malware-gen [Trj]
- File:
Chrome.exe
How to remove Other:Malware-gen [Trj]
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where Chrome.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
Chrome.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like Other:Malware-gen [Trj] add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Other:Malware-gen [Trj], its publisher or created on the day the problem started.Delete those folders, and check
C:\Program FilesandC:\Program Files (x86)too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Other:Malware-gen [Trj] that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Other:Malware-gen [Trj] can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Reset Google Chrome if the Other: Malware-gen pop-ups keep coming back:
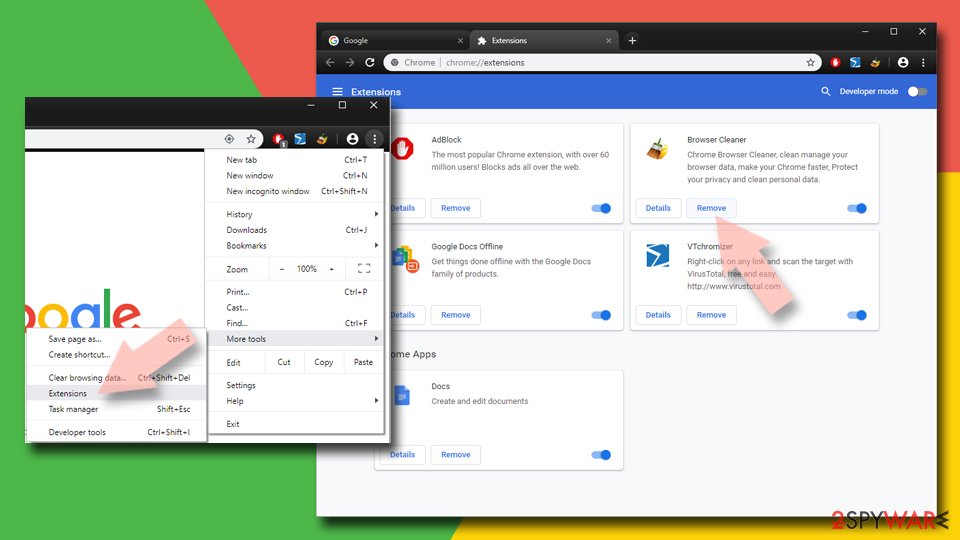
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
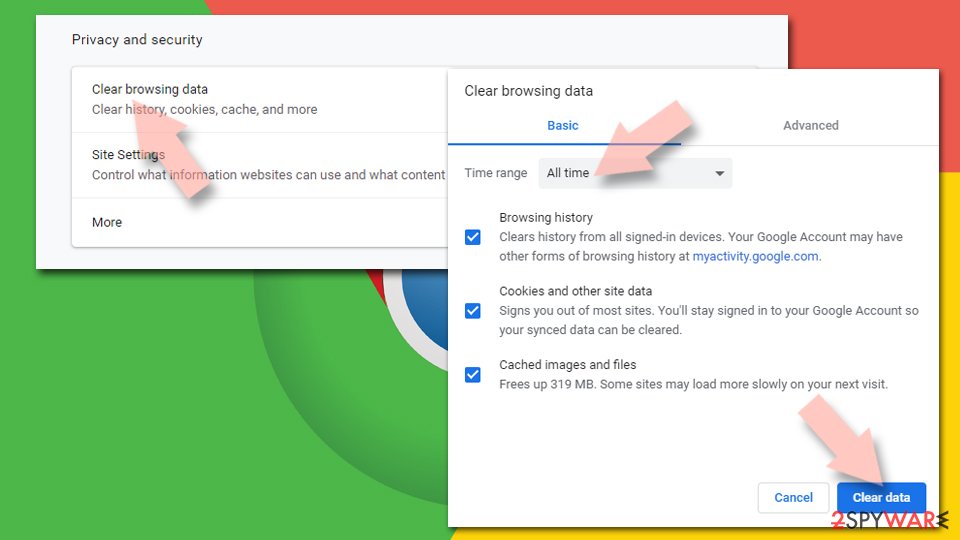
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
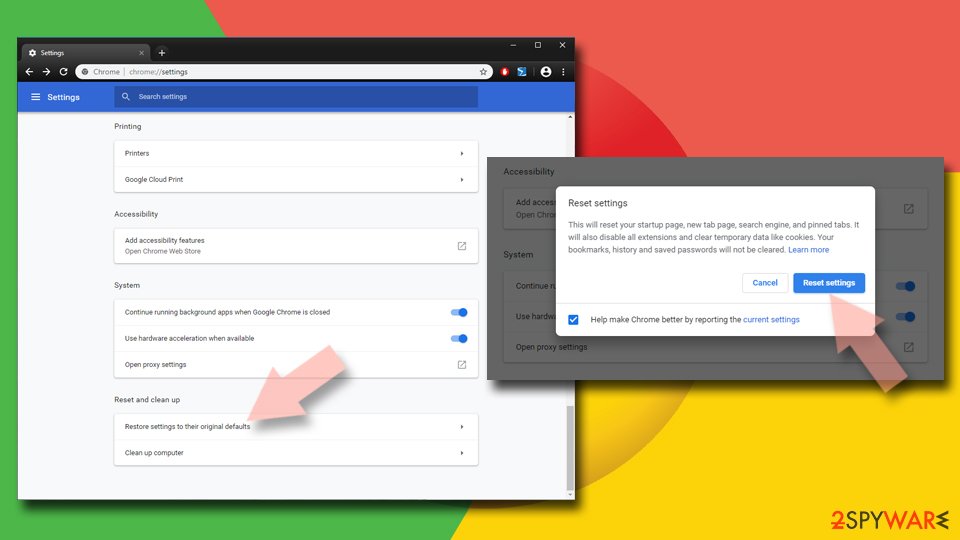
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
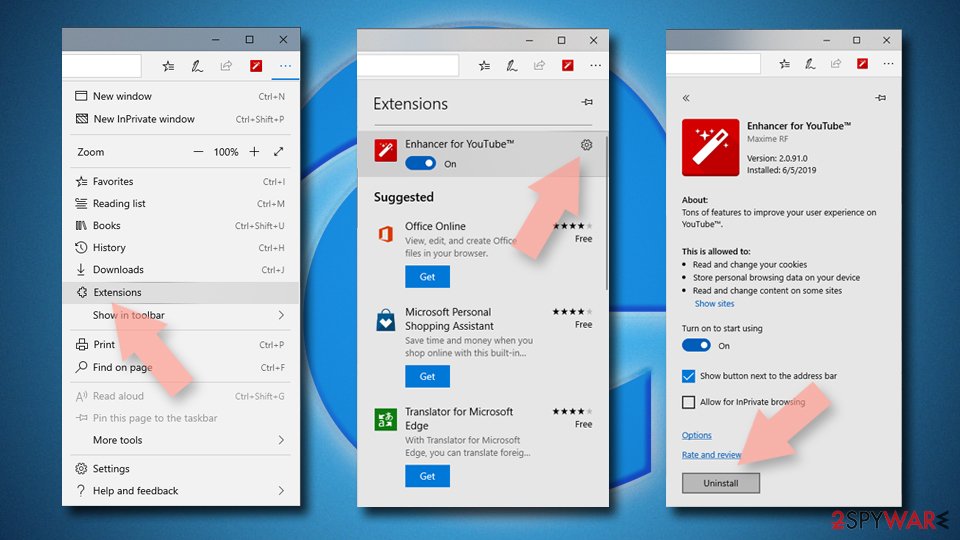
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
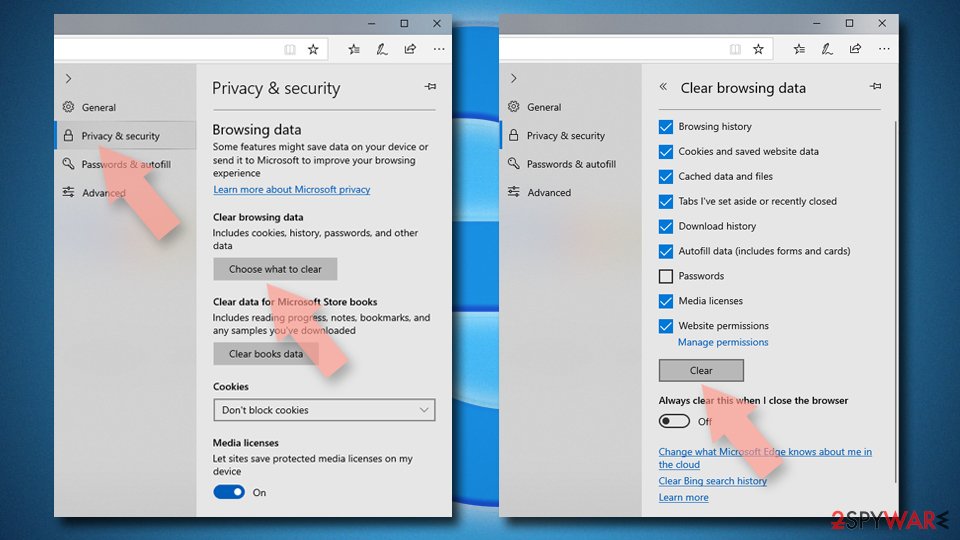
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
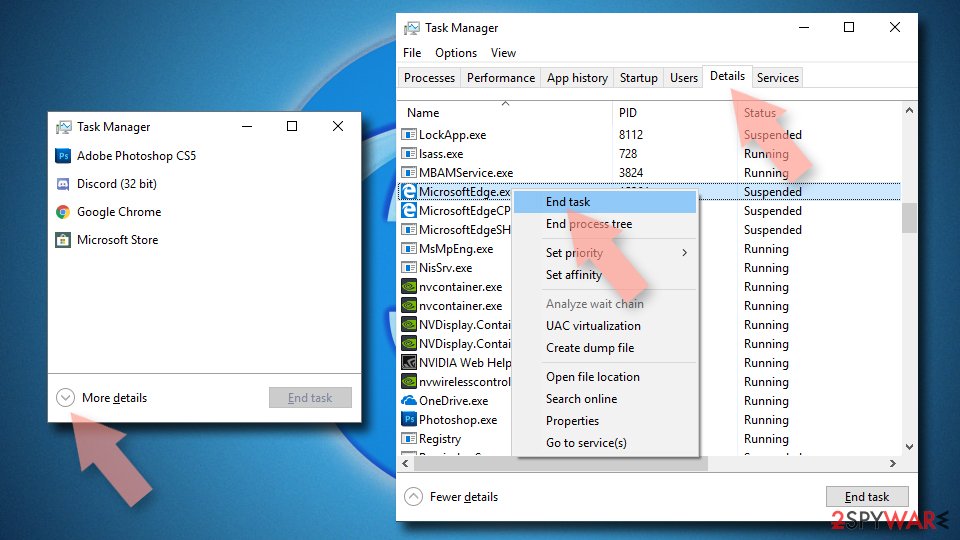
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
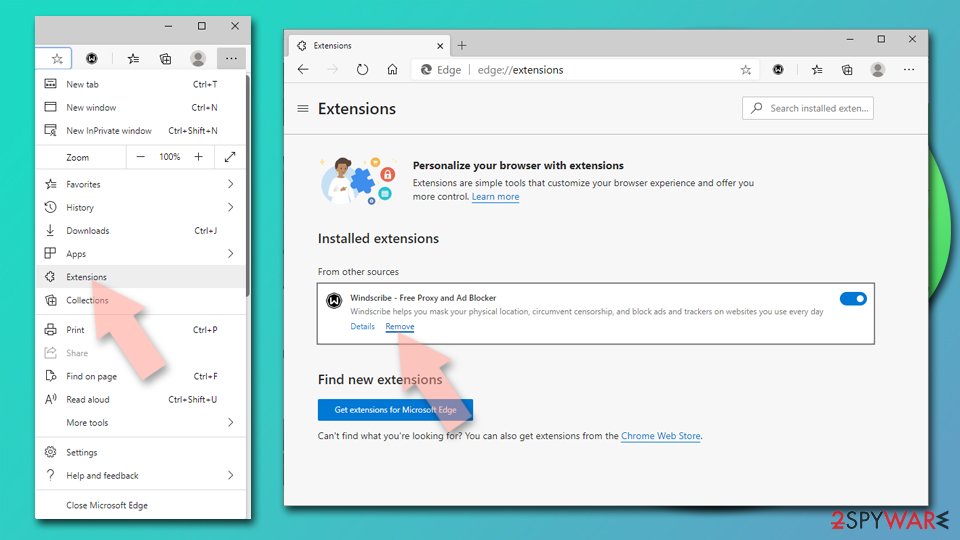
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
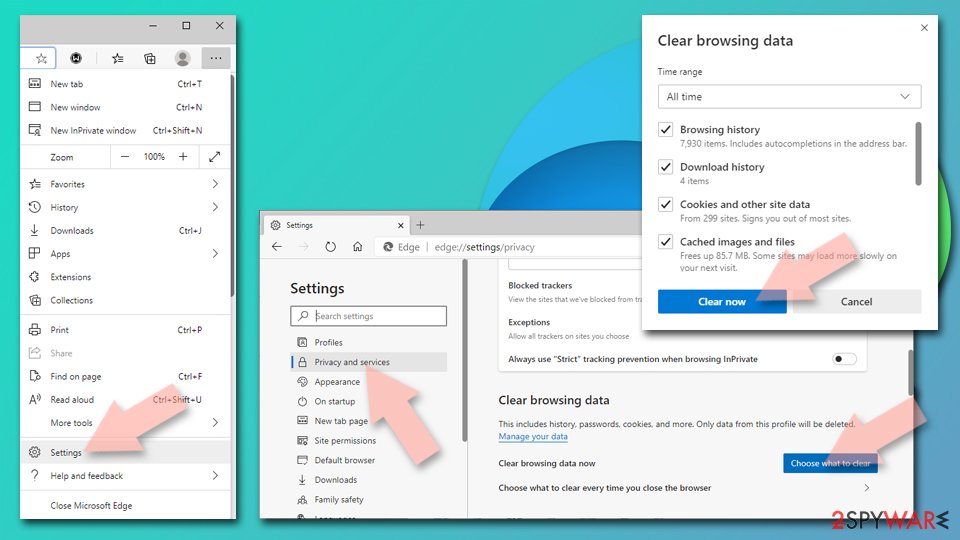
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
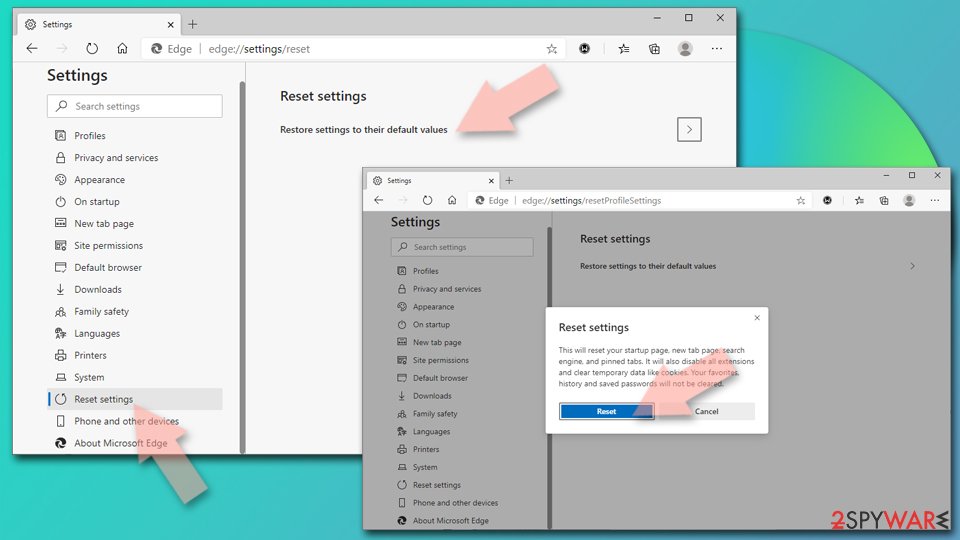
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
To reset Mozilla Firefox, please follow these steps:
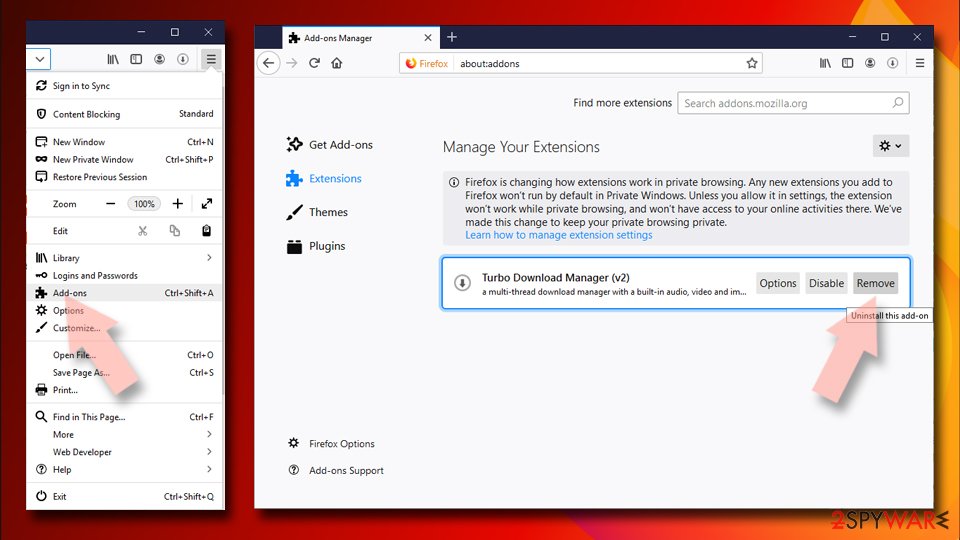
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
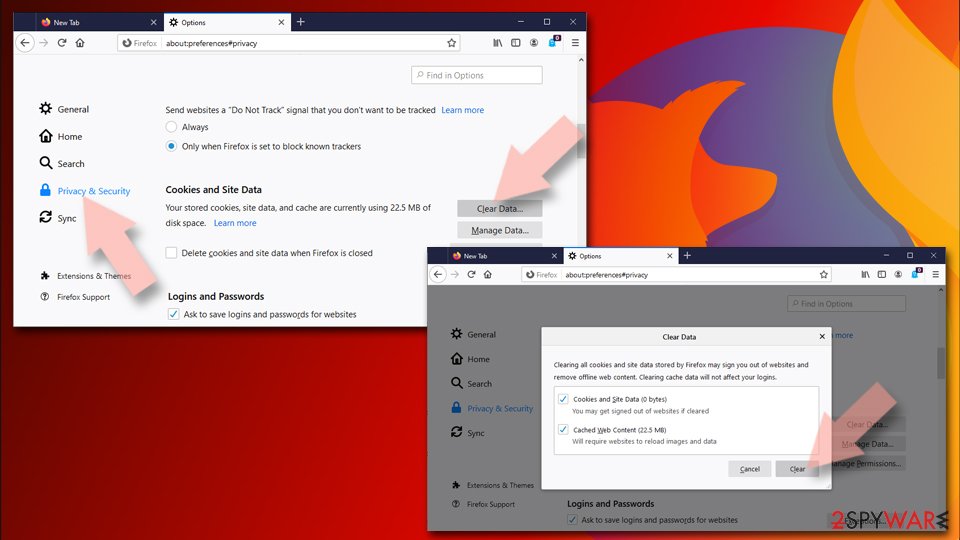
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
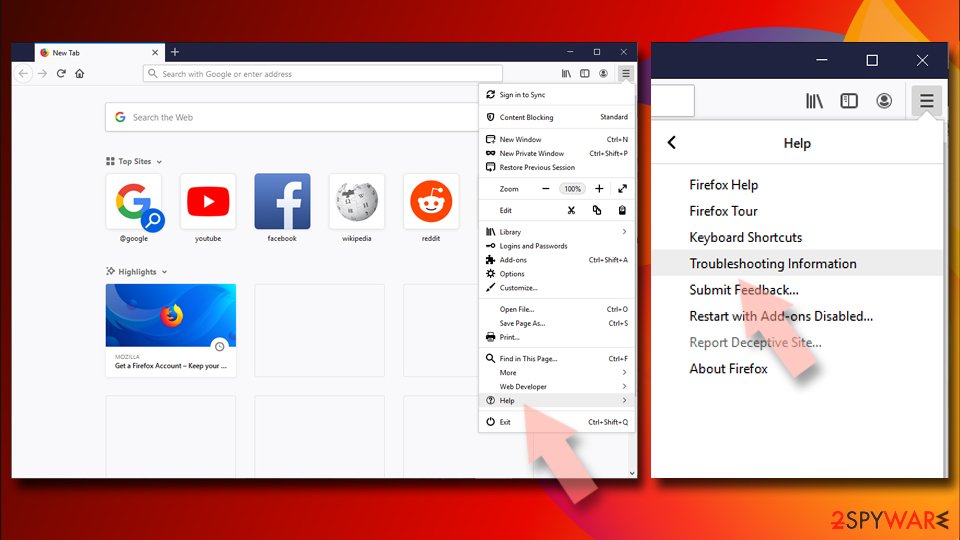
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
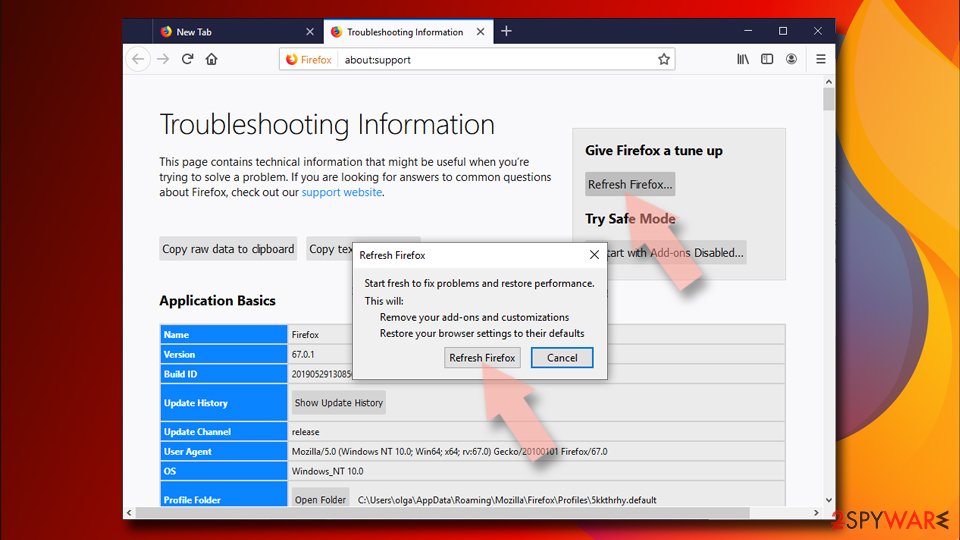
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
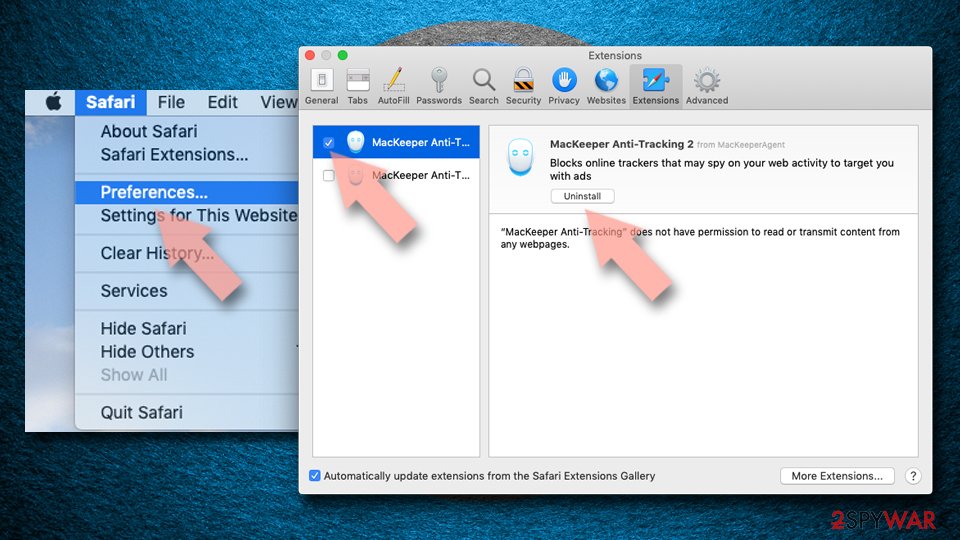
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
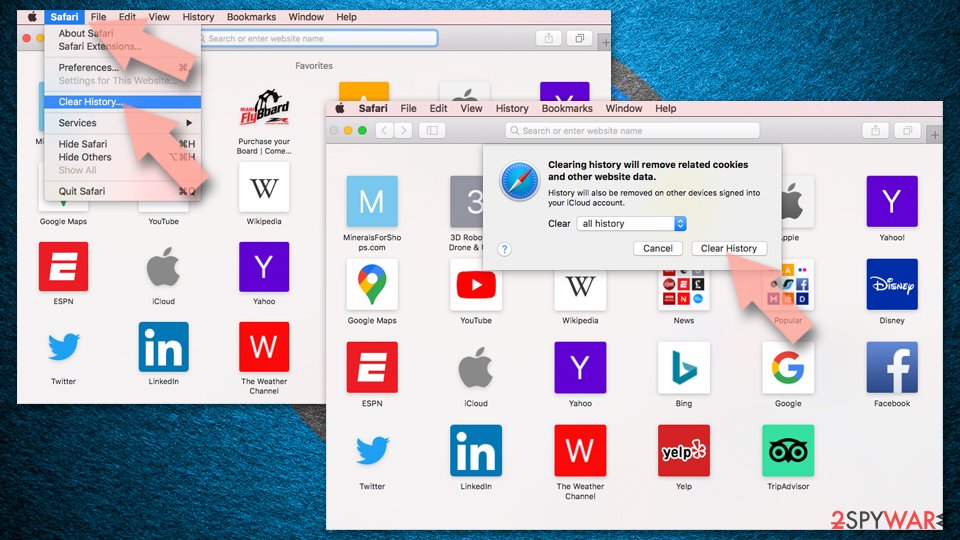
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
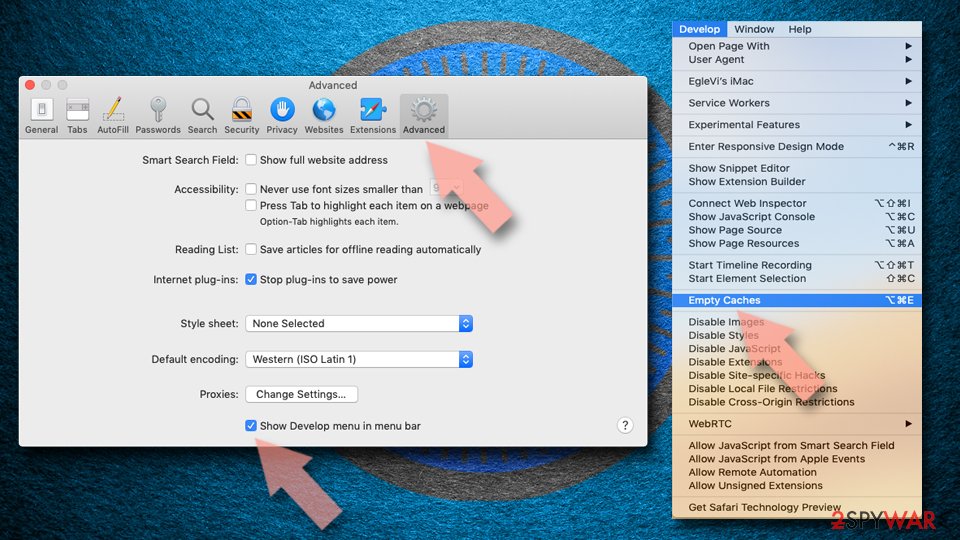
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Reset Internet Explorer
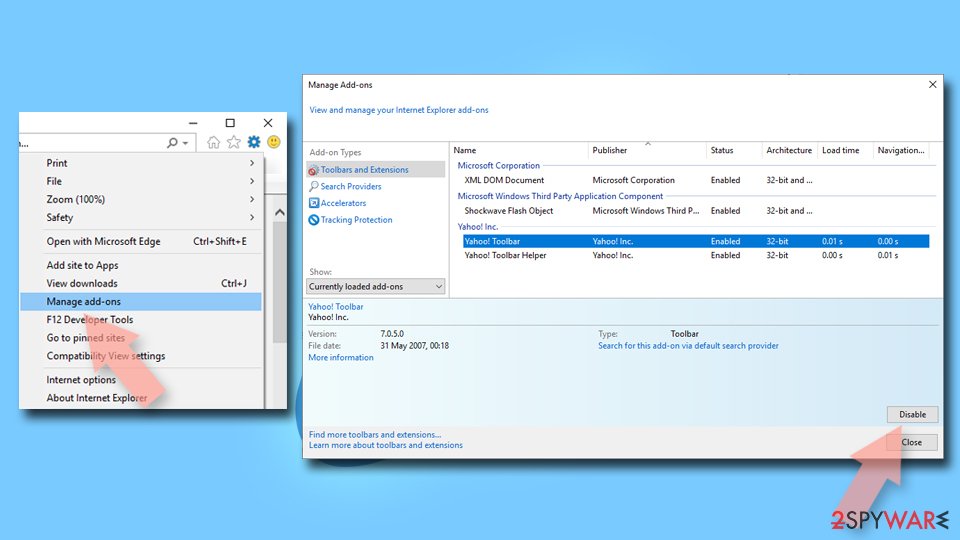
Remove dangerous add-ons:
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
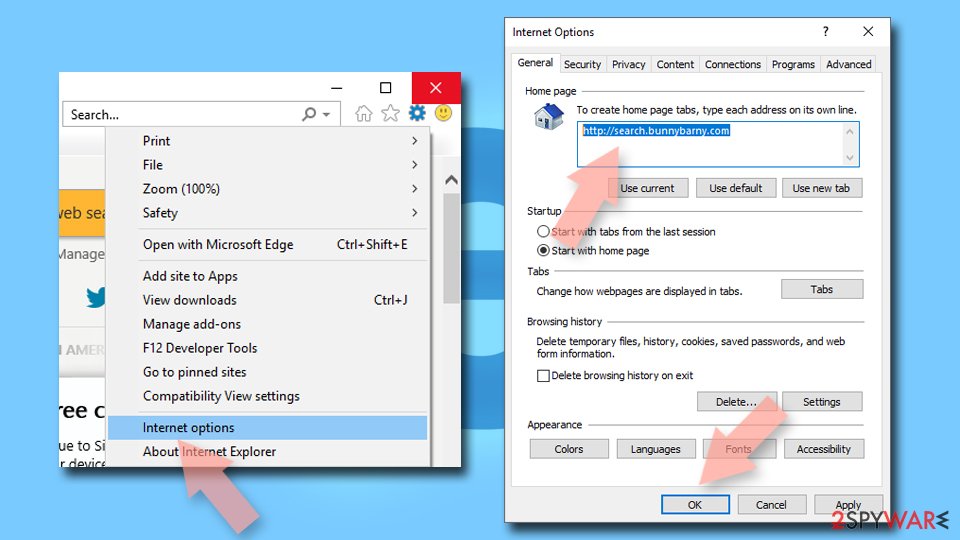
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
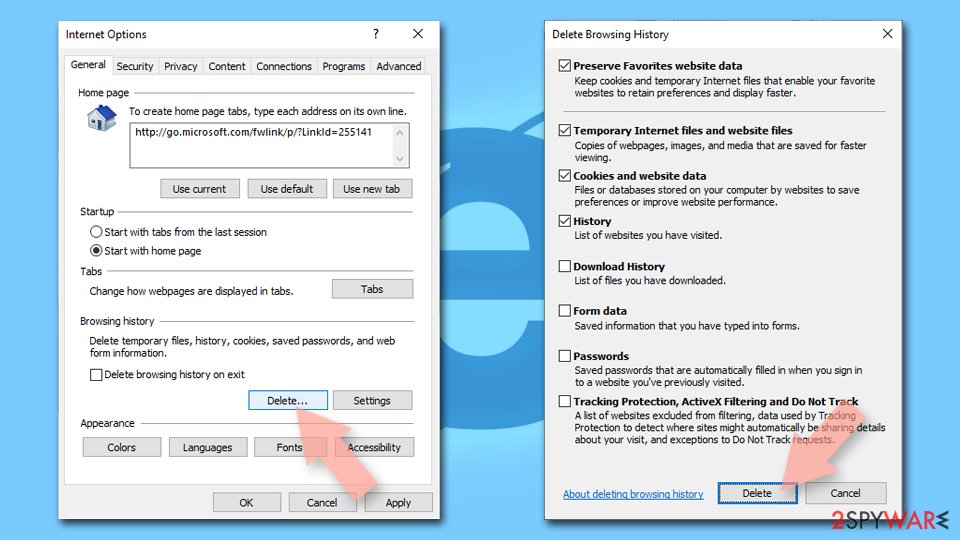
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
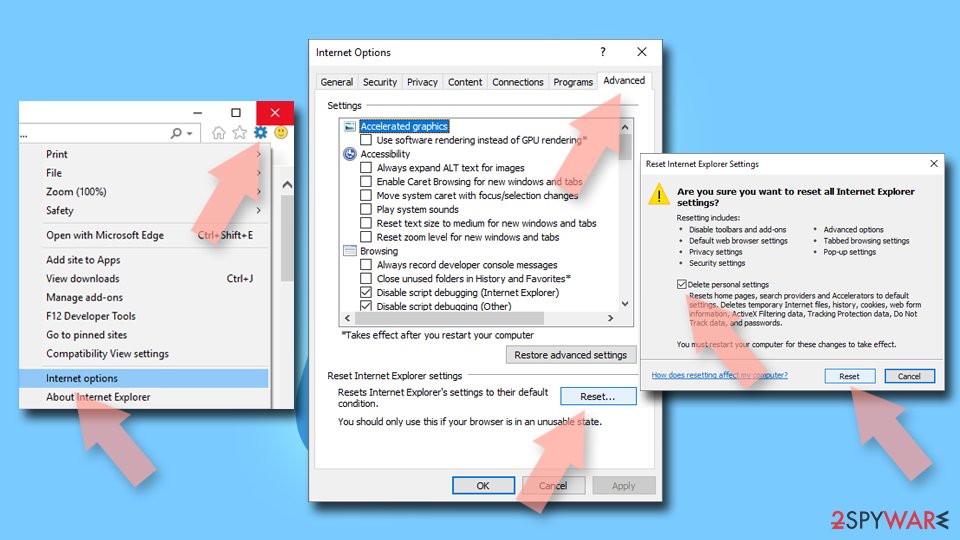
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
From our report of May 2020 · not reviewed since
Prevent malware infections on your machine
Trojans are typically advanced malware infections that can initiate thousands of changes to the infected machine without producing any symptoms.
This happens because these malicious apps are programmed to work stealthy, although it is no secret that there is a lot of badly coded malware that would instantly give away its presence or simply crash the computer. In some cases, however, this might be even worse than the infection itself, as broken code might permanently corrupt vital system files.
Nevertheless, users should not get infected with Trojans in the first place, and for that, multiple security measures should be applied when browsing the internet or even checking your inbox. Here are several tips provided by security experts from dieviren.de:
- Employ a reliable anti-malware software and keep it updated at all times;
- Apply security patches as soon as Microsoft releases new updates;
- Do not allow spam email attachments to run macros or click on links embedded inside the email;
- Protect all your accounts with strong passwords and never reuse them;
- Do not click on links that come via IM applications or social media platforms.
From our report of May 2020 · not reviewed since
Get rid of Other:Malware-gen in one way or another
To remove Other:Malware-gen from your machine, you should first perform a full system scan with another security software and also ensure that your security software that shows pop-ups is up-to-date.
Some components are stored within the web browser's settings and can only be eliminated with a full browser reset.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called Chrome.exe in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Other:Malware-gen [Trj]
What does Other:Malware-gen mean?
Other:Malware-gen is a heuristic detection name used by Avast and AVG antivirus software. It does not identify a specific malware variant; instead, it flags suspicious activity that matches malware patterns.
The detection typically comes from Chrome.exe and indicates the browser accessed a site with suspicious behavior or components. It is often associated with browser-related threats like trojans, PUPs, or malicious scripts. The detection may be a legitimate threat or a false-positive from corrupted antivirus database files.
Is Other:Malware-gen a real virus?
Other:Malware-gen may be either a true malware infection or a false-positive. Many users report the detection appearing constantly even after antivirus sends items to quarantine, with nothing showing in quarantine—indicating a likely false-positive. However, real trojan infections can trigger this detection.
A false-positive often comes from corrupted antivirus program files or outdated security definitions. To determine if it is real, scan your system with a different antivirus tool. If the second tool finds nothing, it was likely a false-positive.
What trojan threats trigger Other:Malware-gen detection?
Trojans like Other Malware Gen Trj can establish background connections to remote Command & Control servers, steal financial information and cryptocurrency wallet data, take screenshots and use video cameras remotely, proliferate other malware like ransomware, gain elevated privileges for lateral movement within networks, and send spam from your machine.
These infections usually complete quickly with changes applied invisibly in the background. Most symptoms go unnoticed by regular users. Trojans may be disguised as legitimate emails, applications, or software cracks.
How do trojans that trigger Other:Malware-gen get on my PC?
Trojans often arrive via email attachments from seemingly reliable sources that are actually compromised or spoofed. Users downloading software cracks and keygens face extreme risk. Third-party websites hosting cracked software often distribute trojans alongside the main program.
Drive-by-downloads from compromised websites and exploit kits can install trojans silently. Trojans may be bundled with legitimate software from untrustworthy download platforms. Phishing emails and social engineering tricks convince users to open malicious attachments or download fake updates.
Can Other:Malware-gen be a false-positive?
Yes. Users frequently report Other:Malware-gen pop-ups despite nothing being found when checking quarantine.
False-positives often result from: corrupted antivirus program files; outdated security definitions; browser vulnerabilities being flagged as threats; or websites whose content triggers heuristic patterns. To verify, scan with another reputable antivirus tool.
If it finds nothing, the detection was false. Avast and AVG have whitelisted several domains after users reported false-positives. Contact your antivirus maker with details if you suspect false-positive detection.
How do I remove Other:Malware-gen if it is real malware?
First, ensure your antivirus is updated to the latest version with current definitions. Run a full system scan with your antivirus and send detected items to quarantine.
If detection persists, run a full system scan with a different reputable antivirus tool to confirm or deny malware presence. If the second scan finds nothing, it was a false-positive.
If both detect malware, use both tools together for removal. After removal, use system repair tools to fix damage done to Windows files and registry. Do not assume your system is clean until a second tool confirms it.
Why do Other:Malware-gen detections keep returning?
If detections constantly return even after quarantine, the infection may not be completely removed, or it is a false-positive. Some trojans hide components in multiple locations that must all be found and removed. Others may use rootkit techniques to hide from antivirus.
If it is a false-positive, enable automatic updates for your antivirus definitions and verify your antivirus installation integrity—corrupted files cause recurring false alerts. Perform a full browser reset, clear all cached data, and revoke access from browser extensions. If problems persist, consider professional malware removal assistance.
How can I prevent trojan infections that trigger Other:Malware-gen?
Employ reliable antivirus software and keep it updated continuously. Apply Windows security patches as soon as Microsoft releases updates. Never allow spam email attachments to run macros or click links embedded in emails.
Protect all accounts with strong, unique passwords and never reuse them across platforms. Do not click links from instant messages or social media platforms.
Avoid downloading software from third-party sites; use official websites only. Never download or run software cracks or keygens. Be suspicious of file attachments and verify sender identity before opening files.
Will Fortect remove Other:Malware-gen [Trj]?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Other:Malware-gen [Trj], follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Trend Micro: Command and Control [C&C] Server (read October 5, 2026)
- Wikipedia: Botnet (read October 5, 2026)
- Dieviren: Dieviren (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)