
Your system is heavily damaged by (4) virus!: what it is and how to remove it
'Your System Is Heavily Damaged by 4 Virus' is a fake tech support scam claiming software damage requiring rogue tool purchase. No viruses cause system 'damage'; close alerts and scan for adware.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
A scan of the PC is a quick way to confirm nothing was installed alongside the "Your system is heavily damaged by (4) virus!" pop-up.
Do it yourself · free Remove Your system is heavily damaged by (4) virus! yourself 2 steps, about 6 minutes, no software needed.
Start the steps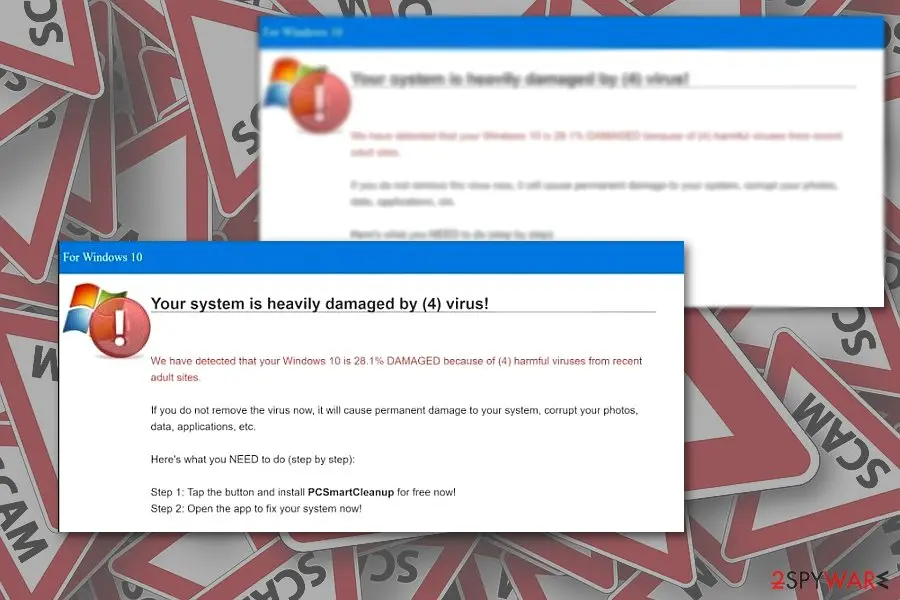
Your system is heavily damaged by (4) virus!: summary
| Distribution | Software bundles, fake Flash Player updates, file-sharing platforms, deceptive ads |
|---|---|
| Damage | PUP installation, malware infections, financial losses, privacy issues |
| name | Your system is heavily damaged by (4) virus! |
| Type | Adware, PUP, tech support scam |
| Purpose | Convince people to download a rogue tool that shows fake scan results trying to persuade you into purchasing its worthless paid version |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Name | Your system is heavily damaged by (4) virus! |
|---|---|
| Symptoms | A fake virus warning in a browser tab |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 12 March 2018 |
| Facts checked | 5 October 2026 |
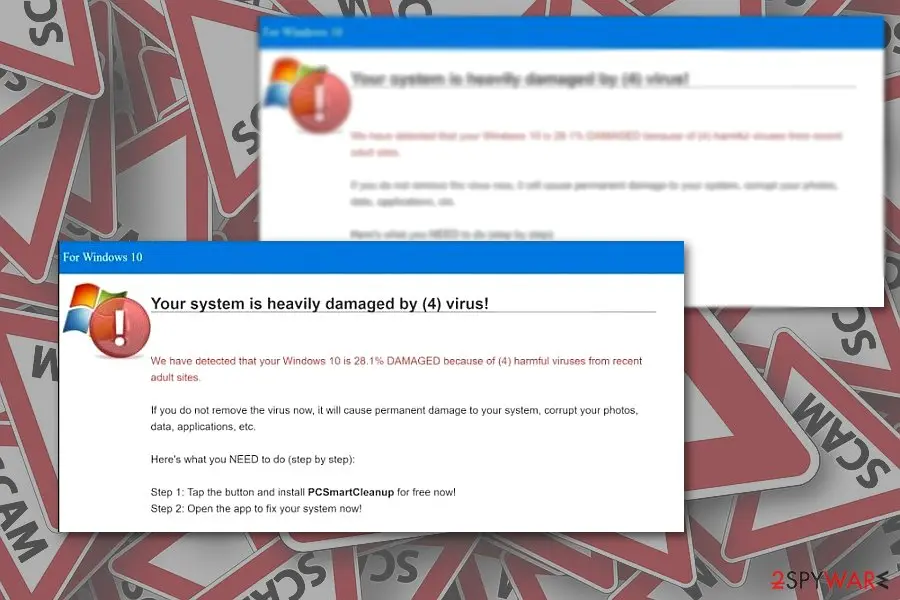
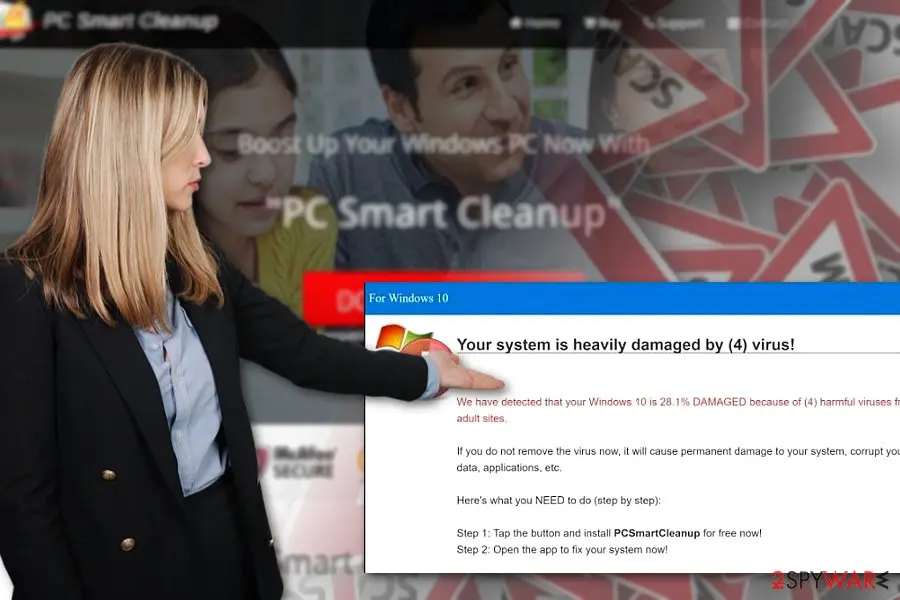
What the Your system is heavily damaged by (4) virus! pop-up looks like
Your system is heavily damaged by (4) virus!
What the Your system is heavily damaged by (4) virus! scammers want
From our report of Mar 2018 · not reviewed since
Tech support scams are carried out via freeware bundles
Browser-based tech support scams are often hidden in the form of web scripts.
You are most likely to get redirected to the article's culprit scam site after you click on the play button in an illegal movie streaming or gaming site, click on deceptive as, etc. Speaking of PC-based tech support scams, you might encounter it if you install a corrupted application or browser extension .
Therefore, it is of utmost importance to pay attention to the installation of any new software, especially if you downloaded it from a third-party vendor. Always choose the Advanced/Custom installation modes over the Recommended/Standard/Quick ones. Only then will you be able to deselect all additional, untrustworthy, questionable applications from installing on your device.
Why Your system is heavily damaged by (4) virus! opens in your browser
From our report of Mar 2018 · not reviewed since
"Your system is heavily damaged by (4) virus!" is a social engineering attack know as bait or tech support scam .
Its developers use multiple psychological strategies to create the feeling of immediacy, the risk of a fatal system crash, and fear of personal data loss.
To protect the system from possible consequences, the victim is asked to purchase the PC Smart Cleanup utility, which is nothing else but malware. In the middle of March 2018, a version of this dangerous infection has been spotted circulating around. Dubbed as Four Virus, this potentially malicious infection is considered to become as widespread as the Android and iPhone viruses.
According to people's reports, a target for both Four virus and "Your system is heavily damaged by (4) virus!" versions are iPhone, Android, and iPad users. The tablet and smartphone users may get another variant, stating that your battery is badly damaged by 4 virus.
Nonetheless, comparing this scam with other samples of the online felony, it does not manifest any extraordinary behavior or features. On the other hand, there is a distinguishable feature.
Unlike the majority of tech support scams which alert users with Zeus virus, for instance, Your computer has been infected with Zeus virus and threatens that your Facebook login and email account information is about to be stolen, this sample of the tech support scam behaves a bit differently.
It says that your computer is heavily damaged by four virus. However, it is unknown whether the "four" indicates the malware's name or the number of viruses supposedly detected on the system. Furthermore, this tech support scam sample advised you to acquire technical support not by dialing a specific number but by installing a program called PCSmartCleanup. Here's where the problem lies.
The Four virus is not only intrusive as it locks the web browser completely but can expose the system to potentially unwanted programs (PUPs). The pretend-to-be legitimate PCSmartCleanup utility has been condemned for questionable behavior, such as the usage of cookies, delivery of predetermined scan results, and ongoing proposals to purchase the Advanced or Licensed version.
Thus, it is not recommended to install it or if you already did, remove it. Speaking of the scam, ignore it and close the tab.
If you got redirected to its counterpart -- "Your Computer is heavily damaged! (33.2%)" scam – you should not comply with the demands either. If you cannot exit the page, shut it down via the Task Manager.
In addition, it is recommended to scan the device and remove "Your system is heavily damaged by (4) virus!" web elements. You can do so with the assistance of .
How to get rid of the Your system is heavily damaged by (4) virus! Pop-up
The warning is a web page and your PC is not infected by it.
Close it, then remove what keeps bringing it back.
Step 1: Close the page without touching its buttons
The warning is a web page, not Windows, so closing the browser ends it. If the page blocks the browser or goes full screen, press Esc first, then end the browser in Task Manager (Ctrl + Shift + Esc).
Start the browser again without restoring the session, and do not follow any instruction the page gave. On Windows 11 and Windows 10 the steps are identical.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
Resetting the browser to finish infection removal.
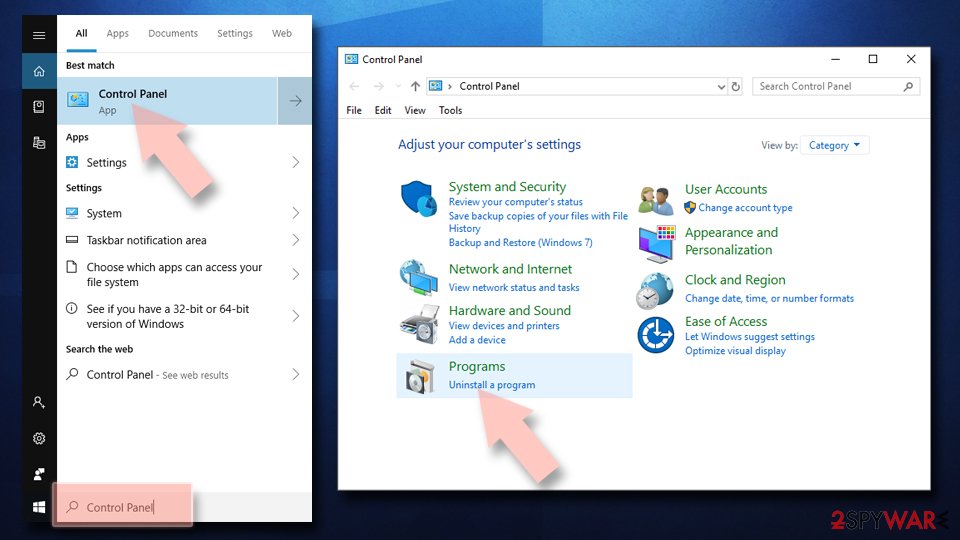
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
Uninstall from Windows 7/XP:
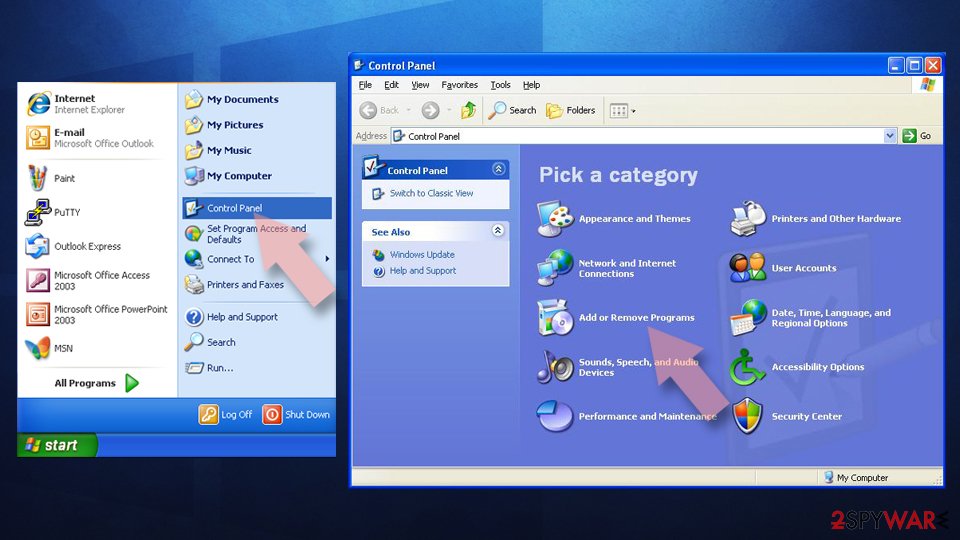
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
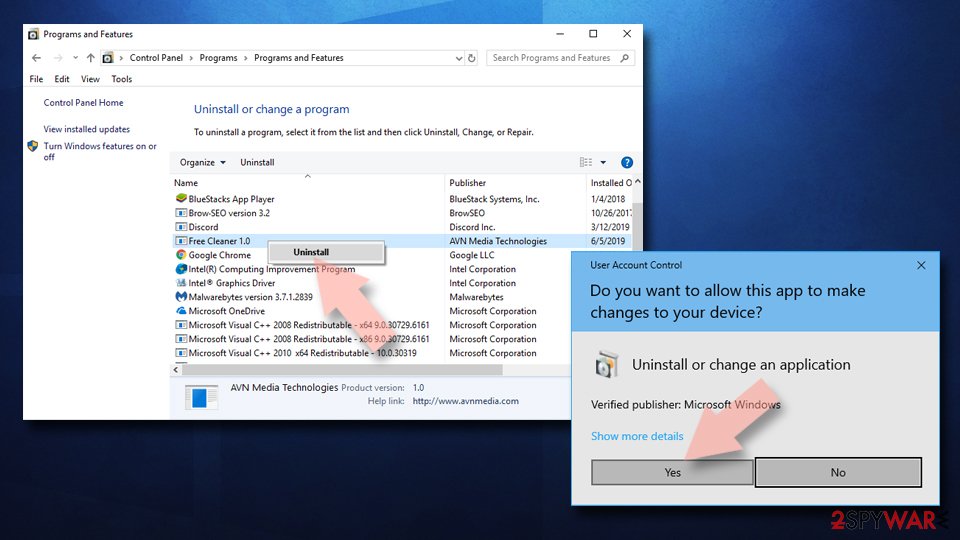
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
Remove dangerous extensions:
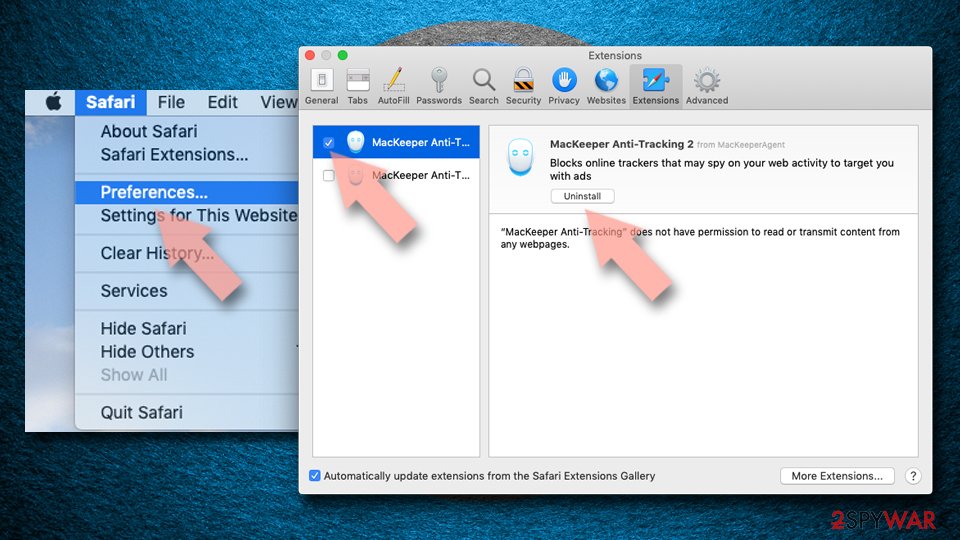
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
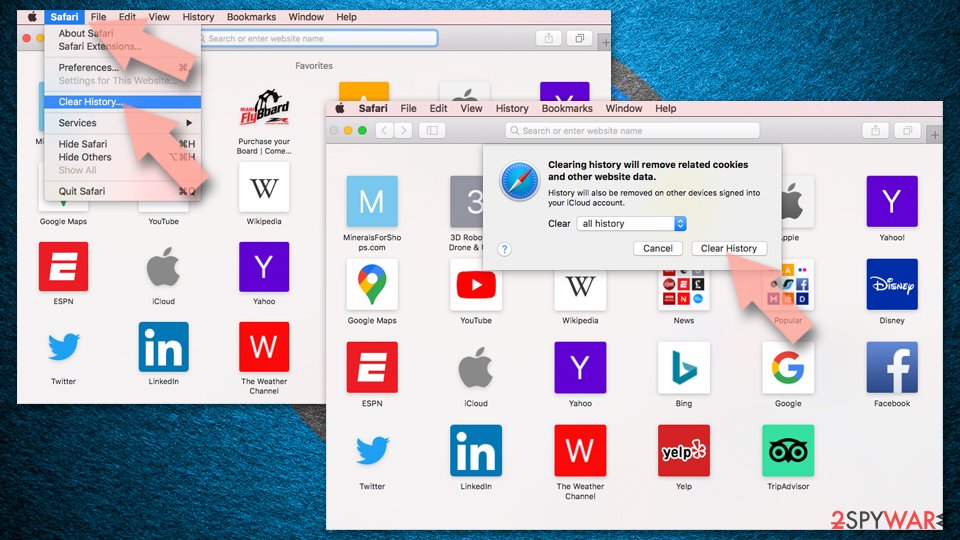
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
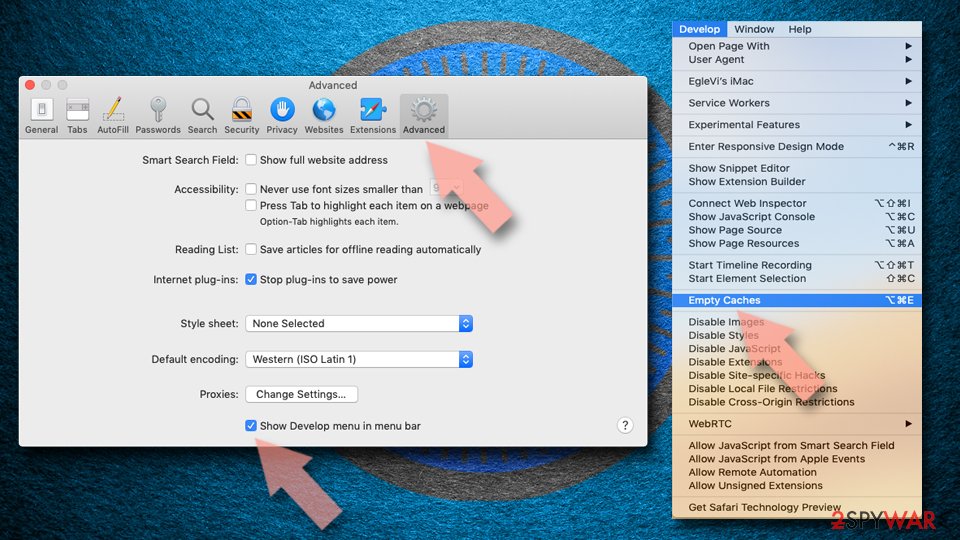
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Remove the unwanted application:
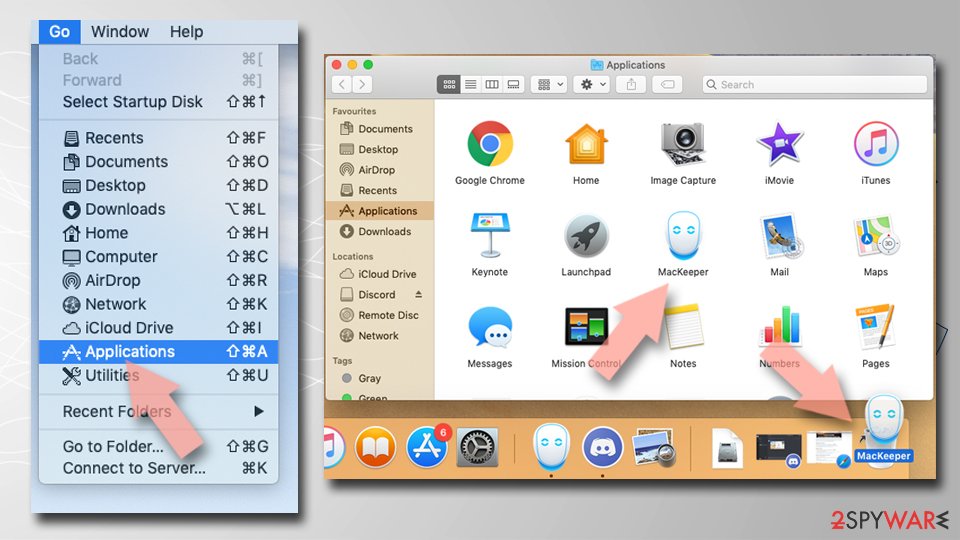
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
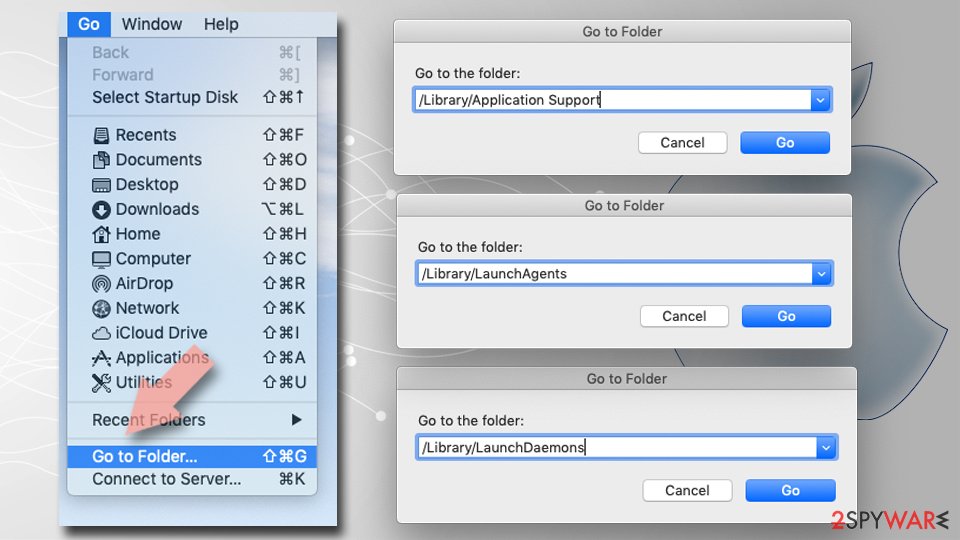
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
From our report of Mar 2018 · not reviewed since
Get rid of "Your system is heavily damaged by (4) virus!" hoax
All browser-based scams can be terminated by closing the tab or the browser.
If you get regularly redirected to such a site, it is necessary to clean your browser and device from adware or other PUPs. You can do so by scanning the device with a malware elimination tool. It will also come in handy dealing with PC-based tech support scams.
In order to cease "Your system is heavily damaged by (4) virus!" ads and pop-up alerts, it is also recommended to reset your affected browser. For your convenience, detailed instructions for doing that are posted below this article.
All, not only UK users should be wary of the scam as the browser scam might pop up in miscellaneous web pages. After you remove virus elements with an anti-spyware tool, you should check the manual guidelines as well and run system diagnostics to ensure a stable working environment.
Questions about Your system is heavily damaged by (4) virus!
What is the 'Your System Is Heavily Damaged by 4 Virus' scam?
'Your System Is Heavily Damaged by 4 Virus' is a fake alert that claims your system has been infected with four (or a different number of) viruses and requires immediate action. The scam creates psychological pressure through urgency, exaggerating system damage to manipulate users into purchasing rogue software called 'PC Smart Cleanup' or 'Speed Booster.'
According to 2018-2021 reports, this threat affects Windows PCs, iPhones, and Android devices, with slightly different messaging per device. The 'Four Virus' variant particularly targets mobile users by claiming battery damage, exploiting battery-related concerns. All versions employ identical social engineering:
- fake technical jargon
- intimidation through catastrophe claims
- pressure to purchase worthless 'security' software
Is my system actually damaged by viruses?
No. Your system is not damaged by any virus. The fake alert uses psychological manipulation claiming system damage that doesn't exist. If your device is functioning normally (no unusual slowdowns, strange processes, or unexpected behavior), the scam alert is purely a browser manipulation with no basis in reality.
If you arrived at the alert through browser hijacking (unwanted redirects), adware is installed; however, even adware doesn't 'damage' your system—it merely displays unwanted content and collects browsing data. Real malware infections cause observable symptoms:
- extreme slowdowns
- frequent crashes
- unfamiliar programs in your applications list
- network activity in Task Manager
The alert alone is insufficient proof of actual infection.
What is PC Smart Cleanup and should I install it?
PC Smart Cleanup is a rogue optimization tool promoted through tech support scams. It is not legitimate security software and provides no actual protection or system optimization.
The program displays predetermined fake scan results claiming 'critical threats' to pressure users into purchasing the paid version. Even the paid version delivers no actual benefits and often contains behaviors suspicious even for adware (using cookies, delivering false scan results, continuous upsell attempts).
Legitimate system optimization comes from manufacturer updates, removing unnecessary installed programs, or upgrading hardware—never through rogue software promoted via scam popups. Installing PC Smart Cleanup or similar tools wastes money and introduces additional unwanted software into your system.
Why does the scam claim battery damage on phones?
The battery damage variant specifically targets smartphone and tablet users who legitimately worry about battery degradation over time. Battery failure is one of the few real hardware issues mobile users experience, making the threat seem credible. Scammers know users understand natural battery degradation and are receptive to claims of battery damage.
However, software viruses cannot damage hardware batteries; battery degradation is purely a hardware physics process occurring over months or years from charging cycles. The scam exploits legitimate battery concerns to create believability for its false claims. The presence of battery damage claims is itself proof of a scam, since software cannot physically damage hardware components.
What is the 'Four Virus' and where did it come from?
'Four Virus' is not a real malware name; it's a fabricated threat used in the scam alert. The 'four' may refer to the claimed number of infections or be an arbitrary name choice. According to 2018 reports, this scam variant circulated primarily targeting mobile device users and was considered likely to become as widespread as other tech support scams.
Real malware has documented names (Zeus, Emotet, Ransomware variants), trackable origins, and definable behaviors. Scammers invented 'Four Virus' as generic-sounding terminology that sounds technical without being specific enough for users to research its legitimacy online.
What happens if I call the number or install the software?
Calling provided phone numbers connects you to criminals who attempt identity theft, sell fake security software for $100-$300+, or trick you into granting remote device access.
Installing PC Smart Cleanup or similar rogue tools introduces additional unwanted software that displays fake scan results and pressures you to purchase paid versions. If you provided credit card information, monitor accounts closely for fraud.
If you granted remote access, assume criminals explored your device and potentially installed additional malware. If you purchased rogue software with a credit card, contact your card issuer to report fraud and request chargeback. Report the scam to the FTC (reportfraud.ftc.gov) and IC3.gov.
How should I respond to this alert?
Do not call provided phone numbers or click any buttons on the alert. Immediately force-close your browser using Task Manager (Windows: Ctrl-Alt-Delete > Task Manager > End Task) or Activity Monitor (Mac). Restart your device completely.
Try accessing your browser again; the alert should disappear. If redirects to the scam continue after restart, adware is installed. Download anti-malware software (using a different browser if necessary) and perform a complete system scan.
After removing adware, reset your primary browser to factory settings. Delete any suspicious programs from your applications list. If the alert appears on a mobile device, restart the device and run an antivirus scan using mobile anti-malware apps.
How do I prevent these tech support scams?
Avoid high-risk websites (illegal streaming, gambling, adult content) where these scams frequently launch. Use browser security extensions that block malicious popups and scripts. Maintain updated anti-malware software with real-time scanning enabled.
Understand that legitimate system warnings originate from your operating system's official control panel or actual installed security software, never from browser popups. Do not download software promoting urgent action through popups; legitimate security tools use stable channels and straightforward installation.
If concerned about actual system health, use built-in tools (Windows Defender, Activity Monitor, official manufacturer diagnostics), not tools promoted through aggressive alerts. Remember: real security companies never use panic and urgency as primary marketing tactics.
Will Fortect remove Your system is heavily damaged by (4) virus!?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Your system is heavily damaged by (4) virus!, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- FTC: How to spot, avoid and report tech support scams (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)