
Viruses · 307 guides

Trojans removal guides, page 3 of 12

Hidden programs that give attackers remote access, and how to find and remove them.
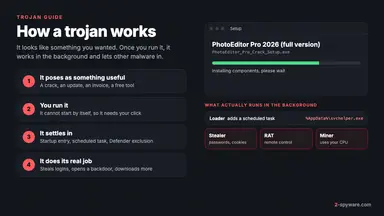
Start hereWhat is a trojan and how to remove itA trojan is malware disguised as something you wanted, such as a cracked program, a fake update or an invoice. It does nothing until you run it, then steals passwords, gives a stranger remote access or downloads more malware. To remove it, cut the startup entries it added, run a full and an offline scan, then change your passwords from a clean device.

Most searched trojans guides

  1. 1Remove Csrss.exe trojan
  2. 2Remove Memz virus
  3. 3Remove Wcupdater
  4. 4Remove Win32/Lodi
  5. 5Remove Chrome.7z
  6. 6Remove Iplogger.org

Trojans removal guides 55–81 of 307

Remove Vagus RAT

Vagus - a dangerous Remote Access Trojan that can steal personal info and perform other malicious actions Vagus is a type of malware attributed to the RAT category. It isTrojansHigh riskLinas Kiguolis ·

Remove Puabundler:win32/msetup virus

Puabundler:win32/msetup is a potentially unwanted program that can cause harm to your system Puabundler:win32/msetup is a typical detection name for an unwanted program in Windows. This is a potentially maliciousTrojansHigh riskAlice Woods ·

Remove CapraRAT virus

CapraRAT is Android-based malware that steals sensitive user data CapraRAT is a Remote Access Trojan that has recently surfaced in the wild,[ref en-3] mainly targeting Indian users. It is believedTrojansHigh riskOlivia Morelli ·

Remove Healthy.exe virus

Healthy.exe virus has come to the surface after a few users installed "cracked" video games Healthy.exe recently surfaced as a potential threat. It is still unknown exactly what it doesTrojansHigh riskJake Doevan ·

Remove DevilsTongue malware

DevilsTongue malware is a virus that is written in C and C++ programming languages DevilsTongue malware was discovered by researchers, and it is reported as a cyber threat that hasTrojansHigh riskJulie Splinters ·

Remove VirTool:Win32/ExcludeProc.D

VirTool:Win32/ExcludeProc.D can generate revenue for cybercriminals by using your computer VirTool:Win32/ExcludeProc.D is the detection name of a malicious program that Windows users have recently discovered. It is a Trojan thatTrojansHigh riskJake Doevan ·

Remove Wacatac Trojan

Wacatac is malware triggering the alert that can informal about security issues but also appears when there are no threats at all Wacatac Trojan is a threat that can affectTrojansHigh riskLinas Kiguolis ·

Remove Pterodo malware

Pterodo is politically motivated malware related to cyberattacks against Ukraine Pterodo is a Trojan known in the cybersecurity landscape since at least 2014. The date is significant due to theTrojansHigh riskUgnius Kiguolis ·

Remove 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware

17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F is a dangerous clipper-hijacking malware that spreads via torrent sites 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F is a Trojan[ref en-2] that specializes in stealing funds from users' cryptocurrency wallets. The principle of the virusTrojansHigh riskOlivia Morelli ·

Remove Hancitor Trojan

Hancitor is a widespread Trojan that downloads other malware onto infected systems or networks Hancitor Trojan first emerged in 2014 and immediately spread relatively widely thanks to extensive malspam campaigns.TrojansHigh riskJake Doevan ·

Remove Trojan.Win32.BitCoinMiner.la

Trojan.Win32.BitCoinMiner.la slows down the computer by mining cryptocurrencies and causes crashes, bugs Trojan.Win32.BitCoinMiner.la is a detection name of a malicious program that engages in cryptojacking[ref en-1] activities or it canTrojansHigh riskAlice Woods ·

Remove Unix.trojan.coinminer virus

Unix.trojan.coinminer is dedicated to hijacking users' systems for illegal usage The category of Trojans is very versatile - the function of these malicious programs can vary greatly - from encryptingTrojansHigh riskJake Doevan ·

Remove Trojan.WIN32.PDF.Alien.gen

Trojan.WIN32.PDF.Alien.gen is a malicious program for Windows that might sneak into your PC without warning PDF.Alien.gen is a Trojan that users might see flagged by their security applications. As evidentTrojansHigh riskGabriel E. Hall ·

Remove Trojan:Win32/Mamson!MSR

Trojan:Win32/Mamson!MSR is the detection name of a trojan that spreads around via pirating services Trojan Mamson is an infection that can easily affect various functions of the machine once itTrojansHigh riskUgnius Kiguolis ·

Remove Js Miner

Js Miner is the tool used by cryptojackers who try to get money easily without directly involving victims Js Miner is a crypto miner that can be used by websiteTrojansHigh riskGabriel E. Hall ·

Remove HEUR.Trojan.MSIL.Miner.gen

HEUR.Trojan.MSIL.Miner.gen is a detection name alerting about a virus on your system  HEUR.Trojan.MSIL.Miner.gen is a heuristic detection name that might be an alert of a real virus or a false positive,TrojansHigh riskUgnius Kiguolis ·

Remove SendGrid email scam

SendGrid's name used to steal user credentials SendGrid is a legitimate marketing platform that is used by many website developers to monetize their content. In order to operate successfully, usersTrojansHigh riskLinas Kiguolis ·

Remove Trojan.Win32.Cometer.gen

Trojan.Win32.Cometer.gen is fileless malware designed to steal valuable information Some malware is just worse than the other, and Trojan.Win32.Cometer.gen definitely meets these criteria. Residing only in memory, this malicious programTrojansHigh riskUgnius Kiguolis ·

Remove Trojan.Win64.Miner.gen

Trojan.Win64.Miner.gen is the threat that affects the performance of the computer significantly because it uses resources to mine cryptocurrency Trojan.Win64.Miner.gen is the type of cyber infection that damages the machineTrojansHigh riskLinas Kiguolis ·

Remove Zoom Conference Invitation email virus

Don't want to be infected with data-stealing malware? Don't click on "Zoom_Conference_Invitation.zip" file Email spam campaigns are the most common methods for malware propagation, and this time cybercriminals are usingTrojansHigh riskJake Doevan ·

Remove Biopass RAT

Biopass RAT – a Python-based backdoor capable of various devastating actions Biopass RAT is an extremely perilous malware infection spreading through fake Adobe Flash Player and Microsoft Silverlight's installers/updates. However, servicesTrojansHigh riskJake Doevan ·

Remove Trojan.Zeroaccess

ZeroAccess - is the silently distributed malware that focuses on accessing particularly valuable data or acts directly like installer ZeroAccess is a malicious Trojan horse[ref en-1] which was named likeTrojansHigh riskUgnius Kiguolis ·

Remove Zeus Panda virus

Zeus Panda is a banking trojan that targets numerous countries around the world, although exempts Russia, Ukraine, Belarus, and Kazakhstan Zeus Panda virus is a trojan horse developed for data-stealing purposes.TrojansHigh riskLinas Kiguolis ·

Remove Trojan:Win32/Dex@hot

Trojan:Win32/Dex@hot – a Windows infection that could upload additional malware Trojan:Win32/Dex@hot is an extremely hazardous computer virus that can infect any Windows device that doesn't have sufficient protection to identify, isolate,TrojansHigh riskLinas Kiguolis ·

Remove Bitcoin virus

Bitcoin virus – malware that can use victims' PC resources to mine cryptocurrency for criminals Bitcoin virus is a type of malicious program that seeks to mine cryptocurrency illegally whileTrojansHigh riskJake Doevan ·

Remove UNP Campaign Manager

UNP Campaign Manager is a trojan that causes various system failures and endangers its users UNP Campaign Manager is a malicious application associated with Game Cracker developed by Dark BayTrojansHigh riskAlice Woods ·

Remove WinHound

WinHound is a trojan, which silently installs itself to vulnerable computers by exploiting certain system or web browser security flaws. It can also be dropped by some parasites. Once executed,TrojansHigh riskUgnius Kiguolis ·
5,557 members already hereReading, writing, commenting and voting. 0 verified · 282 joined this year