
Tinba: what it is and how to remove it
Tinba is a tiny banker trojan that injects into browsers to steal login credentials and credit card numbers via email phishing. Modern anti-malware is required for removal.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether explorer.exe is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove Tinba yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Tinba: summary
| Distribution | It spreads via email notifications and malicious links |
|---|---|
| Name | Tinba |
| Type | Trojan, malware |
| Issues | The threat can inject codes and install files on the machine |
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Symptoms | An unknown process in Task Manager |
|---|---|
| Evidence | One write-up by a security site; details still limited |
| File names | explorer.exe and %SystemDrive%\Documents |
| First seen | 27 April 2021 |
| Facts checked | 5 October 2026 |
What Tinba does on an infected PC
From our report of Apr 2021 · not reviewed since
The most common way to catch a trojan on the computer - spam email
We get email notifications daily, and as normal that is it is not normal to get random invoices, order confirmation messages from companies but from emails that are not related to them.
For example, if you get an email that is listed like Amazon customer support, the email address should include Amazon's name and something indicative of the company. If not - the email is fake and possibly malicious.
You need to pay attention to such detailed grammar mistakes, typos, attachments, or shortened links in emails directly. Do not open the email that message that is sent from the service you do not use.
Pay attention to these alleged order confirmation messages and always delete any emails with attachments that raise any questions. Those attachments include malicious code and direct trojan injection files. Avoid them at any cost.
From our report of Apr 2021 · not reviewed since
Make the machine clear of any trojans and malware with AV tools
If you cannot find the program that needs to get removed - it becomes difficult to clear threats off of the machine.
This is the case with trojan Tinba too. Since the malware is not easily found, you can run the machine in Safe Mode as shown in the guide and then launch the anti-malware tool like or to remove the infection.
There are various changes that the trojan can make and various parts of the system that malicious virus can lead to, so you need to terminate the malware and double-check before doing anything with the computer again. Another good tip would be to run the process of the Tinba removal and then move to PC recovery with or a similar tool.
From our report of Apr 2021 · not reviewed since
More from our earlier report on Tinba
- The best removal tip - running the anti-malware tool
- [http://]dakotavolandos.com [http://]dakotavolandos.com [http://]dak1otavola1ndos.com [http://]dako22tavol2andos.com [http://]d3akotav33olandos.com [http://]d4ak4otavolandos.com
What Tinba can steal or download
From our report of Apr 2021 · outdated details corrected in October 2026
Tinba is the threat that can add/remove files and folders, make registry changes and inject into other programs.
Additionally, it monitors and records network traffic information in the following file: %SystemDrive%\Documents and Settings\All Users\Application Data\default\web.dat.
Moreover, the threat modifies Mozilla Firefox, to disable warnings when you're visiting insecure sites. It also modifies the system registry to be able to execute every time Windows starts. It injects malicious code into Google Chrome, Mozilla Firefox, and Microsoft Edge. Then it injects itself into explorer.exe and svchost.exe processes and tries to end them.
Trojan Timba has another name - Zusy. A trojan is famous for its really small size. Including all web injects and configs, it weights only 20kb.
It comes without any packing or encryption. The trojan virus belongs to a family of malware.
The name of this trojan was shortened from the words "Tiny Banker" - Tinba. This is a trojan that hooks into browsers and steals all sensitive data, including but not limited to logins and credit card numbers. A trojan is not detected by most antivirus software because it manages to run processes in the background without triggering any system issues that AV tools could notice.
Trojan timba uses really sneaky techniques, it injects itself into legitimate processes like explorer.exe, svchost.exe, firefox.exe also creates a process called winvert.exe. It targets a very small list of sites, mostly financial websites abuse these pages can provide information to people-s accounts.
Here's a list of command-and-control (C&C) servers, to which Tinba tries to send the stolen information:

How to check the PC for Tinba
- Path:
%SystemDrive%\Documents - File:
explorer.exe
How to remove Tinba
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where explorer.exe runs from and stop it
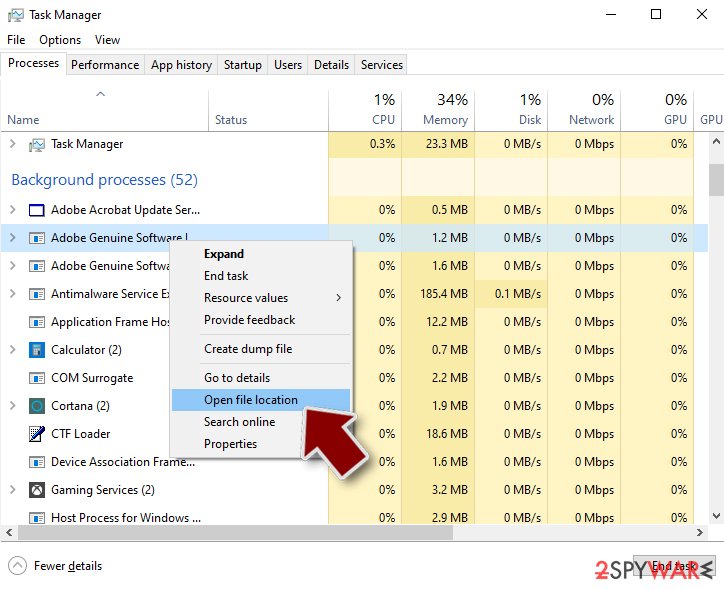
explorer.exeis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
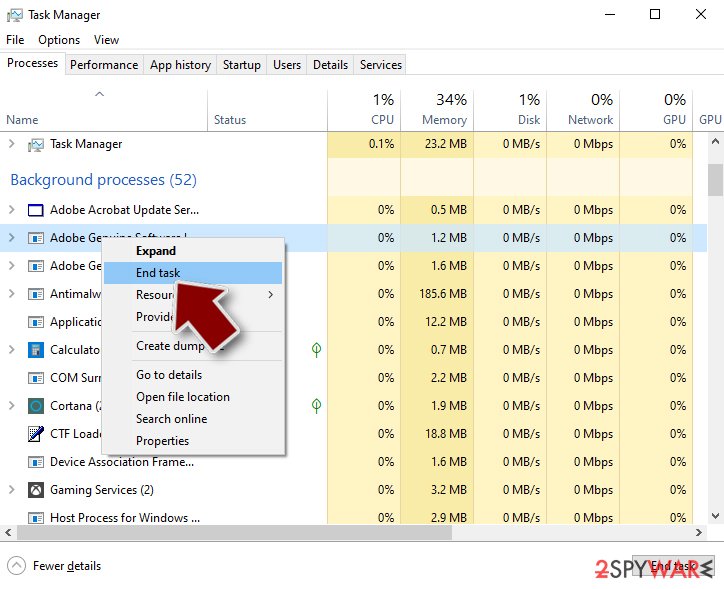
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Tinba or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 3: Remove it from startup
Whatever Tinba installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Repair damaged system components
Once a computer is infected with malware, its system is changed to operate differently. For example, an infection can alter the Windows registry database, damage vital bootup and other sections, delete or corrupt DLL files, etc. Once a system file is damaged by malware, antivirus software is not capable of doing anything about it, leaving it just the way it is. Consequently, users might experience performance, stability, and usability issues, to the point where a full Windows reinstall is required.
Therefore, we highly recommend using a one-of-a-kind, patented technology of repair. Not only can it fix virus damage after the infection, but it is also capable of removing malware that has already broken into the system thanks to several engines used by the program. Besides, the application is also capable of fixing various Windows-related issues that are not caused by malware infections, for example, Blue Screen errors, freezes, registry errors, damaged DLLs, etc.
- Download the application by clicking on the link above
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
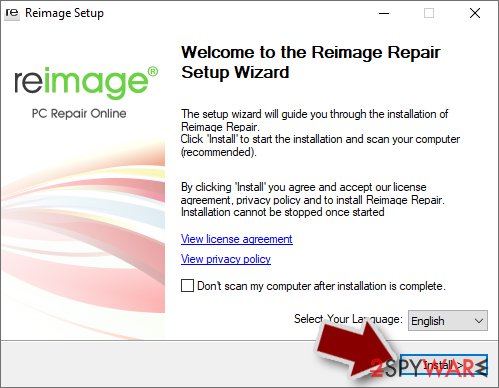
- The analysis of your machine will begin immediately
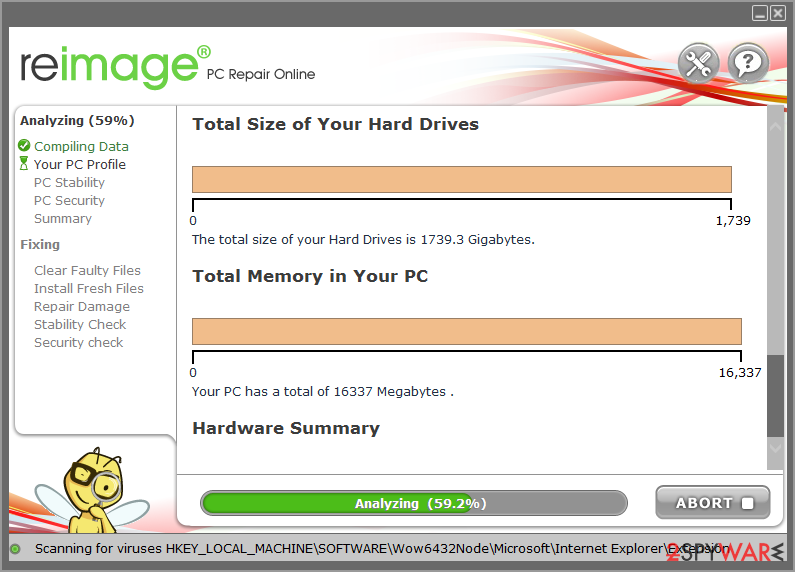
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
- If you see many problems that you find difficult to fix, we recommend you purchase the license and fix them automatically.
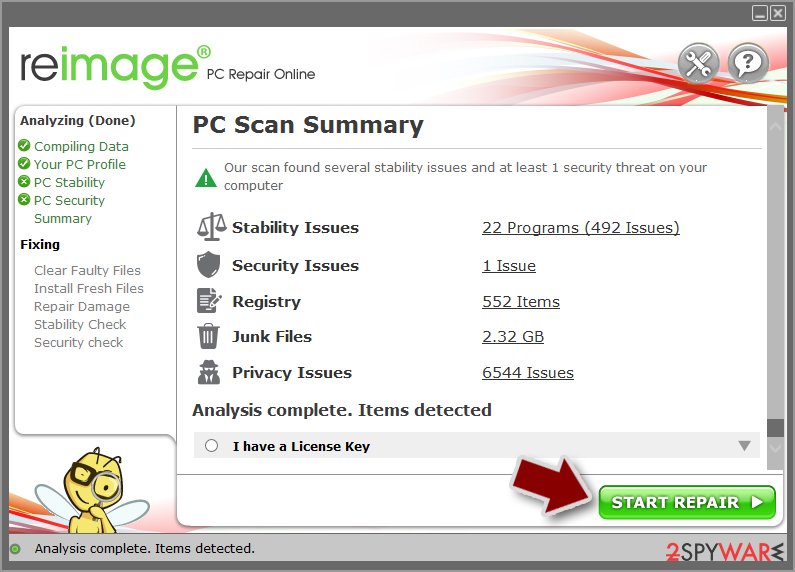
By employing , you would not have to worry about future computer issues, as most of them could be fixed quickly by performing a full system scan at any time. Most importantly, you could avoid the tedious process of Windows reinstallation in case things go very wrong due to one reason or another.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
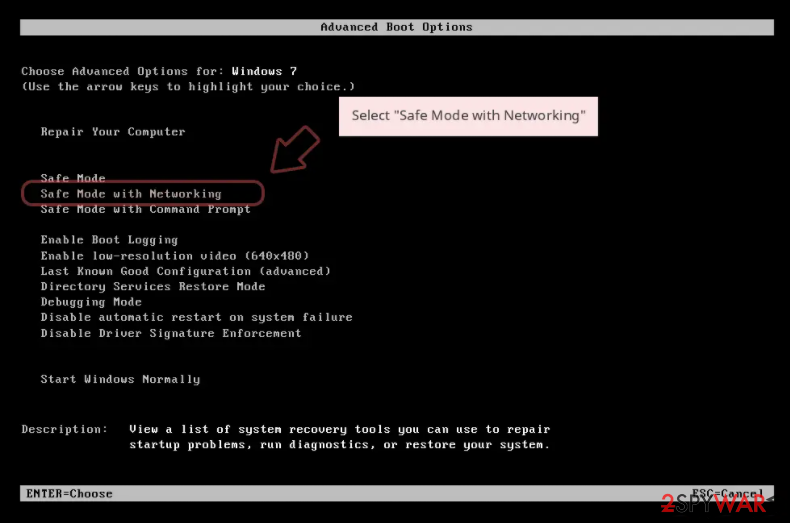
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
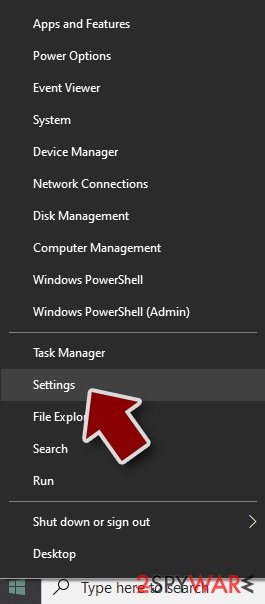
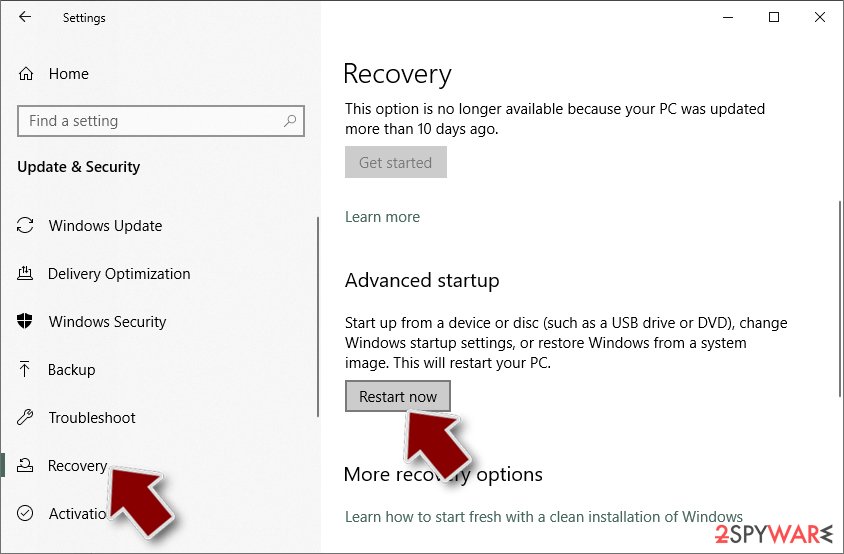
- Right-click on Start button and select Settings.
- Scroll down to pick Update & Security.
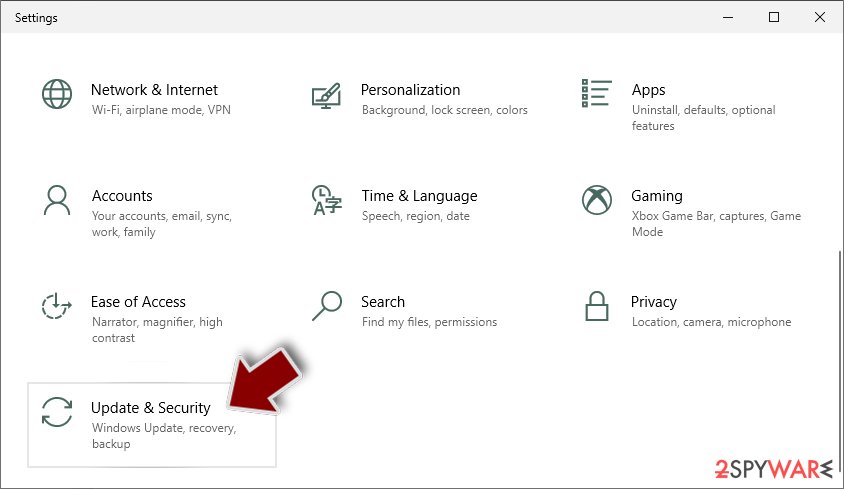
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
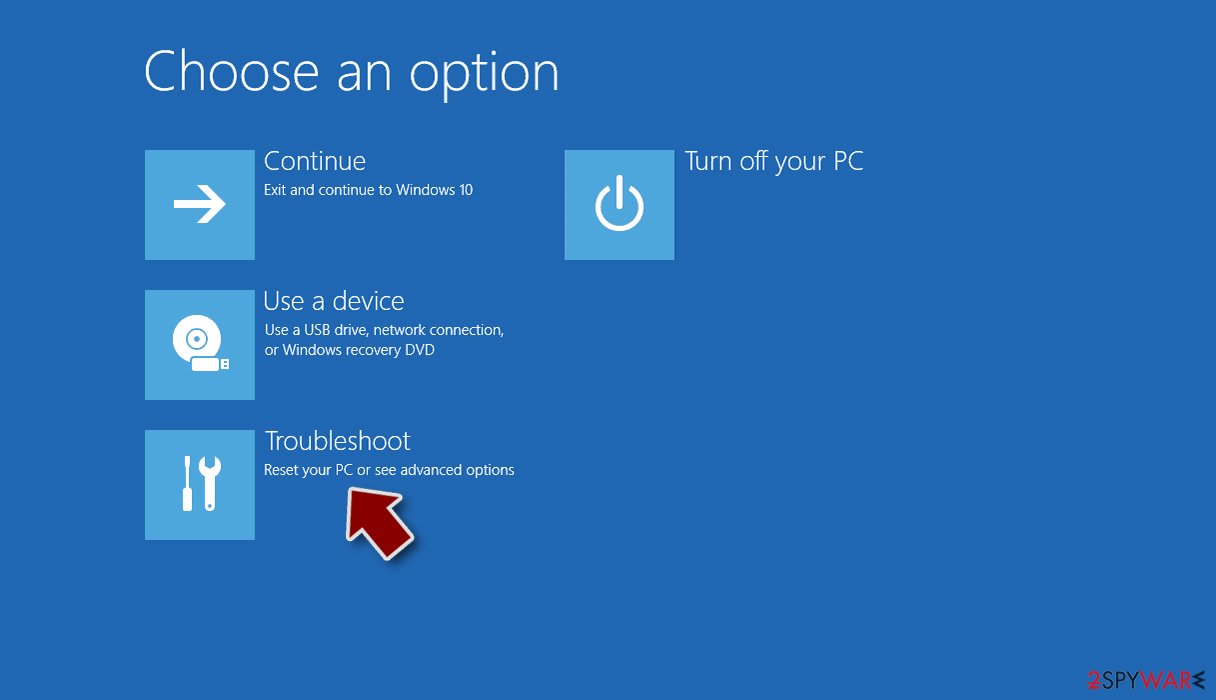
- Select Troubleshoot.
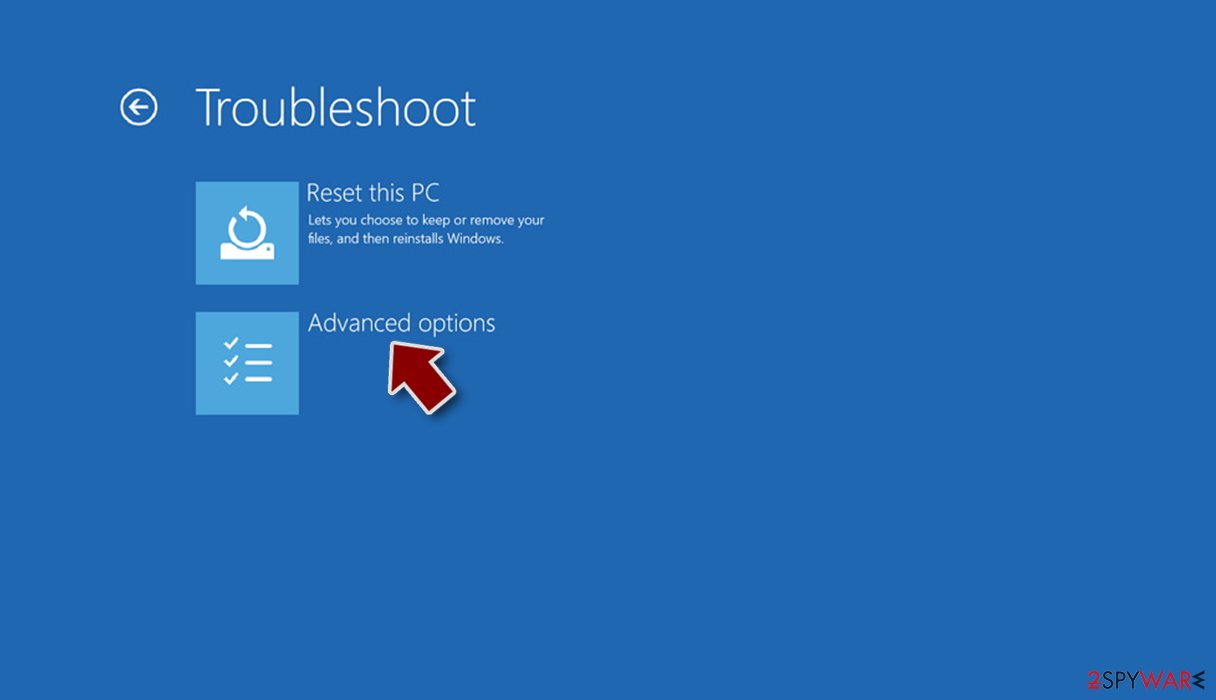
- Go to Advanced options.
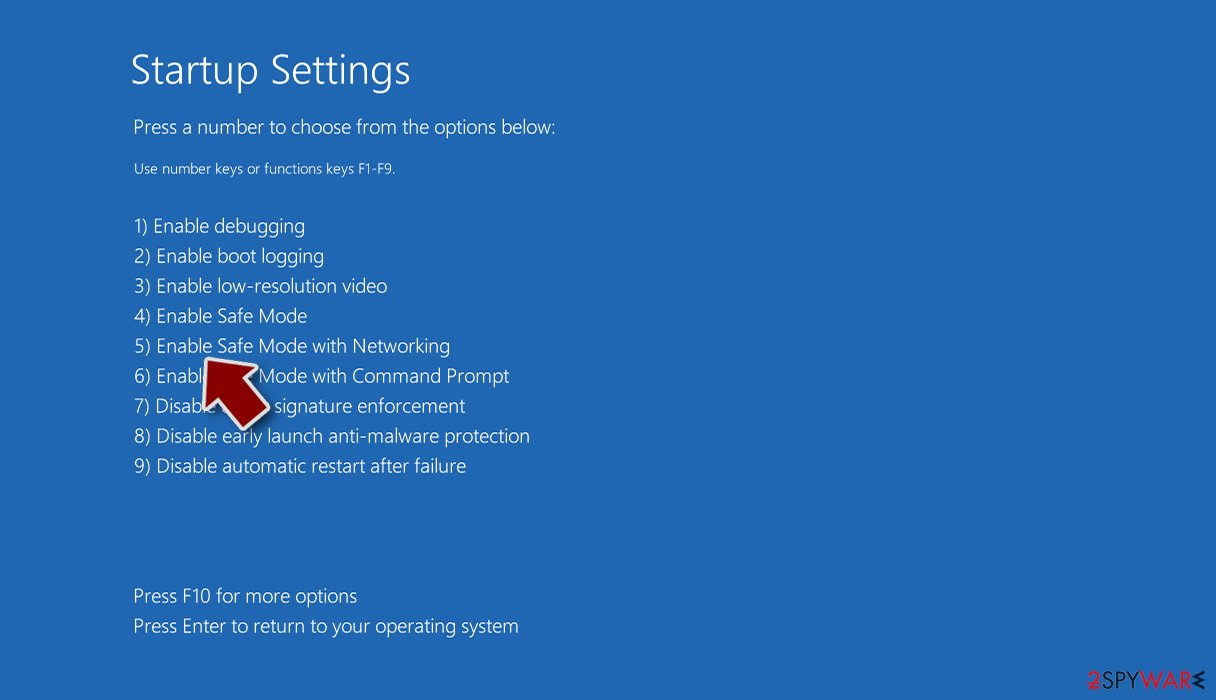
- Select Startup Settings.
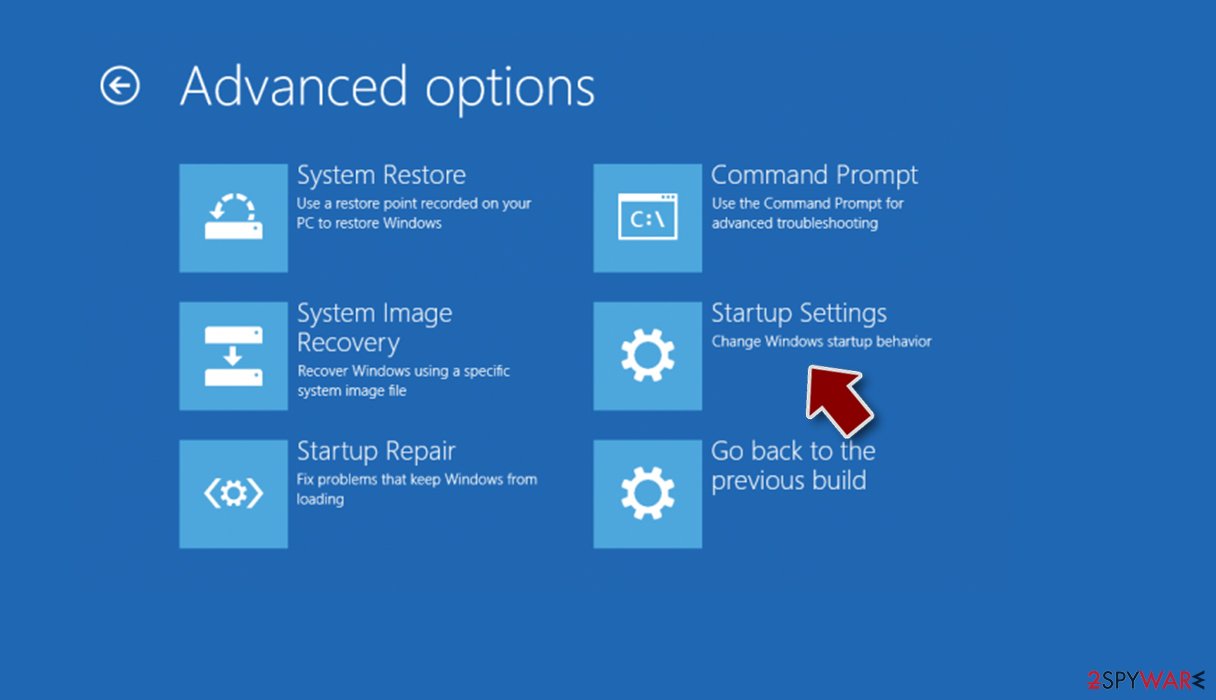
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
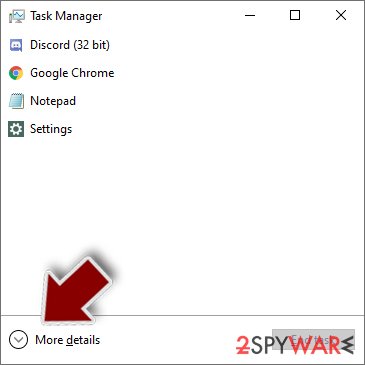
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
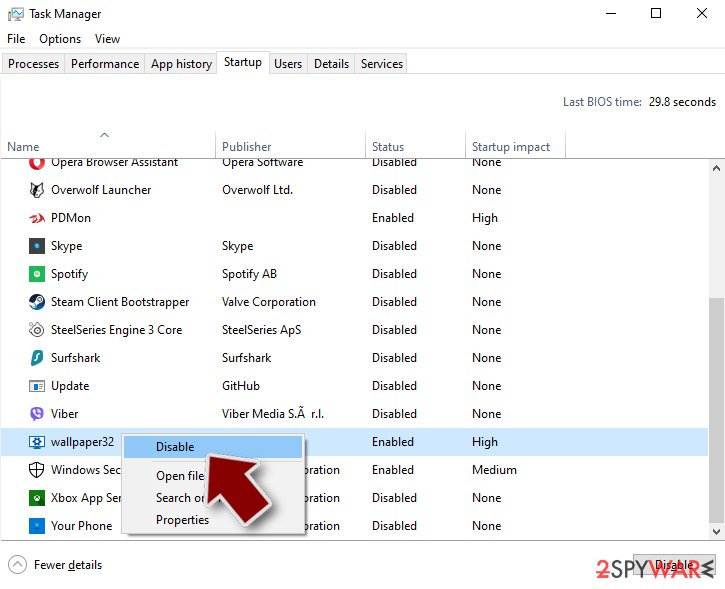
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.
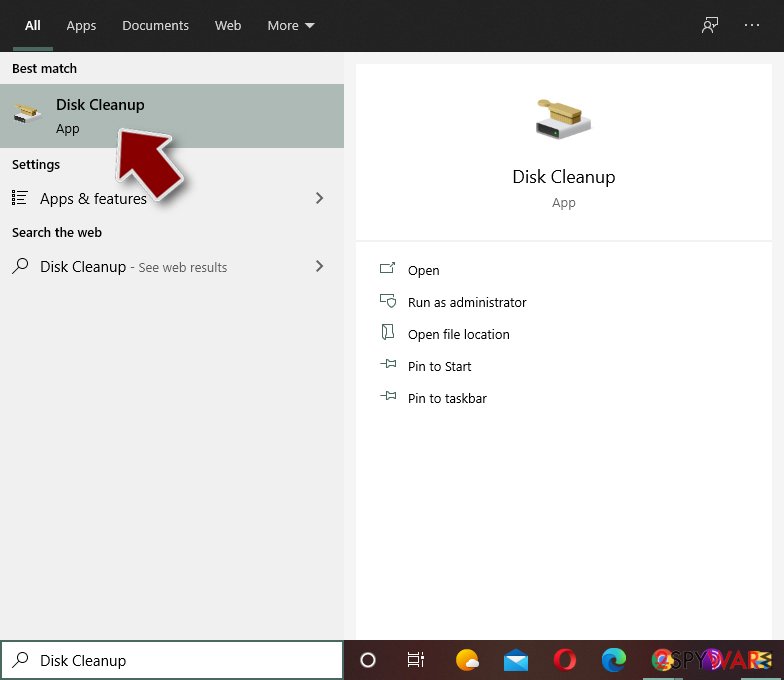
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
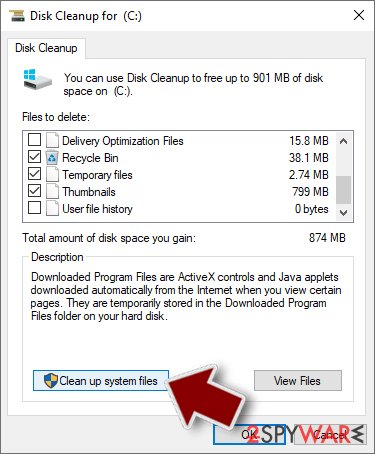
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Scan your system with anti-malware
If you are a victim of ransomware, you should employ anti-malware software for its removal. Some ransomware can self-destruct after the file encryption process is finished. Even in such cases, malware might leave various data-stealing modules or could operate in conjunction with other malicious programs on your device.
or can detect and eliminate all ransomware-related files, additional modules, along with other viruses that could be hiding on your system. The security software is really easy to use and does not require any prior IT knowledge to succeed in the malware removal process.
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed an unfamiliar process called explorer.exe in Task Manager has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Tinba
What is Tinba?
Tinba, also known as 'Tiny Banker' or by its variant name Zusy, is a malicious trojan that steals personal and sensitive information from compromised computers. According to the 2021 guide, Tinba is famous for its tiny size—including web injects and configurations, it weighs only 20KB and comes without encryption.
It hooks into web browsers to steal sensitive data including login credentials and credit card numbers. It's highly difficult to detect because it runs processes in the background without triggering obvious system issues that antivirus software might notice.
How does Tinba steal banking information?
Tinba injects malicious code into Internet Explorer, Google Chrome, and Mozilla Firefox by hijacking legitimate processes like explorer.exe and svchost.exe. The 2021 guide noted it targets a specific list of financial websites to intercept and steal account login information and credit card details.
It monitors and records network traffic in the file %SystemDrive%\Documents and Settings\All Users\Application Data\default\web.dat. Tinba also modifies Mozilla Firefox to disable warnings when visiting insecure sites, allowing it to intercept data silently.
How does Tinba get installed?
Tinba spreads primarily through spam emails containing malicious links or attachments. The 2021 guide emphasized paying attention to suspicious emails—verify the sender, check for grammar mistakes, and avoid opening attachments from unknown sources.
Users should scan any downloaded files with anti-malware before opening them. Emails may claim to be order confirmations or business documents from companies you don't actually have accounts with. Be especially cautious of emails with shortened links or attachments that raise questions.
Why isn't Tinba detected by most antivirus?
Tinba avoids detection by injecting itself into legitimate system processes like explorer.exe and svchost.exe, hiding among normal Windows operations. The 2021 guide noted that trojan Tinba uses sneaky techniques to run in the background without triggering system issues that antivirus tools could notice.
Its small size and lack of encryption make it harder for signature-based antivirus to identify. However, running malware scans in Safe Mode can help detect the injected code.
What command-and-control servers does Tinba use?
According to the 2021 guide, Tinba communicates with multiple command-and-control servers to transmit stolen information:
- dakotavolandos.com
- dak1otavola1ndos.com
- dako22tavol2andos.com
- d3akotav33olandos.com
- d4ak4otavolandos.com
These servers receive the stolen login credentials and credit card numbers harvested from infected systems. Monitoring network traffic and blocking connections to these domains can help contain the infection, though removing the trojan entirely is the primary solution.
How do I remove Tinba?
Run anti-malware software in Safe Mode with Networking to disable Tinba's active processes and remove it. The 2021 guide recommended using reputable security tools. Since Tinba is difficult to find due to its small size and injected nature, anti-malware is more reliable than manual removal.
After removing Tinba, use tools like to repair any altered or corrupted system files the malware modified. Double-check your system before resuming normal activities to ensure complete removal.
Should I assume my banking information was stolen?
If your computer was infected with Tinba, assume your banking information, login credentials, and credit card data were stolen. The 2021 guide emphasized the trojan's history as a significant bank account and credit card stealer.
Contact your financial institutions immediately to check for unauthorized activity and place fraud alerts on your accounts. Change all passwords from a clean computer—not the infected one—and monitor your accounts for suspicious transactions. Consider freezing your credit to prevent identity theft.
How do I prevent Tinba infection?
Never open email attachments or click links from unknown senders or suspicious emails. Verify sender email addresses match legitimate companies—if you don't use a company's services, their emails are fake.
Delete emails with attachments that raise questions without opening them. Keep your antivirus and operating system updated with the latest patches.
Use strong, unique passwords for financial accounts. Monitor your bank and credit card statements regularly for unauthorized charges. When downloading files, always scan them with anti-malware before opening.
Will Fortect remove Tinba?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Tinba, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)