
Viruses · 307 guides

Trojans removal guides, page 2 of 12

Hidden programs that give attackers remote access, and how to find and remove them.
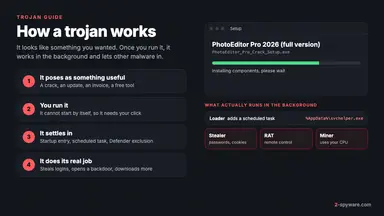
Start hereWhat is a trojan and how to remove itA trojan is malware disguised as something you wanted, such as a cracked program, a fake update or an invoice. It does nothing until you run it, then steals passwords, gives a stranger remote access or downloads more malware. To remove it, cut the startup entries it added, run a full and an offline scan, then change your passwords from a clean device.

Most searched trojans guides

  1. 1Remove Csrss.exe trojan
  2. 2Remove Memz virus
  3. 3Remove Wcupdater
  4. 4Remove Win32/Lodi
  5. 5Remove Chrome.7z
  6. 6Remove Iplogger.org

Trojans removal guides 28–54 of 307

Remove OpenDrive virus: why web.opendrive.com shows up in malware alerts, and what to do if a file from it installed Remcos

OpenDrive is a legitimate cloud storage service, not a virus, but criminals upload files to it that hide malware and point their loaders at them. On 9 and 10 September 2026 URLhaus listed eight such file addresses on...TrojansHigh riskUgnius Kiguolis ·

Remove Cloudinary virus: why res.cloudinary.com shows up in malware alerts, and what to do if a loader fetched its pictures

Cloudinary is a legitimate image hosting service, not a virus, but criminals upload JPG pictures that hide malware and point loaders at them. In September 2026 URLhaus listed eleven such pictures on...TrojansHigh riskUgnius Kiguolis ·

Remove jsDelivr virus: why cdn.jsdelivr.net shows up in malware alerts, and what to do if you ran a pasted command

jsDelivr is a legitimate free CDN, not a virus, but criminals publish malware on GitHub and link to it through cdn.jsdelivr.net. In September 2026 URLhaus listed five such files: If you only saw the address in a log,...TrojansHigh riskUgnius Kiguolis ·

Remove c2.teamzeroday.net: a Mirai botnet host that offered manta files for routers and other small devices, and how to clean one

c2.teamzeroday.net is a host name on a domain registered on 20 September 2026 that URLhaus listed on 1 October 2026 for eleven files in a folder called bin, named manta.x86_64, manta.armv7l, manta.mipsel and so on,...TrojansHigh riskUgnius Kiguolis ·

Remove xiangduck.sld.tw: a server that handed out Mirai bot files for routers and cameras, and what to do if a device fetched them

xiangduck.sld.tw is a web address that URLhaus listed eleven times on 2 October 2026 for files named violet.x86, violet.arm, violet.mips and eight more, six of them tagged Mirai. Mirai is a bot for routers, cameras...TrojansHigh riskUgnius Kiguolis ·

Remove fahrzeugvergabe.de: a German FileFix page that made visitors paste a PowerShell command, and what to do if you did

fahrzeugvergabe.de is a German web address that URLhaus lists three times on 3 October 2026 for malware delivery, tagged ClickFix, FileFix, Loader and powershell. Those tags describe a page that makes you paste a...TrojansHigh riskUgnius Kiguolis ·

Remove truswallet.foundation: a server that handed out Mirai botnet files for routers and cameras, and what to do about it

truswallet.foundation is a web address that URLhaus lists eleven times on 3 October 2026 for Linux program files (ELF) in a folder called bins, all tagged mirai and botnetdomain. These files are made for routers,...TRHigh riskUgnius Kiguolis ·

Remove nd.tdpqnf.com: a server handing out text files tagged Agent Tesla, and what to do if a loader fetched them

nd.tdpqnf.com is a web address that URLhaus lists four times in two days for small .txt files, one tagged AgentTesla, a spyware trojan for Windows, and three tagged rev-base64-loader. A text file like that is not a...TRHigh riskUgnius Kiguolis ·

Remove andbake.cam: a server that handed out files tagged XWorm, and what to do if a loader on your Windows PC fetched them

andbake.cam is a web address that URLhaus lists four times, on 7 October 2026, for files tagged xworm, and two of them are PNG pictures tagged stego, meaning code hidden inside an image. XWorm is a remote access...TRHigh riskUgnius Kiguolis ·

Remove chibomaydan.devs.surf: a download server for Mirai botnet programs aimed at routers and other Linux devices

chibomaydan.devs.surf is a web address that URLhaus lists 13 times on 3 October 2026 for Linux programs (ELF files) tagged mirai and botnetdomain, one file for each chip type that routers, cameras and small servers...TRHigh riskUgnius Kiguolis ·

Remove www.wuming0.tech: a server that handed out Mirai botnet files for routers and Linux devices, and what to do if a device asked for them

www.wuming0.tech is a web address that URLhaus lists 13 times on 3 October 2026 for files named after processor types (arm7, mips, x86_64, sh4 and others), all tagged elf and mirai. These are Linux programs for...TRHigh riskUgnius Kiguolis ·

Remove iloveanal.work.gd: a download server for Mirai botnet files, and what to do if your router or camera fetched them

iloveanal.work.gd is a web address that URLhaus lists 31 times on 3 October 2026 for Linux program files (ELF) tagged mirai and botnetdomain, one file for each kind of processor used in routers, cameras and small...TRHigh riskUgnius Kiguolis ·

Remove emwqkekwqmekwq[.]work[.]gd: a Mirai botnet download host for Linux routers and IoT devices

emwqkekwqmekwq[.]work[.]gd is an address that the abuse.ch URLhaus project listed 31 times on 3 October 2026 as a place where Mirai botnet programs for Linux and IoT devices were offered for download. It is not...TRHigh riskUgnius Kiguolis ·

Remove wemqmewkqewq.work.gd: a free subdomain that handed out Mirai botnet files for Linux and router chips

wemqmewkqewq.work.gd is a web address that URLhaus lists 32 times in two waves (27 September and 3 October 2026) for program files tagged mirai and elf, the kind that infect routers, cameras and Linux servers, not...TRHigh riskUgnius Kiguolis ·

Remove donutsmpclient.com: fake Minecraft client .jar files tagged SilentNet, and what to do if you ran one on Windows

donutsmpclient.com is a web page that offers a free Minecraft 1.21.11 client, and URLhaus lists eight of its .jar files (GoobaClient, FakeClientV3, FrostClientV2, WaterClientV6) as malware tagged SilentNet, six of...TRHigh riskUgnius Kiguolis ·

Remove maxxlavalink.cyou: a server that handed out Mirai and coin miner files for Linux routers and IoT devices, and what to do

maxxlavalink.cyou is a web address that URLhaus lists 19 times, all on 4 October 2026 within about sixteen minutes, for Linux program files named after processor types (arm, mips, x86_64 and more), eleven tagged...TRHigh riskUgnius Kiguolis ·

Remove likedrink.beer: a domain that served 27 Mirai botnet files for routers and other Linux devices, and what to do about it

likedrink.beer is a web address that URLhaus lists 27 times on 4 October 2026 for files named mirai followed by a chip type, such as mirai.arm7 and mirai.mips32. These are builds of the Mirai botnet program for...TRHigh riskUgnius Kiguolis ·

Remove ikovrsps.com: a server handing out Java game files and an EXE tagged stealer and CoinMiner, and what to do if you ran them

ikovrsps.com is a web address that URLhaus lists three times in two days for game style files (Ikov.jar, Mina.jar and gamefiles/image.exe), all tagged stealer and runelite, two also tagged CoinMiner. If you only saw...TRHigh riskUgnius Kiguolis ·

Remove donutclients.st: a Minecraft mod site whose 30 .jar files URLhaus tags as stealers, and what to do if you ran one on Windows

donutclients.st is a website that offers 30 free Minecraft mods for Fabric, and URLhaus lists all 30 of its .jar files (such as Sodium-26.2.jar and meteor-client-26.2.jar) as malware downloads tagged stealer on 7...TRHigh riskUgnius Kiguolis ·

Remove aqclqkcfjwbgknkwnvmm.supabase.co: a Supabase storage bucket that served SilentNet .jar files, and what to do if you ran one on Windows

aqclqkcfjwbgknkwnvmm.supabase.co is one customer project on Supabase, a legitimate cloud storage service. On 5 October 2026 URLhaus listed three .jar files in its public client-files folder, all tagged SilentNet, a...TrojansHigh riskUgnius Kiguolis ·

Remove www.tmcksa.com: a hacked site serving a PowerShell stub for the Formbook stealer, and what to do if your PC ran it

www.tmcksa.com is a website registered in 2013 that URLhaus listed three times on 5 October 2026 for a PowerShell script, secured_stub.ps1, tagged Formbook. Formbook is a Windows information stealer that takes...TRHigh riskUgnius Kiguolis ·

Remove astroliper.ac: a botnet file server for Linux machines entered through SSH, and what to do

astroliper.ac is a web address that URLhaus lists eleven times for nodewatchd, one Linux program built for eleven processor types and tagged ssh: the kind of file botnets put on servers, routers and boards after...TRHigh riskUgnius Kiguolis ·

Remove thisisafalsepositive.st: a SilentNet stealer server behind fake Minecraft mods, and how to clean a Windows PC

thisisafalsepositive.st is a web address that URLhaus lists 13 times for files tagged SilentNet, a stealer spread as fake Minecraft mods, plus a Python kit for Windows. Despite its name, the warning you saw is not a...TrojansHigh riskUgnius Kiguolis ·

Remove www.beinke-aufzuege.de: a hacked website hosting FormBook PowerShell stubs, and what to do if a script fetched them

www.beinke-aufzuege.de is the address of a German website that URLhaus lists for four PowerShell files tagged Formbook, a password stealer for Windows, hidden in random folders inside the site's own Joomla media...TrojansHigh riskUgnius Kiguolis ·

Remove flocmaterials.shop: a new server that handed out PowerShell scripts for VIP Keylogger, and what to do if one ran

flocmaterials.shop is a web address registered on 28 September 2026 that URLhaus lists six times on 5 and 6 October 2026 for PowerShell scripts called secured_stub.ps1, all tagged VIPKeylogger and two also...TrojansHigh riskUgnius Kiguolis ·

Remove qpwot.cfd: a server handing out scripts that lead to the MassLogger and VIP Keylogger stealers, and what to do if one ran

qpwot.cfd is a web address that URLhaus listed seven times on 6 October 2026 for JavaScript files and PowerShell files named secured_stub.ps1, tagged MassLogger and VIPKeylogger, two keyloggers that steal passwords...TrojansHigh riskUgnius Kiguolis ·

Remove aksiyononline.best: a server handing out PowerShell stubs for MassLogger and VIP Keylogger, and what to do if a script fetched them

aksiyononline.best is a web address that URLhaus lists thirteen times for PowerShell and JavaScript files named Crypted.ps1 and secured_stub.ps1, three of them tagged MassLogger and one VIPKeylogger, keyloggers that...TrojansHigh riskUgnius Kiguolis ·
5,557 members already hereReading, writing, commenting and voting. 0 verified · 282 joined this year