
Windows file
winhttp.dll: genuine Windows HTTP Services file, or a copy next to a program?
winhttp.dll is Windows HTTP Services, the Windows library that sends web requests for services and programs. The copies in System32 and SysWOW64 are genuine and safe. A winhttp.dll next to a game's or program's .exe is never Windows' copy: most often it is the BepInEx mod loader's proxy, and sometimes code that hides behind a trusted program.
Prefer to do it yourself? The manual steps follow.
winhttp.dll in C:\Windows\System32 (and C:\Windows\SysWOW64 on 64-bit Windows) is a genuine Microsoft file and is safe. Windows components such as Remote Desktop, netsh and the proxy script worker use it to talk to web servers. Do not delete or replace it.
Programs look for winhttp.dll in their own folder before System32, so a file with this name next to an .exe is loaded and run by that program. The BepInEx mod loader uses this on purpose; attackers can use the same route with a signed program and their own DLL. Check the folder, the signature and the hash.
- Description in the file
- Windows HTTP Services
- What it is
- The WinHTTP client library: sends HTTP and HTTPS requests for Windows services and programs and keeps the WinHTTP proxy setting
- Genuine folders
- C:\Windows\System32\winhttp.dll and, on 64-bit Windows, C:\Windows\SysWOW64\winhttp.dll for 32-bit programs
- Not genuine by location
- Any winhttp.dll in a game or program folder, next to an .exe, in Downloads, Temp or AppData. Windows never puts it there
- Size of the genuine file
- Windows 11 24H2 and 25H2: 1,253,704 bytes (64-bit), 958,632 bytes (32-bit). Windows 10 22H2: 1,096,152 bytes (64-bit), 831,664 bytes (32-bit)
- Signature
- Catalog-signed by Microsoft Windows (Microsoft Windows Production PCA 2011), so the file itself may show no Digital Signatures tab
- Newest indexed build
- Windows 11 26H1: 10.0.28000.2704, delivered by KB5121000 on 11 August 2026
- Known Microsoft builds
- 360 file hashes across 20 Windows releases in Winbindex
- Is it a process
- No. It is a library loaded into the programs that send web requests, so it never appears on its own in Task Manager
What winhttp.dll does, and why programs load other copies of it
winhttp.dll is Windows HTTP Services, usually called WinHTTP. Microsoft documents it as the HTTP client interface for services and server applications: a program opens a session, connects to a web server, sends a request and reads the answer, with HTTPS, authentication and proxy support handled by the library. Windows ships it in every release and updates it together with Windows.
Because winhttp.dll is not on the short list of libraries Windows always takes from System32, a program looks for it in its own folder first. A tool author builds a library with the same name and the same exported functions, puts it next to the .exe, and the program loads it at start. The copy passes the real web calls on to the Windows file, so the program works normally, and in the same moment runs the tool's own code inside it.
BepInEx, an open-source mod loader for Unity games, does this on purpose: its documentation says the Doorstop proxy it uses is usually named winhttp.dll. Attackers use the same technique, called DLL side-loading. HijackLibs, a public list of DLL hijacking cases, names 21 programs that load winhttp.dll this way: 20 Windows programs such as mstsc.exe, netsh.exe, mshta.exe and msdt.exe when they are copied out of System32, and the Minecraft Launcher, signed by Mojang AB.
So the question is never whether winhttp.dll is a virus, but which winhttp.dll you are looking at. The copies in the Windows folders are Microsoft's. A copy next to a program is whatever the person who made it put into it.
About .dll files. A .dll file is a library: it cannot run on its own and is loaded into a program's process. It does not appear in Task Manager under its own name; Process Explorer shows which process loaded it.
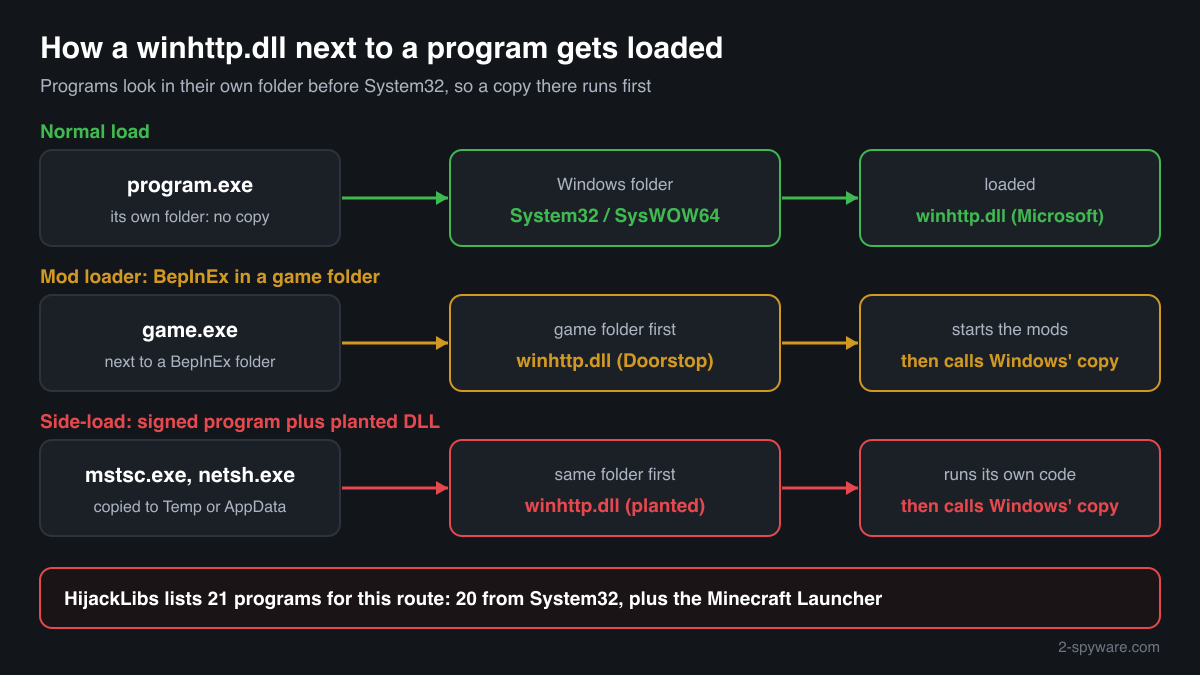
How to tell Windows' winhttp.dll from a copy next to a program
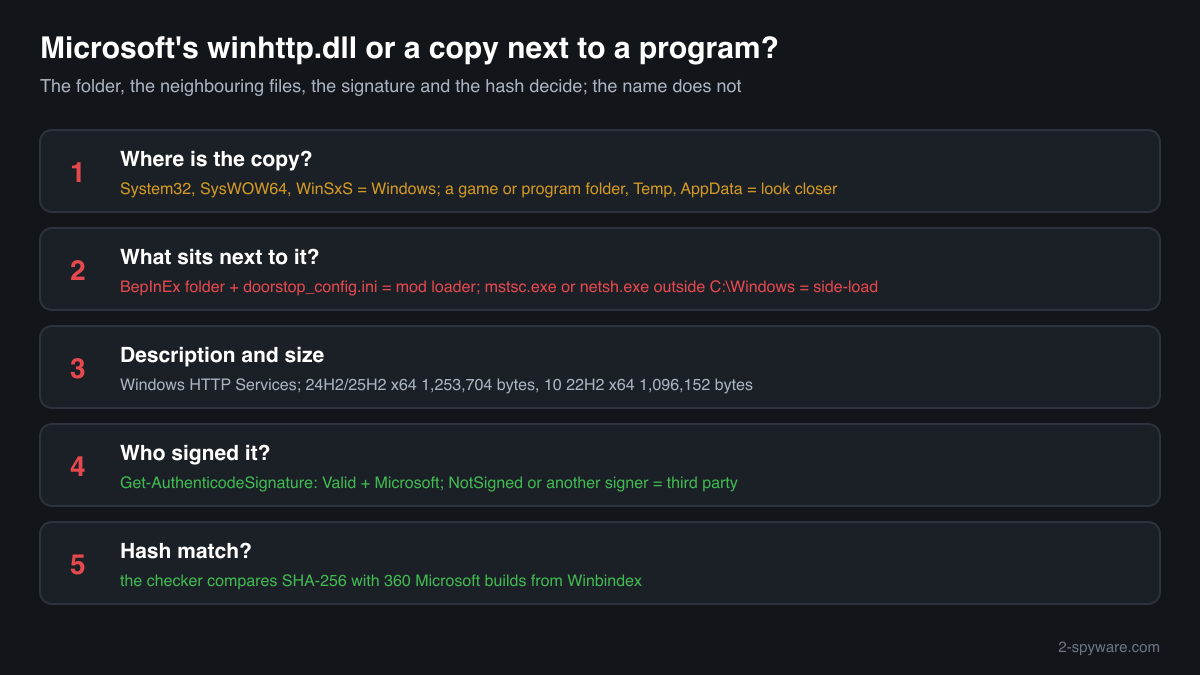
A DLL is not listed in Task Manager as a process, so use the folder, the neighbouring files, PowerShell or Process Explorer.
- Where the file is. List every copy with the command below. C:\Windows\System32 and C:\Windows\SysWOW64 are Windows' copies, and copies under C:\Windows\WinSxS belong to Windows' component store. Every other path is a copy that something installed.
Get-ChildItem C:\ -Recurse -Filter winhttp.dll -ErrorAction SilentlyContinue | Select-Object FullName, Length, @{n='Description';e={$_.VersionInfo.FileDescription}} - What sits next to it. A BepInEx folder and a doorstop_config.ini next to a game's .exe mean the BepInEx loader, which you or a mod manager installed. A Windows program such as mstsc.exe, netsh.exe or msdt.exe outside C:\Windows, or any signed .exe in Temp, AppData or Downloads with a winhttp.dll beside it, is the pattern of a side-load package.
- The Description field and the size. Right-click the file, Properties, Details. The genuine file says Windows HTTP Services, with Microsoft Corporation as the company and a Windows version number such as 10.0.26100. It is about a megabyte or more in Windows 10 and Windows 11. A copy can fake these fields, so this check only rules files out.
- The digital signature. Windows' copy is signed by Microsoft through a catalog rather than inside the file, so the Properties window may show no Digital Signatures tab. PowerShell reads both kinds. Valid with a Microsoft signer means genuine; NotSigned or another signer means a third-party file.
Get-AuthenticodeSignature 'C:\path\to\folder\winhttp.dll' | Format-List Status, SignatureType, SignerCertificate - What the program loads. Start the program, then open Process Explorer from Microsoft Sysinternals, choose Find > Find Handle or DLL, type winhttp.dll and press Search. The path column shows which copy each process really loaded. A path outside the Windows folders means that copy is running inside the program.
- Compare the hash with Microsoft's builds. Use the checker on this page: it computes the SHA-256 in your browser and compares it with 360 known Microsoft builds. A matching copy outside the Windows folders is an unneeded Windows file; one that does not match is a third-party file.
A match to a Microsoft build proves the file is Microsoft's. A file that does not match is not automatically malicious: most game folder copies are the BepInEx proxy, doing exactly what its documentation says. What decides is whether you chose to install that mod loader, from where, and whether the folder it sits in makes sense.
Check your winhttp.dll
Choose the winhttp.dll you are unsure about. Its SHA-256 checksum is calculated in your browser and compared with the 377 Microsoft builds indexed from Windows releases and updates.
The file stays on your computer. Nothing is uploaded: the checksum is computed locally.
Warning signs and what they mean
| What you see | What it means |
|---|---|
| winhttp.dll in a game folder although you never installed BepInEx, a mod manager or any mod for that game | Something else put it there: a repackaged game, a bundled installer, or code that uses the game as a launcher. Treat it as not genuine and scan. |
| winhttp.dll next to mstsc.exe, netsh.exe, mshta.exe, msdt.exe or another Windows program outside C:\Windows | Windows never copies its own programs into other folders. A Windows program plus winhttp.dll in one folder is a side-load pair, the pattern HijackLibs documents. |
| winhttp.dll in Temp, AppData, Downloads or ProgramData, with no game in the folder | No game loads it from there. A copy outside a game folder and outside the Windows folders has no normal reason to exist. |
| The file claims to be Windows HTTP Services from Microsoft Corporation, but has no valid Microsoft signature | A file that pretends to be Windows' copy. The BepInEx proxy does not need to hide; one that imitates Microsoft's details deserves a close look. |
| The mod pack came from a repack, a file-sharing link or a stranger in a chat, not from the BepInEx release page or a mod site with versioned uploads | Proxy loaders are easy to repackage with extra code. Download loaders and plugins only from their authors' own pages. |
| Unexpected outgoing connections, new sign-in alerts or password resets after installing a mod pack | Possible theft of browser sessions or saved passwords. Remove the copy, scan the PC, and change passwords from another device. |
| Microsoft Defender names winhttp.dll in System32 or SysWOW64 | Rare. Check the hash with the checker on this page and run the Microsoft Defender Offline scan before anything else. |
Programs that have been made to load a fake winhttp.dll
Each program below is genuine and signed, and security researchers have documented that it can be made to load a planted winhttp.dll. Usually the attacker copies the program into another folder and puts a fake winhttp.dll next to it: Windows looks in the program's own folder first. A winhttp.dll next to one of these programs, outside the folders below, is the copy to check.
Where the genuine winhttp.dll belongs: C:\Windows\System32C:\Windows\SysWOW64
The genuine winhttp.dll is signed by: Microsoft Windows, a Windows catalog signature (Properties shows no Digital Signatures tab; check it with Get-AuthenticodeSignature)
| Program | How |
|---|---|
C:\Program Files\Minecraft Launcher\MinecraftLauncher.exesigned by Mojang AB SHA-256 of the genuine program: 6511ef24c41cf20f707119dd40971420f1cd6f97f0e888b7d24b5e0dec9d5495 | Side-loading |
C:\Windows\System32\cmdl32.exesigned by Microsoft Windows | Side-loading |
C:\Windows\System32\devicecensus.exesigned by Microsoft Windows | Side-loading |
C:\Windows\System32\dmclient.exesigned by Microsoft Windows | Side-loading |
C:\Windows\System32\dsregcmd.exesigned by Microsoft Windows | Side-loading |
C:\Windows\System32\mdmdiagnosticstool.exesigned by Microsoft Windows | Side-loading |
C:\Windows\System32\msdt.exesigned by Microsoft Windows | Side-loading runs as administrator |
C:\Windows\System32\mshta.exesigned by Microsoft Windows | Side-loading |
C:\Windows\System32\mstsc.exesigned by Microsoft Windows | Side-loading |
C:\Windows\System32\musnotification.exesigned by Microsoft Windows | Side-loading |
and 11 more programs. Source: the HijackLibs entry for winhttp.dll, 4 public reports.
Everyday problems with winhttp.dll
My security software flagged winhttp.dll in a game folder
A detection on a mod loader proxy is common, because a DLL that runs its own code inside another program behaves the way side-loaded malware does. It is not automatically a false alarm either: the same name can carry harmful code.
Decide by origin. If you installed BepInEx from its own release page or through a mod manager and a BepInEx folder sits next to the file, the detection is most likely about the technique. If you do not know where the file came from, leave it quarantined.
Removing a game folder copy never harms Windows: the game then uses the genuine copy in System32 and only the mods stop loading.
I want to remove BepInEx from a game
Delete or rename winhttp.dll in the game folder, together with doorstop_config.ini and the BepInEx folder. The game's own verify option does not remove extra files, so do this by hand.
If you installed the mods through a mod manager, remove them there as well, so it does not put the files back on the next start.
Two winhttp.dll files are in the Windows folders
That is normal on 64-bit Windows: System32 holds the 64-bit library and SysWOW64 the 32-bit one. Both are genuine Microsoft files with different sizes and hashes.
More copies under C:\Windows\WinSxS are normal as well. That is Windows' component store, which keeps the builds Windows needs for updates and repairs.
winhttp.dll versions by Windows release
The newest build indexed for each release, and the update that delivered it. 360 Microsoft builds in total are known.
| Windows release | File version | Delivered by | Size, 64-bit |
|---|---|---|---|
| Windows 11 26H1 | 10.0.28000.2704 | KB5121000, Aug 11, 2026 | 1,216,360 bytes |
| Windows 11 25H2 | 10.0.26100.9549 | KB5127648, Oct 13, 2026 | 1,253,704 bytes |
| Windows 11 24H2 | 10.0.26100.9549 | KB5127648, Oct 13, 2026 | 1,253,704 bytes |
| Windows 11 23H2 | 10.0.22621.7376 | KB5099414, Jul 14, 2026 | |
| Windows 11 22H2 | 10.0.22621.7376 | KB5099414, Jul 14, 2026 | |
| Windows 11 21H2 | 10.0.22000.3079 | KB5044280, Oct 8, 2024 | 1,146,104 bytes |
| Windows 10 22H2 | 10.0.19041.7663 | KB5129236, Sep 14, 2026 | 1,096,152 bytes |
| Windows 10 21H2 | 10.0.19041.7663 | KB5129236, Sep 14, 2026 | 1,096,152 bytes |
| Windows 10 21H1 | 10.0.19041.7663 | KB5129236, Sep 14, 2026 | 1,096,152 bytes |
| Windows 10 20H2 | 10.0.19041.7663 | KB5129236, Sep 14, 2026 | 1,096,152 bytes |
Known versions of winhttp.dll
A public DLL catalogue lists 17 versions of winhttp.dll, from 5.1.2600.2180 to 10.0.18362.778, by Microsoft Corporation. Its copies are uploaded by users and not verified, so a checksum match identifies the version, while the digital signature tells you whether the file is genuine. Even a genuine file clears only the file, not the folder: attackers ship genuine libraries next to a program they abuse, so where the copy sits still decides whether it is safe.
Every version with its checksums, and how to fix winhttp.dll errors on uGetFix
Questions people ask
Is winhttp.dll a virus?
No, not the Windows copy. winhttp.dll is Windows HTTP Services, and the files in System32 and SysWOW64 are genuine Windows libraries. A winhttp.dll next to a game or program is a different file with the same name, most often the BepInEx mod loader's proxy. Other code can use the name too, so check where the copy came from and compare its hash.
Why is there a winhttp.dll in my game folder?
Usually because BepInEx is installed there. Its documentation says the Doorstop proxy it uses to start is usually named winhttp.dll, and mod managers place it next to the game's .exe when you add BepInEx mods to a Unity game. If you never installed mods for that game, treat the file as suspicious and scan the PC.
Why does a program connect to the internet through winhttp.dll?
Because that is the library's job. WinHTTP is the Windows interface for sending web requests from services and programs, so seeing it loaded in a program that checks for updates or talks to a server is normal. It only matters which copy is loaded: the one in System32 or SysWOW64, or another one next to the program.
What can a malicious winhttp.dll do?
Anything the program that loads it can do. The copy runs inside that program with your user account's rights, or with administrator rights if the program has them, so it can read and write files, read browser data, open network connections and start other programs, while still passing web requests on to Windows so nothing looks broken. That is why the folder and the origin matter more than the name.
Is it safe to use BepInEx, which installs winhttp.dll?
It is as safe as its source. BepInEx is an open-source mod loader, and a copy from its own release page or a mod site with versioned uploads is a normal modding tool. The same file name in a repack, a file-sharing link or a chat message can contain anything. Keep the loader updated, check the plugins you add, and remove it when you stop modding.
How do I check if my winhttp.dll is genuine?
Check three things. The folder: only System32 and SysWOW64, plus the WinSxS store, hold Windows' copies. The signature: Get-AuthenticodeSignature in PowerShell shows Valid with a Microsoft signer for the genuine file. The hash: the checker on this page compares the SHA-256 with 360 known Microsoft builds. A copy that fails these checks is not Windows' file.
Sources
- Microsoft Learn: About WinHTTP
- Microsoft Learn: Dynamic-link library search order
- HijackLibs: winhttp.dll
- BepInEx Docs: Troubleshooting
- BepInEx on GitHub: discussion #331, the Doorstop proxy file
- MITRE ATT&CK T1574.002: DLL Side-Loading
- Microsoft Sysinternals: Process Explorer
- Winbindex, the Windows binaries index (m417z)
- Winbindex, the Windows binaries index (m417z)
Version data read on Oct 17, 2026.
Questions and experiences
Ask about this page: members and our editors answer. Reading is open; writing needs a free account.
…