
VMware Vulnerability 2026: Exploited ESXi and vCenter CVEs
- VMware vulnerabilities in 2026: the short answer
- Timeline: VMware exploits from 2025 to 2026
- What changed since 2025
- Risks for VMware users right now (our analysis)
- How to secure VMware systems in 2026
- What is still unknown
- Our original 2025 report
- Inside the VMware ESXi security risks
- Steps to secure your VMware systems
- Related guides on 2-Spyware
VMware vulnerabilities in 2026: the short answer
VMware products are still a prime target in 2026. The three ESXi, Workstation and Fusion flaws from our original March 2025 report, CVE-2025-22224, CVE-2025-22225 and CVE-2025-22226, stay listed by CISA as known exploited vulnerabilities.[6] Systems that never got the VMSA-2025-0004 patches are still exposed.[4]
A newer and larger risk arrived in summer 2026. On July 29, 2026, Broadcom published VMSA-2026-0006, which fixes five flaws in ESX, vCenter Server, Workstation and Fusion.[7][8] Two of them, CVE-2026-59309 and CVE-2026-59310 in vCenter Server, are rated CVSS 9.8 and were reported as exploited in the wild.[8] If you run vCenter, patch that first.
| Question | VMSA-2025-0004 | VMSA-2026-0006 |
|---|---|---|
| Main products | ESXi, Workstation, Fusion[4] | vCenter Server, ESX, Workstation, Fusion[7] |
| Key CVEs | CVE-2025-22224, CVE-2025-22225, CVE-2025-22226[4] | CVE-2026-59309, CVE-2026-59310[8] |
| Highest CVSS | 9.3 for CVE-2025-22224[4] | 9.8 for both vCenter flaws[8] |
| Attacker needs | Admin rights inside a virtual machine[6] | Network access, no valid credentials for CVE-2026-59310[8] |
| Exploited in the wild | Yes, listed in CISA KEV[6] | Yes, according to public reports[8] |
| Workaround | None listed; patch[4] | None; patch[8] |
Timeline: VMware exploits from 2025 to 2026
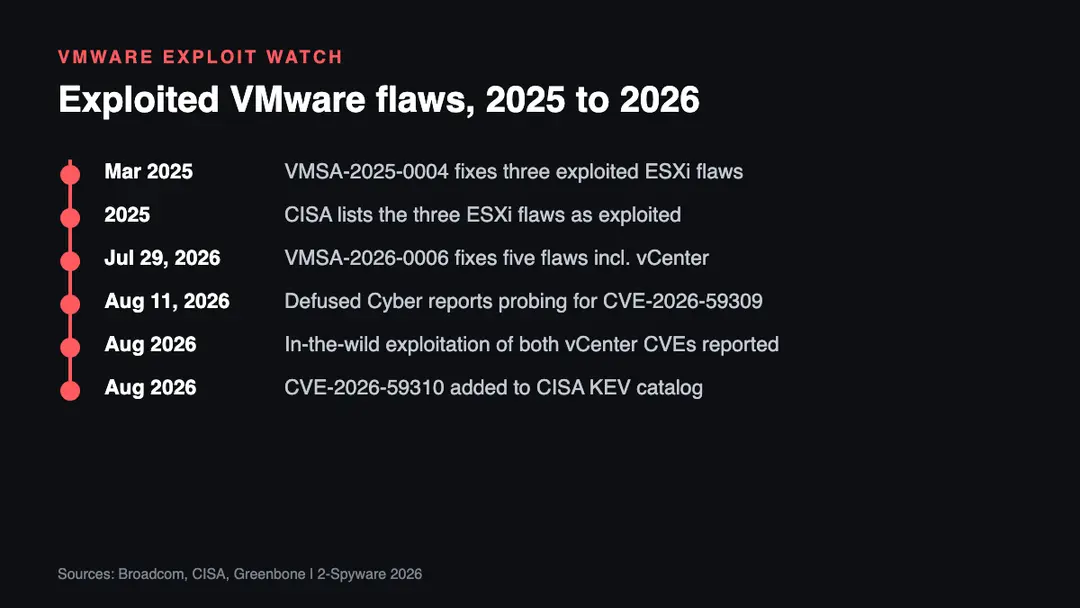
| Date | Event |
|---|---|
| March 2025 | Broadcom releases VMSA-2025-0004 for CVE-2025-22224, CVE-2025-22225 and CVE-2025-22226, all exploited in the wild[4] |
| 2025 | CISA adds the three flaws to its Known Exploited Vulnerabilities catalog[6] |
| July 29, 2026 | Broadcom publishes VMSA-2026-0006 for five flaws in ESX, vCenter, Workstation and Fusion[8] |
| August 11, 2026 | Defused Cyber reports probing for CVE-2026-59309, according to Greenbone[8] |
| August 2026 | Reports say both vCenter flaws are exploited; CVE-2026-59310 is added to CISA KEV[8] |
What changed since 2025
Our original report covered a VM escape chain. An attacker first needed admin rights inside a guest machine and then broke out to the hypervisor.[6] That limited who could use it. The 2026 vCenter flaws remove that hurdle. Greenbone describes CVE-2026-59310 as a directory traversal in the vCenter Syslog component that lets an unauthenticated remote attacker run code.[8]
The second flaw, CVE-2026-59309, is an authentication bypass in the VMware Directory Service.[8] vCenter manages many hosts at once, so control over it can mean control over a whole virtual estate. Greenbone also notes that technical details were published right after disclosure, which shortens the time defenders have.[8]
We also corrected an error in our original 2025 text. Its first paragraph listed CVE numbers from 2024. The correct identifiers, as in Broadcom's advisory, are CVE-2025-22224, CVE-2025-22225 and CVE-2025-22226.[4] The rest of the old report is unchanged.
Risks for VMware users right now (our analysis)
- Internet-facing vCenter. A management interface open to the internet is the easiest path for the 2026 flaws, which need no valid login.[8]
- Ransomware on hypervisors. Our original report named ransomware gangs that target VMware environments.[5] One encrypted host can take down every virtual machine on it.
- Old unpatched builds. The 2025 ESXi flaws are still on CISA's exploited list.[6] Any host that missed VMSA-2025-0004 is still a target.
- Fake patch downloads. In our analysis, urgent patch news brings phishing emails with fake "VMware update" links. Download fixes only through the Broadcom support portal.
How to secure VMware systems in 2026
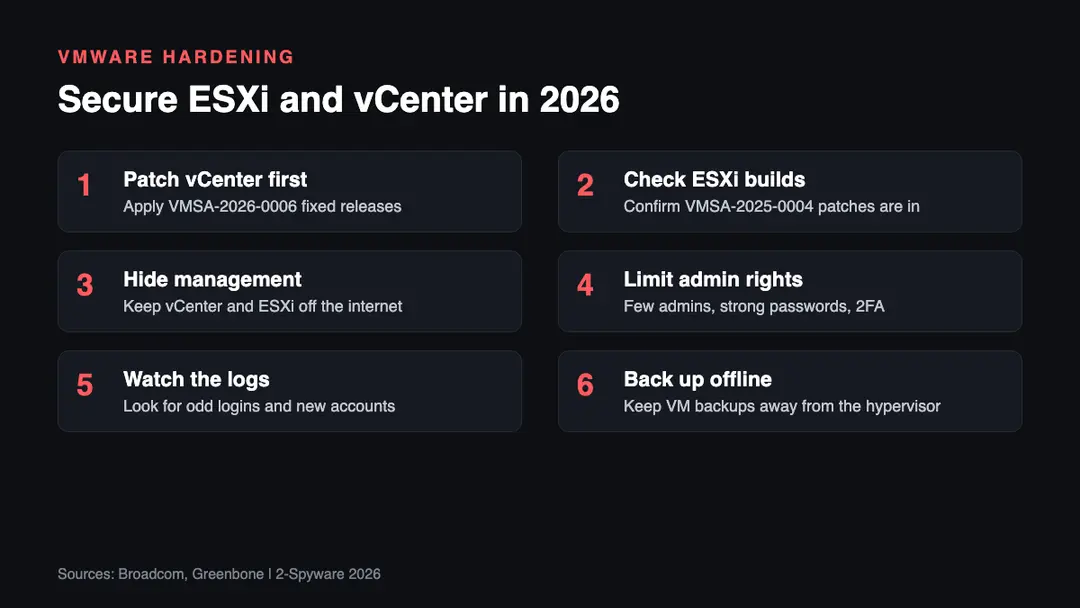
1. Patch vCenter first. Map your vCenter version to the fixed releases in VMSA-2026-0006 and update.[7] Greenbone says there is no workaround.[8]
2. Check every ESXi build. Confirm each host runs a build at or above the fixed releases in VMSA-2025-0004, such as build ESXi80U3d-24585383 for ESXi 8.0.[4]
3. Hide management interfaces. Keep vCenter and ESXi management behind a VPN or a separate admin network. This blocks the remote, no-login path of CVE-2026-59310.[8]
4. Limit admin rights. The 2025 chain started with admin access inside a guest.[6] Fewer admin accounts mean fewer starting points.
5. Watch the logs. Look for unknown logins, new local accounts and unexpected changes on vCenter and hosts after July 29, 2026. If you see them, treat the system as compromised.
6. Back up offline. Keep copies of virtual machines where a hijacked hypervisor cannot reach them. Our malware removal guides cover ransomware recovery basics.
What is still unknown
- Who is behind the 2026 vCenter attacks. Some reports point to a suspected China-linked group, but we found no official attribution as of 2026.
- How many organizations were breached through CVE-2026-59310. We found no confirmed count from Broadcom or CISA.
- Whether ransomware groups use the 2026 vCenter flaws yet. We found no confirmed case.
Our original 2025 report
The text below is our report as first published in 2025. We keep it unchanged for the record; the sections above bring it up to date.
In March 2025, Broadcom released critical patches for three zero-day vulnerabilities in VMware products, including VMware ESXi, Workstation, and Fusion. These flaws, identified as CVE-2025-22224,[1] CVE-2025-22225,[2] and CVE-2025-22226,[3] were already being exploited by attackers in real-world scenarios, making them a serious threat. Broadcom's security advisory says:[4]
Updates are available to remediate these vulnerabilities in affected VMware products.
These vulnerabilities allow attackers with high-level access inside a virtual machine to break out of its sandbox and target the hypervisor – the software that manages all virtual machines on a system. If successful, attackers could steal sensitive data, disrupt operations, or take full control of the host. The Microsoft Threat Intelligence Center first spotted these issues, showing how vital it is to stay proactive in cybersecurity.
This news affects many users because VMware ESXi is common in data centers, while Workstation and Fusion are popular on desktops and Macs. Broadcom acted quickly to release fixes, but the responsibility now falls on users to apply them. The scale of the problem and the active exploitation make this a top priority for IT teams everywhere.
Inside the VMware ESXi security risks
The three vulnerabilities fixed by Broadcom have specific names and risks. CVE-2025-22224 is a "Time-of-Check Time-of-Use" flaw that lets an attacker with admin rights in a virtual machine write outside its allowed memory, running harmful code on the host. CVE-2025-22225 is an "arbitrary write" issue that also helps attackers escape the sandbox. CVE-2025-22226 allows attackers to read hidden memory, leaking sensitive data from the system.
For these attacks to work, an attacker needs administrative access (like "root") inside a virtual machine first. From there, they can chain the flaws together to move from the virtual machine to the hypervisor. This could let them steal data, disrupt systems, or install more malware, making it a dangerous threat.
Since the affected products are common in businesses and IT setups, the vulnerabilities could impact many users. Broadcom confirmed that attackers were already exploiting these flaws before the patches were released.
It's worth noting that numerous ransomware cybercriminal gangs, such s Helldown and Play,[5] are known to exploit VMware environments to infect systems with malware.
Steps to secure your VMware systems
Broadcom has released patches to fix these vulnerabilities, so users should visit the Broadcom website to download and install the updates as soon as possible. Waiting too long could leave systems open to attacks, especially since hackers are already using these flaws.
Beyond patching, it's smart to secure virtual machines properly. Limit who gets admin rights, watch for unusual activity, and keep all software updated. These steps can make it harder for attackers to start an exploit, even if they find a way into your system.
For extra protection, companies should also use tools like network segmentation (to keep systems separate) and intrusion detection (to spot threats early). By acting quickly and following these tips, VMware users can lower the risk of attacks and keep their data and systems safe from this serious vulnerability.
Related guides on 2-Spyware
Frequently asked questions
Which VMware vulnerabilities are being exploited in 2026?
Two vCenter Server flaws, CVE-2026-59309 and CVE-2026-59310, were reported as exploited in the wild after Broadcom fixed them on July 29, 2026.{8} The 2025 ESXi flaws CVE-2025-22224, CVE-2025-22225 and CVE-2025-22226 also remain listed as known exploited by CISA.{6}
Where are VMware security advisories published now?
On the Broadcom support portal. Since Broadcom bought VMware, VMware Security Advisories (VMSA) appear there, for example VMSA-2025-0004 for the ESXi flaws and VMSA-2026-0006 for the vCenter flaws.{4}{7} Each advisory lists affected versions, CVSS scores and fixed releases.
What is CVE-2026-59310?
It is a critical directory traversal flaw in the Syslog component of VMware vCenter Server. An unauthenticated remote attacker can use it to run code, and it is rated CVSS 9.8.{8} Greenbone reports that it was added to CISA's Known Exploited Vulnerabilities catalog.{8}
Is there a workaround for the 2026 vCenter vulnerabilities?
No. Greenbone says no workarounds are available for any of the CVEs in VMSA-2026-0006.{8} The only fix is to install the patched releases listed in Broadcom's advisory.{7}
What did the VMSA-2025-0004 ESXi vulnerabilities allow?
They let an attacker with admin rights inside a virtual machine escape to the host. CISA describes CVE-2025-22224 as a race condition that lets that attacker run code as the VMX process on the host, and CVE-2025-22225 as an arbitrary kernel write that leads to a sandbox escape.{6}
How do I check if my VMware system is vulnerable?
Compare your exact ESXi, vCenter, Workstation or Fusion build with the fixed releases in the relevant Broadcom advisory.{4}{7} If your build is older than the fixed one, it is vulnerable. Also check the CISA KEV catalog, which lists VMware flaws known to be exploited.{6}
Log in to comment
No comments yet. Be the first.