
Chrome Bug Bounty Maximum Reward in 2026: $250,000 and More
- Chrome bug bounty in 2026: the short answer
- Timeline: Chrome and Google bounty milestones
- What changed since 2024
- Bug bounty scams to watch for (our analysis)
- How to report a Chrome bug and stay safe
- What is still unknown
- Our original 2024 report
- Incentivizing deep security research
- Broad reward category expansion beyond memory corruption
- Bug bounties can save Google from devastating cybersecurity flaws
- Related guides on 2-Spyware
Chrome bug bounty in 2026: the short answer
The $250,000 top reward announced in 2024 is still in the Chrome rules. Google's Chrome VRP rules say a novel demonstration with a functional exploit can earn between $85,000 and $250,000.[7] On top of that, a valid MiraclePtr bypass is eligible for $250,128, which can be added as a bonus to a qualifying use-after-free report.[7]
Payouts are also larger than before. Google paid more than $17 million to 747 researchers across all its programs in 2025, an all-time high.[5] The Chrome team's share was $3,716,750 to more than 100 reporters, according to BleepingComputer.[6] The highest single reward Google lists for 2025 is $250,000.[5]
| Question | Answer in 2026 |
|---|---|
| Top exploit reward | $85,000 to $250,000 for a novel demonstration with a functional exploit[7] |
| MiraclePtr bypass | $250,128, at most four rewards after the April 2026 update[7] |
| AI feature bugs | Up to $20,000 for rogue actions, up to $10,000 for data exfiltration[7] |
| Chrome paid in 2025 | $3,716,750 to over 100 reporters[6] |
| All Google programs 2025 | Over $17 million to 747 researchers[5] |
| Since 2010 | $81.6 million in total rewards[5] |
Timeline: Chrome and Google bounty milestones
| Date | Event |
|---|---|
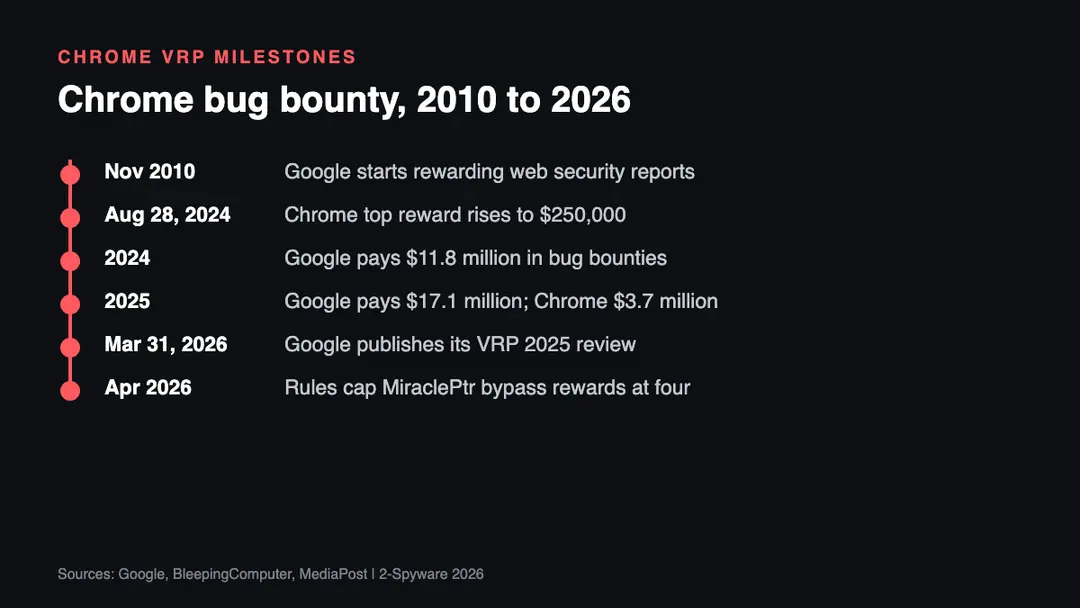
| November 2010 | Google starts rewarding web application security reports[4] |
| August 28, 2024 | New Chrome reward structure takes effect with a $250,000 top amount[1] |
| 2024 | Google pays $11.8 million in bug bounties[8] |
| 2025 | Google pays over $17 million; Chrome awards $3,716,750[5][6] |
| March 31, 2026 | Google publishes its VRP 2025 Year in Review[5] |
| April 2026 | A rules update limits MiraclePtr bypass rewards to four[7] |
What changed since 2024
The 2024 change was about depth: Google wanted reports that show the full impact of a bug, not only a crash.[1] The current rules keep that idea. Basic memory bugs earn modest base amounts, and the large sums go to novel exploits and to bypasses of Chrome protections.[7]
Two new areas appeared. Google says the Chrome VRP now has reward categories for AI features, and the rules list amounts for rogue actions and data exfiltration.[5][7] Google also says it launched a separate AI VRP in 2025, moved out of the Abuse program.[5]
The money grew too. Google's total payouts went from $11.8 million in 2024 to over $17 million in 2025, which Google calls an increase of more than 40 percent.[8][5] Over 16 years the programs have paid $81.6 million in total.[5]
Bug bounty scams to watch for (our analysis)
Large reward figures attract fraud. This list is our own analysis, not a Google warning.
- Fake bug bounty emails that claim you won a Google reward and ask for a fee or bank login. Google rewards go through Bug Hunters, not random messages.
- Sellers of so-called Chrome zero-day exploits on forums and Telegram. Buying them can be illegal and many are fake.
- Fake "Chrome security update" downloads that use bounty news as bait. Chrome updates itself from Google.
- Phishing pages that copy the Bug Hunters site to steal Google account logins. Check the address bar before you sign in.
- Middlemen who promise to submit your bug for a share of the reward. You can report directly.
How to report a Chrome bug and stay safe
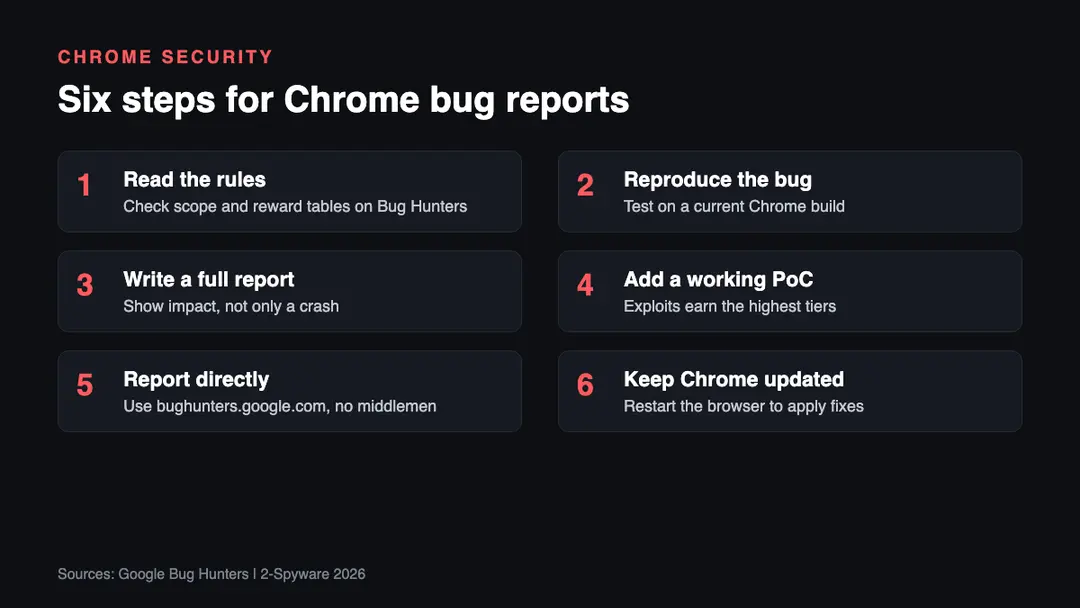
1. Read the rules. Open the Chrome VRP rules on Google Bug Hunters and check whether your bug class and the affected process are in scope.[7]
2. Reproduce the bug. Confirm it on a current Chrome build so the team can verify it quickly.
3. Write a full report. Explain the real impact. Google said in 2024 that it wants reports that paint the full picture of a bug.[1]
4. Add a working proof of concept. The highest tiers, from $85,000 to $250,000, require a functional exploit.[7]
5. Report directly. Submit through bughunters.google.com yourself. Ignore anyone who asks for a fee to submit or to release a reward.
6. Keep Chrome updated. For everyday users, the benefit of the bounty arrives as updates. Restart Chrome when it asks, and use our leak check if you suspect your Google account was exposed.
What is still unknown
- How many Chrome reports reached the $250,000 tier. The 2025 figures we read give totals, not a breakdown by tier.[5][6]
- Whether Google will raise the Chrome maximum again in 2026. We found no announcement.
- How many of the four MiraclePtr bypass rewards have been paid since April 2026.[7]
- How the AI feature categories will grow as Gemini tools spread in Chrome.
Our original 2024 report
The text below is our report as first published in 2024. We keep it unchanged for the record; the sections above bring it up to date.
Google has recently announced a major update to its Chrome Vulnerability Reward Program. As a part of ongoing efforts to harden the security of the Chrome browser, Google increased the maximum reward for finding critical security flaws to an impressive $250,000 – encouraging researchers to look in this direction and report high-impact vulnerabilities:[1]
While the reward amounts for baseline reports of memory corruption will remain consistent, we have increased reward amounts in the other categories with the goal of incentivizing deeper research into the full consequences of a given issue. The highest potential reward amount for a single issue is now $250,000 for demonstrated RCE in a non-sandboxed process.
Effective August 28, 2024, this new reward structure aims to entice top security talent with higher payouts for detailed reports that paint the full picture of a bug's impact. This raises the cap from the earlier set limit of $115,000 and underscores Google's commitment to staying ahead in the cybersecurity landscape.
The top prize will be awarded for research that uncovers and reports memory corruption bugs in non-sandboxed processes, some of the most severe vulnerabilities, as they might allow attackers to execute hostile code on a user's system.
Incentivizing deep security research
The higher rewards from Google are not just about the numbers; they are really incentives for security researchers to give an in-depth scrutiny of the implications of the vulnerabilities they identify. The most interesting reports for Google would be those not only indicating a flaw but also including a profound analysis of its possible impact and how it could be further exploited by attackers.
For instance, the maximum prize is awarded when one demonstrates RCE in a non-sandboxed process, up to $250,000. The prize can go higher if this RCE can be done without having to compromise Chrome's renderer process, depending on the complexity and impact of the exploit.
These large rewards show Google's goal of promoting a collaboratory approach to security that encourages researchers to explore vulnerabilities to their full potential. These important insights allow Google security teams to provide strong patches, mitigating the risk out there.
Broad reward category expansion beyond memory corruption
While memory corruption bugs are one major focus, Google's updated VRP rewards are also extending to other categories of vulnerabilities. For example, high-quality reports on client-side vulnerabilities (such as cross-site scripting attacks or site isolation bypasses) now earn researchers up to $30,000.[2]
Apart from these, Google also reemphasized the importance of its MiraclePtr technology, which stands as the primary defense to the exploitation of use-after-free. The success reward for the bypass of MiraclePtr has been set at $250,128 – the step that shows it featuring in the security structure of Chrome.[3]
These reward increases are part of a more general strategy by Google to have all potential security threats taken up with as much fervor as only the most critical ones. By categorizing vulnerabilities according to their impact and offering tailored rewards, Google is capable of covering a very wide area of potential problems.
Bug bounties can save Google from devastating cybersecurity flaws
Trend on Cybersecurity Google's motivation to boost bug bounty incentives reflects a more widespread trend in the cybersecurity space. Every day, as threats become more sophisticated, companies lean on bug bounty programs to identify and fix vulnerabilities before they are exploited by malicious actors.
High-dollar payouts drive competitive, talented security researchers to invest and pour themselves into uncovering critical flaws. This proactive approach helps companies like Google to continue staying ahead in the evolving threat landscape, maintaining the safety of their users and trust in their products.
Since launching our VRP in 2010,[4] Google has paid out over $50,000,000 in reward payments to researchers reporting over 15,000 vulnerabilities. The recent reward increase to $250,000 is an indication of the company's determination to continue this collaborative approach to cyber security and the importance of independent research in keeping its products secure.
Related guides on 2-Spyware
Frequently asked questions
What is the maximum reward in the Chrome bug bounty in 2026?
The headline figure is still $250,000. Current Chrome VRP rules say a novel demonstration with a functional exploit can earn $85,000 to $250,000.{7} A valid MiraclePtr bypass is eligible for $250,128, and the rules say it can be added as a bonus on top of a qualifying use-after-free reward.{7} So one exceptional report can go past $250,000.
How much did Google pay Chrome researchers in 2025?
BleepingComputer reports that the Chrome security team awarded $3,716,750 to more than 100 reporters in 2025.{6} Across all Google programs, Google says it paid over $17 million to 747 researchers, an all-time high and more than 40 percent above 2024.{5}
When did Google raise the Chrome bounty to $250,000?
Google announced the new Chrome reward structure effective August 28, 2024.{1} The top amount of $250,000 was set for a demonstrated remote code execution in a non-sandboxed process, up from an earlier cap of $115,000.{1}{2} The amount still appears in the Chrome rules in 2026.{7}
What is a MiraclePtr bypass reward?
MiraclePtr is a Chrome protection against use-after-free memory bugs. The Chrome VRP rules say a valid bypass of it is eligible for $250,128.{7} The rules also say that a maximum of four MiraclePtr bypass rewards will be paid following the April 2026 rules update.{7}
Does the Chrome bug bounty cover AI features?
Yes. Google says the Chrome VRP now includes reward categories for problems in AI features.{5} The rules list rogue actions at up to $20,000 and sensitive data exfiltration at up to $10,000 for high-impact, reliable reports.{7}
Where do I report a Chrome security bug?
Reports go through Google Bug Hunters at bughunters.google.com, which hosts the Chrome VRP rules and the reward tables.{7} Read the rules first, since the amount depends on the bug class, the process affected and the quality of the report and exploit.{1}{7}
Log in to comment
No comments yet. Be the first.