
Accenture Ransomware Attack: LockBit 2021 and 2026 Breach
- Accenture ransomware attack in 2026: the short answer
- Timeline: Accenture and LockBit, 2021 to 2026
- What changed since 2021
- Risks for Accenture clients and staff (our analysis)
- What to do if you work with Accenture
- What is still unknown
- Our original 2021 report
- There is a possibility for an insider job
- Ransomware attacks remain the biggest issue and a headache
- Related guides on 2-Spyware
Accenture ransomware attack in 2026: the short answer
Accenture was attacked by the LockBit ransomware gang in the summer of 2021. The company found the intrusion on July 30, 2021, restored its systems from backup, and later told the SEC that attackers took proprietary information.[7] LockBit had demanded a $50 million ransom.[7]
Accenture is back in security news in 2026 for a different reason. On July 8, 2026 Cybersecurity Dive reported that a hacker calling themselves "888" claimed to have stolen about 35GB of Accenture data, including source code and access keys.[8] Accenture called it an isolated matter and said it had fixed its source, with no impact on operations.[8] We found no link between this claim and LockBit.
| Question | 2021 LockBit attack | 2026 data theft claim |
|---|---|---|
| Who claimed it | LockBit ransomware gang[1] | A hacker using the name "888"[8] |
| When | Found on July 30, 2021, disclosed in August[7] | Intrusion in early July 2026[8] |
| What was taken | Proprietary information, per the SEC filing[7] | About 35GB, said to include source code and keys[8] |
| Ransom | $50 million demanded[7] | None reported in the source we read |
| Accenture's response | Servers isolated and restored from backup[2] | Called it isolated and remediated[8] |
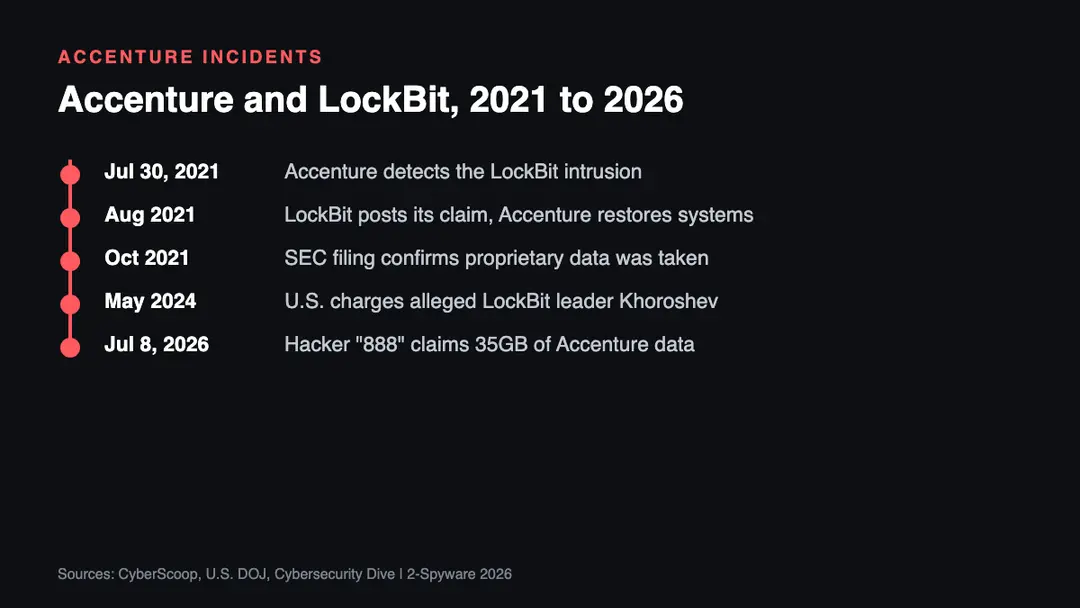
Timeline: Accenture and LockBit, 2021 to 2026
| Date | Event |
|---|---|
| July 30, 2021 | Accenture discovers the intrusion[7] |
| August 2021 | LockBit advertises Accenture data, Accenture says systems are restored[1][2] |
| October 2021 | Accenture's SEC filing says proprietary information was extracted[7] |
| May 2024 | U.S. charges Dmitry Khoroshev as LockBit's developer and administrator[9] |
| July 8, 2026 | Report of a new data theft claim against Accenture by "888"[8] |
What changed since 2021
In 2021 the open question was what LockBit took. Accenture answered it in an SEC filing: the attackers extracted proprietary information, though the company did not describe its exact nature.[7] That confirmed the incident was more than a short outage.
LockBit itself has changed a lot. Law enforcement disrupted the group in February 2024, and in May 2024 the U.S. charged Russian national Dmitry Khoroshev as its developer and administrator.[9] LockBit attempted a comeback, suffered a breach of its own infrastructure in May 2025 and released LockBit 5.0 in September 2025.[10] Our separate report on Khoroshev covers that case.
For Accenture, the 2026 claim is a reminder that large IT suppliers stay a target. Cybersecurity Dive said the stolen data, if real, could put clients at risk, because it reportedly includes Azure access tokens, RSA keys and SSH keys.[8] Accenture said there was no impact on operations and service delivery.[8]
Risks for Accenture clients and staff (our analysis)
The points below are our own analysis of what such incidents mean for people and companies around Accenture. They are not statements from Accenture.
- Leaked keys and tokens. If access keys are real and not rotated, they can open cloud systems of the firm or its clients.[8]
- Targeted phishing. Staff names and project details from leaks help criminals write convincing emails to clients and employees.
- Fake "Accenture breach" notices. Scammers send messages that claim to be breach alerts and ask you to log in or pay.
- Insider recruitment. Our 2021 report notes claims that LockBit tried to hire insiders. Such offers remain a risk for any large employer.[3]
What to do if you work with Accenture
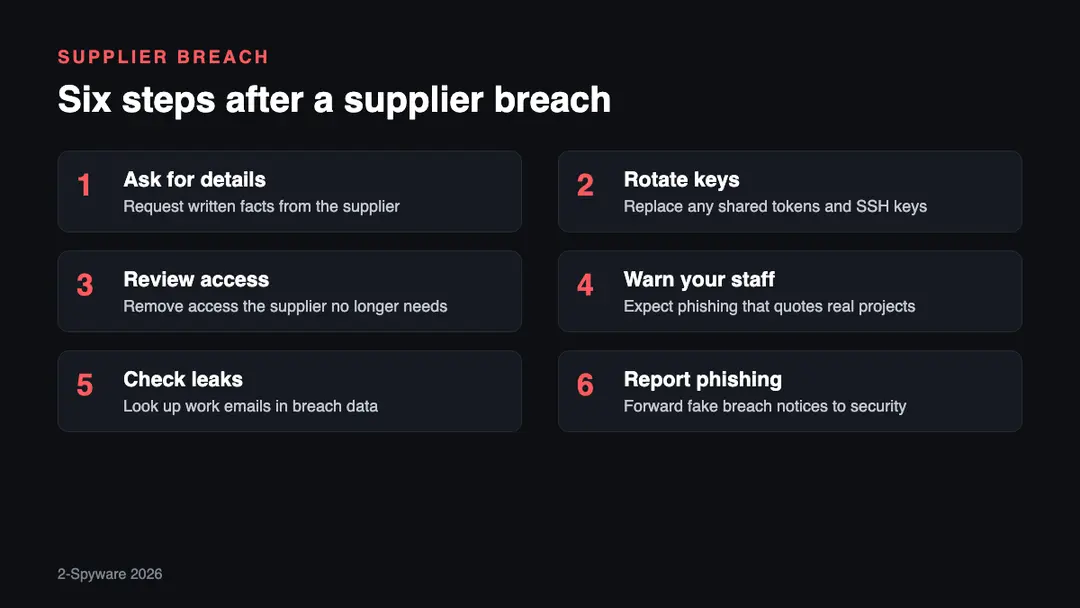
1. Ask for details. If you are a client, ask your account team in writing whether any of your data or credentials were involved.
2. Rotate keys. Replace any shared access tokens, RSA keys or SSH keys that a supplier could have held. The 2026 claim names exactly these types.[8]
3. Review access. Remove supplier accounts and remote access that are no longer needed.
4. Warn your staff. Tell employees to expect emails that mention real projects or names, and to verify requests by phone.
5. Check leaks. Look up work email addresses with our leak check and follow our data breach list.
6. Report phishing. Forward fake breach notices to your security team. Our guide on how to report phishing explains where else to send them.
What is still unknown
- What exact proprietary information LockBit took in 2021. Accenture's filing did not say.[7]
- Whether the 35GB claimed in 2026 is genuine and complete. The report we read is based on the attacker's claim and Accenture's short statement.[8]
- Whether any client systems were accessed with the reported keys. We found no public statement on that.
We will update this page if Accenture, a regulator or law enforcement publishes more details.
Our original 2021 report
The text below is our report as first published in 2021. We keep it unchanged for the record; the sections above bring it up to date.
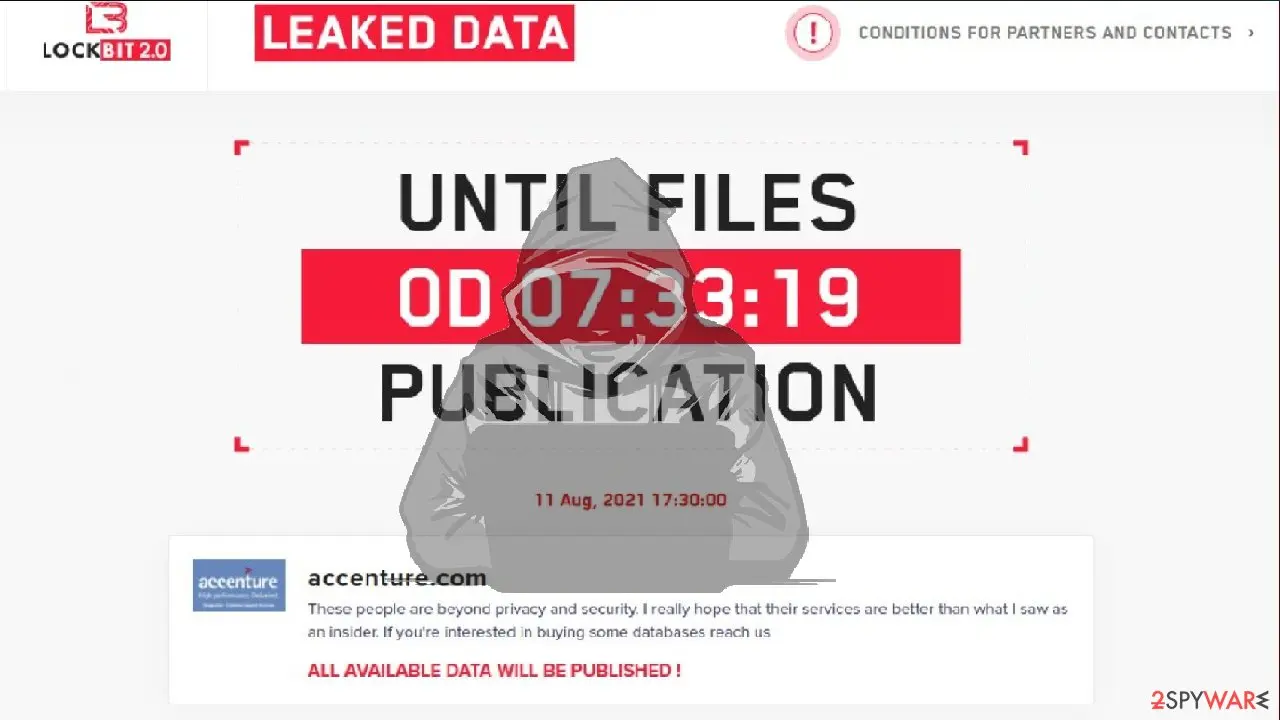
Global IT consultancy firm Accenture joined the long list of companies that were hit by the LockBit ransomware gang, which became even more active after the shutdown of the two most dangerous threats. It seems that LockBit 2.0 creators hacked Accenture's databases, affected files, and then made a post on the Dark Web site offering said Accenture's databases up for sale, and even made fun of companies' sad security system. The post made by the malware creators:
These people are beyond privacy and security. I really hope that their services are better than what I saw as an insider
However, as of right now, the company communicated that all of the affected systems are fully restored and back to work. The threat was identified by a CNBC reporter who tweeted that the hacker group is bragging about attacking the IT consulting firm using LockBit ransomware. Private data and confidential client information were threatened to be released in several hours too.[1]
The company released a statement sharing that all irregular activities were immediately contained, affected servers were isolated, and fully restored from backup. Representatives of the company, while speaking on Wednesday, assured that all operations are safe and clients have nothing to worry about.[2]
Accenture has some high-profile clients that may be concerned and interested in recent events. The firm works with 91 of the Fortune Global 100 companies. According to its 2020 annual report, widely known e-commerce names like Alibaba, Cisco, and even Google itself are some of the most influential clients. However, Accenture is no small fish, as it is valued at $44.3 billion and is regarded as one of the world's largest tech consultancy firms.
There is a possibility for an insider job
Some researchers seem to think that Accenture's hit was an insider job. Cyble researchers tweeted that the LockBit virus group has been hiring corporate employees to gain access to their targets' networks, and this information is circulating for a while now. Even threat actors themselves alleged that the hack was an insider job by someone who is still employed there. However, it's unclear how much truth is behind such a statement.[3]
Since the in-depth research on the attack is not done yet, there are no official reports on whoever helped threat actors to gain access to the companies database. However, it is believed that obtained information could be used by hackers. There is a possibility that even later, certain demands for ransom payments could be received. In addition, it is still unclear whether victims individually received any threatening messages.
Ransomware attacks remain the biggest issue and a headache
In recent years ransomware attacks seem to be on the rise, especially the ones, connected to high level companies or even national government and economic sectors. However, a lack of cybersecurity could be pointed out. After such attacks, businesses are usually left in confusion and met with angered clients. It's clear that critical data is not safe from any cybercrime nowadays.[4]
LockBit ransomware is a virus that is borrowing tricks from other threats like REvil and Maze, so it can take ransomware attacks to the next level. Cybercriminals behind the malware use double extortion techniques to make victims pay the ransom. First, the attackers breach the company's network, begin gathering information, and later deploy the LockBit virus to directly affect found files.[5]
The first known ransomware virus, PC Cyborg, was recorded back in the day, in 1989, with victims infected via nowadays basically extinct floppy disk. Back then, hackers told victims to send a $189 cheque to an address in Panama[6]. Today, these hacks are far more sophisticated and are spreading rapidly due to technological evolvement. Therefore, cybersecurity and internet awareness should be taken into consideration from personal and business perspectives alike.
Related guides on 2-Spyware
Frequently asked questions
Was Accenture attacked by ransomware?
Yes. LockBit ransomware hit Accenture in the summer of 2021. The company found the intrusion on July 30, 2021, contained it and restored the affected servers from backup.{2}{7} In a later SEC filing Accenture confirmed that the attackers extracted proprietary information.{7}
Did Accenture pay the LockBit ransom?
We found no report that Accenture paid. LockBit demanded $50 million, according to CyberScoop.{7} Accenture said it restored its systems from backup, which meant it did not need a decryption key to recover.{2} The gang still threatened to publish the stolen data.
Was Accenture hacked in 2026?
A hacker claimed so. On July 8, 2026 Cybersecurity Dive reported that someone using the name "888" claimed to have stolen about 35GB of Accenture data, including source code and keys.{8} Accenture called it an isolated matter that it had remediated, with no impact on operations.{8}
What data was stolen in the Accenture breach?
For 2021, Accenture only said proprietary information was taken, without details.{7} For the 2026 claim, the attacker said the data included source code, Microsoft Azure personal access tokens, RSA encryption keys and SSH keys.{8} Neither set of data has been fully described in public.
Who is behind LockBit, the gang that hit Accenture?
The U.S. Justice Department charged Russian national Dmitry Khoroshev in May 2024 as LockBit's developer and administrator.{9} He is accused of running the group from around September 2019. LockBit continued after a 2024 law enforcement disruption and released LockBit 5.0 in September 2025.{10}
Does Accenture Security offer ransomware services?
Accenture sells cybersecurity services to other companies, which made the 2021 attack embarrassing for the firm, as our original report notes. The company said it contained the attack and restored systems from backup.{2} Being a security provider does not make a company immune to ransomware.
Sources
- TheHackerNews. Cybersecurity and hacker news.
- YahooFinance. Financial news, data and commentary.
- ThreatPost. IT and business security news.
- Pbs. Public media news and broadcasts.
- 2spyware. Spyware news, discussions.
- FT. Business and economic affairs.
- CyberScoop
- Cybersecurity Dive
- U.S. Department of Justice
- Wikipedia
Log in to comment
No comments yet. Be the first.