
Zxcvb ransomware: what it is and how to recover your files
Zxcvb ransomware is a Dharma (CrySIS) file encryptor for Windows that renames your files to end in .zxcvb and tells you to e-mail the attackers. No free decryptor is known, so removing it and restoring from backups is the realistic route; paying is not.
Facts checked October 9, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
A free scan checks for the encryptor still on the PC; it does not decrypt .zxcvb files.
Do it yourself · free Remove Zxcvb ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps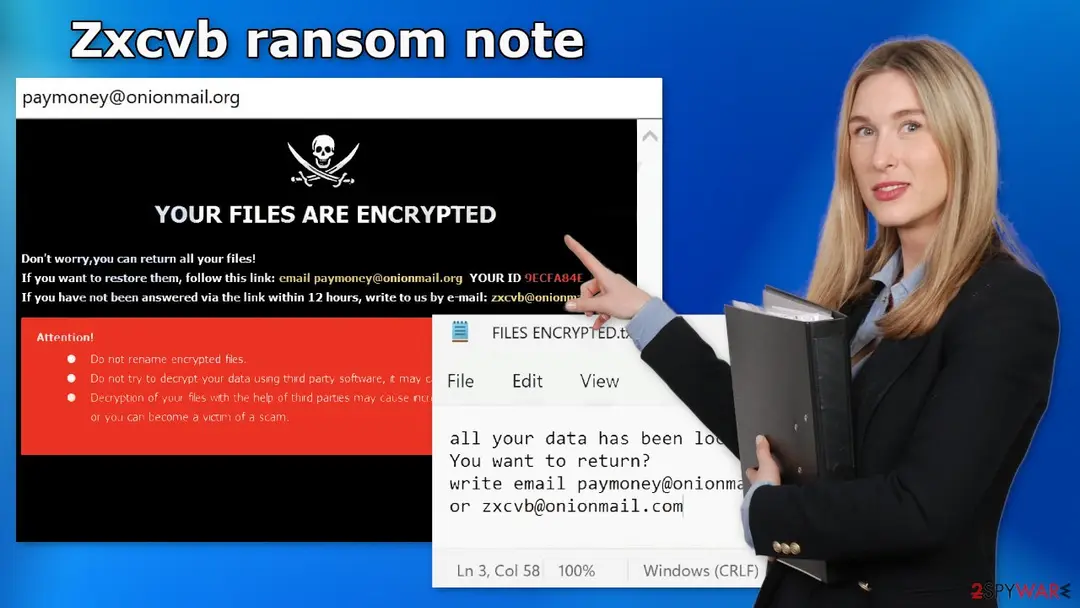
Zxcvb ransomware: summary
| Type | File-encrypting ransomware (Dharma / CrySIS family), Windows only |
|---|---|
| Risk | High: files are encrypted with a key the attackers hold; no free decryptor is known |
| Symptoms | Files renamed name.id-XXXXXXXX.[paymoney@onionmail.org].zxcvb, a black pop-up headed YOUR FILES ARE ENCRYPTED, FILES ENCRYPTED.txt |
| How to get rid of it | Disconnect, scan with Microsoft Defender from Safe Mode and with its offline scan, then restore from backups; see the plan |
| Our check | Source check on 6 October 2026 (PCrisk, Fortinet, Kaspersky, No More Ransom); we did not run the malware |
| First seen | Sample reported 23 August 2022; the Dharma family since at least 2016 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 15 more facts
| Decryptor | None known for .zxcvb; the Dharma entry on No More Ransom does not list this extension |
|---|---|
| Contact | paymoney@onionmail.org and zxcvb@onionmail.com; no wallet is shown |
| Detection names | Microsoft: Ransom:Win32/Wadhrama!hoa; Kaspersky: Trojan-Ransom.Win32.Crusis.to; ESET: Win32/Filecoder.Crysis.P |
| Name | Zxcvb ransomware |
| Evidence | 0 write-ups by security sites; no sample analysed yet |
| Encrypted files | .zxcvb |
| Example | 1.jpg.id-9ECFA84E.[paymoney@onionmail.org].zxcvb |
| Ransom note | FILES ENCRYPTED.txt |
| Attacker contacts | paymoney@onionmail.org and zxcvb@onionmail.com |
| Free decryptor | No free decryptor is known (checked 6 October 2026) |
| Microsoft Defender name | Ransom:Win32/Wadhrama!hoa |
| Distribution | Typically cracked programs, keygens and game cheats, fake installers, e-mail attachments, and Remote Desktop with weak passwords in small offices |
| Damage | Files on the PC and connected drives encrypted, restore points often deleted, sometimes a password stealer installed as well |
| Encrypted file extension | .zxcvb |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against PCrisk, Fortinet's analysis of Dharma variants, Kaspersky's and No More Ransom's decryptor lists and our own 2022 screenshots. We did not run the malware.
What Zxcvb ransomware is
Zxcvb is a Windows file encryptor of the Dharma (CrySIS) family: it scrambles your documents and photos with a key the attackers keep, renames them to end in .zxcvb, and tells you to e-mail one of two addresses.
- Family
- Dharma, also written CrySIS or Crysis (Fortinet, PCrisk)
- Extension
.zxcvb, after the victim ID and the contact e-mail- Notes
- A pop-up window and
FILES ENCRYPTED.txt(PCrisk) - Contacts in the notes
paymoney@onionmail.organdzxcvb@onionmail.com; no wallet or price is shown
How the Zxcvb story went
November 2016
Dharma first appears
Healthcare IT News reported that Dharma, a variant of Crysis, first showed up in the wild in November 2016.
March 2017
Old master keys are published
Master keys of the early Dharma and Crysis releases were posted on BleepingComputer, and Kaspersky, ESET and Avast made decryptors (Healthcare IT News). They cover early releases only.
23 August 2022
Our first report
We described Zxcvb after PCrisk found it on VirusTotal: a 92.50 KB
payload.exe, flagged by 57 of 71 engines.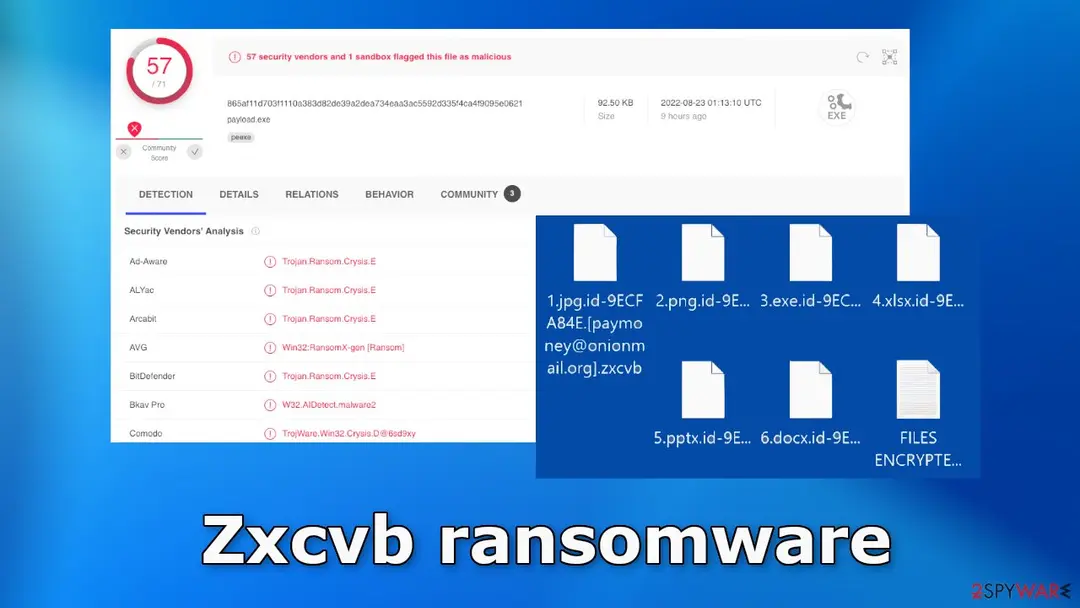
Our 2022 screenshot: the VirusTotal verdict, and six files such as 1.jpg.id-9ECFA84E.[paymoney@onionmail.org].zxcvbshown with blank white icons.
What we checked and what we did not
There is no website here, so there is no site test; this is a source check, and we did not run the malware.
Zxcvb ransomware · source check · 6 October 2026
- DecryptorPCrisk says none exists. The No More Ransom list has a Dharma entry that uses Kaspersky's Rakhni Decryptor, but Kaspersky's page lists
.xtbl,.CrySiS,.wallet,.dhramaand.onion, not.zxcvb. - Behaviour detailsShadow-copy deletion, a Startup copy and the
Info.htapage come from Fortinet's analysis of other Dharma variants. Not confirmed for.zxcvb.
Files probably lost without a backup The encryption is real and the key is held by the attackers. Removing the program stops more damage but does not give files back.
Which name will your scanner show?
Microsoft's name for Zxcvb ransomware is Ransom:Win32/Wadhrama!hoa.
Defender sorts threats by category first, so the word before the colon tells you what kind of program was found, even if the family name means nothing to you.
Do not search for a removal tool by the detection name alone; fake "removal tools" use the same keywords. How the naming works is explained in our guide to antivirus detection names.
- Path:
1.jpg.id-9ECFA84E.[paymoney@onionmail.org].zxcvb - File extension:
.zxcvb - Note file:
FILES ENCRYPTED.txt - Contact:
paymoney@onionmail.org and zxcvb@onionmail.com - Note file:
Pop-up window
Zxcvb meaning, the misspellings zxvcb and bvcxzxcvb, and the zxcvb.cyou address
Zxcvb has no hidden meaning: it is the five letters in a row at the bottom left of a QWERTY keyboard.
People type it as a quick filler, and attackers often pick such keyboard runs as throwaway names. Our reading is that the Dharma operators chose it the same way, as a label for this variant. The name tells you nothing about who is behind it.
The searches zxvcb, zxxxcccvb and bvcxzxcvb are almost certainly the same keyboard run typed by hand, with letters swapped, doubled or reversed. We found no ransomware sold under these spellings. If your files end in one of them, check the exact extension on a renamed file and the contact address in the note. Then compare them with the details in this guide.
The keyboard run also appears in harmless software. Dropbox named its password strength checker zxcvbn, and its own page says it flags keyboard patterns such as qwertyuiop as weak. So a file or folder called zxcvbn on your computer is usually part of a website or app, not this ransomware.
We found no reliable source for zxcvb.cyou. No vendor report we read links that address to Zxcvb ransomware or to the Dharma family. Our reading is that it is an unrelated site that shares the keyboard name. Do not open it to test it; look the address up on a reputation service, and trust only a scan of your own files.
How Zxcvb ransomware behaves
What it does to your files
Each file keeps its own name, then gets the victim ID, the contact e-mail in square brackets and .zxcvb; PCrisk's example is 1.jpg turning into 1.jpg.id-9ECFA84E.[paymoney@onionmail.org].zxcvb.
| Part | Example | What it is |
|---|---|---|
| Original name | 1.jpg | The file as you knew it |
| Victim ID | .id-9ECFA84E | The code you are told to quote when you write to the attackers |
| Contact | .[paymoney@onionmail.org] | The first e-mail address from the notes |
| Extension | .zxcvb | The marker that the file is encrypted |
The icons also turn into blank white pages, so Explorer shows no thumbnails; you can see this in the old screenshot further down. A renamed file is not damaged by the rename. It is unreadable because its content is encrypted.
How it reaches PCs
No source documents the route for this sample.
These are the routes sources give for Dharma in general, listed as possibilities. Our 2022 guide named torrent sites, e-mail and software flaws; the first and the last come up again below.
- High
Exposed Remote Desktop
Fortinet calls exposed Microsoft RDP servers the most famous way in for Dharma operators. Remote Desktop listens on TCP port 3389; with a weak password, an attacker can simply log in and run the file.
- Medium
E-mail attachments
Fortinet notes attachments disguised as installers of legitimate software, including antivirus programs. PCrisk adds malicious macros in Office files.
What to do in the first hour
Disconnect first. If you try to recover files while the program is still running, it can encrypt them again and make the loss permanent.
- 1
Cut the network
Unplug the Ethernet cable or turn off Wi-Fi. At work, tell IT first: shared drives and other computers must be checked too.
- 2
Photograph the pop-up and keep the note file
Take a photo of the screen and keep
FILES ENCRYPTED.txt. The ID in them is the same as in the file names. - 3
Unplug external drives
A connected backup drive can be encrypted too. Do not plug a backup back in until the PC is clean.
The Zxcvb ransomware note
What a ransom note left in folders said
all your data has been locked us
You want to return?
write email paymoney@onionmail.org or zxcvb@onionmail.com
Text of a ransom note left in folders, as people saw it
YOUR FILES ARE ENCRYPTED
Don't worry,you can return all your files!
If you want to restore them, follow this link: email paymoney@onionmail.org YOUR ID -
If you have not been answered via the link within 12 hours, write to us by e-mail: zxcvb@onionmail.com
Attention!
Do not rename encrypted files.
Do not try to decrypt your data using third party software, it may cause permanent data loss.
Decryption of your files with the help of third parties may cause increased price (they add their fee to our) or you can become a victim of a scam.
The two ransom notes
There are two notes: a black pop-up window headed YOUR FILES ARE ENCRYPTED, and a short FILES ENCRYPTED.txt that says the data has been locked. Neither names a price, a deadline or a wallet.
Fortinet's analysis of other Dharma variants adds an Info.hta page and an info.txt; we did not confirm that for this sample.
| Item | What the note says | What it means |
|---|---|---|
| Contact | Write to paymoney@onionmail.org with your ID; if there is no answer within 12 hours, write to zxcvb@onionmail.com | Free, throw-away mailboxes. The attackers set the price by mail, per victim. |
Can Zxcvb ransomware files be decrypted?
Can .zxcvb files be decrypted for free?
Not as far as we can tell. PCrisk says there is no free decryptor, and the old release keys do not cover the .zxcvb label as far as any list we read shows.
- 1
Keep every encrypted file and both notes
Copy them to an external drive. Decryptors sometimes appear later, and the ID in the file names is what a helper would ask for.
- 2
Identify the family
Upload the note and one small encrypted file to ID Ransomware; treat the answer as a hint.
- 3
Check the decryptor lists
Open the No More Ransom tools list and look for Dharma. Kaspersky names the extensions its Rakhni Decryptor handles;
.zxcvbwas not among them on 6 October 2026.
Do
- Test any tool on copies of the files
Don't
- Do not rename or edit the encrypted files
- Do not pay a "decryption service" that is not the attackers
Should you pay the ransom?
No. Ransomware exists to make money, and the only way to your files is the key the criminals hold, but paying does not guarantee you will get it.
The 2022 guide said victims reported never receiving the promised tool; we found no source for how many, so we do not quantify it.
- High
You pay and get nothing, or a broken tool
These notes give no price, so you would be negotiating by e-mail with a stranger.
- High
Cryptocurrency is hard to undo
Attackers ask for it because it offers anonymity. Once it is sent, it cannot be recalled.
How to remove Zxcvb ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Zxcvb ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Zxcvb ransomware encrypts everything it can reach, including drives and shares you connect later. Cut the network first: cable out, or Wi-Fi off from the taskbar.
Then unplug every USB stick and backup disk and pause cloud sync, so the encrypted versions do not replace your online copies. Do not reconnect any of them until the ransomware is removed from the Windows 11 or Windows 10 PC.
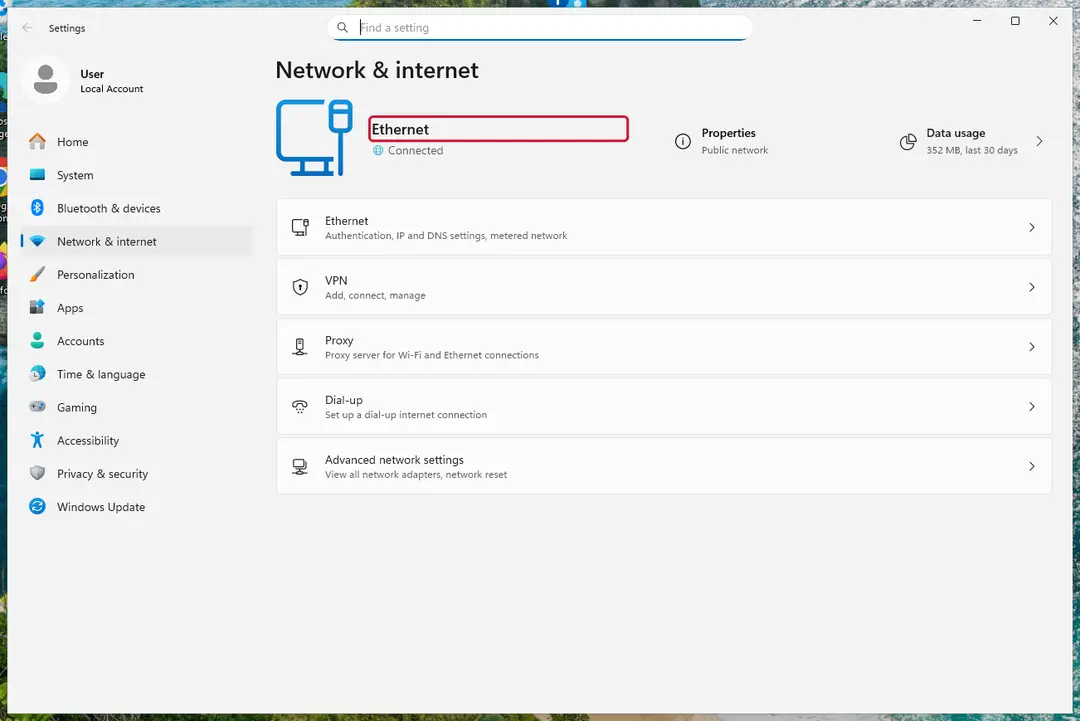
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Copy
FILES ENCRYPTED.txtand one or two files ending in.zxcvbto a USB stick, and leave the originals where they are.From another device, upload the note and a sample file to ID Ransomware or No More Ransom's Crypto Sheriff, which name the family from the note, the extension and the file structure.
Write down the contact address and your personal ID from the note, because a decryptor or the police may ask for them.
Warning: Never contact the attackers from the infected Windows 11 or Windows 10 PC.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
For Zxcvb ransomware, no free decryptor is known (checked 6 October 2026). Search the family name in the No More Ransom decryption tools list and in the free decryptors of Emsisoft, Avast and Kaspersky, because new tools appear years after an attack.
Important: Keep the encrypted files even if nothing works today, and do not pay before every free option is ruled out: payment does not guarantee a working key.
Decryptors run on Windows 11 and Windows 10, but only after the ransomware itself is removed.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Restoring or decrypting files while Zxcvb ransomware still runs lets it encrypt them again. Run a Full scan in Windows Security > Virus & threat protection > Scan options, then the Microsoft Defender Antivirus (offline scan).
If the ransomware blocks Windows Security, start Safe Mode with Networking and scan from there. Some families install a password stealer as well, so let both scans finish on Windows 11 or Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Open Command Prompt as administrator and run
vssadmin list shadows. If it lists copies dated before the attack, right-click a folder with encrypted files in File Explorer, choose Properties > Previous Versions, and open or restore a version from before that date.ShadowExplorer, a free tool, shows the same copies when the tab is empty or hidden. Most current families delete shadow copies, so an empty list is normal, but the check takes two minutes on Windows 11 or Windows 10.
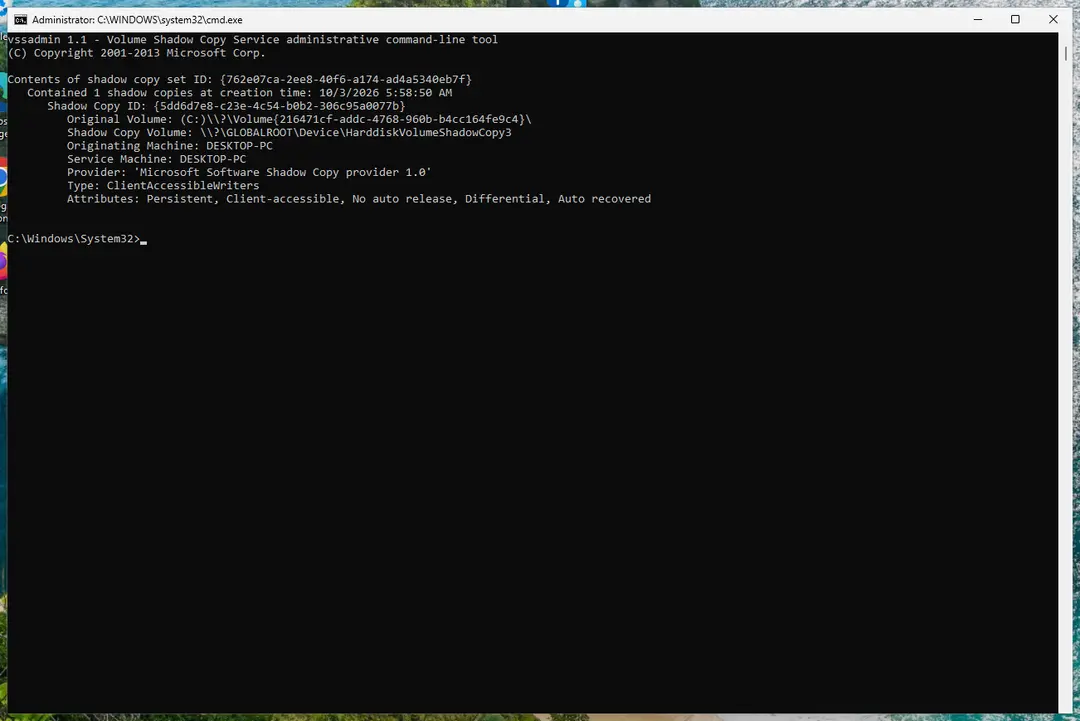
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
Restore from an external backup, File History or OneDrive's version history, choosing a date before the attack. Connect the backup drive only after the scans are clean, or the ransomware encrypts it too.
If there is no backup, file recovery software can sometimes find the deleted originals, because some ransomware writes an encrypted copy and deletes the original file.
Stop writing to the drive and try recovery on Windows 11 or Windows 10 before new files overwrite the space.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Ways to get files back without the attackers
Before you start: copy the encrypted files to a USB drive or another disk first, because security or recovery tools can damage them further.
Do the recovery only after the malware has been removed.
- 1
Your own backups
A copy on an external drive, a NAS or cloud storage is the most reliable source. Connect it only after the PC is clean.
- 2
Cloud version history
OneDrive, Dropbox and Google Drive keep earlier versions. OneDrive can roll an account back up to 30 days (PCrisk).
- 3
Previous Versions and shadow copies
Right-click a folder, choose Properties > Previous Versions. Run
vssadmin list shadowsas administrator to see what exists. Fortinet reports that Dharma variants delete shadow copies, so expect an empty list; we did not confirm it for Zxcvb. - 4
A deleted-file recovery program
Install it on a different disk and run a deep scan of the drive. It finds only copies the disk still holds; PCrisk puts success at roughly 5 to 20 percent in some cases.
Back up with the 3-2-1 rule
The 2022 guide pointed out that recovery is almost impossible without backups.
The 3-2-1 rule, which CISA's guidance recommends, makes the habit concrete.
| Number | Rule | Example |
|---|---|---|
| 3 | Three copies of every important file | The working file plus two backups |
| 2 | Two different kinds of storage | Your disk and a USB drive |
| 1 | One copy away from the PC | An unplugged drive in a drawer, or cloud storage with version history |
How to prevent Zxcvb ransomware and the next attack
Five habits cover the routes that Dharma and most other ransomware use.
Do
- Keep Windows and your programs updated, since attackers use software flaws
- Install programs only from official stores and developer sites, and read reviews and ratings first
- Close Remote Desktop (TCP port 3389) to the internet, or put it behind a VPN with a strong password and two-step sign-in
Don't
- Do not download cracks or files from torrent and peer-to-peer sites
Questions about Zxcvb ransomware
What is the .zxcvb file extension?
It is the ending that Zxcvb ransomware adds to files it has encrypted. The full name looks like 1.jpg.id-9ECFA84E.[paymoney@onionmail.org].zxcvb:
- the original name
- a victim ID
- the contact e-mail in brackets
.zxcvb
PCrisk files it under the Dharma (CrySIS) family. A file with this ending is not a document in a strange format.
Its content is encrypted, so no program can open it until it is decrypted or replaced from a backup. Keep copies of the files exactly as they are before you try anything on them.
Is there a decryptor for Zxcvb ransomware?
None is known for .zxcvb. PCrisk lists no free decryptor. The No More Ransom list has a Dharma entry that uses Kaspersky's Rakhni Decryptor, but Kaspersky's page names the extensions it supports, such as .xtbl, .CrySiS, .wallet, .dhrama and .onion, and .zxcvb is not among them when we read it on 6 October 2026.
The 2017 master keys unlocked early Dharma releases only. Keep copies of your encrypted files and check the lists again later, because tools sometimes appear years after an attack.
Do paid decryption services work for .zxcvb files?
Be careful:
- PCrisk says only the attackers can decrypt the files unless the ransomware has flaws
- so a third party that offers to decrypt for money is either a scammer
- a middleman who passes your payment on
The pop-up note itself warns that outside help raises the price, which is a way of keeping you from other options. A free tool from the lists on No More Ransom, tested on a copy, costs nothing. Anyone who promises a guaranteed result for a fee should be treated with suspicion.
Was my data stolen by Zxcvb ransomware?
We found no source that says so. The notes only ask you to write by e-mail, and no leak site is known for Zxcvb. PCrisk does warn that password-stealing trojans and other malware can arrive together with ransomware, so treat saved passwords as exposed and change them from a clean device after the cleanup.
If the way in was Remote Desktop, someone logged in as a user, so assume they could see what that account could see. Check your online accounts for new sign-ins and turn on two-step verification wherever you can.
Is Zxcvb the same as other Dharma ransomware or other .zxcvb-like names?
Zxcvb is one label of the Dharma (CrySIS) family, which has existed since at least 2016. Kaspersky calls the sample Trojan-Ransom.Win32.Crusis.to and Microsoft calls it Ransom:Win32/Wadhrama!hoa. Fortinet says a leaked version lets many operators publish variants with their own extensions and e-mail addresses, so .wallet, .dharma and .onion files look alike.
Do not assume a tool for one label works for another. It is also not STOP/Djvu, which has a different ID format and different tools, and the name is not the keyboard row it resembles.
How do I remove Zxcvb ransomware?
Disconnect from the network, then scan with Microsoft Defender from Safe Mode with Networking, and run its offline scan from Windows Security, followed by a full scan. Removal stops the program from encrypting more files, but it does not bring encrypted files back.
Do not restore from a backup before the PC is clean, because anything you restore can be encrypted again. If your antivirus will not start, Safe Mode is the usual way around it. Change your passwords afterwards from a clean device.
How did Zxcvb get on my computer?
No source documents the route for this sample. For Dharma in general, Fortinet names exposed Remote Desktop servers as the most famous way in, and also phishing with attachments disguised as installers of legitimate software.
PCrisk lists mail attachments, torrent sites, fake updaters and malicious ads for ransomware generally. Think back to what you installed or opened before the files changed, and if Remote Desktop is open on your router or PC, close it.
Should I pay the Zxcvb ransom?
No. Nothing guarantees the attackers will send a working decryptor after you pay, and agencies such as CISA and the FBI advise against paying. The notes name no price or wallet, so you would be negotiating with a stranger by e-mail and sending cryptocurrency that cannot be recalled.
A payment may also break sanctions rules, according to a US Treasury advisory summarised by Fortinet. A better use of the time is to remove the program, protect your accounts and look for backups.
How do I open .zxcvb files, and will Previous Versions bring them back?
You cannot open .zxcvb files, because their content is encrypted; renaming them does not help. Previous Versions only helps if copies survived.
Fortinet reports that Dharma variants delete the Windows shadow copies, which are the source of Previous Versions, so the list is often empty. We did not confirm this for Zxcvb. Run vssadmin list shadows in an administrator Command Prompt to see what exists.
Cloud version history on OneDrive, Dropbox or Google Drive and a backup drive that was unplugged during the attack are far more likely to help. Look at them before anything else.
Will Fortect remove Zxcvb ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Zxcvb ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- PCrisk: Zxcvb ransomware (read October 6, 2026)
- Fortinet: Ransomware Roundup, CrySIS/Dharma variants (read October 6, 2026)
- Healthcare IT News: Kaspersky, ESET, Avast release Dharma ransomware decryptors (read October 6, 2026)
- Kaspersky: RakhniDecryptor (read October 6, 2026)
- No More Ransom: decryption tools (read October 6, 2026)
- Microsoft Support: Virus and threat protection in Windows Security (read October 6, 2026)
- CISA: StopRansomware (read October 6, 2026)
- Dropbox on GitHub: zxcvbn password strength estimator (read October 9, 2026)