
Viruses · 307 guides

Trojans removal guides, page 6 of 12

Hidden programs that give attackers remote access, and how to find and remove them.
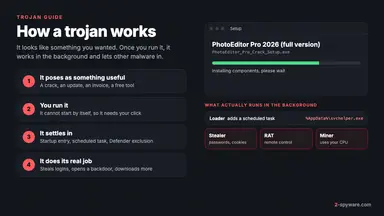
Start hereWhat is a trojan and how to remove itA trojan is malware disguised as something you wanted, such as a cracked program, a fake update or an invoice. It does nothing until you run it, then steals passwords, gives a stranger remote access or downloads more malware. To remove it, cut the startup entries it added, run a full and an offline scan, then change your passwords from a clean device.

Most searched trojans guides

  1. 1Remove Csrss.exe trojan
  2. 2Remove Memz virus
  3. 3Remove Wcupdater
  4. 4Remove Win32/Lodi
  5. 5Remove Chrome.7z
  6. 6Remove Iplogger.org

Trojans removal guides 136–162 of 307

Remove Csrss.exe trojan

Csrss.exe trojan is a file masking infection that is responsible for damaging the machine and stealing information Csrss.exe Trojan is a type of malware designed to perform numerous malicious activities onTrojansHigh riskJake Doevan ·

Remove Orcus RAT

Orcus RAT is a widely spread computer virus that spies on its victims and steals their banking credentials or Bitcoin wallets  Orcus RAT is a threat distributed via highly sophisticatedTrojansHigh riskOlivia Morelli ·

Remove Chrome.7z

Chrome.7z - a trojan horse that can infect your PC with additional malware Chrome.7z is a type of malware infection that enters computers via malicious websites or is installed whenTrojansHigh riskGabriel E. Hall ·

Remove GetX64BTIT.exe

GetX64BTIT.exe is an executable file that might indicate a Trojan infection GetX64BTIT.exe is a file that arrives on the system without users' knowledge. Since it is categorized as a Trojan,TrojansHigh riskUgnius Kiguolis ·

Remove Hadsruda!bit

Hadsruda!bit is a trojan that infiltrates your computer and tries to expose users to malicious websites Hadsruda!bit virus is a dangerous computer infection related to spyware and malware. We identify thisTrojansHigh riskAlice Woods ·

Remove TrojanDropper:MSIL/Perseus!rfn

TrojanDropper:MSIL/Perseus!rfn is the threat indication that alerts about a trojan infection TrojanDropper:MSIL/Perseus!rfn is the heuristic detection name that should be taken seriously because trojans are one of the more dangerousTrojansHigh riskJake Doevan ·

Remove Win32:KadrBot

Win32:KadrBot - a Trojan that negatively impacts your online security Win32:KadrBot is a detection name for a potentially malicious file or program that can be found while browsing the webTrojansHigh riskJulie Splinters ·

Remove TrojanDownloader:HTML/Adodb.gen!A

TrojanDownloader:HTML/Adodb.gen!A - malware that typically resides in Discord cache folder TrojanDownloader:HTML/Adodb.gen!A is a detection name that you can encounter at any time when your computer is running. This type of malwareTrojansHigh riskJake Doevan ·

Remove TrojanDropper:Win64/Tnega!MSR

TrojanDropper:Win64/Tnega!MSR is the Trojan name that shows up in the detection alerts TrojanDropper:Win64/Tnega!MSR is the indication of a possible threat to the system. The trojan name can appear in WindowsTrojansHigh riskJulie Splinters ·

Remove Kryptik Trojan

Kryptik Trojan is a dangerous malware that can steal your sensitive data and severely damage your computer Win32:Kryptik is a trojan that typically enters users machines via infected installers andTrojansHigh riskLucia Danes ·

Remove Trojan.LockScreen

Trojan.LockScreen - ransomware that locks all data on the system with AES encryption algorithm Trojan.LockScreen is an especially dangerous cyber threat that belongs to the trojan and ransomware categories. ItsRansomwareHigh riskJake Doevan ·

Remove Dyreza virus

Dyreza - a banker Trojan that can steal your passwords and other data Dyreza virus is a dangerous Trojan horse that is used for stealing valuable information from PC users.TrojansHigh riskLucia Danes ·

Remove Zbot

Zbot - one of the most impactful Trojans to date Zbot is a dangerous trojan horse that mainly focuses on information-stealing - whether it is regular computer users or financialTrojansHigh riskUgnius Kiguolis ·

Remove Dyre Trojan

Dyre trojan is a banking malware that is mostly known for stealing one's financial information or even money Dyre virus is a dangerous trojan horse, which in other sources canTrojansHigh riskUgnius Kiguolis ·

Remove Beast

Beast - a malicious tool that can give access to your computer to cybercriminals Beast is just another virus that belongs to a broad family of Remote Administration Tools (ifTrojansHigh riskGabriel E. Hall ·

Remove Andromeda Trojan

Andromeda is an evasive malware downloader that is capable of stealing information from the infected users Andromeda virus is a family of Trojans that was first introduced in 2011 andTrojansHigh riskJake Doevan ·

Remove VBS:Malware-gen

VBS:Malware-gen is a virus that is capable of modifying targeted system settings for malicious purposes VBS:Malware-gen is a generic name used for various trojan horses. The threat can range fromTrojansHigh riskGabriel E. Hall ·

Remove Absunset

Absunset is the infection that is indicated by poor performance and speed or CPU usage problems related to executable file Absunset is a Trojan horse[ref en-2] that enters the computerTrojansHigh riskJake Doevan ·

Remove Brocoiner

Brocoiner is the malware piece that relies on resources of the affected PC to run crypto Brocoiner is a trojan infection which secretly uses the PC's resources to mine cryptocurrenciesTrojansHigh riskLucia Danes ·

Remove Commondatastorage Googleapis virus

Googleapis virus is a set of trojans that is being spread using legitimate Google service Googleapis virus is a scheme used by cybercriminals to spread trojans[ref en-1] and adware. Initially, GoogleTrojansHigh riskLucia Danes ·

Remove Back Orifice

Back Orifice - remote administration software created by a member of Cult of the Dead Cow hacking organization Back Orifice, later known as BackOrifice2K, is a remote administration application thatTrojansHigh riskGabriel E. Hall ·

Remove Gootkit Banking trojan

Gootkit is the malware also known as a banking trojan that aims to steal sensitive credentials Gootkit Banking trojan is the malware that was discovered back in 2014 and canTrojansHigh riskUgnius Kiguolis ·

Remove Trojan:Win32/CryptInject!ml

Trojan:Win32/CryptInject!ml is the malware that can act in the background and damage the machine significantly Trojan:Win32/CryptInject!ml is the malware detection name that can indicate a threat running in the background.TrojansHigh riskJake Doevan ·

Remove Memz virus

Memz virus is the custom-made trojan that overwrites Windows boot sequence with Nyan Cat meme animation   Memz virus is the trojan originally created by Leurak as viewer-made malware forTrojansHigh riskLucia Danes ·

Remove Trojan.Multi.GenAutorunReg.a

Trojan.Multi.GenAutorunReg.a is the trojan that mainly spreads in Russia and aims to steal data Trojan.Multi.GenAutorunReg.a is a variant of a trojan horse that aims to access sensitive information and controlTrojansHigh riskAlice Woods ·

Remove Trojan.Win32.Bazon.a

Trojan.Win32.Bazon.a is the detection name indicating that the machine has an intruder running in the background Trojan.Win32.Bazon.a - a malicious program that can be set to affect an infected machineTrojansHigh riskJulie Splinters ·

Remove Trojan.MalPack

Trojan.MalPack is the detection name indicating a threat that is capable of infecting the machine further or affecting the system directly Trojan.MalPack - malware packer that spreads various threats, dependingTrojansHigh riskJake Doevan ·
5,558 members already hereReading, writing, commenting and voting. 0 verified · 283 joined this year