
Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn: what it is and how to remove it
Js/Adrozek.A virus is a relatively old detection name used by Windows Defender to identify suspicious activity on various web browsers. In most cases, such potentially unwanted programs are distributed via deceptive methods such as software bundling or fake update prompts - this usually results in unintentional installation.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
After Defender reports BrowserModifier:JS/Adrozek.A., an automatic scan can look for related files it may have missed.
Do it yourself · free Remove Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn yourself 5 steps, about 15 minutes, no software needed.
Start the steps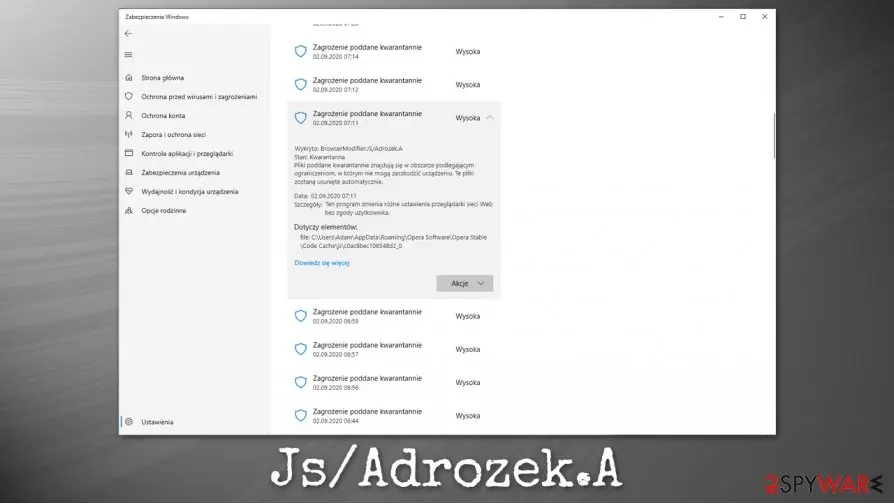
Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn: summary
| Damage | Installation of other potentially unwanted programs or malware, data theft, monetary losses |
|---|---|
| Name | Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn |
| Type | Browser hijacker, potentially unwanted program |
| Related browsers | Google Chrome, MS Edge, Yandex, and Mozilla Firefox |
| Executables dropped | Audiolava.exe, QuickAudio.exe, and converter.exe are placed into the Program Files folder of the main drive |
| Symptoms | Symptoms may vary, but common ones include changed homepage URL, modified search engine, |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 13 January 2021 |
| Microsoft Defender name | BrowserModifier:JS/Adrozek.A. |
| Facts checked | 7 October 2026 |
Is Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn dangerous? What it collects
From our report of Jan 2021 · not reviewed since
Js/Adrozek.A is based on "expansive, dynamic attacker infrastructure"
Browser hijackers are among the oldest threats on the internet and while they became much less of a headache for users over the years due to the implemented regulations and security measures, threats like Adrozek remain very harmful for everyone who are affected.
Since May 2020, security researchers from Microsoft have been observing the newest campaign that mainly targeted European and Indian internet users. The peak of infections was reached in August of the same year, when the tech giant saw more than 30,000 attempts to infect users on a daily basis.
Security experts wrote:
While the main goal of the attackers is to make users click on ads inserted at the top of the search results, there are far more dangerous traits of Js/Adrozek.A. Primarily, it was uncovered that, if installed, the virus can be very persistent and difficult to eliminate (due to its polymorphic aspect), and it can also compromise the host machine's security even further by stealing credentials entered on various websites.
Another disturbing feature of this campaign is that the attackers heavily rely on polymorphism during its distribution, which is performed via the drive-by download technique. Due to the ever-changing payload, many security solutions might fail to detect Adrozek, hence the infiltration rate is quite high.
Once installed, the malware drops several malicious files (Audiolava.exe, QuickAudio.exe, and converter.exe) into the Program Files folder. It then modifies the Windows registry to establish persistence and prevent all the affected browsers from being updated. It also creates a new service titled "Main Service" to prevent modification of the newly-established settings.
To mitigate Js/Adrozek.A and prevent its infiltration, ensure that your security software is running with the latest updates applied and also secure your operating system, as well as the installed software from vulnerabilities by patching them with the latest security updates.
From our report of Jan 2021 · not reviewed since
Do not ignore anti-malware software warnings
Security software is one of the essential components of any modern computer - industry experts advise keeping a robust anti-malware running at all times.
Unfortunately, there are plenty of people who ignore this advice and believe that they are smarter than malware - this couldn't be further from the truth, as modern computer threats are programmed in a way to operate without any trace whatsoever.
Additionally, many users visit high-risk torrent sites and download pirated programs or software cracks, which are almost always detected by anti-malware. Delete such files straight away, as cracks/keygens are the main distribution method for devastating infections such as Geno ransomware, which would encrypt all the files on your system and then demand ransom for their return.
Thus, if you are downloading new software, browsing the web, or are facing with a suspicious ad asking you to download an unknown program, always pay attention to your security software, as definitions are updated regularly, and there are plenty of invisible threats around that you would never notice without it.
From our report of Jan 2021 · not reviewed since
Handle Js/Adrozek.A virus detection correctly
False positives can be pretty hard to understand for regular computer consumers, and they can often be very damaging overall.
This is why independent testing labs always take into account a number of false-positives when ranking anti-malware software. While Windows Defender has been doing much better in this regard from a few years ago, false detections are still possible. So, you should not rush Js/Adrozek.A virus removal immediately.
To determine whether it is indeed a false positive, you should keep in mind several factors, for example, what were you doing during the time of the pop-up; if you were about to download software crack, you for sure remove Js/Adrozek.A without thinking twice.
However, if the detection is repeated at certain time periods and occurs when you are performing regular activities (for example, watching YouTube videos) or accessing a legitimate program (Opera), you should consider putting it as an exclusion via the security software settings.
From our report of Jan 2021 · not reviewed since
More from our earlier report on Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn
- Such a sustained, far-reaching campaign requires an expansive, dynamic attacker infrastructure.
- We tracked 159 unique domains, each hosting an average of 17,300 unique URLs, which in turn host more than 15,300 unique, polymorphic malware samples on average.
How Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn got into your browser
From our report of Jan 2021 · not reviewed since
Js/Adrozek.A virus is a relatively old detection name used by Windows Defender to identify suspicious activity on various web browsers.
In most cases, such potentially unwanted programs are distributed via deceptive methods such as software bundling or fake update prompts - this usually results in unintentional installation. However, this threat is related to JavaScript malware, which typically infiltrates machines automatically. If anti-malware software is installed, it will block the threat and flag it as Js/Adrozek.A or BrowserModifier:JS/Adrozek.A.
While the heuristic detection Js/Adrozek.A is not new, there have been multiple reports about its increased activity. Security researchers from Microsoft have been investigating the campaign by cybercriminals - it was revealed that malware affects various browsers such as Google Chrome, MS Edge, Yandex, and Mozilla Firefox.
If the targeted machine is not protected, users could be subjected to extensive advertisements that would be shown at the top of regular search results. Ads are generated based on keywords that victims type into their searches, and each of such clicks would profit cybercriminals through affiliate advertising programs.
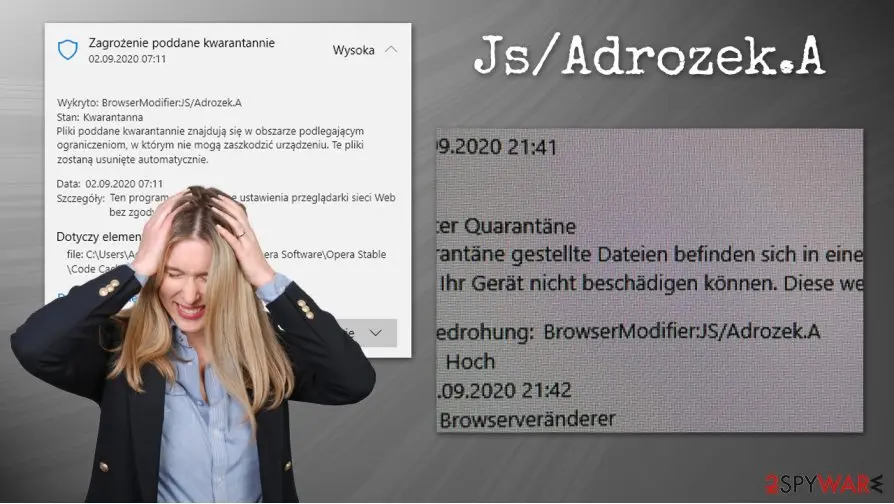
Another case could be attributed to security software flagging a false-positive. Users from Germany, Poland, and other countries reported that the popups were frequent as soon as the Opera web browser was used. Even though the detection should be investigated, it is highly likely that Adrozek popups are caused by an update of either Microsoft Defender definitions or the Opera web browser.
While Js/Adrozek.A virus is commonly used for describing browser hijacking actions; the detection name also indicates that the infection is related to JS, otherwise known as JavaScript. JavaScript is a programming language that is widely used on various web pages to make them interactive.
Nonetheless, the JavaScript is also commonly used to launch malicious attacks, which could result in malware infiltration, and, under certain circumstances, can occur without any user interaction whatsoever. To mitigate such attacks, it is important to ensure that all the software is updated, including the operating system, as the drive-by download would fail if no software vulnerabilities are found during it.
If the detection is not a false-positive, it is much more dangerous than a regular browser hijacker due to this, as it can establish persistence mechanisms, change the Windows registry, and perform other actions that would prevent an easy Js/Adrozek.A removal. If your anti-virus software is incapable of deleting the found threat, we highly advise you to try using an alternative solution, such as or .
Nonetheless, it is also important to note that Js/Adrozek.A virus detection can also be a false positive. These instances are relatively common (other common heuristic detections suffering from the same problem include Win32/Lodi, Js/Adware.Agent.AW, HTML:RedirME-inf, and many others) and often happen with when a particular program, in this instance, Opera, gets updated, and security application flags it mistakenly.
One of the main reasons why Js/Adrozek.A might be a false positive is when many users report the same activity on the same platform. Despite this, each of the heuristic detections should be carefully investigated to ensure that it is not indeed a false positive. For that, perform the following steps:
In case repeated scans with other anti-malware show that the detection is indeed a false positive, you should add the location/file to the exclusions list.
- Update security software and the related program, e.g., Opera
- Remove Js/Adrozek.A virus if other security programs detect it as well.
Check your browser and PC
Microsoft Defender reports Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn as BrowserModifier:JS/Adrozek.A..
In a Defender name, the part before the colon is the category, the part after it is the platform, and the part after the slash is the family Microsoft assigned. A suffix after ! is an internal Microsoft marker, not a different threat.
Generic labels such as Agent, GenericKD or Malware.AI only say that a file looks malicious, not what it does; our guide to antivirus detection names shows how to read them.
How to remove Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn
Remove the extension first.
The search settings only stay fixed once nothing on the PC can change them again.
Step 1: Remove extensions you did not add
In Chrome open
chrome://extensions, in Edgeedge://extensions, and in Firefox the menu > Extensions and themes.Remove every extension you do not remember adding, especially search, new tab, coupon, PDF, weather or video downloader add-ons. Check every browser and every profile, because each keeps its own list.
If an extension has no Remove button or comes back, a browser policy holds it (see "Managed by your organization" in the procedure below). The pages are the same on Windows 11 and Windows 10.
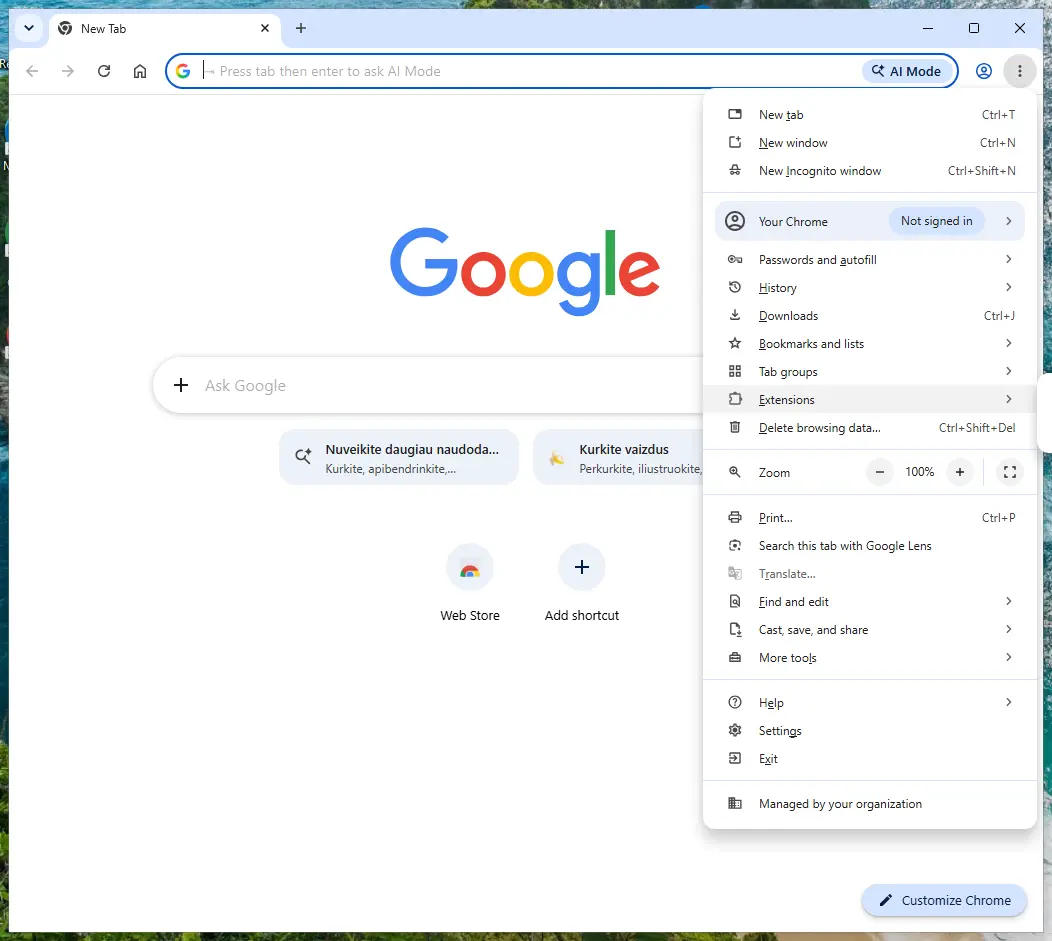
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Put the search engine back
In Chrome open Settings > Search engine > Manage search engines and site search, make an engine you trust the default, and delete entries you did not add.
In Edge type
search engineinto the search box at the top of Settings and open Manage search engines; in Firefox use Settings > Search. Then check the homepage and the new tab page in the same settings, because hijackers change all three.If the wrong engine is back after a restart, an extension, a program or a policy still sets it, so finish the other steps and check again. The settings are the same on Windows 11 and Windows 10.
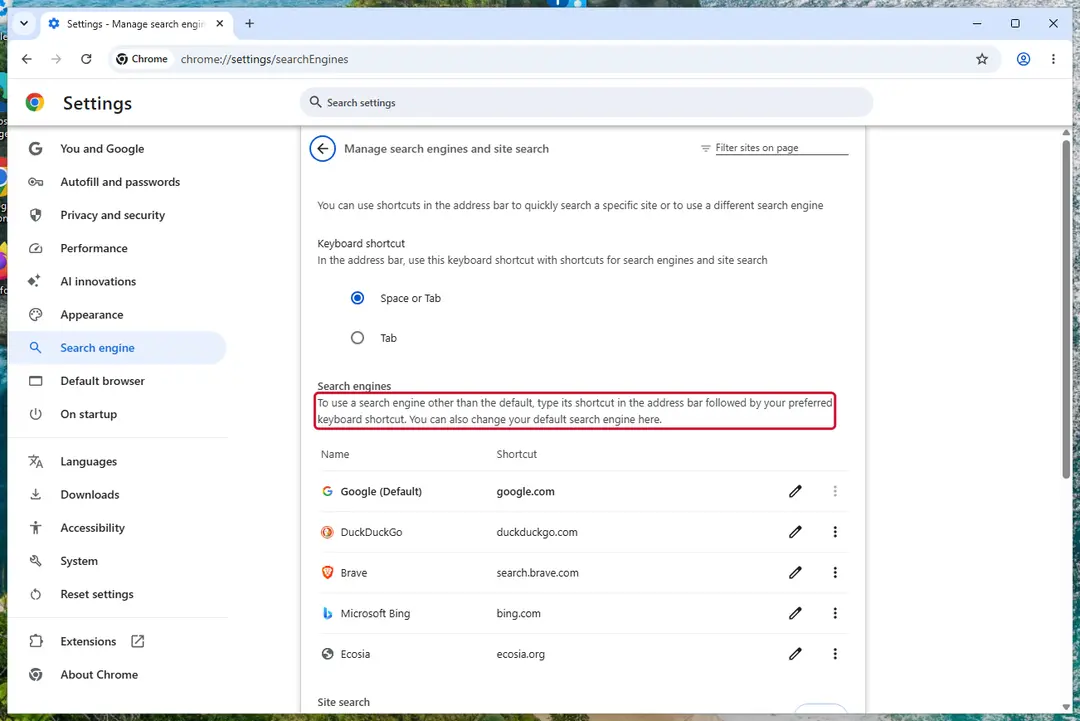
Chrome on Windows 11: check Search engine and On startup. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Uninstall programs you did not mean to install
Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn rarely comes alone: it is usually installed by, or together with, a free program. In Windows 11 open Settings > Apps > Installed apps, in Windows 10 Settings > Apps > Apps & features, and sort by install date.
Uninstall every entry from the day the trouble began that you did not install on purpose, for example a download manager, a converter or a browser you never chose.
Keep drivers and entries from Microsoft, Intel, AMD, NVIDIA or your PC's maker unless you are sure.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 4: Reset the browser
A reset removes what the steps above could miss:
- changed start pages
- site permissions
- hidden settings
In Chrome open Settings > Reset settings > Restore settings to their original defaults; in Edge Settings > Reset settings; in Firefox Help > More troubleshooting information > Refresh Firefox.
Tip: Bookmarks and saved passwords stay, while extensions are turned off and the search engine and start page return to the defaults.
Reset every browser on the PC, including Edge, which Windows 11 and Windows 10 always have.
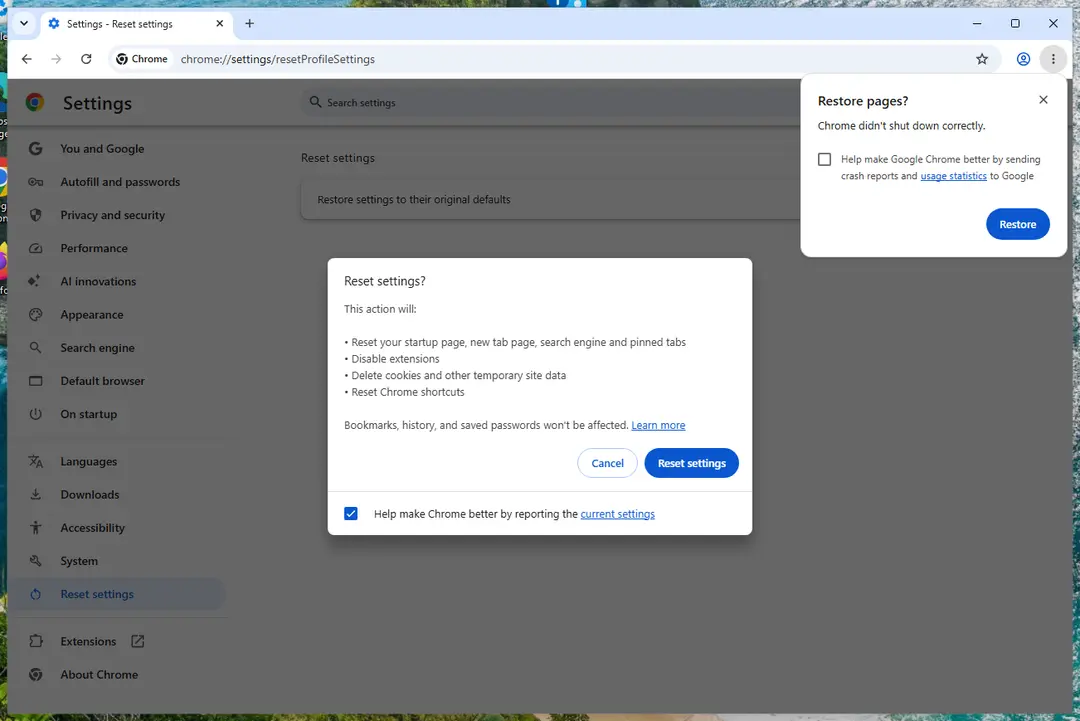
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
To uninstall potentially unwanted programs from Windows, follow these steps:
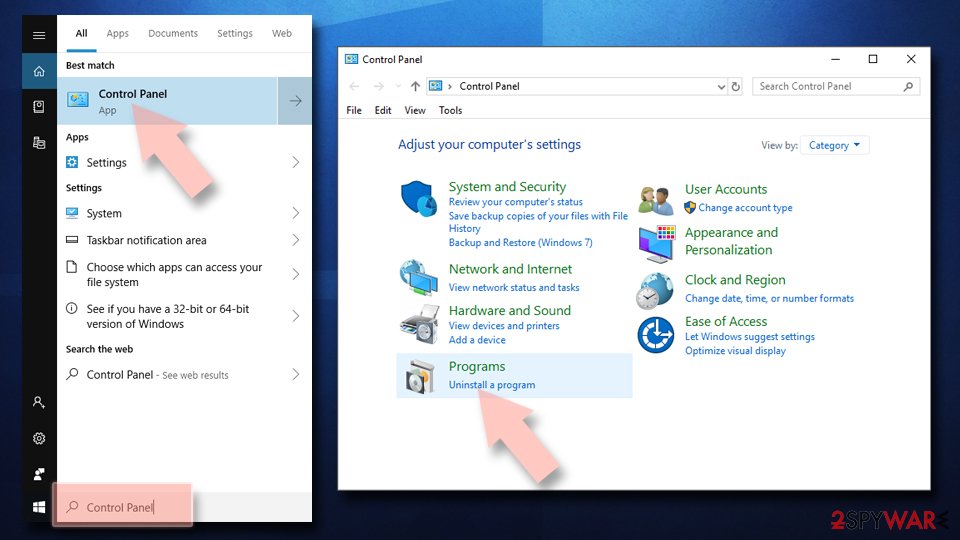
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
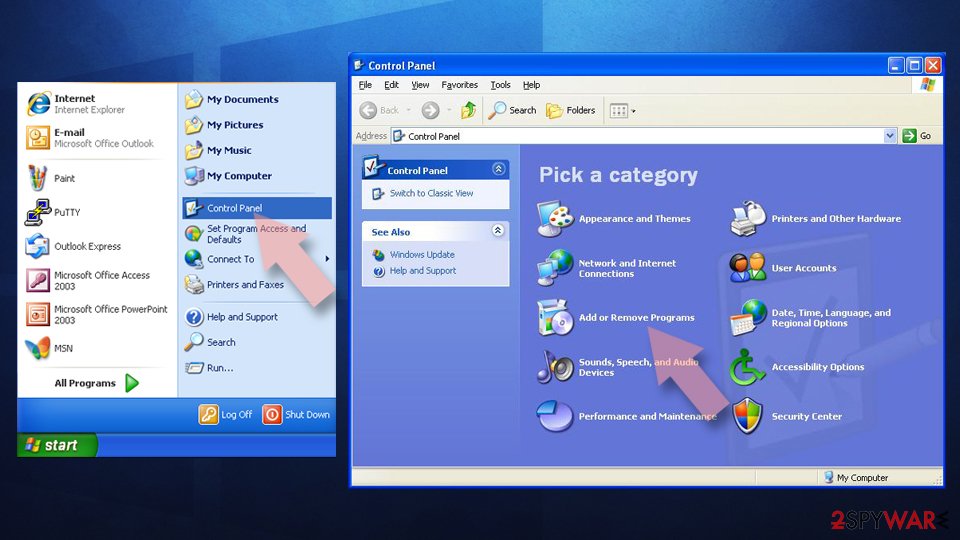
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
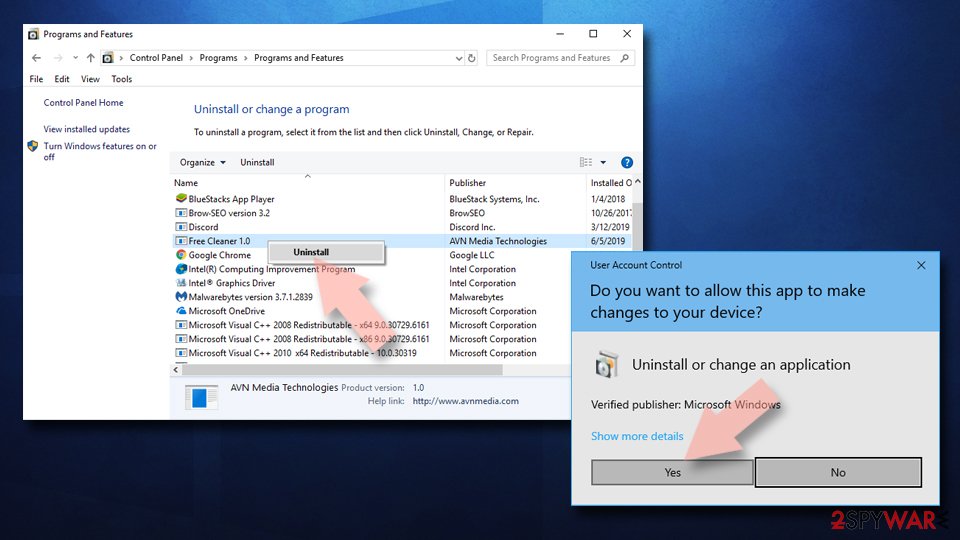
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
If you are unable to eliminate suspicious browser activity, you should reset Google Chrome:
Delete malicious extensions from Google Chrome:
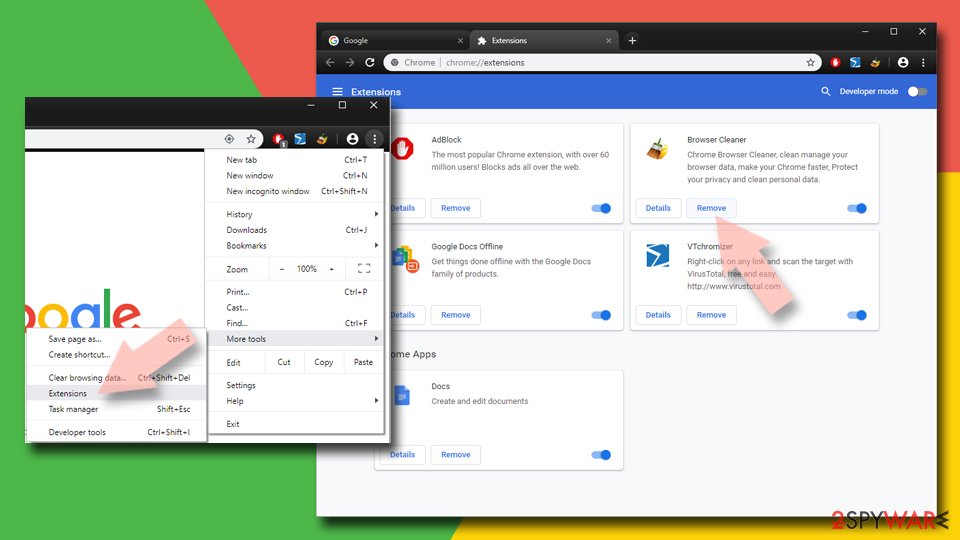
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
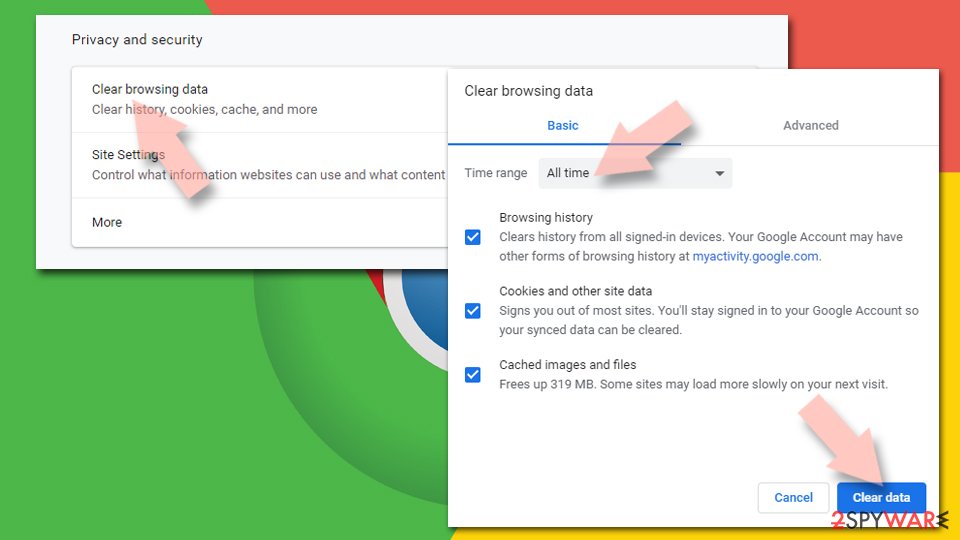
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
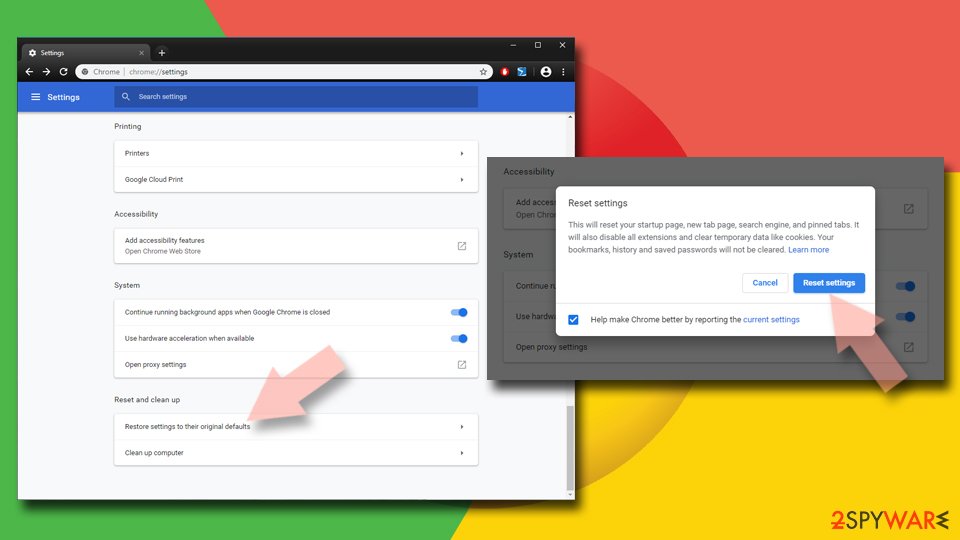
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
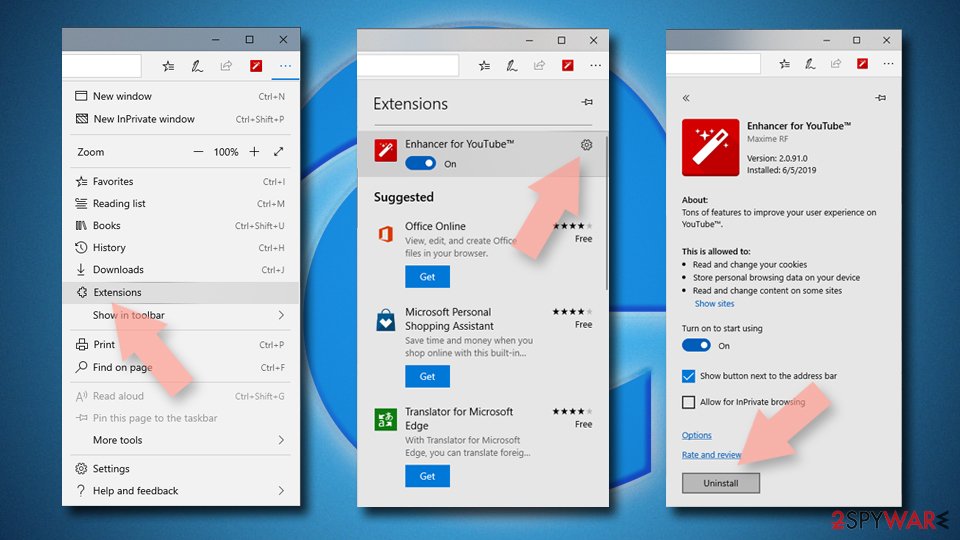
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
Clear cookies and other browser data:
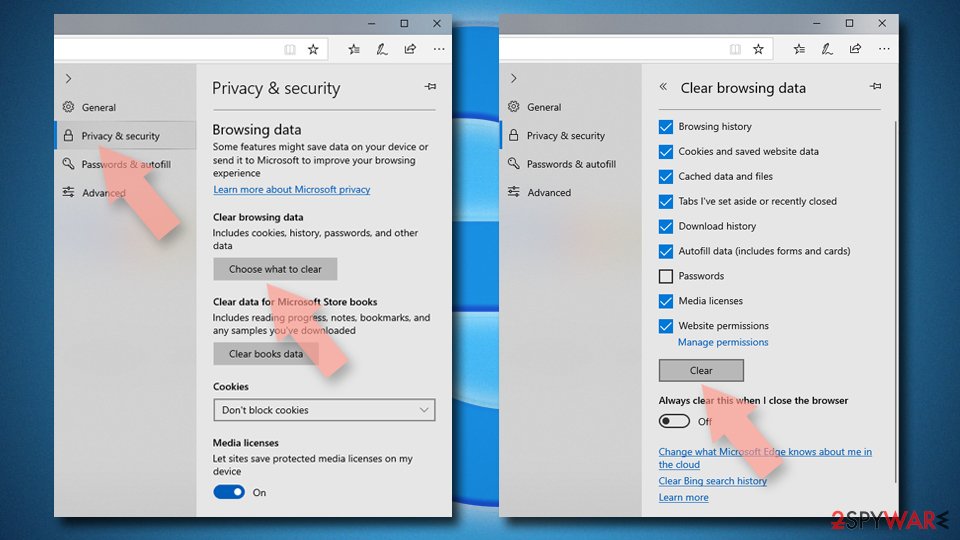
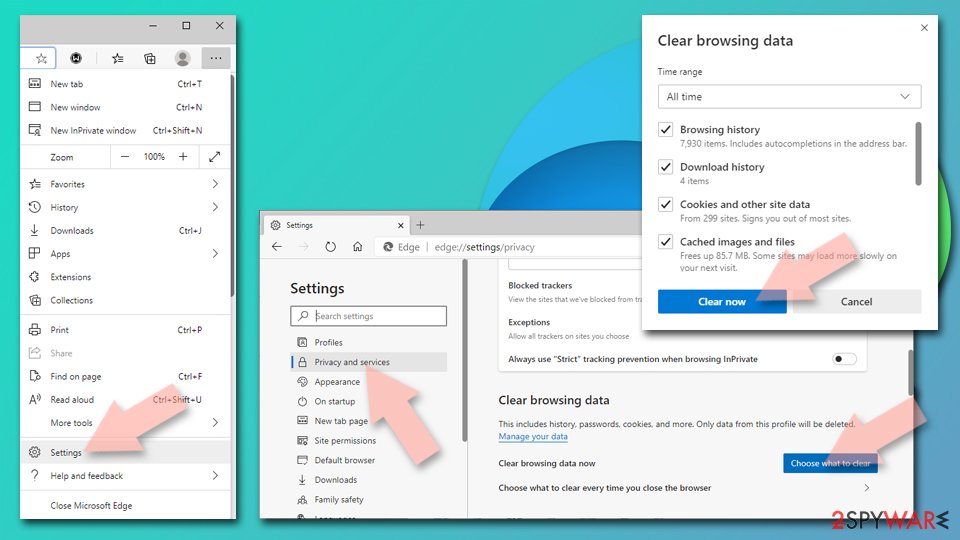
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
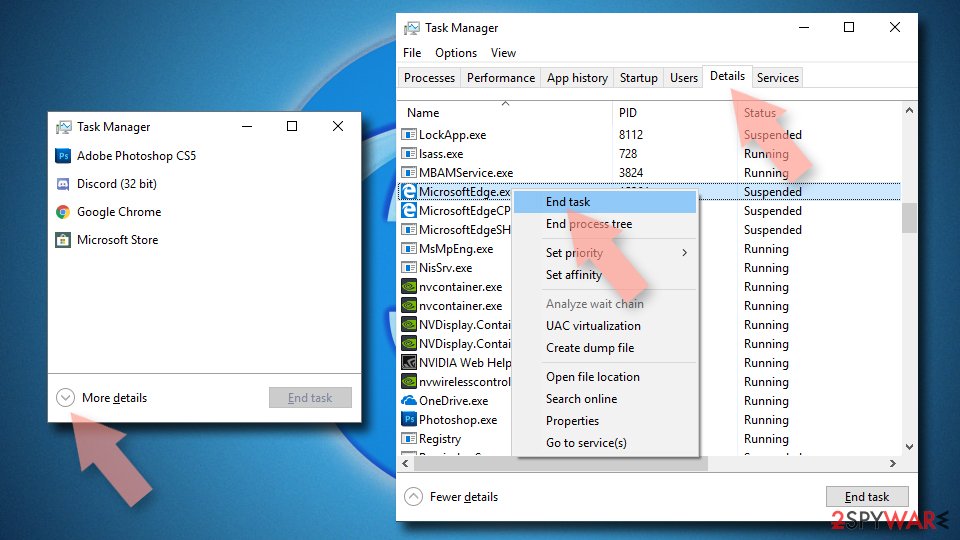
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
Delete extensions from MS Edge (Chromium):
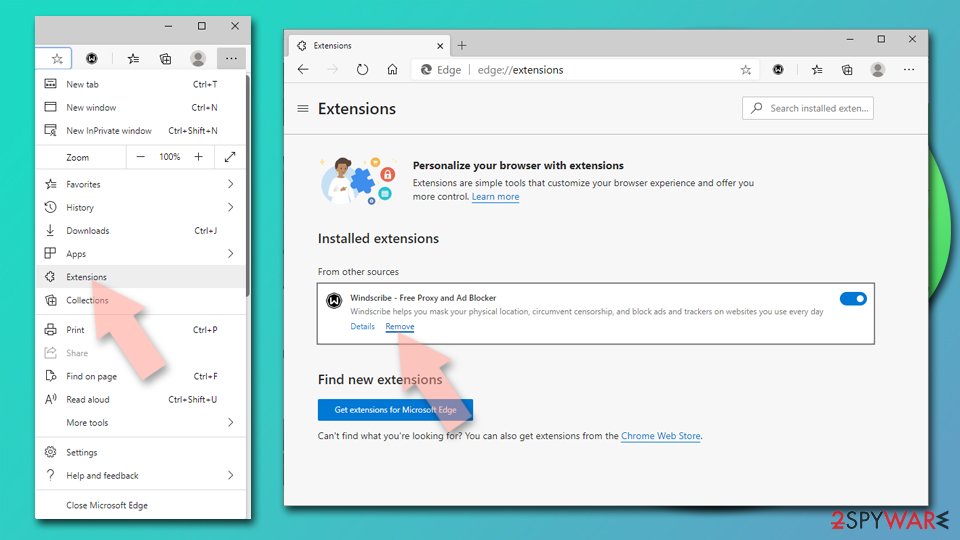
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
Reset Chromium-based MS Edge:
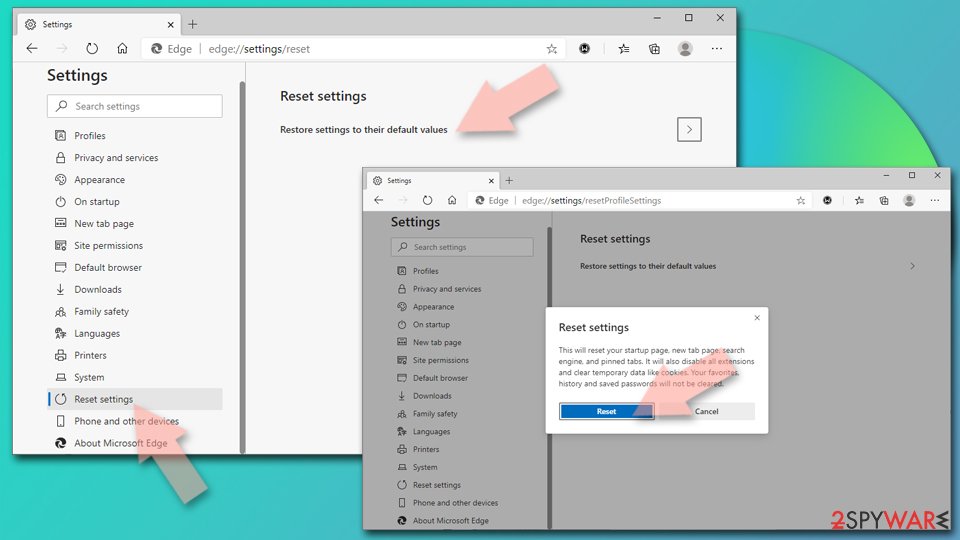
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
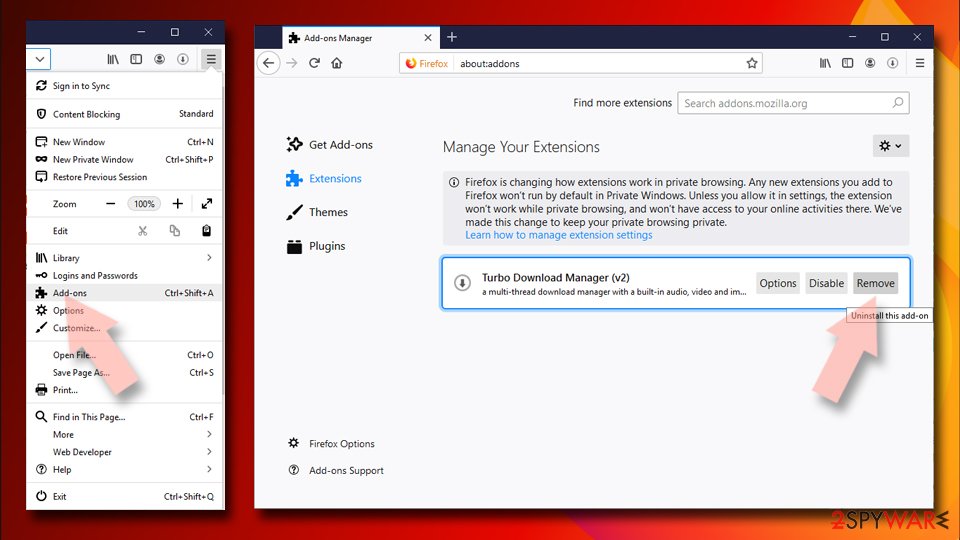
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
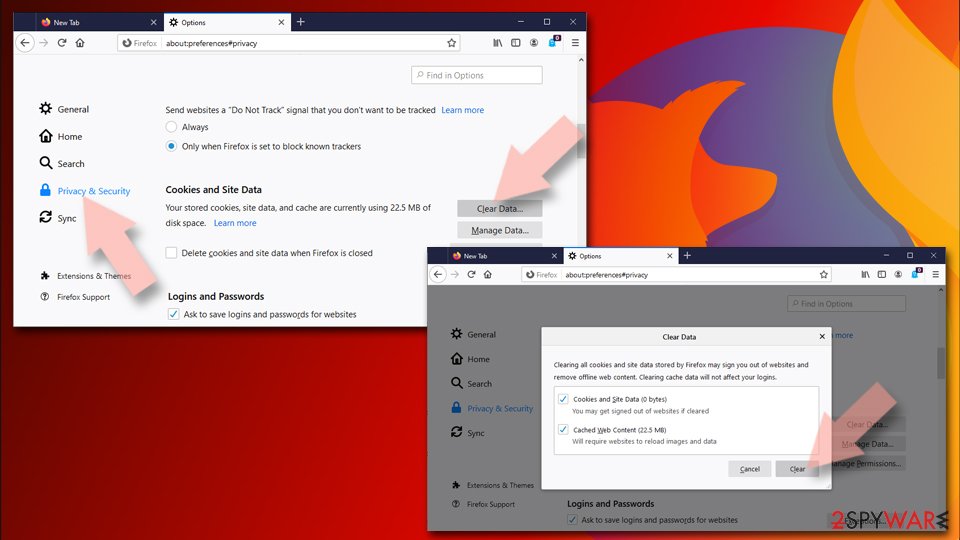
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
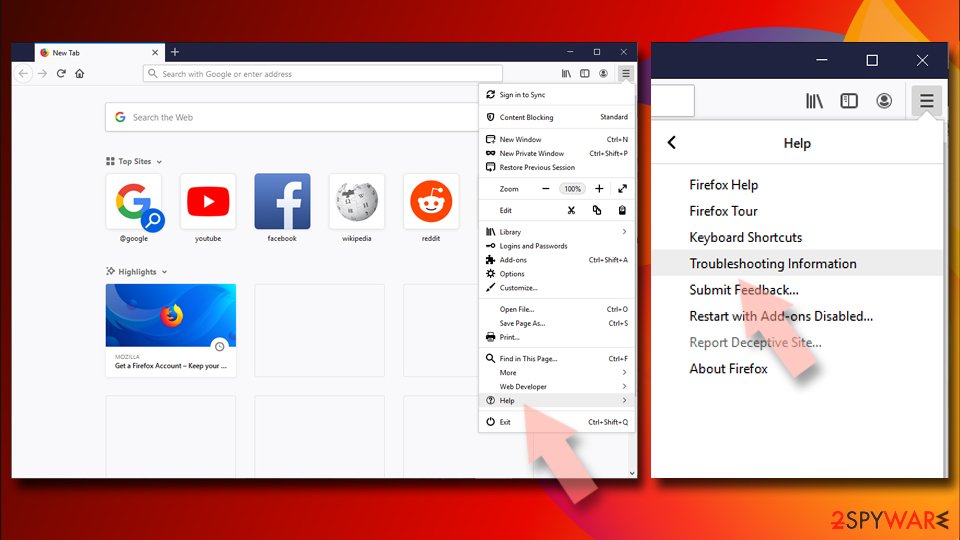
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
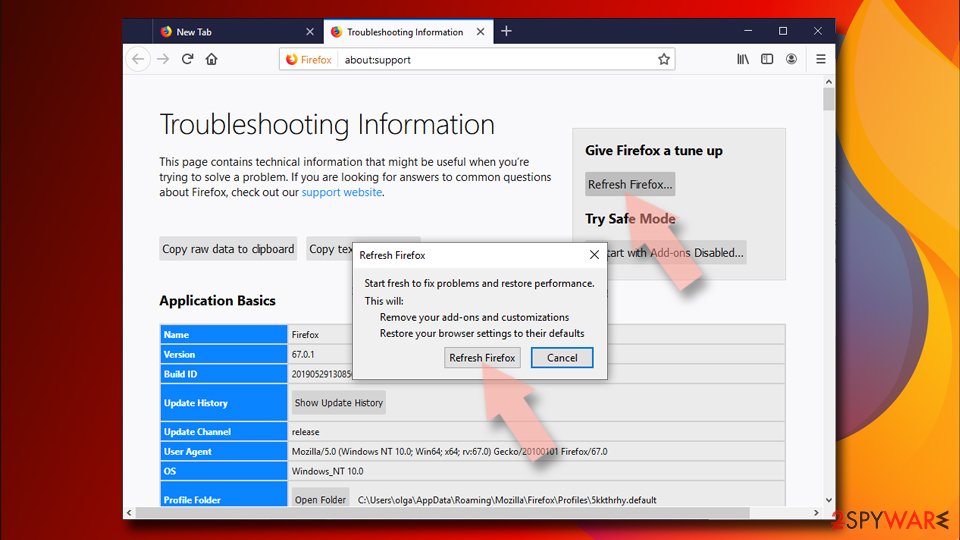
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
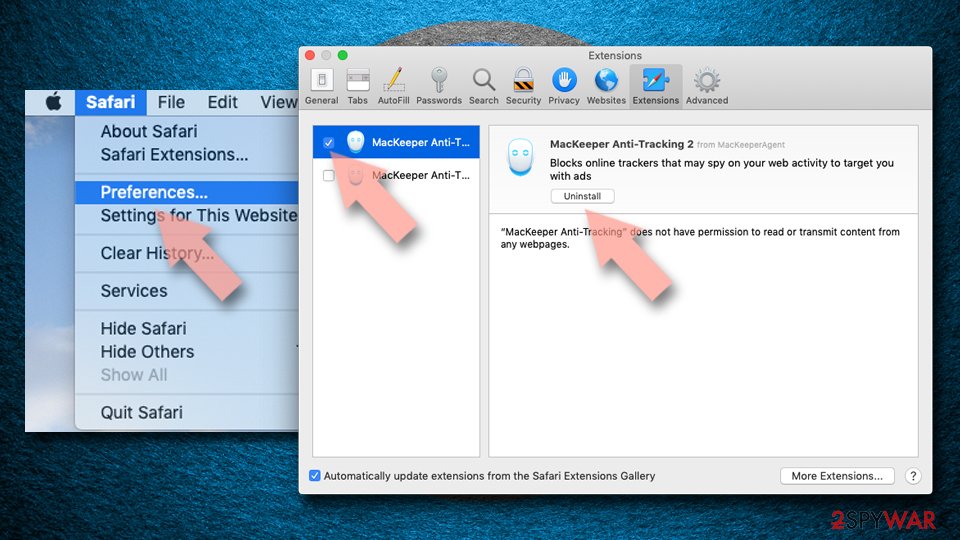
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
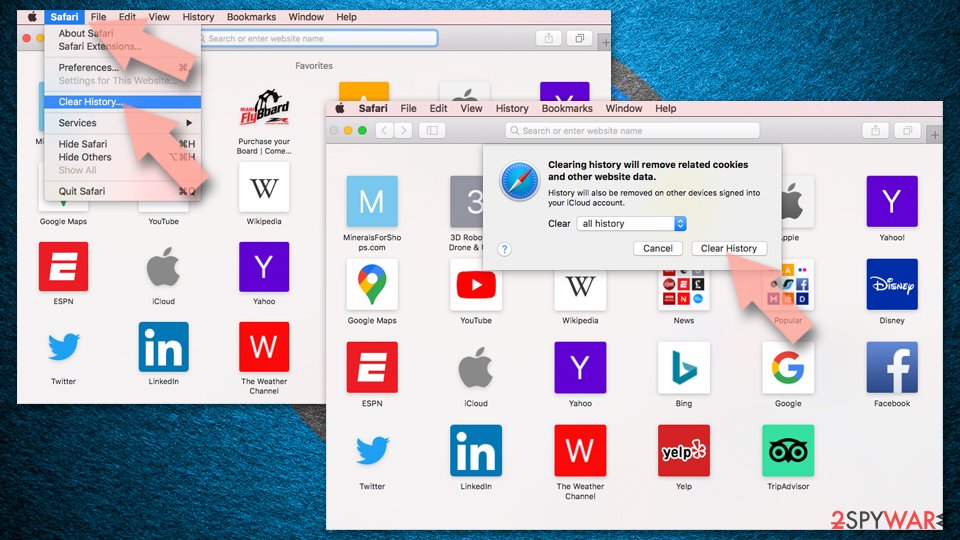
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
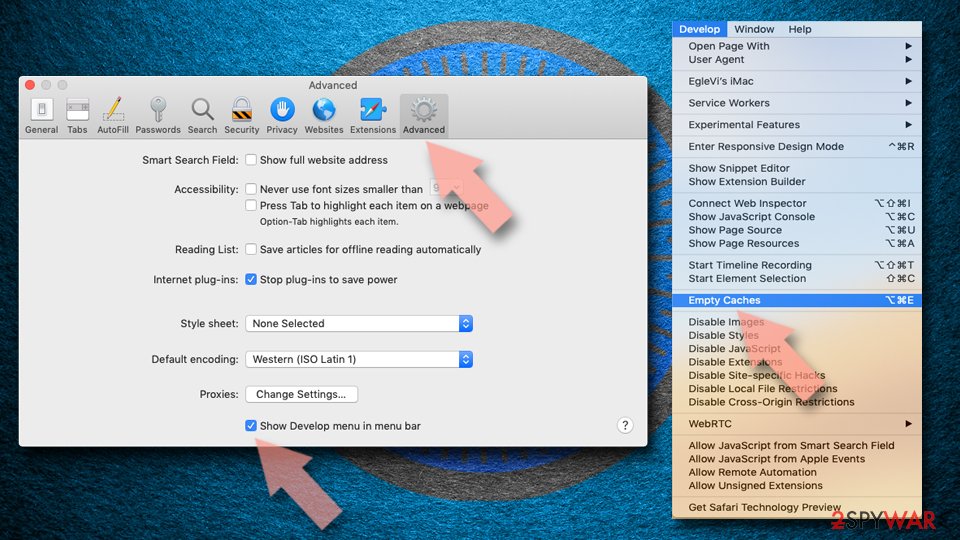
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
macOS users should get rid of PUPs as explained below:
Remove the unwanted application:
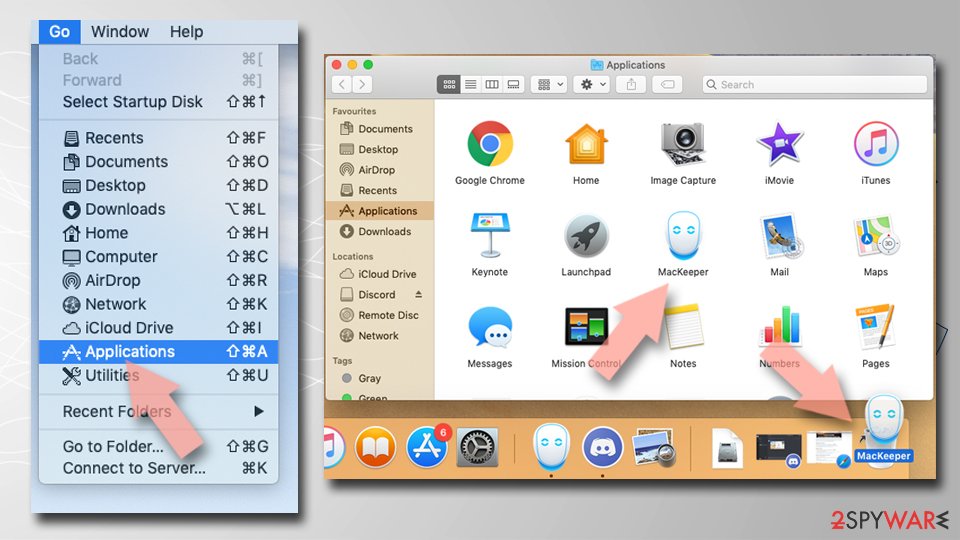
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
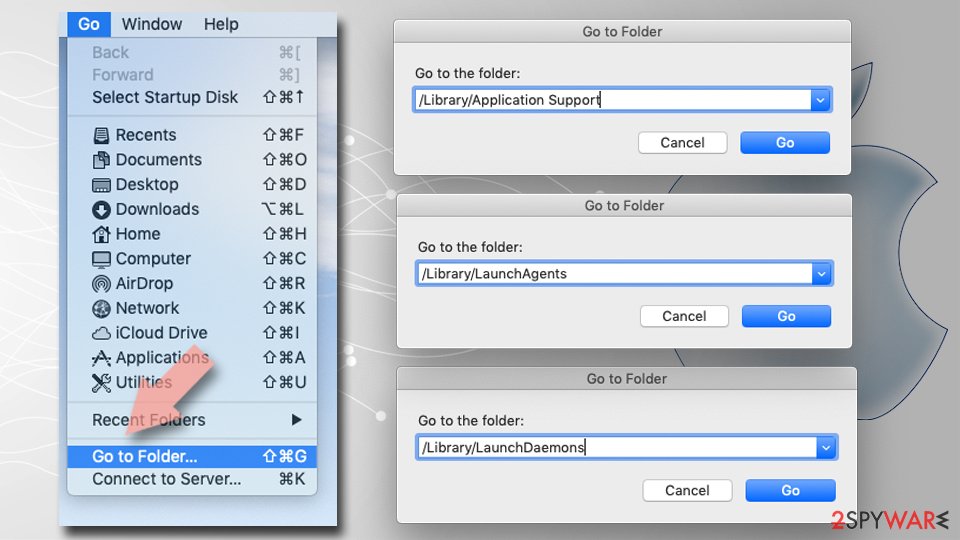
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
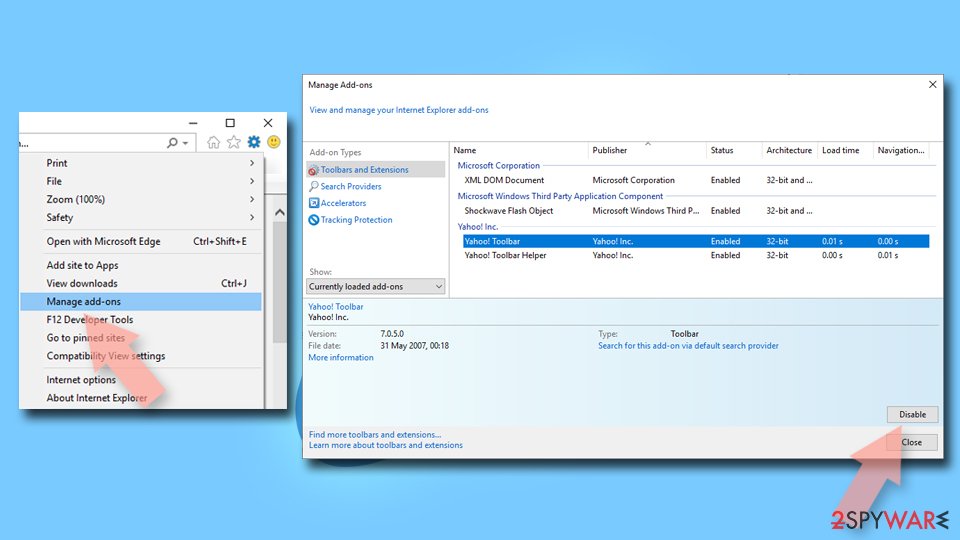
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
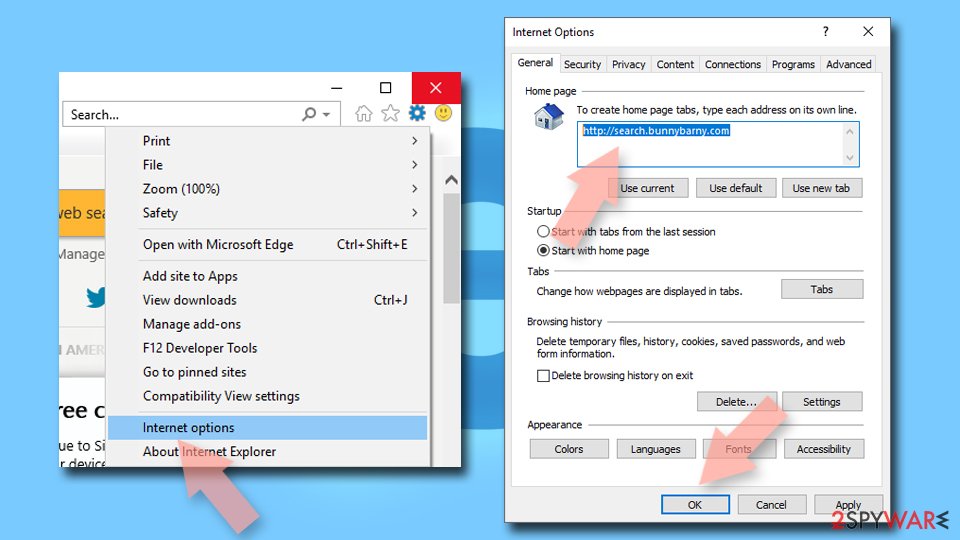
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
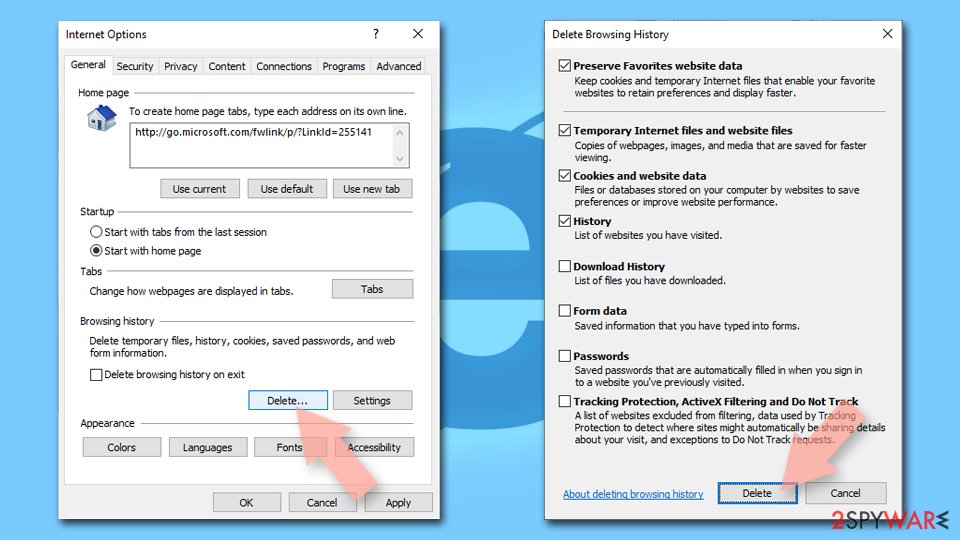
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
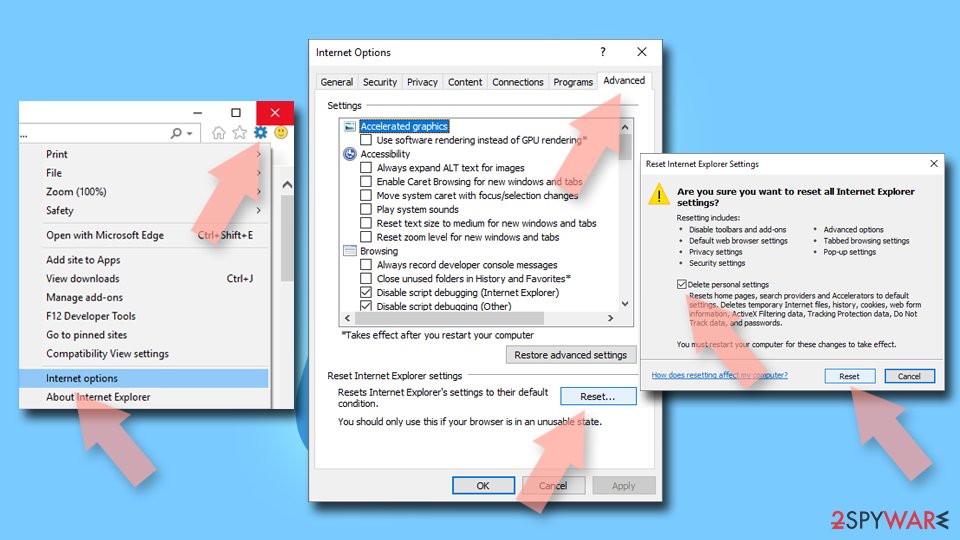
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
Questions about Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn
Defender removed BrowserModifier:JS/Adrozek.A.. Am I safe now?
Often yes, but check two things. First, whether the detection was caught on arrival: a file in Downloads or in an archive that Defender quarantined before it ran is the best case.
Second, whether BrowserModifier:JS/Adrozek.A. comes back. If it returns, or if Protection history shows several different detections around the same date, something on the PC keeps producing the file and needs to be found.
Run a full scan and, if anything remains, an offline scan. If the category names a password stealer or a backdoor, change your passwords from another device even if the file is gone.
Should I change my passwords after BrowserModifier:JS/Adrozek.A.?
It depends on the category and on whether the file ran. If the name begins with PWS, Spy, Backdoor or Trojan and the file sat in AppData, ProgramData or Temp, assume it ran and change your important passwords from a different device, starting with e-mail, then banking.
Sign out of all sessions too. If BrowserModifier:JS/Adrozek.A. is a PUA or was caught in Downloads before you opened anything, a password change is a precaution rather than a must. When in doubt, change the e-mail password and turn on two-step verification; it is quick and protects everything else.
Why does Defender call Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn a browser modifier?
Microsoft uses the BrowserModifier category for software that changes browser settings without proper consent, such as the search engine or home page. Defender names this one BrowserModifier:JS/Adrozek.A.. The label means the program is unwanted rather than destructive: it does not encrypt files or open the PC to attackers.
Removing the detected files is a good start, but a scan does not restore your search engine, new tab or policies, so follow the browser steps in this guide afterwards, in every browser you use.
Is Microsoft Defender enough to remove Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn?
For most home PCs it is a solid first step. Defender detects this threat as BrowserModifier:JS/Adrozek.A., and a full scan followed by an offline scan covers the places where Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn usually hides. The offline scan runs before Windows starts, so malware that hides while Windows is running cannot interfere: Run a Microsoft Defender Offline scan.
Defender does not undo everything, though. It does not restore browser settings, decrypt files or change passwords that may have been copied, which is why this guide has separate steps for those. If Defender finds the same item again after removal, something else keeps reinstalling it.
Is only one browser affected?
Often not. Programs that install hijackers tend to change every browser they find, and sync can carry the extension to other computers signed in to the same browser account. Check Chrome, Edge and Firefox, even the ones you rarely use, and look at the shortcut targets on the desktop and taskbar for each.
If you use sync, remove the extension while signed in so the removal syncs too. Also check the On startup setting and the new tab page, because hijackers change those as well as the search engine.
What do I lose if I reset Chrome or Edge?
Less than you might think. A reset turns off all extensions, which you can turn back on one by one, restores the default search engine, home page, new tab and pinned tabs, and clears cookies, so you are signed out of most sites.
Bookmarks, history, saved passwords and autofill data stay. Firefox's equivalent, Refresh Firefox, keeps the same essentials but removes add-ons completely. Before you reset, make sure you know your main passwords or have them saved, since you will need to sign in again.
Why can't I change my search engine back?
Because something keeps setting it. If an extension controls the search engine, Chrome and Edge show a note that an extension is controlling this setting, and your change is reverted. If a policy controls it, the field is greyed out and the browser shows Managed by your organization.
Remove the extension first, then the policies, and only then change the search engine; the change will stay. If it still reverts, look for a program in Installed apps or a scheduled task that reinstalls the extension.
What is Js/Adrozek.A, BrowserModifier:JS/Adrozek.A,?
Js/Adrozek.A virus is a relatively old detection name used by Windows Defender to identify suspicious activity on various web browsers. In most cases, such potentially unwanted programs are distributed via deceptive methods such as software bundling or fake update prompts - this usually results in unintentional installation.
Damage: Installation of other potentially unwanted programs or malware, data theft, monetary losses. The summary table at the top of this guide lists the type, the detection names, the symptoms and the damage of Js/Adrozek.A, BrowserModifier:JS/Adrozek.A,. Reading it first helps you decide whether your computer shows the same signs.
Will Fortect remove Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Js/Adrozek.A, BrowserModifier:JS/Adrozek.A, Trojan:Win32/Adrozek!rfn, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Drive-by download (read October 7, 2026)
- Microsoft: Widespread malware campaign seeks to silently inject ads into search results, affects multiple browsers (read October 7, 2026)
- Virukset: Virukset (read October 7, 2026)
- AV-Test: AV-TEST Product Review and Certification Report – May-Jun/2020 (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)