
Viruses · 307 guides

Trojans removal guides, page 7 of 12

Hidden programs that give attackers remote access, and how to find and remove them.
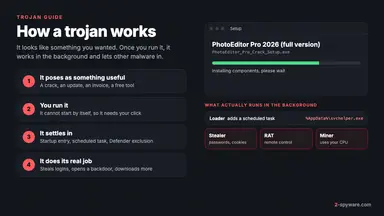
Start hereWhat is a trojan and how to remove itA trojan is malware disguised as something you wanted, such as a cracked program, a fake update or an invoice. It does nothing until you run it, then steals passwords, gives a stranger remote access or downloads more malware. To remove it, cut the startup entries it added, run a full and an offline scan, then change your passwords from a clean device.

Most searched trojans guides

  1. 1Remove Csrss.exe trojan
  2. 2Remove Memz virus
  3. 3Remove Wcupdater
  4. 4Remove Win32/Lodi
  5. 5Remove Chrome.7z
  6. 6Remove Iplogger.org

Trojans removal guides 163–189 of 307

Remove Precomp.exe

Precomp.exe - a Windows background process that might indicate malware infection Precomp.exe is a process that users might find running on their Task Manager under the name of Command Line Precompressor,TrojansHigh riskJake Doevan ·

Remove Abaddon RAT

Abaddon RAT is the malware that uses the Discord app as a command & control server Abaddon RAT is the intruder with a ransomware feature and gets instructions from creatorsTrojansHigh riskJulie Splinters ·

Remove Svcvmx virus

Svcvmx is a malicious process related to a Trojan horse that connects to various sites in the background Svcvmx virus is a dangerous ad-clicking Trojan[ref en-1] is usually installed togetherTrojansHigh riskJake Doevan ·

Remove Trojan:O97M/Mountsi.D!ml

Trojan:O97M/Mountsi.D!ml is the possible false detection that informs about malware on the computer Trojan:O97M/Mountsi.D!ml - heuristic detection name that states about a trojan malware installed. It might be the caseTrojansHigh riskUgnius Kiguolis ·

Remove Trojan.genericKDZ

Trojan.genericKDZ – the malware that can be used as a hacking tool or to spread other threats on the computer Trojan.genericKDZ – the generic threat detection that indicates a dangerous component thatTrojansHigh riskGabriel E. Hall ·

Remove JS.Nemucod

JS.Nemucod - a trojan that can install Crowti, Tescrypt, Locky, Fareit, and Ursnif viruses   JS.Nemucod, also known as Nemucod Trojan or TrojanDownloader:JS/Nemucod, is a very dangerous parasite that canTrojansHigh riskJulie Splinters ·

Remove Trojan Woreflint

Trojan Woreflint - a security threat that might be marked by your anti-malware Trojan Woreflint is a malicious program that can be designed for numerous purposes. Some of its versionsTrojansHigh riskAlice Woods ·

Remove BazarLoader malware

BazarLoader malware - dangerous backdoor operated by Trickbot cybercriminal group BazarLoader is a malicious program categorized as a Trojan and a backdoor - it is designed to infiltrate Windows machinesBackdoorsHigh riskGabriel E. Hall ·

Remove Backdoor.Win.DARKCHEESE

Backdoor.Win.DARKCHEESE is the detection of a threat that possibly falls in the category of backdoor trojans Backdoor.Win.DARKCHEESE is the threat that can launch malicious processes and run on systems' resources.TrojansHigh riskOlivia Morelli ·

Remove Backdoor.SDBot

Backdoor.SDBot is the trojan that allows attackers to control the targeted computer by opening the backdoor Backdoor.SDBot is the malware that belongs to a backdoor trojan family because of theTrojansHigh riskJulie Splinters ·

Remove Trojan.agent.evin

Trojan.agent.evin is a malicious program that gets reported by anti-malware tools Trojan.agent.evin - the detection name for a threat that, unfortunately, can be set to perform the various processes. TheTrojansHigh riskAlice Woods ·

Remove Trojan:win32/tiggre!plock

Trojan:win32/tiggre!plock is the virus that can negatively affect the performance and state of the security Trojan:win32/tiggre!plock is the trojan detection result that shows up on the screen once the infectionTrojansHigh riskUgnius Kiguolis ·

Remove Trojan:win32/fuery.b!cl

Trojan:win32/fuery.b!cl - malicious program that is spread through third-party downloads Trojan:win32/fuery.b!cl is a heuristic detection name a particular computer threat, typically assigned by Windows Defender. Trojans can represent a wideTrojansHigh riskJulie Splinters ·

Remove xmr-stak.exe

xmr-stak.exe is the trojan responsible for extracting Monero and other cryptocurrency running on the CPU of your PC xmr-stak.exe is the threat that creates issues with the system because itTrojansHigh riskLinas Kiguolis ·

Remove Trojan.Downloader

Trojan.Downloader is the general term used to describe trojans designed to download other malware on the machine Trojan.Downloader is the type of trojan horse that installs files, malware, and maliciousTrojansHigh riskUgnius Kiguolis ·

Remove TrickBot virus

TrickBot - a modular banking malware employed by criminals in different campaigns to steal sensitive data TrickBot is a financial Trojan first discovered in 2016 and targeted customers of leadingTrojansHigh riskJulie Splinters ·

Remove Iplogger.org

Iplogger.org is a misleading URL that may be misused by malware for tracking users' IP addresses  Iplogger.org or Iplogger.com is a website that allows users to track people's IP addresses byTrojansHigh riskJake Doevan ·

Remove Trojan/Win64.Meterpreter

Trojan/Win64.Meterpreter is not a false positive detection - it's an activity sign of a dangerous Meterpreter banking trojan Trojan/Win64.Meterpreter is a generic threat detection name that can be brought byTrojansHigh riskGabriel E. Hall ·

Remove GraceWire trojan

GraceWire trojan is the information-stealing malware that gets sent via phishing emails GraceWire trojan is the product from the Evil Corp hacker group that spreads malware that avoids detection andTrojansHigh riskLucia Danes ·

Remove Win32/Lodi

Win32/Lodi is a heuristic detection used to describe applications that use misleading diagnostic results about computer health Win32/Lodi is a generic name that is applied to applications that are ofSystem toolsMedium riskUgnius Kiguolis ·

Remove Program:Win32/Wacapew.B!ml

Program:Win32/Wacapew.B!ml can be a false positive detection or refer to an SDBbot Remote Access Trojan Program:Win32/Wacapew.B!ml is a generic detection name delivered to Windows users by Windows Defender antivirus program. Typically,TrojansHigh riskJake Doevan ·

Remove Uds dangerousobject.multi.generic

Uds dangerousobject.multi.generic is the heuristic detection name for dangerous ransomware or trojan Uds dangerousobject.multi.generic is a detection name that can either be a false positive or imply a ransomware orTrojansHigh riskGabriel E. Hall ·

Remove Ursnif virus

Ursnif is the info-stealing threat distributed in various online scam campaigns   Ursnif (also known as Gozi, ISFB, or Dreambot) is a virus that specializes in banking credentials and other information-stealingTrojansHigh riskGabriel E. Hall ·

Remove Gh0st RAT

Gh0st is the trojan that is used to hack computers and spy on users by running in the background Gh0st RAT is the remote access trojan that can be setTrojansHigh riskOlivia Morelli ·

Remove ProstoStealer

ProstoStealer is the trojan promoted online as a tool for information stealing and system hacking purposes ProstoStealer - malware that is sold online in various Russian hacking sites and forums,TrojansHigh riskLinas Kiguolis ·

Remove Agent Tesla

Agent Tesla is a dangerous Trojan used by criminals to collect banking information, logins, Wi-Fi passwords, and other credentials Agent Tesla is a Trojan infection, which exhibits traits of anTrojansHigh riskGabriel E. Hall ·

Remove Remcos

Remcos RAT is a dangerous info-stealing trojan that abuses the Coronavirus as a theme for the malicious spam attacks Remcos or Remote Control and Surveillance[ref en-1] are promoted as aTrojansHigh riskAlice Woods ·
5,558 members already hereReading, writing, commenting and voting. 0 verified · 283 joined this year