
bratarfood.com: an open folder that handed out Windows malware files (AzaleaAgent, CoinMiner), and what to do if a PC fetched them
bratarfood.com is a web address that URLhaus lists 12 times on 23 September 2026 for files in an open folder called /new/:
- eight .exe programs
- one .bat script and three .txt loader files
- some tagged AzaleaAgent
- CoinMiner
All 12 are now marked offline, but when we asked the home page on 17 October it still answered with a plain file listing. If you only saw the name in a log, nothing is proven; if something on your PC may have fetched these files, treat the PC as watched, change your passwords from another device, then scan and clean or reset Windows.
Facts checked October 17, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like a script, loader or program that downloads files from bratarfood.com usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove bratarfood.com (AzaleaAgent, CoinMiner, encoded loader files) yourself 5 steps, about 15 minutes, no software needed.
Start the steps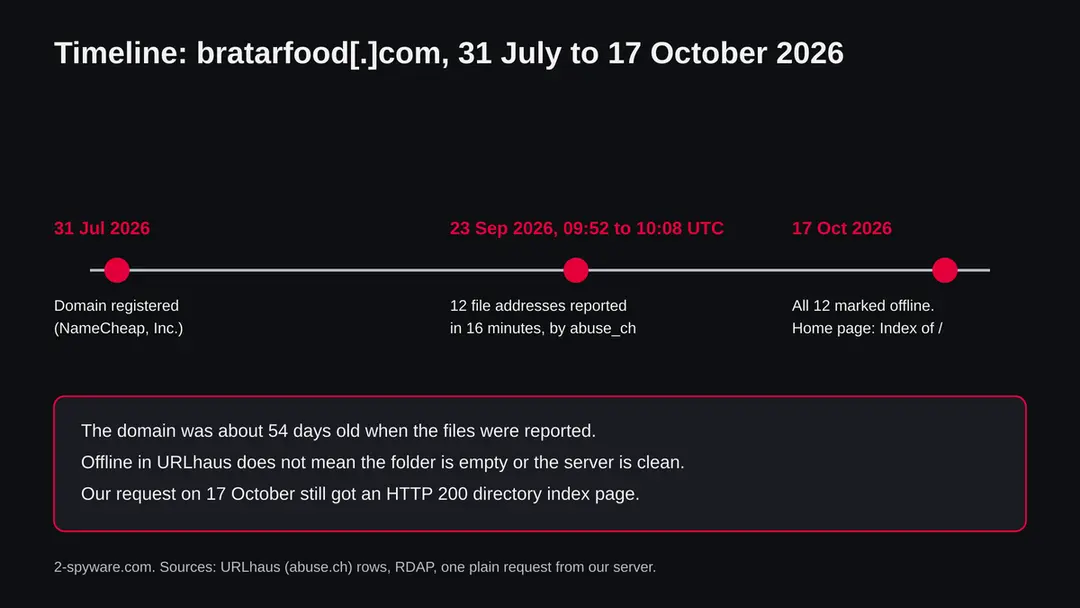
Bratarfood.com (AzaleaAgent, CoinMiner, encoded loader files): summary
| Type | A malware server: 12 files in an open folder, tagged AzaleaAgent, CoinMiner and rev-base64-loader (Windows programs, one script, three encoded loaders) |
|---|---|
| Risk | High if a loader on your PC fetched its files: keystrokes, passwords, screen and files may be seen or taken. Low if you only saw the name |
| Symptoms | Often none. Unknown scheduled tasks or startup entries, and a busy processor with nothing open, are the signs in the reports |
| How to get rid of it | Change passwords from another device, run Microsoft Defender Offline, remove the startup entries, and reset Windows if you are not sure |
| Our check (17 October 2026) | One plain request from our server: status 200, a page titled Index of /. A quiet answer clears nothing; the danger rating comes from URLhaus |
| Running since / first seen | Domain registered 31 July 2026; files reported on 23 September 2026 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Platform | Windows. Nothing we read says Mac or phones are affected |
|---|---|
| Detection names | No Microsoft detection name is known for these files, because we did not open them |
| Name | Bratarfood.com |
| Domain registered | 31 July 2026 |
| Evidence | 12 write-ups by security sites; details still limited |
| First seen | 23 September 2026 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 17 October 2026 |
Facts checked on 17 October 2026 against the URLhaus data for bratarfood.com held in our database, RDAP, one plain request from our server, and published pages by Logpoint, Rubrik Zero Labs, Expert Insights, Microsoft Learn and Microsoft Support. We did not download the files and we infected no PC; the removal steps follow Microsoft's pages and were not tried on a live infection.
What bratarfood.com is, and what we know about it
bratarfood.com is not a program on your PC. It is a web address that the abuse.ch project URLhaus lists as a place where malware files were served from an open folder. We found no public write-up of this one address, so what follows is what URLhaus shows, what our own request returned, and what security vendors have published about the malware names in the tags.
- 1
What URLhaus lists
Twelve file addresses, all inside the folder /new/ on bratarfood.com, all added on 23 September 2026 between about 09:52 and 10:08 UTC by the reporter abuse_ch. They are eight programs (alibaba.exe, masa.exe, msc.exe, agents.exe, msn.exe, mns_protected.exe, baidu.exe and microsoft.exe), one batch script (alibaba.bat) and three text files (XWormClientupload.txt, agentupload.txt and playload12upload.txt). All carry the threat label malware_download and all 12 are marked offline.
- 2
What the tags mean
opendir means the folder could be listed by anyone, which is how a whole set of files was found within minutes. AzaleaAgent is on four programs (alibaba.exe, mns_protected.exe, baidu.exe and microsoft.exe); it is a name linked to the Azalea remote access trojan. CoinMiner is on agents.exe and microsoft.exe and means a program that mines cryptocurrency on someone else's PC. The three .txt files carry the tags ascii, Encoded and rev-base64-loader, which describe text that is written backwards in base64 and is turned into a program by a script.
- 3
What we could not confirm
We did not download any file, so we cannot tell you what is inside, which builds they are, or where they report to. The file name XWormClientupload.txt suggests XWorm, a remote access trojan, but URLhaus did not put XWorm in the tags, so that is a hint from a name, not a proof. We also do not know which message or program makes a victim's PC ask for these files.
- 4
What this means for you
If you only saw the name in a firewall log, a blocked request or a warning, you are not infected by that alone. The risk is for a Windows PC where something already ran and went to fetch one of these files. Nobody opens a folder like /new/ by hand to read a menu; a program does it.
- Kind of threat
- A server with an open folder of malware files: programs tagged AzaleaAgent and CoinMiner, a batch script and three encoded loader text files
- Where the files were
- hxxps://bratarfood[.]com/new/NAME: ordinary https on the normal port, in one folder called new
- Domain registered
- 31 July 2026 through NameCheap, Inc.; status client transfer prohibited (RDAP, read 17 October 2026)
- URLhaus entries
- 12 file addresses, all added on 23 September 2026; all 12 offline when we read our copy of the data on 17 October 2026
- Delivery trick
- Staging in an open folder, plus text files holding reversed base64 that a script rebuilds into a program. The entry step on the victim's PC is not known
- Platform
- Windows. The files are .exe, .bat and loader text for Windows scripts. Nothing we read says Mac, iPhone or Android are affected
What bratarfood.com (AzaleaAgent, CoinMiner, encoded loader files) does on an infected PC
What we checked on 17 October 2026, and what we could not
Our check was one plain request from our server, with no browser and no clicks. It returned HTTP status 200 and a page titled Index of /, served by LiteSpeed. That is a bare file listing, not a website. It clears nothing.
Our site test, 17 October 2026
- The home page is a directory listingThe page title was Index of /. A server that shows its folders to every visitor is either unfinished or used as a storage place. It is the same kind of open listing that the opendir tag in URLhaus describes for the /new/ folder. We did not open the listing further and do not know what it shows today.
- Why this is not a clean resultThe reported files are marked offline, but we only made one request to the front page. Files can be moved, renamed or put back in another folder. A quiet front page is common for servers of this kind and is not a sign of safety.
- Notification request, pop-ups, redirects, ad networksNone seen in the plain request (the answer mentioned no notification service). A plain request cannot show scripts that run in a browser, so this is not a statement that the site never does these things.
- URLhaus listingTwelve file addresses tagged malware_download, four with AzaleaAgent, two with CoinMiner, three with rev-base64-loader; all reported on 23 September 2026.
- Downloads and the files themselvesWe did not download any file. We cannot tell you what the files contain or whether they are still stored on the server.
Dangerous: treat it as a malware server Our test was one plain request and proves nothing either way. The danger rating comes from the twelve URLhaus reports and their tags, not from our visit. Do not request files from this address and do not run anything that does.
What happened to bratarfood.com, from registration to our check
This is a young domain. It was registered about eight weeks before the reports, and all 12 reports fall within sixteen minutes. The dates come from RDAP and from the URLhaus data we hold; the times are UTC.
31 July 2026
The domain is registered
RDAP shows bratarfood.com registered on 31 July 2026 at about 15:20 UTC through NameCheap, Inc. The only status is client transfer prohibited, which is a normal registrar lock and says nothing about the content.
23 September 2026, 09:52 UTC
The first loader files are reported
abuse.ch adds alibaba.bat, playload12upload.txt and agentupload.txt within about a minute. The two text files are tagged ascii, Encoded and rev-base64-loader; the batch file is tagged bat and opendir.
23 September 2026, 09:53 UTC
Eight programs are reported in about six seconds
microsoft.exe, baidu.exe, mns_protected.exe, msn.exe, agents.exe, msc.exe, masa.exe and alibaba.exe are added between 09:53:13 and 09:53:18. Four carry AzaleaAgent, two carry CoinMiner (microsoft.exe carries both), and msn.exe, msc.exe and masa.exe carry only exe and opendir.
23 September 2026, 10:08 UTC
The last file, with an XWorm name
XWormClientupload.txt is added at about 10:08 UTC with the loader tags ascii, Encoded and rev-base64-loader. Its name points to XWorm, but the tags do not.
17 October 2026
All offline, front page still a listing
All 12 entries are marked offline in our copy of the data. Our plain request to the home page the same day still returned a directory listing with status 200.
The three dates that matter for bratarfood.com: registration, the 12 reports, and our check. The picture is our own drawing of the data, not a screenshot of the site.
What the pattern suggests, and what it does not: a new domain whose whole content was reported in one sweep looks like a staging server set up to hold tools, with a folder anyone could browse. That is our reading of the dates and the tags, not something any report says. We do not know who runs it, and the domain may be hacked rather than built for this.
The 12 files, one by one
The list below is what URLhaus shows for each address. The tags are labels from the reporter and from matching, not a proof of what a file does, and we opened none of them.
| File in /new/ | Tags in URLhaus | What the tags suggest |
|---|---|---|
| alibaba.exe | AzaleaAgent, exe, opendir | A program linked to the Azalea remote access trojan |
| baidu.exe | AzaleaAgent, exe, opendir | Same tag. The name copies a well known Chinese company; that is a disguise or a label, not a link to the company |
| mns_protected.exe | AzaleaAgent, exe, opendir | Same tag; the word protected may mean a packer or crypter was used, which is our guess |
| microsoft.exe | AzaleaAgent, CoinMiner, exe, opendir | Two labels on one file. It is not from Microsoft; the name borrows a trusted brand |
| agents.exe | CoinMiner, exe, opendir | A program labelled as a cryptocurrency miner |
| msn.exe, msc.exe, masa.exe | exe, opendir | Programs with no family tag. Unknown. Treat them like the others |
| alibaba.bat | bat, opendir | A Windows batch script; such scripts often start the next stage |
| agentupload.txt, playload12upload.txt, XWormClientupload.txt | ascii, Encoded, opendir, rev-base64-loader | Text that is reversed base64; a script reverses it, decodes it and runs the program inside |
How the files fit together: a loader, an agent and a miner
We did not see how a PC reaches this folder, and no vendor has written about this address. The chain below is built from the file names, the tags and from what vendors describe for the same malware names, so treat it as a model of what is likely, not a record of what happened.
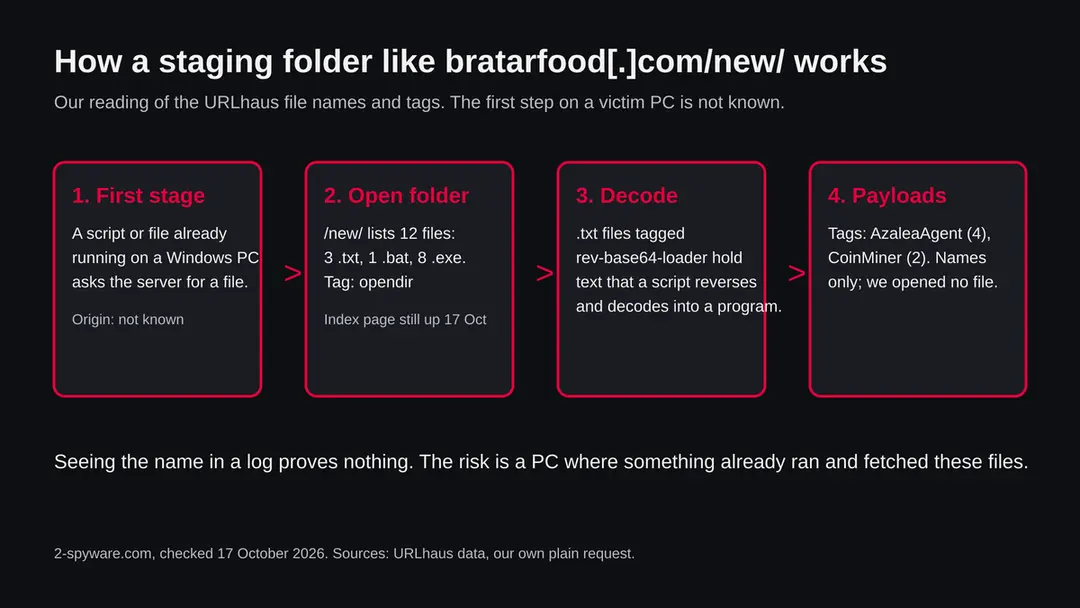
- 1
A first program is already running
Nothing in the reports says how. Vendors describe a phishing attachment, a shortcut file or a downloaded script as the usual start. That first program then asks a server for the next piece, and here the server is bratarfood.com.
- 2
A text file is fetched and rebuilt
Public analyses of XWorm batch to PowerShell chains describe embedded base64 that is cleaned, reversed and decoded to rebuild a .NET program, which then resolves to XWorm. The rev-base64-loader tag on the three .txt files fits this pattern. The file looks like harmless text, so a filter that only checks file type sees nothing wrong.
- 3
The program starts and stays
Logpoint lists three ways XWorm keeps itself on a PC: a file in the Startup folder, a scheduled task and a registry Run key. Point Wild, quoted by Expert Insights, reports a scheduled task called UpdateTask for two Azalea samples. Whether the files here do the same is not confirmed.
- 4
A person or a miner takes over
A remote access trojan lets someone else use the PC. A coin miner uses your processor and power to earn money for someone else. Both can run on the same PC, which is why the tags AzaleaAgent and CoinMiner on one file (microsoft.exe) matter.
What AzaleaAgent, XWorm and a coin miner are
The three names are different things. The sources agree on what they can do and differ on what each campaign adds. None of these sources looked at the files on bratarfood.com.
| Question | What the sources say | Source |
|---|---|---|
| What is Azalea? | A remote access trojan sold as malware as a service on underground forums, with modules for privilege escalation, persistence and information theft | Rubrik Zero Labs |
| What can it do? | Remote access, keylogging, hidden VNC (a screen control that the user does not see), Active Directory discovery and privilege escalation; an operator panel called AzaleaControl was found | Point Wild, via Expert Insights |
| How was it delivered? | One sample as a batch file that no engine of 61 flagged when tested; another from a malicious shortcut that used curl to fetch its next stage | Expert Insights |
| Is AzaleaAgent the same thing? | Not proven. A search for the exact name AzaleaAgent found nothing; the tag looks like a MalwareBazaar label for Azalea samples. Our reading, not a confirmed fact | Our reading |
| What is XWorm? | A commodity remote access tool with keylogging, remote desktop, command execution and data theft; plugins add features, so a build differs from the next | Logpoint |
| How does XWorm stay? | Startup folder, scheduled task or registry Run key; some builds inject into trusted Windows processes such as explorer.exe or svchost.exe | Logpoint |
| What is a CoinMiner? | A program that mines cryptocurrency. We found no source that links a miner to this server beyond the URLhaus tag | URLhaus tag only |
| Which builds are on this server? | Not known. We opened none of the files | Not available |
What bratarfood.com (AzaleaAgent, CoinMiner, encoded loader files) can steal or download
What these programs can take from a Windows PC
A remote access trojan gives a person a seat at your computer, so the list below is what such a person can do rather than what one build does by itself. A miner takes power, not data.
Reported as possible
- Every key you type
- A live view of your screen
- Hidden remote control of the desktop
- Commands run on your PC
- Files searched and sent away
- Saved browser logins
- Extra malware downloaded
- Higher rights on your PC
- Your processor and power used for mining
| Data | Detail | Source |
|---|---|---|
| Keystrokes and screen | Keylogging, remote desktop and hidden VNC | Logpoint; Expert Insights |
| Commands and control | Command execution, plugins, privilege escalation | Logpoint; Rubrik |
| Company networks | Active Directory discovery and changes were reported for Azalea | Expert Insights |
| Power and speed | A miner slows the PC and raises its power use. This follows from what a miner is; no source measured it for these files | Our reading |
What this can cost you
Seeing the name costs nothing. The risks below apply to a Windows PC where one of these files ran.
- High
Passwords and accounts
A keylogger records what you type into every site, including new passwords you set. Changing passwords on the infected PC does not help; the person watching sees them too.
- High
Someone using your PC live
A remote access trojan is not a one time theft. The controller can come back at any time and act while you are signed in.
- High
A work network
Expert Insights reports Active Directory discovery for Azalea. A PC that belongs to a company should go to the IT team at once, not be cleaned alone.
- Medium
A slow, hot PC and a higher power bill
A miner uses the processor for someone else's gain. It rarely steals data, but it means someone else had control of the PC.
- Medium
More malware on the same PC
Loaders in these chains download further tools, and the tags show at least two kinds of payload on one server.
- Low
Nothing, if you only saw the name
A name in a block list, a log or a warning is not an infection.
What you may notice, and what you may not
Remote access trojans are built to be quiet. The signs below come from the sources and from what they imply; none is certain, and many victims notice nothing.
| Sign | What the reports show |
|---|---|
| A scheduled task or startup entry you did not make | Logpoint lists the Startup folder, scheduled tasks and the Run key for XWorm; Point Wild's Azalea samples used a task named UpdateTask |
| High processor use with nothing open | A miner works in the background. Check Task Manager, sorted by CPU. This follows from what a miner does; it is our reading |
| Fans loud and the PC hot while idle | The same cause. A busy processor makes heat |
| A trusted Windows program using the network | Logpoint says some XWorm builds inject into explorer.exe, svchost.exe or similar. These are real Windows programs, so one running with unusual network use is worth a look |
| A Defender message | Protection history may show a blocked or quarantined item. We do not know what Microsoft calls these files, because we did not open them |
| Accounts you did not touch | Logins from new places and password reset emails follow from stolen logins |
| Nothing at all | Stealth is the point of a loader that runs from text |
How to check the PC for bratarfood.com (AzaleaAgent, CoinMiner, encoded loader files)
How a PC ends up asking for these files
Nobody visits bratarfood.com/new/ on purpose. The request comes from a program, so the real question is how that program got on the PC. We cannot say for this server; the routes below are the ones vendors found with the same families.
- 1
A script or batch file from an email
Public analyses of XWorm describe a phishing attachment that is a BAT script, which starts PowerShell to fetch a base64 payload that turns into XWorm. Opening the attachment is what starts it.
- 2
A shortcut file that downloads the next stage
Expert Insights describes an Azalea sample that came through a malicious shortcut using curl.
- 3
A file that poses as a known program
Names such as microsoft.exe, baidu.exe and alibaba.exe borrow trusted brands. A file that claims to come from a big company but sits on an unknown server is a warning in itself.
Check your PC before you delete anything
Start with the question that matters: did something on this PC contact bratarfood.com, or did you open an unexpected attachment, shortcut, script or installer? If you saw the name in a log from your own network, the device that asked is the one to check. None of the checks below deletes anything.
While you check, stop using the PC for banking, email, work or crypto, and disconnect it from the network if you can.
- 1
Disconnect first
Turn off Wi-Fi or unplug the network cable. A remote access trojan needs the connection to be used.
- 2
Find which device asked for the address
If you came here from a log, a router page or an alert, note the device and the time. Only that device is in question, not every device on the network.
- 3
Look at Task Manager
Press Ctrl+Shift+Esc, open the Processes tab and sort by CPU. A program you do not know that keeps the processor busy while you do nothing is a candidate for a miner. Right-click it and choose Open file location to see where it lives. Do not end it or delete it yet; write down the name and the folder.
- 4
Open Task Scheduler
Press Start, type Task Scheduler and open it. Look in Task Scheduler Library for tasks you do not know, with random names or a name like UpdateTask that runs a script or a program from a user folder. Logpoint and Expert Insights both name scheduled tasks as a way these families stay. Write the name and the program it runs.
- 5
Look at Startup apps and the Startup folder
Open Settings > Apps > Startup and switch off nothing yet; just look for names you did not install. Then press Windows key + R, type shell:startup and press Enter, to see the Startup folder. Logpoint names that folder as a place where XWorm copies itself.
- 6
Open Protection history
In Windows Security > Virus & threat protection > Protection history, look for anything blocked or quarantined around the time of first contact. Microsoft says the results of an offline scan also appear there. A clean list does not clear the PC.
- 7
Check your accounts from another device
Look at the sign in activity of your email, bank and exchange accounts, and at crypto balances. This is quicker than any file check.
- 8
A scan helps, but it does not clear the PC
A scan with Microsoft Defender or another product can find known files. Treat a clean result like a clean site test: one data point. We did not infect a PC, so the order of the plan is our judgement from Microsoft's pages, not a tested result.
How to remove bratarfood.com (AzaleaAgent, CoinMiner, encoded loader files)
How to remove bratarfood.com
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to bratarfood.com or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever bratarfood.com installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
If you use a Mac, an iPhone or an Android phone
The files are .exe programs, a .bat script and Windows loader text. We found nothing that says they affect anything else.
| Your device | What we know | What to do |
|---|---|---|
| Mac | A .exe and a .bat file do not run on macOS. The sources we read describe Windows threats | Nothing to remove for this threat. Do not follow the Windows steps on a Mac |
| iPhone or iPad | No source ties these files to iOS | Nothing to remove. If you typed passwords on a page, change them |
| Android | No source mentions it | Nothing to remove for this threat; change passwords if you entered any |
After removal: passwords, accounts and prevention
If a PC may have run these files: clean it and protect what was taken
The PC is one half. The other half is everything you typed or stored on it while the trojan was there. The order matters: another device first, then the PC.
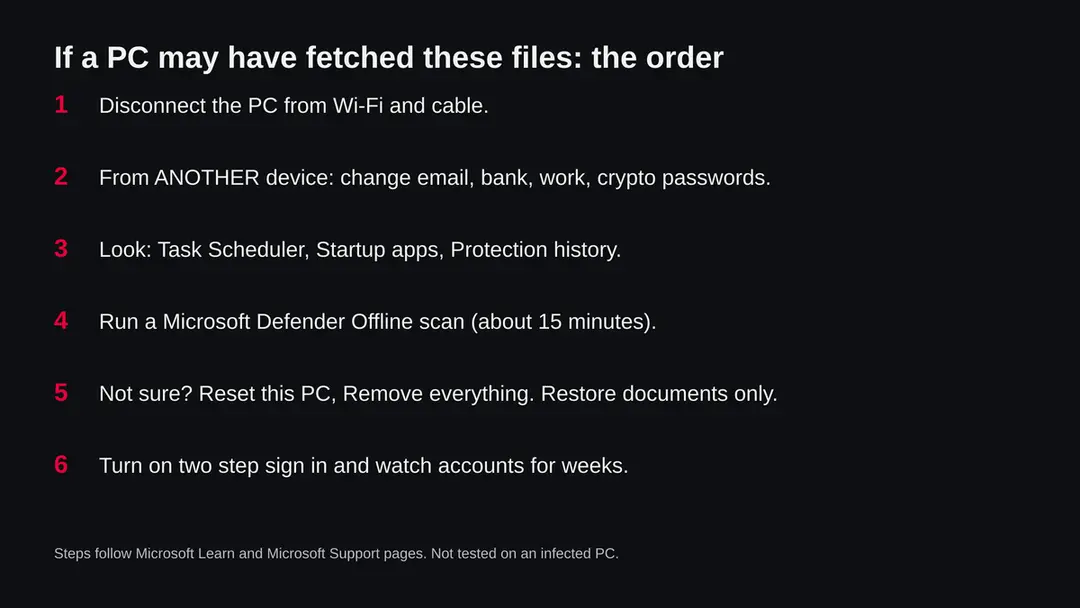
- 1
Change passwords from a clean device
Start with email, because it resets everything else, then bank, work, cloud storage and crypto. Anything typed on the PC while it was watched is already known. Use a phone or a different computer that you trust.
- 2
Turn on two step sign in and sign out other sessions
Use an authenticator app or a security key where the service offers it, so a stolen password alone does not open the account. Sign out of all devices and update the recovery email and phone.
- 3
Move crypto first if a wallet was on the PC
If a seed phrase or wallet file was ever on the PC, assume it is known. Create a new wallet and recovery phrase on a clean device and move the funds there.
- 4
Run Microsoft Defender Offline
Open Windows Security > Virus & threat protection > Scan options, choose Microsoft Defender Offline scan and select Scan now. Save your work first: Windows signs you out and restarts, and Microsoft says the scan takes about 15 minutes. If BitLocker is on, Microsoft says to suspend it first or the restart may ask for the recovery key. It does not apply to ARM versions of Windows. Results are under Protection history.
- 5
Remove what the check found, with care
If Task Scheduler, the Startup folder or Startup apps showed an entry you can tie to the malware, remove it. If you cannot tell, do not guess: the safe answer is the reset below.
- 6
If you are not sure, reset Windows
Go to Settings > System > Recovery > Reset this PC. Microsoft says Keep my files keeps personal files but removes apps and settings, and Remove everything reinstalls Windows from scratch and is the most disruptive. For a PC that may have been under remote control, the full wipe is the answer that does not depend on finding every piece. Microsoft warns that some recovery options can cause data loss, so back up first.
- 7
Restore only documents by hand
Copy back documents and photos, not programs, and not a full system image from after the first contact. Install apps from their makers' own sites.
- 8
Watch your money and your accounts
Check card statements and exchange logs for a few weeks and turn on alerts. If a company PC was involved, tell the IT team and let them check the network, because Active Directory discovery was reported for Azalea.
- 9
Tell the people you message
If your accounts were used to send links, tell your contacts not to open them.
If you run a site on bratarfood.com or a server like it
We cannot tell whether bratarfood.com was built for this or hacked. If it is your site, the facts below decide what to do. We found no source for this specific address, so these are general steps, not a tested procedure.
- 1
Look at the folder
Open your hosting file manager and look for a folder called new and for files such as alibaba.exe, microsoft.exe or any .txt named upload. Write down their dates before you touch them. If you did not put them there, someone else did.
- 2
Find how they got in
Check your hosting account log for sign ins you do not know, outdated site software and plugins, and weak or reused passwords. Open directory listings that show every file are a setting you can switch off.
- 3
Clean and lock
Remove the files, change the hosting, FTP and database passwords, update the site software, and turn on two step sign in for the host. Ask the host for help if you cannot tell what else changed.
- 4
Ask for a review
After cleaning, tell the host and the reporting services that the files are gone. URLhaus lists the files as offline, but our request on 17 October still got a directory listing, so check the front page too.
Keep a PC out of this kind of chain
The files on this server are the late part of the chain. Every vendor write-up we read starts earlier, with a file or a script a person opened.
Do
- Treat an unexpected attachment, shortcut or script as an attack, and close it, even when it looks like an invoice.
- Show file endings in File Explorer so a .lnk or .bat posing as a document is visible.
- Keep Windows and Microsoft Defender updated; the offline scan uses the latest definitions.
- Get programs from their makers' own sites or from the Microsoft Store.
- Use a password manager and two step sign in, so one stolen password is not enough.
- Keep a backup of documents on a disk that you unplug.
Don't
- Do not run a file called microsoft.exe or baidu.exe that came from anywhere except those companies.
- Do not run cracked programs or bundles from sites that promise free versions of paid software.
- Do not change your passwords on the PC you suspect.
- Do not rely on a quiet scan or a quiet site test to say that you are safe.
Questions about bratarfood.com (AzaleaAgent, CoinMiner, encoded loader files)
What is bratarfood.com?
It is a web address that URLhaus, the malware tracking project run by abuse.ch, lists for 12 files in an open folder called /new/. They are eight .exe programs, one .bat script and three .txt loader files, all reported on 23 September 2026.
Some are tagged AzaleaAgent and CoinMiner. It is not a program on your PC and not a site anyone is meant to visit. We did not download the files, so what they contain is not confirmed by us.
Is bratarfood.com safe to open?
No. Do not request files from it, and do not run anything that does. Our own check was one plain request from our server, with no browser, and it returned a file listing with status 200.
That proves nothing: all 12 reported files are marked offline, but files can be moved or put back, and a quiet front page is common for this kind of server. The rating comes from the twelve URLhaus reports and their tags.
Is bratarfood.com a virus or malware?
The address itself is not a virus; it is a server. The files that were stored on it are the concern: URLhaus labels all 12 as malware_download, and tags four with AzaleaAgent, two with CoinMiner and three with rev-base64-loader.
We did not open them, so we cannot name the exact family of each file. Treat the server as hostile, and treat a PC that fetched its files as possibly infected.
What does rev-base64-loader mean on a .txt file?
It describes a text file that holds a program written as base64 and then reversed. On its own it does nothing: a script that is already running reads the text, reverses it, decodes it and starts the program inside.
Public analyses of XWorm chains describe the same trick. The text file looks harmless to a filter that checks only the file type. We did not open these three files.
What are AzaleaAgent and XWorm?
Azalea is a remote access trojan sold as malware as a service; reports list keylogging, hidden VNC, privilege escalation and Active Directory discovery. XWorm is another remote access tool, with keylogging, remote desktop and command execution.
AzaleaAgent is a tag in URLhaus on four files here, and one file name mentions XWorm, but no tag does. We cannot say which build the files hold, since we did not open them.
I saw bratarfood.com in my firewall or DNS log. Am I infected?
Not necessarily, and the name alone proves nothing. It does mean that a device on your network asked for it, and a person does not usually do that by hand. Find which device it was, disconnect it, and run the checks on this page:
- Task Manager
- Task Scheduler
- Startup apps
- Protection history
- a Microsoft Defender Offline scan
Do the account changes from another device, not from the PC in question.
How do I remove this malware from Windows?
Change your passwords from another device first. Then run a Microsoft Defender Offline scan (Windows Security, Virus and threat protection, Scan options), check Task Scheduler and the Startup apps for entries you did not make, and remove the ones you can tie to the malware.
If you are not sure, reset Windows with Remove everything and restore only documents. We followed Microsoft's pages and did not test these steps on an infected PC.
Does a coin miner steal my data?
Usually not; a miner uses your processor and power to earn cryptocurrency for someone else, so the sign is a slow, hot PC with high CPU use in Task Manager.
The worry is what else came with it. Here microsoft.exe is tagged AzaleaAgent and CoinMiner together. A PC with a miner had a stranger's program running, so check it as you would for a trojan.
Does bratarfood.com affect Mac, iPhone or Android?
We found nothing that says so. The files are .exe programs and a .bat script, which do not run on macOS, iOS or Android, and the vendor reports we read describe Windows threats.
On a Mac, iPhone or Android phone there is nothing to remove for this threat; if you typed a password on a suspicious page, change it and turn on two step sign in.
Will Fortect remove bratarfood.com?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For bratarfood.com, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Logpoint: XWorm RAT analysis, steal, persist, control (read October 17, 2026)
- Rubrik Zero Labs: Azalea RAT, from stealthy loader to full-system control (read October 17, 2026)
- Expert Insights: Windows AZALEA RAT loader slipped past 61 antivirus engines (reporting Point Wild) (read October 17, 2026)
- Microsoft Learn: Microsoft Defender Offline scan in Windows (updated 25 August 2026) (read October 17, 2026)
- Microsoft Support: Recovery options in Windows (Reset this PC) (read October 17, 2026)