
crystalbranchtw.blog: a .blog address that served Mirai files for routers and cameras, and what to do if a device of yours may be infected
crystalbranchtw.blog is a web address that URLhaus lists for 36 malware downloads, 34 of them tagged mirai, a botnet that takes over routers, cameras and recorders. All 36 were added within 23 seconds on 28 September 2026, and the name no longer resolves. If a device of yours contacted it, disconnect the device, restart it offline, set a new password and only then reconnect it.
Facts checked October 10, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like a file or script that a device or a shell command fetched from crystalbranchtw.blog usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove crystalbranchtw.blog (Mirai botnet files) yourself 5 steps, about 15 minutes, no software needed.
Start the steps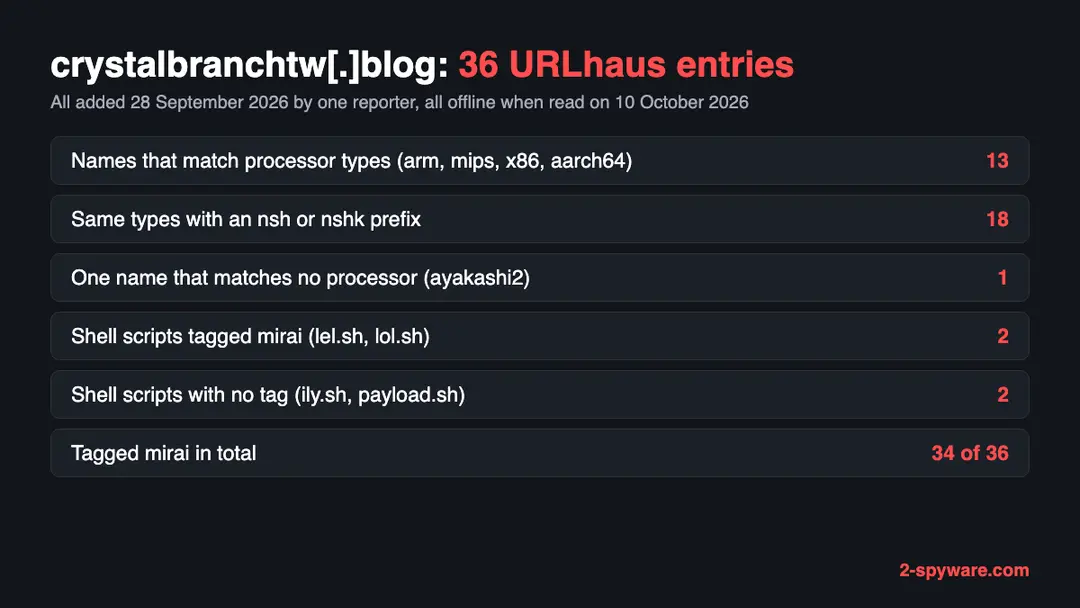
Crystalbranchtw.blog (Mirai botnet files): summary
| Type | A malware download host for network devices: URLhaus lists 36 files, 34 tagged mirai |
|---|---|
| Risk | High for a router, camera or recorder that contacted it: the device may be part of a botnet |
| Symptoms | Often none. A factory login, remote admin switched on, a slow or hot device or a provider notice are the signs |
| How to get rid of it | Disconnect the device, restart it offline, set a new password, update the firmware, turn off remote admin and UPnP, reset or replace it if in doubt |
| Our check (10 October 2026) | One lookup: the name did not resolve, no page. A dead site clears nothing; the danger rating comes from URLhaus |
| Running since / first seen | Registered 27 May 2026 (Namecheap); first malware URLs reported 28 September 2026 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Platform | Routers, cameras and other Linux-based devices, by the processor names and the mirai tag |
|---|---|
| Detection names | No Microsoft detection name is known for these files, because we did not open them and they are built for network devices, not Windows. The URLhaus tag is mirai. On a router the only check is the firmware and the steps on this page |
| Name | Crystalbranchtw.blog |
| Evidence | 36 write-ups by security sites; details still limited |
| First seen | 28 September 2026 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 10 October 2026 |
Facts checked on 10 October 2026 against our copy of the URLhaus data for crystalbranchtw.blog and two other hosts, one browser test of our own, the registration record, the CISA Mirai alert TA16-288A, a USENIX Security paper on Mirai, the FTC page on home Wi-Fi and the CISA page on network infrastructure devices.
We did not download the files and we infected no device; the removal steps follow CISA and were not tried on a live infection.
What crystalbranchtw.blog is, and how much we know
crystalbranchtw.blog is a domain name, not a program. The malware tracker URLhaus lists it as a place that served Mirai files. Mirai goes after small Linux devices such as home routers, IP cameras and video recorders, not after ordinary Windows or Mac computers. We found no public write-up of this domain, so the page rests on the URLhaus rows in our database, our own lookup, a registration record and what CISA and researchers say about Mirai.
- 1
What URLhaus lists
36 file addresses on this host, every one with the threat type malware_download, every one added on 28 September 2026 by a single reporter account named von. The first, /ily.sh, arrived at 18:41:15 UTC and the last rows, among them /arm and /nshkarm6, at 18:41:38 UTC. All 36 were offline when we read them.
- 2
What the tags say
34 rows carry the tag mirai. Two scripts, ily.sh and payload.sh, carry no tag. Thirteen file names look like processor types, for example arm7, mips, ppc and x86. Eighteen more repeat those types behind the prefix nsh or nshk. One name, ayakashi2, matches no processor, and two scripts are called lel.sh and lol.sh.
- 3
What we could not confirm
We downloaded nothing and found no analysis of these exact files. So we do not know which Mirai variant they are, which logins they try or where an infected device would report. The tags are the reporter's labels, not our finding.
- 4
What it means for you
If the name only showed up in a block list or a security scan, your device is not infected because of it. If a device of yours asked for this address or ran a file from it, treat that device as infected and follow the plan below.
- Kind of threat
- A malware download host: 36 files, 34 tagged mirai, 2 untagged shell scripts
- Malware family
- Mirai, an IoT botnet (the reporter's tag; not confirmed by us)
- Registration
- Registered 27 May 2026 through Namecheap, expires 27 May 2027, record last changed 29 September 2026, the day after the reports. The owner is not shown
- URLhaus entries
- 36 file addresses, all added on 28 September 2026; all 36 offline when we read them
- Platform
- Routers, cameras and other Linux-based network devices. Not an ordinary PC threat
What crystalbranchtw.blog (Mirai botnet files) does on an infected PC
What our check on 10 October 2026 showed, and what it cannot show
We opened https://crystalbranchtw.blog/ once, from Lithuania, in an automated Chromium browser set to English. The browser reported that the name could not be found, so no page loaded. That is not a clean result. It clears nothing.
Our site test, 10 October 2026
- The name did not resolveOur browser reported ERR_NAME_NOT_RESOLVED, so there was no address to connect to. URLhaus shows all 36 files offline, which fits a name that was suspended or removed.
- Why a dead name proves littleA registrar can disable a name, an owner can drop it, or the operator can move the files to a new name. A device that already holds the old address may keep asking for it.
- Notification request, pop-ups, redirects, ad networksNone seen, because no page loaded on this one visit. A host of this kind serves files to devices, not pages to people.
- URLhaus listing36 malware addresses, 34 tagged mirai, added within 23 seconds on 28 September 2026.
- Registration dataThe record shows Namecheap as registrar, a creation date of 27 May 2026 and a last change on 29 September 2026. It does not show who owns the name, and we cannot say why it changed.
Dangerous: treat it as a botnet download host Our test was a single failed lookup and proves nothing either way. The rating rests on the URLhaus reports. A dead address does not heal a device that already ran something it served.
From registration to our test: the dates we have
The history is thin. We have a registration date, one burst of reports lasting 23 seconds, a record change the next day and our failed lookup. We have nothing between May and September.
27 May 2026
The domain is registered
The registration record gives this creation date, with Namecheap as the registrar and a one-year term ending 27 May 2027. We do not know who registered it or what it was used for in the following four months.
28 September 2026, 18:41 UTC
36 files are reported in 23 seconds
URLhaus receives ily.sh at 18:41:15 and then a fast run of files named after processor types, the nsh and nshk copies, the scripts lel.sh, lol.sh and payload.sh, and ayakashi2. The last arrives at 18:41:38. Every row is tagged mirai except ily.sh and payload.sh.
The URLhaus entries for crystalbranchtw.blog, summarised from our copy of the feed on 10 October 2026. 29 September 2026
The registration record changes
The record shows a last change on this date, one day after the reports. The record does not say what changed. It may be a routine update or an action by the registrar, and we found no source that tells which.
10 October 2026
Our lookup finds no address
Our browser visit to https://crystalbranchtw.blog/ ends in ERR_NAME_NOT_RESOLVED. URLhaus lists all 36 files as offline, twelve days after the reports.
We could not read the URLhaus pages themselves because they ask for a browser check. The entries above come from the same feed as held in our own database.
The same file names on two other addresses
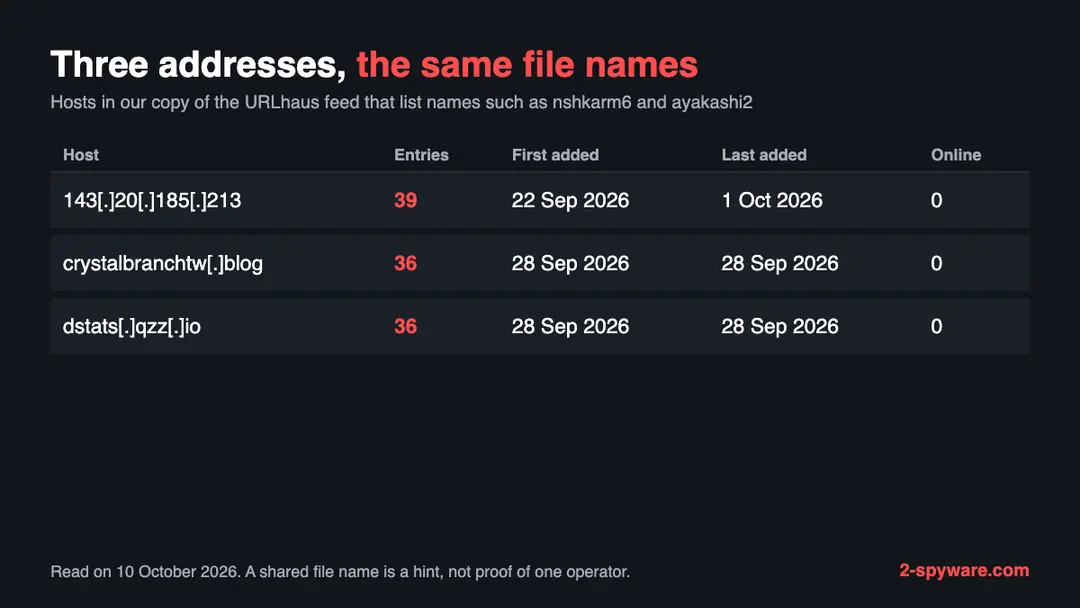
We searched our copy of the URLhaus feed for two of the odd file names, nshkarm6 and ayakashi2. Three hosts list them, and this domain is one of the three.
| Host | Entries and dates | What we can say |
|---|---|---|
| crystalbranchtw.blog | 36 entries, 28 September 2026, 18:41:15 to 18:41:38 UTC, reporter von | The subject of this page. All offline on 10 October 2026 |
| dstats.qzz.io | 36 entries, 28 September 2026, from 18:41:20 UTC, reporter von | Same file names, same day, same reporter. We cover it in our guide /remove-dstats-qzz-io.html. All offline |
| 143.20.185.213 | 39 entries, 22 September to 1 October 2026, four reporters including von | A bare IP address that lists the same names, six days earlier at first. All offline |
A shared file name is a hint and not proof. Different people can copy a public Mirai kit and keep its names. Still, the same set on the same day, within seconds of each other and filed by the same reporter, points to one batch of files placed on several addresses at once. That helps you in one way: blocking a single name does not stop the files, and a device that tries one of these hosts may try the others.
Reading the file names: what each group may be
File names are weak evidence. We separate what URLhaus states from what we guess, and we mark each guess.
| Group of files | What URLhaus says | What it may be (our reading) |
|---|---|---|
| arm, arm5, arm6, arm7, armv5, armv7, aarch64 | Offline, tagged mirai, added 28 September 2026 | Builds for several generations of ARM chip, the kind inside many routers, cameras and recorders. Not confirmed |
| mips, mpsl, ppc, sh4, x86, x64s | Offline, tagged mirai | Builds for other chips: MIPS in two byte orders, PowerPC, SuperH, and 32 and 64 bit x86. Not confirmed |
| nsharm, nshkarm7, nshkmips and 15 more with the same prefixes | Offline, tagged mirai | A second full set under another prefix, possibly a newer build or a variant. We found no source that explains nsh or nshk |
| lel.sh and lol.sh | Offline, tagged mirai | Shell scripts that usually try each download in turn until one fits the device. Not confirmed |
| ily.sh and payload.sh | Offline, no tag | Scripts without a label, maybe a first stage or a helper. Not confirmed |
| ayakashi2 | Offline, tagged mirai | A name that matches no processor, perhaps a nickname for a variant. We could not confirm |
The count of builds tells you more than any single name. An operator who prepares thirty-odd files for many chip types does not know in advance which device a victim runs. This matches CISA's description of Mirai's wide range of targets, though it does not prove how these particular files were used.
How Mirai takes over a device, as CISA and researchers describe it
We did not run or open any of the files. This is the general Mirai method from CISA and a university study, so you know what to look for on your own devices.
- 1
A scan finds the device
CISA says Mirai keeps scanning the internet for vulnerable IoT devices. A device with a public address and an open login gets found whether or not anyone knows it is there.
- 2
A short list of factory logins
According to CISA, Mirai tries a list of 62 common default usernames and passwords. That small list reached a huge number of devices because many owners never changed the login printed on the label.
- 3
The usual victims
CISA names home routers, network-enabled cameras and digital video recorders. It also describes a later variant that used a flaw in broadband routers that leave port 7547 open.
- 4
The scale
A USENIX Security paper followed the botnet for seven months and found a peak near 600,000 infections, mostly embedded devices. The authors blame the simplicity of the infection for its growth.
An infected device carries on with its normal job, so owners rarely notice. In the background it looks for more devices and takes part in attacks on other targets. That is why a download host like this one matters even to people who never visited it.
What crystalbranchtw.blog (Mirai botnet files) can steal or download
What you might see, and why you probably will not
Most owners see nothing. The signs below follow from how Mirai works. None of them proves infection alone.
| Sign | What it means |
|---|---|
| The router or camera still accepts its factory login | This is exactly what Mirai relies on. Treat the device as exposed even if it behaves normally |
| Telnet or remote administration is open to the internet | CISA tells people to watch Telnet traffic on ports 23 and 2323, where Mirai tries its logins |
| Slow internet, a hot device or a camera that lags | A device that scans and attacks uses bandwidth and processor time. Many other causes exist, so this is weak evidence |
| A notice from your internet provider | A provider may write when a device on your line scans or attacks others. Read the date and the device it names |
| Nothing at all | The malware lives in the device's memory, and the device keeps working |
What an infected device can cost you
Seeing this name in a log costs nothing. The risks below apply to a device that really connected to it or ran one of its files.
- High
Your connection is used to attack others
An infected router or camera joins a botnet that can flood other targets with traffic. The harm lands on strangers, but the traffic leaves from your line.
- High
A foothold in your home network
A router sits between your devices and the internet. Control of it could let someone watch or redirect traffic. We found no source describing this for these files, so it is a risk and not an observation.
- Medium
Infection again within minutes
CISA warns that a device reconnected before its password is changed can be reinfected quickly, because the scanners never stop.
- Medium
A warning or a limit from your provider
Providers may warn or restrict a customer whose device takes part in attacks. This is general practice, not something we saw here.
- Low
Nothing, if you only saw the name
A name in a firewall log or a blocked link is not an infection.
How to check the PC for crystalbranchtw.blog (Mirai botnet files)
How a device comes to contact an address like this
No source tells us how any device reached crystalbranchtw.blog. These are the routes CISA and the research describe for Mirai.
- 1
A scanner found the device
A bot probed the internet, met an open login and tried the default passwords. Nobody clicked anything. CISA describes this as the main route.
- 2
An unpatched flaw
CISA notes a variant that abused routers with port 7547 open. An old router without updates stays open to flaws of this kind.
- 3
A command after break-in
Once logged in, the attacker has the device fetch the file that fits its chip. A script such as ily.sh or payload.sh could do the fetching, but we never saw the scripts.
- 4
A line in a log
If you only found crystalbranchtw.blog in a router or DNS log, some device on your network asked for the name. Find out which one, because that device is the suspect.
Check the router and the cameras first, before you reset anything
The question that matters is whether a device of yours reached this address, or still uses its factory login with remote access on. If either is true, follow the plan on this page. The checks below change nothing.
Phones and ordinary computers are not the target of these files, so this page gives no steps for them.
- 1
Find the device that asked for the name
Open your router's admin page (the address and login are on the label or in the manual) and look at its log or its list of connected devices. Search for crystalbranchtw. If the router keeps no log, a DNS filtering service you use may show who asked.
- 2
Test the factory login
If the admin page still lets you in with the login printed on the label, or the default for your model, a bot could have done the same.
- 3
Look at remote access
Find remote management or remote administration in the router settings and see whether it is on for the internet. The FTC advises turning it off, along with WPS and UPnP.
- 4
Compare the firmware
Read the firmware version on the status or system page and compare it with the maker's site. An old version, or a model the maker no longer updates, is a reason to plan a replacement.
- 5
Read any provider notice
If your provider wrote about attack traffic from your line, the notice usually has a date and an address. Match them to the device list.
- 6
Know what a clean check means
These checks cannot look inside the device. The malware sits in memory, so a device that looks normal may still be infected until it is restarted offline.
How to remove crystalbranchtw.blog (Mirai botnet files)
How to remove crystalbranchtw.blog
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to crystalbranchtw.blog or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever crystalbranchtw.blog installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Clean a router, camera or recorder: CISA's order, step by step
CISA's removal advice is short because Mirai lives in the device's memory. We follow it and add the settings that the FTC and CISA recommend for afterwards. We did not test these steps on an infected device.
- 1
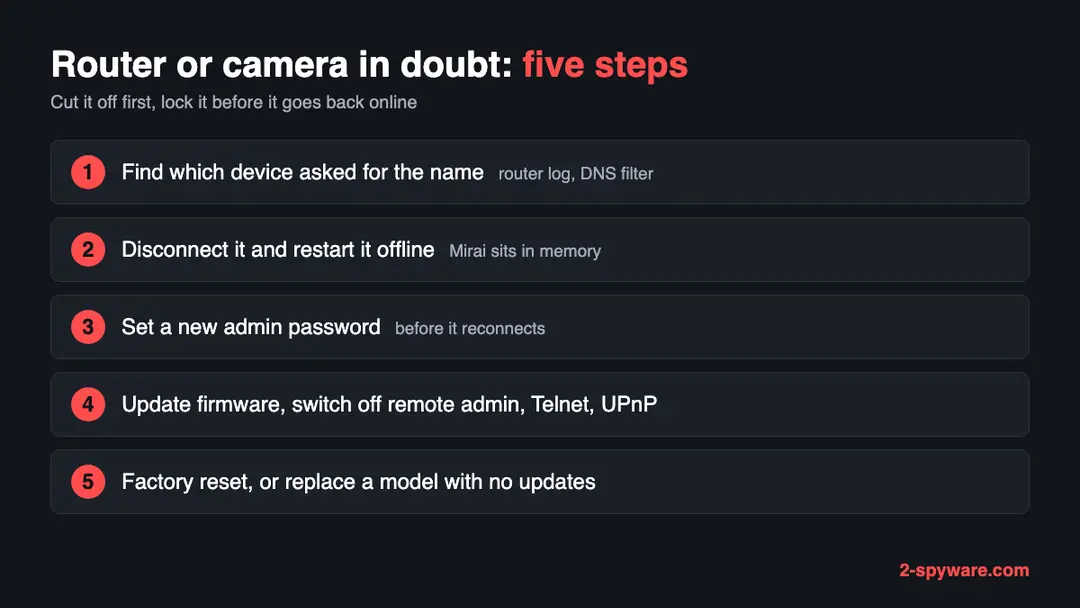
Take it off the network
Pull the network cable and switch off its Wi-Fi if it has any. If it is your only router, do the next steps from a phone on mobile data and expect your home internet to stay down for a while.
- 2
Restart it offline
Power it off and on with no network attached. CISA says the malware resides in dynamic memory, so a restart removes it. A restart does not stop it coming back.
- 3
Set a new password before it goes online
Sign in on the local address and choose a strong admin password that you use nowhere else. CISA warns that a device reconnected first could be reinfected quickly.
- 4
Install the newest firmware
Take it from the maker's own site. The FTC says to check that site before setup and now and then, to register the router for update notices and to ask your provider about automatic updates.
- 5
Close what a bot uses
Turn off remote management and UPnP. CISA lists disabling UPnP on routers unless it is needed, and turning off unencrypted remote administration such as Telnet. Make sure the built-in firewall is on.
- 6
Reset to factory settings if you cannot be sure
The CISA and FTC pages we read give no reset procedure, so use the manual for your model. Most devices have a small reset button held for some seconds. After a reset set the password first, then update the firmware, and only then reconnect.
- 7
Replace a model that gets no more updates
If the maker has stopped issuing fixes, a new password does not close the flaws. Buy a replacement from a maker with a record of security updates, as CISA advises.
If you use a Windows PC, a Mac or a phone
The files are built for the small processors in network devices. We found nothing that says they run on an ordinary computer or phone.
| Your device | What we know | What to do |
|---|---|---|
| Windows PC or Mac | The names match router and camera chips, and nothing says a PC was a target | No removal is needed because of this address. Check the router your computer uses, as above |
| iPhone, iPad or Android phone | No source mentions phones | Nothing to remove. A phone that could not load a page from this host is normal, since the name no longer resolves |
| A Linux server or a NAS | These run Linux and may share processor types with the list. We found no source about them for this host | If one of yours contacted this address, treat it as compromised and ask its maker or administrator how to rebuild it |
After removal: passwords, accounts and prevention
Mirai depends on devices that people set up once and forgot. These measures come from CISA and the FTC.
Do
- Change every default password on a router, camera or recorder on the day you install it.
- Install security updates when they appear, and register the device for notices.
- Switch off remote management, WPS and UPnP on the router unless you need them.
- Use WPA3 Personal on Wi-Fi, or WPA2 Personal if WPA3 is not offered.
- Pick devices from makers with a record of security fixes, and replace ones that no longer get them.
Don't
- Never leave a camera or recorder reachable from the internet with its factory login.
- Never leave Telnet on for remote login. CISA lists it as an unencrypted protocol to turn off.
- Never reconnect a cleaned device before the new password is set.
- Never assume a restart fixed things for good. Without a new password the device can be infected again.
- Never ignore a provider notice about attack traffic from your line.
Questions about crystalbranchtw.blog (Mirai botnet files)
What is crystalbranchtw.blog?
crystalbranchtw.blog is a domain name that URLhaus, the malware tracker run by abuse.ch, lists for malware downloads. Thirty-six file addresses were added on 28 September 2026 within 23 seconds, and 34 carry the tag mirai.
Its record shows registration on 27 May 2026 through Namecheap. When we looked it up on 10 October 2026 the name did not resolve, and every file was offline. We found no public write-up of it.
Is crystalbranchtw.blog a virus?
A domain name is not a virus, but this one is listed as a source of Mirai malware. The files are aimed at routers, cameras and similar devices, not at an ordinary computer.
We did not download them, so we cannot say exactly what they do. Treat the address as dangerous and do not try to fetch its files. Reading this page cannot harm you.
What is Mirai?
Mirai is malware that turns network devices into a botnet. CISA says it keeps scanning the internet for vulnerable devices and logs in with a short list of 62 common default usernames and passwords.
The devices named are primarily home routers, network-enabled cameras and digital video recorders. A USENIX Security study found the botnet peaked at about 600,000 infections.
Is it connected to dstats.qzz.io?
The URLhaus rows suggest so, but we cannot prove it. Both hosts list the same set of 36 file names, filed on 28 September 2026 by the same reporter within seconds of each other.
A third address, an IP, lists similar names from 22 September. A shared kit can be copied by different people, so treat it as a hint that one batch of files was placed in several places.
How do I know if my router is infected?
Often you cannot tell. The device keeps working, and Mirai lives in its memory.
Warning signs are a factory login that still works, remote administration open to the internet, a slow or hot device, or a notice from your provider about attack traffic. If you suspect it, follow CISA's order:
- disconnect
- restart offline
- set a new password
- only then reconnect
How do I remove Mirai from a router or camera?
Disconnect the device and restart it while it is offline, because CISA says the malware resides in dynamic memory. Change the default password to a strong one before you reconnect, since a device reconnected first could be quickly reinfected.
Then update the firmware, turn off remote management and UPnP, and reset to factory settings using the manual if you are unsure. Replace a model that gets no updates.
Will restarting my router be enough?
A restart removes Mirai itself, but it does not close the way the malware got in. If the factory password and open remote access are still there, a scanner can log in again, sometimes within minutes. Restart offline, set a new password before the device goes back online, and update the firmware so the same flaw is not left open.
Why does the site not load any more?
On 10 October 2026 our browser reported ERR_NAME_NOT_RESOLVED, so the name gave no address, and URLhaus showed all 36 files offline.
The registration record was last changed on 29 September 2026, the day after the reports, but it does not say why. A name may be suspended, dropped or moved. None of that cleans a device that already ran a file from here.
Does this affect my Windows PC, Mac or phone?
Almost certainly not directly. The file names match the processors in routers, cameras and similar devices, and Mirai is described as a threat to such IoT devices.
We found nothing that says these files run on a PC or a phone. The risk to you is the router and other network devices at home. Check those; your computers need no cleaning because of this address.
Will Fortect remove crystalbranchtw.blog?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For crystalbranchtw.blog, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- URLhaus (abuse.ch): host page for crystalbranchtw.blog (entries read from our copy of the feed) (read October 10, 2026)
- CISA: Heightened DDoS Threat Posed by Mirai and Other Botnets (TA16-288A) (read October 10, 2026)
- USENIX Security 2017: Understanding the Mirai Botnet (read October 10, 2026)
- FTC Consumer Advice: How to Secure Your Home Wi-Fi Network (read October 10, 2026)
- CISA: Securing Network Infrastructure Devices (read October 10, 2026)