
delta-canvas.com: a Mac malware download site and what to do if you opened its files
delta-canvas.com is a website that URLhaus lists for five Mac malware downloads (three zip files and two Mach-O programs), and it answered our plain request with a Cloudflare 520 error. If you opened a file from it or pasted a command it showed you into Terminal, treat the Mac as compromised:
- change your passwords from another device
- move any crypto
- then back up documents
- erase the Mac
Facts checked October 17, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
Programs like a download or a pasted command from delta-canvas.com usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove delta-canvas.com (Mac malware downloads) yourself 7 steps, about 21 minutes, no software needed.
Start the steps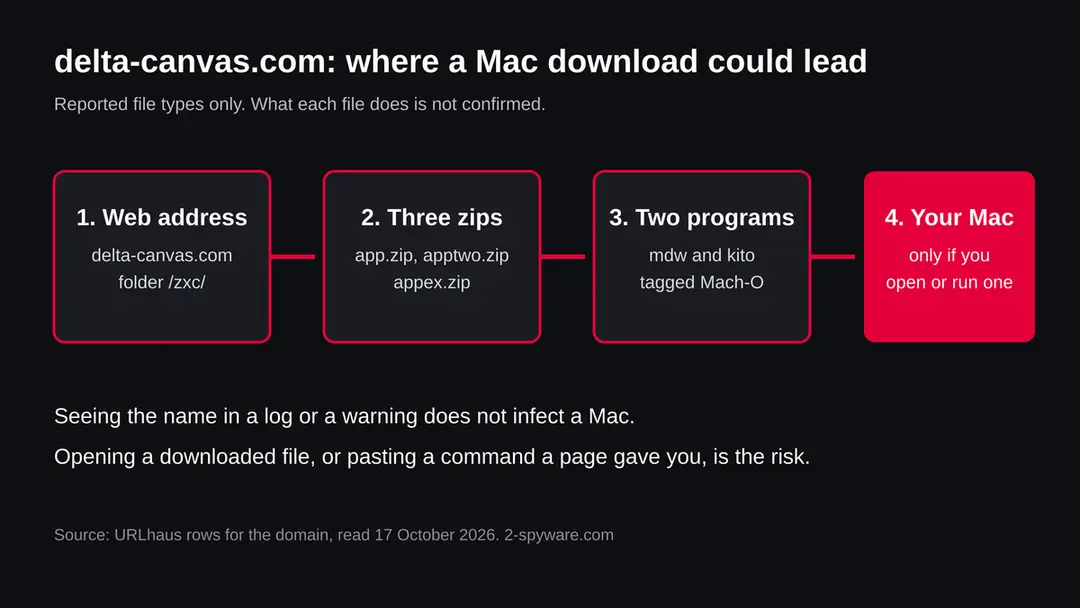
Delta-canvas.com (Mac malware downloads): summary
| Type | A malware download site for Macs: URLhaus lists five files (three zip, two Mach-O), no family named |
|---|---|
| Risk | High if you opened its files or pasted its command: passwords, cookies, wallets and files may be at risk, depending on what the files do (not confirmed) |
| Symptoms | Often none. A fake password box, Terminal asking for access and hidden folders are the signs in reports on similar Mac malware |
| How to get rid of it | Change passwords from another device, move crypto, revoke sessions and keys, then back up documents and erase the Mac |
| Our check (17 October 2026) | One plain request from our server: Cloudflare error 520, no page. A quiet or broken site clears nothing; the danger rating comes from URLhaus |
| Running since / first seen | Domain registered 22 September 2026; five malware URLs reported 23 September 2026 |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Platform | macOS, by the tags; no source says Windows or phones are affected |
|---|---|
| Detection names | No Microsoft detection name is known (a Mac threat) and we found no antivirus name for these five files |
| Name | Delta-canvas.com |
| Domain registered | 22 September 2026 |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 23 September 2026 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 17 October 2026 |
Facts checked on 17 October 2026 against the URLhaus rows and RDAP data for delta-canvas.com held by our server, one plain request from our server, and published pages by Kaspersky, Palo Alto Networks Unit 42, Sophos and Apple. We did not download the files and we infected no Mac; the removal steps follow Apple's pages and the vendors' advice and were not tried on a live infection.
What delta-canvas.com is, and what we know about it
delta-canvas.com is not a program on your Mac. It is a web address that the abuse.ch project URLhaus lists as a place where Mac malware was served. We found no public write-up of this one site, so this page rests on what the URLhaus rows show, what the domain registration shows, one plain request from our server, and what security vendors have published about the kind of Mac malware that is spread this way.
- 1
What URLhaus lists
Five file addresses on delta-canvas.com, all in a folder called zxc and all added on 23 September 2026 at 07:22 UTC by one reporter. Three are zip archives: app.zip, apptwo.zip and appex.zip. Two have no file ending, mdw and kito, and carry the tag macho. Every row also carries the tag macOS. The threat type on every row is malware_download. When we read the rows, app.zip was marked online and the other four offline.
- 2
What the tags mean
macOS says the files are meant for a Mac. zip says the file is an archive that you open by double clicking. macho says the file is a Mach-O program, the native executable format of macOS and iOS. None of the rows carries a malware family name, so we cannot tell you whether this is a password stealer, a loader, a backdoor or something else.
- 3
What we could not confirm
We did not download any of the five files and we did not see the page that leads people to them. So we do not know what lure the site uses, what is inside the zip files, what mdw and kito do, or whether a ClickFix style command is involved. Anything said below about malware families is background from vendors, not a finding about these files.
- 4
What this means for you
If you only saw the name in a log, a link or a warning, you are not infected by that alone. The risk is for people who downloaded a file from the site and opened it, ran a program from it, or pasted a command it showed them into Terminal on a Mac.
- Kind of threat
- A malware download site for macOS: five reported file addresses, family not named
- Files reported
- app.zip, apptwo.zip, appex.zip (zip archives), mdw and kito (Mach-O programs), all under /zxc/
- Domain registered
- 22 September 2026 at 13:58 UTC, registrar Eranet International Limited, status client transfer prohibited (RDAP, read 17 October 2026)
- URLhaus entries
- 5 file addresses, all added 23 September 2026 at 07:22 UTC; 1 online (app.zip) and 4 offline when we read them
- Hosted behind
- Cloudflare: our request was answered by a Cloudflare server, so the real server is not visible to us
- Platform
- macOS, by the tags. Whether Windows, iPhone or Android are hit is not stated by any source we read
What delta-canvas.com (Mac malware downloads) does on an infected Mac
What we checked on 17 October 2026, and what we could not
Our check was one plain request from our server: no browser, no clicks, no scrolling. The site answered with a Cloudflare 520 error. That tells you nothing good about the site, and it clears nothing.
Our plain request, 17 October 2026
- The site did not give a pageStatus 520, server header cloudflare, no title and no redirect. Cloudflare describes a 520 as an unknown problem between Cloudflare and the origin web server. The server behind it did not give a normal answer to our request.
- Why that is not a clean resultA 520 can mean the operators took the server down, that it refuses requests like ours, or that it was briefly broken. One request cannot tell which. Sites that hand out malware often show different things by country, device, browser or visit.
- Notification request, pop-ups, redirects, ad networksNone seen on this one request. There was nothing to see: the request returned only an error, and our request ran no page code, so it could not have shown a pop-up anyway.
- URLhaus listingFive malware URLs on this domain, tagged macOS, zip and macho, all reported on 23 September 2026. app.zip was the one marked online.
- Downloads and the page itselfWe did not download the files and we did not reach any page that leads to them. We cannot tell you what the page says or what the files do.
Dangerous: treat it as a malware site The test was a single plain request that ended in an error, so it proves nothing either way. The danger rating comes from the five URLhaus reports and the age of the domain, not from our request. Do not open the site, and do not run anything it gives you.
What happened to delta-canvas.com, from registration to our check
The history is short because the domain is under a month old at the first report. The dates come from RDAP, from the URLhaus rows and from our own request.
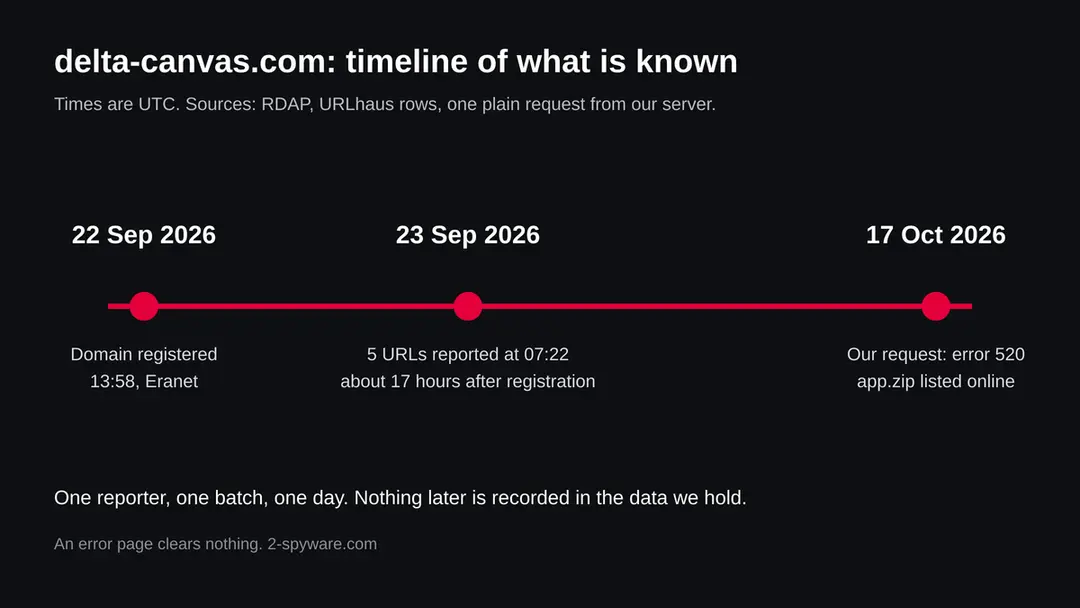
22 September 2026
The domain is registered
RDAP shows delta-canvas.com registered on 22 September 2026 at 13:58 UTC through the registrar Eranet International Limited. The only status is client transfer prohibited, which is a lock against moving the domain to another registrar and says nothing about its use.
23 September 2026
Five malware URLs are reported
At 07:22 UTC a reporter using the handle c4ffeine adds app.zip, apptwo.zip, appex.zip, mdw and kito, all under /zxc/, with the tags macOS, zip or macho. That is about 17 hours after the domain was registered, which suggests it was set up for this purpose, though no source states the intent.
17 October 2026
Our request gets a 520
Our server asks for the site and receives a Cloudflare 520 error. At the time of our reading, the URLhaus data we hold still lists app.zip as online. We hold no record of any later report for the domain.
The same folder and file names appear on another domain
The folder zxc and the file names app.zip, apptwo.zip and appex.zip are not unique to this site. The same set of names appears in URLhaus reports for loop-lumen.com, another domain we have a guide for, where the reporter's tags named the Atomic macOS Stealer (AMOS) and ClickFix.
That is a reason to read the AMOS background below, and it is not proof. The delta-canvas.com rows carry no family tag, the two sites have different registrars and registration dates, and we do not know whether the same people run both.
Our reading is that the pattern looks like a reused kit, and we label it as our reading, not as a finding. Do not assume that the files on delta-canvas.com are AMOS.
How a paste-a-command trick works on a Mac
We did not see delta-canvas.com's page, so we do not know if it uses this trick. Kaspersky and Unit 42 describe it as a common way Mac stealers reach people, which is why it is explained here.
- 1
You land on a page with a check or a guide
Kaspersky describes a fake CAPTCHA or verification step on a hacked or fake website. Unit 42 describes a page advertising a macOS toolkit with quick setup instructions. Both end with a command to copy.
- 2
You are told to open Terminal and paste
Because you run the command yourself, Kaspersky notes that macOS security warnings are often dismissed as part of the instructions. Its test command raised no warning at all on macOS Tahoe 26.5.2.
- 3
The command fetches the real malware
In Kaspersky's example the command downloads a disk image into the /tmp folder under a random name, mounts it without showing it in Finder or on the desktop, finds the app inside and launches it. In Unit 42's example the command fetched a Zsh script, which unpacked a second script, which downloaded a Mach-O installer saved as /tmp/helper.
- 4
A password box appears
Kaspersky and Sophos both describe a fake macOS system window asking for your password. Sophos says the malware keeps asking until a correct password is entered, then uses it for actions that need administrator rights.
- 5
Nothing seems to happen
That is the aim. Unit 42 saw Terminal ask for access to Finder, the Desktop, Documents and Notes during its test infection, and then the data left the Mac in the background.
Unit 42 says its toolkit example is not technically ClickFix, because it does not pose as a check, though the copy and paste step is the same. For the reader the rule is the same too: no website needs you to paste anything into Terminal.
Background: what a Mac stealer such as AMOS is
The table is background on the best documented Mac stealer that is spread by zip files and pasted commands. It describes AMOS, the Atomic macOS Stealer, in general. It is not a statement about the delta-canvas.com files.
| Question | What the sources say | Source |
|---|---|---|
| What is it? | An information stealer for macOS sold as malware as a service, so the people who use it are not the people who write it | Sophos |
| How common is it? | Sophos says it made up almost 40% of its macOS protection updates in 2025, more than twice any other macOS family, and nearly half of its macOS stealer customer reports over three months | Sophos |
| How old is it? | Tracked publicly since at least April 2023 | Sophos |
| How does it arrive? | Pasted Terminal commands, fake installers, cracked app lures, poisoned search results (including ones tied to AI chat answers), and malicious ads | Sophos; Unit 42 |
| Does it change? | Yes. Unit 42 stresses that indicators change frequently and that its domains and addresses differed between two infections a few days apart | Unit 42 |
| Does it check where it runs? | Sophos says it checks for virtual machines and sandboxes before running, which is one reason an automated visit can see nothing | Sophos |
| Is this site's file AMOS? | Not known. The URLhaus rows for delta-canvas.com give no family name | URLhaus rows in our data |
What delta-canvas.com (Mac malware downloads) can steal or download
What a Mac stealer of this kind takes
If the files turn out to be a stealer, this is the range of what such malware collects in one sweep. Each item is named by at least one source about AMOS; no single source lists all of them, and nothing here is confirmed for the delta-canvas.com files.
Reported as taken by AMOS
- Browser passwords
- Browser cookies and session tokens
- Autofill data
- Saved bank cards
- Apple Keychain
- Your Mac login password
- Safari cookies
- Apple Notes
- Crypto wallet apps
- Crypto browser extensions
- Telegram data
- Discord data
- PDF, TXT and RTF files
- Cloud and developer config (aws, docker, gcloud, FileZilla)
- Shell history (zsh_history)
| Data | Detail | Source |
|---|---|---|
| Browsers | Cookies, saved logins and passwords, autofill, saved cards and profile data from Chromium browsers such as Chrome, Edge, Brave and Opera, and from Firefox based browsers such as Tor Browser and Waterfox | Kaspersky |
| Crypto | Desktop wallets such as Exodus, Electrum and Atomic Wallet, and data from more than 200 wallet related browser extensions | Kaspersky |
| Hardware wallet apps | Replaces the Ledger Wallet and Trezor Suite apps with malicious fakes. The recovery phrase typed into the fake is the target | Kaspersky; Sophos |
| Apple data | Safari cookies, Apple Notes and passwords from the Keychain | Kaspersky; Sophos |
| Developer files | In Unit 42's test: folders for aws, docker, FileZilla and gcloud, Binance and TonKeeper folders and the zsh history, staged in /tmp and packed into out.zip | Unit 42 |
| How it leaves | Packed into one archive and sent by HTTP POST to the attackers' server, with URL endings such as credentials, browsers and wallets | Unit 42; Sophos |
What this can cost you
Reading the site or seeing its name costs nothing. The risks below apply to a Mac where a file from the site was opened or a command from it was pasted, and they are the risks of the malware type described above, not proven for these files.
- High
Account takeover
Cookies and session tokens let someone use your logged in email, social and work accounts without your password, so a stolen session can outlive a password change until you sign out everywhere.
- High
Crypto theft
Wallet files and recovery phrases are a main prize of Mac stealers. A blockchain transfer cannot be reversed, so speed and order matter more here than anywhere else.
- High
Your Mac password in the attackers' hands
Both Kaspersky and Sophos describe a fake password prompt. With your password an attacker can read the Keychain and approve actions on that Mac, so changing it matters as much as changing the web passwords.
- Medium
Keys and tokens from your work
Unit 42 saw cloud, container and file transfer config folders taken. If you are a developer, keys and API tokens on the Mac are exposed.
- Medium
A hidden program that starts again
Sophos describes a LaunchDaemon and a hidden helper in the user folder. Until such leftovers are gone, the Mac can keep talking to the attackers.
- Low
Nothing, if you only saw the name
A name in a warning, a firewall log or a blocked link is not an infection.
What you may notice, and what you may not
Most victims of Mac stealers notice nothing. The signs below come from the vendor reports on AMOS, and the first three happen during the infection, not after it.
| Sign | What the reports show |
|---|---|
| A password box you did not expect | A fake macOS system window asking for your login password, repeated until the right one is entered (Kaspersky, Sophos) |
| Terminal asks for permissions | Unit 42 saw Terminal request control of Finder and access to Desktop, Documents and Notes during the infection |
| A downloaded app that does nothing | A zip or program that opens and shows no window, or a Terminal window that closes at once. This is our reading of how a quiet loader behaves, not a quote |
| Hidden folders and files | Names that start with a dot, such as .com.apple.accountsd and .com.apple.metadata.mds in Application Support (Unit 42), or a hidden helper in your home folder with a plist named com.finder.helper.plist (Sophos) |
| Accounts you did not touch | Logins from new places, password reset emails and messages sent from your accounts. This follows from stolen sessions; it is our reading |
| Missing crypto | Balances that fall after the infection |
| Nothing at all | Stealers are built to finish quickly and stay quiet |
How to check the Mac for delta-canvas.com (Mac malware downloads)
How people end up on a page like this
We do not know how visitors reach delta-canvas.com, and no source says. The routes below are the ones the sources name for Mac stealers in general.
- 1
A fake human check on a site you wanted
A hacked or fake page shows a CAPTCHA style check and sends you on. Kaspersky describes this form.
- 2
A malicious ad or a poisoned search result
Unit 42 says AMOS has been spread through malicious ads, and Sophos names poisoned search results, including ones tied to AI chat answers, and AI themed lures.
- 3
A cracked or free copy of Mac software
Sophos and Unit 42 both name cracked app and fake installer lures. A site that offers a paid Mac app for free is a typical place for a zip like app.zip.
- 4
A download you started
Three of the five reported files are zip archives. Opening a downloaded zip that claims to be an app, or running a bare program such as mdw or kito, is another way in.
Check your Mac before you delete anything
Start with the question that matters: did you open a file from delta-canvas.com, or paste a command from a page on it? If yes, stop here and follow the numbered plan on this page, because a clean looking check does not clear a Mac. If you are not sure, do the checks below first. None of them deletes anything.
While you check, stop using the Mac for banking, email, work or crypto, and take it off the network if you can, so that anything running cannot send more data out.
- 1
Think back to what you opened
Look in your Downloads folder in Finder for app.zip, apptwo.zip, appex.zip, mdw or kito, or for an app that appeared after a visit to a page you do not trust. Do not open or run them again. Note the date you downloaded them.
- 2
Look at Login Items and background items
Open Apple menu > System Settings > General > Login Items & Extensions. Apple says this list holds items that open at login and apps allowed to run in the background. Look for names you did not install, including names that copy Apple's, such as accountsd, mdworker or softwareupdate. To remove an entry, select it and click the Remove button below the list.
- 3
Look for the hidden folders other reports found
In Finder choose Go > Go to Folder and type
/Library/Application Support/. Unit 42 found hidden folders named .com.apple.accountsd and .com.apple.metadata.mds there, which copy Apple's names. Sophos lists a plist named com.finder.helper.plist in /Library/LaunchDaemons/. These names come from other samples, so a match is a strong sign and no match clears nothing. - 4
Look in the home folder and in /tmp
In Terminal,
ls -la ~lists hidden files in your home folder and only lists them. Sophos describes a hidden helper binary there. Unit 42 saw installers and staging files in /tmp, such as helper, starter and out.zip, but /tmp is cleared by macOS, so an empty folder proves nothing. - 5
Check your accounts
Look at the sign-in activity of your email, your Apple Account, banks and exchanges for places and devices you do not know. Look at your crypto balances. This is quicker than any file check, and it is done from another device.
- 6
A scan helps, but it does not clear the Mac
A scan with a Mac security product can find known files. Treat a clean result as one data point, the way you treat a clean site test. We found no vendor removal procedure for these five files and we infected no Mac, so the order of the plan is our judgement from the vendor reports and Apple's pages, not a tested result.
How to remove delta-canvas.com (Mac malware downloads)
How to remove delta-canvas.com from a Mac
Start with the passwords and crypto, from another device: a stealer copies them in seconds.
Then clean the Mac, or erase it.
Step 1: Change passwords from another device first
If you pasted a command into Terminal or opened a downloaded file from delta-canvas.com, assume the passwords saved in the browsers and in Keychain on this Mac are known to the attacker.
From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and work accounts, and sign out of all other sessions on each one.
Move any cryptocurrency to a new wallet created on a clean device, because a seed phrase that was stored on this Mac is compromised. Do this before cleaning the Mac: cleaning does not undo the theft.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Step 3: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 4: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from delta-canvas.com or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 5: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 6: If it was an infostealer, erase and reinstall macOS
Stealers copy data and often leave persistence you cannot be sure you found.
The only complete fix is to back up your personal files only (documents, photos, not apps or settings), then open System Settings > General > Transfer or Reset > Erase All Content and Settings, or use macOS Recovery to erase the disk and reinstall macOS, as Apple describes in its support articles.
Restore only your files afterwards, and install apps again from their official sources.
Step 7: Report it and watch your accounts
Report the site and the command to the authorities in your country, and tell your bank if any card was saved in a browser or in Keychain.
Over the next weeks watch your e-mail, bank and exchange accounts for sign-ins and transfers you did not make. Keep the notes you made, such as the process names and the file dates, in case a bank or the police ask for them.
Full procedure with screenshots: Report a cyber attack or scam to the authorities
If you use Windows, an iPhone or an Android phone
The tags say macOS and every vendor source we read describes a Mac threat. We found nothing that says the five delta-canvas.com files run on anything else.
| Your device | What we know | What to do |
|---|---|---|
| Windows PC | The URLhaus tags say macOS. A Mach-O program or a Mac zip does not run on Windows. We do not know what the site shows a Windows visitor | Nothing to remove for these files. If you typed passwords on a page of the site, change them. If you ran a command on Windows, treat it as a separate case and use a Windows guide |
| iPhone or iPad | No source describes these files on iOS. A pasted Terminal command cannot be run on an iPhone | Nothing to remove. If you typed passwords on a page of the site, change them |
| Android | No source mentions it | Nothing to remove for the Mac files; change passwords if you entered any |
After removal: passwords, accounts and prevention
If you opened a file: protect what may have been taken
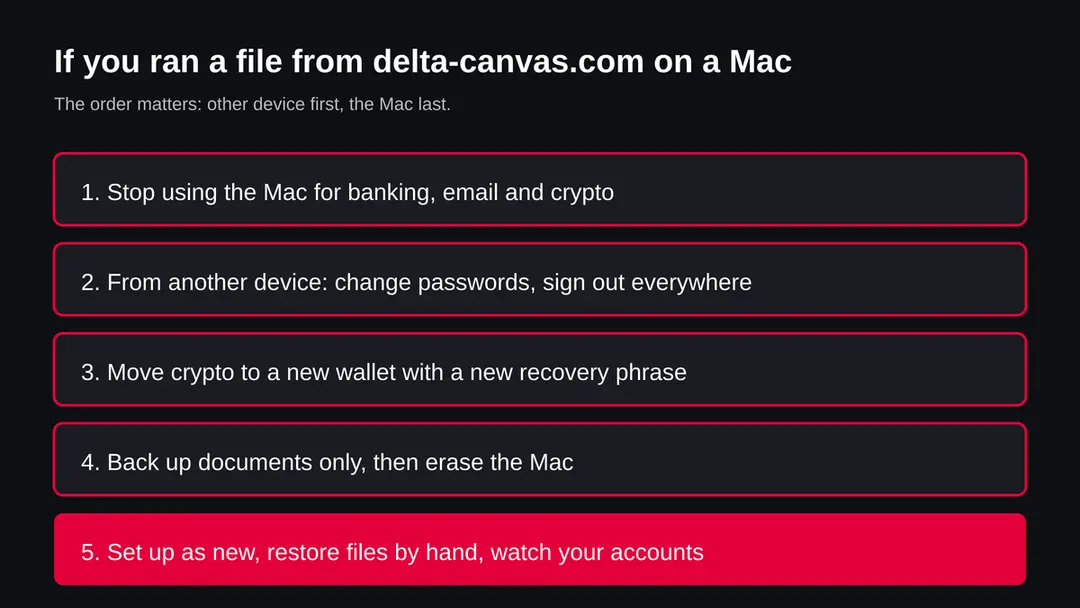
The Mac is one half. The other half is everything that was on it, which the attackers may already have. The order matters: another device first, then crypto, then the Mac.
- 1
Change passwords from a clean device
Start with your email and your Apple Account, then banks, exchanges, work accounts and social media. Passwords typed on the infected Mac may go to the attackers too, so do not type the new ones on it.
- 2
Sign out other sessions and revoke keys
Cookies may have been taken, so a new password alone may not end a stolen session. In each important account use the option to sign out everywhere. Revoke API tokens, SSH keys and cloud keys that were on the Mac, since Unit 42 saw those folders taken.
- 3
Move crypto first if a wallet was on the Mac
If a recovery phrase was stored on or typed into the Mac, assume it is known. From a clean device create a new wallet with a new recovery phrase and move the funds there. We did not read a wallet maker's page for this job, so check your wallet maker's own guidance for the exact steps.
- 4
Back up documents, then erase the Mac
Erasing is the only step that removes unknown leftovers. Copy documents and photos to an external drive and leave out apps and system folders. Apple says Erase Assistant needs a Mac with Apple silicon or an Intel Mac with the T2 chip, running macOS 12 or later.
- 5
Run Erase All Content and Settings
Open System Settings > General > Transfer or Reset > Erase All Content and Settings. Enter your administrator information and click Unlock, review the list and click Continue. Apple says this signs you out of Apple services, erases all volumes and user accounts and removes apps and settings, and that the Mac then shows a Hello screen. Macs without a T2 chip use Apple's separate erase and reinstall steps.
- 6
Set up as new and restore only your files
Restoring a full backup could bring the malware back if it was already in it. Restore documents by hand, install apps from their makers, and change your passwords once more when the Mac is clean.
- 7
Watch your money and your accounts
Check card statements and exchange logs for several weeks and turn on alerts. Stolen sessions and keys can be used long after the infection.
- 8
Use a password manager and two step sign in
After the erase, do not let the browser save passwords again. Use a password manager, and a sign in app or a security key rather than text messages where the service offers it.
- 9
Report it
File a report with your national cybercrime service, and keep the date, the file names and any amounts lost. Banks and exchanges often ask for a police report number.
- 10
If you own a hacked site
If delta-canvas.com is yours, or you run a site that unexpectedly serves these files, treat it as a break in: take the server offline, change every password and key, find how files reached the /zxc/ folder, restore from a clean copy and ask URLhaus to review the entries afterwards. We saw no sign that this is a hacked legitimate site; the domain is weeks old at the first report.
Keep a Mac out of this kind of trap
The rule that would have stopped the paste-a-command trick is one line: a website never needs you to paste something into Terminal.
Do
- Treat a request to paste a command into Terminal from a web page as an attack. Close the tab.
- Enter your Mac password only into prompts you started yourself.
- Install macOS updates, ideally automatically (Kaspersky).
- Get apps from the App Store or from their makers' own sites.
- Use a password manager, so you never type passwords into odd pages.
- Keep a backup of documents on a disk that you unplug afterwards.
Don't
- Do not copy and paste a command to pass a CAPTCHA, fix a browser or verify you are human.
- Do not run cracked Mac apps or downloads from sites that promise free versions of paid software.
- Do not trust that macOS will warn you: Kaspersky's test command raised no warning on macOS Tahoe 26.5.2.
- Do not open a zip that arrives by link and claims to be an app.
- Do not rely on a quiet scan to say that you are safe.
Questions about delta-canvas.com (Mac malware downloads)
What is delta-canvas.com?
It is a website that URLhaus lists for handing out Mac malware, not a program on your computer. Five file addresses on it, all added on 23 September 2026, are tagged macOS:
- three zip archives named app.zip
- apptwo.zip and appex.zip
- two Mach-O programs named mdw and kito
The domain was registered on 22 September 2026, one day before the reports. On 17 October 2026 our plain request got a Cloudflare 520 error instead of a page, so we cannot say what it shows visitors today.
If you only saw the name in a log, you are not infected by that. If you opened a file from it, use the cleaning steps.
Is delta-canvas.com safe to open?
No, do not open it. URLhaus lists five malware downloads on the domain, and the domain was registered only a day before they were reported.
Our one plain request on 17 October 2026 returned an error page, which clears nothing: sites that spread malware often show different content by country, device, browser or visit, and some check whether they run in a sandbox.
Loading a page is a smaller risk than running what it gives you, but there is no reason to take either. Close the tab, and if your network allows it, block the domain.
Is delta-canvas.com a virus?
A website is not a virus, but the files it hands out can be malware. The URLhaus rows tag the five files as malware downloads for macOS, and none names a malware family, so we cannot tell you what they do.
A Mach-O file is a native Mac program, which means mdw and kito can run on a Mac without any further step once started. The zip files can contain an app or an installer.
We did not download any of them, so we do not claim a family, a behaviour or a detection name. Treat any of the five files as dangerous.
I downloaded app.zip from delta-canvas.com. What do I do?
If you only downloaded it and did not open the archive or run anything inside, delete the file and empty the Trash. If you opened it, started an app from it or typed your password into a prompt it showed, treat the Mac as compromised.
Stop using it for banking, email and crypto. From another device change your passwords, starting with email and your Apple Account, and sign out of all sessions.
Move any crypto to a new wallet. Then back up documents and erase the Mac. A scan that finds nothing does not prove the Mac is clean.
I pasted a command from a page into Terminal. What now?
Treat it the same way:
- stop sensitive use
- take the Mac off the network if you can
- change passwords from another device
Kaspersky and Unit 42 describe commands of this kind that fetch a script or a disk image, launch the malware and ask for your password with a fake window. If you typed your Mac password into such a window, the attackers may have it, and with it the Keychain.
We do not know whether delta-canvas.com uses a pasted command at all, because we did not reach its page. Back up documents and erase the Mac if you ran the command.
How do I remove it from my Mac?
The only way that leaves no unknown leftovers is to erase the Mac and set it up again. We found no vendor procedure for these five files, so the steps on this page are our reading of Apple's pages and the vendor reports.
You can look in Login Items & Extensions and in the hidden folders the reports name and delete what you find, but those names change between samples, and a clean look does not clear the Mac. On a Mac with Apple silicon, open System Settings, General, Transfer or Reset, then Erase All Content and Settings, after backing up documents only.
Is it the Atomic macOS Stealer (AMOS)?
We do not know. The URLhaus rows for delta-canvas.com carry no family tag. The same folder name zxc and the same zip names also appear in URLhaus reports for a different domain, loop-lumen.com, whose reporter tagged them AMOS and ClickFix.
Our reading is that this looks like a reused kit, but that is a guess, not a finding, and the two sites have different registrars and dates.
AMOS is a Mac stealer sold as malware as a service that Sophos says made up almost 40% of its macOS protection updates in 2025. Read the background on this page, but do not assume it.
Does delta-canvas.com affect Windows, iPhone or Android?
We found no source saying it does. The URLhaus tags say macOS, and the two non zip files are tagged macho, the native program format of macOS. A Mach-O program does not run on Windows, and a pasted Terminal command cannot be run on an iPhone.
We do not know what the site shows a Windows or phone visitor, since we saw only an error page. If you typed passwords on any page of the site, change them on every device where you used them. If you ran a command on Windows, treat it as a separate case and use a Windows guide.
Will erasing my Mac remove it, and is my data safe?
Erasing removes everything on the Mac, including hidden files you did not find, but it does not undo theft. Anything already sent to the attackers, such as passwords, cookies and wallet files, stays with them, so change passwords and sign out other sessions from a clean device and move crypto to a wallet with a new recovery phrase.
Apple says Erase All Content and Settings signs you out of Apple services, erases all volumes and user accounts and removes apps and settings. Restore documents by hand rather than a full backup, in case the malware is in it.
Will Fortect remove delta-canvas.com?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For delta-canvas.com, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- Kaspersky: ClickFix on macOS, how the Terminal based attack works (27 July 2026) (read October 17, 2026)
- Palo Alto Networks Unit 42: Atomic macOS (AMOS) Stealer Activity (16 September 2026) (read October 17, 2026)
- Sophos X-Ops: Why AMOS matters, the macOS malware stealing data at scale (read October 17, 2026)
- Apple Support: Erase your Mac (Erase Assistant) (read October 17, 2026)
- Apple Support: Open items automatically when you log in on Mac (Login Items & Extensions) (read October 17, 2026)