
Libexec virus: what it is on a Mac and how to remove it
The "Libexec virus" is Mac adware of the AdLoad kind, and /usr/libexec, the folder it is named after, is a normal part of macOS. To remove it, delete its startup items, app folders, proxy and profile, then restart and check again.
Facts checked October 11, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
Programs like an unknown app or startup item on a Mac that came with a fake update usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove Libexec virus yourself 5 steps, about 15 minutes, no software needed.
Libexec virus: summary
| Type | Mac adware of the AdLoad kind, delivered by a trojan installer; "Libexec" is a label from a macOS folder name, not a family name |
|---|---|
| Risk | Medium to high: ads and hijacked searches, plus root-level startup items and a proxy; card theft is not confirmed |
| Symptoms | Unknown extensions or apps, a changed homepage or search engine, ads on every site, a repeating pop-up that names analyticsd |
| How to get rid of it | Remove the startup items first (LaunchAgents, LaunchDaemons, cron), then the app folders, the proxy and the profile; restart and check again |
| Our check (5 October 2026) | One clean Mac on macOS 26.4.1: Apple files in /usr/libexec signed by Apple, no AdLoad-pattern names, proxy off; no sample run |
| Running since | AdLoad from at least late 2017 (SentinelOne); our first guide 9 March 2020 |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Detection | No Microsoft detection name is known for the Libexec label. Microsoft names the family AdLoad as Adware:MacOS/Adload.A |
|---|---|
| Also called | AdLoad, Adware:MacOS/Adload.A; installs under names such as SearchQuest, ArtemisSearch or Kreberisec |
| Not to be confused with | /usr/libexec, trustd and xpcproxy, which are part of macOS |
| Name | Libexec virus |
| Evidence | 0 write-ups by security sites; details still limited |
| First seen | 9 March 2020 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 5 October 2026 |
Facts checked on 5 October 2026 against Microsoft's Adload.A description, SentinelOne Labs, Red Canary, Adobe and Apple Support. We checked one clean Mac (macOS 26.4.1) and ran no AdLoad sample; the removal steps follow SentinelOne and Apple and were not tested on a live infection.
What the "Libexec virus" is, and what it is not
"Libexec virus" is a label, not a program you can look up. It comes from /usr/libexec, a folder inside macOS itself. What people really have is Mac adware of the AdLoad kind: a trojan installer that arrives with a fake update or a free app, adds more adware and keeps itself running from several places.
- 1
The name
We found no vendor write-up that lists a malware family called Libexec, so treat it as a search term. On the Mac we checked,
/usr/libexecheld 428 items, including Apple's owntrustdandxpcproxy. - 2
The family it behaves like
Microsoft calls it Adware:MacOS/Adload.A: adware that impersonates apps such as video players, arrives through malicious links on third-party sites and is also dropped by the UpdateAgent trojan. SentinelOne has seen it since at least late 2017.
- 3
What the old guide got wrong
It called Libexec an AdLoad component, said it abuses the AppleScript app and said it can collect card numbers. None of this appears in the Microsoft or SentinelOne descriptions we read, so we marked those claims as not confirmed.
What /usr/libexec/frauddefensed is, and whether it is part of the adware
/usr/libexec/frauddefensed is most likely an Apple helper program that comes with recent macOS, not adware.
We found no reliable public source that documents it, so this is our reading. The name follows Apple's habit of ending background daemons with a d, and fraud defense points to Apple's own checks against account or payment abuse. AdLoad hides its files in LaunchAgents, LaunchDaemons and Application Support folders, not in /usr/libexec.
On macOS 11 and later, /usr/libexec sits on the signed system volume. Apple says the kernel rejects any code or data on that volume without a valid Apple signature, and the volume changes only through a macOS update. Adware therefore cannot drop a new file such as frauddefensed into that folder. On a Mac with FileVault turned on, the protection cannot be switched off at all.
You can check the file yourself in Terminal. Type codesign -dv --verbose=4 /usr/libexec/frauddefensed and press Return. A genuine Apple file lists Authority=Software Signing, then Apple Code Signing Certification Authority and Apple Root CA.
The same check works for any other name in /usr/libexec. A real warning sign is a plist in /Library/LaunchDaemons or ~/Library/LaunchAgents that borrows the name but starts a program from another folder.
What Libexec virus does on an infected PC
What we checked on a Mac, and what we could not
We ran no AdLoad sample. We looked at the files the old guide named and at the places adware leaves traces, on one clean Mac.
macOS 26.4.1 · Apple silicon · 5 October 2026
- The libexec folder
/usr/libexecis owned byroot:wheel.trustdandxpcproxysit in it, andcodesignprinted Apple identifiers for both:com.apple.trustdandcom.apple.xpc.proxy. - analyticsdThe file the old pop-up named exists at
/System/Library/PrivateFrameworks/CoreAnalytics.framework/Support/analyticsd. - Startup foldersNo file in
/Library/LaunchAgents,/Library/LaunchDaemonsor~/Library/LaunchAgentsended in SearchDaemon, Lookup or Results. The files present came from known vendors. - Proxy and profilesThe SOCKS proxy for Wi-Fi was off and
profiles listshowed no profile. - Not testedA Mac with AdLoad, the root-only
/var/rootfolder and the browsers' extensions.
One clean Mac, no sample This shows what the Apple files look like. It says nothing about your Mac: adware changes names and can sit unseen, so one clean look is not an all-clear.
The pop-up that mentions xpcproxy and analyticsd
Our 2020 guide quoted a pop-up that readers saw about every ten minutes: "Infection: User: _analyticsd Process: /usr/libexec/xpcproxy File: /System/Library/PrivateFrameworks/CoreAnalytics.framework/Support/analyticsd". We could not find which program shows it; everything it names is Apple's.
| In the message | What we found | What it means |
|---|---|---|
_analyticsd | The account macOS uses for its analytics service | A normal name |
/usr/libexec/xpcproxy | Apple-signed, owned by root | launchd uses it to start services, so many processes show it |
analyticsd | Present in the CoreAnalytics folder | Apple's analytics helper |
What AdLoad does after the installer runs
SentinelOne describes a password prompt followed by files in the user and system libraries, so the Mac ends up with several copies. The example name SearchQuest is SentinelOne's; real ones differ.
| Where | What goes there |
|---|---|
~/Library/LaunchAgents/com.SearchQuest.plist | A LaunchAgent that starts a program in ~/Library/Application Support/com.SearchQuest/ at login |
/Library/LaunchDaemons/com.SearchQuestDaemon.plist | A LaunchDaemon that starts a copy in /Library/Application Support/ as root |
/Library/LaunchDaemons/com.SearchQuestP.plist | A second daemon that runs a program in the hidden /var/root/.SearchQuest/ folder and opens a proxy |
A UUID-named folder in Application Support | Started by a cron job every 2 hours 30 minutes, so deleted files come back |
| Network settings | A SOCKS proxy on localhost:8080 that survives restarts |
The three lures from our 2020 guide
The old guide showed how people met it. These are pictures of those pages, not screenshots we took.
2019
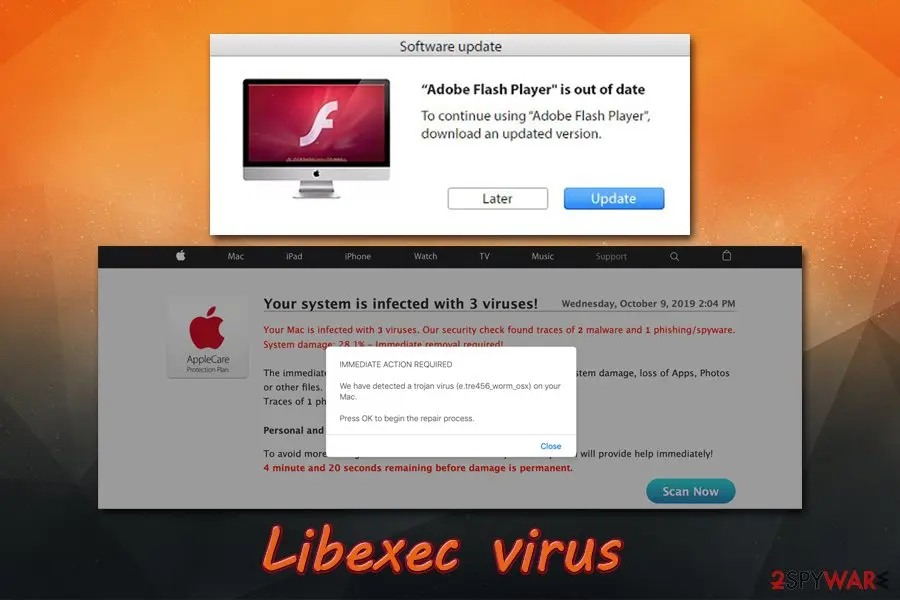
A Flash update that is not one
A dialog says "Adobe Flash Player is out of date" above a page that claims three viruses and counts down. Adobe stopped supporting Flash on 31 December 2020.
From our 2020 guide: a fake Flash update dialog above a scare page that claims three viruses and counts down 4 minutes 20 seconds. A picture of the fakes, not a screenshot we took. 2019
An installer with SafeFinder inside
A "FlashPlayer" installer offers SafeFinder, which changes the search provider and home page, in the fine print.
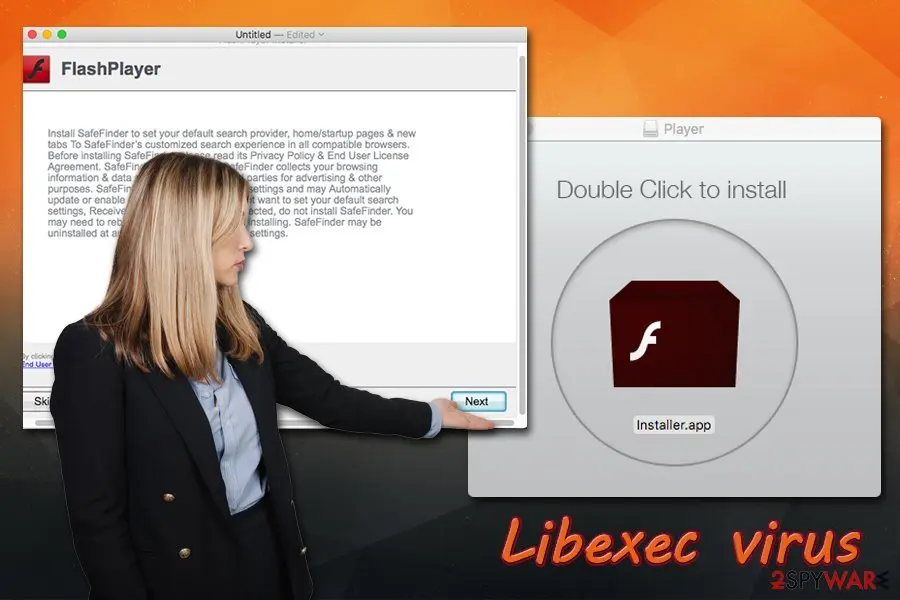
From our 2020 guide: a fake FlashPlayer installer whose first window offers SafeFinder, which changes the default search provider, home pages and new tabs. A picture of the installer, not a screenshot we took. 2019
A Java update prompt
A page styled as an Install Java window says "UPDATE RECOMMENDED! Your version may be outdated" with an OK button.
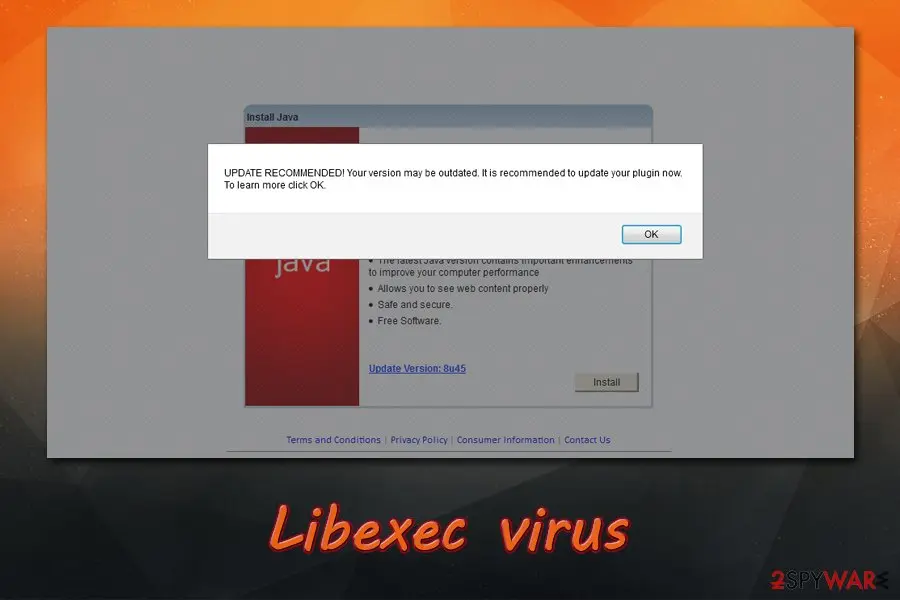
From our 2020 guide: a fake Install Java page with the message "UPDATE RECOMMENDED! Your version may be outdated". A picture of the page, not a screenshot we took.
What Libexec virus can steal or download
Most of the harm is ads and hijacked searches, but the installer asked for your administrator password.
- High
Root access and a proxy
SentinelOne says AdLoad installs a man-in-the-middle proxy and runs programs from
/var/root. Microsoft says that if Adload has launched, the device is likely under complete attacker control. - Medium
More software you did not choose
Microsoft: Adload drops more payloads. Red Canary describes Shlayer, a related Mac family, as an installer disguised as another app. SentinelOne found extras such as Mughthesec beside it.
- Medium
Ads, redirects and changed searches
Unexpected ads in system apps, extensions you did not add and a changed home page or search engine (Microsoft's symptom list).
Card numbers and logins
Our 2020 guide said it can read them. Microsoft and SentinelOne do not list that for AdLoad, so it is unconfirmed. With a proxy on the Mac, change important passwords anyway.
How to remove Libexec virus
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Which browser shows the ads?
Look for what matches the table above: an unknown name in startup, a proxy you did not set, a profile you did not install. Do not delete anything yet.
Remove extensions you do not recognise
Paste
chrome://extensionsinto the address bar and click Remove on anything you did not install yourself, especially search helpers.Full procedure with screenshots: Remove a browser extension
Set the homepage and search engine
Open Settings > On startup and Settings > Search engine and put back your own choice.
Reset Chrome
Open Settings > Reset settings > Restore settings to their original defaults and confirm. This resets the start page and search engine and turns off extensions; bookmarks and saved passwords stay. Locked settings point to a profile: see the Mac chapter above.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Remove add-ons you do not recognise
Paste
about:addonsinto the address bar, open Extensions, click the three dots beside an add-on you did not install and choose Remove.Set the homepage and search engine
Open Firefox > Settings > Home and set Homepage and new windows and New tabs to Firefox Home (Default), then Settings > Search and choose your own Default Search Engine.
Refresh Firefox
Paste
about:supportinto the address bar and click Refresh Firefox. This removes extensions and resets settings; bookmarks and passwords stay.
Remove extensions you did not add
Open Safari > Settings > Extensions, select every extension you do not recognise and click Uninstall. Safari extensions are optional, so you can remove all of them and add back the ones you want.
Set the homepage and search engine
In Safari > Settings > General set the Homepage, and in Settings > Search pick your own Search engine.
Clear the website data
Open Safari > Settings > Privacy > Manage Website Data, select the sites you do not trust or click Remove All, then Remove. If settings change back, the cause is outside Safari: see the Mac chapter above.
Then, whichever browser you use
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Libexec virus or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever Libexec virus installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Remove it from a Mac
Order matters: SentinelOne found that a surviving persistence item can rewrite what you deleted. Remove the startup items first, the programs second, then restart and check again. We did not test these steps against a live infection.
- 1
Disconnect and back up
Turn off Wi-Fi so the proxy cannot send your traffic, and copy your documents (not apps) to an external drive.
- 2
Stop the processes
In Activity Monitor choose View > All Processes, select a name from your check and click the stop button > Quit (Force Quit if it stays).
- 3
Delete the startup items
Move the matching
.plistfiles from~/Library/LaunchAgents,/Library/LaunchAgentsand/Library/LaunchDaemonsto the Bin. Never delete anything startingcom.apple.or from a vendor you know. Daemons need your administrator password. - 4
Delete the program folders and the cron job
Remove the matching folders in
~/Library/Application Supportand/Library/Application Support, including the UUID-named one. In Terminal runcrontab -l; if one line points at that folder, runcrontab -eand delete only that line. If you are unsure, leave it and use a security tool. - 5
Turn off the proxy and profile, then restart
Switch off the SOCKS Proxy, remove the unknown profile, drag the unknown app out of Applications, remove its Login Items entry, empty the Bin and restart. Check again after an hour; if a file is back, repeat (SentinelOne: several attempts can be needed).
The old guide listed five folders, among them Library/PrivilegedHelperTools/ and /System/Library/Frameworks/. We kept the first three, added the user's ~/Library copies and dropped /System/Library/Frameworks/: protected Apple code that nothing we read ties to AdLoad.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unknown app or startup item on a Mac that came with a fake update in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work. The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
If you ran the installer
Typing your password into the installer gave the adware its place. These steps cover what the browser cleanup does not.
- 1
Change passwords from another device
Start with your Apple Account and email, then banks. Turn on two-step sign-in.
- 2
Erase the Mac if it keeps coming back
Back up documents only, erase the Mac from macOS Recovery, reinstall macOS and restore the documents, not apps or a system image from after the infection.
Keep adware off your Mac
The old guide's tips still hold; here they are with current details.
Do
- Install apps from the App Store or the developer's own site and read each installer screen.
- Pick Custom or Advanced installation.
- Keep Gatekeeper on: System Settings > Privacy & Security, Allow applications from set to App Store & identified developers.
- Keep macOS updated: it brings XProtect updates, which remove known malware but not every variant.
- Keep a Time Machine backup on a disk you unplug afterwards.
Don't
- Do not follow a Flash or Java update prompt.
- Do not type your administrator password into an installer you did not start.
Questions about Libexec virus
What is the Libexec virus?
The Libexec virus is a name for Mac adware of the AdLoad kind, not a program with that name. It comes from /usr/libexec, a folder that belongs to macOS.
People who search it usually have a trojan-delivered adware that arrived with a fake Flash or Java update or a free-software bundle, installed extra apps, changed the browser and keeps itself running from startup folders.
We found no vendor write-up of a family called Libexec, so our advice follows what Microsoft and SentinelOne document for AdLoad. If you see unexplained ads or a changed search engine, follow the steps on this page.
Is /usr/libexec a virus?
No. /usr/libexec is a normal macOS folder owned by root that holds Apple's own helper programs. On the Mac we checked it held 428 items, and trustd and xpcproxy, the two the old guide named, were signed by Apple as com.apple.trustd and com.apple.xpc.proxy.
Do not delete anything in it: it is protected, and removing files there can stop services from starting. What matters is a program outside that folder, in LaunchAgents, LaunchDaemons or Application Support, that you did not install. Use the check above for names ending in SearchDaemon, Lookup or Results.
Is the pop-up about analyticsd and xpcproxy a real infection?
Not by itself. The message the old guide quoted names _analyticsd, /usr/libexec/xpcproxy and the analyticsd file in CoreAnalytics.framework, and all three are Apple components that exist on a normal Mac. We could not find which program shows the message, so it does not prove a virus.
Note which app displays it, then check Activity Monitor, Login Items and the startup folders. Never call a number or install a cleaner from a message like this. If you find unknown startup entries or a SOCKS proxy you did not set, follow the removal steps.
How did the Libexec virus get on my Mac?
Most likely you ran an installer. Our guide and the vendors describe the same routes:
- a fake Flash or Java update page
- a free app that bundles extras
- an unsigned installer with instructions to bypass Gatekeeper
- malicious links on third-party sites
SentinelOne notes that the adware asks for the administrator password and then drops files in the user and system libraries. Adobe ended Flash on 31 December 2020, so any Flash update prompt today is fake. Think back to what you installed or updated when the problems began.
How do I remove the Libexec virus from my Mac?
Check first, then remove the startup items before the programs they start. Open Applications, Login Items & Extensions, ~/Library/LaunchAgents, /Library/LaunchAgents and /Library/LaunchDaemons and look for names you do not know. Quit the process in Activity Monitor, move the matching files and folders to the Bin, switch off any SOCKS proxy and unknown profile, and restart.
Check again after an hour, because SentinelOne found that a surviving item can rewrite what you deleted. We did not test this on a live copy, so a scan with a reputable Mac security product is a sensible second check.
Is cleaning Safari, Chrome or Firefox enough?
No, not alone. The browsers show the symptoms:
- unknown extensions
- a changed homepage or search engine
- ads on every page
But AdLoad sits outside the browser, in startup folders and network proxy settings, and it can put the changes back.
Do the browser steps for your browser to remove extensions and reset settings, then follow the Mac steps on this page so the part that restores them is gone too. Cleaning only the browser is the usual reason the problem returns the next day.
Can it steal my passwords and card details?
We cannot confirm it. Our 2020 guide said the malware can gather card details and logins, but neither Microsoft nor SentinelOne lists that for AdLoad. They do say the adware can install a man-in-the-middle proxy and that, if it has launched, the device is likely under complete attacker control.
That is reason enough to act as if something could have been read. Change your passwords from another device, starting with your Apple Account and email, check card statements and turn on two-step sign-in, even if your Mac looks fine afterwards.
Does Apple's built-in protection remove it?
Only in part. Apple updates XProtect in the background and lists removal of known malware among its security updates, but SentinelOne reported that AdLoad variants changed their code so that a published XProtect rule no longer matched.
Gatekeeper helps most when you do not click past its warning. Keep macOS updated, because definitions arrive with updates, and do not treat a missing alert as proof of a clean Mac. Our check on one Mac found nothing, which tells you only what normal looks like.
Will Fortect remove Libexec virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Libexec virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- SentinelOne Labs: How AdLoad macOS Malware Continues to Adapt & Evade (updated 17 July 2026) (read October 5, 2026)
- Microsoft: Adware:MacOS/Adload.A threat description (published 19 October 2021, updated 15 November 2021) (read October 5, 2026)
- Red Canary: Shlayer, Threat Detection Report (read October 5, 2026)
- Adobe: Flash Player End of Life (read October 5, 2026)
- Apple Support: Safely open apps on your Mac (read October 5, 2026)
- Apple Support: About background updates in macOS (read October 5, 2026)
- Apple Support: Change Login Items & Extensions settings on Mac (read October 5, 2026)
- Apple Support: Use configuration profiles to standardize settings on Mac computers (read October 5, 2026)
- Our own check of /usr/libexec, startup folders, proxy and profiles on macOS 26.4.1 (ls, codesign, networksetup, profiles) (read October 5, 2026)
- Apple Platform Security: Signed system volume security (read October 11, 2026)