
Soltilid.live e-mail scam: how to spot it and what to do
Soltilid.live is a deceitful website created by online fraudsters to mislead users in multiple ways. It is not something that people actively encounter; rather, they are diverted from another website after clicking a link or are forwarded by malicious software installed on their systems (typically, adware).
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove Soltilid.live e-mail scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps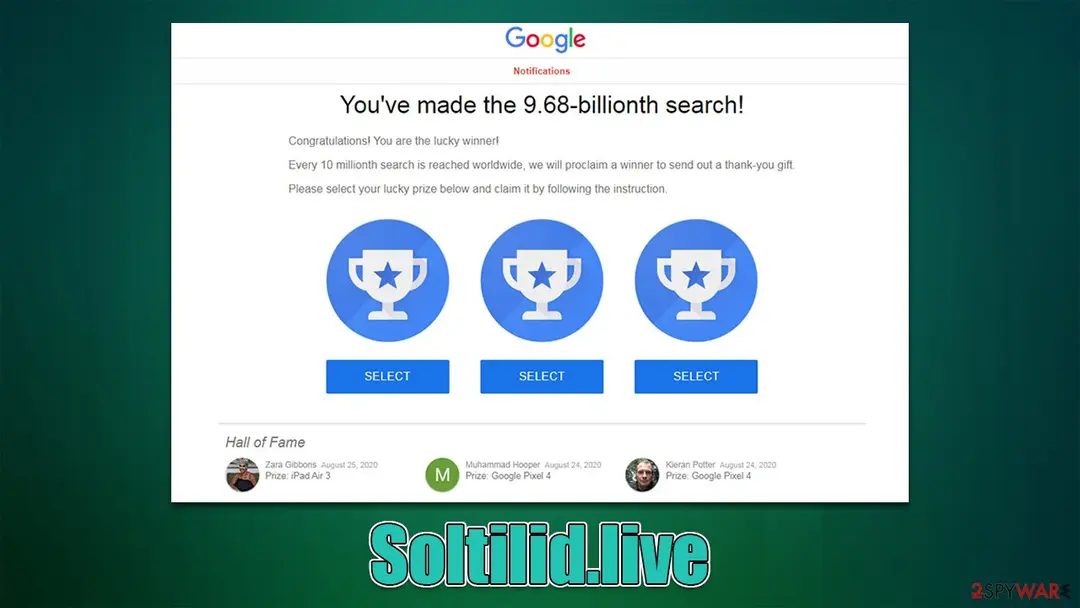
Soltilid.live e-mail scam: summary
| Distribution | Adware, redirects from other websites, malicious links |
|---|---|
| Name | Soltilid.live |
| Type | Scam, phishing, adware |
| Operation | Claims that the user has been selected for a free gift; those who proceed to reclaim the alleged gift, are asked to provide personal details |
| Goal | Make people provide personal information, subscribe to useless services, download malicious software or subscribe to push notifications |
| Symptoms | A phishing e-mail asking you to sign in |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Evidence | 4 write-ups by security sites; details still limited |
|---|---|
| Arrives as | |
| Pretends to be | A well-known company |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| First seen | 26 October 2022 |
| Facts checked | 7 October 2026 |
What the Soltilid.live e-mail scam e-mail looks like
What a phishing e-mail asking you to sign in said
You've made the 9.68-billionth search!
Congratulations! You are the lucky winner!
Every 10 millionth search is reached worldwide, we will proclaim a winner to send out a thank-you gift.
Please select your lucky prize below and claim it by following the instruction.
From our report of Oct 2022 · not reviewed since
Soltilid.live is a suspicious website that spreads misleading messages and fake giveaways
Soltilid.live is a deceitful website created by online fraudsters to mislead users in multiple ways.
It is not something that people actively encounter; rather, they are diverted from another website after clicking a link or are forwarded by malicious software installed on their systems (typically, adware). What they see next is a claim that they have won some valuable prize from Google, Amazon, or another well-recognized company.
The message typically states that the user has been chosen in some way to get a free gift, which is typically an expensive item like an iPhone, PlayStation, or TV. Some users are taken aback by this turn of events and think they are lucky to be eligible for a free gift.
However, Soltilid.live's real goal is to coerce people into revealing personal information, downloading questionable software, or paying for pointless services. People are frequently requested to provide their home address, email, or even their credit card information, which can later be used by cybercriminals.
We advise against responding to any of the communications displayed on this fake website. If you frequently find yourself redirected to Soltilid.live, your computer may be infected with adware; we will show you how to get rid of it. We'll also offer advice on how to get things back on track after being a victim of an online scam.
How to tell the Soltilid.live e-mail scam e-mail is fake
From our report of Oct 2022 · not reviewed since
- can help you when dealing with leftover adware files, for example, you can get rid of various browser trackers and fix system damage automatically
Is Soltilid.live e-mail scam dangerous? What the senders want
From our report of Oct 2022 · not reviewed since
How you end up on a scam site
It is not a secret that thanks to sophisticated security scanners, search results provided by a reputable search provider such as Google is usually secure and would not insert malicious links for users to visit (even though there's no guarantee).
However, whenever users expose themselves to less-than-secure websites, such as torrents or illegal video streaming platforms, their browsers may immediately forward them to other suspicious places, be it automatically or due to deceptive link clicks on the said sites.
As mentioned, suspicious redirects may also be caused by adware installed on one's device. This potentially unwanted application usually arrives on users' devices without their knowledge or consent because it is often spread via the software bundling technique, where several applications are installed in one installer package.
Optional components are often hidden with various tricks, such as misplaced "Agree and install" buttons, fine print text, or even the incentive of people selecting the "Recommended" settings instead of the "Advanced" ones, with the former installing optional applications in the background.
From our report of Oct 2022 · not reviewed since
Scam techniques exposed
In terms of numerous internet fraud methods, the element of surprise is especially powerful.
Gift card scams and other giveaway schemes sometimes concentrate on persuading individuals to move forward by using well-known brands or company names, like Google or Amazon. On the Soltilid.live website, the following message is among the most often seen ones:
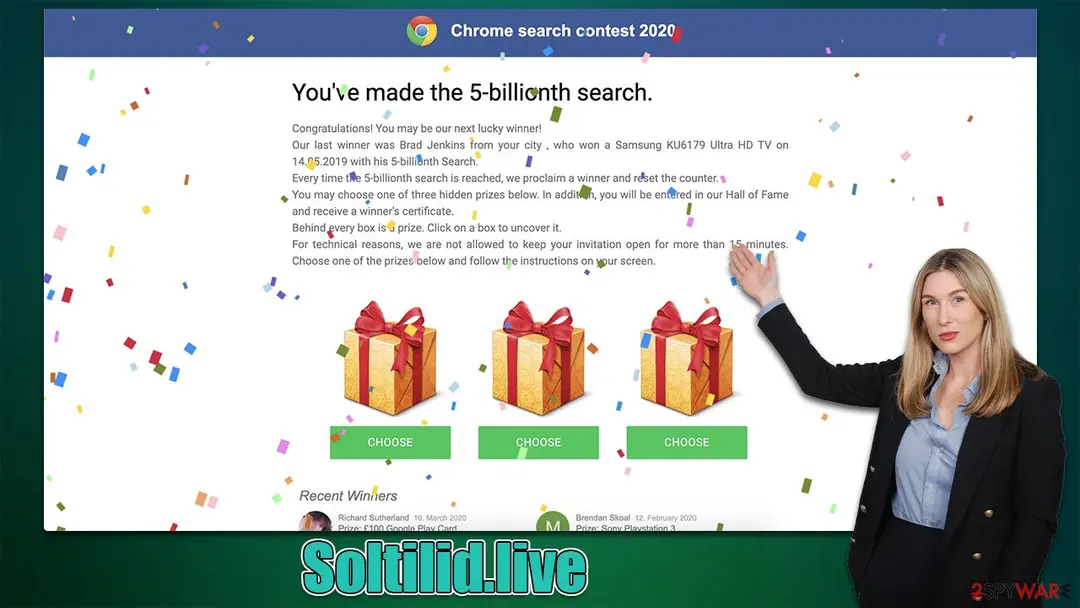
The bogus message "You've made the 9.68-billionth search!" suggests that users were chosen because they conducted the ten billionth search and are now qualified for a "thank-you" gift. They are then presented with three identical-looking awards or gifts and are instructed to select one of the claimed goods.
When picked, they are shown a valuable item and claim that they have already won it. Those who proceed are then usually asked to provide personal information, such as a home address, email, or even credit card details for the alleged delivery. However, no matter how long users would wait, they will not receive the long-awaited item.
What to do after the Soltilid.live e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you typed a password on the page the Soltilid.live message opened, assume the sender has it. Go to the real site by typing its address yourself and change the password there, choosing one you have never used.
Change it anywhere else the same password was used, and sign out all other sessions if the service offers it. Any browser on Windows 11 or Windows 10 will do, as long as you do not follow the e-mail's link.
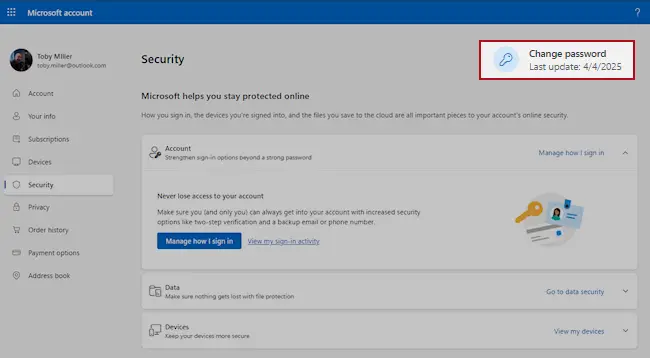
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
With two-step verification on, a stolen password alone no longer opens the account, because a sign-in from a new device also needs a code from your phone.
Switch it on for the e-mail account first, then for banking, shopping and social accounts that use that address.
Check the recovery phone, the recovery e-mail and any forwarding rules while you are in the settings, since attackers change them to come back. The pages are the same on Windows 11 and Windows 10.
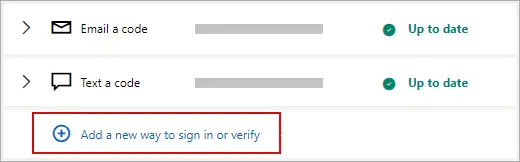
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Do not reply and do not click anything else in the message. In Outlook select the e-mail and choose Report > Report phishing; in Gmail open the three-dot menu next to Reply and pick Report phishing.
That trains the filter for everyone on the service, and the message goes to the junk folder. If the e-mail came to a work address, forward it to your IT team as an attachment first.
The steps are the same in the web mail and the mail apps on Windows 11 and Windows 10.
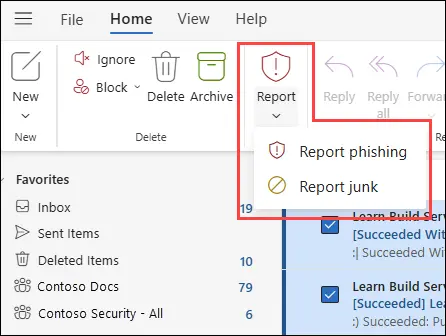
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A fake sign-in page only steals what you type, so most readers can skip this step. If the Soltilid.live e-mail made you download or open a file, delete it and scan the PC.
In Windows Security > Virus & threat protection > Scan options, run a Full scan and then Microsoft Defender Antivirus (offline scan) > Scan now. The offline scan restarts Windows 11 or Windows 10 and takes about 15 minutes.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
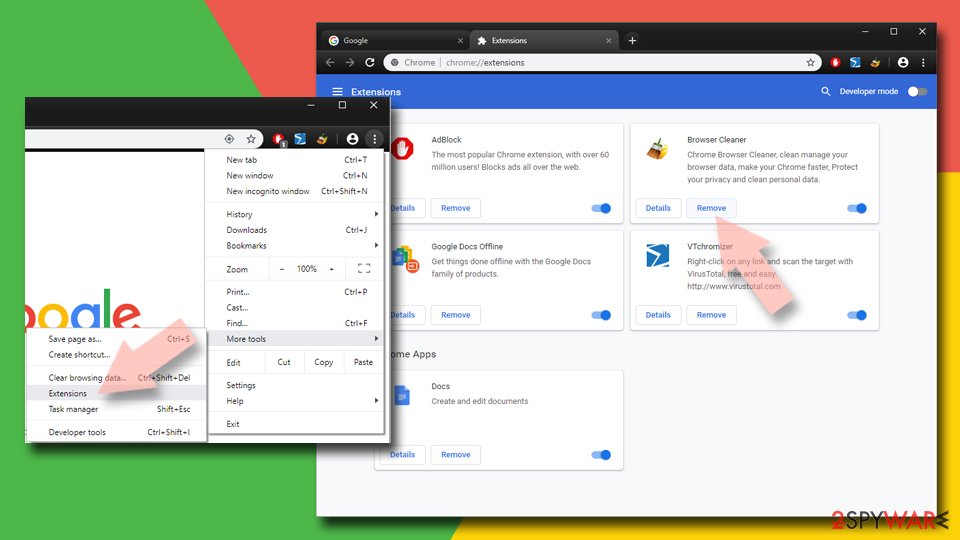
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
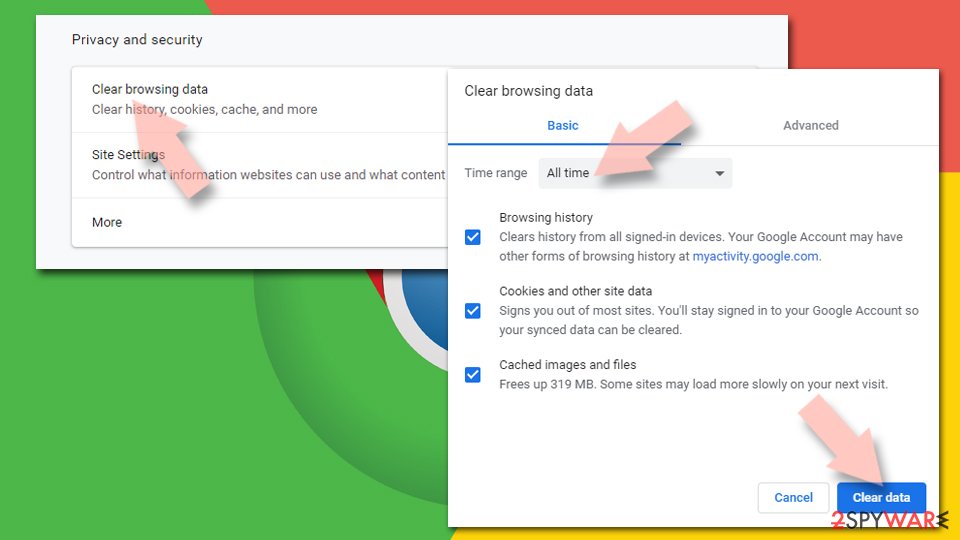
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
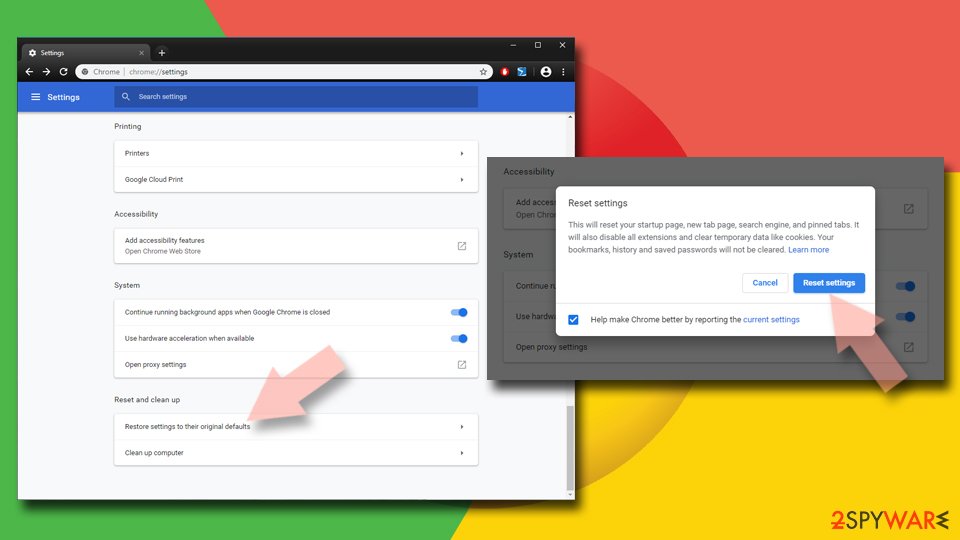
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
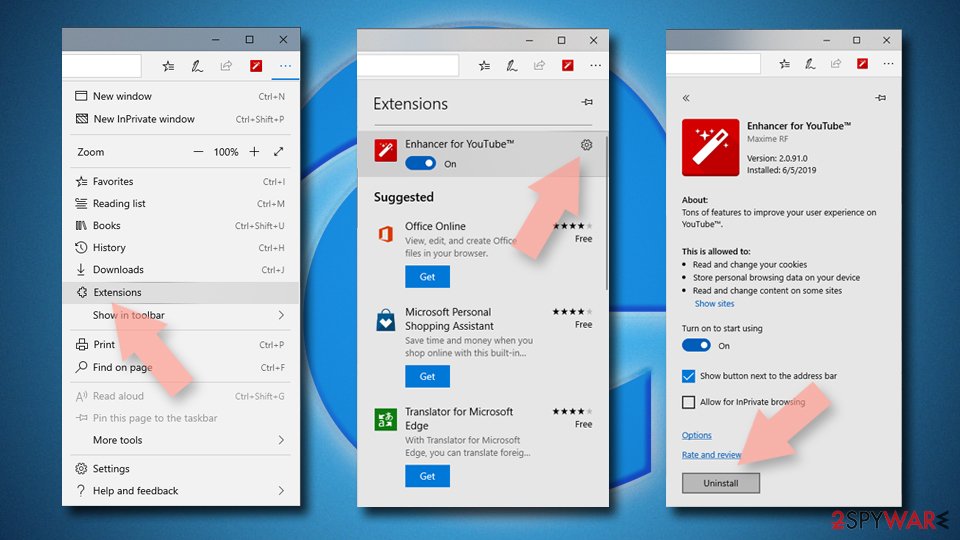
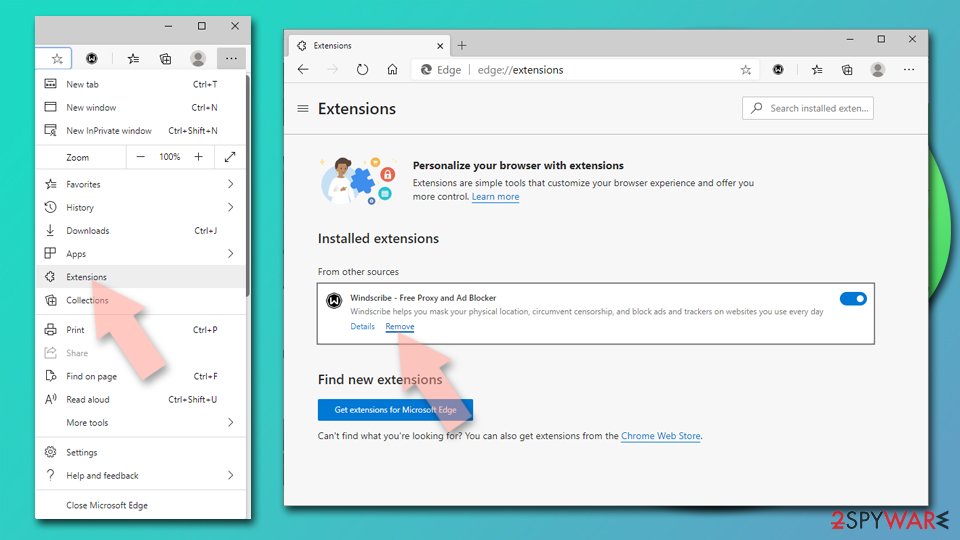
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
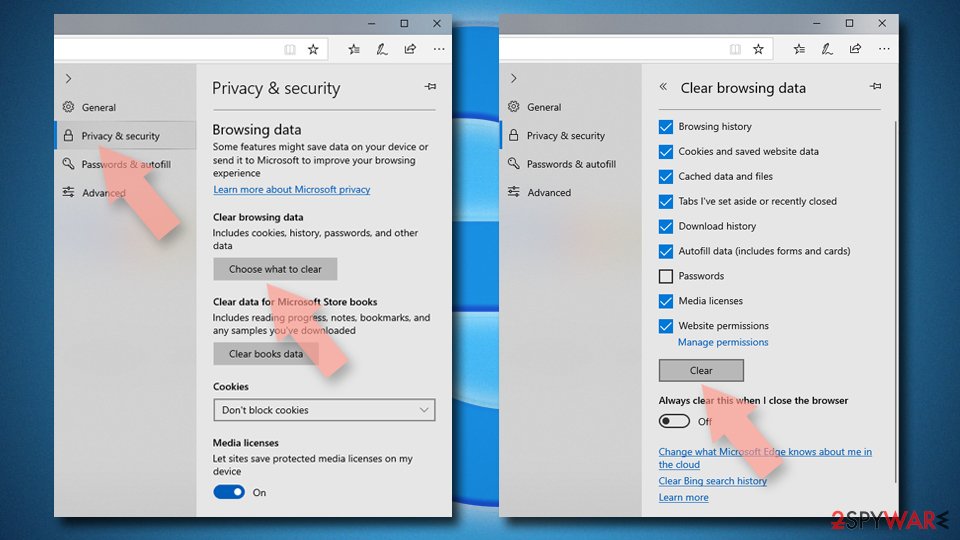
Clear cookies and other browser data:
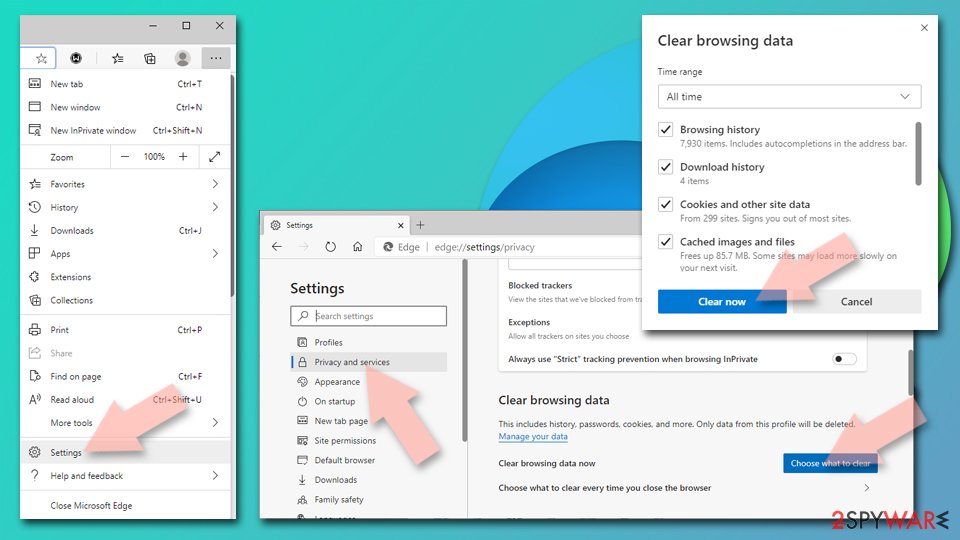
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
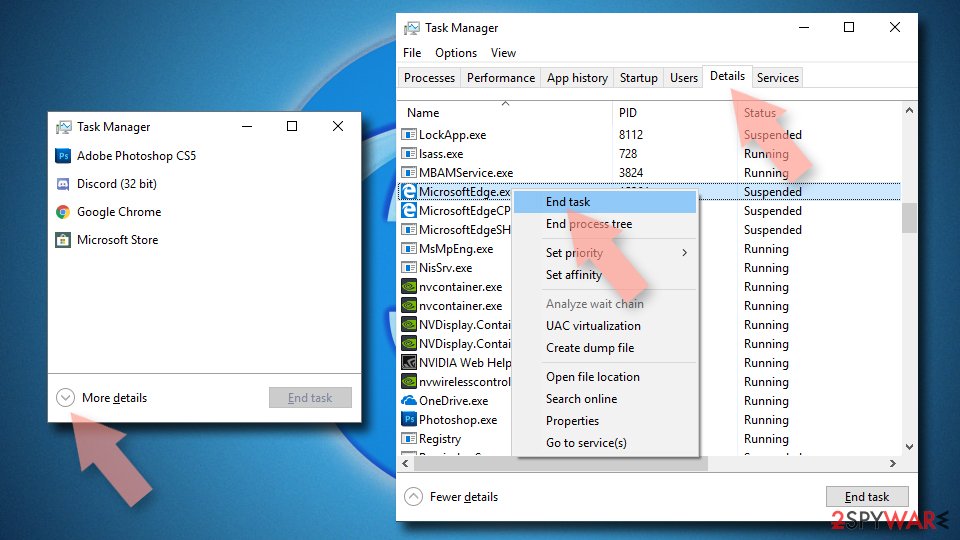
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
Reset Chromium-based MS Edge:
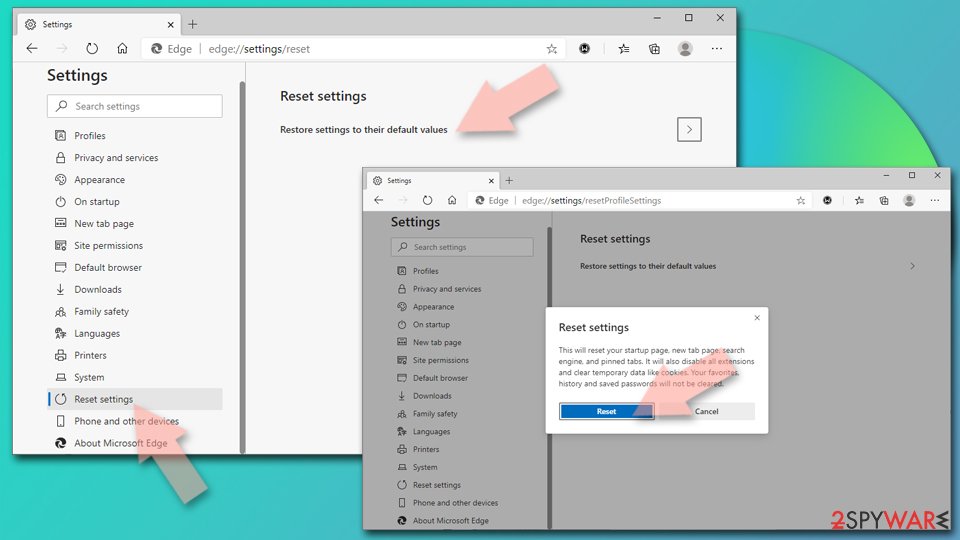
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
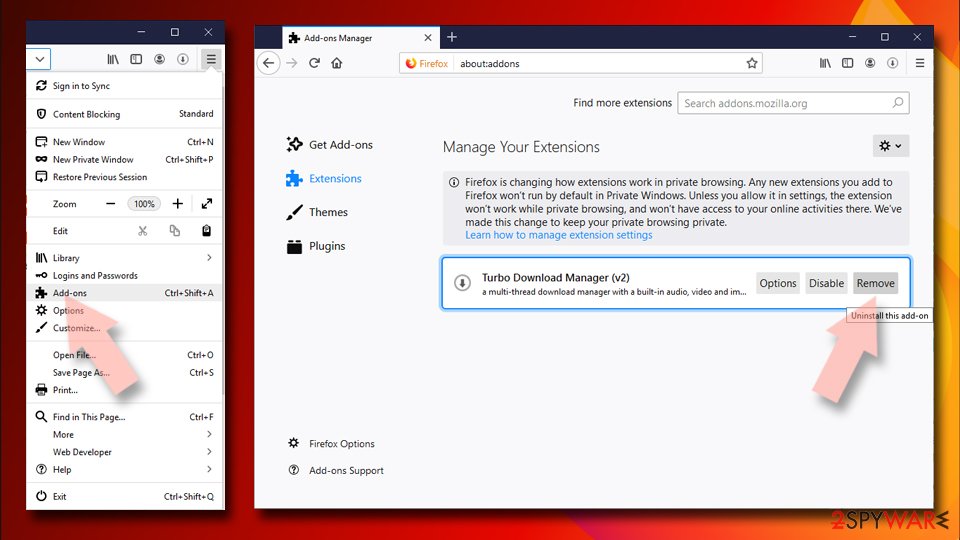
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
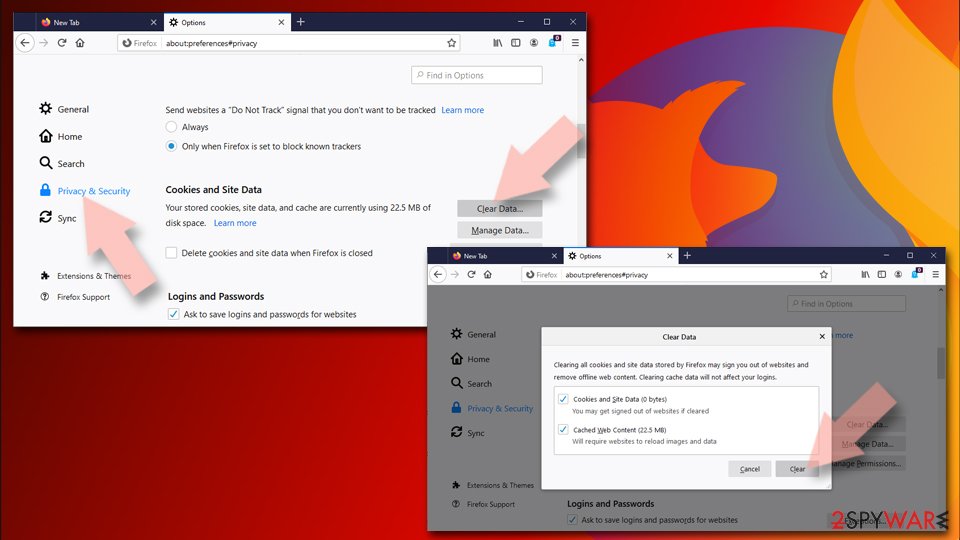
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
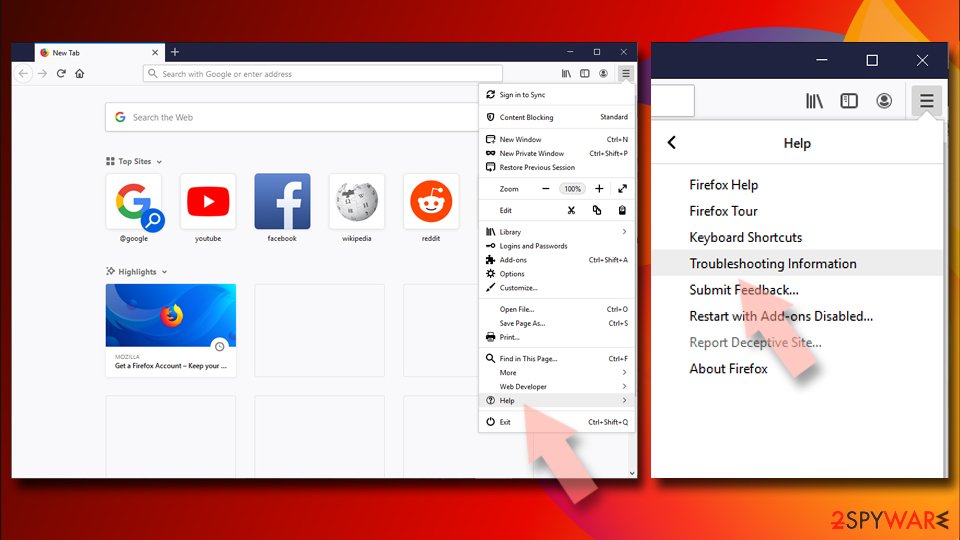
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
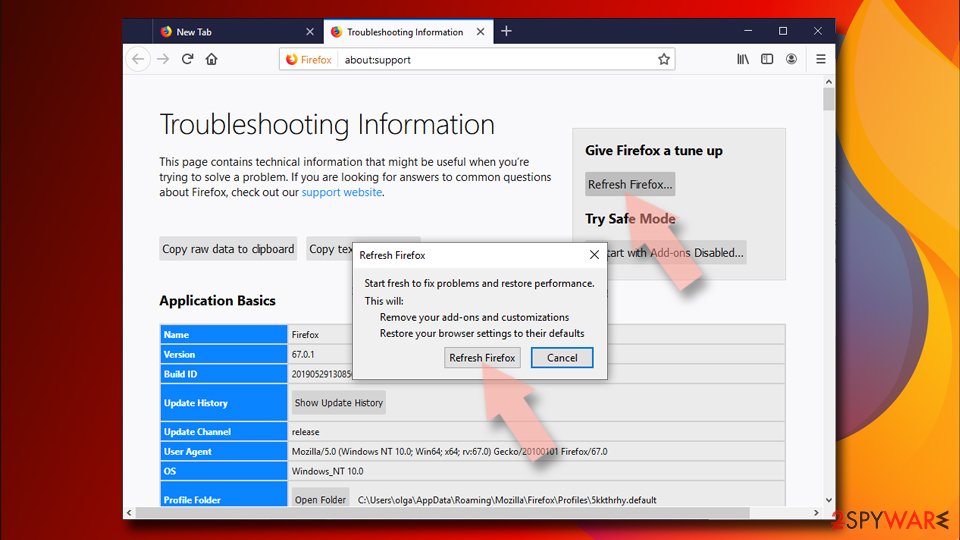
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
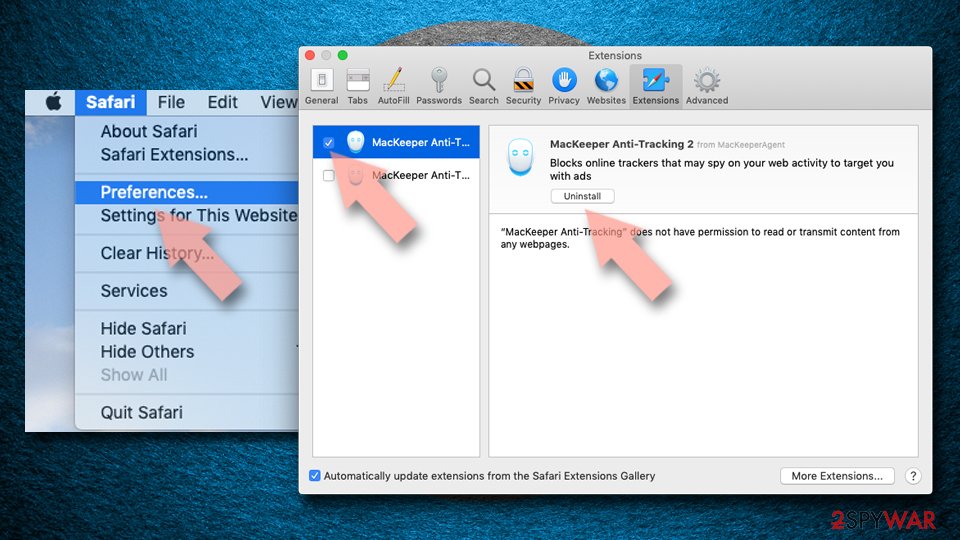
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
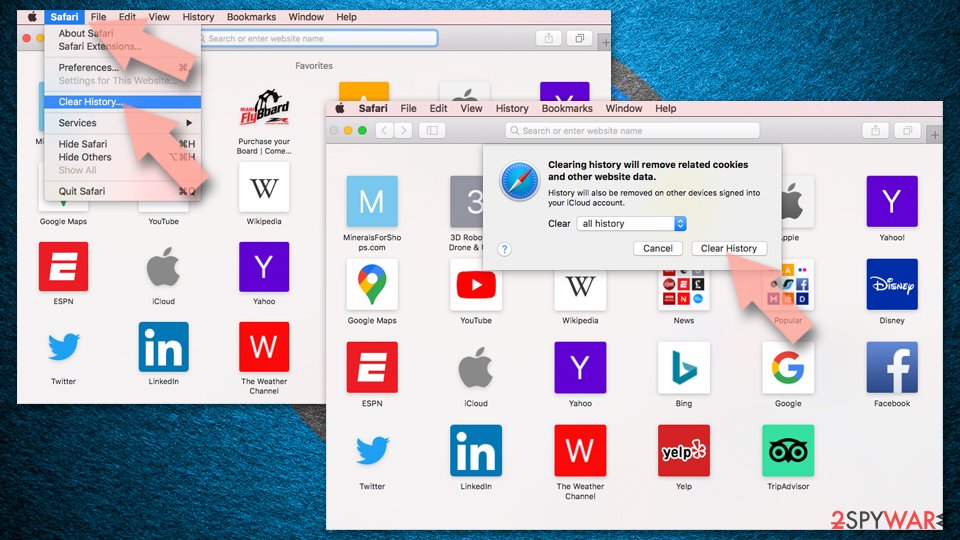
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
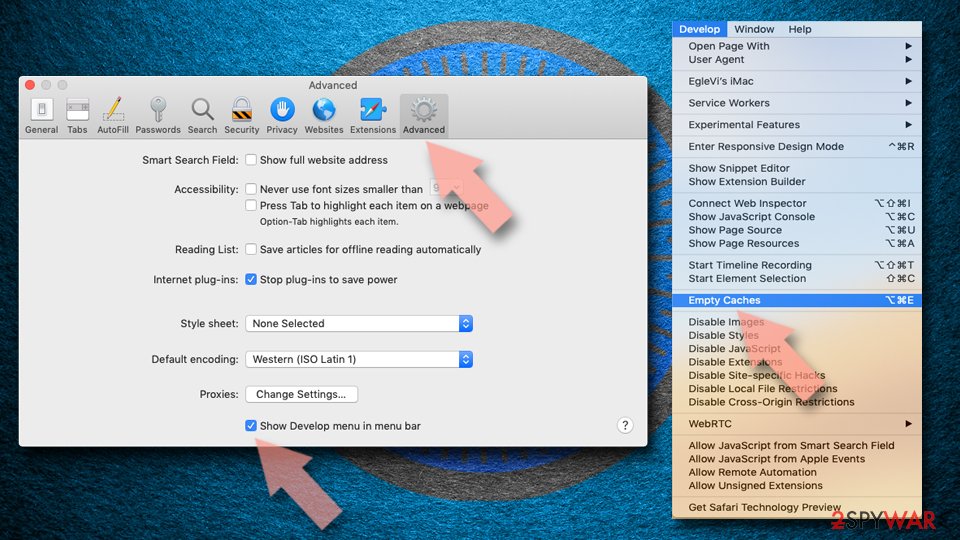
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
From our report of Oct 2022 · not reviewed since
Removal of adware and other tips
We suggest carrying out the following procedures to ensure a safer and more enjoyable user experience: deleting suspicious extensions, uninstalling programs at the system level, and running a , , or other anti-malware tool scan on your computer.
Since unwanted adverts and redirection are commonly brought on by adware, thorough checks are essential. Please take note that the automated removal provided by security software maintains the security of your system, therefore, using the manual techniques listed below is not necessary. Regardless of the method, we do advise clearing web browsers.
To thoroughly remove an unwanted app, you need to access Application Support, LaunchAgents, and LaunchDaemons folders and delete relevant files:
Adware can also be installed as a browser extension. Even if this software cannot have high privileges on the system and is, therefore, far less impactful, there are many malicious addons that might be tied to it. As a result, it's essential to remove any possibly harmful browser extensions.
Click on the "Extensions" button next to the options menu to the right of the URL bar to remove extensions from your browser. Then click More Actions and select Uninstall/Remove.
A crucial step in the recovery process is making sure that adware or other unidentified parties do not automatically collect information about you. Trackers like cookies may be used to closely monitor your online activities when you visit a website or install adware-type software. To prevent this, we suggest using to clear the caches on your browser promptly. A manual solution for this process is also included below.
- Enter Control Panel into the Windows search box and hit Enter or click on the search result.
- Under Programs, select Uninstall a program.
- From the list, find the entry of the suspicious program.
- Right-click on the application and select Uninstall.
- If User Account Control shows up, click Yes.
- Wait till the uninstallation process is complete and click OK.
- From the menu bar, select Go > Applications.
- In the Applications folder, look for all related entries.
- Click on the app and drag it to Trash (or right-click and pick Move to Trash)
- Select Go > Go to Folder.
- Enter /Library/Application Support and click Go or press Enter.
- In the Application Support folder, look for any dubious entries and then delete them.
- Now enter /Library/LaunchAgents and /Library/LaunchDaemons folders the same way and terminate all the related .plist files.
Questions about Soltilid.live e-mail scam
Does getting "You've made the 9.68-billionth search!" mean my account was compromised?
Not by itself. Phishing waves are sent to long lists of addresses collected from old breaches, websites and guessing, and the sender does not know whether you even have the account the message mentions. Getting "You've made the 9.68-billionth search!" only means your address is on such a list.
It becomes a problem if you sign in through the link. To be sure, open the real service from a bookmark and check recent activity and security alerts. If you see nothing unusual and you did not type your password into the fake page, your account is fine.
I typed my password after "You've made the 9.68-billionth search!". What now?
Act within the hour. From another device, open the real site of the account the message "You've made the 9.68-billionth search!" imitated and change the password. If the same password is used anywhere else, change it there too.
Sign out of all other sessions, check the recovery e-mail and phone number, and look for mail forwarding rules or filters you did not create. Then turn on two-step verification with an authenticator app or a passkey.
If the fake page also asked for a card number or a bank login, call your bank and ask them to block the card. Finally, report the e-mail so others are warned.
Could Soltilid.live be a genuine message?
We checked it, and it is not. A well-known company is only the costume. The message exists to get your password, and real companies handle that inside your account, after you sign in normally, not through links, attachments or phone numbers in a message you did not expect.
Scammers copy logos and footers perfectly, so the design proves nothing. The sender address, the link target and the request are the reliable signs, and all three point to a scam here. Delete it, and if you are worried, check your account directly.
Why does Soltilid.live say that your account needs urgent attention?
Because that story works. A problem that needs fixing, a deadline and a simple solution make people act before they check.
The claim that your account needs urgent attention is the same for everyone who received Soltilid.live; it was written once and sent in bulk. Nothing about your own situation triggered it.
If you are unsure, look at the real account or service the normal way, without using the message. The claim will not be there, which settles the question. Then report the message.
What does Soltilid.live want from me?
In the end, your password. Everything else in Soltilid.live, from the logo to the deadline, is there to get you to that point without stopping to think. Knowing the goal helps you judge your risk.
If you did not give it, you lost nothing and can delete the message. If you did, the steps in this guide are ordered by what you handed over:
- passwords first
- then card and bank details
- then documents and anything you installed
- ran
Act on the highest item on that list first.
How do I contact the real a well-known company?
Not through anything in Soltilid.live. Type the official website address into the browser yourself, use the app you already have, or use the phone number printed on your card, contract or a previous genuine invoice. Search results can be risky too, because scammers buy ads for support numbers.
Once you reach the real a well-known company, you can ask whether there is any problem with your account and report the scam message; many companies have a dedicated address for phishing reports on their security page.
Is it worth reporting a scam if I lost nothing?
Yes. Reports from people who did not fall for Soltilid.live are how blocklists, mail filters and hosting companies find new scam pages quickly, often before most recipients open the message. Reporting the message as phishing in your mail app is enough for most people.
If the message impersonates a company, its security or abuse team usually accepts forwarded copies too. Police reports matter mainly when money or documents were lost, but national fraud centres also collect reports without losses to spot campaigns.
Why did I receive Soltilid.live?
Scam messages go to millions of addresses and numbers collected from data breaches, public websites and simple guessing. Receiving Soltilid.live does not mean your PC is infected or that an account of yours was hacked.
If the message includes an old password of yours, it comes from a breach of some website; change that password wherever you still use it. Mark the message as spam or phishing so your provider blocks similar ones. Never reply to ask to be removed from the list: the sender treats a reply as proof that the address works.
What should I do first after Soltilid.live?
Secure the account involved. From a device you trust, open the official app or website directly, change the password and sign out of all sessions. Turn on two-step verification with an app or a passkey rather than text messages if the service allows it.
Then check recent activity, linked e-mail addresses and recovery phone numbers for changes you did not make. If an e-mail with the subject "You've made the 9.68-billionth search!" involved money, call your bank using the number on the back of your card. Only after that look into how it happened.
Will Fortect remove Soltilid.live?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Soltilid.live, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: HTTP cookie (read October 7, 2026)
- FTC: How to recognize and avoid phishing scams (read October 7, 2026)
- CISA: Recognize and report phishing (read October 7, 2026)
- Microsoft Support: Protect yourself from phishing (read October 7, 2026)
- NCSC: Phishing attacks, dealing with suspicious e-mails and messages (read October 7, 2026)