
Immediate Action Required: a fake virus alert, and what to do
"Immediate Action Required" is the headline of a fake virus alert: a web page that says your Mac or PC has a trojan called e.tre456_worm and tells you to press OK and download a cleaner. Close the page and download nothing; only if you downloaded, paid or entered details do you need the steps below.
Facts checked October 9, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
Do it yourself · free Remove Immediate Action Required alert yourself 2 steps, about 6 minutes, no software needed.
Start the steps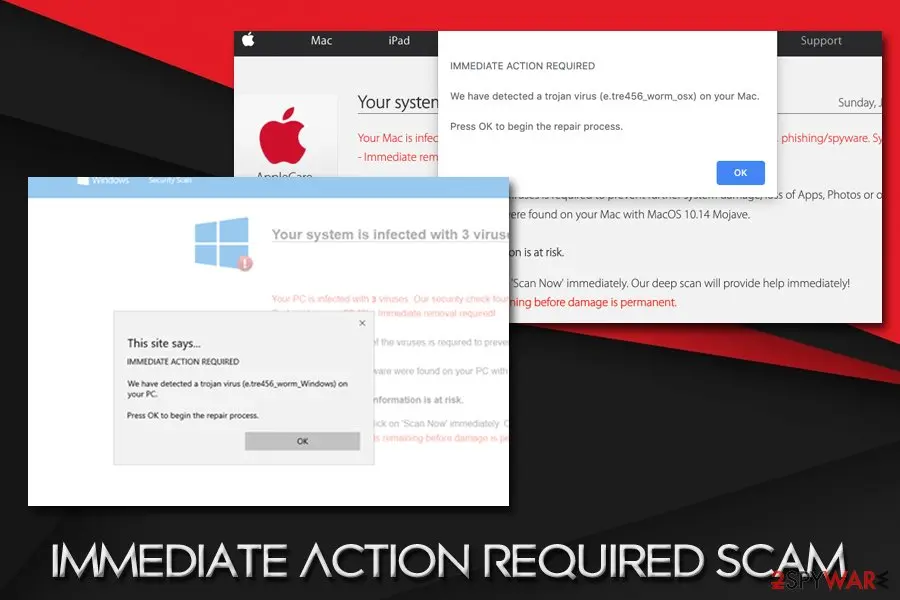
Immediate Action Required alert: summary
| Type | Fake virus alert (scareware page) for Mac and Windows; not a virus and not a message from Apple or Microsoft. Related: tech-support scam |
|---|---|
| Risk | Medium to high if you download the "cleaner" or pay for it; seeing the page alone is harmless |
| Symptoms | A page with an Apple or Windows look and a pop-up reading "IMMEDIATE ACTION REQUIRED. We have detected a trojan virus (e.tre456_worm_osx) on your Mac" with one OK button, a countdown and a fake scan |
| How to get rid of it | Do not click OK or Scan Now; close the tab (Command-W or Ctrl-W) or end the browser. If it returns on many sites, check apps, login items and extensions; if you downloaded the cleaner, see the plan |
| Our check | Registry and DNS check on 6 October 2026: of the seven addresses in our 2019 text, five (four parent domains and tweakingtools.info) have no registration record, one was registered in 2026 and one in 2024; no live test, so what a current copy does is unconfirmed |
| First seen | Our pictures are dated 9 May 2018 and 6 August 2019 on the pages themselves; our guide of 20 September 2019; PCrisk's Mac guide updated 19 January 2022 |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | None: a web page is not a file, so a scanner has nothing to detect unless a program was installed from it |
|---|---|
| Damage | A purchase for a program that fixes nothing, card details entered on the page, unwanted ads and tracking from a downloaded program |
| Name | Immediate Action Required |
| Addresses | apple[.]com-scan[.]live |
| Evidence | One write-up by a security site; details still limited |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against PCrisk's guides, Apple's, Microsoft's, Google's and Mozilla's support pages, the FTC's tech support scam page, registry and DNS answers for the addresses in our 2019 text, and our 2019 guide. We did not open a live page.
What the "Immediate Action Required" alert is
- What it is
- A web page, not a program on your device: a pop-up headed IMMEDIATE ACTION REQUIRED that says a trojan named e.tre456_worm_osx (Mac) or e.tre456_worm_Windows (PC) was found, drawn over a page made to look like Apple's or Microsoft's. The name belongs to the page; we found no source that lists it as a program
- What it claims
- That your computer has "3 viruses" (2 malware and 1 phishing/spyware), that a percentage of the system is damaged, and that personal and banking information is at risk
- What it wants
- A click on OK, then on Scan Now, a made-up scan, and then a download of a "cleaner" that the page rates highly. That program, and the payment for its "full version", is what the page is selling
- Does it need an infection?
- No. Visiting a site that shows it is enough to see it. A computer is only at risk from what you then download, open or pay for, so seeing the page does not mean you have a Trojan
- Which devices
- Our pictures show a Mac page and a Windows copy; the page changes its look to match what the visitor's browser reports. Any browser can display a web page like this. We have tested no steps for phones and name only what Apple's Safari page says
Our 2019 guide called this a "fake notification". It is not a notification in the browser sense (the sort you allow with a button); it is an alert box drawn by a page you opened. That difference decides what to remove: a page is closed, a program is uninstalled, and a notification permission is revoked.
rahsecure.com says, e.tree 456 worm and other words people search for
"rahsecure.com says Immediate Action Required" means the fake alert was opened by a page on rahsecure.com.
The browser puts the name of the site that opened a pop-up box in front of the word "says", so the line shows who sent the message, not that Apple or Microsoft did. The same holds for "securewalle.com says Immediate Action Required". Close the tab, click nothing in the box and download nothing it offers.
"e.tree 456 worm windows" and "e.tree 465 worm windows" are misspellings of e.tre456_worm, the made up trojan name this alert shows. On a Mac the page writes it as e.tre456_worm_osx; on a Windows PC the same page simply swaps in the Windows look.
It is not a real virus, and a web page is not a file, so a scanner has nothing to find unless you installed a program from it.
"Claim your resources, last step" is a phrase we found no reliable source for. Our reading is that it comes from a similar page that pushes you to click once more, download a file or enter details to finish a reward or a scan.
Treat it the way you treat this alert: close the tab and do not enter anything. If you already downloaded or paid, follow the steps for people who clicked Scan Now, downloaded or paid.
What the Immediate Action Required alert message looks like
| Route | What it means for you |
|---|---|
| A malicious site or ad | Our 2019 text says a visit to a malicious site can be enough. Microsoft says malicious ads on dubious sites, such as downloads of pirated software, videos or music, can redirect people to scam pages automatically. |
| Redirects from an unwanted application | PCrisk says most visitors reach these pages by redirect from unwanted applications or intrusive ads. Our 2019 text said people with adware see it more often, which fits. If it happens on many unrelated sites, check the apps and extensions below. |
| Free-software bundles | Our 2019 text says adware installs during freeware and shareware setup, and PCrisk says developers hide extra programs in Custom or Advanced settings. Apple says some third-party download sites include software you do not want. |
| Search results and other pages | PCrisk says scam pop-ups are reached by fake download buttons, torrent sites or search results, and shown according to your location and device. Our 2019 text added that the same visit can lead to a fake Windows technician. |
Ending up on the page does not mean your computer is infected, and certainly not with the trojan the page names. What matters is whether it happened once or keeps happening.
How to tell the Immediate Action Required alert message is fake
What we checked and what we did not
Immediate Action Required alert · registry and DNS check · 6 October 2026
- What Apple says about pop-ups like thisApple's Safari support page says some pop-ups are third-party ads that use warnings or prizes to look as if they come from Apple, and some claim to offer software or plug-ins to trick you into installing something unwanted.
- What the FTC and Microsoft sayThe FTC says tech-support scams start with a bogus warning, often a fake pop-up that looks like it comes from a well-known company. Microsoft says its error and warning messages never include a phone number, and that scam pages can go full screen, play audio and keep opening pop-ups.
- Four of the five Apple-style addresses in our 2019 textNeither com-faster.live, com-speed-macos.live, com-repair-os.live nor com-fast.live (the domains under the names Apple.com-faster.live, Apple.com-speed-macos.live, Apple.com-repair-os.live and Apple.com-fast.live) has a registration record in the registry's RDAP service today, and tweakingtools.info has none either. Those copies cannot be shown any more.
- apple.com-scan.liveThe domain com-scan.live was registered on 27 July 2026 and expires on 27 July 2027, so it is not the 2019 registration. The name apple.com-scan.live had no DNS answer when we asked. We do not know who holds the domain or what it will show, and we did not open it.
- nextmobile.siteNamed in our 2019 text. The registry shows it registered on 18 September 2024, after our guide was written, and the name resolves to Cloudflare addresses. We did not open it, so we say nothing about what it shows.
- Our own site testNone. We hold no live address and no 2026 copy of the page. One visit would not clear a site anyway: scam pages can differ by country, device, referrer, a delay or a click, so a quiet visit shows only that one visit was quiet. Whether this exact alert still circulates is unconfirmed.
A scareware page by its own wording Do not click OK or Scan Now and do not download what it offers. We could not test a live copy, so what a current version does is unconfirmed; the advice rests on Apple's, Microsoft's and the FTC's pages and on PCrisk's records.
The addresses behind it
| Address in our 2019 text | Where it stands on 6 October 2026 |
|---|---|
| Apple.com-scan.live (the address shown in the pop-up quote) | Registry: com-scan.live registered 27 July 2026; apple.com-scan.live has no DNS answer. Not opened. |
| Apple.com-faster.live, Apple.com-speed-macos.live, Apple.com-repair-os.live, Apple.com-fast.live | No registration record for the parent domains in the registry's RDAP service. |
| tweakingtools.info | No registration record in the registry's RDAP service. |
| nextmobile.site | Registered 18 September 2024; resolves. Not opened. |
The names follow one trick: the Apple name comes first and the real domain comes at the end, so apple.com-scan.live is a page on the domain com-scan.live. The real Apple site is apple.com, with nothing after it but a slash. Our 2019 text said the sites are shut down quickly because search and security companies flag them. We have no source for the reason, but the registry answers above are in line with short-lived domains.
The pages and versions we know of
9 May 2018
A Safari capture
The date printed on our Safari picture. The page shows the visitor's current date, so this is the capture day, not the start of the scam. Its address ends in .download, which is where the real domain sits.
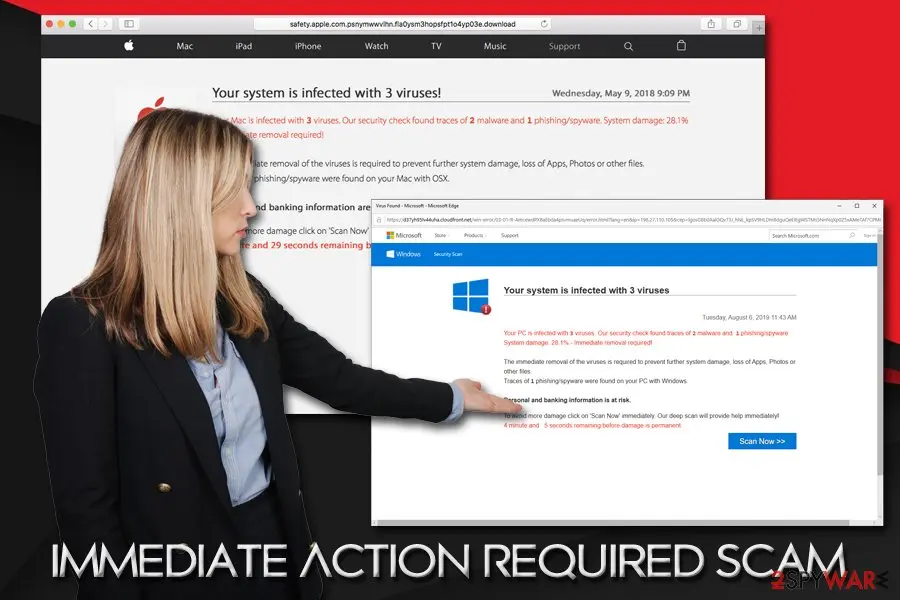
Two captures of the page: a Safari window dated 9 May 2018 on the page itself, and an Edge window dated 6 August 2019 at a long cloudfront.net address. Both read 28.1% damage and a countdown. The woman is stock art we added; she is not part of the page. 2018
PCrisk's first record
PCrisk records the fake alert for Mac with a fake scan and an Advanced Mac Cleaner download. The same name is used on a Windows page.
17 December 2018
A new version
PCrisk records an updated page that adds "Your MacOS 10.14 Mojave is infected with 3 viruses!" and promotes Mac Cleanup Pro.
6 August 2019
The Windows copy
The date printed on our Edge capture: the same text in Microsoft colours with a Windows Security Scan header.
20 September 2019
Our guide
We published the first version of this guide. We updated it on 29 June 2020.
19 January 2022
PCrisk's page updated
PCrisk's guide for the Mac version shows its last update on this date.
25 August 2026
Same words, a different scam
PCrisk updates its guide to an e-mail headed "Immediate Action Required" that asks you to update an e-mail password. It is not this alert; see the next section.
6 October 2026
This rewrite
We corrected the notification wording, separated the page from adware, checked the old domains and rewrote the steps for current macOS and Windows.
Same words, other scams
| Name | What it is | What to do |
|---|---|---|
| "Immediate Action Required" e-mail | PCrisk (updated 25 August 2026) describes an e-mail that says you must update your e-mail password within 72 hours or the account will stop receiving mail, with a "Click to Update Password" button that opens a fake login page. Another copy claims 19 mails are pending and will be deleted in 3 hours. | Do not click. If you entered a password, change it from another device and sign out of other sessions (PCrisk). It has nothing to do with the pop-up on this page. |
| Pornographic virus alert from Microsoft | A fake Microsoft alert, listed in our 2019 text. Not re-checked in 2026. | Close the tab; Microsoft says its messages never include a phone number. |
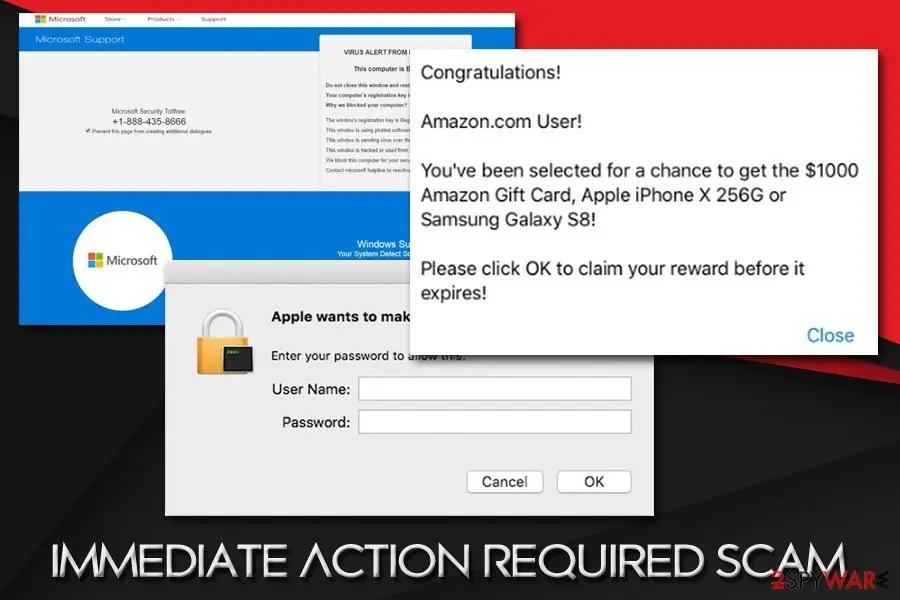
| Apple wants to make changes | A fake Apple password prompt like the dialog in our picture below. Not re-checked in 2026. | Do not type a password into a box a web page opened; close the page. |
| Unlock this Page to Continue | Listed in our 2019 text as a similar scam. Not re-checked in 2026. | Leave the page. |
| Google Critical Security alert | Listed in our 2019 text as a similar scam. Not re-checked in 2026. | Leave the page. |
How to spot the next one
Do
- Read the address bar: a page from Apple is on apple.com and one from Microsoft is on microsoft.com, not on apple.com-something-else
- Close the tab with Command-W or Ctrl-W without clicking inside it
- Install apps from the App Store or from the developer's own site, not through an ad or a link on a page
- Choose Custom or Advanced when an installer offers it, read the small print, and untick pre-ticked extras
- Keep the system and browsers updated, and keep a backup so a mistake costs little
Don't
- Do not click OK on a pop-up that says your computer has a virus
- Do not download a "cleaner" a web page tells you to install
- Do not trust a scan that runs inside a web page: a page cannot scan your computer
- Do not choose Restore or Reopen last session after closing a scam page
Our 2019 guide warned that pre-ticked boxes, small print and misleading button placement are how extra programs get installed, and that popular download sites have policies that third-party sites may not. We kept the habits and dropped the claim about site policies, because Apple's advice is simpler: get apps from the App Store or from the developer. A VPN, which the old page promoted, does not stop a web page from showing a fake alert.
Is Immediate Action Required alert dangerous? What the senders want
What the alert says, line by line
| What the page says | What is wrong with it |
|---|---|
| IMMEDIATE ACTION REQUIRED. We have detected a trojan virus (e.tre456_worm_osx) on your Mac. Press OK to begin the repair process. | The box is drawn by the page and speaks for the page. Chrome titles such boxes with the page's own address ("Apple.com-scan.live says" in our 2019 text); Apple is not speaking. "Repair" means the fake scan. |
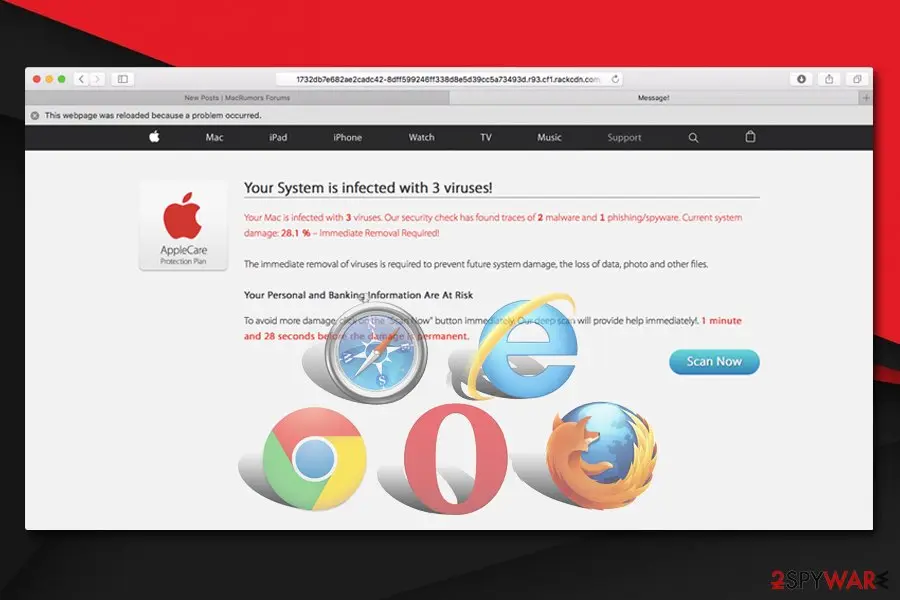
| Your system is infected with 3 viruses! | Every visitor gets the same count. A web page cannot look inside your computer, which is also PCrisk's reason for calling any scan shown by a page a scam. |
| System damage: 28.1% - Immediate removal required! | A computer does not report a damage percentage. Our pictures show 28.1% and the results page shows 33.2%; the number is a prop. |
| A countdown: "1 minute and 28 seconds" in one picture, "4 minute and 5 seconds" in another, and five minutes in our 2019 text | The timer runs from the page's own script and changes between copies. It exists to make you click before you think. |
| The Apple look: a logo, the Mac, iPad and iPhone menu bar, an AppleCare Protection Plan badge | Our 2019 guide noted the badge borrows a real Apple product name. Apple's pages are on apple.com; the address in the browser, not the artwork, tells you where you are. |
| Virus names such as e.tre456_worm_osx or Zeus Trojan | The first name is invented. Our 2019 text says the pages sometimes use names of real malware; a name shown by a page proves nothing about your computer. |
Our reasoning, not a sourced fact: if a program really were stealing your data, it would not stop to show a countdown. The countdown tells you the page is selling something.
The fake scan and the download it sells
Step 1
OK
The pop-up has one button. It starts the page's own scan; our 2019 text said it offers an "alleged system scan". Nothing on your computer is read.
Step 2
Scan Now and a progress bar
The page shows a scan running and then lists results. They are the same for everybody. PCrisk's page on the Mac version says the scan is fake and the results are used to push dubious software.
Step 3
Made-up names and a damage figure
The results page lists three invented viruses (Tapsnake, CronDNS and Dubfishicv on the Mac page that PCrisk copied), a risk of HIGH and "infected files" in folders that no source we found describes. On the Windows copy the list includes a name such as Ransomware 2.0.
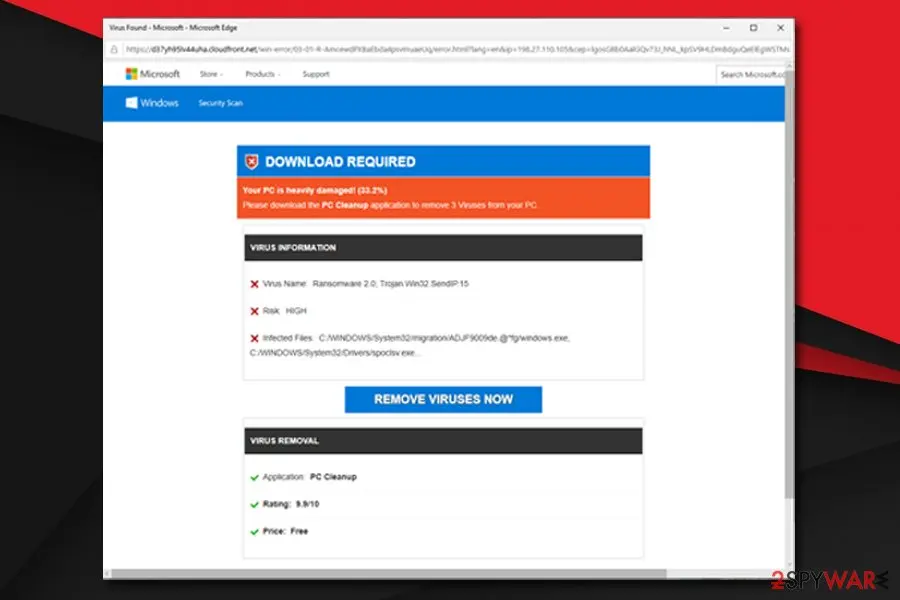
The page at the end of the fake scan, in its Windows form: "Your PC is heavily damaged! (33.2%)", a list of invented virus names with risk HIGH, a blue Remove Viruses Now button, and the program to download, PC Cleanup, rated "9.9/10" and priced "Free" by the page itself. Step 4
A cleaner, rated and priced by the page
The button says Remove Viruses Now and the page names a program to download: Advanced Mac Cleaner in PCrisk's 2018 copy, Mac Cleanup Pro in its later one, PC Cleanup on the Windows page above. Our 2019 text also named Mac Auto Fixer, Driver Tonic and Malware Crusher; we found no 2026 source for those, so treat them as unconfirmed.
Step 5
Payment
PCrisk says the free version cannot remove what it lists and asks for payment for the full one. That is the same pattern as a fake support call: the "problem" and the fix come from the same seller.
Our 2019 text observed that the scheme matches a tech-support scam and that what the programs do mirrors the page they came from: both invent a problem and then offer a paid fix. We have tested none of these programs, so we make no claim about their behaviour beyond what PCrisk records.
Why a page like this works on people
| The pressure | How it works |
|---|---|
| Authority | Apple's or Microsoft's colours, logos and a product badge make the page look official before you read a word. |
| Urgency | A countdown, a percentage and the words IMMEDIATE ACTION REQUIRED leave no time to check the address. The FTC makes a similar point about tech-support scams: they rely on stories, threats and pressure. |
| Fear of loss | The text names the things you care about: apps, photos, banking information. |
| A single easy action | One OK button. Nothing asks for a password or a phone call, so it feels harmless to press it. |
Our 2019 guide said these scams are easy for experienced users to spot and that the aim is to get people to install software and pay. We keep that and add the part we can source: the FTC says legitimate tech companies do not contact you to say there is a problem with your computer, and Microsoft says its error messages never include a phone number. We dropped the claim that one group is more vulnerable than others, because no source we read supports it.
What clicking can cost
- High
Paying for a program that fixes nothing
PCrisk says the free version shows threats it cannot remove and asks for payment for the full version. If you paid, call the bank or card issuer.
- High
Handing over card or personal details
A fake scan result and a payment form can collect card numbers and an e-mail address. The FTC says to change a password you gave a scammer right away, and wherever else you use it.
- Medium
An unwanted program on your computer
PCrisk records the cleaners these pages promote as unwanted applications that track browsing and show intrusive ads, and says such ads can lead to other unwanted programs or malware. Our 2019 text said the same, adding that they can be hard to remove; we found no source for that part.
- Low
Only seeing the page
A page that shows a warning does not change your computer, and closing it ends it. Our 2019 text listed money loss, useless software and malware infections; all three begin with a download or a payment.
If you called the number or paid
| What you did | What to do |
|---|---|
| Clicked OK or Scan Now, downloaded nothing | Close the page as above. As far as PCrisk and Apple describe, the click alone installs nothing. Look in your Downloads folder in case the browser saved a file. |
| Downloaded a file but did not open it | On a Mac, open Finder > Downloads and drag the file (often a .dmg or .pkg) to the Trash. On Windows, open File Explorer > Downloads and delete it. |
| Installed the program | On a Mac, drag the cleaner from Finder > Applications to the Trash, then check Login Items (below). On Windows, open Start > Settings > Apps > Installed apps, select More > Uninstall next to the program (Microsoft), then run a full scan in Windows Security. |
| Entered card details or paid | Call the bank or card issuer, say it was a scam and ask to cancel the card and dispute the charge. Our 2019 text said to report it to local authorities that deal with fraud; in the United States that is ReportFraud.ftc.gov. |
| Gave a password | Change it from another device, and change it everywhere you used it (FTC). |
Microsoft adds that if you let someone connect to your computer, you should consider resetting it. That applies to fake support calls; this alert does not ask for a call, so it only matters if a phone number was involved.
What to do about Immediate Action Required
Do not call the number in the message.
If you already called or let someone connect, follow every step.
Step 1: Stop replying and keep the evidence
Do not reply, pay, or send documents, even to "cancel" or "verify" something: every answer marks you as a target worth more messages. Take screenshots of the messages, the sender address, the phone numbers and any payment details, then block the sender.
If you already sent money or an ID document, the next steps cover what to do. The screenshots work the same on a phone or on Windows 11 and Windows 10, where Windows + Shift + S captures part of the screen.
Full procedure with screenshots: What to do after paying a scammer
Step 2: Report it
A report takes ten minutes and helps take Immediate Action Required down.
Send it to ReportFraud.ftc.gov in the US (and ic3.gov when money was lost), to Action Fraud in the UK, or to your national police in the EU, with screenshots, sender details and any payment references.
Report the message inside the mail or chat app too. Keep a copy of everything until the case is closed, whether you use a phone or a Windows 11 or Windows 10 PC.
Full procedure with screenshots: Report a cyber attack or scam to the authorities
First: how to close the alert
- 1
Do not click OK, Scan Now or Remove Viruses Now
Apple says some pop-ups have fake buttons that resemble a close button. Here OK starts the scam. Our 2019 text said to ignore the alert and not to download the suggested apps; that is still the right first move.
- 2
Leave the page
On a Mac, click the address bar and type a new address or a search (Apple's advice), or close the tab with Command-W. On Windows close it with Ctrl-W. If unsure, close the whole window.
- 3
If the page will not close, end the browser
PCrisk says some scam pages use scripts that stop a tab from closing, and that you then end the browser from Activity Monitor or restart the Mac. On a Mac press Command-Q, or Option-Command-Esc, choose the browser and click Force Quit. On Windows, if the page is full screen, press Esc or F11, then Ctrl-Shift-Esc, select the browser and click End task. Microsoft says scam pages can go full screen and try to disable Task Manager; if so, restart the PC. These key presses are standard but untested here on a live alert.
- 4
Reopen without the old tabs
In Safari, quit it, then hold Shift while opening it so it does not reopen the old windows (Apple). In other browsers do not choose Restore or Reopen last session: PCrisk warns that restoring it takes you back to the page.
If you only saw the page, you are done with the urgent part. Nothing needs to be uninstalled and no scan is required for a page you closed.
Stop it coming back: notifications and extensions
| Browser | Remove the notification permission | Check extensions |
|---|---|---|
| Safari (Mac) | Apple menu > System Settings > Notifications, click the website under Application Notifications and turn off Allow Notifications. To stop the requests: Safari > Settings > Websites > Notifications and deselect "Allow websites to ask for permission to send notifications". | Safari > Settings > Extensions: turn off or uninstall any you did not add. Pop-ups are managed under Websites > Pop-up Windows (Apple). |
| Google Chrome | More > Settings > Privacy and security > Site settings > Notifications. Add the site you do not know under "Not allowed to send notifications" (Chrome Help). | Type chrome://extensions and remove any you did not add. Chrome Help also lists Reset settings, if the page keeps returning. |
| Mozilla Firefox | Menu > Settings > Privacy & Security > Permissions > Notifications > Settings…, select the site and click Remove Website (Mozilla). | Type about:addons, open Extensions and remove anything you did not add. |
| Microsoft Edge | Type edge://settings/content/notifications and remove the site you do not know. We did not check Edge's menu names against a page of Microsoft's. | Type edge://extensions and remove any you did not add. |
This alert is a page, not a notification, so these steps matter only if you once clicked Allow on a site that sent you to it. Our 2019 guide said to reset each browser after removing adware; we keep it as a last step, for a page that returns after everything else. Internet Explorer was retired in 2022 and is not covered.
If the pop-ups keep coming: look for unwanted software
Our 2019 guide said the alert is seen most by people with adware, and that the programs causing it must be found and uninstalled. Apple and PCrisk agree on the narrower part: if you see such pages on many unrelated sites, something on the computer may be sending you there. If it appeared once, that site's ads are the cause.
- 1
Update, then restart
Apple says to update to the latest macOS and, if it is already current, restart: macOS includes a tool that removes known malware at restart. On Windows, apply updates under Start > Settings > Windows Update > Check for updates (Microsoft).
- 2
Remove apps you did not choose
On a Mac, in Finder > Applications, sort by Date Added and drag anything you do not recognise, or installed just before the alerts began, to the Trash. On Windows use Settings > Apps > Installed apps and sort by install date.
- 3
Remove unknown login items on a Mac
System Settings > General > Login Items & Extensions. Select an item you do not know and click the remove (minus) button (Apple).
- 4
Check extensions
Use the table above. An extension you did not add is a more common cause than a file you cannot see; we have no figures for that, so treat it as a place to look.
- 5
Scan, with the right expectation
Our 2019 text recommended automatic removal software. A scan can find an installed cleaner or adware, but this alert is a web page with nothing to find, so a clean scan does not mean the page cannot come back. Microsoft's page suggests a full scan in Windows Security after you uninstall what scammers asked for. We recommend no product and tested none.
PCrisk's note on PUAs: they record data such as search queries and visited pages and show intrusive ads. That is why unfamiliar programs are worth removing even when the alert itself was only a page.
Questions about Immediate Action Required alert
What is the "Immediate Action Required" pop-up?
It is a fake virus warning shown by a web page, not by your computer. The page copies the look of Apple or Microsoft, opens a box headed IMMEDIATE ACTION REQUIRED that names a trojan called e.tre456_worm_osx or e.tre456_worm_Windows, and tells you to press OK. A pretend scan follows, then a push to download a cleaner and pay for it.
Nothing by that name exists as a program that we could find, and the page cannot see your files. Close the tab and download nothing. The plan on this page covers what to do if it keeps returning.
Is e.tre456_worm_osx a real virus?
No, it is a name written into the page. PCrisk calls the message a fake error used to push dubious software, and the three viruses its results page lists later (Tapsnake, CronDNS, Dubfishicv) are also names printed by the page; we found no source showing them as programs on a Mac.
A web page cannot scan a computer, so its results are the same for every visitor. Our 2019 text noted that scammers sometimes use real malware names such as Zeus, but a name on a page does not mean a computer has that malware. What can be real is an unwanted program that sends you to the page.
How do I get rid of the Immediate Action Required alert?
Close the page instead of trying to remove a virus, because there is none. Do not click OK, Scan Now or Remove Viruses Now. Close the tab with Command-W on a Mac or Ctrl-W on Windows.
If it will not close, end the browser: Command-Q or Force Quit on a Mac, Task Manager on Windows (these key presses are standard but untested on a live alert).
In Safari, hold Shift while reopening so the old tabs do not return. In other browsers, do not choose Restore last session. If it comes back on different sites, check apps and extensions you did not add.
I clicked OK on the Immediate Action Required pop-up. Am I infected?
Probably not. By PCrisk's description, OK only starts the page's own fake scan, and an install needs a download that you then open. Close the page, look in your Downloads folder and your installed apps for anything new from that day, and remove a program you did not choose.
If you entered card details, call your bank and ask to cancel the card. If you gave a password, change it from another device and everywhere you reuse it, as the FTC advises. If nothing new appears and you entered nothing, you can stop there.
I downloaded the cleaner the page told me to. What now?
Remove it and check what it left behind. On a Mac, drag the app from Applications to the Trash, delete the downloaded file, then open System Settings, General, Login Items and Extensions, and remove an item you do not know.
On Windows, open Settings, Apps, Installed apps, choose More, then Uninstall, and run a full scan in Windows Security, as Microsoft suggests.
PCrisk records the cleaners these pages promoted as unwanted applications that show ads and track browsing. If you paid, ask the card issuer to cancel the card and dispute the charge. We have not tested these programs.
Why does the Immediate Action Required alert keep coming back?
Something keeps sending you there. PCrisk says most visitors reach these pages by redirect from unwanted applications or intrusive ads, and Apple says pop-ups that will not go away can mean adware, which can arrive with downloads from third-party sites.
If it only happens on one site, that site's ads are the source. If it happens everywhere, check Applications or installed apps, login items, profiles and extensions, update the system and restart. Restoring the last session also brings the page back, so open a fresh window after you close it.
Does the Immediate Action Required scam work on iPhone, iPad and Android?
A web page can open in any browser, so a page like this can appear on a phone too, but we have no copy of this alert on one and tested no steps.
Apple's Safari page says that on an iPhone or iPad you can open Settings, tap Apps, tap Safari and turn on Block Pop-ups, and that you should avoid interacting with pop-ups that take over the screen.
If a page will not close, enter a new address in the search field or close the tab. Do not install an app a page tells you to; get apps from the official store.
Is the "Immediate Action Required" e-mail the same scam?
No, the words are the same but it is a different scam. PCrisk's page, updated on 25 August 2026, describes an e-mail that claims you must update your e-mail password within 72 hours or the account will stop receiving mail, with a button that opens a fake login page meant to collect your address and password.
A fake alert box with a countdown on a web page is this guide. If you entered a password on a page from an e-mail, change it from another device, sign out of other sessions and check your account for changes, as PCrisk advises.
Do I need to scan my computer after seeing this alert?
Not if you only saw the page and closed it. The alert is a web page with no file to find, so a scan has nothing to detect unless you installed something.
If you downloaded or installed a cleaner, or if the alert returns on many sites, remove the program and run a scan with the security software you already use; Microsoft suggests a full scan in Windows Security after you uninstall what scammers asked for.
A clean scan does not mean the page cannot come back. We recommend no particular product and did not test any.
Will Fortect remove Immediate Action Required?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Immediate Action Required, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- PCrisk: E.tre456_worm_osx Trojan Virus POP-UP Scam (Mac), updated 19 January 2022 (read October 6, 2026)
- PCrisk: How to spot scams like "Immediate Action Required" (e-mail), updated 25 August 2026 (read October 6, 2026)
- Apple Support: Block pop-up ads and windows in Safari (January 2026) (read October 6, 2026)
- Apple Safari User Guide: Customize website notifications in Safari on Mac (read October 6, 2026)
- Apple Support: Open items automatically when you log in on Mac (read October 6, 2026)
- FTC Consumer Advice: How To Spot, Avoid, and Report Tech Support Scams (September 2025) (read October 6, 2026)
- Microsoft Support: Protect yourself from tech support scams (read October 6, 2026)
- Microsoft Support: Uninstall or remove apps and programs in Windows (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- Mozilla Support: Web Push notifications in Firefox (read October 6, 2026)
- RDAP answer for com-scan.live (registered 27 July 2026) (read October 6, 2026)
- RDAP answer for nextmobile.site (registered 18 September 2024) (read October 6, 2026)
- RDAP answer for com-faster.live (not found) (no longer online) (read October 6, 2026)