
Thickwatchhad.xyz e-mail scam: how to spot it and what to do
Thickwatchhad.xyz is a scam website created by cybercrooks to mislead users. People do not encounter it intentionally but are rather redirected from some other website after they click a link or are rerouted by malicious scripts.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove Thickwatchhad.xyz e-mail scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps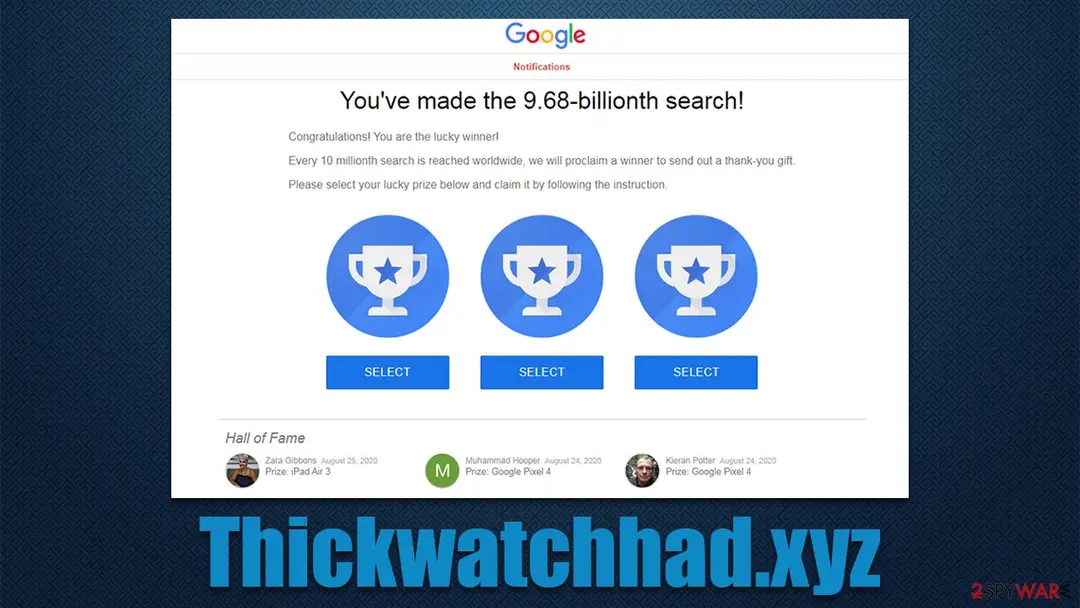
Thickwatchhad.xyz e-mail scam: summary
| Distribution | Adware, redirects from other websites, malicious links |
|---|---|
| Name | Thickwatchhad.xyz |
| Type | Scam, phishing, adware |
| Goal | Make people provide personal information, subscribe to useless services, download malicious software or subscribe to push notifications |
| Dangers | Malicious software can cause redirects to malicious websites – financial losses, malware infections, and data disclosure can be more likely |
| Symptoms | A phishing e-mail asking you to sign in |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Evidence | One write-up by a security site; details still limited |
|---|---|
| Arrives as | |
| Pretends to be | A well-known company |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| First seen | 11 May 2022 |
| Facts checked | 6 October 2026 |
What the Thickwatchhad.xyz e-mail scam e-mail looks like
You've made the 9.68-billionth search!
Congratulations! You are the lucky winner!
Every 10 millionth search is reached worldwide, we will proclaim a winner to send out a thank-you gift.
Please select your lucky prize below and claim it by following the instruction.
How to tell the Thickwatchhad.xyz e-mail scam e-mail is fake
From our report of May 2022 · not reviewed since
- You should check your system with to fix virus damage and remove various trackers from your browsers
Is Thickwatchhad.xyz e-mail scam dangerous? What the senders want
From our report of May 2022 · not reviewed since
Thickwatchhad.xyz ads are fake and seek to make you provide your personal details
Thickwatchhad.xyz is a scam website created by cybercrooks to mislead users.
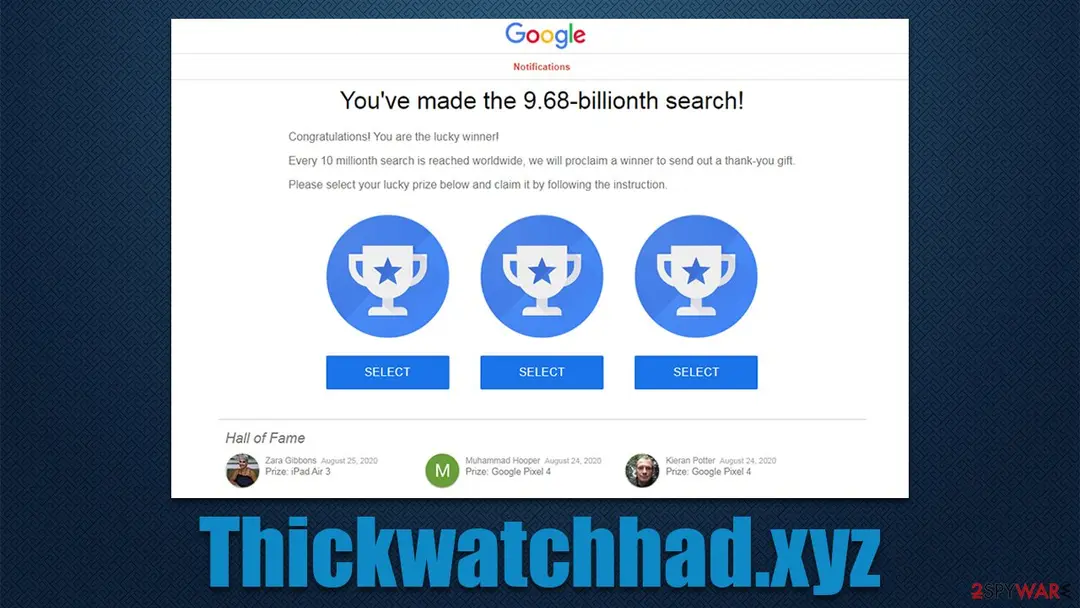
People do not encounter it intentionally but are rather redirected from some other website after they click a link or are rerouted by malicious scripts. People do not expect to see that they have allegedly won a prize from Google, Amazon, or another well-known company.
Usually, the message claims that the user was somehow selected to receive a free gift, which is usually something valuable, such as iPhone, PlayStation, or a TV. Surprised by such a course of events, some users believe that they are lucky and that they can actually receive a free gift.
However, the true purpose of Thickwatchhad.xyz is to make users provide their personal information, make them download suspicious software, or make them spend money on useless services. Usually, people are asked to provide their home address, email, or even credit card details, which cybercriminals can later abuse.
We do not recommend interacting with any of the messages shown on this scam site. If you have experienced frequent redirects to Thickwatchhad.xyz, there might be adware installed on your device, so we will explain how to remove it. Also, we will give tips on how to remediate the situation after being a victim of a scam.
From our report of May 2022 · not reviewed since
Scammers seek to trick gullible users
The element of surprise is very powerful when it comes to various online fraud schemes.
A gift card and similar giveaway scams often focus on convincing users to proceed thanks to familiar brands or company names, such as Google or Amazon. One of the most commonly encountered messages on the Thickwatchhad.xyz site is the following:
The "You've made the 9.68-billionth search!" fake message implies that users were selected due to them performing the 10 millionth search and that they are now eligible for a "thank-you" gift. They are then shown three trophies or presents, which look identical - users are meant to choose one of the alleged gifts.
Once they do, they usually find out that they are about to receive a new iPhone, PlayStation, or a similar valuable item, which makes them happy. Without thinking much, they proceed and then are asked to enter their home address, email, and sometimes even credit card information to allegedly receive the gift.
However, the item never arrives, and only later do users realize that they have provided their personal information to cybercriminals. In some other cases, people might be tricked into subscribing to useless services or paying money directly.
What to do after the Thickwatchhad.xyz e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you typed a password on the page the Thickwatchhad.xyz message opened, assume the sender has it. Go to the real site by typing its address yourself and change the password there, choosing one you have never used.
Change it anywhere else the same password was used, and sign out all other sessions if the service offers it. Any browser on Windows 11 or Windows 10 will do, as long as you do not follow the e-mail's link.
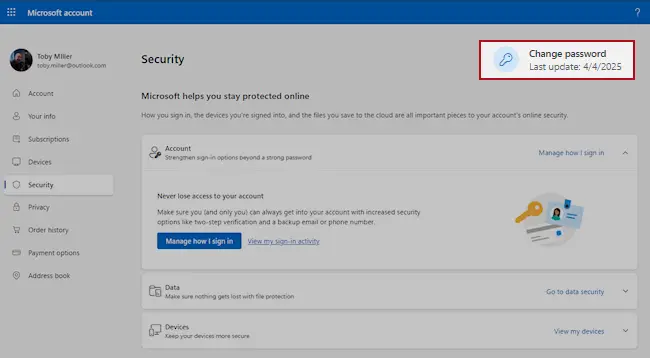
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
With two-step verification on, a stolen password alone no longer opens the account, because a sign-in from a new device also needs a code from your phone.
Switch it on for the e-mail account first, then for banking, shopping and social accounts that use that address.
Check the recovery phone, the recovery e-mail and any forwarding rules while you are in the settings, since attackers change them to come back. The pages are the same on Windows 11 and Windows 10.
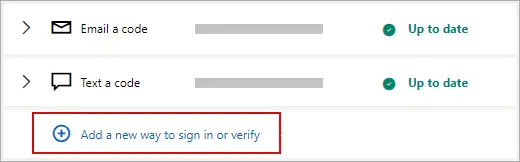
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Do not reply and do not click anything else in the message. In Outlook select the e-mail and choose Report > Report phishing; in Gmail open the three-dot menu next to Reply and pick Report phishing.
That trains the filter for everyone on the service, and the message goes to the junk folder. If the e-mail came to a work address, forward it to your IT team as an attachment first.
The steps are the same in the web mail and the mail apps on Windows 11 and Windows 10.
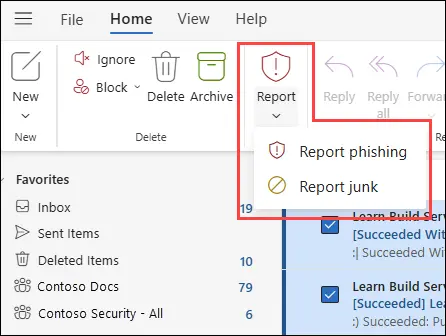
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A fake sign-in page only steals what you type, so most readers can skip this step. If the Thickwatchhad.xyz e-mail made you download or open a file, delete it and scan the PC.
In Windows Security > Virus & threat protection > Scan options, run a Full scan and then Microsoft Defender Antivirus (offline scan) > Scan now. The offline scan restarts Windows 11 or Windows 10 and takes about 15 minutes.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
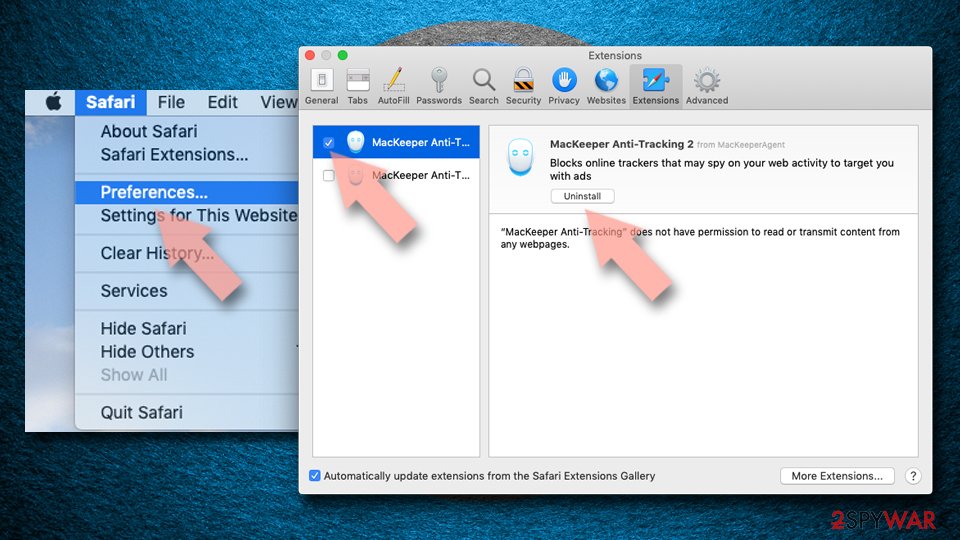
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
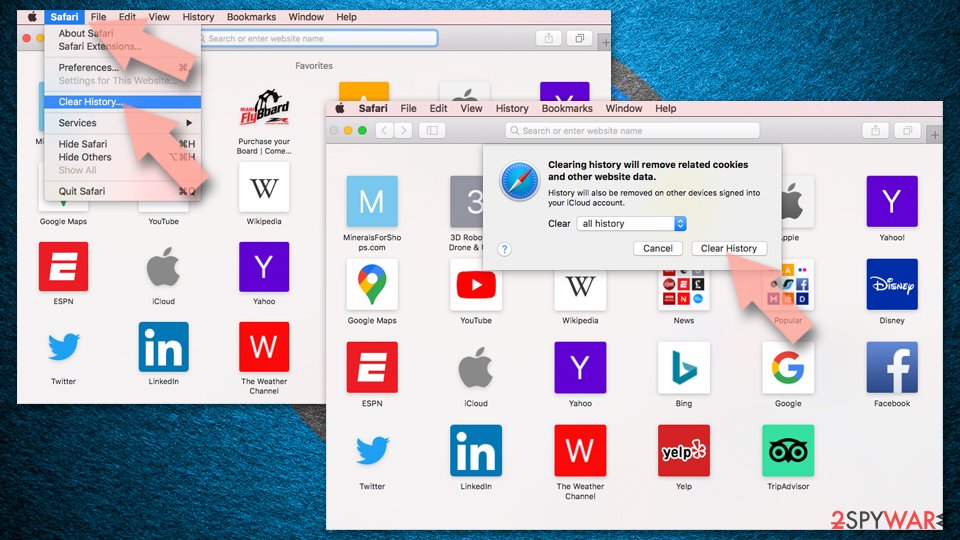
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
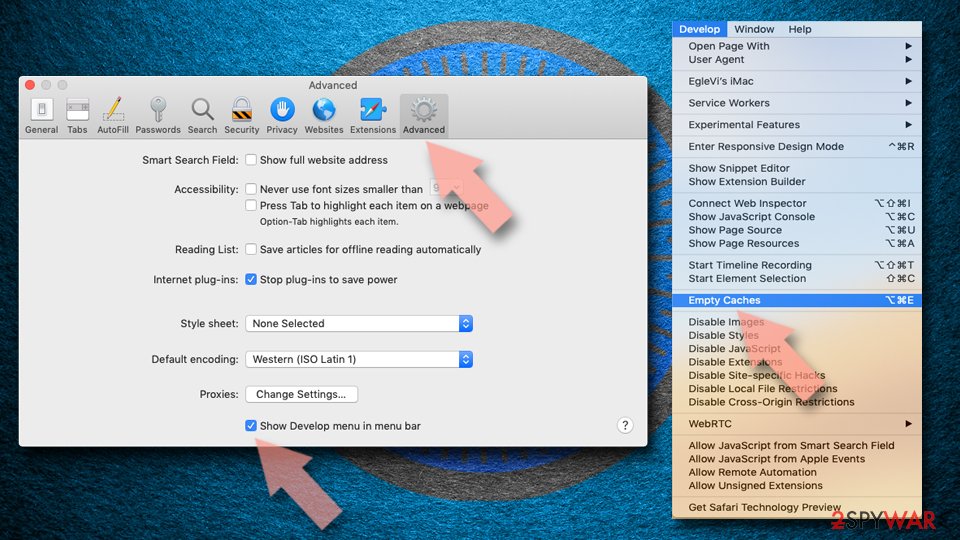
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
From our report of May 2022 · not reviewed since
What to do now?
After you encounter a scam online, the best thing to do is to leave the page by clicking the "X" button on the browser tab, without interacting with it at all. Some users who understand it's a scam wonder whether their personal safety or computer security has been compromised; as long as you don't interact with any element of the scam site, you are likely to be safe.
However, if you have provided your personal information, expect to receive more phishing attempts against you. For example, if crooks know your phone number and name, they might call you with this information, pretending to be somebody from law enforcement or other reputable association, and make you pay money.
Thus, the first advice is to ignore all the incoming emails, calls, letters, or any other communications that might seem believable. Always contact the party the crooks claim to be direct via the official support number, and never provide further personal details.
From our report of May 2022 · not reviewed since
Check your device for adware
Your next step is to check your device for infections.
Sometimes, the main goal of online fraud is to make people download and install software, which crooks benefit financially from. This software sometimes could be categorized as adware or even malware, so it is important to check your system thoroughly.
Likewise, if you experience more ads than you are used to and frequently encounter phishing content online, adware could already be installed on your system.
While moving apps into Trash is usually how you delete most normal applications, adware tends to create additional files for persistence. Thus, you should look for .plist and other files that could be related to the virus. If you are not sure, skip this step entirely.
To fully remove an unwanted app, you need to access Application Support, LaunchAgents, and LaunchDaemons folders and delete relevant files:
You should also check the installed extensions, as adware is known to spread as such. You can find the full list of the installed add-ons by clicking the "Extensions" button next to the browser menu or accessing browser settings directly.
- Enter Control Panel into the Windows search box and hit Enter or click on the search result.
- Under Programs, select Uninstall a program.
- From the list, find the entry of the suspicious program.
- Right-click on the application and select Uninstall.
- If User Account Control shows up, click Yes.
- Wait till uninstallation process is complete and click OK.
- From the menu bar, select Go > Applications.
- In the Applications folder, look for all related entries.
- Click on the app and drag it to Trash (or right-click and pick Move to Trash)
- Select Go > Go to Folder.
- Enter /Library/Application Support and click Go or press Enter.
- In the Application Support folder, look for any dubious entries and then delete them.
- Now enter /Library/LaunchAgents and /Library/LaunchDaemons folders the same way and terminate all the related .plist files.
From our report of May 2022 · not reviewed since
Check your browsers
After adware or malware removal, we strongly recommend cleaning your web browsers from trackers and other leftover files.
Upon installation, adware leaves cookies and other items that could be used by third parties to monitor your online activities. For example, they might trace which websites you visit, which links you click, and what you are looking for via your search queries.
The easiest way to clear your browsers and fix virus damage after malware removal is by using the repair and maintenance app. It can find damaged system components and replace them with brand new ones within just a few minutes. Likewise, the browser cleaning process is performed at the same time, and you don't have to worry about anything.
Questions about Thickwatchhad.xyz e-mail scam
I opened the "You've made the 9.68-billionth search!" e-mail. Am I hacked?
No. Opening and reading a phishing e-mail does not give anyone access to your account or your PC. Modern mail programs block scripts and remote content by default, so reading the message "You've made the 9.68-billionth search!" only showed you text and pictures.
The danger comes from clicking the button and typing your password on the page it opens, or from opening an attached file. If you did neither, report the message as phishing and delete it.
If you clicked but closed the page without typing anything, there is also nothing to fix. If you did type a password, change it from another device and turn on two-step verification.
The "You've made the 9.68-billionth search!" page asked for my code too. Is two-step verification enough?
Not when you typed the code yourself. Some phishing pages pass your password and the one-time code to the real site in real time, which lets the attacker sign in once. Change the password immediately, then sign out of all sessions so the stolen session ends.
Check the account's security page for new devices, app passwords and recovery details, and remove anything you did not add. A passkey or a hardware key is the strongest protection against this trick, because it cannot be typed into a fake page. Keep the e-mail "You've made the 9.68-billionth search!" for your report, then delete it.
Could Thickwatchhad.xyz be a genuine message?
We checked it, and it is not. A well-known company is only the costume. The message exists to get your password, and real companies handle that inside your account, after you sign in normally, not through links, attachments or phone numbers in a message you did not expect.
Scammers copy logos and footers perfectly, so the design proves nothing. The sender address, the link target and the request are the reliable signs, and all three point to a scam here. Delete it, and if you are worried, check your account directly.
Why does Thickwatchhad.xyz say that your account needs urgent attention?
Because that story works. A problem that needs fixing, a deadline and a simple solution make people act before they check.
The claim that your account needs urgent attention is the same for everyone who received Thickwatchhad.xyz; it was written once and sent in bulk. Nothing about your own situation triggered it.
If you are unsure, look at the real account or service the normal way, without using the message. The claim will not be there, which settles the question. Then report the message.
What does Thickwatchhad.xyz want from me?
In the end, your password. Everything else in Thickwatchhad.xyz, from the logo to the deadline, is there to get you to that point without stopping to think. Knowing the goal helps you judge your risk.
If you did not give it, you lost nothing and can delete the message. If you did, the steps in this guide are ordered by what you handed over:
- passwords first
- then card and bank details
- then documents and anything you installed
- ran
Act on the highest item on that list first.
How do I contact the real a well-known company?
Not through anything in Thickwatchhad.xyz. Type the official website address into the browser yourself, use the app you already have, or use the phone number printed on your card, contract or a previous genuine invoice. Search results can be risky too, because scammers buy ads for support numbers.
Once you reach the real a well-known company, you can ask whether there is any problem with your account and report the scam message; many companies have a dedicated address for phishing reports on their security page.
What is the single best habit against scams like this?
Never act on a message through the message itself. If something claims to be from a well-known company and asks you to sign in, pay, call or open a file, close it and go to the service the way you always do:
- a bookmark
- the app
- the number on your card
Real problems will be visible there. This one habit defeats almost every phishing, invoice, delivery and account-suspension scam, regardless of how convincing the design is, because the scammers can copy the look but not the real account.
Should I scan my PC after Thickwatchhad.xyz?
Yes, it is a quick way to rule out one possible cause. Open Windows Security and run a full scan; it takes about half an hour.
If it finds nothing and there are no unknown programs or extensions, the account problem behind an e-mail with the subject "You've made the 9.68-billionth search!" most likely started with a leaked or phished password.
If it finds a stealer or trojan, remove it first, then change your passwords from another device, then sign out of all sessions, because stolen cookies keep working until you do.
I entered my password on the fake page. What should I do?
Change the password on the real site right away, through its own website or app, and sign out of all sessions.
If you use the same password anywhere else, change it there too. Turn on two-step verification with an authenticator app or a passkey. Check the account for changes:
- recovery e-mail
- phone number
- forwarding rules
- recently sent messages
If you can no longer sign in, use the provider's account recovery page. Tell your contacts if the account sent messages in your name.
Will Fortect remove Thickwatchhad.xyz?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Thickwatchhad.xyz, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- FTC: How to recognize and avoid phishing scams (read October 6, 2026)
- CISA: Recognize and report phishing (read October 6, 2026)
- Microsoft Support: Protect yourself from phishing (read October 6, 2026)
- NCSC: Phishing attacks, dealing with suspicious e-mails and messages (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)