
viewgit.sbs: a server listed for a PowerShell script tagged RedHiveStealer, and what to do if you ran a command from it
viewgit.sbs is a web address that URLhaus lists three times in two days: its home address as a PowerShell script tagged RedHiveStealer, and two files, 2.zip and 7za.exe, in a folder called assets. It is not a program on your PC, and seeing the name in a log proves nothing.
If you ran a PowerShell command that fetched from it, treat the Windows PC as watched: change your passwords from another device, then run a Microsoft Defender Offline scan and reset Windows if you are not sure.
Facts checked October 18, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If a PowerShell command, script or program that downloads files from viewgit.sbs keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove viewgit.sbs (PowerShell script tagged RedHiveStealer) yourself 5 steps, about 15 minutes, no software needed.
Start the steps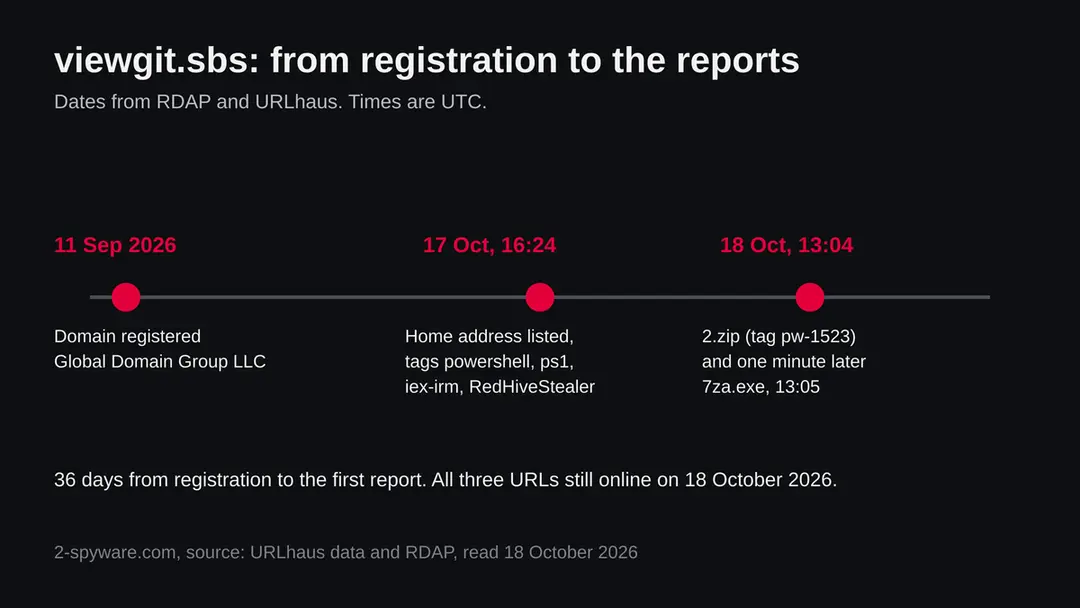
Viewgit.sbs (PowerShell script tagged RedHiveStealer): summary
| Type | A malware server: URLhaus lists a PowerShell script tagged RedHiveStealer, a password protected zip and an exe |
|---|---|
| Risk | High if a command from this address ran on your PC: saved logins, cookies and files may have been taken. Low if you only saw the name |
| Symptoms | Often none. A PowerShell window that flashed, then logins from new places or password reset emails, are the likely signs |
| How to get rid of it | Change passwords from another device, run Microsoft Defender Offline, and reset Windows if you are not sure |
| Our check (18 October 2026) | One plain request from our server: status 200, no redirect, no title. A quiet answer clears nothing; the danger rating comes from URLhaus |
| Running since / first seen | Domain registered 11 September 2026; first URL reported 17 October 2026 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Platform | Windows. Nothing we read says Mac or phones are affected |
|---|---|
| Detection names | No Microsoft detection name is known for the files on this server, because we did not open them and found no Microsoft entry for RedHiveStealer |
| Name | Viewgit.sbs |
| Domain registered | 11 September 2026 |
| Evidence | 3 write-ups by security sites; details still limited |
| First seen | 17 October 2026 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 18 October 2026 |
Facts checked on 18 October 2026 against the URLhaus data for viewgit.sbs held in our database (the abuse.ch host page was not opened), RDAP, one plain request from our server, and pages by Microsoft, SOC Prime and the FTC.
We found no public analysis of RedHiveStealer. We did not download the files and we infected no PC; the removal steps follow Microsoft's and the FTC's pages and were not tried on a live infection.
What viewgit.sbs is, and what we know about it
viewgit.sbs is not a program on your PC. It is a web address that the abuse.ch project URLhaus lists as a place where malware was served. We found no public write-up of this address or of the name RedHiveStealer, so what follows is what URLhaus shows, what our server saw, and what Microsoft has published about the way such PowerShell commands usually reach a PC.
- 1
What URLhaus lists
Three addresses. The first is the home address, hxxps://viewgit[.]sbs/, added on 17 October 2026 at about 16:24 UTC by a reporter who goes by ffforward. The other two sit in a folder called assets: hxxps://viewgit[.]sbs/assets/2.zip, added on 18 October at about 13:04 UTC, and hxxps://viewgit[.]sbs/assets/7za.exe, added a minute later. All three are marked online and carry the threat label malware_download.
- 2
What the tags on the home address say
The tags are powershell, ps1, iex-irm, mops_to and RedHiveStealer. ps1 and powershell say the address serves a PowerShell script. iex-irm is the name of a common pattern: a command that downloads text from an address and runs it at once, written with the PowerShell words irm (Invoke-RestMethod) and iex (Invoke-Expression). RedHiveStealer is the malware name the reporter chose; it looks like an information stealer from the name, but that is our reading. We could not find what mops_to means and will not guess.
- 3
What the tags on the two files say
2.zip carries the tags zip and pw-1523. The tag pw-1523 most likely means the archive is locked with the password 1523, which is how criminals stop scanners from looking inside; that is our reading of the tag, not something we tested. 7za.exe is tagged exe. The name matches the stand alone command line version of the legitimate 7-Zip archiver, which unpacks password protected zip files. Whether this copy is the real 7-Zip or something else, we do not know.
- 4
What we could not confirm
We did not download any file, so we cannot tell you what is inside the script, the archive or the program, what it steals, or where it sends the data. We also do not know how people end up running a command that points here. That first step is not visible from the server side.
- 5
What this means for you
If you only saw the name in a firewall log, a blocked request or a security alert, you are not infected by that alone. The risk is for a PC where someone ran a PowerShell line that fetched from this address, or ran a file that came from it.
- Kind of threat
- A server that hands out a PowerShell script tagged RedHiveStealer, a password protected zip and an exe, for Windows
- Where the files are
- hxxps://viewgit[.]sbs/ (the script), hxxps://viewgit[.]sbs/assets/2.zip and hxxps://viewgit[.]sbs/assets/7za.exe
- Domain registered
- 11 September 2026, registrar Global Domain Group LLC; status server transfer prohibited and client transfer prohibited (RDAP, read 17 October 2026)
- URLhaus entries
- 3 addresses, added 17 and 18 October 2026; all 3 online in our copy of the data on 18 October 2026
- Delivery pattern
- A PowerShell download and run command (tag iex-irm). How the command reaches a victim is not known for this address
- Platform
- Windows, because the tags name PowerShell and an exe. Nothing we read says Mac, iPhone or Android phones are affected
What viewgit.sbs (PowerShell script tagged RedHiveStealer) does on an infected PC
What we checked on 18 October 2026, and what we could not
Our check was one plain request to https://viewgit.sbs/ from our server, with no browser, no clicks and no PowerShell. The server answered with status 200, no redirect and no page title. That clears nothing: a server that serves malware can show an empty or ordinary page to a visitor and a script to a PowerShell client.
Our check, 18 October 2026
- The address answersStatus 200, no redirect, server header nginx/1.24.0 (Ubuntu). The server is up. A page title was not found, so we cannot describe a page for people.
- Why that is not a clean resultWe asked once, as a plain web client. Servers can answer different clients differently, by browser, country, user agent or request method. Our request would not look like the command that URLhaus tagged, so we did not see the script.
- Notification request, pop-ups, redirects, ad networksNone seen on this one request. Nothing was run, so this says little.
- URLhaus listingThree addresses, all online, one tagged RedHiveStealer with powershell, ps1 and iex-irm. Added on 17 and 18 October 2026.
- Downloads and the files themselvesWe did not download the script, the zip or the exe. We cannot tell you what they contain.
Dangerous: treat it as a malware server Our check was one plain request, so it proves nothing either way. The danger rating comes from the three URLhaus reports and their tags, not from our request. Do not run any command that fetches from this address.
What happened to viewgit.sbs, from registration to our check
The domain was registered five weeks before the first report, and the reports came in two bursts a day apart. The dates come from RDAP and from the URLhaus data we hold; the times are UTC.
11 September 2026
The domain is registered
RDAP shows viewgit.sbs created on 11 September 2026 at about 01:01 UTC through Global Domain Group LLC. Both transfer prohibited statuses are set. A new domain is not proof of anything, but a name that is 36 days old at its first report is typical of addresses made for one campaign.
17 October 2026
The home address is listed
At about 16:24 UTC the reporter ffforward adds https://viewgit.sbs/ with the tags iex-irm, mops_to, powershell, ps1 and RedHiveStealer. The status is online.
18 October 2026
A zip and an exe are listed, then our check
At about 13:04 UTC the reporter NDA0E adds /assets/2.zip (tags pw-1523 and zip), and at about 13:05 UTC /assets/7za.exe (tag exe). All three addresses are still online when we read the data. Our plain request the same day gets status 200.
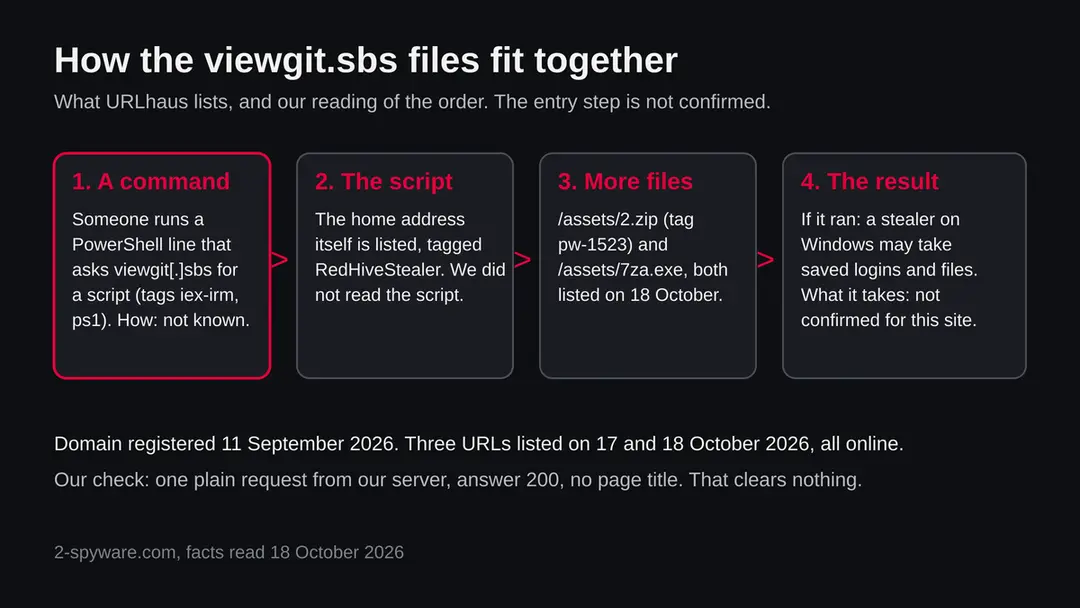
How the three listed addresses may fit together. The order is our reading of the tags; the entry step on a victim's PC and the contents of the files are not confirmed.
What the pattern suggests, and what it does not: two different reporters listed three different kinds of file on the same server within a day. A script, a locked archive and an archiver would fit a chain in which the script downloads the archive and unpacks it with 7za.exe. That is our reading of the file names and tags, and no report says it.
How a download and run command reaches a PC
A PowerShell line of the iex-irm kind does nothing until a person or a program runs it. We do not know which route led to viewgit.sbs. Microsoft describes the route most often seen with this kind of command, and we use it only as background.
- 1
A page tells you to fix something
Microsoft Threat Intelligence (21 August 2025) describes ClickFix, a technique in which a fake error, a fake CAPTCHA or a fake human check tells the visitor to copy a command and paste it into the Windows Run box, Windows Terminal or PowerShell. The page often puts the command on the clipboard by itself.
- 2
The command fetches a script and runs it
The pasted line downloads text from a server and runs it in memory. Microsoft says many of these payloads are fileless and run through built in programs such as PowerShell, msbuild.exe or regasm.exe. This is the same shape as the tag iex-irm.
- 3
The script brings in the rest
Microsoft names infostealers such as Lumma Stealer and Lampion as the most common final payload, and remote access tools such as AsyncRAT among others. For viewgit.sbs the tag says RedHiveStealer; we found no description of that family.
- 4
Why the pasted command matters
Because you ran the command yourself, a download filter and a mail scanner never saw a file arrive. That is why removal begins with what the PC did, not with a file you can see.
A separate report, from SOC Prime (summarising EclecticIQ), describes a different campaign in which fake installer pages for AI coding tools gave victims a single irm and iex command that loaded an information stealer in memory. It is not linked to viewgit.sbs or to RedHiveStealer by any source we read. We mention it only because it shows the same command shape in use in 2026.
What viewgit.sbs (PowerShell script tagged RedHiveStealer) can steal or download
What an information stealer can take from a Windows PC
We do not know what RedHiveStealer takes, because we found no analysis of it. The list below is what the sources say about stealers delivered by this kind of command. Treat it as the worst case to plan for, not as a finding about this server.
Reported for similar stealers
- Saved browser passwords
- Session cookies
- VPN keys and configuration
- Cryptocurrency wallet files
- Documents and other files
- System details of the PC
- Extra malware downloaded later
| Data | Detail | Source |
|---|---|---|
| Logins and cookies | SOC Prime, summarising EclecticIQ, lists credentials, session cookies and VPN keys taken by a stealer that was started with an irm and iex command | SOC Prime |
| Files | The same report lists sensitive files, sent out in encrypted form to a controlling server | SOC Prime |
| Other payloads | Microsoft says a pasted command can also bring remote access tools, loaders and rootkits, not only stealers | Microsoft |
| This server | Not known. URLhaus gives only the name RedHiveStealer; we did not open the files | Not available |
What this can cost you
Reading about the site or seeing its name costs nothing. The risks below apply to a Windows PC where a command from this address ran, and they are stated as possibilities, because we do not know what the script does.
- High
Passwords and logged in sessions
A stealer that copies saved logins and session cookies can let a stranger into your accounts without the password. Changing a password on the same PC does not help while the malware is still there.
- High
Crypto and banking
If a wallet file or seed phrase was on the PC, assume it is known. Crypto sent from a stolen wallet cannot be reversed.
- Medium
Files and documents
Stealers often look for documents and sensitive files. Anything personal or from work that sat on the PC may have left it.
- Medium
More malware on the same PC
Microsoft says a pasted command may also bring remote access tools or loaders. The zip and the exe on this server mean the chain may have more than one stage.
- Low
Nothing, if you only saw the name
A name in a block list, a log or a warning is not an infection.
What you may notice, and what you may not
Stealers are built to be quick and quiet. They may finish their work within minutes and leave nothing behind, so most victims notice the damage in their accounts, not on the PC.
| Sign | What it means |
|---|---|
| A PowerShell window that flashed and closed | SOC Prime's report describes a first stage script that opens a hidden PowerShell window. A flash right after you pasted a command is worth taking seriously |
| Logins from new places or password reset emails | This follows from stolen logins and cookies; it is our reading and the most common first sign |
| Messages or posts you did not send | Accounts that were taken over are often used to send links to contacts |
| Crypto moved out of a wallet | A wallet drained after the PC ran an unknown command points at a stealer |
| A new scheduled task, startup entry or unknown program | We found no source that says this server's files stay on the PC, so their absence clears nothing |
| Nothing at all | A stealer that runs once in memory and sends its data away may leave no trace you can see |
How to check the PC for viewgit.sbs (PowerShell script tagged RedHiveStealer)
How a person ends up running a command from this address
Nobody visits viewgit.sbs on purpose, and a normal visitor has no reason to request its files. The request comes from a pasted command or from a program. We cannot say how it was spread; these are the routes Microsoft describes for the same kind of command.
- 1
A fake check or fake error on a web page
Microsoft says the lures include fake error messages and fake CAPTCHA or human verification prompts that copy Cloudflare Turnstile or Google reCAPTCHA, and fake pages for platforms such as Discord. A real CAPTCHA never asks you to open the Run box or a terminal and paste something.
- 2
A link from email, an ad or a hacked site
Microsoft names phishing emails with links or attachments, malvertising that leads to scam pages and compromised legitimate websites as the ways people reach those pages.
- 3
A guide or comment that says to paste a line
Any page, video description or chat message that tells you to paste a PowerShell line to install a program or fix a problem is the same trick. Install software from its maker's own site or the Microsoft Store.
Check your PC before you delete anything
Start with the question that matters: did you or a program on this PC run a PowerShell command that fetched from viewgit.sbs, or a file that came from it? If you saw the name in a firewall or DNS log from your network, the device that asked is the one to check. If the answer is yes or you are not sure, do the checks below. None of them deletes anything.
While you check, stop using the PC for banking, email, work or crypto, and do the account steps on another device.
- 1
Disconnect first
Turn off Wi-Fi or unplug the network cable. A stealer or a remote tool needs the connection to send data or to be used.
- 2
Find which device asked for the address
If you came here from a log, a router page or an alert, note the device and the time. Only that device is in question, not every device on the network.
- 3
Open Protection history
In Windows Security > Virus & threat protection > Protection history, look for anything blocked or quarantined around the time of the first contact, and for detection names that mention PowerShell, a stealer or a trojan. Microsoft says offline scan results also appear there.
- 4
Look at Startup apps
Open Settings > Apps > Startup and look for names you did not install. A stealer that runs once will not be here, so a clean list clears nothing.
- 5
Look at running processes
Open Task Manager and look at the Processes tab for programs you do not know, or for powershell.exe, msbuild.exe or regasm.exe running with no reason. Microsoft names the last two as programs these chains use. They are real Windows files, so their presence is not proof.
- 6
Check your accounts from another device
Look at the sign in activity of your email, bank, social and exchange accounts, and at crypto balances. This is quicker than any file check, and the FTC lists the signs: a changed password or phone number, login alerts, messages you did not send, and mail forwarding rules you did not create.
- 7
A scan helps, but it does not clear the PC
A scan with Microsoft Defender or another product can find known files. Treat a clean result like a clean site test: one data point. No vendor publishes a removal procedure for this server's files and we did not infect a PC, so the order of the plan is our judgement from Microsoft's and the FTC's pages, not a tested result.
How to remove viewgit.sbs (PowerShell script tagged RedHiveStealer)
How to remove viewgit.sbs
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to viewgit.sbs or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever viewgit.sbs installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
If you use a Mac, an iPhone or an Android phone
The tags describe a Windows threat: PowerShell and an exe file. We found nothing that says viewgit.sbs affects anything else. Microsoft notes that ClickFix campaigns have also targeted Mac users, but with a different command, and no source links that to this address.
| Your device | What we know | What to do |
|---|---|---|
| Mac | The listed files are a PowerShell script and an exe. Neither runs on macOS as listed | Nothing to remove for this threat. Do not follow the Windows steps on a Mac. If you pasted a command into Terminal from an unknown page, treat that as a separate problem and change your passwords |
| iPhone or iPad | No source describes this server on iOS | Nothing to remove. If you typed passwords on a page, change them |
| Android | No source mentions it | Nothing to remove for this threat; change passwords if you entered any |
After removal: passwords, accounts and prevention
After a clean PC: protect what was taken
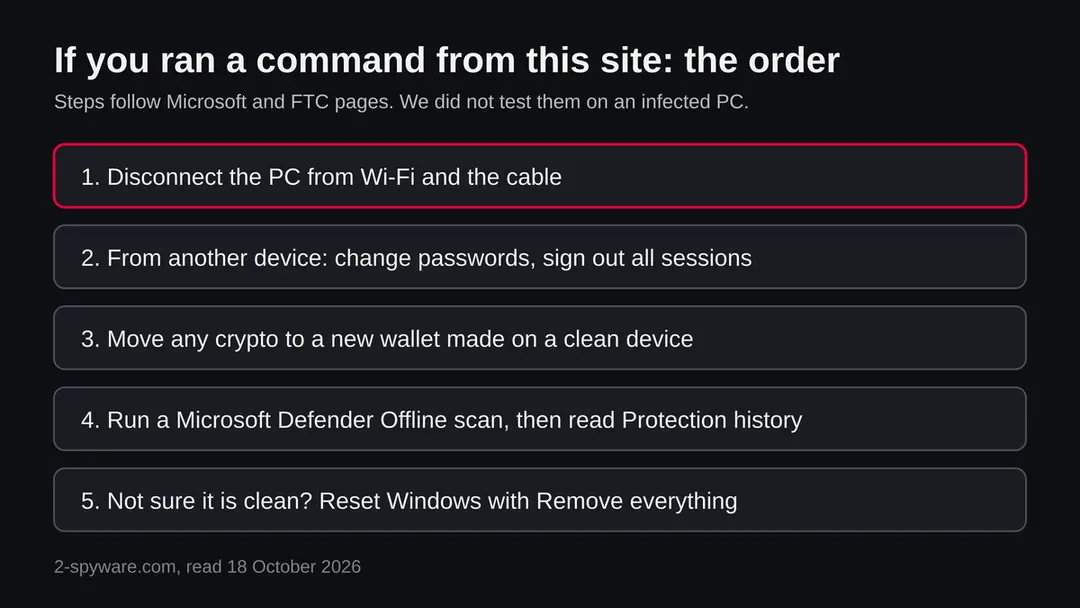
The PC is one half. The other half is everything you typed or stored on it while the malware may have been there. The order matters: another device first, then the PC.
- 1
Change passwords from a clean device
The FTC says to change the password to a unique, strong one of 12 to 15 characters, or a passphrase, and then to sign out of the account on all devices. Start with email, because it resets everything else, then bank, work, cloud storage and crypto. Anything typed on the PC while it was watched may already be known.
- 2
Turn on two factor sign in and update recovery details
The FTC says to turn on two factor authentication if the account offers it, so a password alone does not let anyone in, and to check that the recovery email and phone are yours. Look for mail forwarding rules you did not create.
- 3
Move crypto first if a wallet was on the PC
If a seed phrase or wallet file was ever on the PC, assume it is known. Create a new wallet and recovery phrase on a clean device and move the funds there.
- 4
Run Microsoft Defender Offline
Microsoft says to open Windows Security > Virus & threat protection > Scan options, choose Microsoft Defender Offline scan and select Scan now. Save your work first: Windows signs you out and restarts, and the scan takes about 15 minutes. It runs outside the normal Windows, so malware has a harder time hiding. Results are under Protection history. If BitLocker is on the system drive, Microsoft says to suspend it first or the restart may ask for the recovery key. The page also notes that the scan does not run if the Windows Recovery Environment is disabled, and gives reagentc /info to check it.
- 5
Remove what the check found, with care
If Startup apps or Task Manager showed a program that you can tie to this chain, uninstall or delete it. If you cannot tell, do not guess: the safe answer is the reset below.
- 6
If you are not sure, reset Windows
Microsoft's recovery page says Reset this PC can be started from Settings or from the Windows Recovery Environment, where it is under Troubleshoot > Reset this PC. On our Windows 11 test machine the Settings path is Settings > System > Recovery. You can keep personal files or remove everything. Keeping files does not keep apps or settings. For a PC that ran an unknown stealer command, the full wipe is the answer that does not depend on finding every piece. Microsoft says to back up important files first and, if BitLocker is on, to have the recovery key ready.
- 7
Restore only documents by hand
Copy back documents and photos, not programs, and not a full system image from after the first contact. Install apps from their makers' own sites.
- 8
Rebuild logins in a password manager
Do not let the browser save passwords again on a PC that may have been watched. Use a password manager and an authenticator app or security key for two step sign in.
- 9
Watch your money and your accounts
Check card statements and exchange logs for a few weeks. Turn on alerts. The FTC says that if someone stole your personal information you can report it at IdentityTheft.gov to get a recovery plan.
- 10
Tell the people you message
If your accounts were used to send links, tell your contacts not to open them.
If you own a site and think it is the source
URLhaus lists addresses, not owners. A new domain bought for the purpose is more likely than a hacked site here, since viewgit.sbs was registered five weeks before the first report. We cannot rule out the other case.
- 1
Check whether the name is yours
If you registered viewgit.sbs yourself, look at the files in an assets folder on your server and at who can log in to it. Files named 2.zip and 7za.exe that you did not put there mean the server was changed.
- 2
Clean the server, not just the files
Change every password and key for the server and hosting account from a clean device, remove unknown files and accounts, and update the software. Restore from a backup taken before the first report if you have one.
- 3
Ask for a re-check
Once the files are gone, ask the reporting service to review the listing. We cannot promise when or whether it will be taken down.
Keep a PC out of this kind of chain
The weak point in a pasted command is you, so the defences are habits. Microsoft's own advice for this technique starts with what people copy and paste.
Do
- Treat any page that tells you to open the Run box, Terminal or PowerShell and paste a line as an attack, and close it.
- Keep Windows and Microsoft Defender updated and leave cloud delivered protection on; Microsoft lists both in its advice.
- Show file endings in File Explorer so a script posing as a document is visible.
- Get programs from their makers' own sites or from the Microsoft Store.
- Use a password manager and two step sign in, so one stolen password is not enough.
- Keep a backup of documents on a disk that you unplug.
Don't
- Do not paste a command you do not understand, even when a page says it is a human check.
- Do not run cracked programs or bundles from sites that promise free versions of paid software.
- Do not unpack password protected archives from unknown senders.
- Do not change your passwords on the PC you suspect.
- Do not rely on a quiet scan to say that you are safe.
Questions about viewgit.sbs (PowerShell script tagged RedHiveStealer)
What is viewgit.sbs?
It is a web address that URLhaus, the malware tracking project run by abuse.ch, lists three times. The home address is tagged powershell, ps1, iex-irm and RedHiveStealer, and the folder assets holds 2.zip and 7za.exe.
They were reported on 17 and 18 October 2026. It is not a program on your PC and not a site anyone is meant to browse. We did not download the files, so what they contain is not confirmed by us.
Is viewgit.sbs safe to open?
No. Do not open it in a way that runs anything, and never run a command that fetches from it. Our own plain request returned status 200 with no page title, which proves nothing: servers that serve malware can show an empty page to a browser and a script to a PowerShell client.
The rating comes from the three URLhaus reports and their tags. The domain was also registered only on 11 September 2026.
Is viewgit.sbs a virus?
The address is not a virus itself; it is a server. What it serves, according to URLhaus tags, is a PowerShell script tagged RedHiveStealer, a zip locked with a password and an exe.
If a command that fetched the script ran on your Windows PC, the PC may be infected with an information stealer. If you only saw the name in a log or alert, nothing was installed by that alone, but find the device that asked for it.
What is RedHiveStealer?
RedHiveStealer is the name in the URLhaus tag for the script on the home address. The name suggests an information stealer, but we found no vendor or researcher write-up of it, so we cannot say what it takes, how it sends data or which Microsoft detection covers it.
For general background, stealers started by a download and run PowerShell command have been reported to take saved logins, session cookies, VPN keys and files.
What does the tag iex-irm mean?
It names a pattern in PowerShell: irm is short for Invoke-RestMethod, which downloads text from an address, and iex is short for Invoke-Expression, which runs text as a command.
Joined, they download a script and run it at once, usually in memory, so no file is saved first. Microsoft describes the same shape in ClickFix attacks, where a page tells you to paste such a line into the Run box or a terminal.
I saw viewgit.sbs in my firewall or DNS log. Am I infected?
Not necessarily, and the name alone proves nothing. It does mean that a device on your network asked for it, and a person does not usually do that by hand. Find which device it was, disconnect it, and run the checks on this page:
- Protection history
- Startup apps
- Task Manager
- a Microsoft Defender Offline scan
Check your accounts and change passwords from another device.
I ran a PowerShell command from a website. What do I do now?
Disconnect the PC from the network first. From another device, change passwords, starting with email, sign out of all sessions, turn on two factor sign in and move any crypto to a new wallet.
Then run a Microsoft Defender Offline scan on the PC, read Protection history, and reset Windows with Remove everything if you are not sure. We followed Microsoft and FTC pages and did not test the steps on an infected PC.
Does viewgit.sbs affect Mac, iPhone or Android?
We found nothing that says so. The tags name PowerShell and an exe file, which are Windows things. Microsoft notes that ClickFix campaigns have also targeted Mac users, but with a different command and a different set of malware, and no source ties that to this address.
On an iPhone or Android phone there is nothing to remove for this threat; if you typed a password on a suspicious page, change it.
Will resetting Windows fix it, and are my accounts safe afterwards?
A reset with Remove everything wipes programs and startup entries, which is the answer that does not depend on finding every piece. It does not undo what was already taken.
Passwords, session logins and crypto seed phrases that a stealer saw stay exposed until you change them, from another device, and turn on two step sign in. Restore documents by hand, not a full system image, and watch your accounts for several weeks.
Will Fortect remove viewgit.sbs?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For viewgit.sbs, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Microsoft Security blog: Think before you ClickFix, analyzing the ClickFix social engineering technique (21 August 2025) (read October 18, 2026)
- Microsoft Learn: Microsoft Defender Offline scan in Windows (updated 25 August 2026) (read October 18, 2026)
- Microsoft Support: Recovery options in Windows (Reset this PC) (read October 18, 2026)
- FTC: Email or social media hacked? Here's what to do (read October 18, 2026)
- SOC Prime: SEO poisoning campaign uses Gemini and Claude Code lures to deliver an infostealer (a different campaign with the same irm and iex command shape; it does not name RedHiveStealer) (read October 18, 2026)