
porterneuman.mx: PowerShell and JavaScript files tied to the AveMaria remote access trojan, and what to do
porterneuman.mx is a web address where URLhaus found five script files in a WordPress plugin folder on 30 September 2026: four PowerShell stubs and one JavaScript file. One stub is tagged AveMariaRAT, a remote access trojan for Windows also called Warzone, and the JavaScript file was still online on 8 October.
If you only saw the name in a log, nothing is proven. If a file from it ran on your PC, change your passwords from another device, then scan and clean Windows.
Facts checked October 8, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like a JavaScript or PowerShell file downloaded from porterneuman.mx usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove porterneuman.mx (AveMaria RAT script stages) yourself 5 steps, about 15 minutes, no software needed.
Start the steps
Porterneuman.mx (AveMaria RAT script stages): summary
| Type | A server holding Windows script stages; URLhaus tags one of them AveMariaRAT, a remote access trojan also called Warzone |
|---|---|
| Risk | High if one of its files ran on your PC: keystrokes, passwords, webcam and the whole desktop may be used. Low if you only saw the name |
| Symptoms | Often none. Unknown startup entries or Run keys, and slow or unstable Windows, are the signs in the sources |
| How to get rid of it | Change passwords from another device, run Microsoft Defender Offline, remove unknown startup entries, and reset Windows if unsure |
| Our check (8 October 2026) | One plain request: status 200, no title or server name. A normal answer clears nothing |
| Running since / first seen | Registration date unknown (no RDAP record); files reported 30 September 2026 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Platform | Windows. Nothing we read says Mac or phones are affected |
|---|---|
| Detection names | No exact name is known for these files because we did not scan them. For AveMaria builds Microsoft uses names such as Backdoor:Win32/AveMaria.BK!MTB |
| Name | Porterneuman.mx |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 30 September 2026 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 8 October 2026 |
Facts checked on 8 October 2026 against the URLhaus data for porterneuman.mx held in our database, an RDAP lookup that returned no record, one plain request from our server, MITRE ATT&CK, Microsoft Security Intelligence and Microsoft Support, and WordPress.org's help for hacked sites. We did not download the files and infected no PC; the removal steps follow Microsoft's pages and were not tried on a live infection.
What porterneuman.mx is, and what we know about it
porterneuman.mx is a Mexican web address whose server held a folder of script files that URLhaus lists as malware downloads.
The files sat inside /wp-content/plugins/Team/, the place where a WordPress site keeps its plugins. One of them, secured_stub.ps1, is tagged AveMariaRAT, a remote access trojan for Windows that is also known as Warzone.
We found nothing that says who runs the site or what it was meant for. A folder like this on an otherwise ordinary site is a common sign of a hacked WordPress install, but that is our reading, not something a report states.
- 1
What URLhaus lists
Five file addresses, all added on 30 September 2026 between 15:00:18 and 15:00:25 UTC by abuse_ch, the team that runs URLhaus. Four are PowerShell scripts with names ending in secured_stub.ps1, and one is a JavaScript file called GOMATO.js. All five carry the threat label malware_download and the tag opendir, meaning the folder listed its files openly.
- 2
Which are still online
When we read the data on 8 October 2026, only GOMATO.js was marked online. The four PowerShell files were offline. Offline means they no longer answered when last checked; it does not mean the site is clean, because the script that fetched them was still there.
- 3
What the tags mean
ps1 and powershell mark Windows PowerShell scripts. js marks a JavaScript file, which on Windows can run outside the browser when someone opens it. ascii means plain text. AveMariaRAT and rat on secured_stub.ps1 name the remote access trojan the script is linked to.
- 4
What we could not confirm
We did not download any file. We cannot tell you what GOMATO.js does in detail, where the trojan reports to, or how many people ran these files. We also could not read the domain's registration data: the RDAP lookup for this .mx name returned no record.
- Kind of threat
- A web server holding script stages for a Windows remote access trojan; one is tagged AveMariaRAT
- Where the files are
- hxxps://porterneuman[.]mx/wp-content/plugins/Team/ followed by GOMATO.js or a *secured_stub.ps1 name
- Files reported
- 5 on 30 September 2026: 1 JavaScript file, 4 PowerShell scripts
- Still online when read
- 1 of 5 (GOMATO.js), on 8 October 2026
- Domain registration
- Unknown: RDAP returned no record for porterneuman.mx on 8 October 2026
- Our request
- Status 200, no page title and no server name in the answer
What porterneuman.mx (AveMaria RAT script stages) does on an infected PC
What we checked on 8 October 2026, and what we could not
Our check was one plain request from our server to the home page, without a browser and without clicks.
It shows that the server is up, not what is inside the plugin folder or what a visitor's browser would do.
Our request, 8 October 2026
- The site answeredHTTP status 200 with no redirect. The server is up.
- No title, no server nameThe answer had no page title and no server header. That can be an empty or broken front page, which is common on hacked or neglected sites. It tells us nothing about the files.
- One file still onlineURLhaus still listed GOMATO.js as online when we read the data.
- Notification requestsNone mentioned in what we received. The danger here is the script files, not pop-ups.
Dangerous: do not download files from it A normal answer clears nothing. The reports show a folder of Windows script stages, one tied to a remote access trojan, and one file was still online. Treat any file from this address as malware until the owner has cleaned the site.
What happened to porterneuman.mx, as far as the reports show
The record is short.
Everything we know comes from one batch of reports and our own request a week later.
Unknown
The domain is registered
We could not read a registration date: RDAP returned no record for this .mx name. We draw no conclusion about the site's age.
30 September 2026, 15:00 UTC
Five files are reported
abuse_ch adds four PowerShell scripts and one JavaScript file from /wp-content/plugins/Team/ within seven seconds. secured_stub.ps1 is tagged AveMariaRAT.
By 8 October 2026
Four files go offline
The four PowerShell files are marked offline. GOMATO.js is still online.
8 October 2026
Our request
The home page answers with status 200, without a title or server name.
What the pattern suggests, and what it does not: several near identical stub names with different prefixes look like one operator testing or rotating variants in the same folder. That is our reading of the names, not something a report says.
How a script on a hacked site can end in a remote access trojan
Files on a server do nothing by themselves.
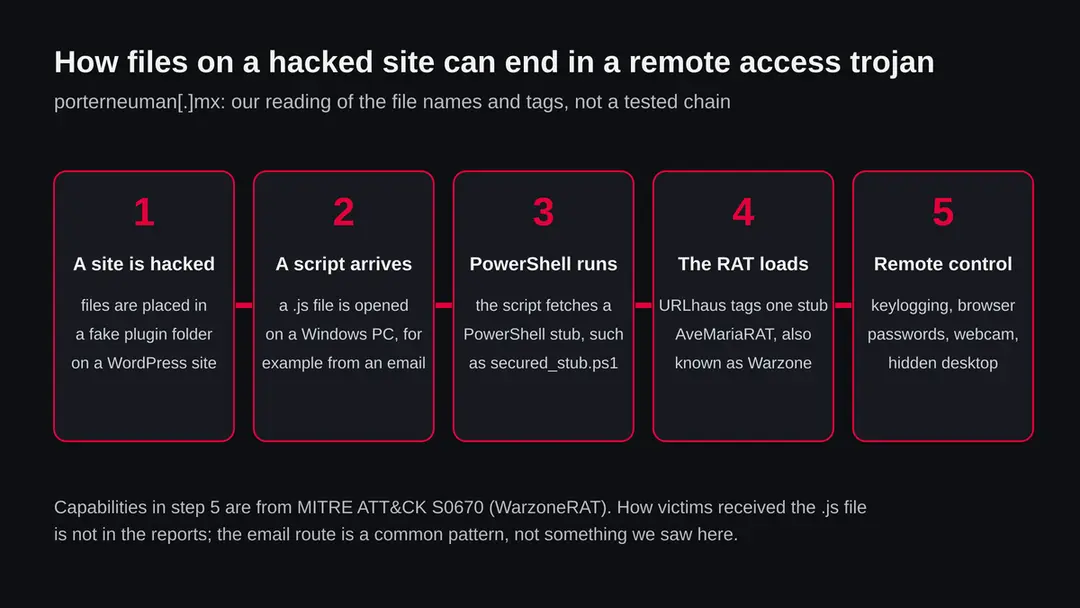
Someone has to fetch and run them on a Windows PC. The names and tags here suggest a chain of small scripts, each one fetching the next, with a remote access trojan at the end.
- 1
Files placed on someone else's site
Attackers often hide their files on a site they broke into, because a known site is less likely to be blocked than a brand new domain. A folder under wp-content/plugins with an odd name such as Team fits that pattern.
- 2
A JavaScript file is opened
On Windows, a .js file saved to disk and double clicked is run by Windows Script Host, not by the browser. That is why such files are sent as email attachments or downloads. We do not know how GOMATO.js reached anyone.
- 3
PowerShell fetches a stub
The PowerShell files are named stubs, a word for a small loader that unpacks or starts the real program. The tag on secured_stub.ps1 links it to AveMariaRAT.
- 4
The trojan runs
MITRE ATT&CK describes WarzoneRAT, also called Ave Maria, as Windows malware sold as a service since at least late 2018. Once it runs, the person controlling it can watch and use the PC.
MITRE also records that WarzoneRAT can download and run further files, so a PC that ran it may hold more than one unwanted program.
What porterneuman.mx (AveMaria RAT script stages) can steal or download
What AveMaria, also called Warzone, can do
These are the capabilities MITRE ATT&CK lists for the family.
We did not analyse the build on this server, so not every item may apply to it.
Listed by MITRE ATT&CK
- Live and offline keylogging
- Passwords from web browsers
- Outlook and Thunderbird passwords
- Webcam access
- Remote desktop and VNC control
- Hidden desktop (hVNC)
- Downloading and running more files
- Start after restart through Run keys
| Question | What the sources say | Source |
|---|---|---|
| Other names | Warzone, Ave Maria, WarzoneRAT | MITRE ATT&CK S0670 |
| Platform | Windows | MITRE ATT&CK S0670 |
| How long around | Sold as malware as a service since at least late 2018 | MITRE ATT&CK S0670 |
| Getting more rights | Bypasses User Account Control with sdclt.exe on Windows 10 | MITRE ATT&CK S0670 |
| Staying on the PC | Registry Run keys and COM hijacking | MITRE ATT&CK S0670 |
| Microsoft's view | Can give a malicious hacker unauthorized access and control of your PC | Microsoft, Backdoor:Win32/AveMaria.BK!MTB |
What this can cost you
A remote access trojan is not a one time theft.
While it runs, someone else can use the PC as if they were sitting in front of it.
- High
Every password you type
Keylogging records what you type, including new passwords. Change passwords from another device, or the controller sees the new ones too.
- High
Saved passwords and email
MITRE lists password theft from browsers and from Outlook and Thunderbird. Email access lets an attacker reset other accounts.
- High
Camera and screen
Webcam access and remote desktop control mean the attacker can see you and what you do.
- Medium
More malware
The trojan can download and run other files, so cleaning one program may not be enough.
What you may notice, and what you may not
Most victims notice nothing.
Microsoft lists general symptoms for its AveMaria detection, and MITRE lists how the family stays on a PC.
| Sign | What it can mean |
|---|---|
| A startup entry or Run key you did not add | MITRE says WarzoneRAT adds itself to Registry Run keys |
| Slow performance, freezing or crashing | Microsoft lists these for Backdoor:Win32/AveMaria.BK!MTB, though they have many other causes |
| Files added or changed, less free space | Also on Microsoft's list |
| A camera light that turns on by itself | Possible webcam use |
| Nothing at all | Common. The absence of signs is not a clean result |
How to check the PC for porterneuman.mx (AveMaria RAT script stages)
How a person ends up running these files
The reports do not say how anyone received these files.
These are the usual routes for script files like them, and we label them as such.
- 1
An email attachment or link
A message with an invoice, order or document theme that delivers a .js file or a zip with one inside. Opening it on Windows runs it.
- 2
A fake download
A page that offers a document, update or tool and hands over a script instead.
- 3
Another program already on the PC
A loader that is already running fetches the next stage from the server. In that case you never see the address.
- 4
A security alert or log
Many people only meet the name in a firewall log, DNS log or antivirus alert. That proves a request, not that anything ran.
Check your PC before you delete anything
If you only saw the name in a log and no file ran, there may be nothing to remove.
If a .js or .ps1 file from this address was opened, do these checks.
- 1
Disconnect first
Turn off Wi-Fi or unplug the cable. A remote access trojan needs the connection to be used.
- 2
Find the device and the time
If you came here from a log or an alert, note which device asked for the address and when. Only that device is in question.
- 3
Check Protection history
Open Windows Security > Protection history and look for detections around that time, such as names that include AveMaria.
- 4
Look at startup
Open Settings > Apps > Startup and Task Scheduler and write down entries you do not recognise before you remove anything.
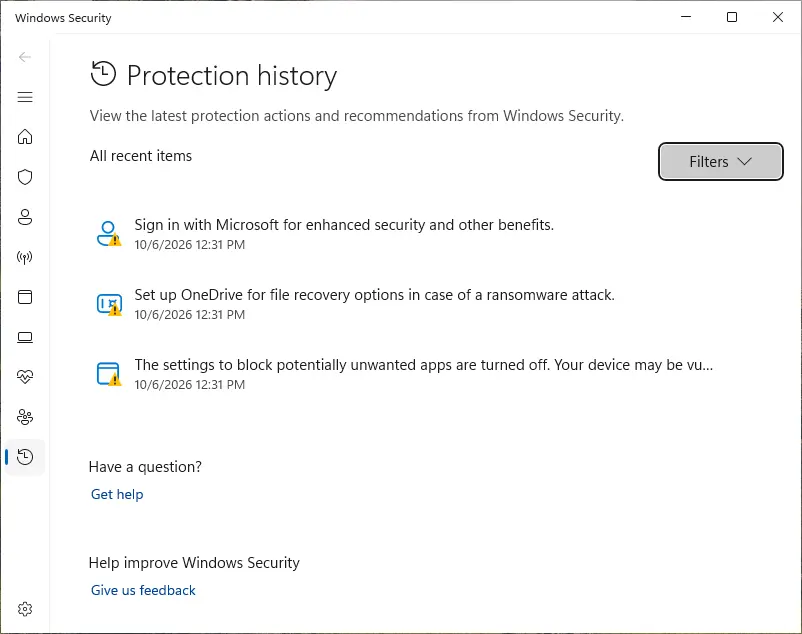
If you find a detection or an unknown startup entry, go to the order of actions below and change passwords from another device first.
How to remove porterneuman.mx (AveMaria RAT script stages)
How to remove porterneuman.mx
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to porterneuman.mx or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever porterneuman.mx installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
If you own porterneuman.mx or run a WordPress site with a folder like this
The folder name and the tag opendir suggest that someone placed these files on a WordPress site.
WordPress.org's own help page for hacked sites gives an order of work, which we summarise here.
- 1
Document and back up
Write down what you see and when, then take a snapshot of the site as it is, even infected, so you have a reference.
- 2
Reset all access
WordPress.org says to change every access point: WP Admin, FTP or SFTP, the hosting panel and the database, for all users. New secret keys in wp-config.php sign everyone out.
- 3
Remove the hack
Delete the unknown plugin folder, replace wp-admin and wp-includes with clean copies of the same version, and check .htaccess, index.php, header.php, footer.php and functions.php.
- 4
Scan your own computer
WordPress.org warns that the attack often starts on the owner's computer, where a trojan steals FTP and wp-admin logins. Scan it fully.
- 5
Update and change passwords again
Update WordPress, themes and plugins, then change the passwords a second time once the site is clean. Talk to your host and check search engine warnings.
If you use a Mac, an iPhone or an Android phone
The reported files are Windows scripts and the trojan they point to is Windows malware.
| Your device | What we know | What to do |
|---|---|---|
| Mac | MITRE lists WarzoneRAT for Windows only; .ps1 and .js scripts of this kind are run by Windows | Nothing to remove for this threat. Do not follow the Windows steps on a Mac |
| iPhone or iPad | No source describes this trojan on iOS | Nothing to remove. Change passwords you typed on an affected PC |
| Android | No source describes this trojan on Android | Nothing to remove for this threat |
After removal: passwords, accounts and prevention
After a clean PC: protect what was taken
Order matters.
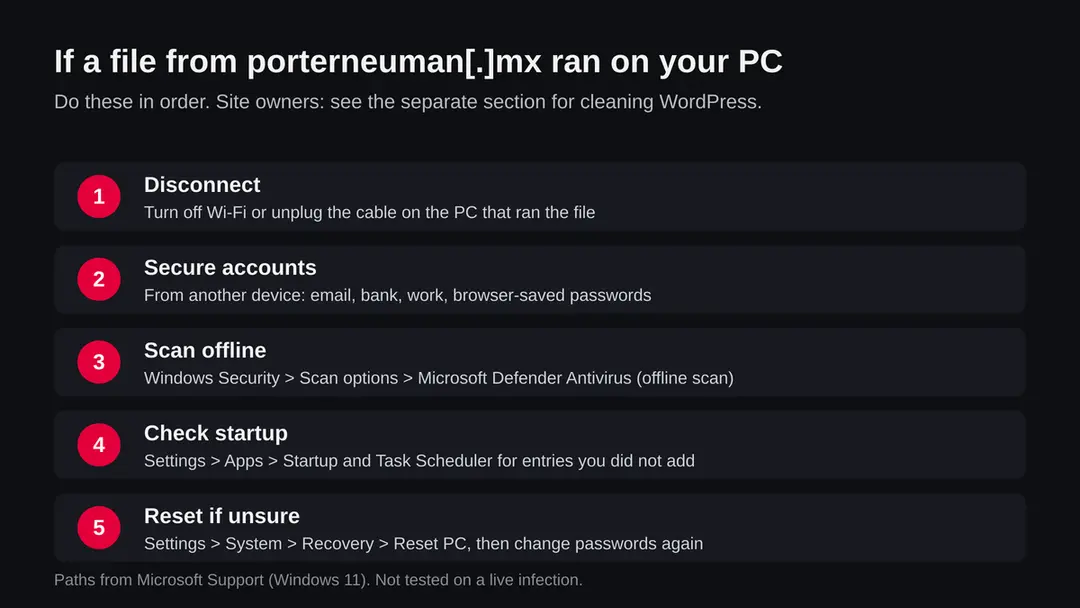
Secure your accounts from a device that never ran the file, then clean the PC, then change the passwords once more.
- 1
Change passwords from a clean device
Start with email, because it resets everything else, then bank, work accounts and anything saved in the browser or in Outlook or Thunderbird.
- 2
Turn on two step sign in
Add a second factor to email and bank accounts, and sign out other sessions where the service allows it.
- 3
Run Microsoft Defender Offline
In Windows Security > Virus & threat protection > Scan options, choose Microsoft Defender Antivirus (offline scan). The PC restarts and scans before Windows loads, so hidden malware has a harder time defending itself.
- 4
Reset Windows if unsure
If anything still looks wrong, use Reset this PC under Settings > System > Recovery, then change passwords once more.
Keep a PC out of this kind of chain
The chain only works if a script is run on the PC.
Make that step harder.
Do
- Show file name extensions in File Explorer so a .js or .ps1 file posing as a document is visible.
- Keep Windows and Microsoft Defender updated.
- Open documents from people you know only when you expected them, and check by phone if unsure.
- Site owners: keep WordPress, themes and plugins updated and use two step sign in for every admin.
Don't
- Do not double click .js, .vbs or .ps1 files from email or downloads.
- Do not allow a script to run because a page or message says it is needed to view a document.
- Do not reuse the same password for your site's admin, FTP and email.
- Do not leave unknown plugin folders on a site you run.
Questions about porterneuman.mx (AveMaria RAT script stages)
What is porterneuman.mx?
It is a Mexican web address whose server held five script files in a WordPress plugin folder called Team. URLhaus listed them as malware downloads on 30 September 2026.
One PowerShell file is tagged AveMariaRAT, a remote access trojan for Windows. We found nothing about who runs the site, and RDAP returned no registration record for it.
Is porterneuman.mx a malicious site or a hacked one?
We cannot say for sure. The files sit in a plugin folder of a WordPress site, which is a common sign of a hacked site whose owner may not know.
That is our reading. Either way, do not download files from it until the owner has cleaned the site and the reports stop.
Is porterneuman.mx safe to visit?
Do not download anything from it. Our plain request got status 200 with no title, which clears nothing. GOMATO.js was still online when we read the data on 8 October 2026.
The four PowerShell files were offline, but the script that could fetch them was still there. Treat any file from this address as malware.
What is AveMaria or Warzone RAT?
MITRE ATT&CK lists WarzoneRAT, also called Ave Maria, as Windows malware sold as a service since at least late 2018. It can log keys, take browser and email passwords, use the webcam, give the attacker remote desktop control, and download more files. Microsoft detects builds under names such as Backdoor:Win32/AveMaria.BK!MTB.
What are the secured_stub.ps1 files?
They are PowerShell scripts. A stub is a small loader that unpacks or starts a bigger program. URLhaus tags secured_stub.ps1 with AveMariaRAT, and the other three have almost the same name.
We did not open them, so we cannot say what each one does in detail or whether they differ.
My firewall log shows porterneuman.mx. Am I infected?
A log entry proves a request, not an infection. Find which device made the request and when, then check Windows Security > Protection history and the startup list on that device. If a .js or .ps1 file was opened on it, follow the full plan on this page from another device.
Should I change my passwords on the same PC?
No. A remote access trojan logs keys, so the new passwords would be seen too. Use a phone or another computer that never ran the file.
Start with email, then bank and work accounts, and change them once more after the PC is clean or reset. Turn on two step sign in where you can.
Does Microsoft Defender remove AveMaria?
Microsoft says Defender detects and removes Backdoor:Win32/AveMaria.BK!MTB, and advises updating definitions and running a full scan because infections can leave remnants.
An offline scan from Windows Security starts before Windows loads, which makes hiding harder. Reset this PC is the safest choice if you remain unsure. Check Protection history afterwards to see what was found.
I run a WordPress site and found a folder like this. What now?
Follow WordPress.org's help for hacked sites:
- document what you see
- take a snapshot
- change every password including FTP
- hosting panel and database
- set new secret keys in wp-config.php
- remove the folder
- replace core files with clean copies
- scan your own computer
- update everything
- change the passwords again
Also talk to your hosting provider.
Will Fortect remove porterneuman.mx?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For porterneuman.mx, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- URLhaus (abuse.ch): host porterneuman.mx, 5 entries, one tagged AveMariaRAT (data held in our database, read 8 October 2026) (read October 8, 2026)
- MITRE ATT&CK: WarzoneRAT, S0670 (modified 3 October 2023) (read October 8, 2026)
- Microsoft Security Intelligence: Backdoor:Win32/AveMaria.BK!MTB (published 13 January 2021) (read October 8, 2026)
- Microsoft Support: Help protect my PC with Microsoft Defender Offline (read October 8, 2026)
- WordPress.org: FAQ My site was hacked (last updated 26 July 2026) (read October 8, 2026)