
www.beinke-aufzuege.de: a hacked website hosting FormBook PowerShell stubs, and what to do if a script fetched them
www.beinke-aufzuege.de is the address of a German website that URLhaus lists for four PowerShell files tagged Formbook, a password stealer for Windows, hidden in random folders inside the site's own Joomla media component. That points to a hacked site, not a malicious business.
The files do nothing on their own; a script already running on a PC fetches them. If you only visited the site or saw the name in a log, nothing is proven. If a script on your PC fetched them, change your passwords from another device, then scan and clean or reset Windows.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with a script or attachment that downloads PowerShell files from www.beinke-aufzuege.de.
Do it yourself · free Remove www.beinke-aufzuege.de (FormBook PowerShell stubs on a hacked site) yourself 5 steps, about 15 minutes, no software needed.
Start the steps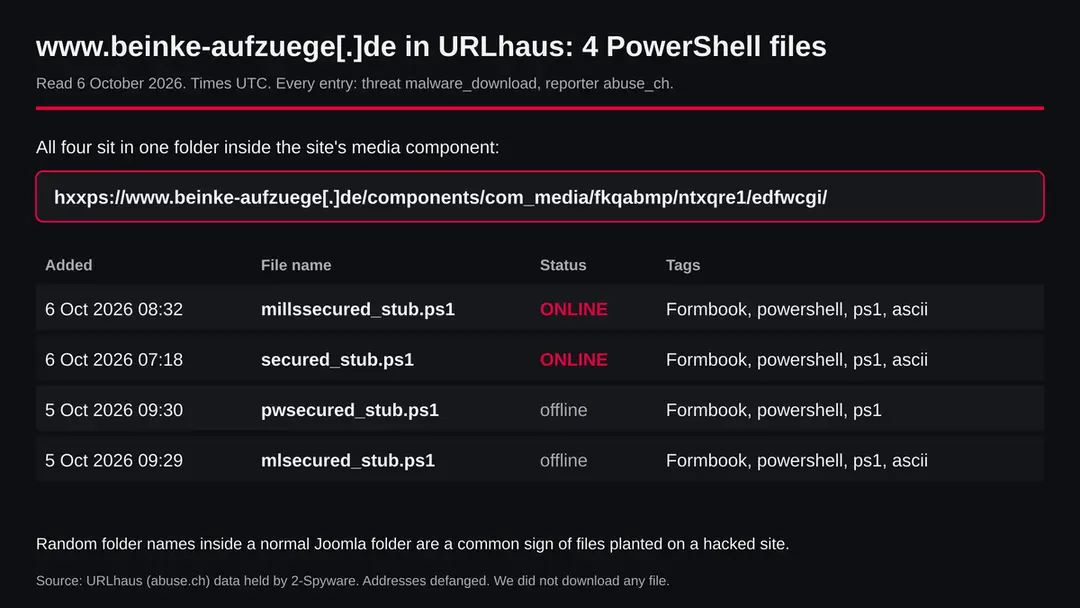
Www.beinke-aufzuege.de (FormBook PowerShell stubs on a hacked site): summary
| Type | A hacked website: URLhaus lists four PowerShell loader files tagged Formbook (an information stealer for Windows) in a planted folder |
|---|---|
| Risk | High if a script on your PC fetched the files: form data, passwords, keystrokes and screenshots may be taken. Low if you only visited the site or saw the name |
| Symptoms | Often none. A script window after opening an attachment, unknown startup tasks, or aspnet_compiler.exe running with no reason are the signs in the reports |
| How to get rid of it | Change passwords from another device, run Microsoft Defender Offline, remove startup entries, reset Windows if unsure. Site owner: remove the folder and close the way in |
| Our check (6 October 2026) | One plain request to the home page: HTTP 200 from nginx. A working site clears nothing; the rating comes from URLhaus |
| Running since / first seen | Domain age not known (no public RDAP record); first files reported 5 October 2026 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Platform | Windows. Nothing we read says Mac or phones are affected |
|---|---|
| Detection names | No Microsoft name is known for these files, because we did not open them. For FormBook in general Microsoft uses Trojan:Win32/Formbook |
| Name | Www.beinke-aufzuege.de |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 5 October 2026 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against the URLhaus data for www.beinke-aufzuege.de held in our database, an RDAP lookup that found no public record, one plain request of our own from our server (no browser, no clicks), and published material from Microsoft, Malpedia, SOC Prime, Sucuri, CSO and the FTC.
We did not download the files, did not access the server and infected no PC; the steps follow Microsoft's pages and Sucuri's guide and were not tried on this case.
What www.beinke-aufzuege.de is, and what we know about it
www.beinke-aufzuege.de is not a program on your PC. It is the address of a German website whose name reads as Beinke lifts (Aufzüge is German for lifts or elevators). URLhaus, the abuse.ch malware tracker, lists four PowerShell scripts on it, all tagged Formbook, a password stealer for Windows.
The files sit in a folder with random names inside the site's own media component. That pattern usually means someone planted them on a hacked site, not that the business itself spreads malware. We could not confirm who runs the site, and we found no public write-up of this case.
- 1
What URLhaus lists
Four file addresses, all in /components/com_media/fkqabmp/ntxqre1/edfwcgi/. Two were added on 5 October 2026 a minute apart (mlsecured_stub.ps1 and pwsecured_stub.ps1) and two on 6 October 2026 (secured_stub.ps1 at 07:18 UTC and millssecured_stub.ps1 at 08:32 UTC). Every entry carries the threat label malware_download, the reporter abuse_ch and the tags Formbook, powershell and ps1.
- 2
Why it looks like a hacked site
components/com_media is the folder of the media manager in Joomla, a widely used website system. A real Joomla site has no folders called fkqabmp, ntxqre1 or edfwcgi there. Random nested folders inside a normal system folder are a common way to hide planted files. This is our reading of the path; we have not seen the server, and the owner may know more.
- 3
What the file names say
A stub, in this trade, is the small piece that unpacks and starts the real malware. The prefixes ml, pw and mills look like labels for different buyers or campaigns. Files called secured_stub.ps1 also appear on other servers in URLhaus this week, for example on aksiyononline.best, where they are tagged MassLogger. That shows a shared naming habit, not a proven link.
- 4
What we could not confirm
We did not download the files, so we cannot tell you what each script does, which FormBook build it leads to or where it sends data. We do not know how the files got onto the site, who the owner is, or which email or attachment makes a victim's PC ask for them.
- 5
What this means for you
If you visited the company's pages to look at lifts, that visit is not what URLhaus reports, and the pages themselves are not tagged. The risk is for a Windows PC where a script already ran and fetched one of these PowerShell files. If you run or look after this website, the files need to come down and the way in needs to be closed.
- Kind of threat
- A real website hosting four PowerShell loader files tagged Formbook, an information stealer for Windows
- Where the files are
- hxxps://www.beinke-aufzuege[.]de/components/com_media/fkqabmp/ntxqre1/edfwcgi/*secured_stub.ps1
- Domain record
- Our RDAP lookup found no public record for beinke-aufzuege.de, which is usual for .de names; we have no registration date
- URLhaus entries
- 4 file addresses added 5 and 6 October 2026; 2 online, 2 offline when we read the data
- Home page
- Answered our plain request with HTTP 200 from an nginx server; no page title was returned
- Platform
- Windows. PowerShell stubs and FormBook are Windows threats; nothing we read says Mac, iPhone or Android are affected
What www.beinke-aufzuege.de (FormBook PowerShell stubs on a hacked site) does on an infected PC
What we checked on 6 October 2026, and what we could not
Our server sent one plain request to the home page on 6 October 2026. It was not a browser visit: nothing was clicked, no page scripts ran and no screenshot was taken. The site answered normally. That clears nothing, because the reported files sit deep in a subfolder and a hacked site usually keeps working while it hosts malware.
Our check, 6 October 2026
- The home page answeredHTTP status 200, no redirect, server header nginx. No page title came back in our plain request. A working home page is expected on a hacked site: the intruder wants the owner to notice nothing.
- Notification requestThe page text did not mention the browser notification API. Scripts that only run in a browser would not show in a plain request.
- URLhaus listingFour PowerShell files tagged Formbook in a random folder under components/com_media; secured_stub.ps1 and millssecured_stub.ps1 still online in our copy of the data on 6 October 2026.
- Who runs the siteNot confirmed. The public RDAP service returned no record for the .de name, and a web search did not show a company page we could tie to it.
- The files themselvesWe did not request or open any of the listed scripts. We cannot tell you what they contain beyond the names and tags.
Dangerous: do not fetch the listed files The rating is about the four files URLhaus lists, not about the company. Until the owner removes them, treat any request to that folder as a malware download and do not run anything that makes one.
What happened on www.beinke-aufzuege.de, as far as the reports show
We only see the end of the story: the dates when the files were reported. When the site was broken into is not known. Times are UTC.
Unknown
The site is opened up
Someone gets the ability to write files under components/com_media. Common ways in for Joomla sites are an outdated core or extension, a stolen admin or hosting password, or another hacked site on the same hosting account. We do not know which applies here.
5 October 2026, 09:29 UTC
The first two files are reported
abuse.ch adds mlsecured_stub.ps1 and, a minute later, pwsecured_stub.ps1. Both are tagged Formbook, powershell and ps1. Both are offline by the time we read the data.
6 October 2026, 07:18 UTC
secured_stub.ps1 appears
A third file with the plain name secured_stub.ps1 is added in the same folder. It is still online when we read the data.
6 October 2026, 08:32 UTC
millssecured_stub.ps1 appears
A fourth file is added, also online. The folder keeps being used across two days, so whoever placed the files still had access on 6 October.
All four URLhaus entries for www.beinke-aufzuege.de on 6 October 2026: one folder, four file names, all tagged Formbook. 6 October 2026
Our check
Our plain request to the home page gets HTTP 200 from nginx. The site still works as a website.
What the pattern suggests, and what it does not: new files keep arriving in the same folder while older ones go offline, which looks like an intruder who still has write access and replaces files as they are reported. That is our reading of the dates, not something a report says, and it is the main reason the owner should not only delete the files.
Why a company website ends up hosting malware
Criminals like real business sites as hosting: the address has a history, is not on block lists and is trusted by mail and web filters more than a domain registered last week. The owner is usually a victim too.
- 1
Old software
Sucuri's Joomla guide calls outdated software one of the leading causes of infection. The media manager itself has had flaws: in 2013 CSO reported a Joomla bug, fixed in 3.1.5 and 2.5.14, that let attackers upload files the media manager should have refused, and that was used to host malware and phishing. We have no sign that this old flaw was used here.
- 2
Extensions
Joomla sites run third party extensions, and each one is another piece of code that needs updates. Sucuri says to update the core and all extensions right after a cleanup.
- 3
Stolen logins
An administrator, FTP or hosting password taken by a stealer (FormBook among them) lets someone upload files without any bug at all. Sucuri says to reset all user passwords and to check for admin accounts that should not exist.
- 4
Backdoors left behind
Sucuri warns that intruders leave several hidden ways back in, and that all backdoors must be closed for a cleanup to hold. Deleting the four .ps1 files alone is unlikely to be enough.
How a PowerShell stub on a hacked site leads to FormBook
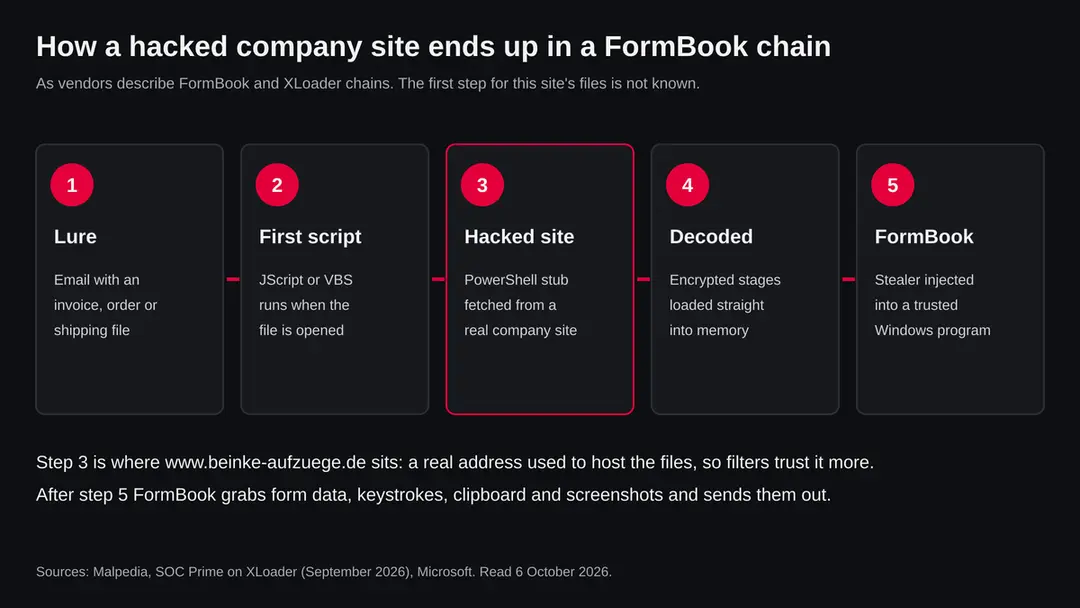
A .ps1 file on a website cannot hurt you by sitting there. It works only when a script already running on a PC downloads it and runs it with PowerShell. We did not see these files; this is how vendors describe FormBook and XLoader chains.
- 1
An email with a business attachment
FormBook is mostly spread by malicious email that looks like invoices, shipping documents or quotes. Malpedia lists many such campaigns with trojanized documents.
- 2
A first script runs
SOC Prime (7 September 2026) describes an XLoader chain that starts with a JScript file from a phishing email. Opening it is the moment the PC is lost.
- 3
PowerShell fetches the stub
In that chain the next stages are AES encrypted PowerShell scripts. A file like secured_stub.ps1 on a trusted website fits this step: a download from a real company address raises fewer alarms.
- 4
Stages are decoded in memory
XOR encrypted payloads and a .NET injector follow, loaded in memory rather than saved as ordinary programs.
- 5
FormBook runs inside a trusted program
SOC Prime names process hollowing into aspnet_compiler.exe, a genuine Windows program. Malpedia notes FormBook's own RunPE crypter for the same purpose. In Task Manager the stealer wears a Microsoft name.
What FormBook is
FormBook is a Windows information stealer that has been sold to criminals for years and is still among the most common. XLoader is its newer descendant. URLhaus tags these files Formbook; it does not say which version.
| Question | What the sources say | Source |
|---|---|---|
| What is it? | A form grabber and keylogger; it takes what you type into web forms and other programs | Malpedia |
| Other names | First called Babushka Crypter; XLoader is tracked as its successor | Malpedia; SOC Prime |
| How is it sold? | As a service to many buyers, so many unrelated campaigns use it | SOC Prime; Malpedia |
| What does it take? | Form data, keystrokes, clipboard and screenshots; the XLoader chain adds browser credentials and mail data | Malpedia; SOC Prime |
| How does it hide? | Its own crypter, process hollowing into trusted programs such as aspnet_compiler.exe, and encrypted stages | Malpedia; SOC Prime |
| What does Microsoft call it? | Trojan:Win32/Formbook; Microsoft says Defender detects and removes it and advises a full scan | Microsoft Security Intelligence |
| Which build is this site's? | Not known. URLhaus gives only the tag; we did not open the files | Not available |
What www.beinke-aufzuege.de (FormBook PowerShell stubs on a hacked site) can steal or download
What FormBook takes from a Windows PC
FormBook does not need anyone watching: once it runs, it collects and sends on its own. The list comes from Malpedia and the XLoader chain write-up; a given build may do less or more.
Reported as collected
- Everything typed into web forms
- Every key you type
- Clipboard contents
- Screenshots
- Browser saved logins
- Email data and logins
| Data | Detail | Source |
|---|---|---|
| Forms | Logins, card numbers and other data typed into web forms, grabbed before the page encrypts them | Malpedia |
| Keystrokes | Recorded in the background | Malpedia |
| Clipboard and screen | Copied text and screenshots | Malpedia |
| Browsers and mail | Saved browser credentials and mail data | SOC Prime |
| Control | Contact with a command server that can send further instructions | SOC Prime; Microsoft |
What this can cost you
Visiting the company's pages is not the risk. The risks below apply to a Windows PC where a script fetched one of these files and FormBook then ran, and, separately, to the site owner.
- High
Passwords and accounts
Form grabbing and keylogging catch logins as you type them, including new passwords set on the infected PC.
- High
Payments
Card numbers typed into shop or bank forms are form data. Treat any card used on the PC since the infection as exposed.
- High
For the site owner: an open door
Files keep appearing in the folder, so someone still has write access. Mail providers and filters may block the domain while it hosts malware, and visitors and customers may be warned away.
- Medium
Work mail and further fraud
Stolen mail logins are often used to send the next wave of invoice emails to the victim's contacts.
- Low
Nothing, if you only saw the name or visited the home page
A name in a log, or a normal visit to the pages, is not an infection.
What you may notice, and what you may not
FormBook is built to stay quiet. The signs below come from the sources and from what they imply; most victims notice nothing until an account is misused.
| Sign | What the reports show |
|---|---|
| A script or PowerShell window that flashed after opening an attachment | The chains start with JScript or VBS and move to PowerShell |
| A Microsoft program running when it should not | aspnet_compiler.exe is named as a hiding place; one running on a home PC with no reason is worth a look |
| A Defender detection | Microsoft's name is Trojan:Win32/Formbook; Microsoft lists slow performance, changed files and crashes as possible effects |
| Accounts acting strangely | New sign ins, password reset emails, mail rules or messages you did not send |
| For the owner: odd folders or files on the server | Random folder names under components/com_media, or .ps1 files anywhere in a web folder |
| Nothing at all | Memory only stages are the point of the chain |
How to check the PC for www.beinke-aufzuege.de (FormBook PowerShell stubs on a hacked site)
How a person ends up asking for these files
Nobody types a path like this by hand. The request comes from a script on the PC, so the real question is how that script got there. We cannot say for these files; the routes below are the ones vendors report for FormBook.
- 1
An invoice, order or shipping email
Fake business documents are the classic FormBook lure. The attachment is often an archive with a script that looks like a PDF when file endings are hidden.
- 2
A link to a real looking site
Because the files sit on a genuine company domain, a link or download from it passes a quick look at the address bar or the mail filter.
- 3
A document that asks you to allow content
Malpedia lists campaigns with trojanized documents. Clicking to enable content or open an embedded file starts the chain.
Check your PC before you delete anything
Did something on this PC request a file under /components/com_media/ on www.beinke-aufzuege.de, or did you open an unexpected attachment or script in the last days? A normal visit to the company's pages is not the question. If you saw the address in a firewall or DNS log, look at the full path if your log shows it, and check the device that asked.
While you check, stop using the PC for banking, email, work or shopping. Use a phone or another computer for anything that needs a password.
- 1
Disconnect first
Turn off Wi-Fi or unplug the network cable on that PC.
- 2
Open Protection history
In Windows Security > Virus & threat protection > Protection history, look for Trojan:Win32/Formbook, any detection with PowerShell or a script in its name, or anything blocked at the time of the first contact.
- 3
Look at what starts with Windows
Open Settings > Apps > Startup and look for names you did not install, then open Task Scheduler and look for tasks that run PowerShell, wscript or a program from a user folder. Write down what you find; do not delete yet.
- 4
Look for trusted programs that should not be running
Open Task Manager and look for aspnet_compiler.exe or a PowerShell process running with no reason. Right click and choose Open file location. Their presence is not proof, and their absence does not clear the PC.
- 5
Check your accounts from another device
Look at sign in activity and mail forwarding rules of your email, bank and work accounts. This tells you more than a file check.
- 6
A scan helps, but it does not clear the PC
Microsoft says Defender detects and removes FormBook and advises a full scan with current definitions. Treat a clean result as one data point. We did not infect a PC, so the order of the plan is our judgement from Microsoft's pages, not a tested result.
How to remove www.beinke-aufzuege.de (FormBook PowerShell stubs on a hacked site)
How to remove www.beinke-aufzuege.de
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like www.beinke-aufzuege.de add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after www.beinke-aufzuege.de, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of www.beinke-aufzuege.de that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Www.beinke-aufzuege.de can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
If you run or look after www.beinke-aufzuege.de
This part is for the owner, the web agency or the host. The files are still being added, so removing them is the first step, not the last. The steps follow Sucuri's Joomla cleanup guide; we have not seen the server.
- 1
Back up the current state, then take the folder down
Copy the site and the database for evidence, then remove /components/com_media/fkqabmp/ and everything below it. Sucuri says to back up before any change.
- 2
Compare the site with clean Joomla files
Sucuri says to compare the installation against a clean copy of the same Joomla version and to check recently modified files. Look in images, media, templates, tmp and the web root as well.
- 3
Hunt for backdoors
Search PHP files for functions such as eval, base64_decode and gzinflate, which Sucuri names as common in backdoors, and check the database for injected content.
- 4
Check every account
Remove administrator accounts you do not recognise, then reset all Joomla, FTP, SSH, database and hosting passwords and turn on two factor sign in. Do this from a PC you trust; a stealer on the admin's own PC may be how the site was opened.
- 5
Update Joomla and every extension
Install the current Joomla release and current versions of all extensions and templates; remove the ones you do not use.
- 6
Ask for the listing to be reviewed
When the files are gone, URLhaus marks them offline. Sucuri also advises requesting a review in Google Search Console if the site was flagged. Watch the folder for a few weeks: new files mean a way in is still open.
If you use a Mac, an iPhone or an Android phone
PowerShell stubs and FormBook are Windows threats. We found nothing that says these files affect anything else.
| Your device | What we know | What to do |
|---|---|---|
| Mac | PowerShell stubs and the FormBook builds in these reports target Windows | Nothing to remove for this threat. Do not follow the Windows steps on a Mac |
| iPhone or iPad | No source describes these files on iOS | Nothing to remove. Change passwords you used on an affected Windows PC |
| Android | No source mentions it | Nothing to remove for this threat |
After removal: passwords, accounts and prevention
After a clean PC: protect what was taken
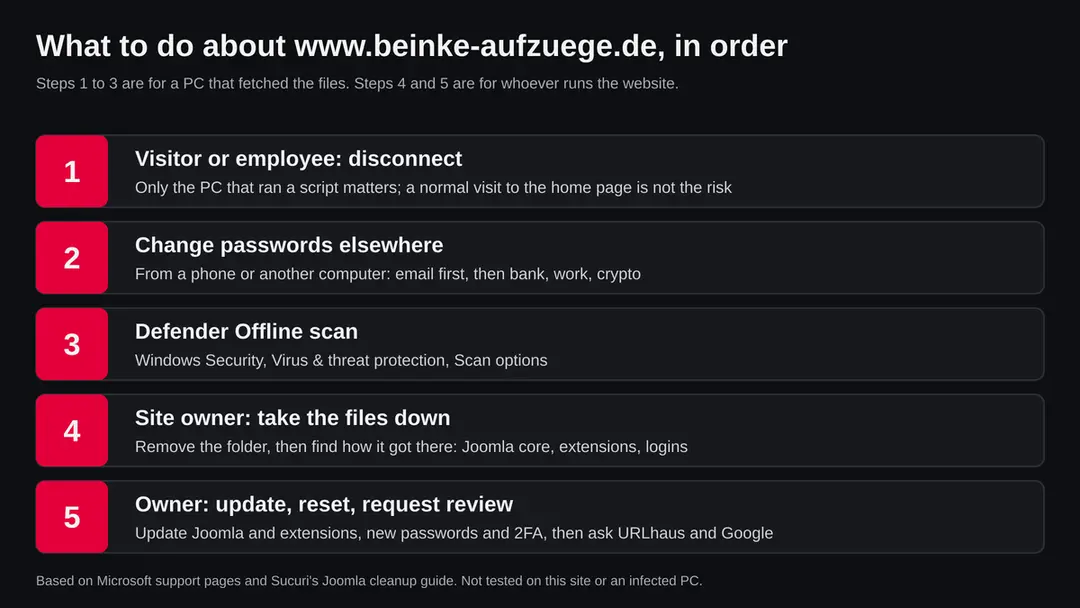
The PC is one half. The other half is everything typed into it while FormBook ran. Do the account steps from another device first.
- 1
Change passwords from a clean device
Start with email, then bank, work, shopping and cloud accounts. Anything typed on the PC while FormBook ran is known.
- 2
Sign out other sessions and turn on two step sign in
The FTC says to sign out of all devices and to turn on two factor authentication, and to check recovery details and forwarding rules.
- 3
Call your bank about cards used on the PC
Form data includes card numbers typed into payment pages. Ask for any such card to be blocked and replaced.
- 4
Run Microsoft Defender Offline
Microsoft says to open Windows Security > Virus & threat protection > Scan options, choose Microsoft Defender Antivirus (offline scan) and select Scan now. The PC restarts and scans before Windows loads; results appear in Protection history.
- 5
If you are not sure, reset Windows
Microsoft puts the reset at Settings > System > Recovery > Reset this PC. Keep my files removes apps and settings; Remove everything wipes the PC. Back up documents first and have your BitLocker recovery key ready.
- 6
Restore only documents by hand
Copy back documents and photos, not programs or scripts.
- 7
Watch your accounts for weeks
Turn on alerts. The FTC says to report stolen personal information at IdentityTheft.gov. If a work account was on the PC, tell your IT team the same day.
Keep a PC, and a website, out of this kind of chain
For a PC the chain starts with an attachment; for a website it starts with old software or a stolen login.
Do
- Treat an unexpected invoice, order or shipping notice with an attachment as an attack until the sender confirms it another way.
- Show file endings in File Explorer so a .js or .vbs file posing as a PDF is visible.
- Keep Windows and Microsoft Defender updated.
- Site owners: keep Joomla, extensions and templates current and remove unused ones.
- Site owners: use two factor sign in for the admin panel and the hosting account.
- Use a password manager and two step sign in for your own accounts.
Don't
- Do not trust a download only because it comes from a real company domain.
- Do not open archives or scripts you did not expect.
- Do not change your passwords on the PC you suspect.
- Site owners: do not only delete the reported files; find the way in.
- Do not take a working home page or a clean scan as proof that all is well.
Questions about www.beinke-aufzuege.de (FormBook PowerShell stubs on a hacked site)
What is www.beinke-aufzuege.de?
It is the address of a German website whose name reads as Beinke lifts. URLhaus, the malware tracker run by abuse.ch, lists four PowerShell files on it, all tagged Formbook, added on 5 and 6 October 2026.
They sit in random folders inside the Joomla media component, which points to a hacked site. We could not confirm who runs it and did not download the files.
Is www.beinke-aufzuege.de safe to visit?
The pages themselves are not what URLhaus lists, and our plain request to the home page got a normal answer. But a site that hosts planted malware may hold more than was reported, and the intruder still seemed to have access on 6 October.
Until the owner cleans it, avoid downloading anything from it and never run a file or script that came from it.
Is the company spreading malware on purpose?
Nothing we read suggests that. Files in random folders such as fkqabmp/ntxqre1/edfwcgi inside a normal Joomla folder are typical of a break in.
Criminals use real business sites because their addresses are trusted more than new domains. The owner is most likely a victim and may not know yet. Telling them helps.
What is FormBook?
FormBook is an information stealer for Windows, sold to criminals as a service for years.
Malpedia describes it as a form grabber and keylogger that also takes clipboard contents and screenshots; its successor XLoader adds browser credentials and mail data in recent chains. Microsoft calls it Trojan:Win32/Formbook. It usually arrives through invoice or shipping emails.
I saw www.beinke-aufzuege.de in my firewall or DNS log. Am I infected?
Not necessarily. A visit to the company's pages would also show the name. What matters is whether the device asked for a file under /components/com_media/.
If your log shows full paths, check for that. If not, and the device opened an unexpected attachment or script recently, disconnect it and run the checks on this page, then change passwords from another device.
How do I remove FormBook from Windows?
Change your passwords from another device first. Then run a Microsoft Defender Offline scan from Windows Security, check startup apps and Task Scheduler for entries that run PowerShell or scripts, and remove what you can tie to the malware.
If you are not sure, reset Windows with Remove everything and restore only documents. We followed Microsoft's pages and did not test this on an infected PC.
I run this website. What should I do?
Back up the current state for evidence, remove the planted folder under components/com_media, compare the site with clean Joomla files, look for backdoors and unknown admin accounts, reset every password from a trusted PC with two factor sign in, and update Joomla and all extensions.
Then watch the folder: new files mean the way in is still open. Sucuri's Joomla guide covers each step.
Does this affect Mac, iPhone or Android?
We found nothing that says so. PowerShell stubs and FormBook are Windows threats, and every source we read describes Windows. On a Mac, iPhone or Android phone there is nothing to remove for this threat, but change any password that was typed on an affected Windows PC, and do it from the clean device.
Will resetting Windows remove it, and are my accounts safe afterwards?
A reset with Remove everything wipes the scripts and the stealer, without having to find every piece. It does not undo what was already sent.
Passwords and card numbers typed while FormBook ran stay exposed until you change them from another device, sign out other sessions and turn on two step sign in. Restore documents by hand, not a full system image.
Will Fortect remove www.beinke-aufzuege.de?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For www.beinke-aufzuege.de, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Malpedia (Fraunhofer FKIE): FormBook (read October 6, 2026)
- SOC Prime: Inside the XLoader infection chain (7 September 2026) (read October 6, 2026)
- Microsoft Security Intelligence: Trojan:Win32/Formbook (read October 6, 2026)
- Sucuri: How to clean a hacked Joomla site (read October 6, 2026)
- CSO: Joomla patches file manager vulnerability responsible for hijacked websites (12 August 2013) (read October 6, 2026)
- Microsoft Support: Help protect my PC with Microsoft Defender Offline (read October 6, 2026)
- Microsoft Support: Recovery options in Windows (Reset this PC) (read October 6, 2026)
- FTC: Email or social media hacked? Here's what to do (read October 6, 2026)