
thisisafalsepositive.st: a SilentNet stealer server behind fake Minecraft mods, and how to clean a Windows PC
thisisafalsepositive.st is a web address that URLhaus lists 13 times for files tagged SilentNet, a stealer spread as fake Minecraft mods, plus a Python kit for Windows. Despite its name, the warning you saw is not a mistake.
If you only saw the address in a block, nothing is proven. If you added a mod or client from outside the usual mod sites, treat your Windows PC and your Minecraft, Discord and browser accounts as exposed: secure them from another device, then clean or reset the PC.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If a Minecraft mod, client or Python script that downloads files from thisisafalsepositive.st keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove thisisafalsepositive.st (SilentNet stealer) yourself 5 steps, about 15 minutes, no software needed.
Start the steps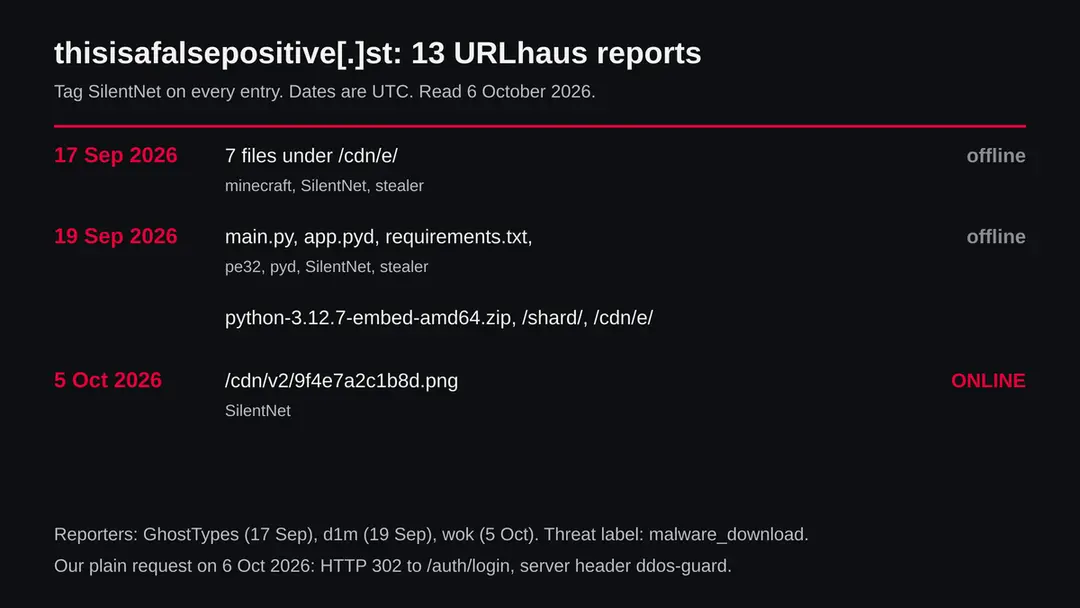
Thisisafalsepositive.st (SilentNet stealer): summary
| Type | A malware server: URLhaus tags its files SilentNet and stealer, seven also minecraft; Triage describes SilentNet as a Minecraft Fabric mod stealer |
|---|---|
| Risk | High if a mod or script from it ran: game, Discord, browser and wallet data may be taken. Low if you only saw the name |
| Symptoms | Often none. An unknown .jar in the mods folder, a Python folder you did not install, Discord messages you did not send |
| How to get rid of it | Change passwords from another device and sign out everywhere, remove the mod and the Python files, run Microsoft Defender Offline, reset Windows if unsure |
| Our check (6 October 2026) | One plain request from our server: a redirect to /auth/login behind ddos-guard. It clears nothing |
| Running since / first seen | First files reported 17 September 2026; registration date not known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Platform | Windows for the Python stage; a Java mod can also run on Mac |
|---|---|
| Detection names | For SilentNet itself no Microsoft detection name is known to us. Microsoft lists Trojan:Java/WeedHack!MTB for the companion Minecraft mod family and a generic Trojan:Python/Stealer |
| Name | Thisisafalsepositive.st |
| Evidence | 13 write-ups by security sites; details still limited |
| First seen | 17 September 2026 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against the URLhaus data for thisisafalsepositive.st held in our database, an RDAP lookup that found no record, one plain request from our server, and published material from Triage, Check Point Research, The Register, Microsoft and the FTC. We did not download the files and we infected no PC; the removal steps follow Microsoft's pages and were not tried on a live infection.
What thisisafalsepositive.st is, and what we know about it
thisisafalsepositive.st is not a program on your PC. It is a web address that the abuse.ch project URLhaus lists 13 times as a place where malware was handed out, and every entry carries the tag SilentNet, a stealer that the sandbox service Triage describes as a Minecraft Fabric mod with blockchain command and control. We found no public write-up of this one address, so what follows is what URLhaus shows, what our plain request showed, and what analysts have published about SilentNet and about fake Minecraft mods.
- 1
What URLhaus lists
Thirteen file addresses on the domain, added on three days. Seven on 17 September 2026, all under a folder called /cdn/e/ and tagged minecraft, SilentNet and stealer. Five on 19 September, including main.py, app.pyd, requirements.txt and python-3.12.7-embed-amd64.zip, tagged pe32, pyd, SilentNet and stealer. One on 5 October, a file ending in .png under /cdn/v2/, tagged SilentNet. The 5 October entry is the only one still marked online.
- 2
What the file names tell us
python-3.12.7-embed-amd64.zip is the name of the official embeddable Python package for 64 bit Windows: a small copy of Python that runs without being installed. main.py is a Python script, app.pyd is a compiled Python module (on Windows a .pyd file is a kind of DLL, which is why it is also tagged pe32), and requirements.txt is the usual list of extra Python libraries a script needs. Put together, this looks like a kit that brings its own Python and then runs a stealer in it. That is our reading of the names, not something a report states.
- 3
What the name of the domain is for
The name reads as a sentence: this is a false positive. A person who sees a warning from an antivirus, a firewall or a browser with this address in it may think the warning itself is a mistake. That is our reading of the name. Nothing about the address makes the warning wrong: the files were reported by three different people and all carry the same malware tag.
- 4
What we could not confirm
We did not download any of the files, so we cannot say which SilentNet build they carry, what exactly it collects or where it sends the data. We also do not know which fake mod, cheat client or message brought victims to it. The .png file still online may be a picture or may hide something else; a file ending does not prove what is inside.
- Kind of threat
- A server that handed out files tagged SilentNet and stealer; seven entries also tagged minecraft
- Where the files were
- hxxps://thisisafalsepositive[.]st/cdn/e/..., hxxps://thisisafalsepositive[.]st/main.py, hxxps://thisisafalsepositive[.]st/app.pyd and similar; the newest is hxxps://thisisafalsepositive[.]st/cdn/v2/....png
- URLhaus entries
- 13 file addresses added on 17 September, 19 September and 5 October 2026; 1 online, 12 offline when we read our copy of the data on 6 October 2026
- Reporters
- GhostTypes (17 September), d1m (19 September) and wok (5 October); threat label malware_download on all
- Domain registration
- Not known. Our RDAP lookup on 6 October 2026 found no record for the .st domain, which is common for this country ending and says nothing about the site
- Platform
- Windows. The files include a Windows Python package and Windows modules; the mod route needs Minecraft Java Edition, which runs on Windows, Mac and Linux, but the second stage seen here is for Windows
What thisisafalsepositive.st (SilentNet stealer) does on an infected PC
What we checked on 6 October 2026, and what we could not
We sent one plain request to the home page of the domain from our server on 6 October 2026. It was not a browser visit: no page was drawn, nothing was clicked and no file was opened. A quiet answer clears nothing.
Our plain request, 6 October 2026
- The answerHTTP 302, a redirect to /auth/login, with the page title Redirecting.... The front door of the site asks for a login, so a casual visitor sees nothing.
- Who answeredThe server header said ddos-guard, a service that sits in front of websites and filters traffic. It hides where the real server is. It is used by many legitimate sites too, so it is not proof of anything on its own.
- Notification requestsNone mentioned in the answer. There was no real page to look at.
- URLhaus listing13 entries tagged SilentNet, 11 also tagged stealer; one file still online on 6 October 2026.
- The files themselvesWe did not request or download any listed file. We cannot tell you what they contain.
Dangerous: treat it as a malware server A login page at the front and a filtering service in front of it are what a hidden file server often looks like. The rating comes from the 13 URLhaus reports by three different reporters, not from our request. Do not download anything from this address and do not run a mod, client or script that points to it.
What happened to thisisafalsepositive.st, report by report
All reports fall within three weeks. Dates and times come from the URLhaus data we hold and are in UTC.
17 September 2026
Seven files under /cdn/e/
Between about 05:44 and 05:46 UTC the reporter GhostTypes adds seven addresses under /cdn/e/, each ending in a 12 character code. All are tagged minecraft, SilentNet and stealer. The minecraft tag says the reporter tied them to the game.
19 September 2026
A Python kit appears
At about 05:55 UTC the reporter d1m adds six addresses: the folders /cdn/e/ and /shard/, and the files main.py, app.pyd, requirements.txt and python-3.12.7-embed-amd64.zip. All are tagged pe32, pyd, SilentNet and stealer. This is the first sign of a Windows stage built on Python.
5 October 2026
A new folder and a picture name
At about 18:02 UTC the reporter wok adds a file under /cdn/v2/ ending in .png, tagged SilentNet. The new folder name, v2, may mean a second version of the delivery. That is our reading.
The URLhaus reports for the address as we read them on 6 October 2026: three groups of files, three reporters, one entry still online. 6 October 2026
Our request
Our plain request to the home page is answered with a redirect to a login page behind ddos-guard. Twelve of the 13 file addresses are marked offline, one is online.
What the pattern suggests: the operator moved files around (/cdn/e/, /shard/, /cdn/v2/) and kept the same domain, which looks like an active service rather than a forgotten leftover. That is our reading of the dates, not something any report says.
What SilentNet is, as far as public sources say
SilentNet is a young family and there is no long vendor report about it that we could find. The table lists what the sources we read actually say, and where they stop.
| Question | What the sources say | Source |
|---|---|---|
| What is it? | A remote access trojan and stealer. Triage describes it as a Minecraft SilentNet RAT, a Fabric mod stealer with blockchain command and control | Triage family notes |
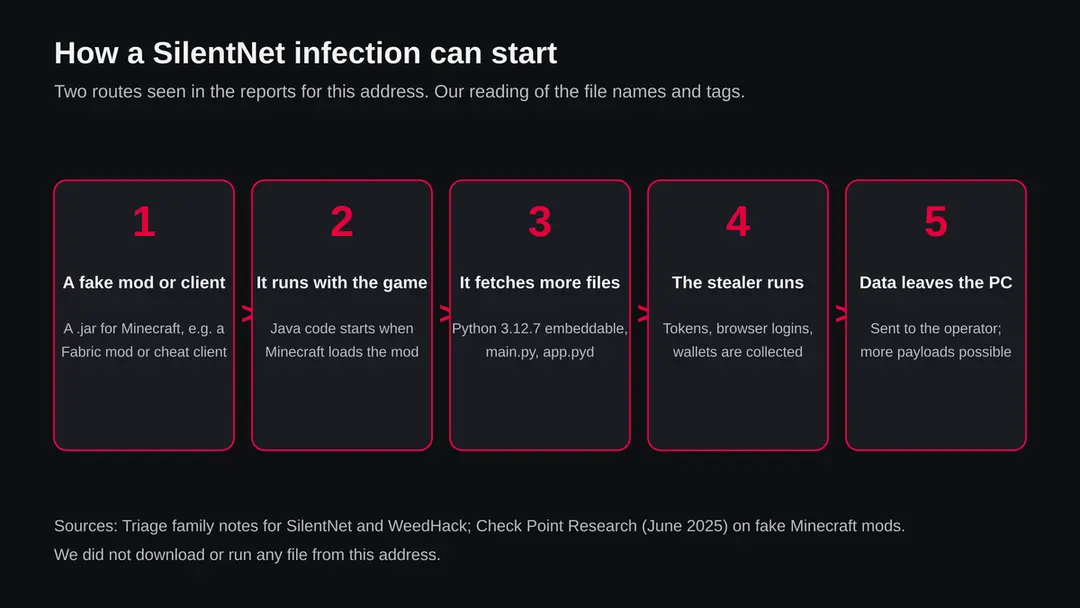
| How does it arrive? | As a .jar file posing as a Minecraft mod or client. The samples we read were named Krypton_Client.jar and fabric-api_14.12.0_1.jar; the second copies the name of a real, popular library mod | Triage reports |
| Does it come alone? | Both samples were also matched to WeedHack, which Triage describes as a Fabric mod that steals session tokens, downloads and runs further payloads and stays hidden | Triage reports |
| What does blockchain command and control mean? | The malware reads its instructions or server address from data stored on a public blockchain instead of from one fixed server, so taking one server down does not cut it off. Triage names the method but does not describe the details | Triage family notes; the explanation is ours |
| Which files did this address serve? | Seven files tagged minecraft, then a Windows Python kit (embedded Python 3.12.7, main.py, app.pyd) and a .png | URLhaus data we hold |
| Is there a Microsoft detection name? | Not for SilentNet by that name. Microsoft lists Trojan:Java/WeedHack!MTB (updated 24 March 2026) for the companion family and a generic Trojan:Python/Stealer; both pages say technical details are not available | Microsoft Security Intelligence |
| What exactly does this build steal? | Not known. We did not open the files | Not available |
Why Minecraft mods are such an easy way in
A Minecraft Java mod is a .jar file that the game loads and runs with your full rights as a user. There is no store review between a random download and your PC. Fake mods are an old trick, and a published case shows how far it goes.
- 1
A known case: Stargazers and fake cheat mods
Check Point Research reported on 18 June 2025 a campaign with about 500 GitHub repositories offering fake versions of cheat tools such as Oringo and Taunahi. The Register reported the same day that the operators were tied to the Stargazers Ghost Network and that over 1,500 devices may have been hit since March 2025.
- 2
It starts when the game starts
Check Point describes a Java loader that runs when Minecraft launches with the mod in place, checks whether it is inside a virtual machine or analysis tool, and only then downloads the next stage.
- 3
Then a second, bigger stealer
In that case the next stages took Minecraft tokens, Discord and Telegram data, browser passwords, crypto wallets, VPN settings and screenshots, and sent them out. The kit on thisisafalsepositive.st uses Python instead of .NET for its Windows stage, but the shape is the same: a small mod, then a stronger program.
- 4
Who it targets
Players who look for cheat clients, free versions of paid clients or mods outside the usual mod sites. Many of them are young and play on a family PC, which means the browser and wallet data of other family members can be exposed too. That last point is our reading.
What thisisafalsepositive.st (SilentNet stealer) can steal or download
What a stealer of this kind can take from a Windows PC
We cannot say what this exact build takes. The list combines what Triage says SilentNet and WeedHack do with what Check Point found in fake Minecraft mods of the same kind.
Reported for this kind of malware
- Minecraft session tokens
- Microsoft account logins
- Discord tokens
- Telegram data
- Saved browser passwords
- Browser cookies and sessions
- Crypto wallet files
- VPN settings
- Screenshots
- Extra malware downloaded
| Data | Detail | Source |
|---|---|---|
| Game accounts | Session tokens that let someone play as you or sell your account | Triage (WeedHack); Check Point |
| Chat accounts | Discord tokens let someone send messages as you, often used to spread the same fake mod to your friends | Check Point; the spreading point is our reading |
| Browser data | Saved passwords and data from Chromium based browsers and Firefox | Check Point |
| Money | Crypto wallets, more than ten types in the Check Point case | Check Point; The Register |
| Control | Download and run further programs, which makes it a remote access tool | Triage |
What this can cost you
Seeing the name costs nothing. The risks apply to a PC where a mod, client or script that uses this address actually ran.
- High
Your Microsoft and Minecraft account
A stolen session token can be used without your password. An account that is sold on is often lost for good.
- High
Discord and friends
A taken Discord account is used to send the same fake mod to everyone on your friend list, with your name on it.
- High
Passwords and crypto
Saved browser passwords and wallet files are on the list of every stealer of this kind. Crypto sent from a stolen wallet cannot be reversed.
- Medium
More malware
Triage says WeedHack downloads and runs further payloads, so a PC that ran it may hold more than one program.
- Low
Nothing, if you only saw the name
A name in a warning, a log or a block list is not an infection. The warning was right to stop it.
What you may notice, and what you may not
Stealers try to be quiet. The signs below are what the reports and the file names point to; none of them is certain.
| Sign | What it can mean |
|---|---|
| A mod or client .jar you do not remember in the mods folder | The usual first stage. Check Point names the mods folder of the launcher as the place to look |
| A folder with python.exe and a python312 file in your user folder | The embeddable Python kit listed on this address unpacks to a folder like that. Python you did not install is worth a closer look |
| Files called main.py or app.pyd outside any program you know | These are the names URLhaus lists for this address |
| Discord messages you did not send | A stolen token in use |
| Logged out of Minecraft, Discord or your browser accounts | Session data used elsewhere or reset by the service |
| Nothing at all | Many victims notice nothing until an account is gone |
How to check the PC for thisisafalsepositive.st (SilentNet stealer)
How a person ends up with files from this address
Nobody opens this address by hand. A downloaded mod, cheat client or script asks for it. We do not know which one for this server; these are the routes the sources and tags point to.
- 1
A cheat or a free paid client
A file named like a client, such as Krypton_Client.jar in a Triage sample, offered on a video page, a Discord server or a file host.
- 2
A copy of a real mod
fabric-api_14.12.0_1.jar copies the name of Fabric API, one of the most downloaded library mods. A copy from an unofficial site can carry anything.
- 3
A link from a friend
A message from a Discord friend whose account was already taken, asking you to test their mod or client. Our reading from how stolen Discord tokens are used.
- 4
A warning that calls itself a mistake
If a tool tells you the antivirus warning is a false positive and asks you to switch protection off, that is the trap. The name of this domain plays on the same idea.
Check your PC before you delete anything
First question: did you, or someone on this PC, add a Minecraft mod or client from outside the usual mod sites in September or October 2026? If you saw the address in a warning that blocked it, nothing may have reached the PC. If you are not sure, do the checks below; none of them deletes anything.
While you check, do not log in to email, bank, Discord or crypto from this PC.
- 1
Disconnect first
Turn off Wi-Fi or unplug the cable. A stealer needs the connection to send what it took and to get new orders.
- 2
Look at the mods folder
Open the mods folder of the launcher you use (for the official launcher it is the mods folder in %APPDATA%\.minecraft; Check Point names the TLauncher path \.tlauncher\legacy\Minecraft\game\mods\ for that case). Write down every .jar you do not recognise and when it was added. Do not start the game.
- 3
Look for a Python you did not install
Search your user folder and %APPDATA% and %LOCALAPPDATA% for python.exe, main.py, app.pyd or requirements.txt. A folder that holds these with no program you know around it matches the kit on this address.
- 4
Look at startup and scheduled tasks
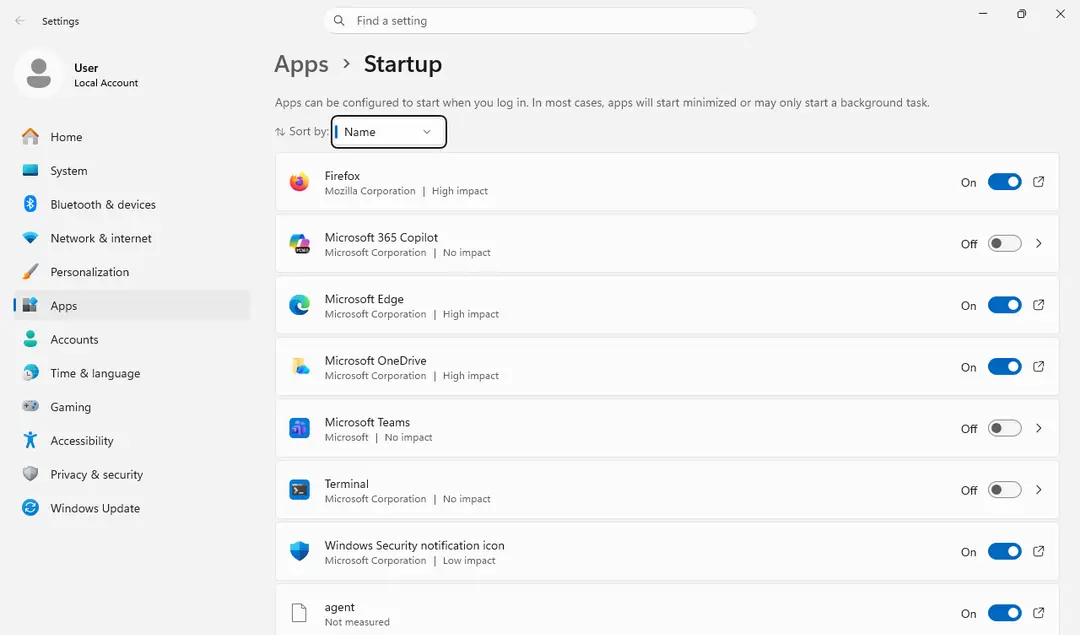
Open Settings > Apps > Startup and switch off what you do not know. Open Task Scheduler and look in Task Scheduler Library for tasks that start python.exe, pythonw.exe or a file from a user folder. Write the name before you remove anything.
- 5
Open Protection history
In Windows Security > Virus & threat protection > Protection history, look for anything found or blocked at the time the mod was added.
- 6
Check your accounts from another device
Look at the sign in activity of your Microsoft account, Discord and email, and at crypto balances. This tells you more than any file check.
How to remove thisisafalsepositive.st (SilentNet stealer)
How to remove thisisafalsepositive.st
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like thisisafalsepositive.st add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after thisisafalsepositive.st, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of thisisafalsepositive.st that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Thisisafalsepositive.st can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
If you play on a Mac, a console or a phone
Every file on this address that hints at a system points to Windows. Minecraft Java mods run on Mac and Linux too, so the first stage could start there, but we found no report of the Windows Python stage working elsewhere.
| Your device | What we know | What to do |
|---|---|---|
| Mac | A malicious Java mod can run on a Mac, and Triage does not say whether SilentNet targets it | Remove unknown mods, change passwords from another device; do not follow the Windows steps |
| Console, Bedrock on phone | Java mods do not run there | Nothing to remove for this threat |
| Any device you used to log in | If your Microsoft or Discord account was taken, it affects all devices | Sign out all sessions and change the password |
After removal: passwords, accounts and prevention
After a clean PC: protect what was taken
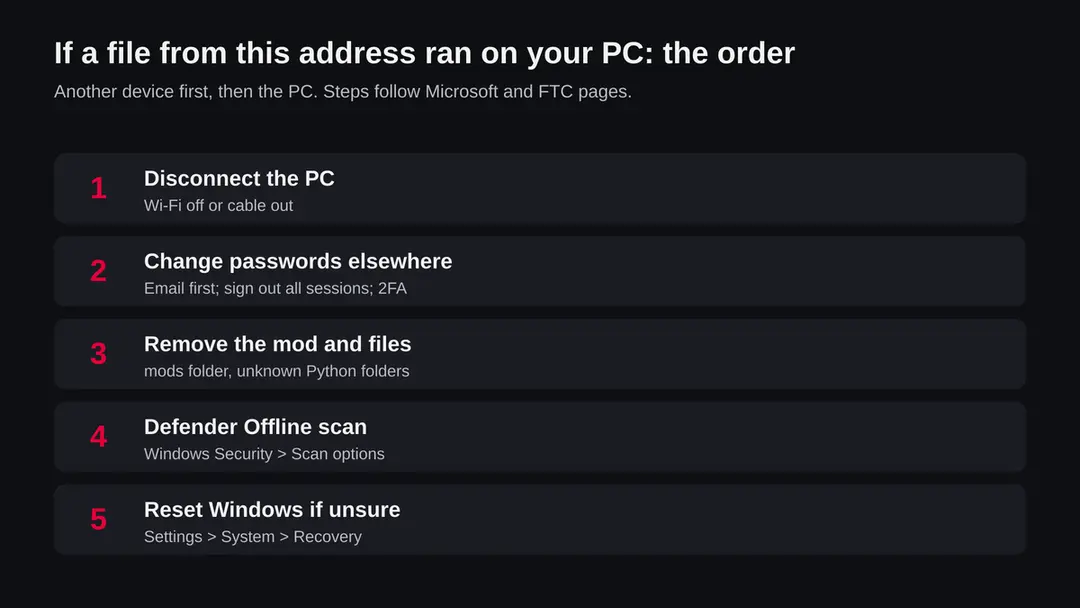
The accounts matter as much as the PC. Do them from another device, in this order.
- 1
Change passwords from a clean device
Start with email, then the Microsoft account used for Minecraft, Discord, bank, and crypto exchanges. Anything typed on the PC may already be known.
- 2
Sign out everywhere and turn on two step sign in
The FTC says to sign out of all devices, to turn on two factor authentication and to check that the recovery email and phone are yours. Session tokens are what these stealers take, and signing out makes them worthless.
- 3
Move crypto if a wallet was on the PC
Create a new wallet on a clean device and move the funds. The old recovery phrase is no longer safe.
- 4
Remove the mod and the Python folder
Delete the unknown .jar files from the mods folder and the folder with the Python kit you found. Empty the Recycle Bin.
- 5
Run Microsoft Defender Offline
Microsoft says to open Windows Security > Virus & threat protection > Scan options, choose Microsoft Defender Antivirus (offline scan) and start it. Save your work: the PC restarts and the scan runs in the Windows Recovery Environment, where malware has a harder time hiding. Results are under Protection history.
- 6
If you are not sure, reset Windows
Microsoft puts it at Settings > System > Recovery > Reset PC. Keep my files reinstalls Windows and keeps personal files; Remove everything removes files, apps and settings. After a stealer with a download function, the full reset does not depend on finding every piece.
- 7
Tell your friends
If your Discord was used, tell your friends not to open the file you seemed to send.
How to avoid fake Minecraft mods
The rules are simple, and they matter most for the cheat and free client downloads that this kind of malware hides in.
Do
- Get mods from the official project page of each mod
- Use a separate Windows account without admin rights for games
- Keep Microsoft Defender on and up to date
- Turn on two step sign in for Microsoft and Discord
- Treat a mod sent by a friend as unknown until you ask them by voice
Don't
- Download cheat clients or cracked paid clients
- Switch off your antivirus because a tool says the warning is a false positive
- Run .jar files from video descriptions or file hosts
- Store a crypto recovery phrase on a gaming PC
Questions about thisisafalsepositive.st (SilentNet stealer)
What is thisisafalsepositive.st?
It is a web address that URLhaus lists 13 times for files tagged SilentNet, a stealer described by Triage as a Minecraft Fabric mod with blockchain command and control.
The reports came on 17 and 19 September and 5 October 2026 from three reporters. It is not a program on your PC. We did not download the files.
Is the warning about thisisafalsepositive.st a false positive?
No reason to think so. The name of the domain says it is, which is our reading of a trick to make people ignore warnings. Three different reporters listed its files as malware, all with the same family tag.
Keep the block. If a tool, a video or a person tells you to switch the antivirus off for a Minecraft mod, treat that as part of the attack, not as advice.
Is thisisafalsepositive.st safe to open?
No. Our plain request on 6 October 2026 got a redirect to a login page behind ddos-guard, which proves nothing. Do not download from it and do not run any mod or client that uses it.
A login page and a traffic filter in front of a site are normal for a hidden file server. The danger rating rests on the 13 URLhaus reports and their tags.
What is SilentNet?
Triage describes it as a Minecraft SilentNet RAT, a Fabric mod stealer with blockchain command and control. Samples we read were .jar files named like a client and like the Fabric API library.
They were also matched to WeedHack, which steals session tokens and downloads more payloads. Microsoft has a detection called Trojan:Java/WeedHack!MTB for the companion family.
Why does the address list Python files?
Because the Windows stage seems to bring its own Python: an embeddable Python 3.12.7 package, main.py, app.pyd and requirements.txt. This lets a script run on a PC without Python installed. That is our reading of the file names.
A .pyd file is a compiled Python module, which on Windows works like a DLL, so it is harder to read than a plain script. If you find these files on your PC, do not open them.
I installed a Minecraft mod from an unofficial site. What now?
Disconnect the PC, change your Microsoft, Discord and email passwords from another device and sign out all sessions. Then remove unknown .jar files from the mods folder, look for a Python folder you did not install, and run Microsoft Defender Offline.
Reset Windows if you are not sure. Tell your Discord friends not to open files you seemed to send.
Can I keep my Minecraft account?
Often yes, if you act fast. Change the Microsoft account password from a clean device, sign out everywhere and turn on two step sign in, so a stolen session token stops working.
If the password or the recovery email was already changed by someone else, use the account recovery of Microsoft from a clean device. Check your Discord account the same way, since stealers of this kind take its token too.
Does this affect Mac or phones?
The Python stage on this address is for Windows. A malicious Java mod can run on a Mac, so remove unknown mods there too.
Consoles and Bedrock on phones do not run Java mods. If you logged in to your Microsoft or Discord account on any device, secure the account itself, because a stolen login works from anywhere.
Will an antivirus scan clean it?
A scan can find known files, but a clean result does not prove the PC is clean or that your accounts are safe. The accounts must be secured from another device either way.
Microsoft Defender has detections such as Trojan:Java/WeedHack!MTB and Trojan:Python/Stealer for this kind of file. Run Microsoft Defender Offline for a scan outside normal Windows, and reset Windows if you remain unsure.
Will Fortect remove thisisafalsepositive.st?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For thisisafalsepositive.st, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Triage report 260424-2ck84set3n: Krypton_Client.jar, families SilentNet and WeedHack (read October 6, 2026)
- Triage report 260428-vrf5dact2y: fabric-api_14.12.0_1.jar, families SilentNet and WeedHack (read October 6, 2026)
- Check Point Research: Minecraft mod malware and the Stargazers Ghost Network (18 June 2025) (read October 6, 2026)
- The Register: Minecraft cheaters never win, but they may get malware (18 June 2025) (read October 6, 2026)
- Microsoft Security Intelligence: Trojan:Java/WeedHack!MTB (24 March 2026) (read October 6, 2026)
- Microsoft Security Intelligence: Trojan:Python/Stealer (read October 6, 2026)
- Microsoft Support: Help protect my PC with Microsoft Defender Offline (read October 6, 2026)
- Microsoft Support: Reset your PC (read October 6, 2026)
- FTC: How to recover your hacked email or social media account (read October 6, 2026)
- URLhaus (abuse.ch) entries for thisisafalsepositive.st, from the data held in our database (read October 6, 2026)