Pro, VIP and Partner members post into rubrics – every follower of the rubric sees the post.Log in

SecurityWeek reports that Citrix is urging immediate patching of a critical NetScaler vulnerability that could lead to remote code execution or denial of service. The flaw affects NetScaler ADC and NetScaler Gateway appliances in specific SAML configurations, as well as Secure Private Access Hybrid deployments. Citrix says it is not aware of unmitigated exploits, but users should update to the fixed versions as soon as possible.
SecurityWeekCitrix Urges Immediate Patching of Critical NetScaler Vulnerability

Source: securityweek.com
Malwarebytes Labs reports that attackers compromised infrastructure behind the .gh, .sl, and .as country-code domain namespaces and used it to obtain unauthorized HTTPS certificates for Google domains and other organizations. Google blocked the certificates in Chrome and worked with certificate authorities to revoke them. Windows users should keep their browser and operating system updated and never bypass certificate warnings.

Malwarebytes LabsAttackers hijack country-code domains to impersonate Google and other services

Source: malwarebytes.com

Chrome OS has received a Long Term Support Channel update to version 150.0.7871.256. Google says it includes selected security fixes, including issues in Browser, Omnibox, Extensions, WebRTC, GPU, PDF, and other components. Devices in the LTC channel will be updated to this version, so users should install it when it arrives.

Chrome ReleasesLong Term Support Channel Update for ChromeOS

Source: chromereleases.googleblog.com

SecurityWeek reports that TP-Link has disclosed five vulnerabilities in its Aginet line of ISP-managed mesh systems, routers and modems. The bugs can let an attacker on the same network take over an affected device, create a super-administrator account, enable SSH access, or recover passwords and Wi-Fi credentials from configuration files. TP-Link says firmware updates are distributed by ISPs, so users should check the device management interface or app for updates and contact their ISP if none are available.

SecurityWeekTP-Link Faces State Lawsuits and New Scrutiny Over ISP Router Flaws

Source: securityweek.com
The Hacker News reports that 16 malicious Firefox extensions were found posing as Rabby and OKX Wallet tools to steal cryptocurrency wallet recovery phrases and private keys. The add-ons intercepted those secrets during wallet import flows and sent them to attacker-controlled Cloudflare Workers. Users who installed any of the extensions and entered a real recovery phrase or private key should assume compromise and move their assets from a clean system.

The Hacker News16 Malicious Firefox Extensions Pose as Rabby and OKX Wallets to Steal Recovery Phrases

Source: thehackernews.com

SecurityWeek reports that Oracle Health says personal and medical information from its legacy Cerner systems was compromised in a cyberattack. The data may have included names, Social Security numbers, and medical record details such as diagnoses, medicines, test results, images, and care information. People affected should watch for suspicious account activity and follow any notice from Oracle Health or their healthcare provider.

SecurityWeekOracle Health Data Breach Tally Climbs to Nearly 20 Million

Source: securityweek.com
SecurityWeek reports that Southern Company is notifying roughly 400,000 customers that an unauthorized third party accessed utility account information through its online customer portal. The exposed data may include names, mailing addresses, phone numbers, email addresses, the last 4 digits of Social Security numbers, and other basic account details. The company says it stopped the activity and is offering affected customers a year of free credit monitoring.

SecurityWeekGeorgia Power, Alabama Power Data Breach Hits 400,000 Accounts

Source: securityweek.com
Google has released Chrome 155 for Windows with 247 security fixes, including four rated critical. Google says the update will roll out over the coming days and weeks, and users can check for it in Chrome by opening the menu, then Help, then About Google Chrome, and relaunching when the download finishes.

gHacksGoogle Releases Chrome 155 With 247 Security Fixes, Four of Them Rated Critical

Source: ghacks.net

The FBI and Secret Service warn that the FortiBleed credential-harvesting campaign is still active and is targeting internet-facing Fortinet FortiGate firewalls and SSL VPN gateways. The agencies say attackers are scanning exposed devices, using stolen credentials, and may be passing access on to ransomware groups. Windows users in small offices should make sure their VPN and admin passwords are changed, active sessions are ended, and device logs are checked for suspicious activity.

The Hacker NewsFBI Warns FortiBleed Remains Active After Amassing 86,644 Fortinet Device Credentials

Source: thehackernews.com

Help Net Security reports that attackers have already started trying to exploit a critical arbitrary file access flaw in Atlassian’s self-managed Data Center products, including Bitbucket, Confluence, Jira Service Management, Jira Software, Bamboo, Crowd, Crucible and Fisheye. Atlassian urged customers to upgrade to a fixed version as soon as possible. Those who cannot update quickly should remove vulnerable instances from the internet or block external access, and check access logs for signs of compromise.

Help Net SecurityExploitation attempts against critical Atlassian flaw have begun (CVE-2026-21589)

Source: helpnetsecurity.com

Infosecurity Magazine reports that unauthorized access to Denmark’s Central Register of Persons exposed names, addresses and CPR numbers for about 8.8 million registered people. The government said the access happened through a private Danish company’s legal access to the system. People should watch for unusual account activity, use unique passwords, keep devices updated and be careful if anyone asks for sensitive information by email, phone or other channels.

Infosecurity MagazineDanish CPR Breach Highlights Challenge of Supply Chain Risk

Source: infosecurity-magazine.com

The Hacker News reports that a malicious spreadsheet can make LibreOffice and Apache OpenOffice run an attacker’s code as soon as the file is opened, without a macro warning. The attack works only when Java support is enabled. LibreOffice has already fixed the flaw, and Apache OpenOffice users should turn off Java or avoid opening spreadsheets they do not trust.

The Hacker NewsLibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Run Code Without Macro Warnings

Source: thehackernews.com

Chrome has been updated on Windows to version 155.0.8059.39/.40, and Google says the release includes 247 security fixes. The update rolls out over the coming days and weeks. Windows users should update Chrome as soon as it appears, since Google says access to bug details may stay restricted until most users are protected.

Chrome ReleasesStable Channel Update for Desktop

Source: chromereleases.googleblog.com

The Register reports that Microsoft is adding .msix and .msixbundle to Outlook’s block list. New Outlook for Windows and Outlook on the Web in Exchange Online will stop users from downloading or opening those attachments by default, because a malicious package could compromise a device. Administrators who need them can allow the file types before the rollout in early to mid-November 2026.

The RegisterMicrosoft extends the Outlook naughty step with two more file types

Source: theregister.com

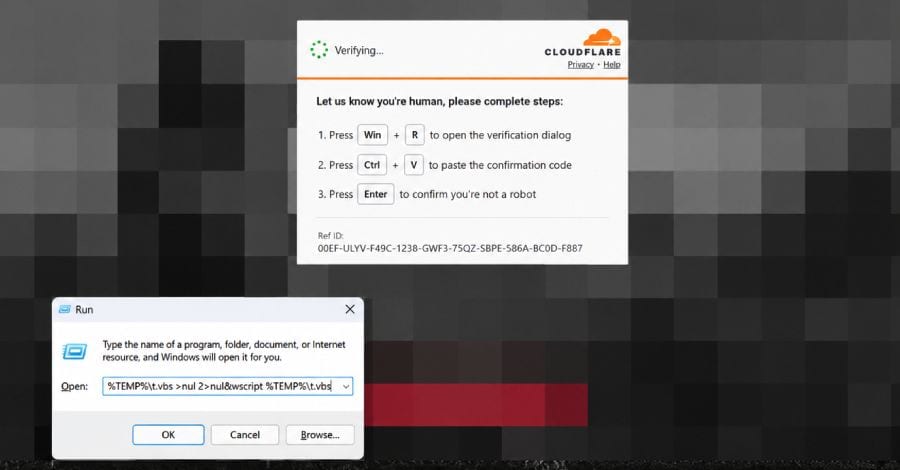
The Hacker News reports that a new ClickFix attack is using compromised websites to trick Windows users into running a malicious payload cached in the browser. The attack hides a script in browser cache, then uses it to fetch more payloads and target browser and device credentials. Windows users should avoid copying and running commands from unexpected sites or pop-ups, and be cautious of fake error, CAPTCHA, or browser update prompts.

The Hacker NewsClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits

Source: thehackernews.com

The Record reports that Ukraine’s largest grocery store chain, ATB, confirmed a cyberattack after hackers posted an extortion demand on its website and claimed they had stolen data from millions of customers. The hackers said the data included names, phone numbers, email and physical addresses, password hashes, and employees’ passport information. People who shopped there should watch for phishing, change reused passwords, and monitor accounts for suspicious activity.

The RecordUkraine grocery chain ATB confirms cyberattack as hackers threaten to leak data

Source: therecord.media

The Hacker News reports that attackers are trying to exploit a now-patched critical flaw in the Realtek Jungle SDK to deploy the Cling botnet. The malware targets routers and DVRs from multiple vendors, so home users and small offices should make sure their router or device firmware is fully updated and check vendor security advisories for fixes.

The Hacker NewsRealtek Jungle SDK Exploit Attempts Deliver Cling Botnet With STUN-Based C2

Source: thehackernews.com

The Hacker News reports that attackers are actively trying to exploit a critical flaw in Rejetto HTTP File Server. The bug can let a remote attacker forge an administrator session cookie and reach remote code execution, and a patch was released in version 3.2.1. Windows users running Rejetto HFS should update right away and avoid exposing unpatched systems to the internet.

The Hacker NewsAttackers Target Rejetto HFS Flaw That Enables Admin Session Forgery and RCE

Source: thehackernews.com

DataBreaches.net reports that the Slate Valley Unified School District in Vermont is responding to a security incident and has refused to pay a ransom demand. Kairos says it has 762 GB of data, including SQL databases with personal and medical information about students and employees. People connected to the district should watch for account and identity misuse and follow any district notices.

DataBreaches.netSlate Valley Unified School District voted not to pay ransom demand; Kairos likely to leak data

Source: databreaches.net

The Register reports that exploitation attempts have already been seen against a critical authentication-bypass bug in Rejetto HTTP File Server that can lead to full admin access and remote code execution. If you use Rejetto HFS, update to v3.2.1 or later, which fixes this and other security flaws.

The RegisterAnthropic's super bug-hunting model Mythos is hardcore good at math, as latest vuln under attack shows

Source: theregister.com

DataBreaches.net reports that Italy’s Data Protection Authority fined IQVIA €7 million after finding that a database of health information on one million patients was not anonymous. The authority said the data could be re-identified, and that the company processed health data without a proper legal basis, did not inform patients adequately, and failed to take adequate security measures. People affected should watch their accounts and be careful with any health-related information tied to them.

DataBreaches.netItaly’s Data Protection Authority fines IQVIA €7 million over data protection breach

Source: databreaches.net

The Hacker News reports that the suspected China-linked group Warlock is still exploiting Microsoft SharePoint vulnerabilities to target organizations in Portuguese- and Spanish-speaking countries. The attacks have hit critical infrastructure, government, and education organizations, so Windows users and small offices running SharePoint should patch and mitigate exposed servers and check for signs of web shells, disabled security tools, or unusual remote connections.

The Hacker NewsWarlock Exploits SharePoint Flaws to Disable Security Tools and Deploy Ransomware

Source: thehackernews.com

DataBreaches.net reports that Italy’s data protection authority fined IQVIA €7 million after finding it had built a database with health information on one million patients from 800 family doctors. The regulator said the data was not anonymous and included identifying details for over 3,300 patients. People affected should watch for any notices about the breach and be careful with accounts tied to their medical information.

DataBreaches.netThe Italian Italy’s Data Protection Authority fines IQVIA €7 million over data protection breach

Source: databreaches.net

5,441 members already hereReading, writing, commenting and voting. 0 verified · 166 joined this year