
How_to_decrypt_files.html virus: what it is and how to recover files
How_to_decrypt_files.html is the name of a ransom note that several different ransomware families have left in encrypted folders, not one virus. Identify the family first, because it decides whether a free decryptor exists; do not pay.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Before you restore backups, a full scan can confirm the program that added .encryptedAES is gone.
Do it yourself · free Remove How_to_decrypt_files.html ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps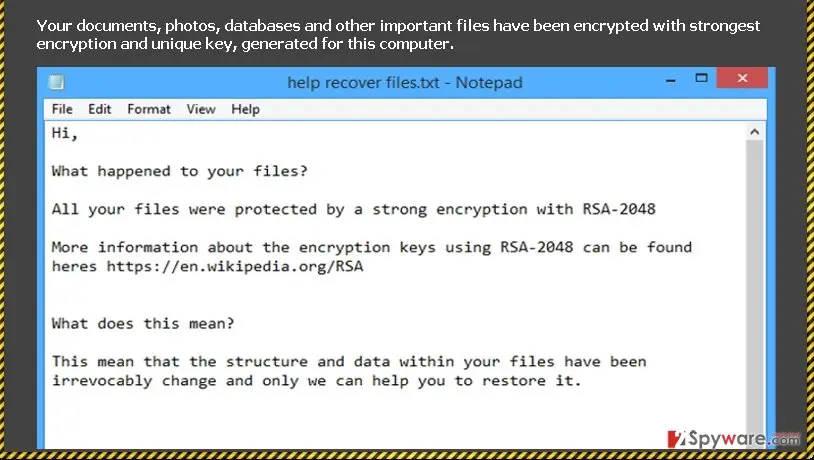
How_to_decrypt_files.html ransomware: summary
| Type | File-encrypting ransomware note; the note name is shared by several families |
|---|---|
| Risk | High: depends on the family, and some have no known decryptor |
| Symptoms | Files renamed (our 2016 report: .encryptedAES), a How_to_decrypt_files.html note in folders, often a .txt note or a wallpaper |
| How to get rid of it | Disconnect, scan offline with Microsoft Defender, then restore from backups; see the plan |
| Our check | Source check on 5 October 2026; no sample, nothing run |
| First seen | Our first report 30 May 2016; the note name was already on BleepingComputer's list |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 12 more facts
| Name | How_to_decrypt_files.html (also written HOW_TO_DECRYPT_FILES.html) |
|---|---|
| Encrypted file extension | .encryptedAES in our 2016 report; other families using the note add other endings |
| Ransom note | Not recorded: neither our 2016 report nor the sources we read quote its text |
| Decryptor | None confirmed for .encryptedAES; depends on the family |
| Contact | Not recorded; some families give an e-mail address, others a Tor page |
| Detection names | No Microsoft detection name is known: the note name belongs to several families |
| Distribution | E-mail attachments, trojans, exploit kits, file sharing sites, exposed remote desktop |
| Damage | Files encrypted and renamed; copies of data and remote access cannot be ruled out |
| Evidence | 0 write-ups by security sites; no sample analysed yet |
| Encrypted files | .encryptedAES |
| Free decryptor | No free decryptor is known (checked 5 October 2026) |
| Facts checked | 5 October 2026 |
Facts checked on 5 October 2026 against BleepingComputer's forum threads, PCrisk's Shifr write-up and Microsoft's HTML smuggling analysis. We have no sample and ran nothing.
What How_to_decrypt_files.html is
How_to_decrypt_files.html is the name of a ransom note, not of one virus: several unrelated ransomware families have dropped a file with this name, so the name alone cannot tell you whether your files can be recovered.
This page keeps what still holds from our 2016 report, corrects the rest, and shows how to find your family.
- What the name is
- A ransom note file, usually an HTML page placed in every folder with encrypted files
- Extension in our 2016 guide
.encryptedAES, which BleepingComputer's moderators listed in 2016 among endings to check- Families known to use the name
- Shifr (PCrisk), Xorist and Samas (BleepingComputer moderator, 2018), a GlobeImposter 2.0 variant (2018 thread)
- Not confirmed
- Which family the 2016 guide described
Which ransomware is yours? Three clues
Identify the family first: a free decryptor exists for some families and for many others nothing does. BleepingComputer's moderators ask every victim for the same clues.
| Clue | Where to find it | Why it matters |
|---|---|---|
| The extension | The end of a renamed file, such as report.docx.encryptedAES | Some families add a fixed ending, others a random one |
| The note | How_to_decrypt_files.html in each folder, plus any .txt note or wallpaper | The name is shared, so its wording and any e-mail or Tor link carry the identity |
| A file marker | A victim ID inside an encrypted file | GlobeImposter 2.0 embeds one, which ID Ransomware uses to recognise it |
- 1
Copy one note and one small encrypted file
Copy, do not move, and keep the originals where they are.
- 2
Upload them to ID Ransomware from a clean device
The service names the family and says whether a decryptor is known.
- 3
Search the No More Ransom tools list
Use the name ID Ransomware returned. Everything on that list is free.
How this note name has been seen
28 April 2016
On a moderator's list
A BleepingComputer thread that month lists HOW_TO_DECRYPT_FILES.HTML among known ransom note names.
30 May 2016
Our first report
We described a file-encrypting virus with this note and
.encryptedAESfiles. A reader asked the same day about a $250 demand.29 October 2018
Another family
A user reported
.[janetcurley]files and this note; moderators identified GlobeImposter 2.0 and said Xorist and Samas use the name too.Later
Shifr
PCrisk describes Shifr, written in Go, which adds
.shifrand drops HOW_TO_DECRYPT_FILES.html.5 October 2026
Our recheck
We found no single family behind the name and rewrote the guide around identification.
What we checked and what we did not
No website is involved and we hold no sample, so this is a check of sources, not a test.
How_to_decrypt_files.html · source check · 5 October 2026
- Note name shared by several familiesShown by BleepingComputer's moderator and PCrisk's Shifr page.
- Shifr has no known decryptorPCrisk states that no tool can decrypt files compromised by Shifr.
- The 2016 familyThe note, extension and picture do not match one family, so we cannot name it.
- Steps on this pageNot tested by us on real infected files.
- Decryptor for `.encryptedAES`We found none.
Depends on the family Until a check names the family, assume the files cannot be decrypted and protect every copy you have.
How How_to_decrypt_files.html ransomware behaves
What the 2016 guide said, and what we can stand behind
Most of the 2016 technical claims were about the note name, not about a family we had tested, so each is marked here.
| 2016 claim | What we found | Verdict |
|---|---|---|
| It uses the RSA algorithm | No source ties RSA to this note name. The picture in our 2016 guide shows a different note, help recover files.txt, that names RSA-2048 | Not confirmed |
It comes with .txt and .bmp files | Many families add a text note or wallpaper beside an HTML note; a 2016 reader also found a .txt file | Plausible, family unknown |
| It belongs to Locky, CryptXXX, zCrypt or TrueCrypter | No source ties the name to them; BleepingComputer's list has _Locky_recover_instructions.txt, a different name | Not confirmed |
It appends .encryptedAES | The ending is on BleepingComputer's 2016 list with no family attached | Not confirmed |
What file-encrypting ransomware does on the PC
These steps describe the general pattern, from PCrisk's ransomware procedure and its Shifr write-up; they are not a recording of your family.
- 1
It looks for files
The 2016 guide said it searches for anything that might matter; ransomware generally goes through user folders, other drives and shares.
- 2
It encrypts and renames
File contents are replaced by encrypted bytes, and most families add an ending such as
.shifror, in our 2016 report,.encryptedAES. - 3
It leaves a note in every folder
PCrisk describes an HTML note for Shifr that points to a Tor website.
- 4
It may remove safety nets
PCrisk lists deleting shadow copies, turning off Defender and spreading to other PCs as common; the sources do not say this note's families do all three.
File types the 2016 guide said were targeted
- Audio
- Video
- Text documents
- Excel sheets
How it reaches PCs
The 2016 guide named three routes; we add what PCrisk and Microsoft list today.
- High
E-mail attachments
The 2016 guide described messages posing as a government office about an invoice, delivery or tax refund, with a
.zipor.docthat ran the virus. - Medium
Trojans and exploit kits
A trojan can bring the encryptor, and exploit kits use flaws in unpatched software.
- Medium
File sharing sites
The 2016 guide named malicious file sharing sites; PCrisk adds fake updaters and cracked software.
- Medium
HTML attachments
Microsoft describes HTML smuggling, where an attached HTML page builds a malware download in the browser.
- Medium
Exposed remote desktop
PCrisk lists remote desktop with a weak password as an entry route.
Notes with similar names
Almost the same note name comes from different families, and instructions for one are useless for another.
| Name | Source | Note |
|---|---|---|
| HOW_TO_DECRYPT_FILES.html (Shifr) | PCrisk | Go-based, adds .shifr, Tor payment page |
| How_to_decrypt_files.html (GlobeImposter 2.0) | BleepingComputer, 2018 | Extension .[name], victim ID in the files |
| How_to_decrypt_files.html (Xorist, Samas) | BleepingComputer, 2018 | Named, not described |
| HOW_TO_DECRYPT_FILES.txt (Hive) | SentinelOne | A text note, not HTML |
Was anything stolen?
We found no evidence either way, so treat the PC as exposed and change passwords from another device.
- Medium
Data may have been copied
PCrisk says modern ransomware often copies data first; a 2016-era family may not have.
- Medium
Remote access
Attackers who came in through remote desktop may still have a way back.
What to do in the first hour
Open the HTML note only in Notepad, because a browser runs the scripts in an HTML file.
- 1
Disconnect
Unplug the cable, turn off Wi-Fi and sign out of cloud storage so encrypted files do not sync over clean ones.
- 2
Unplug drives
Do not plug in a backup drive until the PC is clean.
- 3
Keep the note and one file
Photograph the screen and copy the note and one small encrypted file.
Can How_to_decrypt_files.html ransomware files be decrypted?
Can the files be decrypted?
Only if the family you identified has a free decryptor; renaming files or guessing keys does not work.
The 2016 guide said a private key is needed because the two keys are mathematically linked. That is how public-key schemes work, and it is why only the attackers can undo a family without a flaw.
| Situation | What it means | What to do |
|---|---|---|
| ID Ransomware names a family with a decryptor | The No More Ransom list has a free tool | Run it on copies, as its instructions say |
| No known decryptor (Shifr, per PCrisk) | Nobody can decrypt without the key | Restore from backup and recheck later |
| GlobeImposter 2.0, as the 2018 thread found | ID Ransomware reported no known way then | Back up the encrypted files and recheck |
| Not identified | You cannot know yet | Collect the clues and try again |
- 1
Copy the encrypted files
Work only on copies, on an external drive.
- 2
Remove the malware first
Run an offline scan so that nothing re-encrypts restored files; see the plan.
- 3
PhotoRec and R-Studio
Our 2016 guide named them. They look for deleted files and decrypt nothing, so they help only if the originals were deleted and not overwritten.
Should you pay the ransom?
No. Payment is no promise of a key.
A reader asked us in 2016 about a $250 demand, and PCrisk reports 0.1 Bitcoin, about $120 then, for Shifr.
- High
You may get nothing
PCrisk notes that criminals often ignore victims after payment.
- Medium
Sanctions
PCrisk says paying some groups may be illegal in your country.
How to remove How_to_decrypt_files.html ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove How_to_decrypt_files.html ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so How_to_decrypt_files.html ransomware cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
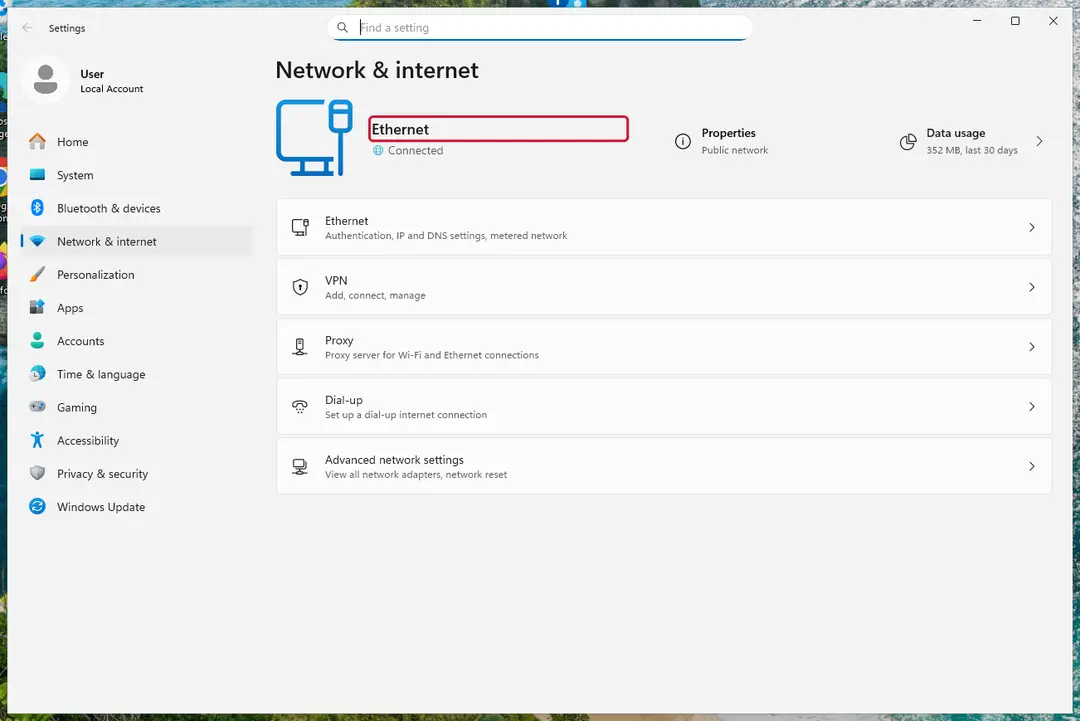
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.encryptedAESand the instructions are inHow_to_decrypt_files.html. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
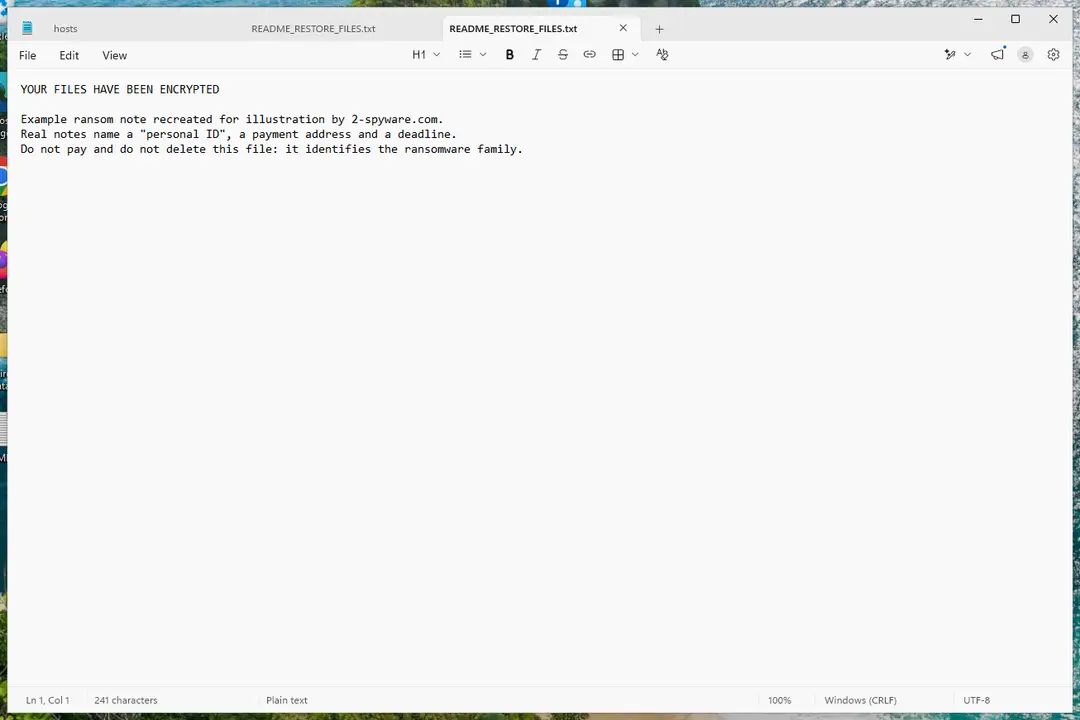
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for How_to_decrypt_files.html ransomware, no free decryptor is known (checked 5 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing How_to_decrypt_files.html ransomware does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
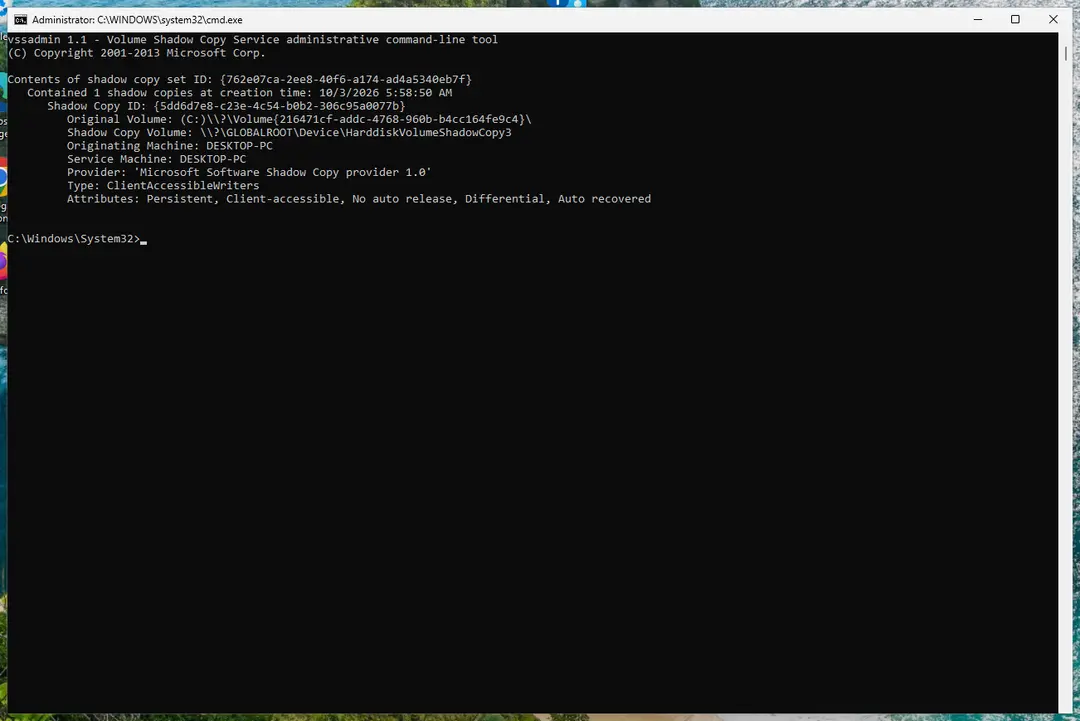
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that How_to_decrypt_files.html ransomware deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Other ways to get files back
Try these in order, before you save anything new to the disk.
- 1
Your backups
A backup from before the attack is the most reliable source; connect it only after the PC is clean.
- 2
Cloud version history
OneDrive, Dropbox and Google Drive keep earlier versions.
- 3
Previous Versions
Right-click the folder, choose Properties > Previous Versions (Windows 11: Show more options first).
- 4
Shadow copies
Run
vssadmin list shadowsin an administrator Command Prompt; many families delete them. - 5
Windows File Recovery
Microsoft's app tries to recover deleted files; it cannot undo encryption.
Back up with the 3-2-1 rule
The 2016 guide advised regular backups on several devices; PCrisk's 3-2-1 rule gives that a shape.
| Number | Rule | Example |
|---|---|---|
| 3 | Three copies | The original and two backups |
| 2 | Two kinds of storage | Your disk and a USB drive |
| 1 | One copy offline | An unplugged drive, or cloud storage with version history |
How to prevent How_to_decrypt_files.html ransomware and the next attack
The 2016 guide closed with updates and careful browsing.
These habits cover the routes above.
Do
- Keep Windows, browsers and apps updated
- Delete unexpected invoice, delivery and tax messages unopened
- Close remote desktop to the internet, or use a long password and two-step sign-in
Don't
- Do not open HTML, ZIP or DOC attachments you did not expect
- Do not run cracks or downloads from file sharing sites
Questions about How_to_decrypt_files.html ransomware
How do I open .encryptedAES files?
You cannot open them directly, because the contents were encrypted and only the right key or a decryptor restores them. Renaming the extension does nothing. BleepingComputer listed .encryptedAES in 2016 as an ending to check, with no family attached.
Copy a file and the note, upload both to ID Ransomware, and search the No More Ransom list for the name it returns. Work on copies only.
Is there a decryptor for How_to_decrypt_files.html ransomware?
There is no single decryptor, because the note name belongs to several families. PCrisk states that nothing can decrypt files compromised by Shifr, and ID Ransomware reported no known way for the 2018 GlobeImposter 2.0 case.
We found no tool for .encryptedAES. Identify the family with a note and one encrypted file, then check the No More Ransom decryption tools list, and keep copies, since tools sometimes appear later for old families.
Should I pay the ransom for How_to_decrypt_files.html?
No, do not pay the ransom. A reader who wrote to us in 2016 was asked for $250, and PCrisk reports 0.1 Bitcoin for Shifr. Payment guarantees nothing:
- PCrisk notes that criminals often ignore victims once paid
- that paying some groups may break sanctions law
- that a payment funds the next attack
Identify the family, check for a free decryptor, and look for backups and shadow copies. Keep the note and one encrypted file in case a tool appears later.
Do paid decryption services or data recovery companies work?
They cannot decrypt a family without a flaw, because the attackers hold the key. A recovery company, or PhotoRec and R-Studio from our 2016 guide, searches the disk for deleted files that were not overwritten.
That helps only if the ransomware deleted originals instead of encrypting them in place, and results are partial. Be wary of anyone who guarantees decryption, and try backups first.
How did How_to_decrypt_files.html get on my PC?
Most likely through an attachment or download you opened. The 2016 guide described e-mails posing as a government office about an invoice, delivery or tax refund, with a ZIP or DOC attachment that ran the virus, and it named trojans, exploit kits and file sharing sites.
PCrisk adds fake updaters and exposed remote desktop, and Microsoft describes HTML attachments that build malware in the browser. Think of the last unusual file you opened before the first renamed file appeared.
Was my data stolen by the How_to_decrypt_files.html ransomware?
We found no evidence either way. PCrisk says modern ransomware often copies data before encrypting, but a 2016-era family may not have, and a note name shared by several families cannot tell you. Treat the PC as exposed:
- change your important passwords from another device
- starting with e-mail and banking
- turn on two-step sign-in
- watch your accounts for sign-in alerts
If the PC holds work data, tell your IT team, because a leak can create reporting duties.
Is How_to_decrypt_files.html the same as Shifr or other ransomware, or different?
The note name is the same, but the families are different. Shifr is written in Go, adds .shifr and sends victims to a Tor page. In 2018 a BleepingComputer moderator said Xorist and Samas also use the name, and a .[janetcurley] case was identified as GlobeImposter 2.0.
Our 2016 guide named Locky, CryptXXX, zCrypt and TrueCrypter, but no source we read ties the name to them. Compare your extension and note wording with an identification service.
Can an HTML file be a virus?
Yes, an HTML file can carry harmful code, although a ransom note is only a message. Microsoft describes HTML smuggling, where an HTML attachment decodes a script in your browser and builds a malware file on your device, used to deliver banking trojans and remote access tools.
Do not open HTML attachments you did not expect. A note called How_to_decrypt_files.html in your folders is a symptom of an infection that already happened, so scan the PC rather than the note.
Can I open or delete How_to_decrypt_files.html?
You can read it safely in Notepad, and deleting it does not harm your files. A browser runs the scripts in an HTML note, so right-click it and choose Open with, then Notepad.
Before you delete it, keep one copy and one encrypted file, because its wording and contact details are how identification services recognise the family. Deleting the note removes neither the malware nor the encryption, so scan the PC offline as well.
Will Fortect remove How_to_decrypt_files.html ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For How_to_decrypt_files.html ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- BleepingComputer forum: have a problem with cryptolocker (note and extension lists) (read October 5, 2026)
- BleepingComputer forum: Ransomware, file ext .[janetcurley], drops How_to_decrypt_files (read October 5, 2026)
- PCrisk: Shifr ransomware, with its ransomware removal and recovery procedure (read October 5, 2026)
- Microsoft Security Blog: HTML smuggling surges (read October 5, 2026)
- Microsoft Support: Windows File Recovery (read October 5, 2026)
- No More Ransom: decryption tools (read October 5, 2026)
- SentinelOne: Hive ransomware (note names) (read October 5, 2026)