
CXK-NMSL ransomware: what it is and how to restore your files
CXK-NMSL ransomware is a Windows batch-file threat that renames your files to .cxk_nmsl, converts them to base64 text and deletes the originals. The files are encoded, not locked with a key, so you can very probably decode copies of them without paying.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Make sure nothing will rename more files to .cxk_nmsl: an automatic scan checks the PC first.
Do it yourself · free Remove CXK-NMSL ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps
CXK-NMSL ransomware: summary
| Type | Batch-file ransomware: renames and base64-encodes files, deletes the originals |
|---|---|
| Risk | Medium: originals are deleted, the encoded copies can very probably be decoded, a hidden program may give remote access |
| Symptoms | Files renamed .cxkdata or .cxk_nmsl, CXK-NMSL-README.txt on the desktop and in folders, a Chinese message box, a new wallpaper, a song playing |
| How to get rid of it | Scan with Microsoft Defender, delete the dropped files, check startup entries and the hosts file, then decode copies of your files; see the plan |
| Our check | Source check on 5 October 2026 (SonicWall, Elastio, No More Ransom); we did not run the malware |
| First seen | 1 July 2019 (Elastio); our first report 7 October 2019 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 12 more facts
| Name | CXK-NMSL ransomware (also ChineseBAT) |
|---|---|
| Encrypted file extension | .cxk_nmsl (and .cxkdata); the content is base64 text, not encrypted |
| Ransom note | CXK-NMSL-README.txt in Chinese, quoted in full below |
| Decryptor | None published and none needed: decode copies with certutil -decode |
| Contact | A private message to a Bilibili account; no e-mail or wallet address |
| Detection names | No Microsoft detection name is known. BitDefender: Trojan.BAT.Ransom.C; Dr.Web: BAT.Encoder.82; SonicWall: Ransom.BatCXK_NMSL |
| Distribution | Not documented; batch files run by the victim, and the routes the 2019 guide listed for ransomware (remote desktop, exploit kits, peer-to-peer sites, spam) |
| Damage | Original files deleted and replaced by base64 text, wallpaper changed, possible remote access |
| Evidence | 0 write-ups by security sites; no sample analysed yet |
| Encrypted files | .cxk_nmsl |
| Free decryptor | No free decryptor is known (checked 5 October 2026) |
| Facts checked | 5 October 2026 |
Facts checked on 5 October 2026 against SonicWall's analysis of version 3.2, Elastio's family page, the No More Ransom tools list and our own 2019 screenshots of the note. We did not run the malware.
What CXK-NMSL ransomware is
CXK-NMSL is ransomware written as Windows batch files: it renames your files, converts them to base64 text and deletes the originals, so the files are encoded rather than locked with a secret key, and its note asks for 100 Bilibili B coins, not Bitcoin.
Our 2019 report said it deletes files because of a bug in its encryption and demanded 100 BTC. Both points were wrong; this page follows SonicWall's technical analysis and Elastio's family tracker.
- Also called
- ChineseBAT ransomware
- Written as
- Windows batch scripts, versions up to
CXK-NMSL V3.2.bat - First seen
- 1 July 2019 (Elastio); our first report 7 October 2019
- Extensions
.cxkdatawhile it works,.cxk_nmslon the finished files- Note
CXK-NMSL-README.txt, in Chinese- Price in the note
- 100 B coins (Bilibili's own in-site currency) and a triple action on 10 videos
How the CXK-NMSL story went
1 July 2019
First seen in the wild
Elastio's family page gives this date for the first sighting and lists the aliases and file names later versions used.
7 October 2019
Our first report
We described a ransom-demanding virus that deletes files because of an error in its encryption code, and put the price at 100 BTC.
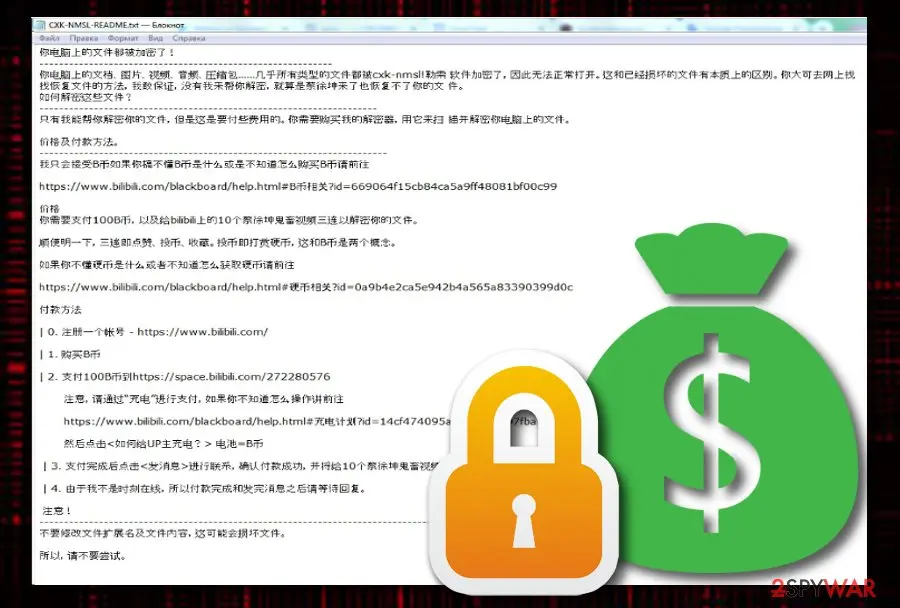
The whole note in our 2019 screenshot: the Bilibili links and the five payment steps are readable (the padlock and money bag are report artwork). 2019 onward
Versions 2.0, 3.1 and 3.2
Elastio lists batch files named
CXK-NMSL V2.0.bat,CXK-NMSL V3.1.batandCXK-NMSL V3.2.bat, plusnyaa.batand anxls.exe. SonicWall later analysed V3.2.5 October 2026
Our recheck
SonicWall's analysis and the tracker show the files are encoded with base64, not encrypted. We rewrote the guide around that.
What we checked and what we did not
We did not run this malware, and no website is involved, so there is no site test; this is a check of sources.
CXK-NMSL ransomware · source check · 5 October 2026
- Ransom note textRead from our own 2019 screenshots of the note in Notepad and translated by us.
- DecryptorThe No More Ransom decryption tools list has no entry for CXK-NMSL or ChineseBAT.
- Decode stepsNot tested by us on real files. They follow from SonicWall's description and Microsoft's certutil documentation.
- 2019 claimsThe hosts file, Task Manager and ExpBoot claims are not in the sources we read; unconfirmed.
Recoverable in principle The originals are deleted, but the encoded copies can very probably be decoded. The risk that remains is the hidden program that may give someone remote access.
- File extension:
.cxk_nmsl - Note file:
CXK-NMSL-README.txt
What antivirus programs call it
Detection names change from week to week, so use them only to confirm that a scan found the right family.
| Who | Name | Where it comes from |
|---|---|---|
| BitDefender | Trojan.BAT.Ransom.C | Our 2019 report |
| Dr.Web | BAT.Encoder.82 | Our 2019 report |
| SonicWall | Ransom.BatCXK_NMSL (Trojan) | SonicWall's post on V3.2 |
| Microsoft Defender | No name known | We found none in public sources |
How CXK-NMSL ransomware behaves
What it does on the PC, step by step
Everything below is from SonicWall's analysis of version 3.2 of the batch file; the earlier versions may differ in detail.
- 1
The batch file starts and lists your files
A
.batfile uses theFORloop of the Windows command line to list files in the folders it targets. - 2
Each file gets the .cxkdata suffix
The listed files are renamed with the
.cxkdatasuffix. - 3
certutil converts the file to base64
The script calls Windows' own
certutil -encodecommand. The result is text made of letters and digits, saved with the.cxk_nmslextension. The original file is then deleted. - 4
A hidden program is unpacked
The batch file carries a base64 copy of a Windows program, decoded with certutil and saved as
X. SonicWall reports that it loadsKrnln.fnrand callsGetNewSock, an API with remote administration abilities. - 5
Wallpaper and message box
A small JavaScript file decodes a zipped
wallpaper.jpg, the registry value for the wallpaper is changed to it, and a VBScript file shows a message box in Chinese. - 6
Note and music
The note
CXK-NMSL-README.txtis written, and at the very end the script drops an MP3 file and plays the song.
Locations SonicWall lists as encoded
- %SystemDrive%\
- %UserProfile%\
- Desktop
- Downloads
- Favorites
- Searches
- Saved Games
- Contacts
- Links
- Videos
- Pictures
- Documents
- Music
Our 2019 report added that it might edit the hosts file and Task Manager entries. Only the wallpaper registry change is documented, so the plan has you check the rest.
What the note demands
The price is partly money and partly an action on a video site, which makes this note unlike most ransomware.
| Item | What the note says | What it means |
|---|---|---|
| Price | 100 B coins and a triple action (like, coin, favorite) on 10 remix videos | B coins are Bilibili's own currency for tipping uploaders, not Bitcoin; the 2019 guide's "100 BTC" was a mistake. |
| Where to pay | The "charge" feature on an uploader's page, then a private message | An ordinary account, so there is no wallet address to trace. |
| Promise | A decryptor you must buy | We found none; the files are base64 text, so decoding needs no key. |
How it reaches PCs
No source we read documents how CXK-NMSL batch files reach their victims.
The 2019 guide listed four general routes for ransomware, which are kept here as possibilities, not as findings.
- Medium
A batch file you ran yourself
The family is a set of
.batfiles such asCXK-NMSL V3.2.batandnyaa.bat(Elastio). A script does nothing until someone opens it. - Medium
Hacked remote desktop
The 2019 guide named remote desktop on TCP port 3389. An exposed one with a weak password lets an attacker run any file.
- Low
Exploit kits
Listed in 2019 for ransomware in general; nothing ties them to this family.
- Medium
Peer-to-peer downloads
The 2019 guide named peer-to-peer sites such as The Pirate Bay.
- Medium
E-mail spam
Unexpected attachments, often pretending to come from FedEx, DHL or another delivery company, as the 2019 guide warned.
Similar names and lookalikes
Several names get mixed up with this one, and the wrong instructions can waste days.
| Name | How it relates | What to do |
|---|---|---|
| CXK-NMSL V2.0, V3.1, V3.2 | Versions of the same batch file | The decode steps apply to the .cxk_nmsl files of any of them, but we only know V3.2 in detail |
| ExpBoot | The 2019 guide passed on a guess that the two are related | Nothing we read confirms it, so do not follow ExpBoot instructions |
STOP/Djvu files (.wwka, .djvu and similar) | Real encryption with keys held by the attacker | Their decryptors will not work on .cxk_nmsl files |
Was anything stolen?
Nothing we read says files were copied out, but the hidden program may give someone remote control, so treat your passwords as exposed.
- Medium
Possible remote access
SonicWall reports that the hidden program calls
GetNewSock, an API with remote administration abilities. Whether it was used is unknown. - Low
No leak site or extortion mail
The note only asks for the payment. Elastio and SonicWall mention no data leak site for this family.
What to do in the first hour
Do not double-click CXK-NMSL-README.txt.exe: Elastio lists a file with that name in every folder, and with file extensions hidden, Windows shows it as a harmless text file.
- 1
Open nothing that came with the note
Leave every
.bat,.vbs,.jsand.exein the affected folders alone. - 2
Photograph the note
Take a photo of the screen and keep
CXK-NMSL-README.txtfor your report. - 3
Disconnect from the network
Unplug the cable or turn off Wi-Fi so that nobody can use the possible remote access while you work.
- 4
Copy the converted files
Copy every
.cxk_nmslfile to a USB drive or a second disk, as the decode chapter explains.
The CXK-NMSL ransomware note
Your files on this computer have all been encrypted!
Your documents, pictures, videos, audio files, archives and almost every other kind of file were encrypted by the cxk-nmsl! ransomware, so they cannot be opened normally. This is fundamentally different from a damaged file. You can search the internet for ways to recover them. I guarantee that without my decryption, not even Cai Xukun himself could restore your files.
How do I decrypt these files?
Only I can decrypt your files, but it costs something. You need to buy my decryptor and use it to scan and decrypt the files on your computer.
Price and payment method
I only accept B coins. If you do not know what B coins are or how to buy them, go to: hxxps://www.bilibili.com/blackboard/help.html#B-coin-help?id=669064f15cb84ca5a9ff48081bf00c99
Price: you must pay 100 B coins, and give a triple action to 10 Cai Xukun remix videos on bilibili, to decrypt your files.
By the way, a triple action means like, coin and favorite. Giving a coin is a tip made with a coin; coins and B coins are two different things.
If you do not know what coins are or how to get them, go to: hxxps://www.bilibili.com/blackboard/help.html#coin-help?id=0a9b4e2ca5e942b4a565a83390399d0c
Payment method
0. Register an account: hxxps://www.bilibili.com/
1. Buy B coins.
2. Pay 100 B coins to the uploader's page at hxxps://space.bilibili.com/[number omitted here]
Note: pay through the "charge" feature. If you do not know how, go to hxxps://www.bilibili.com/blackboard/help.html#charge-plan?id=14cf474095a44dae9a497fba17fa55d7 and click "How to charge an uploader?" (battery = B coin).
3. After paying, click "send message" to contact me, confirm the payment, and send me the screenshots of the triple actions on the 10 videos.
4. I am not online all the time, so after you have paid and sent the message, please wait for a reply.
Attention!
Do not change the extension or the content of the files, this may damage them. So please do not try.
Can CXK-NMSL ransomware files be decrypted?
Can .cxk_nmsl files be restored?
Yes, very probably, and without paying: SonicWall describes the .cxk_nmsl files as base64 text, and base64 is a way of writing bytes as letters that anyone can reverse without a key.
Microsoft's certutil documentation lists -decode as the command that decodes a base64 file, the same tool the batch file uses in the other direction. We could not test it on a real infection, so try one copy first.
| What you see | What it is | Can you get it back? |
|---|---|---|
A file ending .cxk_nmsl | The base64 text of one of your files | Decode it with certutil, steps below |
A file still ending .cxkdata | A renamed original, left when the script stopped before converting it | Copy it and try to open it with the program for the original type |
A file with no .cxk_nmsl twin | The original was deleted and no converted copy exists | Backups, Previous Versions, Windows File Recovery (next chapters) |
- 1
Copy the files first
Copy the
.cxk_nmslfiles to a new folder such asD:\restore. Never decode in the original folder, because it holds your only encoded version. - 2
Look at the file names
A name may end
report.docx.cxk_nmslorreport.docx.cxkdata.cxk_nmsl. The output name must be the original name with its real ending, so check a few files before you decode. - 3
Open Command Prompt in that folder
On Windows 11 and Windows 10, open the folder in File Explorer, click the address bar, type
cmdand press Enter. - 4
Decode one file as a test
Run
certutil -decode "report.docx.cxk_nmsl" "report.docx", then openreport.docx. If it opens, the method works for that file type. - 5
Decode the rest
Run
for %f in (*.cxk_nmsl) do certutil -decode "%f" "%~nf"to decode every file in the folder;%~nfdrops the last ending. If a result still ends in.cxkdata, rename it by removing that ending.
Do
- Remove the malware before you restore, so the files are not converted again
- Check that the decoded files are the right size and open in their programs
Don't
- Do not buy or run any decryptor: the note's "decryptor" does not exist as a product
- Do not delete the
.cxk_nmslfiles until the decoded copies have been backed up
Should you pay the ransom?
No. There is nothing to buy: the note's "decryptor" is not needed for base64 files, and the payment goes to a personal video-site account, not a service that can be held to a promise.
The 2019 guide also told two stories about ransoms in other attacks. They show how mixed the results are, and both are about other malware.
July 2019
New Bedford, Massachusetts
Attackers demanded $5.3 million to unlock the city's computers. The city offered $400,000, and the attackers refused (Tripwire).
August 2019
A dental backup provider
Sodinokibi ransomware hit PerCSoft, which backs up data for dental offices in the United States. Krebs on Security reported that several sources said it paid for the decryptor, which the company never confirmed publicly. The 2019 guide wrote that it agreed to pay; "reportedly paid" is accurate.
- High
You pay a stranger and get nothing
With this note you would also have to message the uploader and send screenshots of actions on ten videos.
How to remove CXK-NMSL ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove CXK-NMSL ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
CXK-NMSL ransomware encrypts everything it can reach, including drives and shares you connect later. Cut the network first: cable out, or Wi-Fi off from the taskbar.
Then unplug every USB stick and backup disk and pause cloud sync, so the encrypted versions do not replace your online copies. Do not reconnect any of them until the ransomware is removed from the Windows 11 or Windows 10 PC.
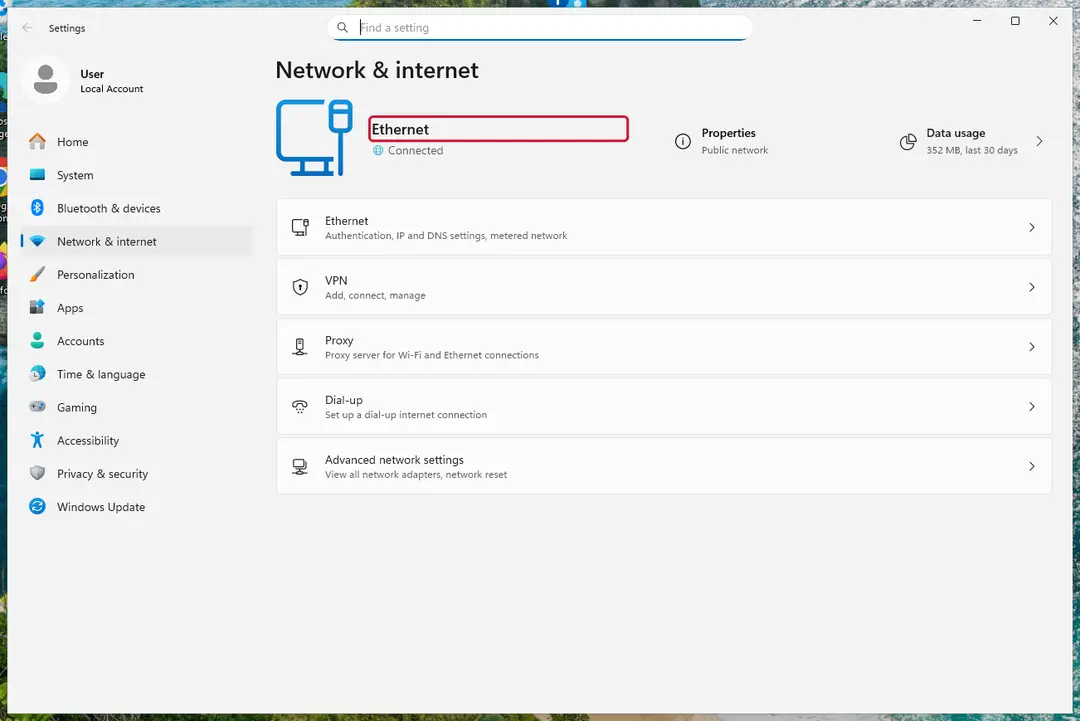
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Copy
CXK-NMSL-README.txtand one or two files ending in.cxk_nmslto a USB stick, and leave the originals where they are.From another device, upload the note and a sample file to ID Ransomware or No More Ransom's Crypto Sheriff, which name the family from the note, the extension and the file structure.
Write down the contact address and your personal ID from the note, because a decryptor or the police may ask for them.
Warning: Never contact the attackers from the infected Windows 11 or Windows 10 PC.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
For CXK-NMSL ransomware, no free decryptor is known (checked 5 October 2026). Search the family name in the No More Ransom decryption tools list and in the free decryptors of Emsisoft, Avast and Kaspersky, because new tools appear years after an attack.
Important: Keep the encrypted files even if nothing works today, and do not pay before every free option is ruled out: payment does not guarantee a working key.
Decryptors run on Windows 11 and Windows 10, but only after the ransomware itself is removed.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Restoring or decrypting files while CXK-NMSL ransomware still runs lets it encrypt them again. Run a Full scan in Windows Security > Virus & threat protection > Scan options, then the Microsoft Defender Antivirus (offline scan).
If the ransomware blocks Windows Security, start Safe Mode with Networking and scan from there. Some families install a password stealer as well, so let both scans finish on Windows 11 or Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Open Command Prompt as administrator and run
vssadmin list shadows. If it lists copies dated before the attack, right-click a folder with encrypted files in File Explorer, choose Properties > Previous Versions, and open or restore a version from before that date.ShadowExplorer, a free tool, shows the same copies when the tab is empty or hidden. Most current families delete shadow copies, so an empty list is normal, but the check takes two minutes on Windows 11 or Windows 10.
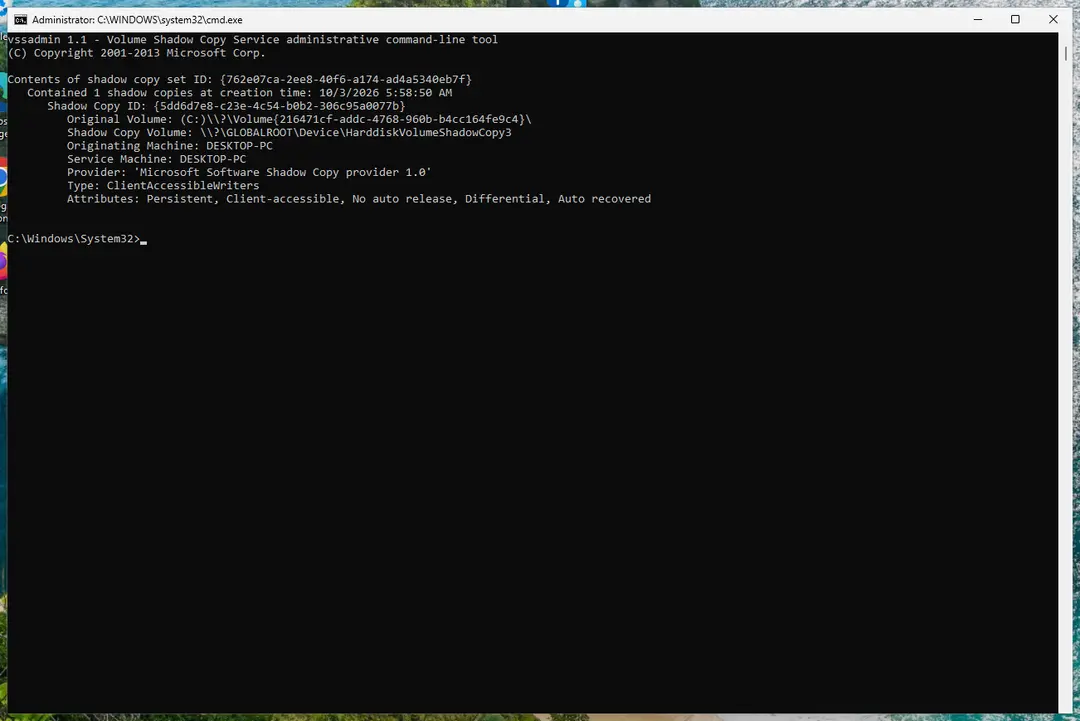
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
Restore from an external backup, File History or OneDrive's version history, choosing a date before the attack. Connect the backup drive only after the scans are clean, or the ransomware encrypts it too.
If there is no backup, file recovery software can sometimes find the deleted originals, because some ransomware writes an encrypted copy and deletes the original file.
Stop writing to the drive and try recovery on Windows 11 or Windows 10 before new files overwrite the space.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
If the decode does not work: other ways to get files back
The deleted originals and anything that was not converted must come from somewhere else.
Check these in order, before you save anything new to the disk.
- 1
Your own backups
A copy on an external drive, a NAS or cloud storage (OneDrive, iCloud, Dropbox) is the most reliable source. Connect it only after the PC is clean.
- 2
Previous Versions
Right-click the folder, choose Properties > Previous Versions (on Windows 11: Show more options first). Pick a date before the attack and copy files out. If System Restore protection was off, nothing is listed.
- 3
Shadow copies
Run
vssadmin list shadowsin an administrator Command Prompt. If copies are listed, a free viewer such as ShadowExplorer can browse them. The sources we read do not say this family deletes them, so check. - 4
Windows File Recovery
Microsoft's
winfrcommand can find deleted files that have not been overwritten, for examplewinfr C: D: /regular /n \Users\<name>\Documents\. On an SSD, deleted data often disappears quickly.
Back up with the 3-2-1 rule
The 2019 guide's advice still holds: keep copies of important files somewhere ransomware cannot reach.
The 3-2-1 rule, which CISA's ransomware guidance recommends, turns it into a plan.
| Number | Rule | Example |
|---|---|---|
| 3 | Three copies of every important file | The working file plus two backups |
| 2 | Two different kinds of storage | Your disk and a USB drive |
| 1 | One copy away from the PC | An unplugged drive in a drawer, or cloud storage with version history |
Do
- Unplug a USB drive after each backup: a connected drive can be converted too
- Keep important documents on a second computer or in cloud storage such as iCloud or Dropbox
- Check once in a while that you can open a file from the backup
Don't
- Do not leave the only backup plugged in all the time
How to prevent CXK-NMSL ransomware and the next attack
Five habits cover how this family and most other ransomware get in.
Do
- Keep Microsoft Defender and Windows updates on, and run a full scan after you open anything unusual
- Sort your e-mail: delete unexpected messages and their attachments, especially fake FedEx or DHL notices
- Close remote desktop (TCP port 3389) to the internet, or protect it with a strong password and two-step sign-in
- Turn on file extensions in File Explorer (View > Show > File name extensions), so a
.txt.execannot pass as a text file
Don't
- Do not run
.bat,.vbsor.jsfiles from chats, forums and archives - Do not install cracks or downloads from peer-to-peer sites
- Do not open attachments from senders you did not expect
Questions about CXK-NMSL ransomware
How do I open .cxk_nmsl and .cxkdata files?
You cannot open .cxk_nmsl files directly, but you can decode them. SonicWall describes them as base64 text made by certutil, which is reversible without a key. Copy a file to a new folder, open Command Prompt there and run certutil -decode with the converted file name first and the original name second.
A .cxkdata file is a renamed original, so try opening it with the program for its real type. We did not test this on a real infection, so try one copy first.
Is there a decryptor for CXK-NMSL ransomware?
No decryptor is published, and none is needed. The No More Ransom tools list has no entry for CXK-NMSL or ChineseBAT, and the 2019 guide also said none existed.
SonicWall's analysis explains why: the batch file encodes files with certutil, and certutil -decode undoes it. Be careful with websites offering a free CXK-NMSL decryptor, since they are a common way to deliver more malware.
Should I pay the CXK-NMSL ransom?
No, do not pay the ransom. The note asks for 100 Bilibili B coins sent to an uploader's page, plus a triple action on ten videos, and then a message.
That payment goes to an ordinary account, nothing obliges anyone to answer, and your files can very probably be decoded for free. Paying also does not remove the hidden program the batch file unpacks. Keep the note and follow the plan instead.
Can a data recovery company or paid service help?
A recovery service can help with deleted files, but not with the converted ones. You can decode the .cxk_nmsl files yourself for free, so a service adds nothing there.
The originals the batch file deleted are a normal disk recovery job: success depends on whether the space was overwritten, and on an SSD it often was. Avoid anyone who guarantees results or offers to negotiate with the attackers, and try backups first.
How did CXK-NMSL get on my PC?
Nobody has documented the delivery for this family, so it was probably a batch file someone opened. The files Elastio lists, such as CXK-NMSL V3.2.bat and nyaa.bat, do nothing until run.
The 2019 guide named hacked remote desktop on port 3389, exploit kits, peer-to-peer sites and e-mail spam as the usual routes for ransomware. Think about which file you opened shortly before the first renamed file appeared, and keep it for the scan.
Was my data stolen by CXK-NMSL?
Nothing we read says it was stolen, but the possibility is not closed. SonicWall reports that the program hidden in the batch file loads an API with remote administration abilities, so someone may have had access.
Neither SonicWall nor Elastio mentions a leak site or a threat to publish files. As a precaution, change your main passwords from a clean device, starting with e-mail and banking.
How is CXK-NMSL different from other ransomware?
It encodes files instead of encrypting them. Ransomware such as STOP/Djvu locks files with keys only the attacker holds, while CXK-NMSL runs certutil -encode and certutil -decode undoes it.
The price is also unusual: B coins on a Chinese video site and actions on ten videos, not a Bitcoin wallet. Do not mix it up with ExpBoot, which the 2019 guide mentioned as a possible relative without proof.
What does the CXK-NMSL-README.txt note say?
It is a Chinese text saying your files were encrypted and offering a decryptor for 100 B coins. It also asks for a triple action on ten videos of a Chinese entertainer, tells you to pay through Bilibili's charge feature and send screenshots by message, and ends by warning you not to change the extensions.
Our translation of the whole note is in the ransom note chapter. It names no e-mail address or wallet.
Why is the ransom in B coins and not Bitcoin?
The attacker chose the currency of one video site that its Chinese-speaking targets already use. A B coin is Bilibili's in-site currency for tipping creators.
The 2019 guide wrote 100 BTC, which was a mistake, because the note says B coins and never Bitcoin. It is still extortion and you should not send anything, but it explains why there is no wallet address to look up.
Will Fortect remove CXK-NMSL ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For CXK-NMSL ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- SonicWall: BAT file based Ransomware targeting people in China (read October 5, 2026)
- Elastio: CXK-NMSL ransomware (read October 5, 2026)
- Microsoft Learn: certutil (read October 5, 2026)
- Microsoft Learn: winfr (Windows File Recovery) (no longer online) (read October 5, 2026)
- No More Ransom: decryption tools (read October 5, 2026)
- CISA: StopRansomware (read October 5, 2026)
- Krebs on Security: Ransomware bites dental data backup firm (read October 5, 2026)
- Tripwire: Ransomware attackers demanded $5.3M from City of New Bedford (read October 5, 2026)