
Vepi ransomware: what it is and how to get your files back
Vepi ransomware is a version of the STOP/Djvu family that encrypts your files, adds .vepi to their names and asks $999 in a note called _README.txt. Whether you can decrypt them depends on the key type: files locked with an offline key the free Emsisoft decryptor knows can be opened, the rest need backups.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Make sure nothing will rename more files to .vepi: an automatic scan checks the PC first.
Do it yourself · free Remove Vepi ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps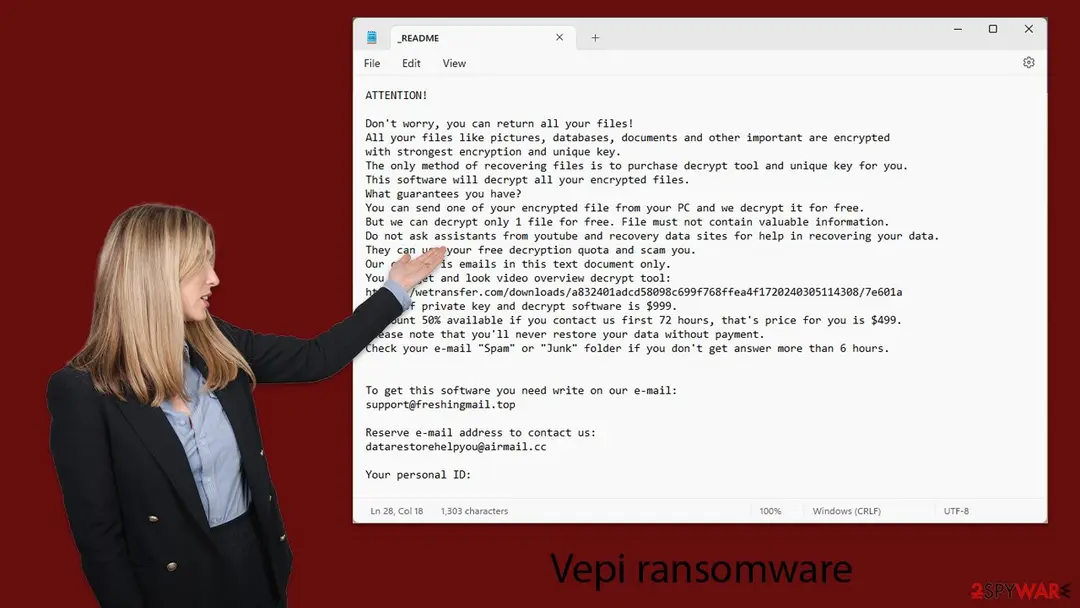
Vepi ransomware: summary
| Type | File-encrypting ransomware of the STOP/Djvu family |
|---|---|
| Risk | High: files are lost unless the key was an offline key Emsisoft has; the installer that brought it may also carry a data stealer |
| Symptoms | Files renamed .vepi, _README.txt in folders, files that no longer open |
| How to get rid of it | Scan in Safe Mode with Microsoft Defender, remove the installer, then try the Emsisoft decryptor and backups; see the plan |
| Our check | Source check on 6 October 2026 (Emsisoft, BleepingComputer, Microsoft, CISA) and our May 2024 screenshots; we did not run the malware |
| First seen | 13 May 2024 (our first report and the VirusTotal sample) |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 15 more facts
| Name | Vepi ransomware (STOP/Djvu) |
|---|---|
| Encrypted file extension | .vepi |
| Ransom note | _README.txt, quoted below |
| Decryptor | Emsisoft STOP Djvu decryptor, only for offline-key files |
| Price in the note | $999, or $499 within 72 hours |
| Contact | Two e-mail addresses in _README.txt; no web page and no wallet address printed here |
| Evidence | 0 write-ups by security sites; no sample analysed yet |
| Encrypted files | .vepi |
| Attacker contacts | support@freshingmail.top |
| Free decryptor | The free Emsisoft STOP Djvu decryptor works only for files locked with an offline key it holds, and we could not confirm a key for .vepi (checked 6 October 2026) |
| Microsoft Defender name | Ransom:Win32/StopCrypt (the Microsoft family name for STOP/Djvu; the exact label for the .vepi sample is not confirmed) |
| Distribution | Typically cracked programs, keygens and game cheats, fake installers, e-mail attachments, and Remote Desktop with weak passwords in small offices |
| Damage | Files on the PC and connected drives encrypted, restore points often deleted, sometimes a password stealer installed as well |
| Detection names | Microsoft: Ransom:Win32/StopCrypt (the Microsoft family name for STOP/Djvu; the exact label for the .vepi sample is not confirmed) |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Emsisoft's STOP Djvu decryptor page and blog post, BleepingComputer's STOP support topic, Microsoft Support and CISA, plus our own May 2024 screenshots. We did not run the malware.
What Vepi ransomware is
Vepi is one of the many four-letter extensions used by the STOP/Djvu ransomware family: it locks documents, photos, videos and databases on Windows, adds .vepi to every name and leaves a ransom note called _README.txt.
- Family
- STOP/Djvu ransomware, the same family as dozens of other four-letter extensions
- Extension
.vepi, soreport.docxbecomesreport.docx.vepi- Note
_README.txt, dropped in each folder that holds locked files- Price in the note
- $999, or $499 if the victim writes within 72 hours
- Contact in the note
- Two e-mail addresses on different mail services; no web page, no chat
- Our first report
- 13 May 2024
- Files that can come back
- Only when they were locked with an offline key that Emsisoft holds
Do not write to the addresses in the note. Its video link changes from copy to copy, and we did not open it.
How the Vepi story went
18 October 2019
Emsisoft publishes the STOP Djvu decryptor
It counted 160 variants and over 116,000 confirmed victims; the tool covered 148 of the 160. Emsisoft's decryptor page still shows version 1.0.0.5 of that date.
13 May 2024
Our first Vepi report
We described
.vepias a new Djvu version. Our VirusTotal screenshot of the sample, a 732 KB file called program.exe, shows 40 of 73 vendors flagging it, among them GData as Win32.Trojan-Ransom.STOP.OXXTM5 and Alibaba as Trojan:Win32/Danabot.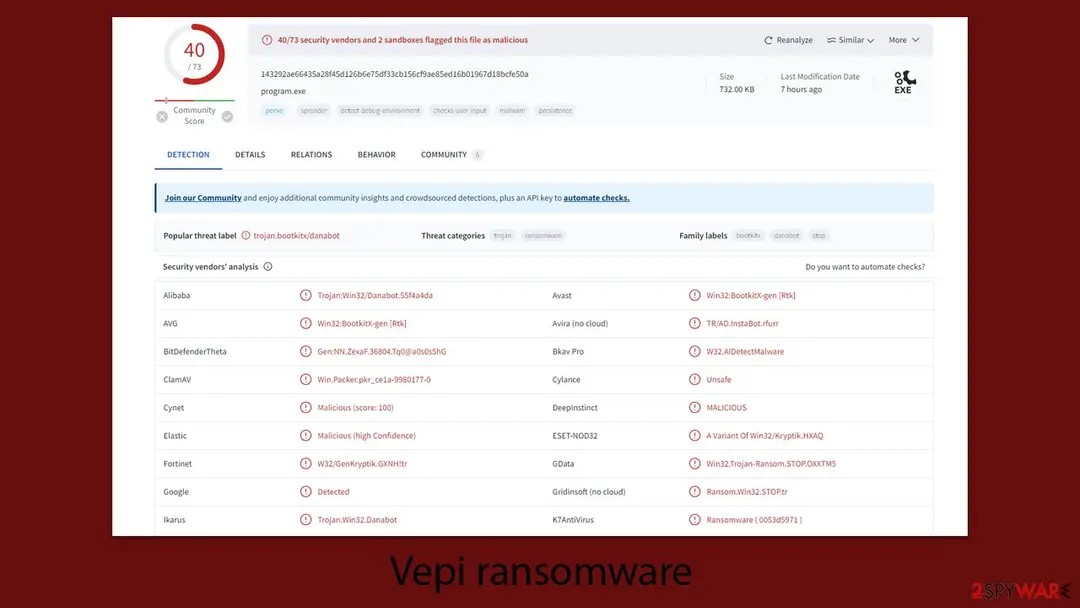
The VirusTotal result for the Vepi sample in our May 2024 report: 40 of 73 vendors, family labels bootkitx, danabot and stop (the title strip underneath is report artwork). 6 October 2026
Our recheck
We found no new public information about
.vepiitself and no new decryptor.
What we checked and what we did not
We did not run this malware and there is no website to test, so this is a check of sources and of our own 2024 screenshots. A quiet check proves nothing about what a file does on your PC.
Vepi ransomware · source check · 6 October 2026
- Family and extensionThe note in our screenshot carries the standard STOP Djvu wording, and the files carry
.vepi. - Detected or hard to detect?On the day of our sample 40 of 73 vendors flagged it. That is wide but not complete; 33 did not, so a clean scan is no proof that a copy of the family is gone.
- Free decryptorEmsisoft's tool opens files locked with an offline key it holds.
- An offline key for .vepi?Not confirmed. Only running the decryptor on your files tells you.
- Microsoft detection nameNone confirmed for
.vepi, no registry or shadow-copy details, so none are listed.
Files probably lost unless the key is offline If your ID does not end in t1, an online key was most likely used and only the attackers hold it. The program that brought the ransomware may also have installed other threats.
- File extension:
.vepi - Note file:
_README.txt - Contact:
support@freshingmail.top
How Vepi ransomware behaves
How the family locks files, in order
Whether your files can be saved is decided in the first seconds, by the kind of key the malware manages to get.
- 1
The installer runs
Emsisoft's October 2019 write-up says STOP spreads almost exclusively through key generators and cracks.
- 2
It calls home for a key
BleepingComputer's support topic says that when the malware reaches its command servers it receives a random key made for this one victim, an online key.
- 3
No connection, built-in key
If the servers cannot be reached, it gives up and uses an offline key that is baked into the program. Everyone who got the same build shares it.
- 4
Files are locked
Emsisoft names the Salsa20 cipher and says files locked by the newer versions grow by 334 bytes. The extension
.vepiis added to each name. - 5
The note is written
_README.txtstates the price, two contact addresses and your personal ID, which you should read before doing anything else.
Online or offline key: read the end of your ID
Open _README.txt and look at the last characters of your personal ID. An ID that ends in t1 is generally an offline ID, and only then has the free Emsisoft decryptor any chance.
| Offline key | Online key | |
|---|---|---|
| How it happens | The malware found no server | The malware reached its server |
| Who shares the key | Every victim with the same build | Nobody, one key per victim |
| Look of the ID | Generally ends in t1 | Does not end in t1 |
| Emsisoft decryptor | Helps only if Emsisoft already holds this key | Cannot help, the key lives with the attackers |
| What the tool prints | "decryption MAY be possible in the future" | "this ID appears to be an online ID. decryption is impossible" |
Our 2024 guide named RSA as the cipher; Emsisoft names Salsa20 for the files, and the sources we read do not mention RSA, so we corrected it. The old text was right on one point that matters: files locked after 29 August 2019 can no longer be opened by sending file pairs to Emsisoft, which only works for the old Djvu versions.
What it does to the PC besides locking files
Our 2024 guide said that installation can wreck system files and even pose as a Windows update. The public record for .vepi is thin, so we sorted those claims by what we could back.
Vepi ransomware · behaviour claims · 6 October 2026
- Locks non-system files, adds `.vepi`Shown in our 2024 note screenshot and in Emsisoft's description of the family.
- Crashes, errors, damaged system filesFrom our 2024 guide. We found no test showing it for
.vepi; if Windows misbehaves after the scan, the plan's repair steps (SFC and DISM) cover it. - Fake Windows update screenFrom our 2024 guide. Not confirmed in any source we read for this extension. If you see an update window you did not start, treat it as part of the infection.
- Data-stealing trojans arrive with itPlausible: engines in our VirusTotal screenshot name Danabot, a trojan that steals data, and Emsisoft says some STOP versions bundle password stealers.
- Shadow copies deletedCommon in ransomware, but we have no source for
.vepi. Check Previous Versions rather than assume.
Behaviour beyond the locking is not confirmed Treat the PC as untrusted until it has been scanned in Safe Mode: whatever came with the installer may still be running.
How it reaches PCs
The documented route is software that was not paid for: cracks, key generators and activators.
- High
Cracks, keygens and activators
Emsisoft says STOP spreads almost exclusively through key generators and cracks. BleepingComputer adds adware bundles, pirated software, activators for Office and Windows, and shady sites.
- Medium
Other malware that came first
Our 2024 guide said Vepi often arrives with trojans and data stealers. The Danabot labels in our VirusTotal screenshot fit that, but one screenshot is not a chain of events.
- Low
E-mail attachments
Our 2024 guide listed a corrupted attachment as the typical case. Neither Emsisoft nor BleepingComputer names e-mail for this family, so we class it as possible and unproven.
What to do in the first hour
- 1
Stop and disconnect
Close the installer or crack, do not start it again, and unplug the cable or switch off Wi-Fi so nothing more is sent out or locked on shared drives.
- 2
Keep the note and copy the locked files
Photograph the screen and keep
_README.txt. Copy the.vepifiles to a USB or external drive before the scan, so a mistake in removal cannot lose them for good, then unplug that drive. - 3
Do not write to the attackers
The free test file is the start of a bargaining script: they ask for your ID and a file, then name the price.
- 4
Report it
In the US, CISA's guide lists cisa.gov/report, your local FBI field office and the FBI's IC3 at ic3.gov. Elsewhere, use your national police or cybercrime service.
The Vepi ransomware note
The wording as reported: a ransom note left in folders
ATTENTION!
Don't worry, you can return all your files!
All your files like pictures, databases, documents and other important are encrypted with strongest encryption and unique key.
The only method of recovering files is to purchase decrypt tool and unique key for you.
This software will decrypt all your encrypted files.
What guarantees you have?
You can send one of your encrypted file from your PC and we decrypt it for free.
But we can decrypt only 1 file for free. File must not contain valuable information.
You can get and look video overview decrypt tool:
hxxps://we.tl/t-FCWSCsjEWS
Price of private key and decrypt software is $999.
Discount 50% available if you contact us first 72 hours, that's price for you is $499.
Please note that you'll never restore your data without payment.
Check your e-mail "Spam" or "Junk" folder if you don't get answer more than 6 hours.
To get this software you need write on our e-mail:
support@freshingmail.top
Reserve e-mail address to contact us:
datarestorehelpyou@airmail.cc
Your personal ID:
The _README.txt note: what it says and what is true
The note is written to sound calm and businesslike. Every promise in it is something only the attackers can confirm, and each one has a purpose.
Vepi ransomware · the note's claims · 6 October 2026
- "Don't worry, you can return all your files!"The first line is reassurance. Whether files can be recovered depends on the key type, not on the attackers' goodwill.
- "We decrypt one file for free"A single test file shows that they hold a key for you. It says nothing about the rest, and it opens a conversation in which they ask for your ID.
- $999, or $499 in 72 hoursThe deadline is a pressure tool; no currency is named in the note we read, so the 'Bitcoin' of our 2024 guide is not confirmed.
- "You'll never restore your data without payment"False in two cases: a backup, and an offline key that Emsisoft has.
- Where it sitsA plain text file in each folder with locked files, not an image or web page as the old guide said of the family in general.
A pressure script, not an offer Do not reply, do not send your ID and do not send a file. Keep the note and a photo of the screen for the police report.
Can Vepi ransomware files be decrypted?
Can .vepi files be decrypted?
Sometimes: only with Emsisoft's STOP Djvu decryptor, and only if your files were locked with an offline key it holds. Files with an online key are out of reach for everyone but the attackers.
Our 2024 guide said Emsisoft's tool works "for a limited number of victims". That holds. It also hoped for tools released after arrests and server seizures; for STOP Djvu we found no report of that, so treat it as a hope, not a plan.
| What the tool says | What it means | What to do |
|---|---|---|
| Files are listed as decrypted | Offline key that Emsisoft holds | Open a few files, then copy them to a clean drive |
| "No key for New Variant offline ID" | Offline ID, key not known yet | Keep the locked copies and try again later; there is no timetable |
| "this ID appears to be an online ID" | Online key | The tool cannot help; use backups |
- 1
Clean the PC, work on copies
Finish the scan in the removal plan first. Then copy a few
.vepifiles and one_README.txtto a USB drive and note how your ID ends. Send the ID to nobody. - 2
Download from Emsisoft only
Use the emsisoft.com page in our sources and press Download. When the pop-up at the bottom of the browser shows
decrypt_STOPDjvu.exe, click it. - 3
Accept the prompts, press Decrypt
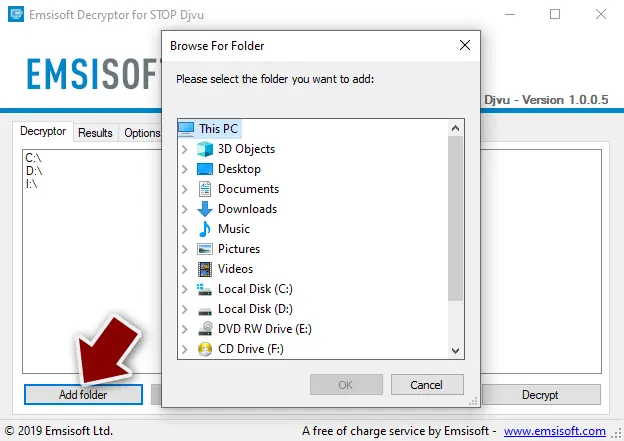
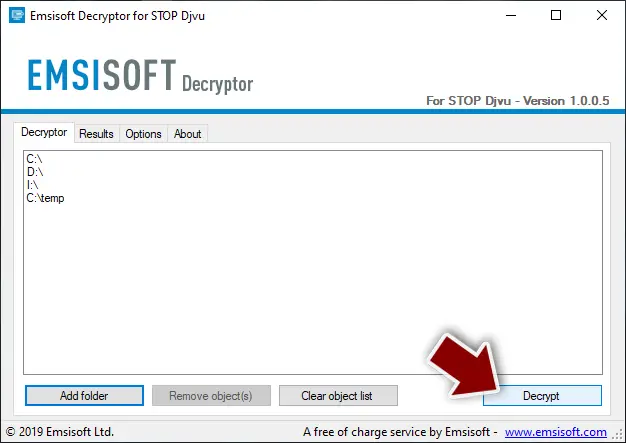
Answer Yes to User Account Control and the License Terms, OK to the Disclaimer. The tool lists your drives; Add folder adds others. It needs the internet to ask Emsisoft's server for the key; compare its message with the table above.
Do
- Keep the locked files even if the tool fails today
- Make sure decrypted files open before deleting the locked ones
Don't
- Do not buy a "decryptor" from anyone, the note's authors included
Should you pay the ransom?
No. The note asks $999, or $499 within 72 hours, and our 2024 guide expected the payment in Bitcoin. The note we read names no currency, and no source we read says that paying works reliably.
- High
You pay and get nothing
Nothing binds the authors to their word, and a payment cannot be taken back.
- Medium
The 72-hour discount is pressure
Half price only if you write within three days. The clock exists to hurry you.
Our 2024 guide said there is no certainty that the attackers keep their promises after payment, and that paying is not recommended. We agree and add the reason: without the key type in your ID, nobody can tell you whether a purchased tool would even exist for your files.
How to remove Vepi ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Vepi ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so Vepi ransomware cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
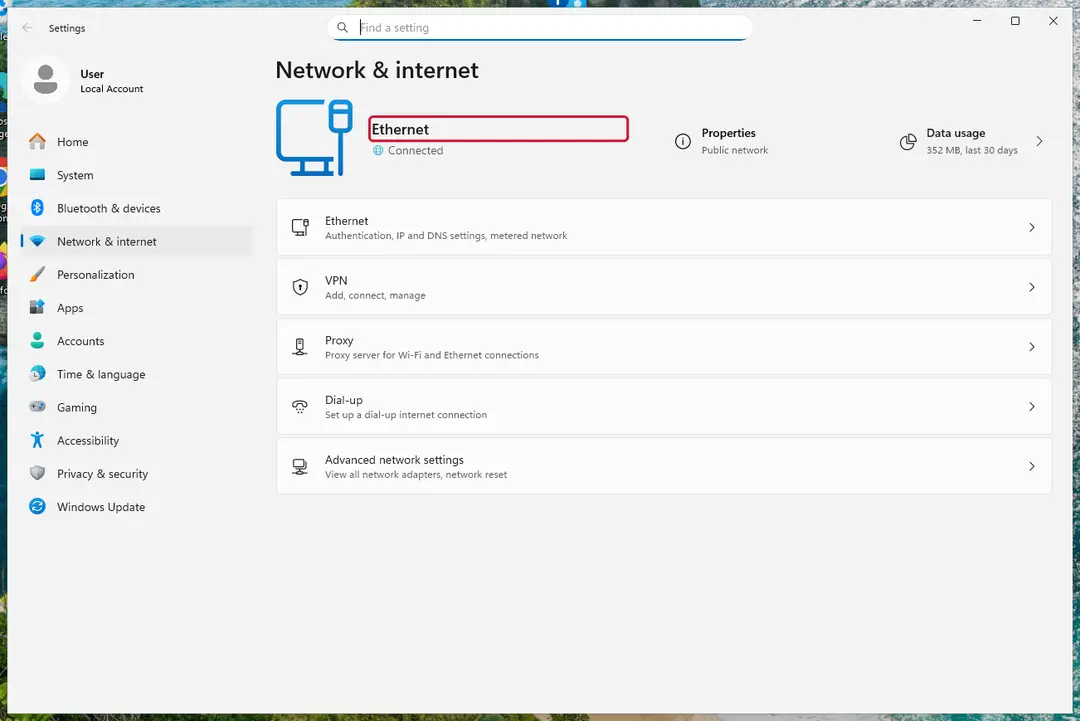
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.vepiand the instructions are in_README.txt. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for Vepi ransomware, the free Emsisoft STOP Djvu decryptor works only for files locked with an offline key it holds, and we could not confirm a key for .vepi (checked 6 October 2026).
Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing Vepi ransomware does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
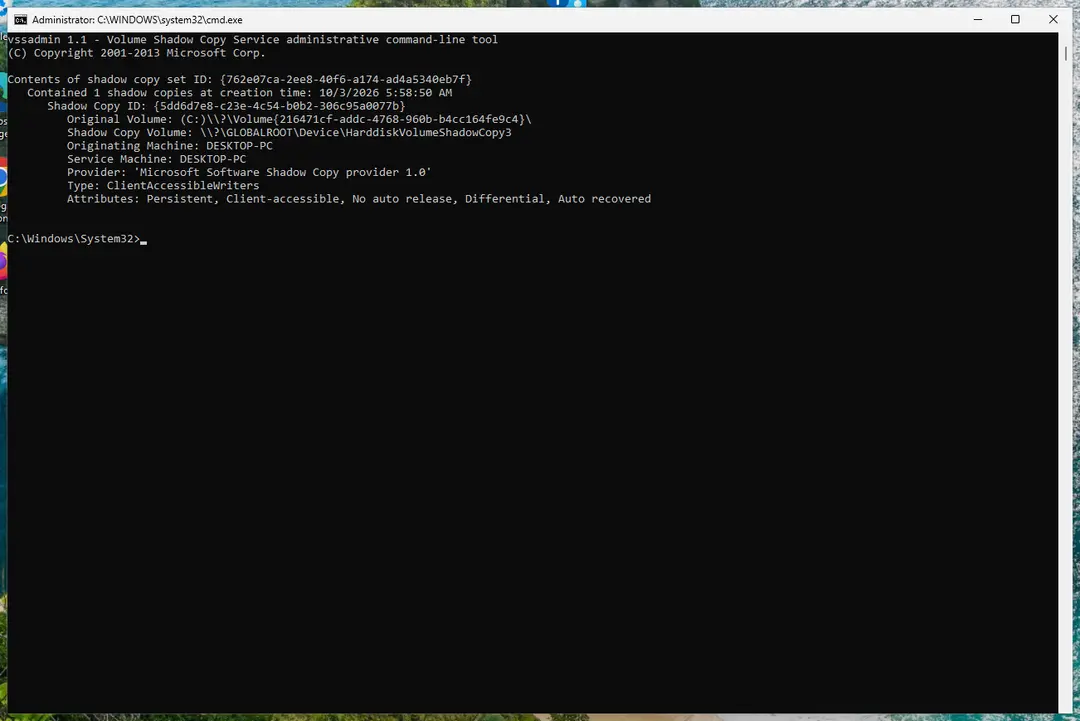
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that Vepi ransomware deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Other ways to get files back
Removing the ransomware and recovering files are two separate jobs: a scan clears the malware but does not turn .vepi files back into documents.
Once the PC is clean, try these in order and before saving anything new to the disk.
- 1
Your own backups
An external drive, a NAS or cloud storage (OneDrive, iCloud, Dropbox) is the most reliable source. Plug it in only after the PC is clean. Our 2024 guide put it first as well.
- 2
Previous Versions
Right-click the folder and choose Restore previous versions (on Windows 11 you may need Show more options first), pick a date before the attack and copy files out. If the malware deleted the copies, this finds nothing; restore one file to find out.
- 3
Windows File Recovery
Microsoft's
winfrcan find deleted files that were not overwritten, for examplewinfr C: E: /regular /n \Users\<name>\Documents\with E: on a different drive. It does not decrypt anything. - 4
A file recovery program
Our 2024 guide suggested one by name; we do not name it. Whatever you pick: install it on a drive other than the one you are scanning, choose Everything or single folders, switch on the deep scan for the disks, press Scan, tick what you need and recover to another drive.
- 5
Reinstalling Windows
Wipes the malware, but also what is on the drive, and brings no
.vepifile back. Do it only after the locked files sit on a drive you have unplugged. - 6
Keep the locked copies
With an offline ID, retry the decryptor after a few weeks.
Back up with the 3-2-1 rule
CISA's ransomware guide says to keep backups offline, because many variants look for backups they can reach and delete or encrypt them.
| Number | Rule | Example |
|---|---|---|
| 3 | Three copies of what matters | The file and two backups |
| 2 | Two kinds of storage | Your disk and a USB drive |
| 1 | One copy away from the PC | An unplugged drive, or cloud storage with version history |
How to prevent Vepi ransomware and the next attack
Our 2024 guide closed with backups, secured accounts and a report to the authorities.
The documented route points at one habit above the others.
Do
- Buy the software, or use a free alternative that is open about its licence
- Keep Microsoft Defender and Windows updates switched on
- Show file extensions in File Explorer (View > Show > File name extensions)
- Change passwords for mail and banking from a clean device, and turn on two-step sign-in
- Keep an offline backup
Don't
- Do not download cracks, keygens, activators or cheats
- Do not switch off antivirus because an installer asks you to
- Do not open attachments from senders you do not know
Questions about Vepi ransomware
How do I open .vepi files?
You cannot open .vepi files normally, because their content is encrypted. They open again only if the free Emsisoft STOP Djvu decryptor has the key for your files. Read your personal ID at the bottom of _README.txt: an ID that ends in t1 is generally an offline ID, which many victims share and which Emsisoft may hold.
An ID that does not end in t1 means an online key that only the attackers have. Deleting the .vepi part of the name does nothing, because the data inside stays locked.
Is there a free Vepi decryptor?
There is a free STOP Djvu decryptor from Emsisoft, but it is built for the whole family and works only for files locked with an offline key it already holds. We could not confirm that a key exists for .vepi.
Download it only from the emsisoft.com page in our sources, because fake decryptor sites are a common trap. The page still shows version 1.0.0.5 of October 2019. Do not buy a decryptor from anyone, including the addresses in the note.
Should I pay the Vepi ransom?
No, do not pay the ransom. The note asks $999, or $499 if you write within 72 hours, and offers to decrypt one file for free. Nothing binds the attackers to their promise, the timer is there to hurry you, and a payment cannot be taken back.
It also does not tell you whether your files were locked with an online key. Keep the note, copy the locked files to a drive you then unplug, run the scan in our plan and check the decryptor and your backups instead.
How did Vepi get on my PC?
Most likely through a crack, key generator or pirated installer for paid software. Emsisoft says STOP is spread almost exclusively through key generators and cracks, and BleepingComputer adds adware bundles, activators for Office and Windows, and shady sites.
Our 2024 guide also named a corrupted mail attachment, but no source we read ties e-mail to this family. Think back to what you downloaded just before the files stopped opening, and do not run it again. Scan the PC before you sign in to anything from it.
Will my passwords be stolen?
They might be. Emsisoft says some versions of STOP bundle password-stealing trojans, and our VirusTotal screenshot shows engines naming Danabot, a data-stealing trojan, for the Vepi sample. We have no proof about the copy on your PC.
Change your important passwords, starting with e-mail and banking, from a clean device, and turn on two-step sign-in so that a stolen password is not enough. Then scan the infected PC as described in the plan before you use it for anything sensitive.
Is Vepi different from .djvu and other STOP extensions?
Not in how it works, only in the extension and the keys it uses. Vepi and older extensions such as .djvu, .rumba, .radman and .gero belong to the same family, so the same kind of note and the same decryptor apply.
What differs is the key. Old Djvu versions allowed submitting file pairs to Emsisoft, while versions after August 2019 do not. The ID in your own note decides what is possible, not the name of the extension.
Do paid decryption or data recovery services work on .vepi files?
Not on files locked with an online key. A recovery service can bring back a file that was deleted and not overwritten, but it cannot decrypt a locked one, and STOP usually writes the locked data over the original.
A service that promises to decrypt online-key files is almost certainly paying the attackers or is a scam, so ask where the key comes from before you hand over money. Try Previous Versions and Windows File Recovery first; they cost nothing.
Will Fortect remove Vepi ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Vepi ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Emsisoft: STOP Djvu decryptor (read October 6, 2026)
- Emsisoft: Emsisoft releases new decryptor for STOP Djvu ransomware (read October 6, 2026)
- BleepingComputer: STOP Ransomware (.STOP .Djvu, .Puma, .Promo) support topic (read October 6, 2026)
- Microsoft Support: Windows File Recovery (read October 6, 2026)
- Microsoft Support: Start your PC in safe mode in Windows (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- CISA: #StopRansomware Guide (read October 6, 2026)