
Win32:Adware ads: what it is and how to remove it
Win32:Adware-gen is a potentially unwanted program detected by Avast that spreads through software bundling. It displays invasive ads and may install additional questionable software.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like Win32:Adware usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove Win32:Adware ads yourself 4 steps, about 12 minutes, no software needed.
Start the steps
Win32:Adware ads: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | Win32:Adware |
| Type | Adware extension |
| Symptoms | An unknown program in Installed apps |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 4 more facts
| Evidence | 4 write-ups by security sites; details still limited |
|---|---|
| Program | Win32:Adware |
| First seen | 16 August 2021 |
| Facts checked | 5 October 2026 |
Is Win32:Adware ads dangerous?
What readers reported about Win32:Adware
My laptop affected with VirTool: Win32/DefenderTamperingRestore. My laptop affected with VirTool: Win32/DefenderTamperingRestore. Help me
What is this C:UsersdadDesktopsqlite-dll-win32-x.zip folder?. C:UsersdadDesktopsqlite-dll-win32-x.zip Why is this folder sitting on my deaktop when I did nothing connected to it?
removal of Clock.Win32.ransomware virus. Is deleting it with anti-virus sufficient?
From the comments under our earlier guide; names and contact details removed.
From our report of Aug 2021 · outdated details corrected in October 2026
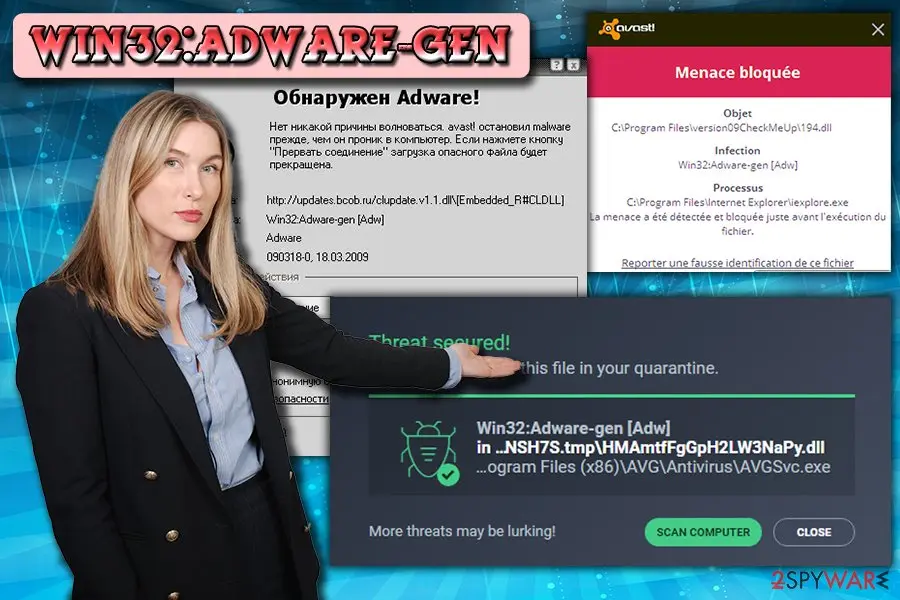
Win32:Adware-gen is the detection name that indicates a PUP-type intruder running on the system
The adware program typically enters computers using software bundling - a technique which allows developers to hide unwanted applications within Recommended or Quick installation settings of legitimate program installers.
The PUP is capable of executing several changes to the targeted machine and may attempt to install additional questionable software.
Win32:Adware-gen virus attacks all installed browsers, including Google Chrome, Microsoft Edge, Safari, Mozilla Firefox, etc. However, adware is a sneaky application that might be not noticed by users at the start, especially if they never saw PUP in action before.
There might not even be a process in the task manager (or it might hide under a legitimate name), neither high activity that would indicate the infection. Nevertheless, users soon notice an increased amount of intrusive ads (in the form of pop-ups, video-ads, in-text links, banners, offers, deals, etc.), obnoxious redirects and, in some cases, a slowdown of the browser or/and the computer.
As soon as it is apparent that a suspicious application is interrupting normal browsing activities, users should start thinking about the threat removal. As this application is quite tricky to detect, we suggest using or for prompt elimination of the PUP. If you do not want to install additional software, however, you can make use of our illustrated guide below.
Another very distinctive feature of Adware-gen is the installation of additional components without permission. The installed unwanted programs may include:
Most of these apps are completely useless and only clutter the machine. The biggest problem is that the more unwanted programs are installed, the more significant is the possibility of severe malware infection.
Generally, adware is legal software that is created to display advertisements to users. However, the tunnel of redirects and accidental clicks on malicious pop-ups might not only infect a machine with other viruses but also steal sensitive information, including name, address, credentials, or even bank details.
Security experts also observed Win32 Adware gen gathering search data, IP address, links clicked, websites visited, and other non-personally identifiable information. This allows developers to research the target's interests and control his/her browsing habits by displaying sponsored content.
Without any doubt, you should remove the virus, as this piece of software, will not only annoy you to death with ads but may also expose your PC to malware infections, as well as snatch your personal information without you even noticing. Identity fraud is a serious problem, and you should do everything to avoid it.
- Toolbars;
- Search engines;
- Add-ons;
- Browser hijackers;
- System optimizers;
- Codec packs, etc.
From our report of Aug 2021 · not reviewed since
Insecure installations of freeware can result in adware-type infection
There is probably no person in the world who would like to see invasive ads deliberately, every day.
Adverts are the plague of the current time, as an average person is exposed to about 5000 ads a day. There is nothing wrong with marketing techniques, but we believe that tricking users into installing software that can harm your PC or even steal sensitive information is not a right thing to do.
Adware and other PUP developers do precisely that. They use software bundling to inject unwanted programs into as many PCs as possible. Unfortunately, the only way to protect yourself from these unwanted programs is to be attentive during the installation process of the application, even if it is a simple 3D screensaver.
Any free software can contain search engines, toolbars, and other useless apps within its installers. Thus, take a good look at what are you clicking - pick Advanced or Custom settings, so that all the additional components could be eliminated before the installation of the desired software is complete.
From our report of Aug 2021 · not reviewed since
More from our earlier report on Win32:Adware
- Win32 Adware-gen is a name under which Avast security software detects this potentially unwanted program.
- Malware infection and exposed personal data
- Google Chrome, MS Edge, Internet Explorer, Safari, Mozilla Firefox, etc.
- Invasive ads in various forms, redirects, slowdown of the browser or/and PC
- Control the virus damage with that can find and fix affected parts
How to remove Win32:Adware ads
How to remove the Win32:Adware extension
Do the browser steps in every browser and profile on the PC, then check Windows for the program that installed the extension.
Step 1: Remove extensions you did not add
Win32:Adware often works through an extension, so go through the extension list of each browser:
chrome://extensionsedge://extensions- Extensions and themes in Firefox
Switch suspicious extensions off one at a time and reload the page where the problem shows, then remove the one that stops it, and any other you did not add.
Remember the other browsers and profiles on the PC. If Remove is missing or greyed out, a policy forces the extension, which the policy step deals with. Windows 11 and Windows 10 show the same pages.
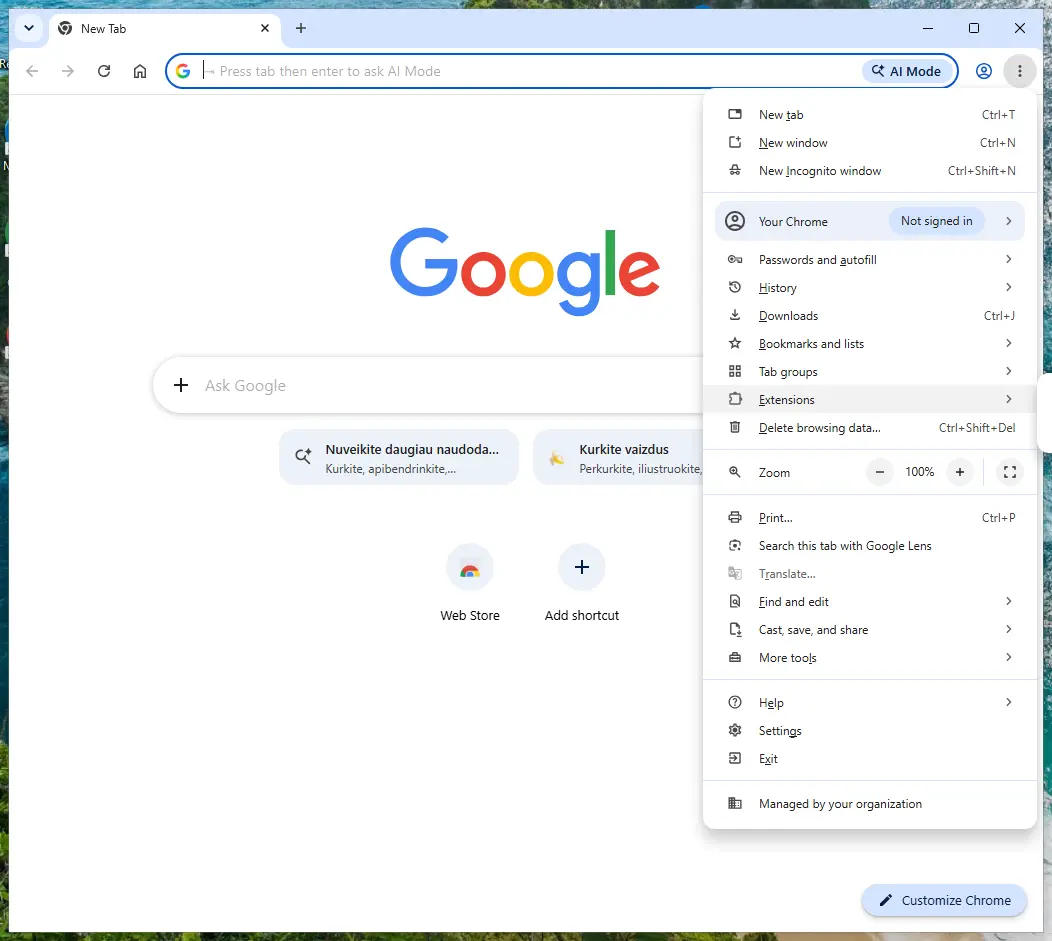
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Uninstall Win32:Adware
Open Settings > Apps > Installed apps in Windows 11, or Settings > Apps > Apps & features in Windows 10. Sort the list by install date and find Win32:Adware, then choose Uninstall from the three-dot menu next to it (in Windows 10, click the entry and then Uninstall).
Remove anything else installed on the same day that you do not recognise, because such programs usually arrive together in one installer. If the uninstaller opens a browser page with an offer or a survey, close it: the program is removed either way.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 3: Reset the browser
Finish the browser part with a reset, which puts the search engine, start page, new tab page and site permissions back to their defaults and switches extensions off. Chrome: Settings > Reset settings > Restore settings to their original defaults.
Edge: Settings > Reset settings. Firefox: Help > More troubleshooting information > Refresh Firefox, which also removes its extensions. Your bookmarks and saved passwords are kept, and the menus are the same on Windows 11 and Windows 10.
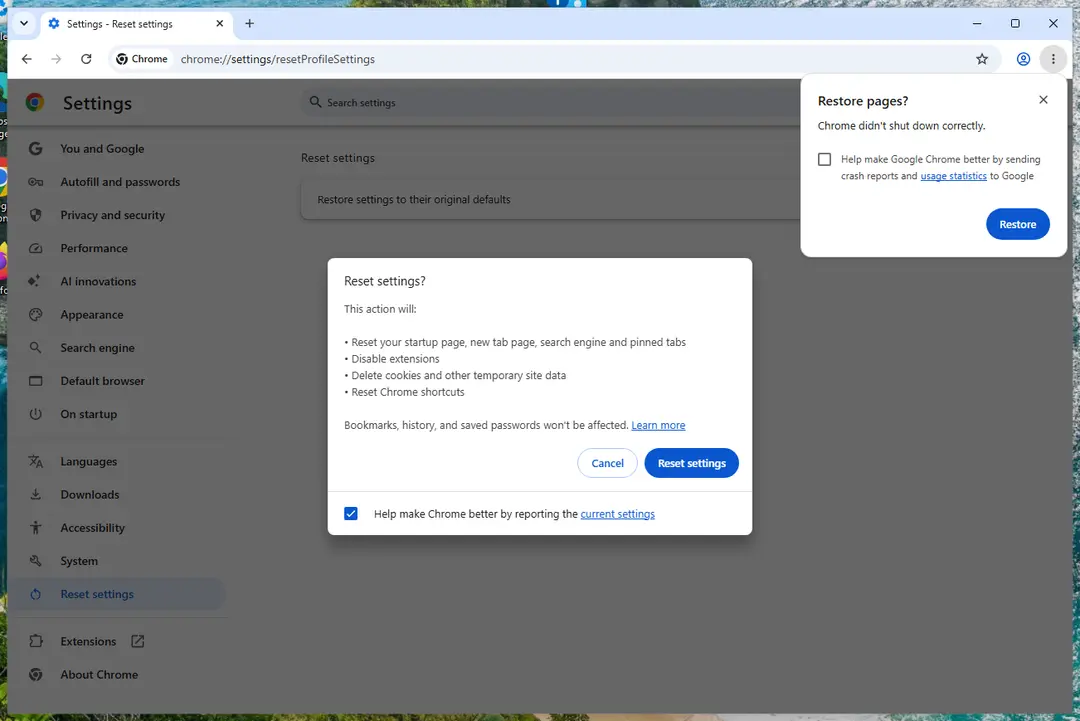
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
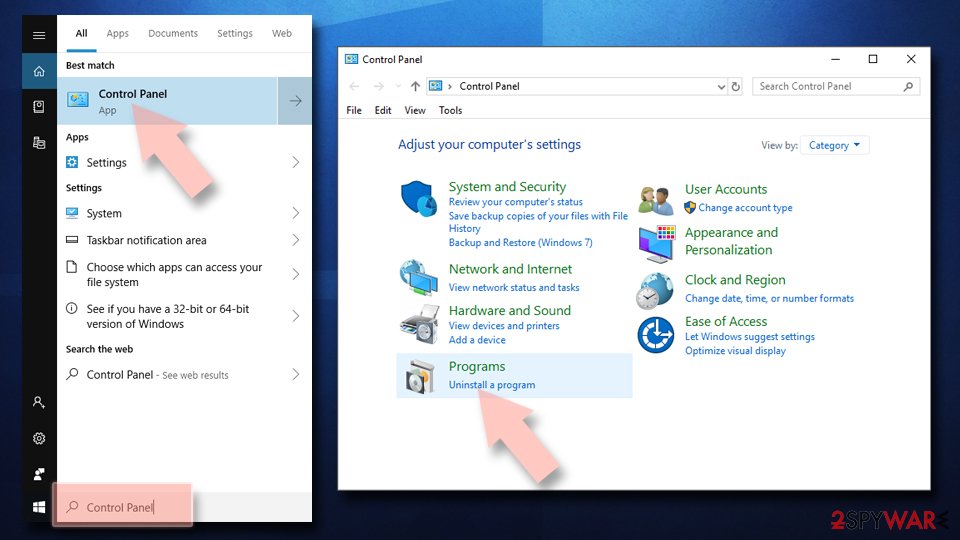
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
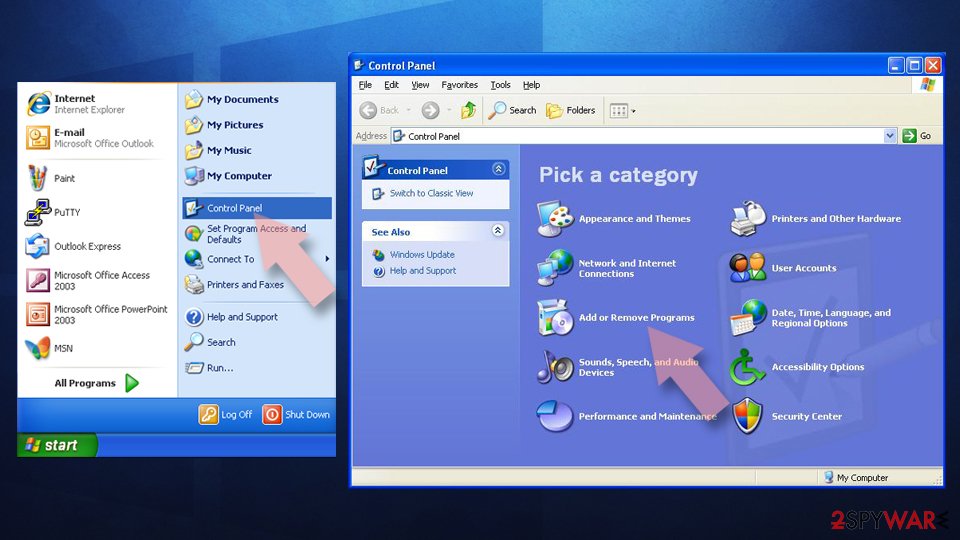
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
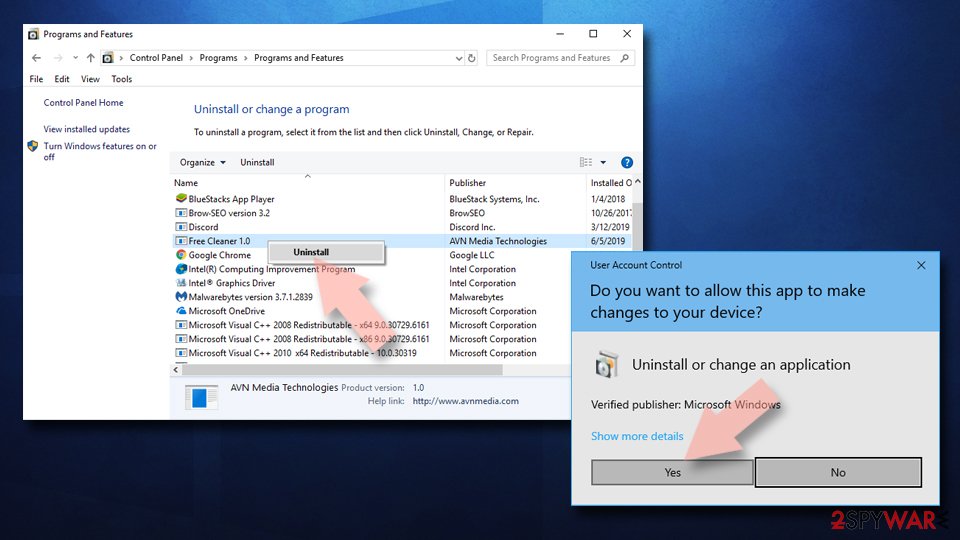
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
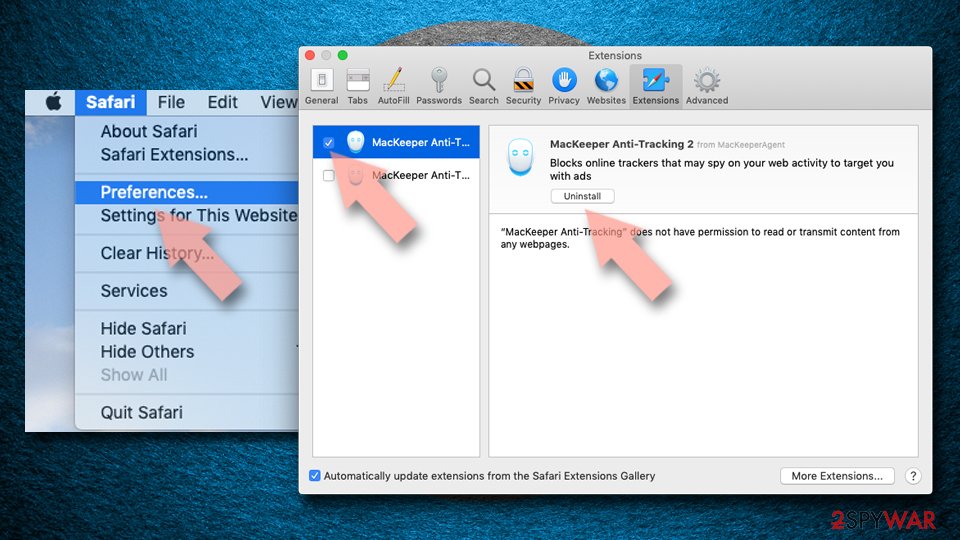
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
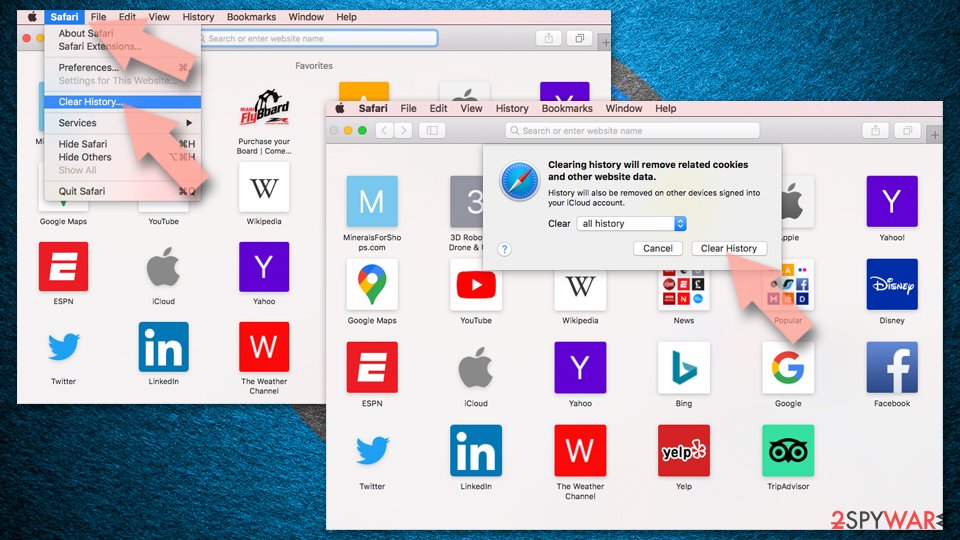
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
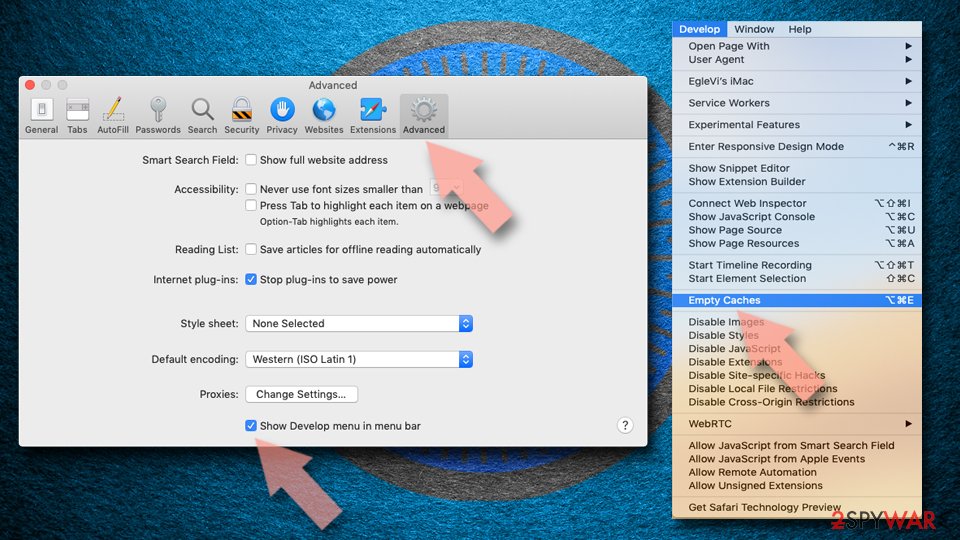
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
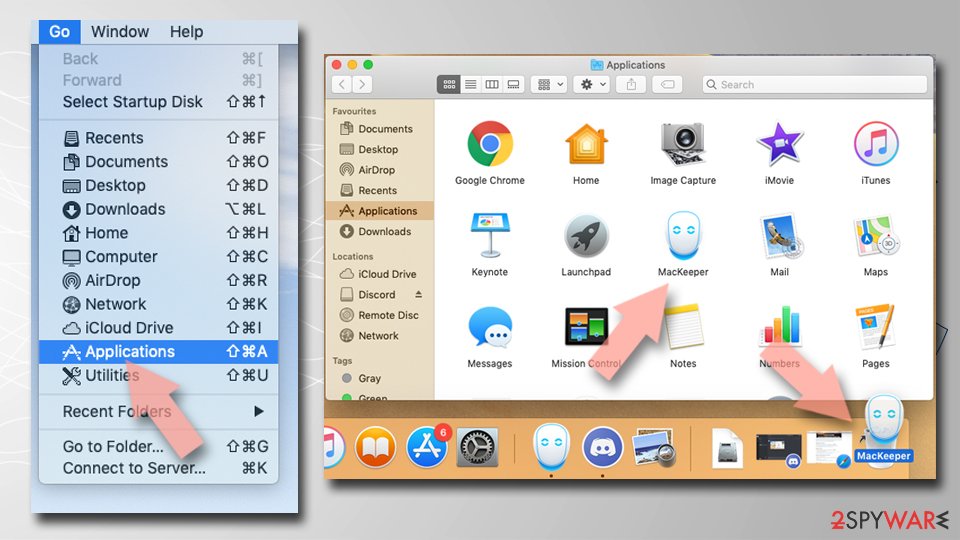
Delete from macOS
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
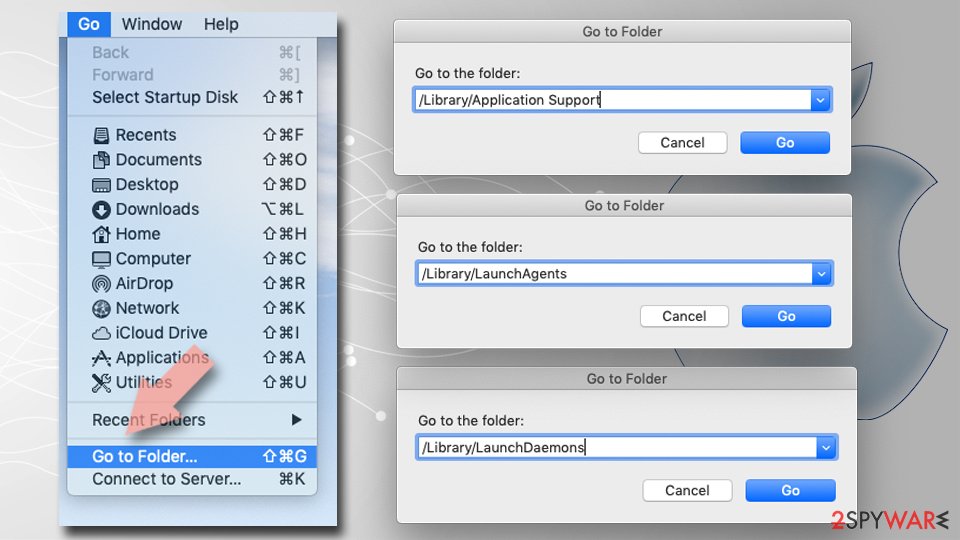
- Finally, empty the Trash to permanently remove the leftovers.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of Aug 2021 · not reviewed since
Get rid of the Win32:Adware-gen virus with AV tools
You can remove the potentially unwanted program in two different ways: manual or automatic.
Both methods are valid, and you should pick the one that suits you most.
Manual Win32 Adware-gen adw removal should be performed with caution. Do not tamper with your system files yourself, and rely on a guide created by our team. Follow each step carefully and in the correct order. If you fail to execute the procedure, the intrusive virus will return.
If you are not that confident in your computer skills, we suggest you pick security software to do the job for you.
Questions about Win32:Adware ads
What is Win32:Adware-gen?
Win32:Adware-gen is a detection name used by Avast antivirus to identify a potentially unwanted program running on Windows. It is an adware application, meaning it displays advertisements to users.
The program enters computers through software bundling, a technique where unwanted applications hide within Quick or Recommended installation settings of legitimate software installers. Unlike viruses, adware is technically legal, but it is invasive and exposes users to financial risk through malicious advertisements.
How does this adware infect my computer?
Win32:Adware-gen spreads primarily through insecure freeware installations. When downloading free software, users often click through installation screens without reading them carefully. During Quick or Recommended setup modes, the installer automatically includes additional components like this adware without explicit user approval.
The adware then integrates itself into the system, sometimes hiding under legitimate-looking process names in the task manager. It may not immediately show obvious activity, making it difficult for users to detect at first.
What damage can this adware cause?
Win32:Adware-gen attacks all installed browsers and displays invasive ads in various forms including pop-ups, video ads, in-text links, and banners. It causes redirects to suspicious websites and can slow down browser and PC performance significantly.
The program gathers search data, IP addresses, links clicked, and websites visited, enabling developers to profile your interests and control browsing habits. More dangerously, the tunnel of redirects and accidental clicks on malicious pop-ups can infect your machine with other viruses and lead to identity fraud.
How can I tell if I have this infection?
Key symptoms include a sudden increase in pop-ups and banner advertisements, especially during browsing. You may notice frequent redirects to unfamiliar websites despite clicking different links. Browser performance may noticeably slow down, and your computer may feel sluggish overall.
If your security software detects Win32:Adware-gen specifically, this confirms the infection. However, the adware can be sneaky; it might hide without showing obvious processes in the task manager or triggering immediate visible signs.
Can this adware install other unwanted programs?
Yes. A distinctive feature of Win32:Adware-gen is its ability to install additional components without permission. These secondary programs may include browser toolbars, search engine replacements, and other useless applications that clutter your machine.
Each additional unwanted program increases the possibility of severe malware infection. The more applications present, the more security holes exist on your system. Cybercriminals exploit this bloated state to deliver ransomware and other high-risk threats to victim machines.
Does this adware steal personal information?
Yes. Security experts observed Win32:Adware-gen gathering search data, IP addresses, links clicked, websites visited, and other non-personally identifiable information. However, the program also exists in ecosystems where other malware can capture sensitive data like names, addresses, and banking credentials.
Personal information collected can be sold on underground forums or used for identity theft. The tunnel of malicious redirects and pop-ups increases the likelihood of you accidentally entering credentials on fake websites designed to harvest login information.
How do I remove this adware?
You can remove Win32:Adware-gen in two ways: automatic or manual. For automatic removal, download and install reputable anti-malware software, update its virus database, and run a full system scan. The software will identify and remove the adware.
For manual removal, follow step-by-step guides carefully without tampering with unknown system files. However, manual removal requires technical expertise and risks system corruption if executed incorrectly. Most users should rely on professional anti-malware tools to handle this removal safely.
How do I prevent this adware in the future?
During software installation, always select Advanced or Custom settings instead of Quick or Recommended modes. Review all installation components carefully and uncheck any additional software or toolbars you do not recognize.
Read privacy policies and terms of use before installing software. Download software only from official developer websites or reputable stores.
Use reputable anti-malware software with real-time protection enabled. Do not click on eye-catching pop-ups promoting system tools or browser helpers. These practices significantly reduce your infection risk.
Will Fortect remove Win32:Adware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Win32:Adware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- How-To Geek: Beware: Never Download "Codecs" or "Players" To Watch Videos Online (read October 5, 2026)
- StopAd: How Many Ads Do You Actually See Daily? (read October 5, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)