
Goldoson Malware in 2026: Affected Apps and What to Do
- Goldoson malware in 2026: the short answer
- Timeline: Goldoson from discovery to 2026
- Which apps had Goldoson
- What changed since 2023
- Risks around Goldoson-type adware (our analysis)
- What to do in 6 steps
- What is still unknown
- Our original 2023 report
- How Goldoson works
- Remediation and prevention
- Related guides on 2-Spyware
Goldoson malware in 2026: the short answer
Goldoson is not an app. It is a third-party software library that 60 legitimate Google Play apps added without knowing what it did. Together those apps had about 100 million downloads, mostly in South Korea.[1][4]
After McAfee reported it in April 2023, many developers removed the library and Google pulled the apps that did not respond in time.[1][4] So if your copy came from Google Play and is updated, the risk is low. Copies from third-party app stores may still carry the library.[4] We found no new Goldoson campaign reported as of 2026.
| Question | Answer |
|---|---|
| What it is | A third-party Android library with adware and data collection[1] |
| Reach | 60 Google Play apps, about 100 million downloads[4] |
| What it collected | Installed apps, Wi-Fi and Bluetooth device data, GPS location[1] |
| Ad fraud | Hidden WebView clicks on ads in the background[4] |
| Status on Google Play | Apps updated without the library or removed[1][4] |
| Remaining risk | Old copies from third-party app stores[4] |
Timeline: Goldoson from discovery to 2026
| Date | Event |
|---|---|
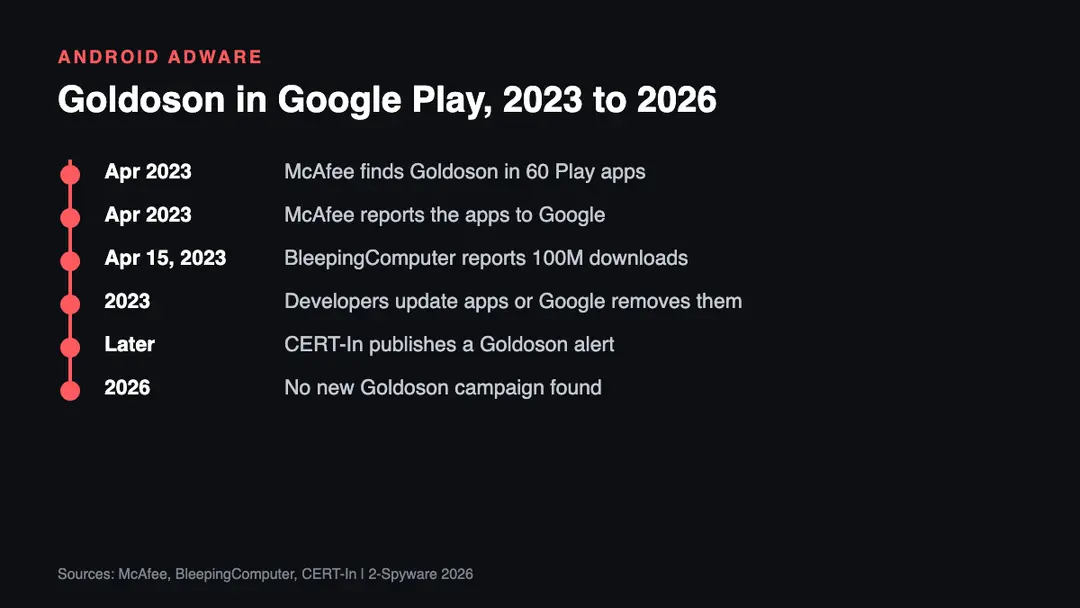
| April 2023 | McAfee's Mobile Research Team names the Goldoson library[1] |
| April 2023 | McAfee reports the apps to Google, which notifies developers[1] |
| April 15, 2023 | BleepingComputer reports 60 apps with 100 million downloads[4] |
| 2023 | Apps are updated without the library or removed from Google Play[1][4] |
| Later | India's CERT-In lists Goldoson in its malware alerts[5] |
Which apps had Goldoson
BleepingComputer listed some of the affected apps with their download counts at the time.[4] Most were later updated, so the current versions on Google Play should be clean. McAfee's report marks each app as updated or removed.[1]
- L.POINT with L.PAY, 10 million downloads[4]
- Swipe Brick Breaker, 10 million downloads[4]
- Money Manager Expense & Budget, 10 million downloads[4]
- GOM Player, 5 million downloads[4]
- LIVE Score, Real-Time Score, 5 million downloads[4]
- Pikicast, 5 million downloads[4]
- Compass 9: Smart Compass, GOM Audio, LOTTE WORLD Magicpass, Bounce Brick Breaker, Infinite Slice, SomNote and Korea Subway Info: Metroid, about 1 million downloads each[4]
What changed since 2023
The clean-up on Google Play worked as planned. McAfee, a member of Google's App Defense Alliance, informed Google, and Google told developers their apps broke Play policies. Apps that were not fixed in time were removed.[4] Google said it takes action when it finds apps that violate its policies.[4]
What has not changed is the method. Goldoson showed that a single software library can bring adware into many honest apps at once. Malicious apps keep reaching Google Play. BleepingComputer has also reported NoVoice, an Android malware spread through more than 50 apps on Google Play that infected 2.3 million devices.[6]
Risks around Goldoson-type adware (our analysis)
The points below are our analysis of how this kind of threat reaches users today.
- Old APKs from third-party stores. Copies made before the 2023 clean-up can still include the library.[4]
- Unused apps that never update. An app you installed in 2023 and never opened again may still be an old build.
- Broad permissions. Goldoson collected more data when apps had location and nearby-device permissions.[1]
- Fake cleaner apps. Apps that promise to remove Goldoson are often adware themselves. Use a known security tool instead.
What to do in 6 steps
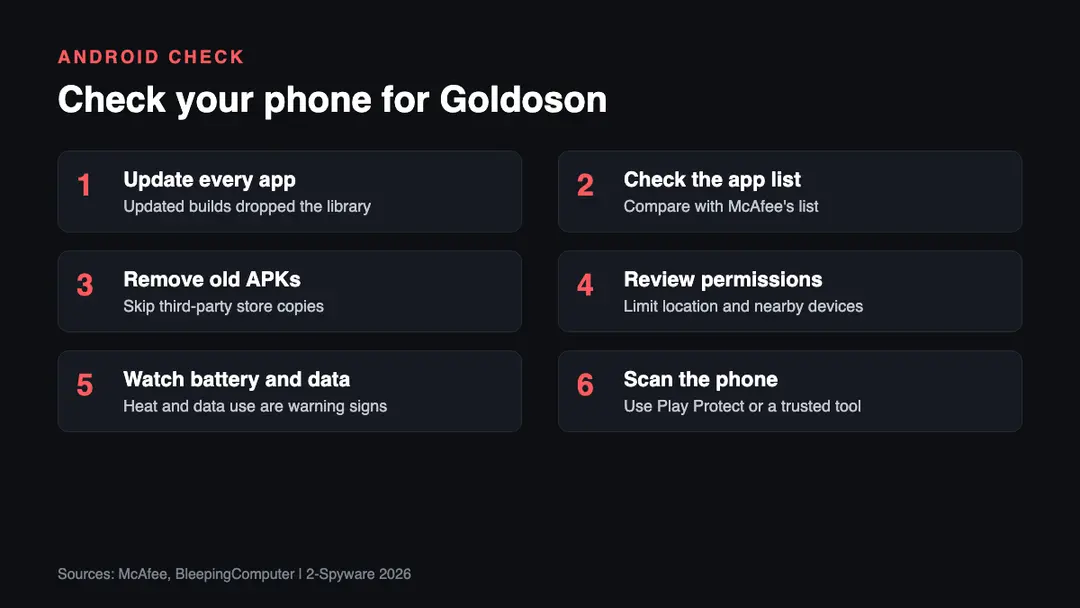
1. Update every app. Open Google Play and install all updates. Updated versions of the affected apps no longer contain the library.[1][4]
2. Check the app list. Compare your apps with the list above and with McAfee's full table, which marks each app as updated or removed.[1]
3. Remove old APKs. Uninstall affected apps you got from third-party stores, since those copies may still carry Goldoson.[4]
4. Review permissions. In Android settings, limit location and nearby-device access for apps that do not need it.[1]
5. Watch battery and data. A phone that heats up, drains its battery fast or uses data while idle may run adware.[4]
6. Scan the phone. Run Google Play Protect or a trusted mobile security app.[3] Our Android virus removal guides explain the next steps, and our leak check shows whether your email was exposed elsewhere.
What is still unknown
- Who built and distributed the Goldoson library. We found no public attribution.
- How much data was sent to the Goldoson servers before the clean-up. We found no figure.
- How many old copies still run on phones today. We found no measurement as of 2026.
Our original 2023 report
The text below is our report as first published in 2023. We keep it unchanged for the record; the sections above bring it up to date.
A new Android malware known as "Goldoson" has infiltrated Google Play via 60 legitimate apps with a total of 100 million downloads. The malware can collect data on installed apps, WiFi and Bluetooth-connected devices, and the user's GPS location, according to McAfee's research team,[1] which discovered Goldoson. It can also commit ad fraud[2] by clicking ads in the background without the user's knowledge.
This is not the first time malware has found its way into the Google Play store. Despite Google's numerous measures to prevent malware spread, cybercriminals continue to find ways around them. This incident emphasizes the importance of increased vigilance among app developers and users in order to prevent such attacks from occurring.
When incorporating third-party libraries into their apps, developers must exercise caution. This incident demonstrates how malware can easily infiltrate legitimate apps if developers do not exercise caution when incorporating third-party code. Users should also exercise caution when downloading apps, particularly those from unknown developers or those requiring extensive permissions.
How Goldoson works
When a user launches a Goldoson-containing app, the library registers the device and obtains its configuration from an obfuscated remote server. The configuration specifies which data-stealing and ad-clicking functions Goldoson should perform on the infected device and how frequently.
The data collection function is typically set to activate every two days, sending a list of installed apps, geographical location history, MAC addresses of devices connected via Bluetooth and WiFi, and other information to the C2 server. The amount of data collected is determined by the permissions granted to the infected app during installation as well as the Android version.
Although Android 11 and later are better protected against arbitrary data collection, McAfee discovered that Goldoson had enough permissions to gather sensitive data in 10% of the apps even in recent versions of the OS. Ad revenue is generated by loading HTML code and injecting it into a customized, hidden WebView, and then using that to perform multiple URL visits.
Because the victim sees no indication of this activity on their device, it is particularly insidious. The malware works in the background, collecting data and clicking on advertisements without the user's knowledge.
Remediation and prevention
Users who downloaded an impacted app from Google Play can mitigate the risk by installing the most recent available update.[3] However, Goldoson can also be found in third-party Android app stores, and the chances of them still containing the malicious library are high.
Device heating up, battery draining quickly, and unusually high internet data usage even when the device is not in use are all signs of adware and malware infection. Users should be on the lookout for these symptoms and keep an eye on their devices.
This incident highlights the value of increased security measures for app developers, Google Play, and Android users. Third-party libraries should be used with greater caution by developers, and Google Play should implement stricter policies to prevent malware from infiltrating its store.
In turn, Android users should exercise caution when downloading apps, particularly those from unknown developers or those requiring extensive permissions. We can prevent similar incidents in the future by working together.
Related guides on 2-Spyware
Frequently asked questions
What is Goldoson malware?
Goldoson is an Android adware library that McAfee found in 60 legitimate Google Play apps in 2023. It collected lists of installed apps, Wi-Fi and Bluetooth device data and GPS location, and it clicked ads in the background.{1}{4} The app developers had added the library without knowing its behavior.
Which apps contained Goldoson?
Affected apps included L.POINT with L.PAY, Swipe Brick Breaker, Money Manager Expense & Budget, GOM Player, LIVE Score, Pikicast and others, about 60 in total.{4} McAfee's report lists every app and marks it as updated or removed.{1} Updated versions on Google Play no longer contain the library.
Is Goldoson still active in 2026?
We found no new Goldoson campaign reported as of 2026. After the 2023 report, developers removed the library or Google pulled their apps.{4} The remaining risk is old copies of the apps from third-party app stores, which may still include it. Updating or removing those apps solves the problem.
How do I remove Goldoson from my phone?
Update every affected app from Google Play, because the updated versions dropped the library.{4} Uninstall any affected app you got from a third-party store. Then run Google Play Protect or a trusted security app and review app permissions for location and nearby devices.{1}{3}
Is Goldoson adware or spyware?
It is both, in effect. McAfee called it privacy-invasive and clicker adware, because it collected device and location data and performed hidden ad clicks for revenue.{1} It did not lock files or steal passwords according to the reports we read, but the data it gathered could profile users.
How many people were affected by Goldoson?
The 60 affected apps had about 100 million downloads in total, mostly in South Korea.{4} Downloads are not the same as infected users, and McAfee found that on recent Android versions the library could gather sensitive data in about 10 percent of the apps.{4}
Sources
- Mcafee. Security Solutions
- Cloudflare. Learning Center
- Google. Google Play Help (no longer online)
- BleepingComputer
- CERT-In Cyber Swachhta Kendra
- BleepingComputer
Log in to comment
No comments yet. Be the first.