
Collection #1 Data Breach: What It Means in 2026
- Collection #1 in 2026: the short answer
- Timeline: Collection #1 and what followed
- What changed since 2019
- Risks and scams linked to Collection #1 (our analysis)
- How to protect yourself in 6 steps
- What is still unknown
- Our original 2019 report
- The origin of the data is not recognized
- Shield yourself from data compromise
- Related guides on 2-Spyware
Collection #1 in 2026: the short answer
Collection #1 was not a hack of one company. It was a giant set of credential stuffing lists, emails paired with passwords taken from earlier breaches, found on a hacking forum in January 2019.[7] It held almost 2.7 billion records, including 773 million unique email addresses and about 21 million unique passwords.[2][7]
In 2026 the lists still matter because old passwords are often reused. Have I Been Pwned still lists the breach, marks it as unverified and advises everyone affected to change the password on every account where it was used and to turn on two-factor sign-in.[7]
| Question | Answer |
|---|---|
| What it is | Credential stuffing lists built from many older breaches[7] |
| Size | Almost 2.7 billion records, 773 million unique emails[7] |
| Unique passwords | About 21 million, in plain text[2][8] |
| Found | January 2019, on a popular hacking forum[7] |
| Added to Have I Been Pwned | January 16, 2019, flagged as unverified[7] |
| Follow-up sets | Collections #2 to #5 seen for sale by January 30, 2019[8] |
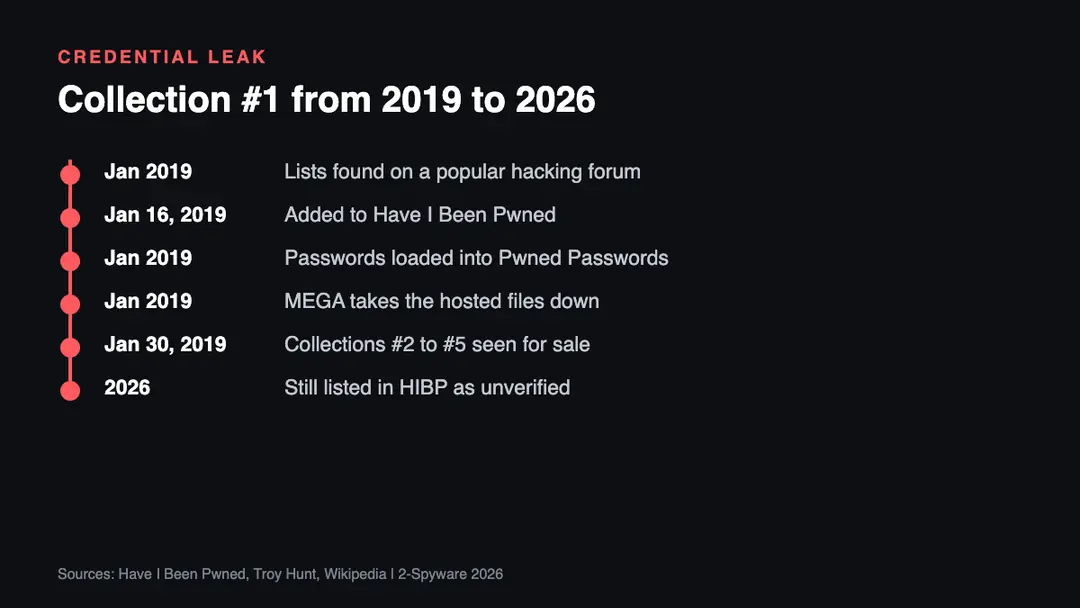
Timeline: Collection #1 and what followed
| Date | Event |
|---|---|
| January 2019 | Credential lists found on a hacking forum[7] |
| January 16, 2019 | Breach added to Have I Been Pwned[7] |
| January 2019 | Troy Hunt adds the passwords to Pwned Passwords[2] |
| January 2019 | MEGA removes the hosted data, as our original report notes |
| By January 30, 2019 | Collections #2 to #5 seen for sale on the dark web[8] |
| 2026 | Breach still listed in Have I Been Pwned as unverified[7] |
What changed since 2019
Collection #1 turned out to be the first of a series. By January 30, 2019 researchers had seen similar sets called Collections #2 through #5 for sale. Researchers at the Hasso Plattner Institute estimated that those later sets held about three times as much data after duplicates were removed.[8]
The way people check their exposure also changed. Troy Hunt loaded the Collection #1 passwords into Pwned Passwords, which lets anyone test a password without sending the full password to the service.[2] Have I Been Pwned now marks Collection #1 as an unverified breach, which means the data is real but its origin could not be fully proved.[7]
What did not change is the core risk. A list of old email and password pairs is only useful to criminals because many people reuse passwords. If you used one password on many sites before 2019 and never changed it, that password may still be in circulation.
Risks and scams linked to Collection #1 (our analysis)
People still search for a "Collection 1 data breach download". The risks below are our analysis of how criminals use old leaks and that curiosity.
- Credential stuffing. Bots try leaked email and password pairs on shopping, email and streaming sites. Reused passwords are the main target.[7]
- Fake download links. Files that claim to be the Collection #1 dump are a common way to spread malware. Do not download them.
- Sextortion emails. Scammers quote an old leaked password in an email to make a blackmail threat look real. The password proves only that it leaked.
- Fake breach checkers. Sites that ask for your password to "check" it may simply collect it. Use known services and our own leak check.
How to protect yourself in 6 steps
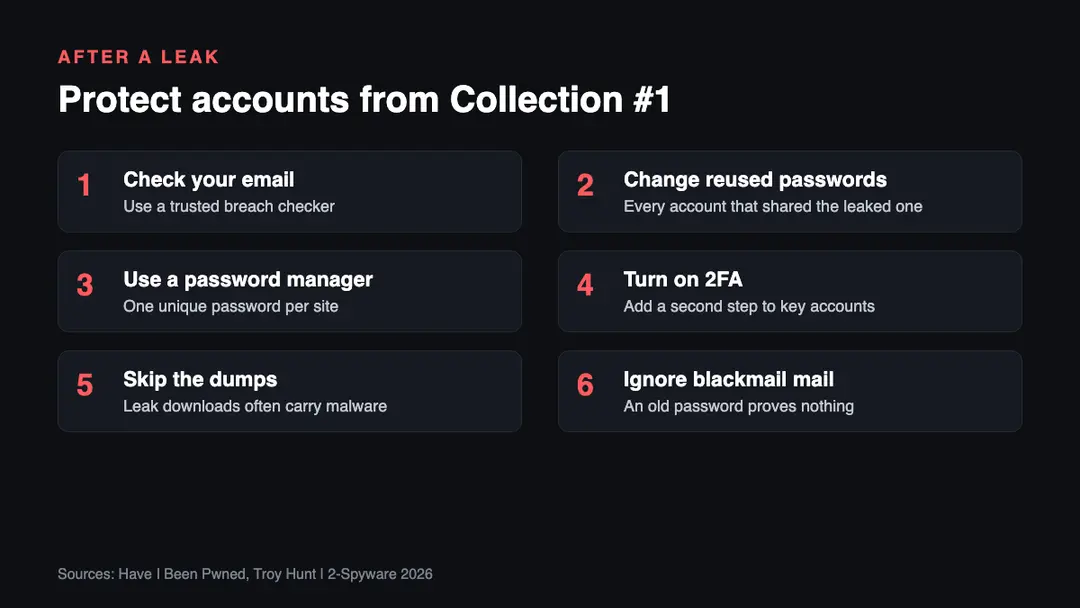
1. Check your email. Search your address in Have I Been Pwned or in our leak check to see whether it appears in Collection #1 or later leaks.[1]
2. Change reused passwords. Change the password on every account where you used a leaked one, as Have I Been Pwned advises.[7]
3. Use a password manager. A manager makes a unique password for each site, so one leak cannot open other accounts.
4. Turn on two-factor sign-in. Add a second step to email, banking and social accounts. A leaked password alone then is not enough.[7]
5. Do not download leak files. Files sold or shared as breach dumps can carry malware. If you opened one, see our malware removal guides.
6. Ignore blackmail emails. If an email quotes your old password and demands payment, do not pay. Report it, and read how to report phishing.
What is still unknown
- Exactly which breaches supplied the data. Troy Hunt recognized many sources, but the full origin was never confirmed, which is why the breach is marked unverified.[7]
- Who compiled and first sold the lists. We found no public attribution.
- How many of the passwords still work in 2026. We found no current measurement.
Our original 2019 report
The text below is our report as first published in 2019. We keep it unchanged for the record; the sections above bring it up to date.
Troy Hunt, a security researcher, Microsoft Regional Director and the owner of Have I Been Pawned,[1] discovered[2] unprotected data that contained 772,904,991 unique email addresses and 21,222,975 unencrypted passwords. This type of mega breach is one of the largest ones ever announced, surpassing even Equifax, but falling short to Yahoo's email hack back in 2013.[3]
The compiled data came from thousands of different data breaches and placed on a cloud-based service called MEGA. Named "Collection #1," the 87 GB container consisted of 12,000 separate files and 2,692,818,238 rows. The researcher received a tip from a colleague that led him to a popular hacking forum where the data was promoted as "a collection of 2000+ dehashed databases and Combos stored by topic."
According to Hunt, users can enter their email addresses and passwords on Have I Been Pawned to find out whether or not they are affected. There are 1,160,253,228 unique combinations of email addresses and passwords, although many of the data was dismissed after the researcher cleaned and software the existing data:
This also includes some junk because hackers being hackers, they don't always neatly format their data dumps into an easily consumable fashion. (I found a combination of different delimiter types including colons, semicolons, spaces and indeed a combination of different file types such as delimited text files, files containing SQL statements and other compressed archives.)
Soon after the discovery, the cloud service MEGA took down the hosted information.
The origin of the data is not recognized
Collection #1 is the largest accumulation of data found in a single piece. While Hunt recognized many breaches where the information came from, the origin of the data is still unclear, and some of the services might not have been involved in the data breach.
Nevertheless, he notes that, after checking his own passwords and email addresses from the past, he confirmed that the data was accurate. The expert also says that many of the uncovered passwords were initially hashed during the compromise. However, hackers managed to "dehash" and convert them to plain text.
Hunt referred to the data as "random" when interviewed by Wired:[4]
It just looks like a completely random collection of sites purely to maximize the number of credentials available to hackers. There's no obvious patterns, just maximum exposure.
Shield yourself from data compromise
Hunt urges people to go and change their passwords immediately if they are included in the HIBP database, as "one or more passwords you've previously used are floating around for others to see."
Credential stuffing is a popular technique used by cybercriminals, and it seems like Collection #1 is created just for that purpose, seeing how untidy the database was. There are over 2.7 billion records on Hunt's site currently, meaning that all of this data can be used for credential stuffing.
The process relies on users reusing their old passwords or keeping the same ones for multiple accounts. After acquiring credentials from a data breach, any criminal can attempt to enter other accounts based on that data. For that reason, changing passwords frequently, or using password managers is vital when it comes to cybersecurity, as explained by Hunt:
Perhaps your personal data is on this list because you signed up to a forum many years ago you've long since forgotten about, but because its subsequently been breached and you've been using that same password all over the place, you've got a serious problem.
According to security experts, 2018 was a "year of the data breach tsunami,"[5] which resulted in such notorious cases like Cambridge Analytica, Quora, Marriott,[6] and many others. Looking into the future, it becomes evident that data harvesting is a lucrative business for criminals, so adequate measures should be undertaken to protect sensitive information in the year 2019.
Related guides on 2-Spyware
Frequently asked questions
What is the Collection #1 data breach?
Collection #1 is a large set of credential stuffing lists found on a hacking forum in January 2019. It combined emails and passwords from many earlier breaches into almost 2.7 billion records with 773 million unique email addresses.{7} Troy Hunt named it after the root folder of the files and added it to Have I Been Pwned.{2}
How many records were in Collection #1?
Collection #1 held almost 2.7 billion records. Inside were 772,904,991 unique email addresses and 21,222,975 unique passwords, according to Troy Hunt.{2}{7} Many rows were duplicates or junk, because the data was merged from thousands of files in different formats.
How do I know if I was in Collection #1?
Search your email address in Have I Been Pwned, which lists Collection #1 as a breach, or use our leak check.{7} You can also test a password with Pwned Passwords, which Troy Hunt loaded with the Collection #1 passwords.{2} If you appear, change that password everywhere you used it.
Is it safe to download the Collection #1 data?
No. Sharing and using stolen credentials can be illegal in many countries, and files sold as breach dumps are a common way to spread malware. You do not need the files to check your exposure. Have I Been Pwned and our leak check answer that question without any download.{7}
What were Collections #2 to #5?
Collections #2 to #5 were similar credential lists seen for sale by January 30, 2019. Researchers at the Hasso Plattner Institute estimated that, after duplicates were removed, they held about three times as much data as Collection #1.{8} The same advice applies: change reused passwords and turn on two-factor sign-in.
Does Collection #1 still matter in 2026?
Yes, if you still use a password that was in it. The lists are built for credential stuffing, so any reused password from before 2019 can still open accounts. Have I Been Pwned still lists the breach and recommends changing affected passwords and enabling two-factor authentication.{7}
Log in to comment
No comments yet. Be the first.