
Can You Get a Virus From Discord? 2026 Malware Guide
- Discord malware in 2026: the short answer
- Timeline: Discord malware from Spidey Bot to invite hijacking
- What changed since 2019
- Discord scams and malware tricks to watch (our analysis)
- How to protect yourself from Discord malware
- What is still unknown
- Our original 2019 report
- Data stolen by the malicious Discord version includes sensitive details
- Another danger – malware in Discord messages
- Related guides on 2-Spyware
Discord malware in 2026: the short answer
Discord itself is not a virus or spyware, but you can get a virus through Discord. Criminals use it to share malicious files, to send stolen data through webhooks and, since 2025, to lure people through hijacked invite links.[6][7] The risk comes from what you click and run, not from the official app.
The Spidey Bot case in our original report showed malware that changed Discord's own files to turn it into a backdoor. Later campaigns moved to new tricks, such as fake verification pages that make you paste a command into Windows.[7][9] The basic advice stays the same: install Discord only from official sources and do not run files that strangers send.
| Question | Answer |
|---|---|
| Is Discord a virus? | No. The official app is not malware |
| Can you get a virus from Discord? | Yes, by running files or links shared on it[6][7] |
| What do attackers steal? | Passwords, browser cookies, crypto wallets and Discord session tokens[6][7] |
| Main 2025 trick | Hijacked expired invite links that lead to fake servers[7] |
| Malware seen | AsyncRAT for remote control and Skuld Stealer for crypto wallets[7][8] |
| What Discord changed | File links that expire, to stop malware hosting on its CDN[6] |
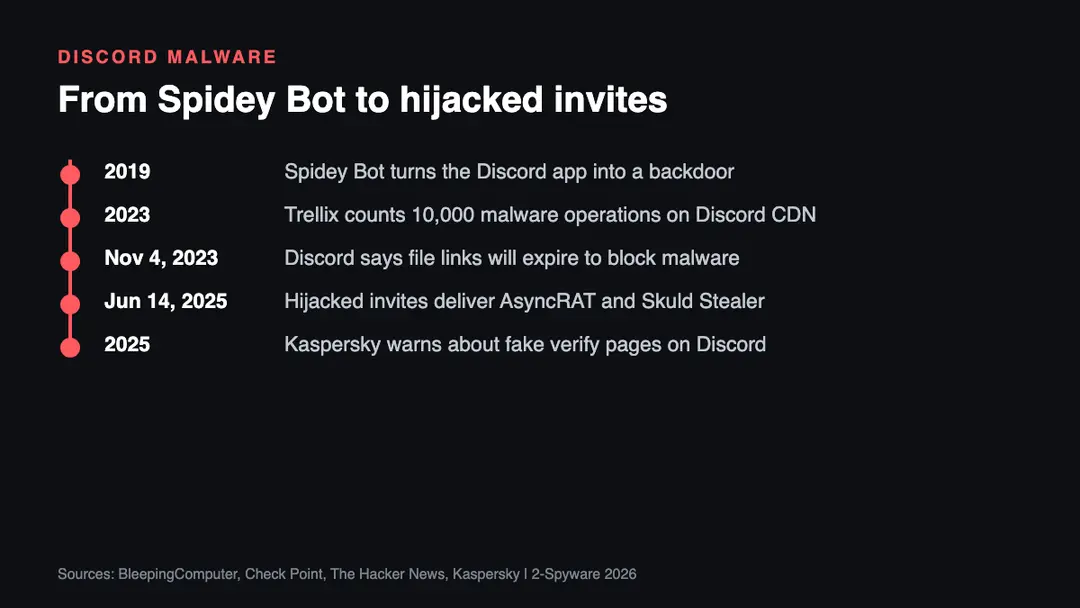
Timeline: Discord malware from Spidey Bot to invite hijacking
| Date | Event |
|---|---|
| 2019 | Researchers report Spidey Bot, which modifies Discord files to steal data and open a backdoor[1] |
| 2023 | A Trellix report says at least 10,000 malware operations used Discord CDN links[6] |
| November 4, 2023 | Discord tells BleepingComputer it will switch to temporary file links to cut malware hosting[6] |
| June 14, 2025 | The Hacker News reports hijacked invite links delivering AsyncRAT and Skuld Stealer[8] |
| 2025 | Check Point Research and Kaspersky describe the invite flaw and the ClickFix trick[7][9] |
What changed since 2019
In 2019 the worry was malware that rewrote Discord's code on the computer. Since then Discord has been misused in other ways. Its file hosting was used to deliver second-stage payloads such as RedLine, Vidar and Agent Tesla, and webhooks were used to send stolen credentials and cookies back to attackers.[6]
Discord reacted in November 2023. It said attachment links would get an expiry time and a signature, and that links to uploaded files would expire after 24 hours, so its CDN could no longer serve as permanent malware hosting.[6]
In 2025 attackers found a new gap. When a server lost its boost status or an invite expired, criminals could register the same code as a custom link for their own server.[7] People who clicked an old invite from a trusted site landed on a fake server, met a fake verification bot and were told to paste a command into Windows. That installed AsyncRAT and a customised Skuld Stealer.[7][9]
Discord scams and malware tricks to watch (our analysis)
Based on the reports above and our own removal work, these are the tricks most worth knowing in 2026.
- Fake verification steps. A server asks you to press Windows keys and paste a command to prove you are human. Discord never needs this.[9]
- Files from strangers. Game cheats, mods, "test my game" requests and cracked software are common carriers of information stealers.
- Old invite links. A link on a forum or website may now point to a criminal server.[7]
- Token stealers. Malware that takes your Discord token can log in as you without your password.[7]
- Fake Discord apps and modified clients. Only the official app from discord.com or app stores is safe.
How to protect yourself from Discord malware
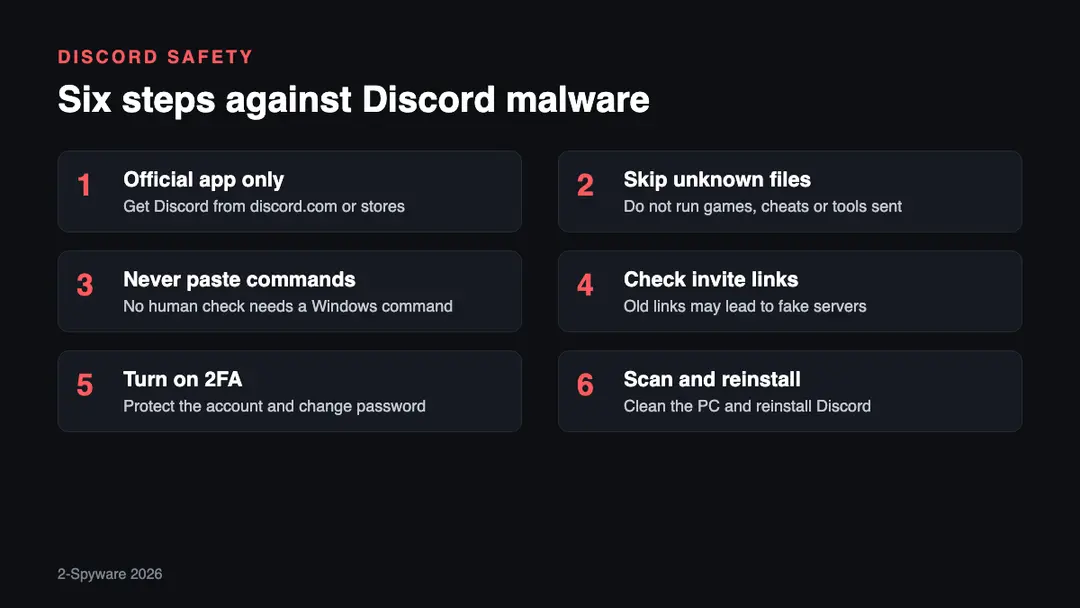
1. Use the official app only. Download Discord from discord.com or the official app stores. Modified clients can carry the same kind of backdoor as Spidey Bot.
2. Skip unknown files. Do not run games, cheats, mods or tools that someone sends you, even a friend. Their account may already be stolen.
3. Never paste commands. If a server asks you to open the Run box and paste text to verify, leave the server. That is the ClickFix trick behind the 2025 campaign.[7][9]
4. Check invite links. Be careful with old invites from forums or websites. Server owners can use permanent invite links to cut the risk of hijacking.
5. Turn on two-factor sign-in. Set a new, unique password and turn on two-factor sign-in. Check whether your email appeared in a leak with our leak check.
6. Scan and reinstall. If you think you ran something bad, scan the PC with a trusted security tool, then uninstall and reinstall Discord, as our original report advises. See our Discord virus removal guide.
What is still unknown
- Whether Discord has fully closed the invite reuse gap. We found no Discord statement on a fix as of 2026.
- How many accounts were stolen through hijacked invites. The reports we read give no total.
- Whether Spidey Bot style file changes are still in use. We found no new report on that technique since 2019.
Our original 2019 report
The text below is our report as first published in 2019. We keep it unchanged for the record; the sections above bring it up to date.
 Warning! Discord users have been targeted by malware which can cause identity theft and other issues.[1] Being named as Spidey Bot, the malware installs files presented as Discord-related data and kills the program at the beginning. Once restarted, specific modules and core files are changed, so the application can launch malicious processes on the machine and perform all the campaigns from the startup.
Since Discord is the Electron application, most of the functions are driven from HTML, CSS, and JavaScript so that malicious actors could modify needed files and run it as a virus.[2] However, the most important fact is that, once malware restarts all the processes related to the legitimate platform and executes numerous API commands, it gets the ability to collect data about the user.
Data stolen by the malicious Discord version includes sensitive details
Once the specific information is recorded, it is sent to the hacker via the Discord webhook. The additional process gets executed at the same time, and the virus acting as a backdoor is launched. Other commands can be executed after the remote site connection is allowed. The attacker gets an ability to perform numerous malicious activities like stealing payment information, executing programs on the system directly, or installing malware further on the device.[3]
The malware is targeting a variety of data that can be obtained from the chatting platform itself:
- details about the Discord version used;
- the browser user agent;
- first 50 characters out of the victims' Windows clipboard;
- zoom factor;
- stored payment information;
- username;
- email address;
- phone number;
- a public IP address;
- a local IP address;
- screen resolution;
- timezone;
- Discord user token.
Data that can be accessed and stored is pretty valuable, especially usernames and clipboard content. After sensitive details like passwords or personal information are copied, hackers may continue their attacks, e.g. steal money directly from the victim's account, send blackmailing emails, etc.[4]
Another danger – malware in Discord messages
Even in-depth analysis cannot confirm that Spidey Bot virus has been delivered by using one distinct method, it is suggested that attackers are using the messaging application itself to spread the malware. Unfortunately, it is not a good thing since users cannot know if the system was infected or not. To indicate this, the network sniffing, during which unusual API and webhook can be determined, is required.
Even if the installer is removed, modified Discord files might still remain on the system and continue to execute the malicious processes on the system with each reboot. Uninstalling and reinstalling the Discord app is the only way to clean the infection completely with all the modified files what is highly recommended if any suspicious activity is noticed.
This is not the first time when Discord is misused for malicious campaigns. Scamming techniques that target stolen credit card data, accounts with weak passwords and malicious apps pretending to be Discord have been misusing app's name for years. However, having in mind how has the popularity of this app increased, there is no surprise that it has been included in dozens of different fraudulent campaigns.[5]
Related guides on 2-Spyware
Frequently asked questions
Can you get a virus from Discord?
Yes, but only if you run a malicious file or follow a malicious link shared on Discord. Criminals have used Discord to host malware files and to send stolen data through webhooks.{6} In 2025 hijacked invite links led users to fake servers that installed AsyncRAT and Skuld Stealer.{7}
Is Discord a virus or spyware?
No. The official Discord app from discord.com or app stores is not a virus or spyware. The danger comes from modified copies of the app, like the Spidey Bot backdoor in 2019, and from files and links that other users share.
Does Discord have viruses?
Discord does not ship with viruses, but files on Discord can contain them. A 2023 Trellix report counted at least 10,000 malware operations that used Discord file links to deliver payloads.{6} Discord moved to expiring file links to make that harder.{6}
Can Discord give you a virus by opening a message?
Reading a message alone is not the usual risk. Infections in the reports we read come from running files, installing fake apps or following steps on a fake server, such as pasting a command into Windows.{7}{9} Do not open attachments or run tools from people you do not trust.
What is the Discord cache trojan?
It usually means malware stored in or linked from Discord's file hosting, the CDN. Attackers used Discord CDN links to drop loaders and stealers on infected PCs.{6} If your antivirus flags a file in a Discord folder, delete it, scan the PC and reinstall Discord.
How do I know if my Discord was hacked?
Signs include messages you did not send, new logins, changed settings or friends who say you sent them files. Change your password, turn on two-factor sign-in, remove unknown authorised apps and scan your PC, because token stealers can log in without your password.{7}
Log in to comment
No comments yet. Be the first.