
Flappy Birr Dog Spyware in 2026: MobSTSPY Facts
- Flappy Birr Dog spyware in 2026: the short answer
- Timeline: from Google Play to removal
- What changed since our first report
- Risks from fake and clone apps (our analysis)
- Steps to check your Android phone
- What is still unknown
- Our original 2019 report
- The functionality of the info-stealing malware MobSTSPY includes the collection of private information
- Data-stealing malware has been distributed in more than 196 countries
- Related guides on 2-Spyware
Flappy Birr Dog spyware in 2026: the short answer
Flappy Birr Dog was a game on Google Play that carried Android spyware that Trend Micro detects as ANDROIDOS_MOBSTSPY. Trend Micro reported in January 2019 that Google had removed all six apps in the campaign, and that five of them had been suspended since February 2018.[6] We found no report of the app being available on Google Play in 2026.
One detail in our original text needs a correction. It said the Flappy Birr Dog app itself had been downloaded more than 100,000 times. Trend Micro's table lists Flappy Birr Dog at 10 downloads, and the 100,000 to 500,000 range belongs to a different app, Win7imulator.[6] The campaign as a whole did reach users in 196 countries.
| Question | Answer |
|---|---|
| Malware name | ANDROIDOS_MOBSTSPY, a spyware family[6] |
| Apps involved | Flappy Birr Dog, Flappy Bird, FlashLight, HZPermis Pro Arabe, Win7imulator, Win7Launcher[6] |
| Biggest app by downloads | Win7imulator, 100,000 to 500,000; Flappy Birr Dog, 10[6] |
| Data it could steal | Location, SMS, call logs, contacts, clipboard items and files[6] |
| Phishing | Fake Facebook and Google pop-ups to collect logins[6] |
| Status in 2026 | Removed from Google Play; we found no 2026 report of the app |
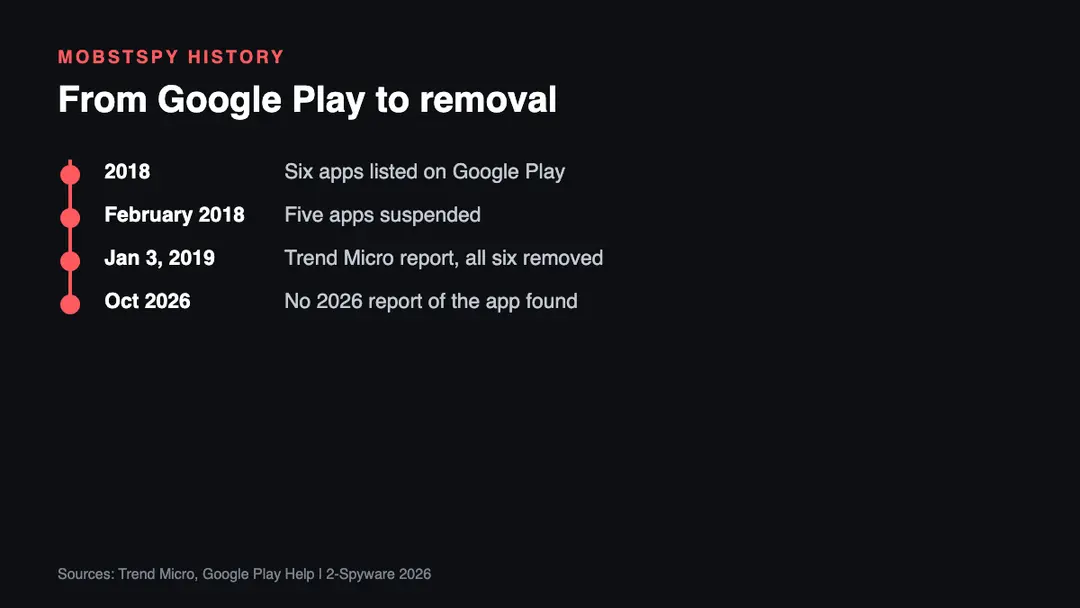
Timeline: from Google Play to removal
| Date | Event |
|---|---|
| 2018 | The six apps are available on Google Play[6] |
| February 2018 | Five of the six apps are suspended from Google Play[6] |
| January 3, 2019 | Trend Micro publishes its report and says all six are removed[6] |
| 2019 | 2-Spyware publishes its first report on the case |
| October 2026 | We found no 2026 report of the app on Google Play |
What changed since our first report
Trend Micro's report gives more detail than our original text. MobSTSPY steals location, SMS conversations, call logs and clipboard items, and it uses Firebase Cloud Messaging to send data to its server.[6] After launch it checks the network, reads a configuration file from its command server and then registers the device by sending collected details such as language, country, package name and manufacturer.[6]
After that the malware waits for commands. Depending on the command it can steal SMS conversations, the contact list, call logs and files from target folders, and it can upload files.[6] It can also show fake Facebook and Google pop-ups, and if you type your login, the pop-up only says that sign-in failed while the credentials are already stolen.[6]
On the defense side, Google says Play Protect checks apps when you install them and scans the device periodically. If it finds a harmful app it can notify you, disable the app or remove it automatically.[7] Our original text said the apps probably passed review because the bad code was added later. We could not confirm that from the pages we read, so treat it as a theory.
Risks from fake and clone apps (our analysis)
These points are our analysis based on how this campaign worked. They apply to many clone apps.
- Clone games. A game that copies a famous title, such as Flappy Bird, is a common disguise for spyware.
- Utility apps. A flashlight or a desktop launcher does not need your SMS, contacts or call logs. Such a request is a warning sign.
- Fake login pop-ups. A pop-up that asks for your Facebook or Google login outside the real app is a phishing attempt.
- Stolen messages. SMS access can expose verification codes and reset links for your other accounts.
- Slow detection. Trend Micro reported that some apps were already downloaded over 100,000 times before removal.[6]
Steps to check your Android phone
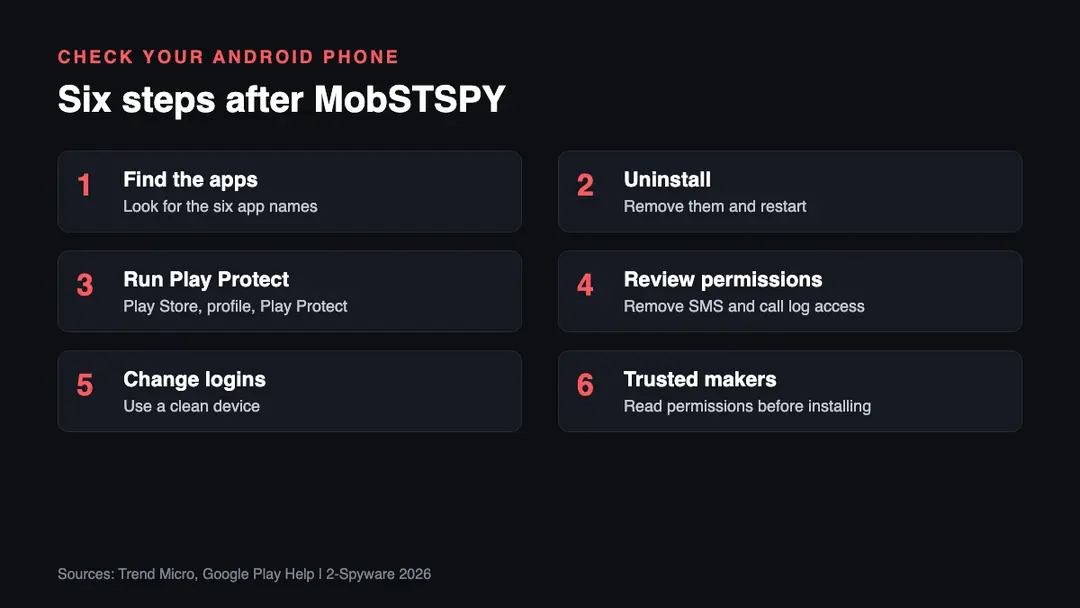
1. Look for the six apps. Open Settings, then Apps, and look for Flappy Birr Dog, Flappy Bird, FlashLight, HZPermis Pro Arabe, Win7imulator and Win7Launcher.[6]
2. Uninstall any you find. Remove the app, then restart the phone.
3. Run Play Protect. Open the Play Store, tap your profile, then Play Protect, and run a scan.[7]
4. Review permissions. In Settings, open app permissions and remove SMS, contacts and call log access from apps that do not need it.
5. Change your logins. From a clean device, change your Facebook, Google and email passwords and turn on two-factor sign-in.
6. Install from trusted makers. Prefer apps from known developers and read the permission list before you install.
What is still unknown
- Who built the MobSTSPY apps. The sources we read do not name the authors.
- How many devices were infected in total. We found no count beyond the figures in Trend Micro's report.
- Whether any copy of these apps is still offered outside Google Play. We found no report either way.
We will update this page if a security vendor or Google publishes new findings.
Our original 2019 report
The text below is our report as first published in 2019. We keep it unchanged for the record; the sections above bring it up to date.
There are numerous apps that have been banned on Google Play Store for being infected with malware. Unfortunately, these cases are still apparent as hackers constantly rely on new deceptive techniques while trying to infect Android users. According to the latest reports, security experts found yet another app on the Google Play Store which is infected with spyware and is capable of accessing details about the user like location, communication logs or even account credentials.
Unfortunately, the infected Android app, which is called Flappy Birr Dog, has been downloaded for more than 100 000 times by users from at least 196 countries.[1] According to the report of Trend Micro, the app and several other apps (Flappy Bird, FlashLight, HZPermis Pro Arabe, Win7imulator, Win7Launcher, etc.) were found to be infected with the ANDROIDOS_MOBSTSPY spyware.[2]
It is possible that the Google Play store approved these apps because the malicious code was added after the initial upload. As mentioned in the report, these apps waited on the app store several months until they were altered by their creators:
Usually Google enforce more stringent checks for new apps, but as updates are made to the app over time and they are proven not to be malicious from the offset, the level of checking may be reduced.
The functionality of the info-stealing malware MobSTSPY includes the collection of private information
After the initial installation of the application, the MobSTSPY malware runs on the system and checks the network, connects to the C&C server[3] and starts collecting information about the infected device. According to the details of the manufacturer and country, the virus decides on the later malicious behavior.
Since this spyware can launch different commands and functions, it is possible that the attackers are focusing on different techniques based on the particular target. MobSTSPY can do the following tasks:
- access SMS messages;
- steal data like screenshots, audio recordings;
- access WhatsApp information;
- gather credentials by using additional phishing attacks.[4]
Additionally, this application can create fake messages from social media or other platforms to steal victim's account logins. Fake pop-ups from Facebook or Google can ask you to type your username and login to the account, but the minute you enter the needed information, malware actors steal those details for their following purposes.
This application can create fake messages from social media or other platforms to steal your account logins. Fake pop-ups from Facebook or Google can ask you to type your username and login to the account, but the minute you enter the needed information, malware actors steal those details for their later purposes.
These pop-ups appear out of nowhere and attempt to get users' account logins and passwords. The window suggests users log in to their account, but when you enter your credentials, the message will state about unsuccessful login. Although, your account information is already gathered and stolen.
Data-stealing malware has been distributed in more than 196 countries
Applications that distribute info-stealing malware was probably updated after the upload to the Google Store, and after that, the main six apps discovered in the investigation were downloaded by at least 100 000 users. Android malware was widely distributed to a large part of the world. Top countries with the most affected users:
- India;
- Russia;
- Pakistan;
- Bangladesh;
- Indonesia;
- Brazil;
- Egypt;
- Ukraine;
- Turkey;
- The United States.
During this research, TrendMicro discovered six applications that distributed the malicious MobSTSPY[5] around the globe: Flappy Birr Dog, Flappy Bird, FlashLight, HZPermis Pro Arabe, Win7imulator, Win7Launcher. All those apps should be removed from your device, and you need a full system cleaning if you want to avoid additional virus damage to the system.
Related guides on 2-Spyware
Frequently asked questions
What is Flappy Birr Dog?
Flappy Birr Dog was a game on Google Play that carried the MobSTSPY spyware. Trend Micro found it together with five other apps and reported that Google had removed all six by January 2019.{6} The spyware could steal location, SMS conversations, call logs and clipboard items and could show fake login pop-ups.{6}
Is Flappy Birr Dog still on Google Play?
We found no sign of it. Trend Micro reported in January 2019 that Google had removed all six apps, and five had been suspended since February 2018.{6} We found no 2026 report of the app on the store. If you still have it on your phone, uninstall it.
Which apps carried the MobSTSPY spyware?
Six apps carried it: Flappy Birr Dog, Flappy Bird, FlashLight, HZPermis Pro Arabe, Win7imulator and Win7Launcher.{6} Win7imulator had the largest download range, 100,000 to 500,000, while Flappy Birr Dog itself is listed at 10 downloads. Check your phone for all six names.
What can MobSTSPY steal from a phone?
It can steal location, SMS conversations, call logs, contacts, clipboard items and files, depending on the commands it receives.{6} It can also show fake Facebook and Google pop-ups that capture your login, then report that sign-in failed.{6} Remove the app and change those passwords.
How do I check my Android phone for spyware?
Look for the six app names, run a Play Protect scan and review app permissions. Google says Play Protect checks apps at install and scans your device periodically, and it can disable or remove harmful apps.{7} Then remove SMS and call log access from apps that do not need it.
Log in to comment
No comments yet. Be the first.