
Russian Keyboard vs Ransomware in 2026: Does It Still Work?
- Russian keyboard against ransomware in 2026: the short answer
- Timeline: language checks in ransomware
- What changed since 2021
- Risks and false comfort around the trick (our analysis)
- Steps that protect you better than a keyboard
- What is still unknown
- Our original 2021 report
- The malware will exit without attacking if the particular language is installed
- The ransomware infection process explained
- Other tips for companies and everyday users that want to avoid ransomware
- Related guides on 2-Spyware
Russian keyboard against ransomware in 2026: the short answer
The trick still works against some malware, but it is a thin layer and not a defence plan. The MITRE ATT&CK knowledge base keeps a list of malware that reads the system language or keyboard layout and stops when it finds Russian or another CIS language.[9] That list includes well known ransomware such as Clop, Cuba, Ryuk, REvil and LockBit 2.0.[9]
The idea became famous in May 2021, when KrebsOnSecurity wrote that many ransomware strains will not install on a Windows computer that already has a Russian or Ukrainian virtual keyboard.[3] The same article warned that attackers can change their checks at any time. Five years later, the safe reading is simple: a Cyrillic layout may make a few strains quit, but backups and patches are what save your files.
| Question | Answer in 2026 |
|---|---|
| Does any ransomware still check language? | Yes, MITRE ATT&CK lists several families that do[9] |
| Which checks are used? | Keyboard layout lists, UI language, install language in the registry[9] |
| Which languages trigger an exit? | Russian, Ukrainian, Belarusian and other CIS languages, depending on the strain[9] |
| Does it protect against all ransomware? | No. Many strains have no such check, and attackers can remove it[3] |
| Is ransomware still active in 2025? | Yes. Check Point tracked LockBit 5.0 attacks in Q3 2025[11] |
| Better protection | Offline backups, updates, careful email habits, security software |
Timeline: language checks in ransomware
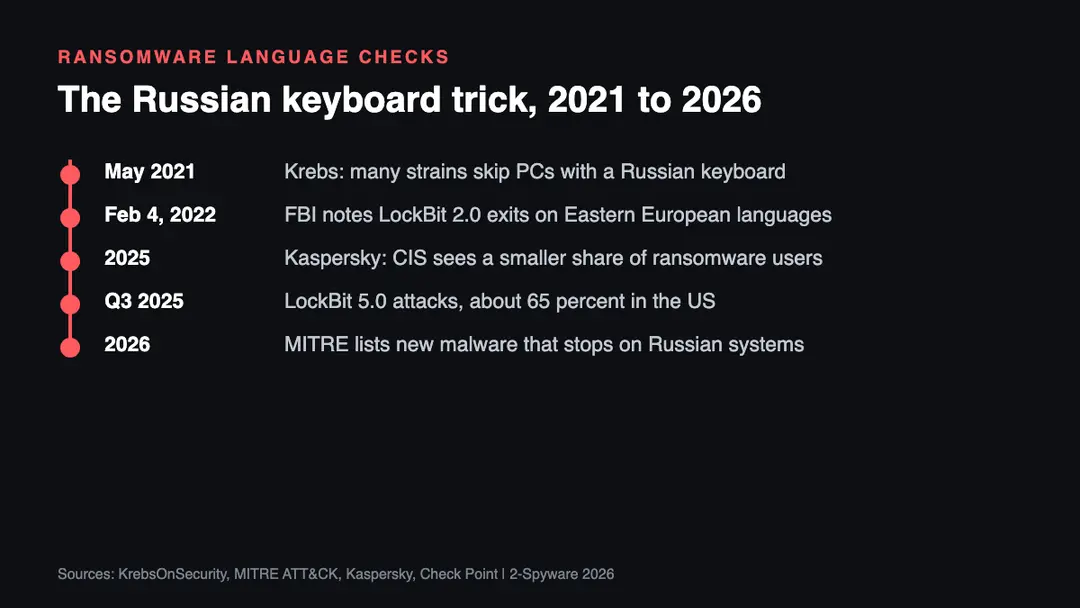
| Date | Event |
|---|---|
| May 2021 | KrebsOnSecurity reports that many ransomware strains will not install on Windows PCs with a Russian or Ukrainian keyboard[3] |
| February 4, 2022 | An FBI alert, cited by MITRE, says LockBit 2.0 can exit when it finds Eastern European languages[9] |
| 2025 | Kaspersky reports that the CIS sees a smaller share of users meeting ransomware[10] |
| Q3 2025 | Check Point tracks LockBit 5.0; about 65 percent of identified attacks hit US organisations[11] |
| 2026 | MITRE ATT&CK lists Mini Shai-Hulud, which stops when a system is set to Russian[9] |
What changed since 2021
The basic behaviour did not go away. MITRE now files it as a named technique, System Language Discovery, with a long list of examples.[9] Ryuk reads the InstallLanguage registry value and stops on Russian, Ukrainian or Belarusian codes. SynAck lists every installed layout, compares it with a hard-coded list, sleeps for 300 seconds and exits.[9]
The checks also spread beyond Windows ransomware. MITRE lists Cuckoo Stealer, which reads the LANG variable on Mac systems to skip Armenia, Belarus, Kazakhstan, Russia and Ukraine. It also lists GlassWorm and Mini Shai-Hulud, supply chain malware that stops on Russian settings.[9] So the trick touches information stealers and developer tools too, not only file encryptors.
What did not change is the target list. Check Point found that about 65 percent of the LockBit 5.0 attacks it identified hit organisations in the United States, with Mexico, Indonesia and European countries next.[11] Kaspersky reports that the CIS sees a smaller share of users who meet ransomware.[10] That pattern matches the reason the language checks exist.
Risks and false comfort around the trick (our analysis)
This section is our own analysis of how the trick can backfire. It is based on the sources above, not on a single report.
- Many ransomware strains have no language check at all, so a Cyrillic layout does nothing against them.
- Attackers who break in by hand can simply ignore the check and run the encryptor anyway.
- Checks differ: some read the keyboard list, others the UI language or a registry value, so one setting does not cover every strain.[9]
- Fake "anti-ransomware language pack" downloads are a lure. Windows adds languages from Settings; no extra file is needed.
- Feeling safe can lead people to skip backups, which are the only reliable way back after encryption.
Steps that protect you better than a keyboard
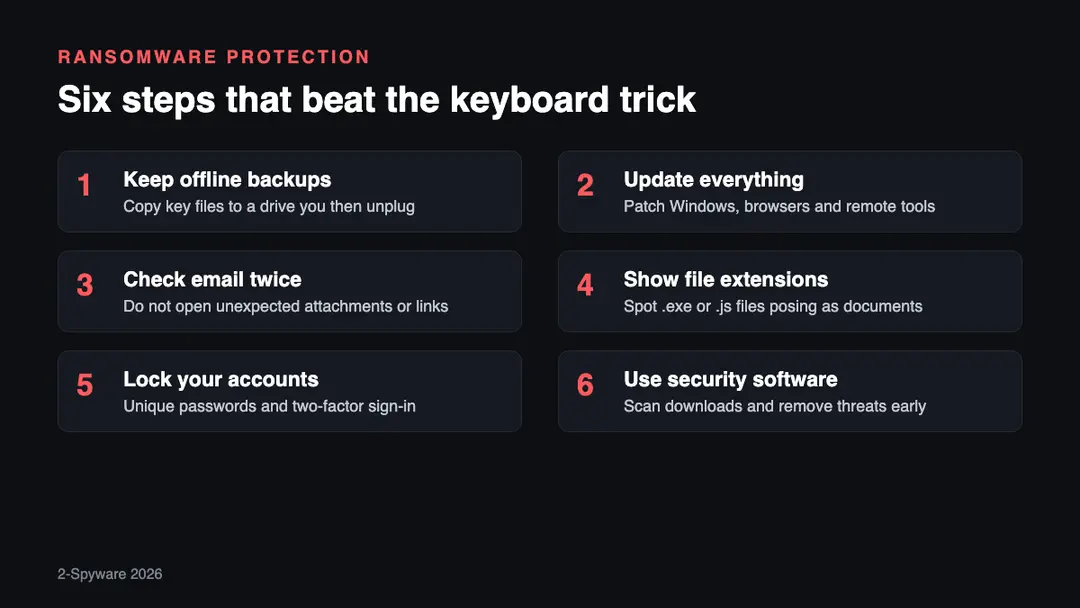
1. Keep offline backups. Copy important files to an external drive or a backup service, then disconnect the drive. Ransomware cannot encrypt a copy it cannot reach.
2. Update everything. Install Windows updates and patch browsers, VPN clients and remote access tools. Attackers often get in through known holes that already have a fix.
3. Check email twice. Do not open attachments or links you did not expect, even from a known name. Phishing remains one of the most common ways ransomware arrives.
4. Show file extensions. Turn on file name extensions in File Explorer so a file called invoice.pdf.exe shows its real type.
5. Lock your accounts. Use unique passwords and two-factor sign-in, and check whether your email appeared in a leak with our leak check.
6. Use security software. Keep a reputable security tool running and scan downloads. Adding a Russian keyboard is fine as an extra, but treat it as a bonus layer only.
What is still unknown
- Whether NotPetya checked keyboard layouts. The sources we read for this update do not list it.[9]
- How many active ransomware strains still carry a language check. We found no 2026 count.
- Whether newer families such as LockBit 5.0 keep the CIS exit. The Q3 2025 report we read does not say.[11]
- Whether ransomware groups will drop the check as the trick becomes known, as Krebs warned in 2021.[3]
Our original 2021 report
The text below is our report as first published in 2021. We keep it unchanged for the record; the sections above bring it up to date.
Recent incidents[1] and changes in cybersecurity policies show that people desperately need to take some actions to avoid hackers and malware attacks. This goes for everyday users ad for large companies. Profit is the main goal for such criminals because they want to make money from victims, so large companies, organizations, businesses in various industries remain common targets for these threats.[2]
Research and various tendencies show that ransomware creators include the feature set to skip the installation on devices where a particular language keyboard is installed.[3] Russian or Ukrainian languages are the typical exceptions, so it can become one of a few ways to avoid ransomware infections.
DarkSide, like a great many other malware strains, has a hard-coded do-not-install list of countries which are the principal members of the Commonwealth of Independent States (CIS) — former Soviet satellites that mostly have favorable relations with the Kremlin.
The analyzed DarkSide ransomware, and many other threats focused on cryptocurrency extortion, include code that installs malicious threats after the system check. In Russia, investigations against criminals like these are commonly not initiated unless the company claims to be a victim. Ransomware is often linked with Eastern European countries and hackers, so this exception technique ensures that affiliates of the virus cannot become victims of the hack or threat infection. It also helps to minimize the scrutiny and avoid interference from authorities.
The malware will exit without attacking if the particular language is installed
Many malware strains check for the keyboard options or language installs when the system is infiltrated. If the particular exclusion language is added, the intruder leaves the machine without executing the malicious code. Main region/language/ keyboard exclusions:
- Russian;
- Ukrainian;
- Belarusian;
- Tajik;
- Armenian;
- Azerbaijani;
- Georgian.
These regions may vary, but the main keyboard option that criminals focus on is Cyrillic.[4] when the huge ransomware group is spreading worldwide, many experts tend to look for connections to other threats and known hacker groups. The most dangerous and the most reported threats[5] in this cryptovirus category remain possible Russian hacker creations like STOP/ Djvu,[6] REvil/ Sodinokibi, Phobos, Dharma, Makop.
When it comes to regions where malware spreads and is reported, Asia is the most common one. The United States comes next, and then other areas follow. However, based on these findings, it is clear that Eastern Europe is not common in these ransomware and other threat attacks. It is believed that hackers do not target their people, so criminals tend to aim further away. It can be relatively easy and not invasive to add the Russian language to your options and install the keyboard settings.
The ransomware infection process explained
Changing language settings or adding a particular keyboard is not difficult, but you should take other security measures. Whether you are a part of a big company or government institution or the everyday user that surfs online daily, you need to take precautionary measures. Understanding how ransomware works is important too here.
Ransomware infects the machine by sending the payload on the targeted device. There are many ways that creators manage to do so.[7] Attack is not starting until the system is checked. If those exclusions are not found, the payload is dropped and launched. Once that is done, the malware gets executed, and files get locked, encrypted, deleted, stolen, or copied. Attackers then receive the notification that the virus was executed. The victim receives the unique key for identification, and the encryption procedure can end with the money extortion and ransom note delivery.
Payment requests and the inability to access files scare victims into considering the ransom paying. Cryptocurrency transfer should be exchanged for the decryption option that can recover files affected in this attack. This is multi-stage malware, and it can be less advanced or more improved, depending on the criminals who created the virus. Sometimes malware steals particular files from huge databases and exports additional payments when victims refuse to pay up. This double-extortion and data-stealing technique became popular in 2020.[8]
Other tips for companies and everyday users that want to avoid ransomware
Dealing with any threat can be stressful and frustrating, but ransomware threats are one of the most dangerous. It depends on who lucky you are and how advanced the virus version you get. It may seem that saying for those criminals is the only option, but often it doesn't mean that locked or affected data will be recovered after all.
Learning from the significant incidents can help prevent these attacks in the future, and mistakes done by others can help to teach industries and governments to improve their security measures. Detecting the ransomware that is already on the machine is not enough. Precautionary measures are needed to prevent the attack in the first place.
- Know what valuable assets are connected to the network. Keep the list of connected software and hardware up to date.
- Personalize security settings. Ransomware can be distributed when the email attachment is opened, so the email server's configuration to block particular types of extensions can help.
- Be cautious and attentive. Think twice before clicking on any link or attachment that looks even a little suspicious. Do not download programs from random sources and torrent sites. Phishing emails and bad links can have major negative consequences.
- Avoid personal information reveal. Criminals can aim to get your personal information and send secondary attacks. Your social media posts, profiles, and other sources can store details that shouldn't be accessible to anyone.
- Educate your employees. Teach all staff members about phishing emails, malicious vectors, common types of circulating attacks. Awareness and training can help avoid infections when people are familiar with tactics.
- Patch and update the software. Keeping machines smoothly working and solving all issues when they occur can help keep the security of the device strong. Exploitation can happen when attackers rely on some vulnerabilities.
- Use Show File Extensions feature. This Windows function allows you to tell what types of files are opened quickly, so you can stay away from potential threats.
- Keep backups. Enterprises and personal computer users should keep current file backups and store essential data on external devices. This is the easiest way to restore any lost data.
- Use VPN services and avid public Wi-fi. Be cautious when using a public network because you cannot be sure about protective measures against malware and make your computer vulnerable to attacks.
Carefulness and caution is the most important thing with any malware. You can be prepared and rely on excellent security software and combat ransomware or different malware. This type of malware targets files directly, so you should be more encouraged to do more frequent backups and prevent attackers. Malicious actors and their products get advanced, which should also resemble the cybersecurity measures that enterprises and people take.
Related guides on 2-Spyware
- LockBit ransomware: what it is and how to remove it
- LockBit 2.0 ransomware: what it is and how to remove it
- REvil ransomware: what it is and how to remove it
- NotPetya ransomware: what it is and how to remove it
- Makop ransomware: what it is and how to remove it
- Sodinokibi ransomware: what it is and how to remove it
Frequently asked questions
Does installing a Russian keyboard still stop ransomware in 2026?
Sometimes, but you should not rely on it. MITRE ATT&CK still lists ransomware and other malware that check keyboard layouts or system language and stop on Russian or other CIS settings.{9} Many other strains do no such check, and attackers can drop it at any time. Backups, patches and careful email habits protect you far better.
Which ransomware checks for specific keyboard layouts?
MITRE ATT&CK names several families. Clop checks the keyboard language with GetKeyboardLayout, Cuba looks for Russian with GetKeyboardLayoutList, SynAck compares installed layouts with a hard-coded list, and Avaddon checks layouts and OS language to avoid CIS targets.{9} LockBit 2.0 and REvil also stop on a list of Eastern European languages.{9}
Did NotPetya check the keyboard layout for Russian?
We could not confirm that. The sources we read for this update describe language checks in Clop, Cuba, Ryuk, REvil, LockBit 2.0 and others, but none of them lists a keyboard check in NotPetya.{9} If you need a firm answer for NotPetya, look for a malware analysis of that exact sample rather than a general list.
Is a Russian language pack itself malware?
No. The Russian keyboard and language pack are normal Windows features, and adding one takes a few clicks in Settings. The idea behind the trick is that some malware reads these settings and exits.{3}{9} Download language packs only through Windows Settings, never from a random site that offers a special anti-ransomware version.
Why do Russian hackers avoid computers with a Cyrillic keyboard?
Mostly to avoid trouble at home. MITRE describes groups that skip CIS language codes because victims there may draw the attention of law enforcement where the operators or their affiliates live.{9} Kaspersky also reports that the CIS sees a smaller share of users meeting ransomware than other regions.{10}
How do I install a Russian keyboard in Windows?
Open Settings, go to Time and language, then Language and region, and add Russian as a language or keyboard. You do not have to switch to it or use it. Keep in mind that this changes only what a few malware checks see; it does not replace backups, updates or security software.
Sources
- ZDNet. Technology news
- Techrepublic. Security and IT news
- Krebsonsecurity. In-depth security news and investigation
- Wikipedia. The free encyclopedia
- Emsisoft. Malware lab blog
- 2spyware. Virus removal guides and spyware news
- ITproportal. Media group (no longer online)
- Helpnetsecurity. Internet security reports
- MITRE ATT&CK
- Kaspersky Securelist
- Check Point Research
Log in to comment
No comments yet. Be the first.