
Moneybird Ransomware News 2026: Agrius Update
- Moneybird ransomware and Agrius in 2026: the short answer
- Timeline: from the first Agrius intrusions to Moneybird
- What changed since 2023
- Risks and scams around Moneybird news
- What to do now: six steps for exposed organizations
- What is still unknown
- Our original 2023 report
- Attack methodology and Moneybird's Operation
- Expanding threat landscape
- Related guides on 2-Spyware
Moneybird ransomware and Agrius in 2026: the short answer
Moneybird is a ransomware strain written in C++ and tied to Agrius, an Iranian threat actor also tracked as Pink Sandstorm. Check Point described it in 2023 as a new tool aimed at Israeli organizations.[1] The MITRE ATT&CK knowledge base still lists Moneybird as software associated with Agrius ransomware operations.[5]
We found no new Moneybird campaign report dated 2026 in the pages we read, so this update does not claim fresh attacks. What the 2026 sources do confirm is the bigger picture: Agrius is active since 2020, public reporting links it to Iran's Ministry of Intelligence and Security, and it is known for wipers disguised as ransomware.[5][6]
| Question | Answer |
|---|---|
| What is Moneybird | A C++ ransomware used by the Agrius group against Israeli organizations[1][5] |
| Other names of the group | Pink Sandstorm, formerly Americium; Agonizing Serpens in some vendor reports[1][6] |
| Active since | 2020, according to MITRE ATT&CK[5] |
| Typical entry point | Vulnerable internet-exposed web servers and an ASPXSpy web shell[1] |
| Known habit | Wipers presented as ransomware, so victims may misjudge the incident[6] |
| New 2026 campaign found | None in the pages we read |
Timeline: from the first Agrius intrusions to Moneybird
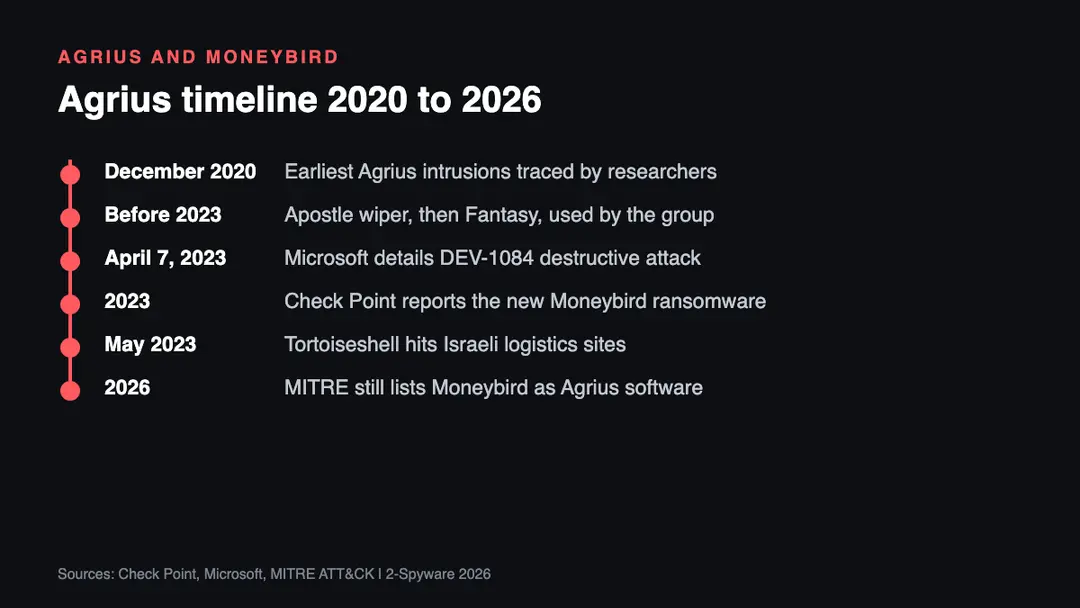
| Date | Event |
|---|---|
| December 2020 | Agrius activity is traced back to at least this month, with intrusions against diamond industries in South Africa, Israel and Hong Kong[1] |
| Before 2023 | The group used the .NET based Apostle, then a successor called Fantasy[1] |
| April 7, 2023 | Microsoft publishes its report on a destructive attack on a hybrid environment by DEV-1084[2] |
| 2023 | Check Point publishes its analysis of Moneybird[1] |
| May 2023 | The Hacker News reports Tortoiseshell compromises of Israeli shipping and logistics sites[3] |
| 2026 | MITRE ATT&CK still describes Moneybird as Agrius ransomware software[5] |
What changed since 2023
In 2023 Moneybird looked like a new step for Agrius, because the group moved from .NET tools to C++. In 2026 the more useful lesson is the pattern behind it. Security vendors describe a group that changes its tools, names and cover stories while keeping the same targets.[5][6]
The group is also known for blurring the line between crime and state activity. Reports describe wipers that pretend to be ransomware, which can send responders down the wrong path at first.[6] A ransom note does not prove that the attacker wants money.
Reference sites have also caught up. MITRE now tracks Moneybird as its own software entry and ties it to data encryption for impact and embedded payloads.[5] That means defenders can map the malware to standard detection and hunting guidance.
Risks and scams around Moneybird news
This section is our own analysis, not a vendor finding. Whenever a ransomware name trends, criminals reuse it as bait.
- Fake decryptor offers. Pages that promise a free Moneybird decryptor can carry malware. We found no public decryptor in the sources we read.
- Panic emails. Messages that claim your files were stolen by Agrius and demand payment within hours copy the 24 hour pressure in the real ransom note.[1]
- Wiper confusion. If data is destroyed rather than locked, paying changes nothing. Treat every incident as possibly destructive until proven otherwise.[6]
- Web server neglect. The documented entry point is an unpatched internet-exposed server, so old systems are the real risk.[1]
What to do now: six steps for exposed organizations
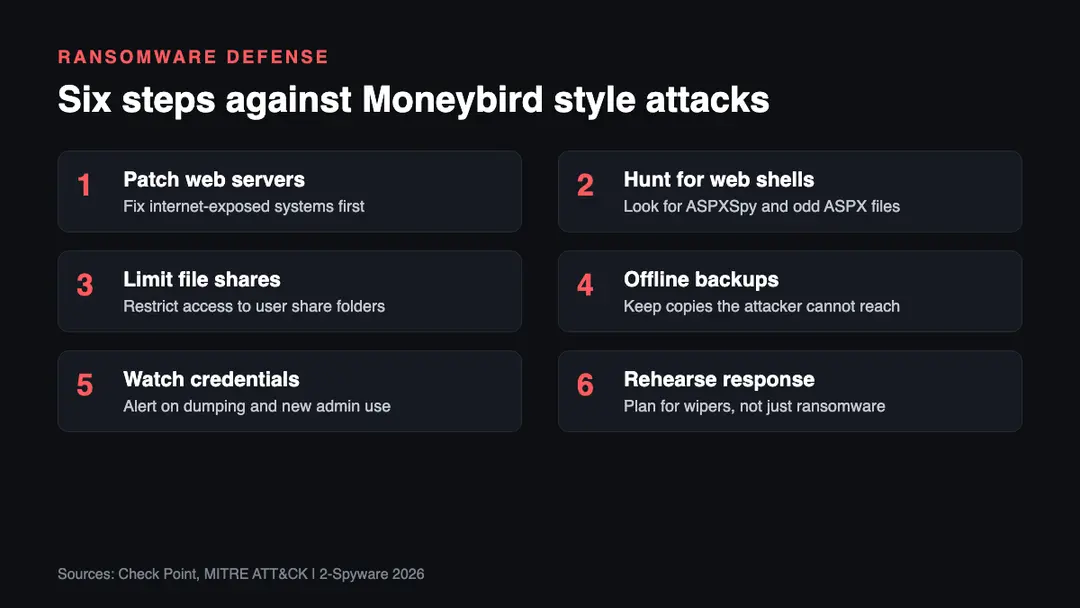
1. Patch exposed web servers. Check Point describes the first foothold as a vulnerability in an internet-exposed web server, so list every public server and update it first.[1]
2. Hunt for web shells. The documented attacks used an ASPXSpy web shell. Search web folders for unknown ASPX files and compare them with a clean copy.[1]
3. Limit file shares. Moneybird was built to encrypt files in a folder named F:\User Shares. Restrict who can write to shared folders and log changes.[1]
4. Keep offline backups. The encryption uses AES-256 in GCM mode with a unique key per file, so restoring from backup is the realistic path.[1]
5. Watch credentials. The attackers harvested credentials and moved sideways with public tools. Alert on credential dumping and unusual admin sign-ins.[1][5]
6. Rehearse for wipers. Because the group is known for fake ransomware, practice an incident where the data is gone and no key exists.[6]
What is still unknown
- Whether Agrius still uses the Moneybird code in 2026. We found no new campaign report.
- How many organizations were hit. Check Point's report did not give a full victim count in the text we read.
- Whether the group changed its name or tools again since the 2023 reports.
Our original 2023 report
The text below is our report as first published in 2023. We keep it unchanged for the record; the sections above bring it up to date.
The Iranian hacker group known as Agrius, also referred to as Pink Sandstorm and formerly Americium, has developed a new ransomware strain dubbed Moneybird. Discovered by CheckPoint researchers,[1] this dangerous malware is being used to target Israeli organizations, marking a significant shift in the group's modus operandi.
Agrius has a known history of perpetrating destructive data-wiping attacks against Israeli entities, often masquerading these as ransomware infections. The advent of Moneybird, written in C++, highlights the group's expanding skills and continued dedication towards crafting fresh cyber tools.
The group's activity has been traced back to at least December 2020, when Agrius was involved in disrupting intrusions aimed at diamond industries in South Africa, Israel, and Hong Kong. Previously, the group used a .NET-based wiper-turned-ransomware named Apostle and its successor known as Fantasy. Unlike these predecessors, Moneybird's programming in C++ exhibits the group's evolving cyber capabilities.
Attack methodology and Moneybird's Operation
The operation of the Moneybird ransomware stands as a testament to the Agrius group's ever-growing technical acumen and efforts to develop newer cyber tools. It demonstrates a sophisticated attack methodology that begins by exploiting vulnerabilities in internet-exposed web servers. This exploitation leads to the deployment of an ASPXSpy web shell, marking the first foothold within the targeted organization's network.
Post-infiltration, the web shell acts as a channel to deliver a suite of publicly-known tools tailored to perform in-depth reconnaissance of the victim environment, move laterally, harvest credentials, and exfiltrate sensitive data.
Moneybird ransomware is subsequently launched on the compromised host, designed specifically to encrypt sensitive files within the "F:\User Shares" folder. Once executed, the ransomware drops a ransom note, pressurizing the victims to make contact within a 24-hour window or risk their stolen data being leaked publicly.
For its encryption methodology, Moneybird employs AES-256 with GCM (Galois/Counter Mode). This sophisticated approach generates unique encryption keys for every file and appends encrypted metadata at the end. This precise targeting and advanced encryption make data restoration and file decryption significantly challenging, if not impossible, in most instances.
Expanding threat landscape
Despite Agrius's expansion and refinement of tactics, it remains just one element of a larger, Iranian state-sponsored cyber operation ecosystem. Other groups, such as MuddyWater and Storm-1084 (aka DEV-1084), have also been found deploying ransomware attacks against Israeli organizations. A recent report from Microsoft highlighted this continued and possibly growing, pattern of state-sponsored cyber aggression.[2]
Simultaneously, recent disclosures from ClearSky indicate an escalation in these cyber threats, with at least eight Israeli websites associated with shipping, logistics, and financial services companies compromised.[3] These compromises are believed to be a part of a watering hole attack orchestrated by the Iran-linked Tortoiseshell group.
Moreover, Israel's regional managed service providers (MSPs) have also been targeted in a recent phishing campaign designed to initiate supply chain attacks against their downstream customers. This trend, highlighted by Proofpoint,[4] underscores the escalating threats faced by small and medium-sized businesses from these sophisticated threat groups.
The persistent cyber operations and the emergence of the new Moneybird ransomware underline the importance of good network hygiene and preparedness against evolving cyber threats. As Agrius and its peers continue to escalate their activities, Israeli organizations must remain vigilant and bolster their cyber defenses to mitigate the risks posed by these formidable adversaries.
Related guides on 2-Spyware
Frequently asked questions
What is the latest Moneybird news in 2026?
We found no new Moneybird campaign report dated 2026. The latest solid facts are Check Point's 2023 analysis and the MITRE ATT&CK entry, which still lists Moneybird as ransomware software tied to Agrius.{1}{5} We will update this page if a vendor publishes a new case.
Who is behind Moneybird ransomware?
The Iranian group Agrius, also called Pink Sandstorm, is behind it. MITRE says the group has been active since 2020 and that public reporting links it to Iran's Ministry of Intelligence and Security.{5} Check Point attributed Moneybird to the group in 2023.{1}
What does Moneybird ransomware target?
It targeted Israeli organizations, according to Check Point. The ransomware was built to encrypt files in the F:\User Shares folder and leaves a ransom note that gives victims 24 hours to make contact before stolen data is leaked.{1}
How does Moneybird get into a network?
Attackers exploit vulnerabilities in internet-exposed web servers and drop an ASPXSpy web shell. From there they use public tools for reconnaissance, lateral movement, credential theft and data exfiltration before launching the ransomware.{1}
Is Agrius the same as Pink Sandstorm?
Yes. MITRE lists Pink Sandstorm as an associated name for Agrius, and the original Check Point and Microsoft reporting uses the same group family.{5} Some vendors use other names, such as Agonizing Serpens.{6}
Log in to comment
No comments yet. Be the first.