
Is LibreOffice Safe in 2026? OpenOffice Flaws and Updates
- LibreOffice and OpenOffice security in 2026: the short answer
- Timeline: office suite flaws from 2021 to 2026
- What changed since 2021
- Risks and scams around office suites (our analysis)
- How to keep LibreOffice and OpenOffice safe
- What is still unknown
- Our original 2021 report
- Weaknesses have been fixed with the newest versions
- Malicious macros can easily get used by criminals
- Related guides on 2-Spyware
LibreOffice and OpenOffice security in 2026: the short answer
LibreOffice is safe to use in 2026 if you keep it updated. Its developers still publish security fixes often. On October 5, 2026 they announced six new flaws, including one that allowed remote code execution, all fixed in LibreOffice 26.2.5 and 26.8.0.[9]
Apache OpenOffice also still ships fixes, but less often. Its security bulletin lists version 4.1.16 as the release that fixes seven flaws numbered CVE-2025-64401 to CVE-2025-64407.[10] The signature spoofing bugs from our 2021 report below were fixed long ago, in OpenOffice 4.1.11 and the LibreOffice versions listed there.[3][4]
| Question | LibreOffice | Apache OpenOffice |
|---|---|---|
| Still getting security fixes? | Yes, advisories announced in September and October 2026[9] | Yes, the latest bulletin covers 4.1.16[10] |
| Version to run | 26.2.5 or 26.8.0 or newer[9] | 4.1.16 or newer[10] |
| Most serious recent flaw | Remote code execution via Calc data mappings and a JDBC connector[9] | Remote documents loaded without a prompt[10] |
| 2021 signature flaws | Fixed, see CVE-2021-25635[4] | Fixed in 4.1.11[3] |
| Official download | libreoffice.org[6] | openoffice.org[5] |
Timeline: office suite flaws from 2021 to 2026
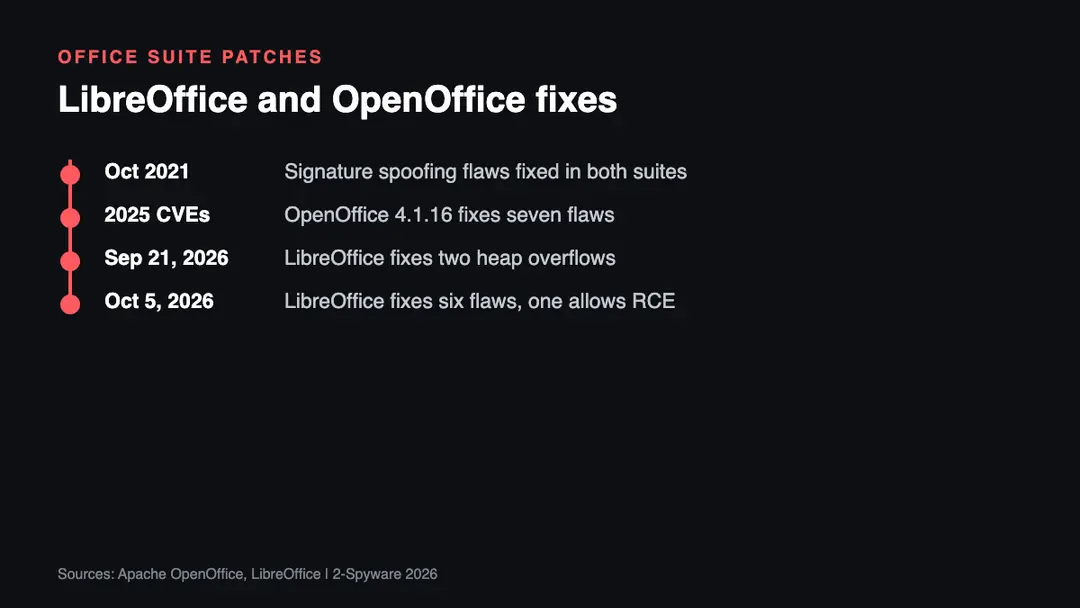
| Date | Event |
|---|---|
| October 2021 | Signature spoofing flaws reported and fixed, covered in our original report[1][3] |
| CVE-2025 series | OpenOffice 4.1.16 fixes CVE-2025-64401 to CVE-2025-64407[10] |
| September 21, 2026 | LibreOffice announces heap buffer overflows in WMF and PDF import, fixed in 26.2.5[9] |
| October 5, 2026 | LibreOffice announces six flaws, including remote code execution, fixed in 26.2.5 and 26.8.0[9] |
What changed since 2021
In 2021 the main worry was forged digital signatures that could make a macro look trusted.[2] The 2026 advisories show a different kind of risk. Several LibreOffice bugs abuse data mapping features in Calc to read local files, reach internal web addresses or, in one case, run code.[9] Others are heap buffer overflows in the import of WMF images and PDF files.[9]
OpenOffice's recent fixes follow a similar theme. Five of the seven flaws in its latest bulletin let a document load remote content without asking the user, through IFrames, OLE objects, external data sources, images or the DDE function.[10] Another lets URL fetching leak settings and environment variables.[10] Opening a file can quietly contact a server the attacker controls.
One thing has not changed. LibreOffice versions now use a year-based number such as 26.2.5, so the old advice to run 7.0.5 or 7.1.1 in the text below is long out of date. Run the newest version the official site offers.[6][9]
Risks and scams around office suites (our analysis)
This list is our analysis of the common ways people get hurt through free office suites. It is not a quote from the vendors.
- Fake download sites. Free and popular software is often copied onto look-alike sites that bundle adware or malware. Download only from libreoffice.org or openoffice.org.[5][6]
- Macro documents in email. A file that asks you to enable macros is still the classic infection route described in our original report.[7]
- Booby-trapped spreadsheets. The 2026 Calc flaws mean a crafted file could read local files or run code on an old version.[9]
- Old installs that never update. Neither suite updates silently by default on every system, so old versions stay in use for years.
How to keep LibreOffice and OpenOffice safe
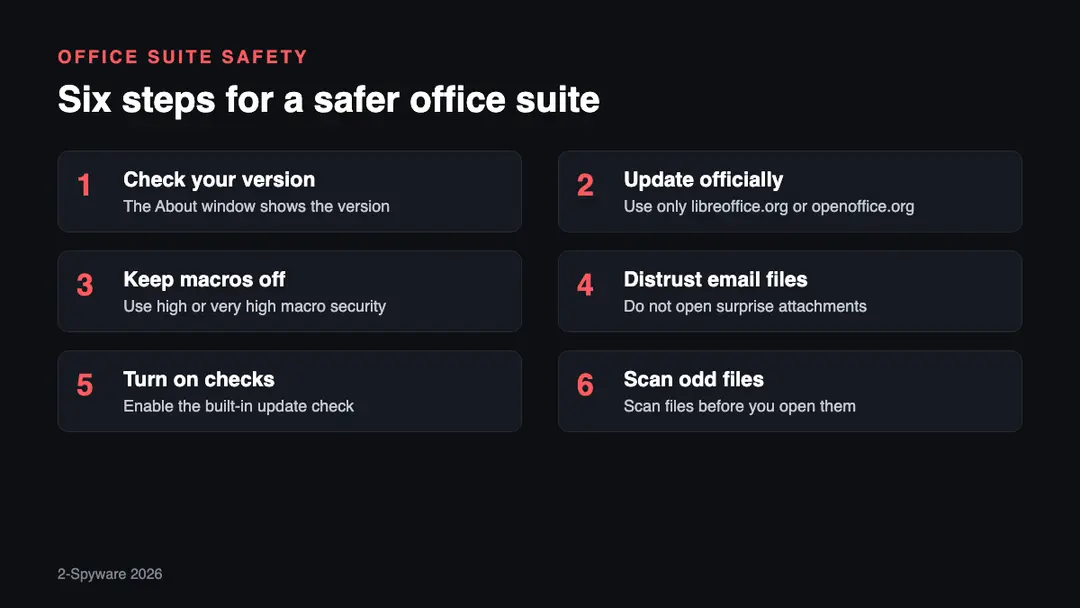
1. Check your version. Open the About window of the program to see which version you run. Compare it with the fixed versions listed in the vendor advisories.[9][10]
2. Update officially. Download LibreOffice from libreoffice.org and OpenOffice from openoffice.org.[5][6] Avoid download portals that wrap the installer in their own setup program.
3. Keep macros off. Open the macro security setting in the program options and choose a high level, so that unsigned macros do not run. The vendors' help pages show the exact menu for your version. Enable macros only for a file you created or fully trust.
4. Distrust email files. Invoices, orders and "confidential" files from unknown senders are typical lures, as our original report explains.[7]
5. Turn on checks. Keep the built-in update check enabled rather than disabling it. Disabling updates leaves known flaws open.
6. Scan odd files. If a file behaves strangely or you already enabled macros, scan the computer. Our virus removal guides explain what to look for.
What is still unknown
- Whether any of the 2026 LibreOffice flaws were exploited before the fix. The advisories we read do not say so.[9]
- The exact release date of OpenOffice 4.1.16 and whether a newer release is planned. The bulletin we read lists the fixes but we did not confirm a date.[10]
- How many users still run versions older than the fixes. We found no public figure.
We will update this page when either project publishes a new security advisory that changes this advice.
Our original 2021 report
The text below is our report as first published in 2021. We keep it unchanged for the record; the sections above bring it up to date.
Productivity software flaws might get used by malicious actors, so the security update is shipped by maintainers.[1] The flaw can provide the ability to manipulate documents into appearing to be digitally signed by the trusted source.[2] These digital signatures are used to verify that the document is not altered and can be trusted.
These flaws are not high in severity, but the consequences can be serious once the flaw gets exploited and signatures are forged in document macros. Signing the random document and faking its legitimacy is the way to trick users into allowing the macros and running malicious code.[3]
- CVE-2021-41830/ CVE-2021-25633. The content and macro manipulation flaw with double certificate attack.
- CVE-2021-41831/ CVE-2021-25634. The timestamp manipulation with signature wrapping.
- CVE-2021-41832/ CVE-2021-25635.[4] Content manipulation with certificate validation attack.
If these flaws get successfully used and permit the attacker to timestamp the document, alter the contents, the document can be used as a trustworthy piece. Attackers can inject other algorithms into these documents and sign them, suggesting that they are not tampered with and signed by a trusted party.
Weaknesses have been fixed with the newest versions
The CVE-2021-41832 flaw tracked in the OpenOffice was disclosed by four researchers from the Ruhr University Bochum. The same flaw was known as the CVE-2021-25635 vulnerability in LibreOffice. Users who use the open-source office suites should upgrade to the latest available versions right away to avoid any consequences. For OpenOffice, it should be 4.1.10 and later, and for LibreOffice, 7.0.5, 7.1.1, or later.
These upgrades need to be done manually because applications do not offer the auto-updating feature. Download the latest versions from particular download centers.[5][6] You can also disable the macro function[7] if the updating is not happening or is not possible. Avoid trusting any random documents with macros. If you are still running the older versions, do not rely on the trusted list function. It is not a severe flaw, but laced and malicious documents can appear as coming from trusted sources.
Malicious macros can easily get used by criminals
Macro malware is the threat type that can be hidden in the Office files like Word or Excel. These files usually get delivered in malicious email campaigns and attached to messages or inside the ZIP files. These are common vectors for infections like ransomware because the payload of the virus can get triggered once macros get enabled on the document.
This type of malware made a comeback, and identifying these threats became very important since the ransomware aims at large businesses, companies, and everyday users. Phishing emails can easily transmit these attachments, and the text in the email requests the person to open the document and view the sensitive content that leads to run off the macro. This is the start of malware code injection into the VBA that begins to cause the infection.
Commonly, when the macro is already set to act maliciously and is included in the particular campaign, these are the signs that users can look out for and be suspicious of:
- unknown senders;
- random emails from unfamiliar or unrelated companies;
- emails with details on unfamiliar purchases;
- subject lines like "confidential", "project", "invoice", "order details";
- documents with preview mode;
- files with the suspicious process of macros.
Apache had another vulnerability discovered recently.[8] The vulnerability revealed that it could allow the remote code execution for unauthorized actors once exploited. Upgrades of software and applications occasionally are always recommended especially, since many developers do not come forward with their or third-party research findings.
Related guides on 2-Spyware
Frequently asked questions
Is LibreOffice safe to use in 2026?
Yes, as long as you keep it updated and download it from libreoffice.org.{6} The project still publishes security advisories, and its October 5, 2026 fixes, including one for remote code execution, are in versions 26.2.5 and 26.8.0.{9} Older versions carry known flaws, so update before you open files from others.
Is LibreOffice malware?
No. LibreOffice itself is legitimate open source software. The risk comes from fake copies on look-alike download sites and from malicious documents that abuse old, unpatched versions.{9} Download only from the official site and keep macros disabled unless you trust the file completely.
Which gets security updates more often, LibreOffice or Apache OpenOffice?
LibreOffice does, based on what we read. It announced new advisories in both September and October 2026.{9} Apache OpenOffice's bulletin lists 4.1.16 as its latest security release, fixing seven 2025-numbered flaws.{10} If security updates matter to you, LibreOffice is the more actively patched suite.
How do I enable macros in LibreOffice or OpenOffice?
Open the macro security setting in the program options, then choose a lower level or add a trusted folder; the official help pages show the exact menu for your version. Do this only for files you created or fully trust. Malicious macros in email attachments remain a common way to spread malware, so keep the level high by default.{7}
Should I disable LibreOffice automatic update checks?
We advise against it. The update check is how most people learn about versions that fix flaws like the ones announced in 2026.{9} If you manage many computers centrally, replace it with your own update process rather than simply turning it off.
Are fake OpenOffice downloads dangerous?
Yes. Copies of free software on unofficial sites can bundle adware or malware with the real installer. Get Apache OpenOffice only from openoffice.org.{5} If you installed it from another site, uninstall it, scan your computer and reinstall from the official page.
Sources
- Thehackernews. News on IT incidents and malicious actors
- Bleepingcomputer. IT and security news
- Apache. Official blog
- LibreOffice. Flaw report
- OpenOffice. Official Apache download
- LibreOffice. Official Apache product (no longer online)
- Digitalguardian. Datainsider blog
- Helpthenetsecurity. Internet security reports
- LibreOffice
- Apache OpenOffice
Log in to comment
No comments yet. Be the first.